Recent Hospitality Cyber Attacks

Page 3 of 3
Hacked Wi‑Fi Portals Steal M365 Logins

Hacked Wi‑Fi Portals Steal M365 Logins

Microsoft and ReliaQuest report a real campaign where attackers tampered with public Wi‑Fi captive portal networks (hotels/conference venues) to redirect users to attacker-controlled pages. The goal was to steal Microsoft 365 credentials (and sometimes deliver malware) by using…

August 3, 2026
Hotel Wi‑Fi Captive Portals Used to Steal M365

Hotel Wi‑Fi Captive Portals Used to Steal M365

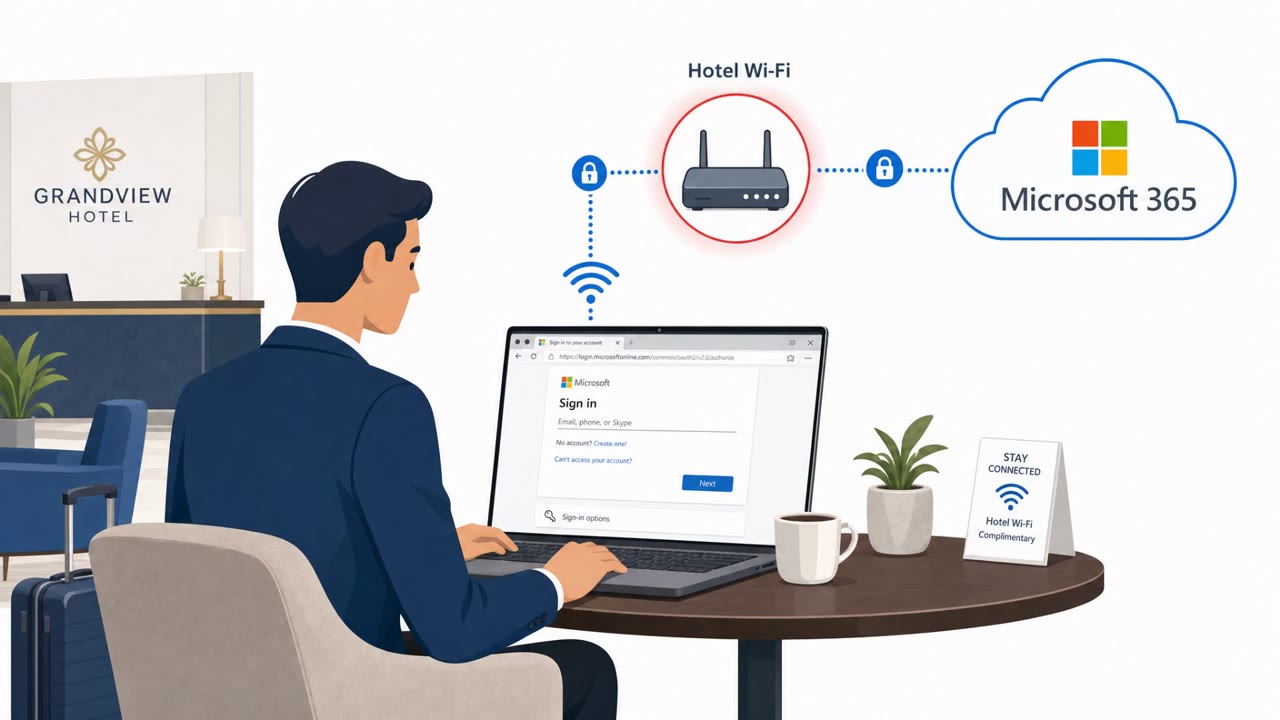
Microsoft reported a real campaign where Russian-linked attackers tampered with hotel and conference Wi‑Fi “captive portals” to redirect travelers to attacker-controlled pages. Victims were tricked into installing malware or completing a Microsoft “device code” sign-in that granted the attacker…

August 1, 2026
Hijacked Hotel Wi‑Fi Serves Fake Updates

Hijacked Hotel Wi‑Fi Serves Fake Updates

Attackers hijacked hotel/captive-portal Wi‑Fi infrastructure to redirect travelers to fake browser or operating system update pages and trick them into installing spyware. The operation (tracked as CaptiveCrunch) used DNS manipulation and user prompts (including “ClickFix” instructions) to get…

August 1, 2026
Captive Portal Trick Hits Travelers With Fake Updates

Captive Portal Trick Hits Travelers With Fake Updates

Microsoft reports a real-world campaign where attackers tamper with Wi‑Fi captive portal traffic at hotels and similar venues to redirect travelers to attacker-controlled pages. Victims are pushed into fake Microsoft sign-ins (device code/OAuth phishing) or tricked into installing “browser/OS…

July 31, 2026
“Half-Click” OWA Email Trap Spreads

“Half-Click” OWA Email Trap Spreads

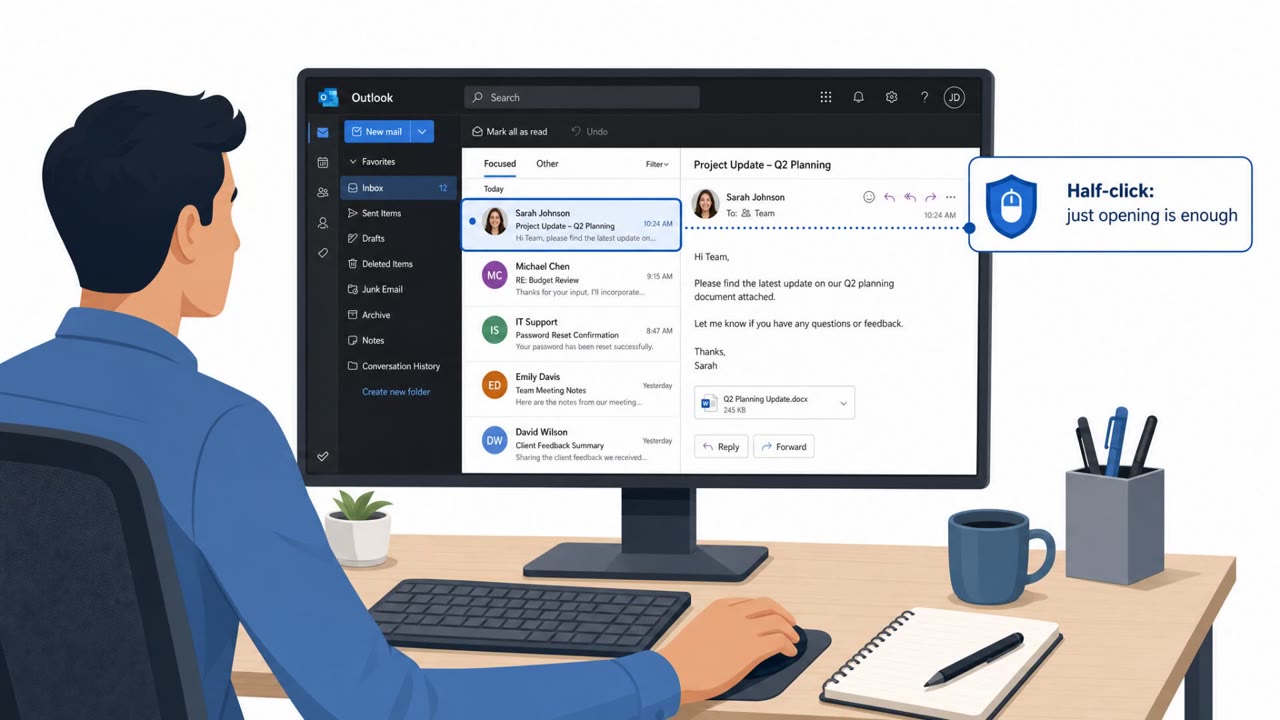
Proofpoint reports a Russian-linked espionage group is using booby-trapped emails that infect users simply when they open the message in Outlook Web Access (OWA) on on‑premises Exchange. The attack runs malicious JavaScript inside the victim’s logged-in mail session and installs a stealthy…

July 30, 2026
Half-Click OWA Emails Trigger Stealth Mailbox Takeover

Half-Click OWA Emails Trigger Stealth Mailbox Takeover

A Russia-aligned group (TA488) sent specially crafted emails that triggered malicious JavaScript simply by being viewed in Outlook Web Access (no link click or attachment needed). The implant (“OWAReaper”) can quietly change server-side mailbox permissions and abuse OAuth tokens, so attackers can…

July 30, 2026
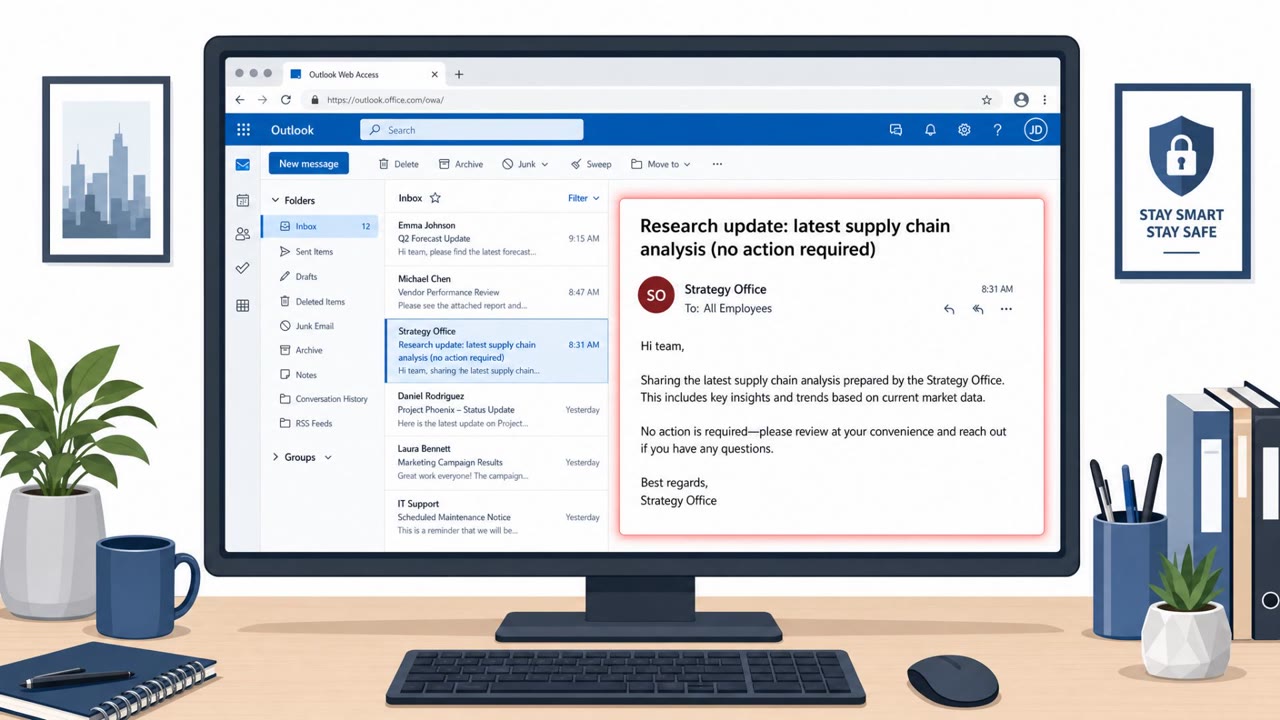
“No-Action” Emails Trigger OWA Mailbox Takeover

“No-Action” Emails Trigger OWA Mailbox Takeover

Russian-linked threat actors sent generic-looking informational emails that required no clicking, but simply opening them in vulnerable Outlook Web Access (OWA) could trigger a hidden exploit. The campaign targeted government and multiple industries, then installed a stealthy browser-based implant…

July 30, 2026
35,000+ World Cup Fake Sites Trap Fans

35,000+ World Cup Fake Sites Trap Fans

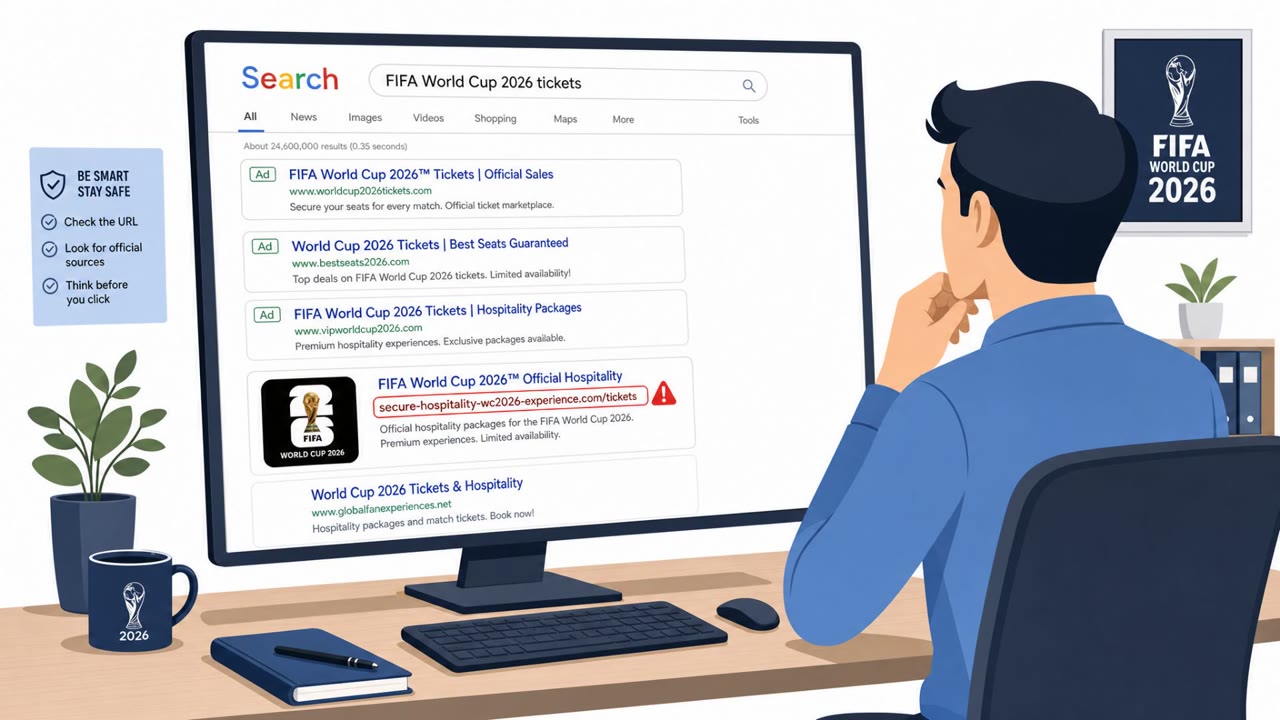
Researchers tracked a large scam wave abusing interest in the 2026 FIFA World Cup, including fake merchandise stores, cloned ticket sites, and bogus “free streaming” pages. The most harmful scams used near-perfect ticket-site clones to steal login details, credit card data, and one-time passwords…

July 29, 2026
Laundry Bear Uses “Half-Click” OWA Email Exploit

Laundry Bear Uses “Half-Click” OWA Email Exploit

UK and US cyber authorities and Proofpoint reported a real campaign where the Russian-linked group “Laundry Bear” (TA488) sent emails that could infect victims simply by being opened in Outlook Web Access. The email’s HTML triggers the server to run attacker code, installing a mailbox-stealing…

July 29, 2026
TA488 Uses “Half-Click” OWA Emails to Persist

TA488 Uses “Half-Click” OWA Emails to Persist

Proofpoint reports a Russia-aligned espionage group (TA488) returned with a campaign that compromises on‑premises Outlook Web Access simply when a user opens an email in the reading pane. The attack uses a cross-site scripting flaw to run hidden JavaScript, install a browser-resident implant, and…

July 29, 2026
Tax and SSA Lures Push Stealth Malware via Cruciferra

Tax and SSA Lures Push Stealth Malware via Cruciferra

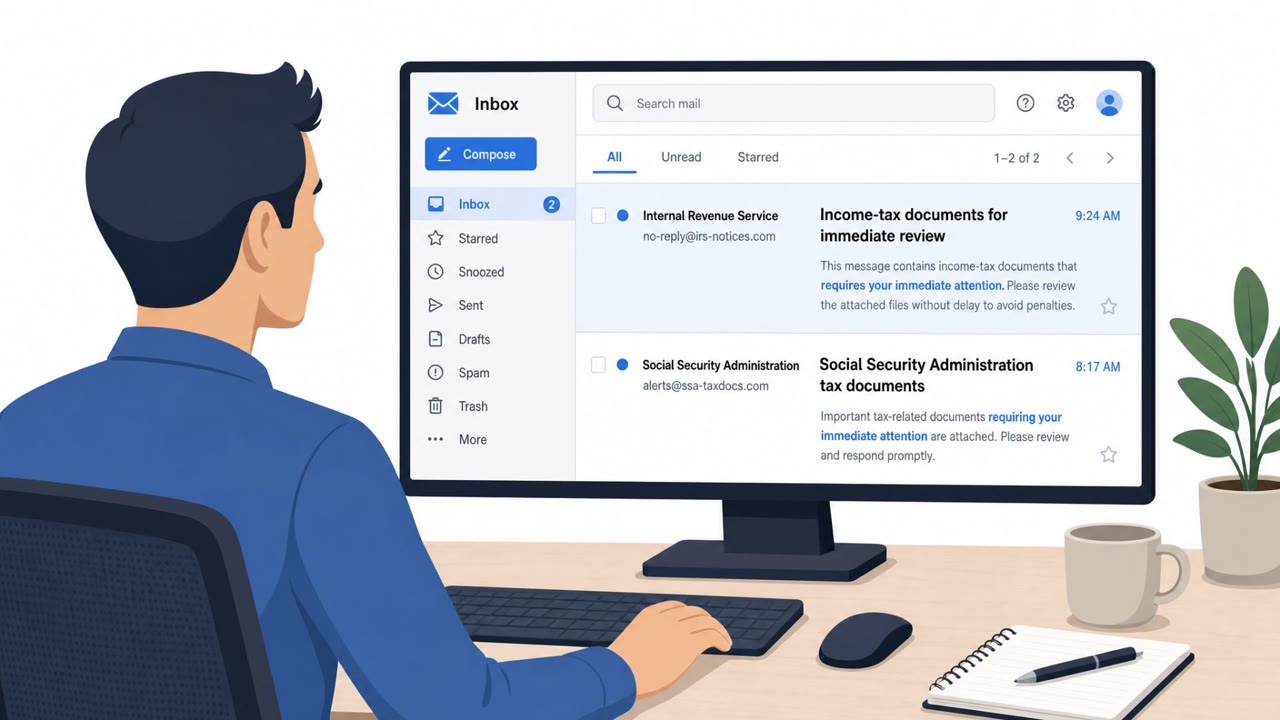
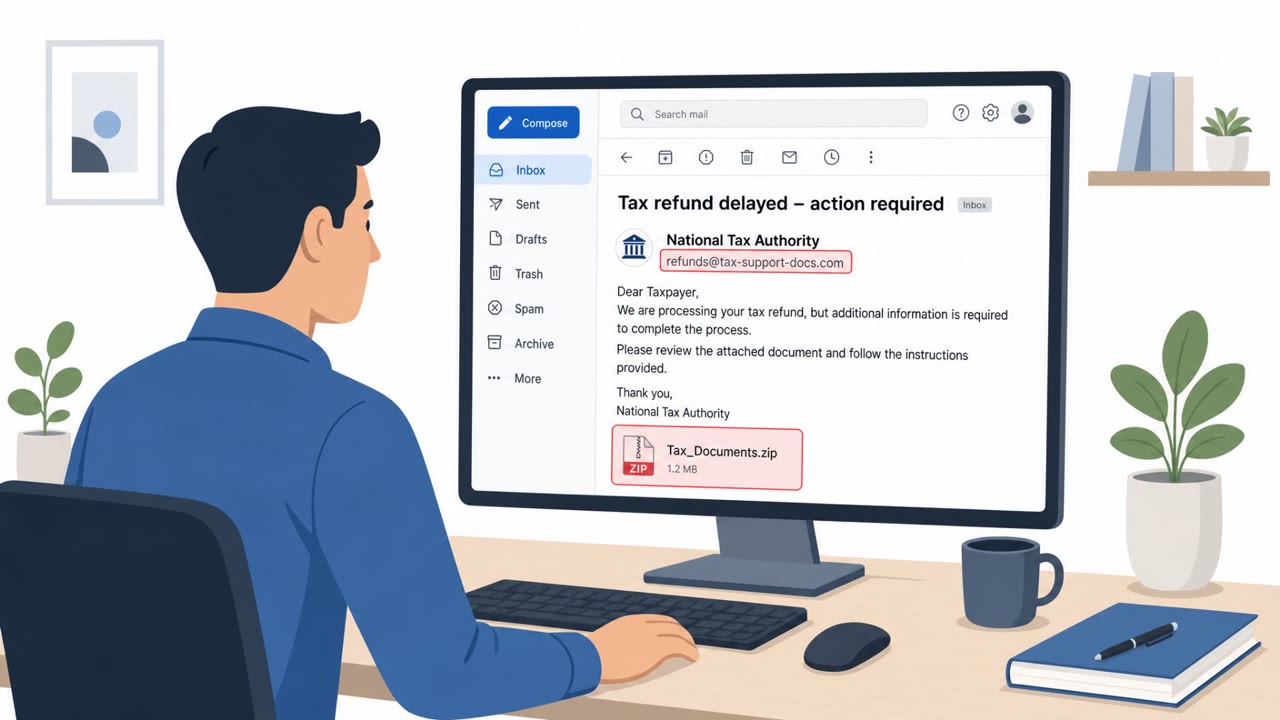
Proofpoint linked multiple real-world email campaigns to “Cruciferra,” a commercial crypter service that helps criminals hide malware from security tools. The campaigns used familiar social-engineering themes, tax documents, U.S. Social Security Administration messages, and even bed-bug complaints,…

July 28, 2026
Hotel Wi‑Fi DNS Hijack Steals M365 Logins

Hotel Wi‑Fi DNS Hijack Steals M365 Logins

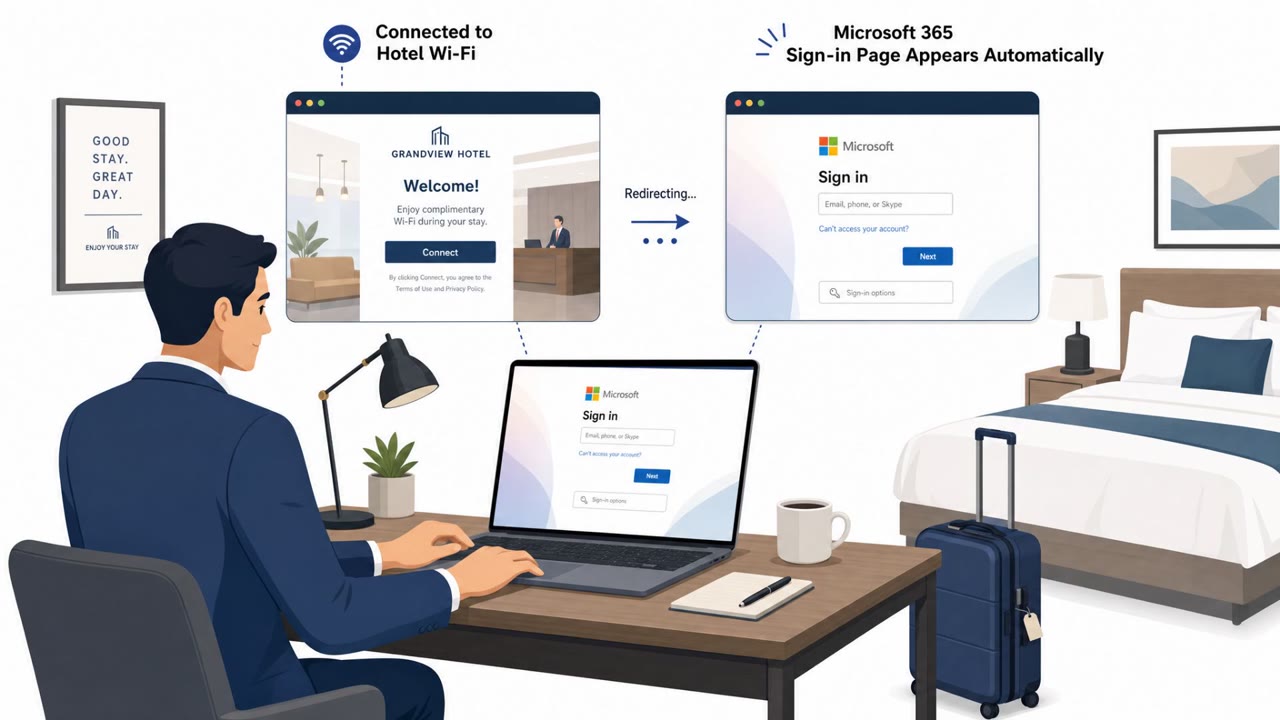
Researchers report attackers compromising hotel and venue Wi‑Fi “captive portal” gateways to redirect Microsoft 365 sign-ins to attacker-controlled lookalike domains. Victims can have their Microsoft 365 credentials stolen without clicking a phishing link or installing malware, because the…

July 28, 2026
Hotel Wi‑Fi Redirect Scam Steals Microsoft 365 Logins

Hotel Wi‑Fi Redirect Scam Steals Microsoft 365 Logins

Attackers are compromising hotel and conference center Wi‑Fi gateways and changing DNS settings so business travelers are silently redirected to fake Microsoft 365 login pages. When victims sign in, attackers steal passwords and potentially session tokens, allowing account takeover even when…

July 27, 2026
Fake ShinyHunters Sextortion Demands $2,000

Fake ShinyHunters Sextortion Demands $2,000

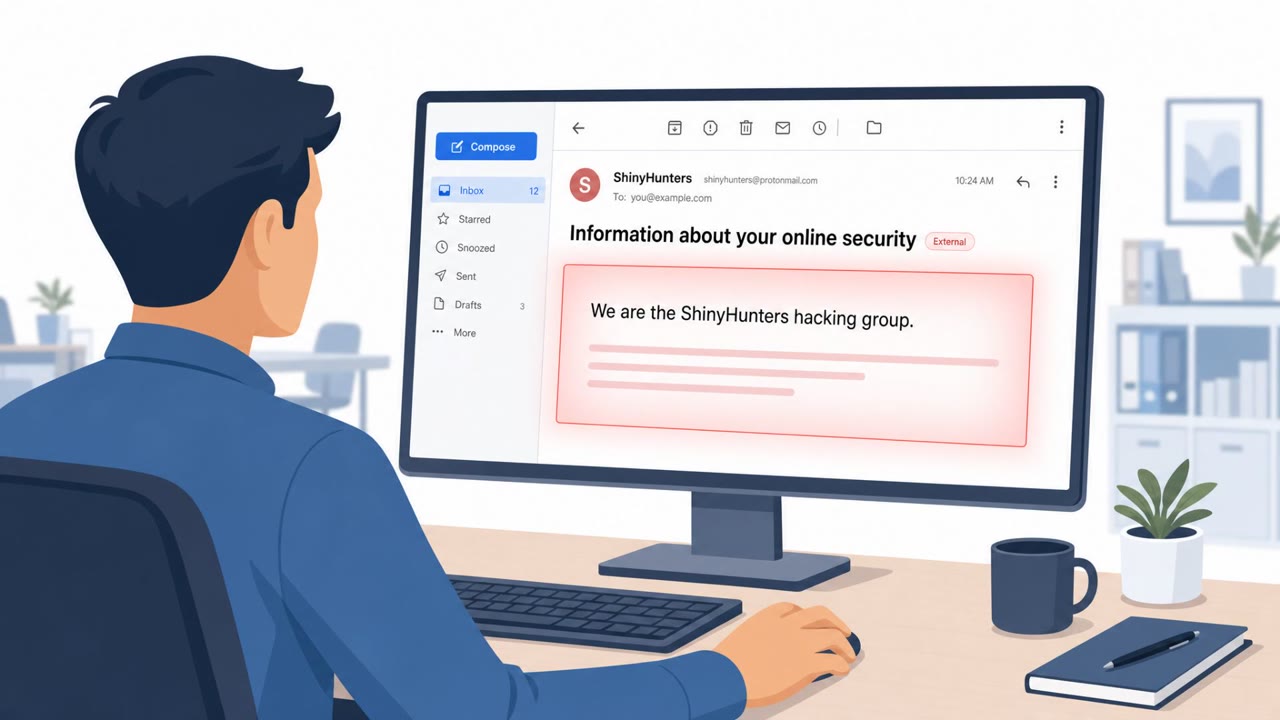
A sextortion email campaign is using real leaked email addresses from ShinyHunters-related data dumps to make threats sound credible. The scammers impersonate the “ShinyHunters hacking group,” claim they recorded victims via webcam, and demand $2,000 in Bitcoin within 48 hours. Reporting indicates…

July 27, 2026
Hotel Wi‑Fi Hijacks Microsoft 365 Logins

Hotel Wi‑Fi Hijacks Microsoft 365 Logins

Researchers report attackers compromising hotel and conference Wi‑Fi gateway equipment to silently redirect travelers to fake Microsoft 365 sign-in pages, without sending phishing emails. In some cases, attackers also abuse Microsoft device-code login prompts so victims unintentionally approve…

July 27, 2026
Tax and SSA Phish Push Cruciferra Malware Loader

Tax and SSA Phish Push Cruciferra Malware Loader

Researchers report multiple real-world email phishing campaigns that used tax and government-benefit themes to trick people into downloading malware. The campaigns used a “crypter” service called Cruciferra to hide malicious files and help malware run while avoiding detection. Targets included…

July 27, 2026
Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

ReliaQuest reports attackers are compromising public Wi‑Fi “captive portal” gateways (such as in hotels and conference centers) and changing their DNS settings to redirect users to attacker-controlled pages. The goal is to harvest traveling employees’ Microsoft 365 credentials using…

July 27, 2026
Hotel Wi‑Fi DNS Trick Steals Microsoft 365 Logins

Hotel Wi‑Fi DNS Trick Steals Microsoft 365 Logins

Researchers found attackers taking over hotel and conference-center Wi‑Fi gateways and silently redirecting guests to fake Microsoft 365 sign-in pages to steal credentials. In some cases, the attackers also tried to route broader device traffic through a malicious proxy (WPAD) or trick users into…

July 26, 2026
Hotel Wi‑Fi DNS Poisoning Steals Work Logins

Hotel Wi‑Fi DNS Poisoning Steals Work Logins

Researchers reported an ongoing campaign where attackers compromise hotel and conference venue Wi‑Fi routers and quietly redirect visitors’ web traffic through attacker-controlled systems. This can lead to corporate usernames and passwords being captured even when the victim does not click a…

July 24, 2026
LinkedIn Exec Impersonation Beat MGM Help Desk

LinkedIn Exec Impersonation Beat MGM Help Desk

The article highlights how attackers can quickly build convincing executive “profiles” from public information and use them to manipulate employees. It cites the 2023 MGM Resorts incident where attackers allegedly used an executive’s LinkedIn details to impersonate them in a help desk phone call…

July 16, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo