Recent Hospitality Cyber Attacks

Attacks on hotels, restaurants, and travel companies, including booking scams and phishing aimed at front-desk and corporate staff. Each entry is broken down with an original video explainer, key findings, and the red flags your team should watch for. How we produce these.

Scammers Relaunch Fake Stores in Hours

Scammers Relaunch Fake Stores in Hours

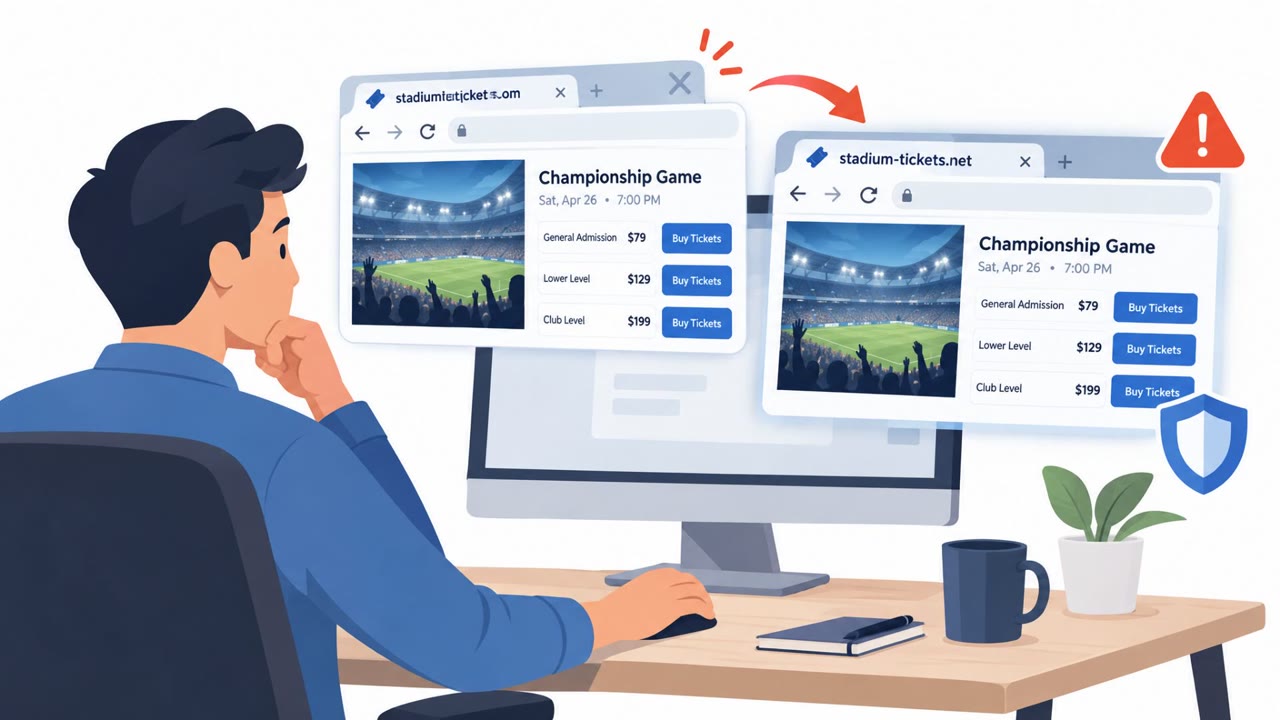
Akamai documented scam operations that use large numbers of look-alike shopping and ticketing websites to steal payment and identity information. The operators can quickly replace a removed site with another domain connected to the same payment-data collection system. Other campaigns used…

October 30, 2026
Booking.com Scams Put Travelers and Hotels at Risk

Booking.com Scams Put Travelers and Hotels at Risk

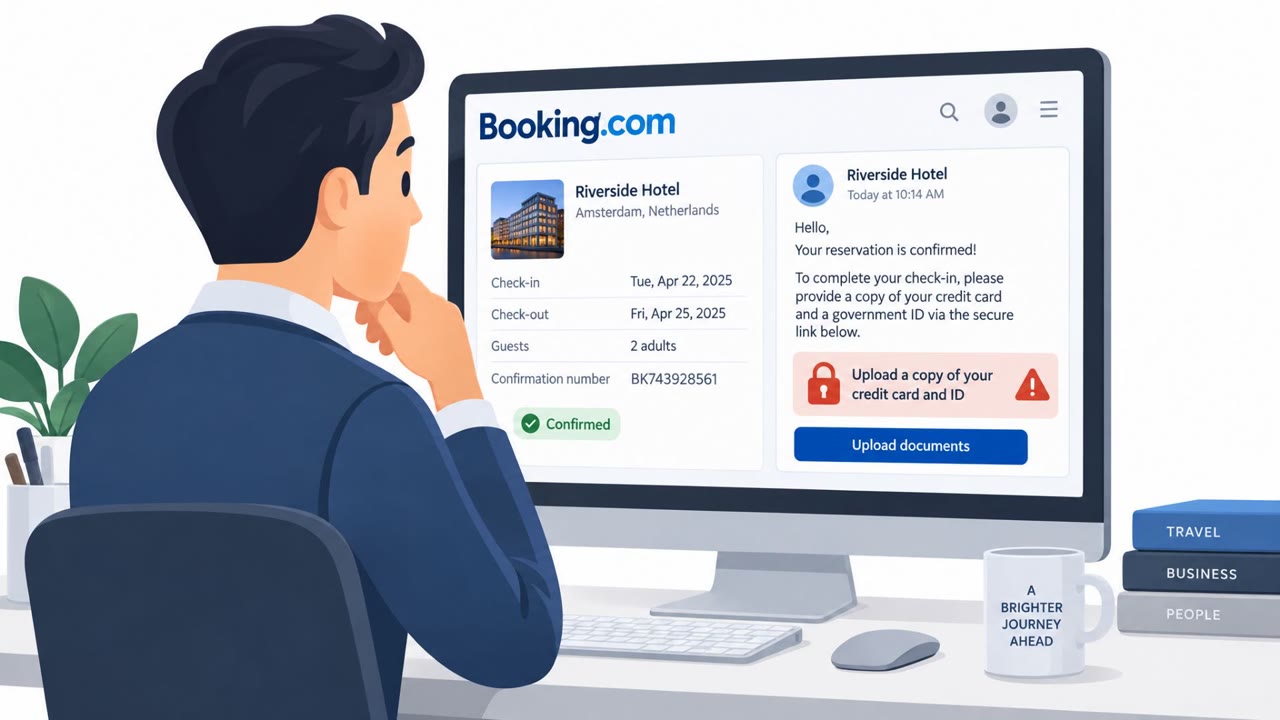
EU regulators are investigating Booking.com over phishing, fraudulent listings, and impersonation scams affecting travelers and accommodation partners. The article describes several real campaigns, including fake Booking.com messages that sought payment details from customers and complaint-themed…

October 22, 2026
Booking.com Scam Probe Targets Fake Stays

Booking.com Scam Probe Targets Fake Stays

EU regulators are investigating whether Booking.com has done enough to stop criminals from posting fake properties and taking over real property-owner accounts. The reported scam workflow involves attackers posing as accommodation owners and sending guests messages demanding additional payments,…

October 21, 2026
Gestohlene Buchungsdaten treiben Kreditkarten-Phishing

Gestohlene Buchungsdaten treiben Kreditkarten-Phishing

Nach einem Angriff auf einen Buchungsdienstleister für Tourismusbetriebe wurden Gästedaten zahlreicher Unterkünfte gestohlen. Die Täter nutzen Namen, Kontaktdaten und Buchungsnummern, um Urlauber mit glaubwürdigen Phishing-Nachrichten zur Herausgabe ihrer Kreditkartendaten zu verleiten.

October 17, 2026
Midnight Blizzard Abuses Hotel Wi‑Fi Captive Portals

Midnight Blizzard Abuses Hotel Wi‑Fi Captive Portals

Microsoft reports a real Midnight Blizzard-linked campaign where attackers tamper with hotel Wi‑Fi captive portals to redirect travelers to phishing and fake update pages. The goal is to steal credentials or trick users into installing malware, which can follow employees back into corporate…

October 8, 2026
Fake Guest Complaints Deliver Hotel RAT Malware

Fake Guest Complaints Deliver Hotel RAT Malware

Cofense tracked real email campaigns targeting hotels with fake guest complaints, reviews, and inquiries. The emails push staff to click a link and open what looks like a photo or video, but it leads to a disguised Windows shortcut (LNK) that installs remote-access malware. The malware hides its…

October 7, 2026
Vishing Help-Desk Scams Bypass MFA at Scale

Vishing Help-Desk Scams Bypass MFA at Scale

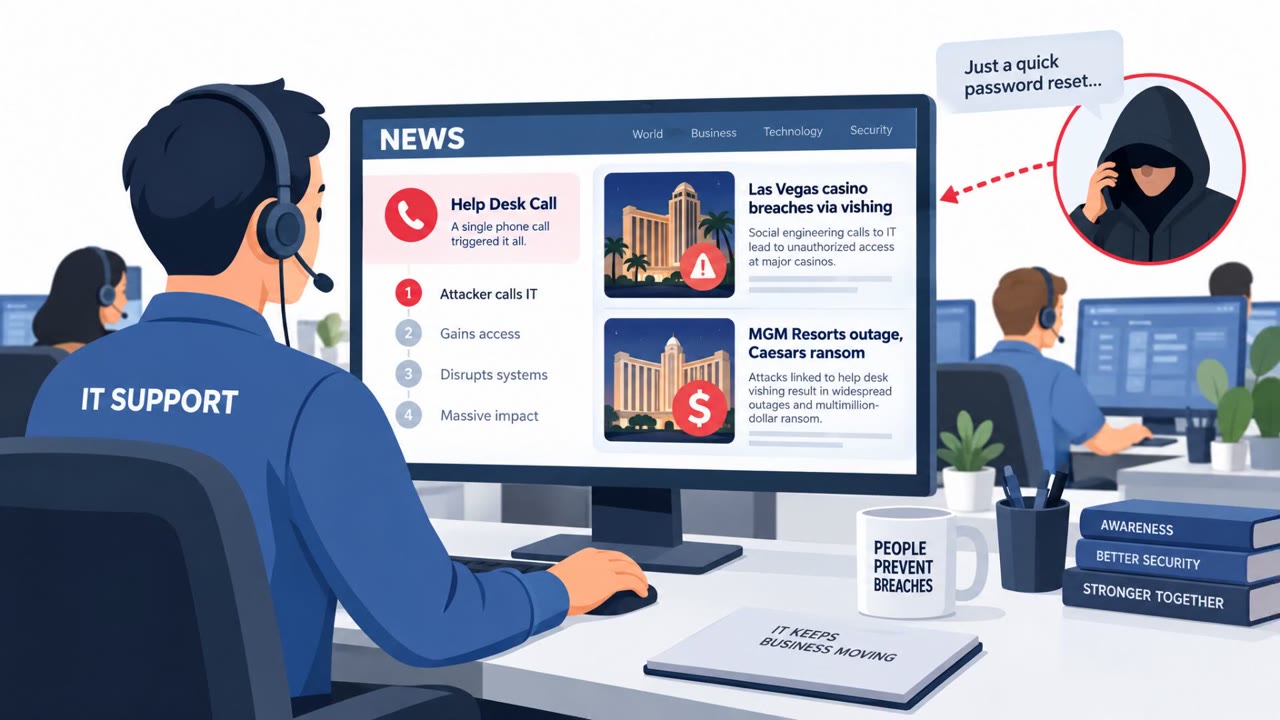
The article highlights real-world voice-phishing attacks where criminals impersonated employees to persuade help desks to reset passwords or approve Microsoft Entra authentication steps, effectively bypassing MFA. It cites major incidents affecting Las Vegas casinos (including MGM Resorts and…

October 6, 2026
Star Blizzard Uses Fake Invites to Install Backdoor

Star Blizzard Uses Fake Invites to Install Backdoor

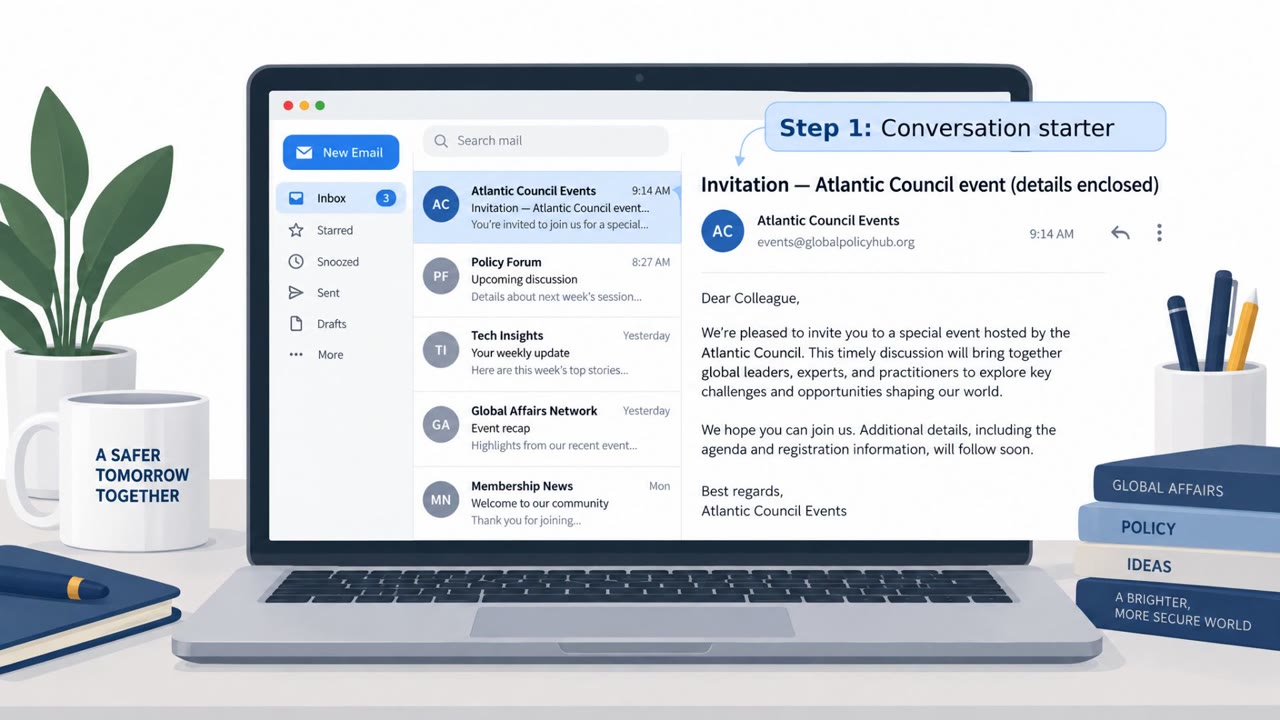
Microsoft reports Russia-linked Star Blizzard sent fake event invitations and other business notices to trick targets into opening disguised files that install a Windows backdoor. The campaigns targeted Ukraine-linked people and organizations and hit 100+ organizations, mainly in the U.S. and U.K.,…

September 29, 2026
Star Blizzard Scales Phishing With “RedFlick”

Star Blizzard Scales Phishing With “RedFlick”

Microsoft reports that the Russian state-linked actor Star Blizzard ran large-scale phishing campaigns in 2026 that use convincing lures like tax notices, fines, and “closed-door” event invitations. After a victim replies, the attacker sends a password-protected ZIP/RAR attachment that triggers a…

September 29, 2026
AI Search Results Turn Into Phishing Traps

AI Search Results Turn Into Phishing Traps

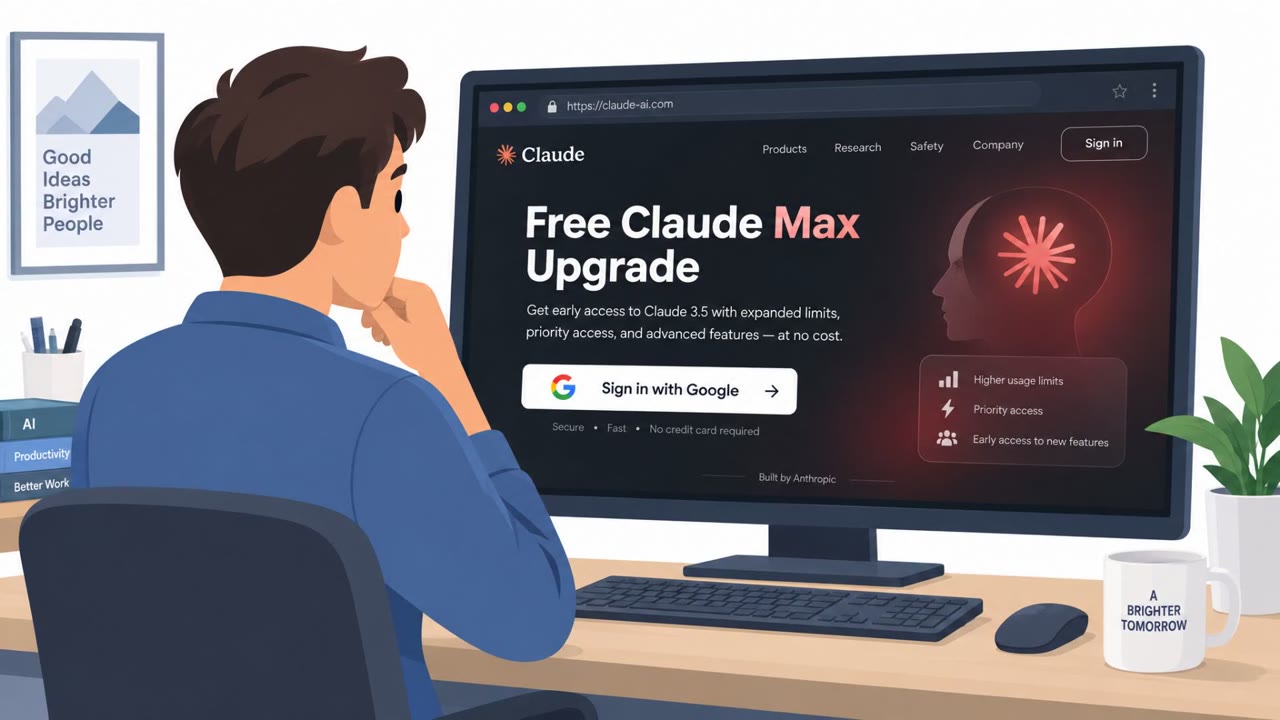
This bulletin describes multiple real-world scams where attackers make fake pages and messages look like routine, trusted experiences (search answers, Google login pop-ups, “giveaways,” and official-sounding calls). Examples include a fake Claude Max giveaway using a convincing fake Google sign-in…

September 24, 2026
Fake IT Support on Teams Enables Full Takeover

Fake IT Support on Teams Enables Full Takeover

Microsoft describes multiple real-world campaigns where attackers use trusted business workflows to trick people into granting access. One campaign impersonates IT support in Microsoft Teams to get remote control of a device, then spreads across the enterprise. Another campaign targets travelers on…

September 17, 2026
Russian Hackers Used AI to Evolve Phishing & Malware

Russian Hackers Used AI to Evolve Phishing & Malware

Anthropic says it disrupted a Russian state-linked campaign that used Claude to continuously rebuild malware when security tools detected it. The group (GTG-20006, linked to Midnight Blizzard/APT29) ran phishing and other human-targeted schemes, including device-code token theft against Microsoft…

September 11, 2026
Fake CAPTCHA “Fix” Tricks Users Into Running Malware

Fake CAPTCHA “Fix” Tricks Users Into Running Malware

Multiple real-world intrusions used a ClickFix-style lure where victims visiting compromised websites saw fake CAPTCHA prompts and were tricked into running a command themselves. Separately, attackers also abused the legitimate, signed Node.js runtime (node.exe) to run malicious JavaScript while…

September 3, 2026
Azure Employee Directories Dumped via Stolen Access

Azure Employee Directories Dumped via Stolen Access

A threat actor called “TheHatman” claims they stole and posted large internal employee directories from multiple Fortune 500 companies’ Microsoft Azure tenants. Hudson Rock says the leaked samples look like real Azure directory exports, but the exact way the attacker got in is still unclear. One…

August 18, 2026
BlackFile Vishing Poses as IT Support to Extort Firms

BlackFile Vishing Poses as IT Support to Extort Firms

Researchers say the BlackFile extortion group is actively targeting large financial and other organizations using voice-phishing calls where attackers impersonate IT support to get initial access. Victims are then pressured with multimillion-dollar extortion demands and, in some cases, escalations…

August 17, 2026
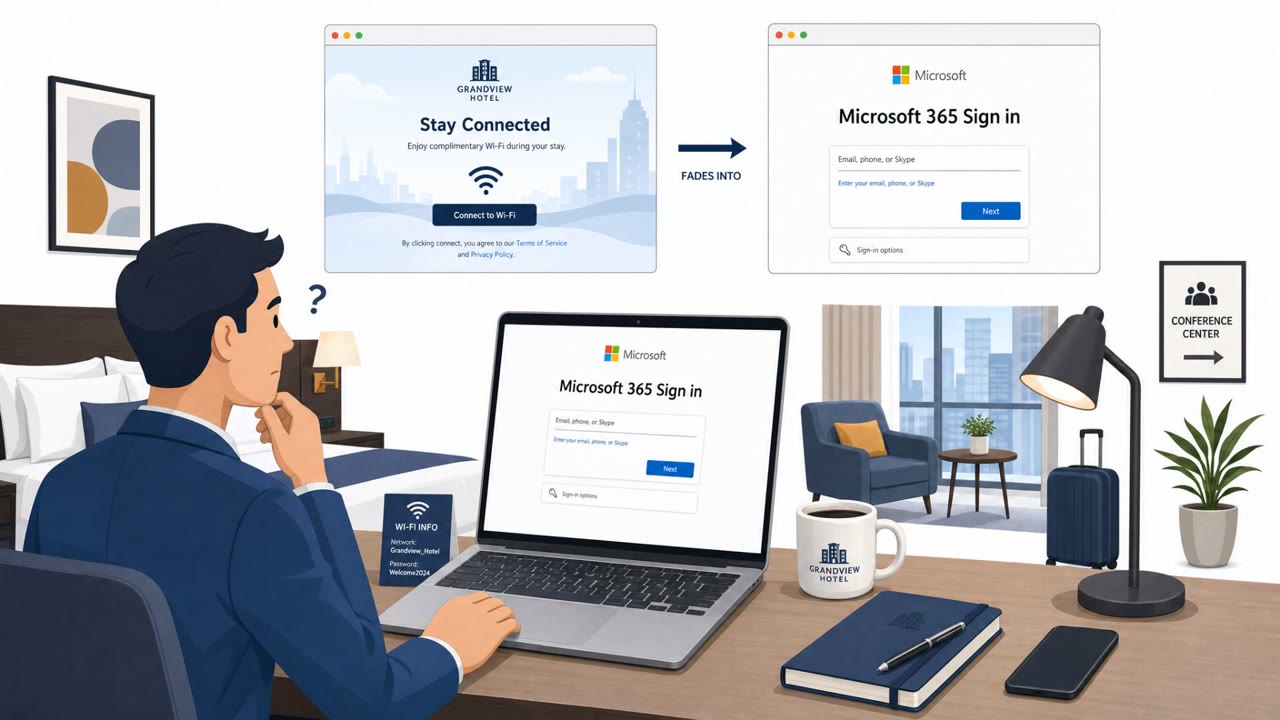
Public Wi‑Fi DNS Hijacks Steal Microsoft 365 Logins

Public Wi‑Fi DNS Hijacks Steal Microsoft 365 Logins

Attackers are compromising public Wi‑Fi equipment (such as in hotels and conference centers) and changing DNS settings so victims are silently redirected to look‑alike login pages. The goal is to capture usernames and passwords, including Microsoft 365 credentials, when users try to sign in.

August 17, 2026
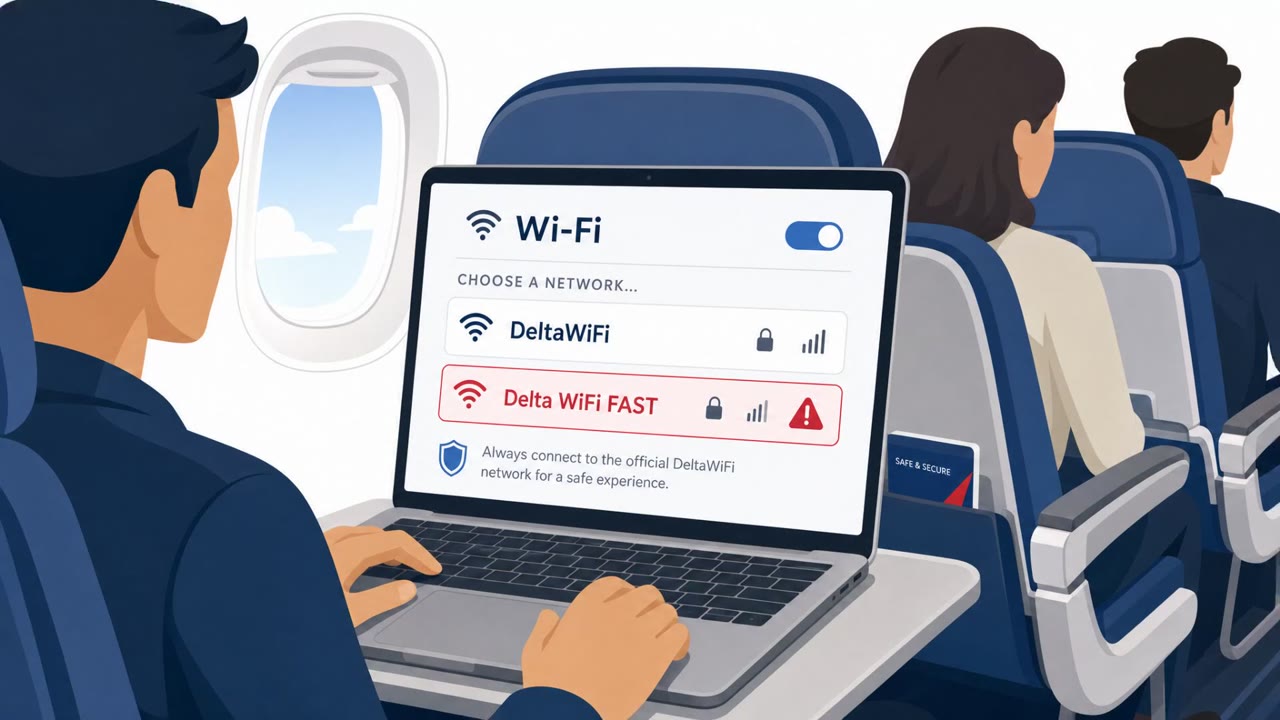
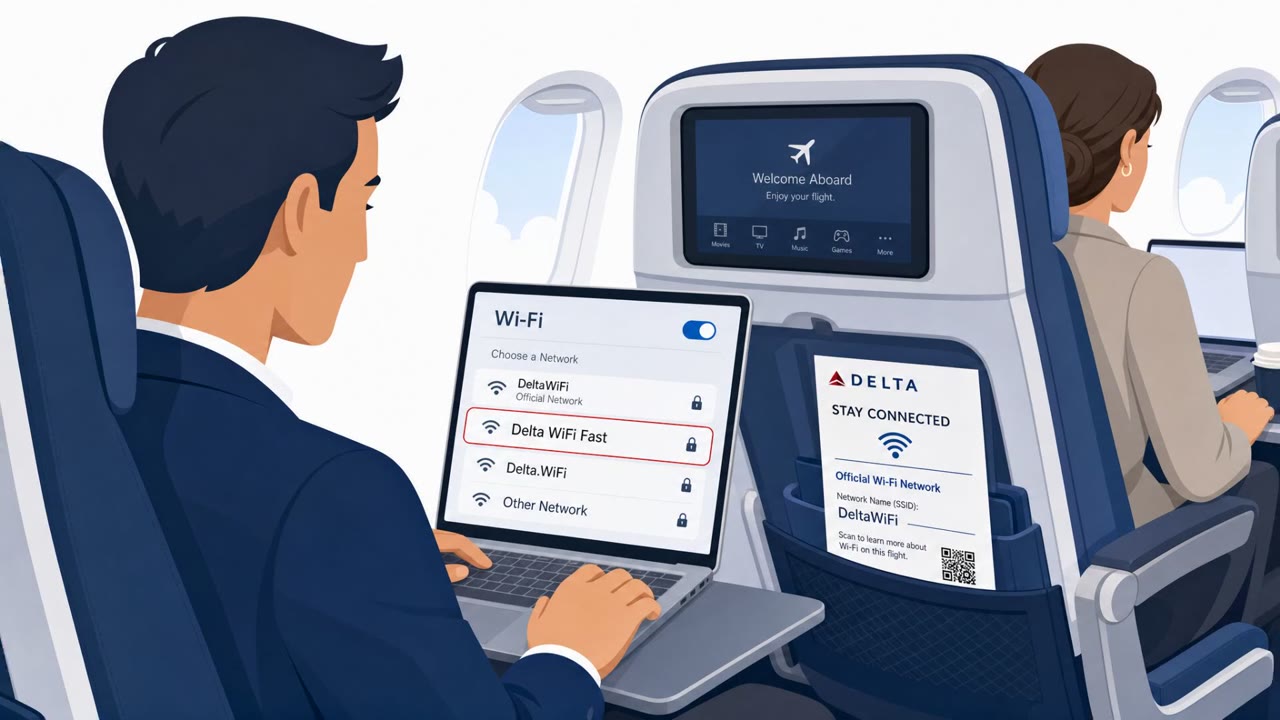
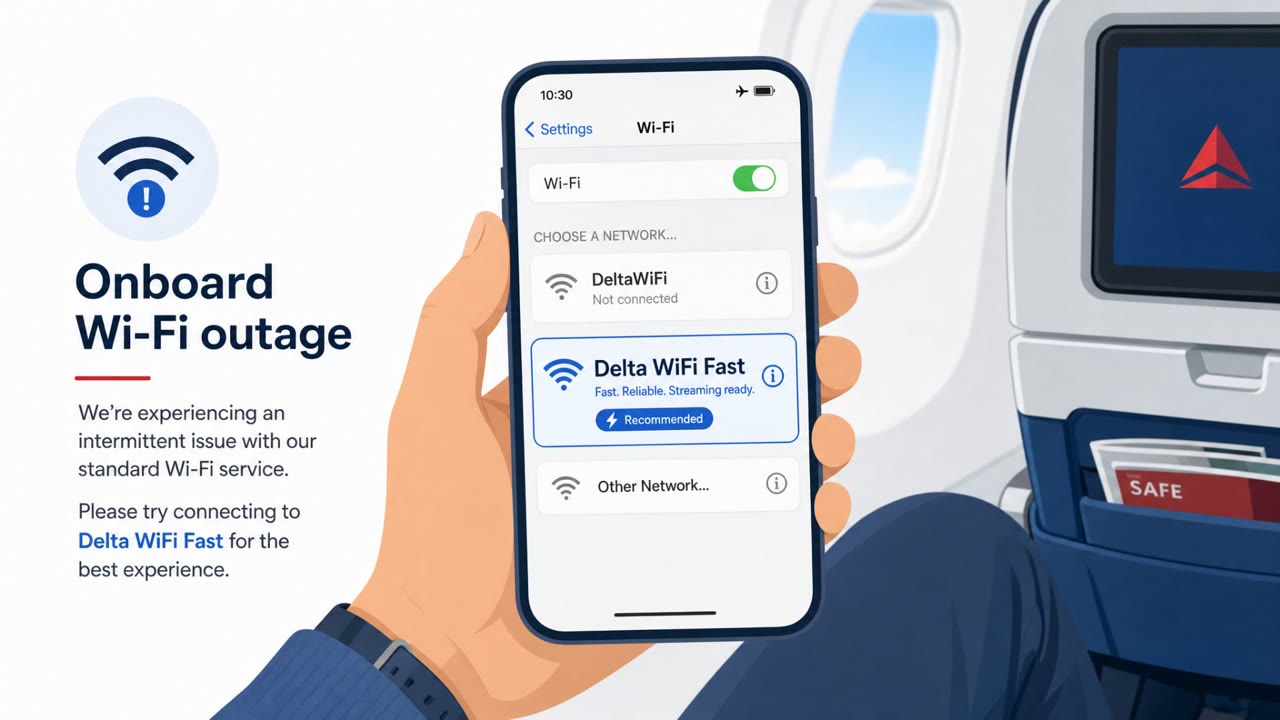
Fake “Delta WiFi FAST” Tricked Flyers

Fake “Delta WiFi FAST” Tricked Flyers

A passenger on a Delta flight allegedly set up a look‑alike Wi‑Fi network (“Delta WiFi FAST”) and tried to disrupt the real onboard Wi‑Fi so other passengers would join the fake hotspot. The goal was likely to push users to a login page and capture credentials (e.g., Google or Facebook). This is a…

August 14, 2026
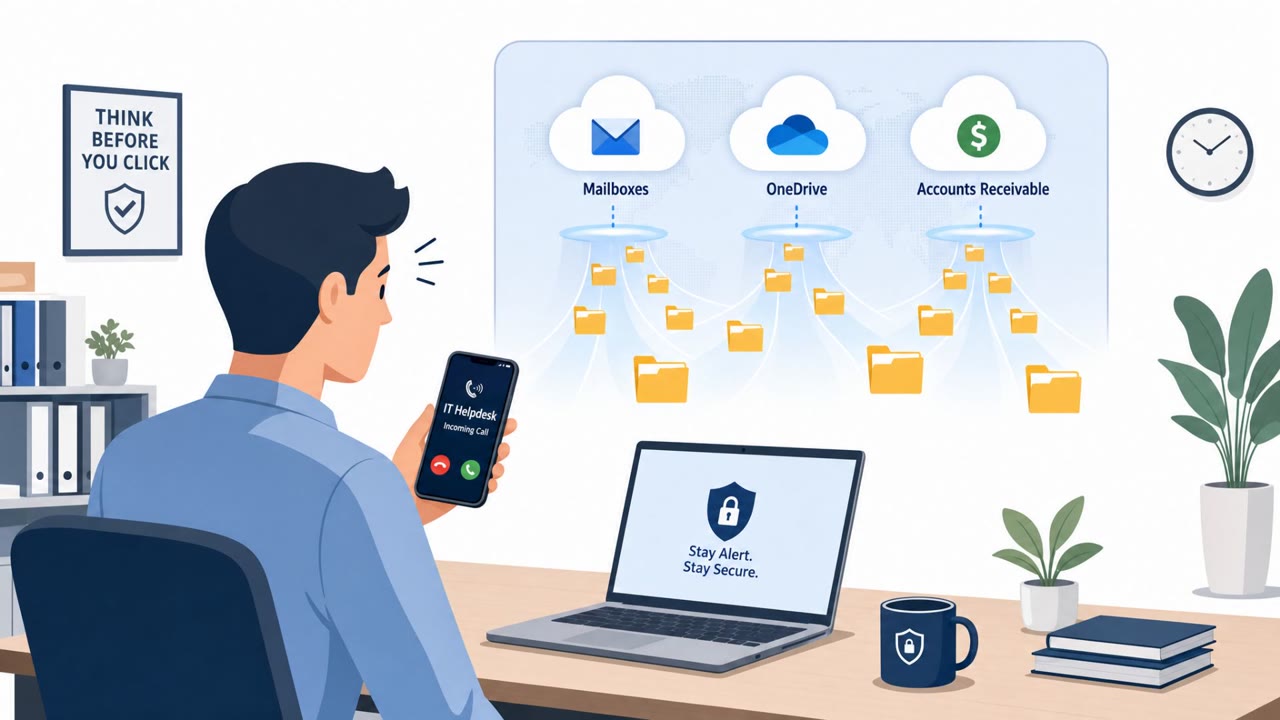
Helix Extortion Hit Uber Freight via Helpdesk Vishing

Helix Extortion Hit Uber Freight via Helpdesk Vishing

Uber Freight is investigating unauthorized access after the Helix extortion group claimed it stole nearly one million files from company cloud and email repositories. Google-linked research says the broader cluster (UNC6671) commonly gets in by calling employees and posing as IT helpdesk staff…

August 12, 2026
Fake “Delta WiFi Fast” Hit Passengers After DEF CON

Fake “Delta WiFi Fast” Hit Passengers After DEF CON

A passenger on a Delta flight allegedly set up a look‑alike in‑flight Wi‑Fi network (“Delta WiFi Fast”) to trick other passengers into connecting. Reports say the fake hotspot led to a phishing page intended to steal personal credentials, including Google login data. Delta confirmed the incident…

August 12, 2026
Rogue “Delta WiFi Fast” Network Disrupts Flight

Rogue “Delta WiFi Fast” Network Disrupts Flight

Delta is investigating an onboard incident where an unauthorized Wi‑Fi network appeared on a flight and the crew shut off Wi‑Fi for about 30 minutes. Reports say a rogue network named “Delta WiFi Fast” may have been used to trick passengers into connecting and potentially entering credentials into…

August 11, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo