Recent Manufacturing Cyber Attacks

Page 2 of 7
Silent Lynx Used Gov Emails to Lure Targets

Silent Lynx Used Gov Emails to Lure Targets

Researchers say the Kazakhstan-linked group “Silent Lynx” has run real espionage campaigns across Central Asia, targeting government bodies and energy organizations. The reported entry method relied heavily on spear‑phishing sent from compromised government email accounts, sometimes using trusted…

October 15, 2026
One-Click Link Triggers Teamcenter XSS Attack

One-Click Link Triggers Teamcenter XSS Attack

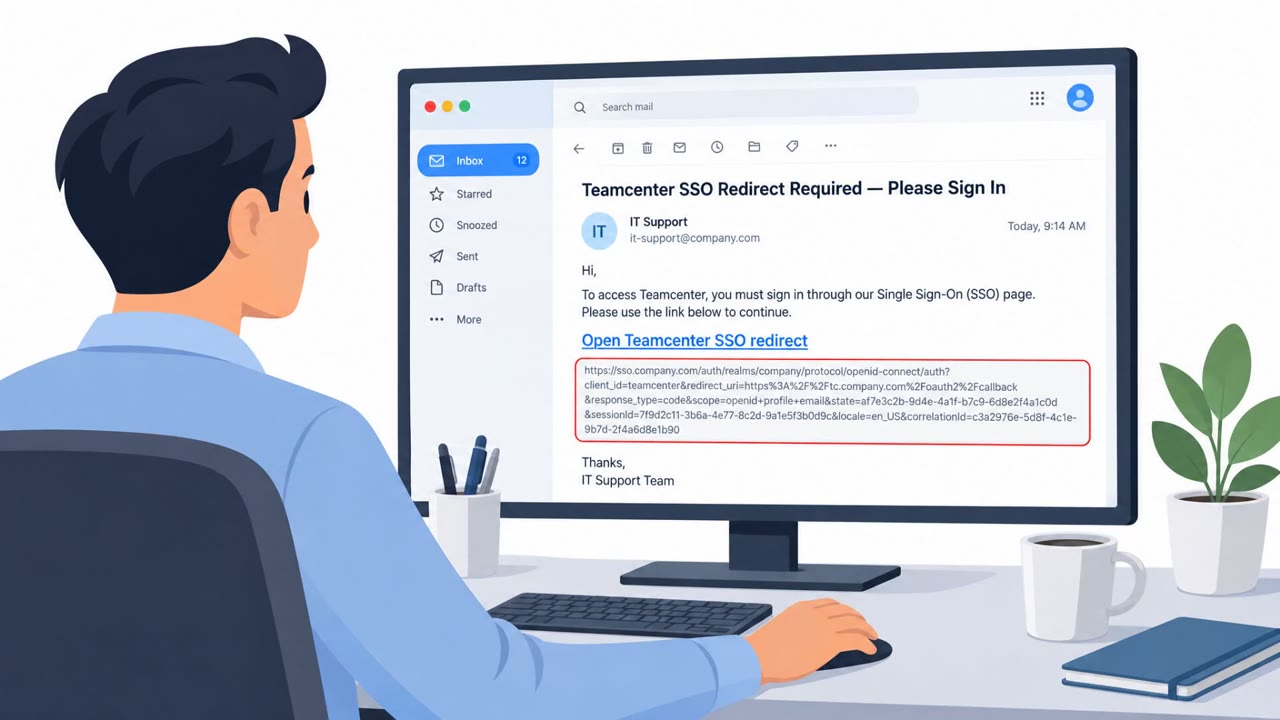
A security assessment found that a single crafted link could run attacker-controlled JavaScript in the browser of a logged-in Siemens Teamcenter user (CVE-2026-58113). Because Teamcenter’s login redirect page auto-submits a form on load, simply opening the link (e.g., from a phishing email or chat)…

October 15, 2026
NK “Laptop Farms” Infiltrate US Remote Jobs

NK “Laptop Farms” Infiltrate US Remote Jobs

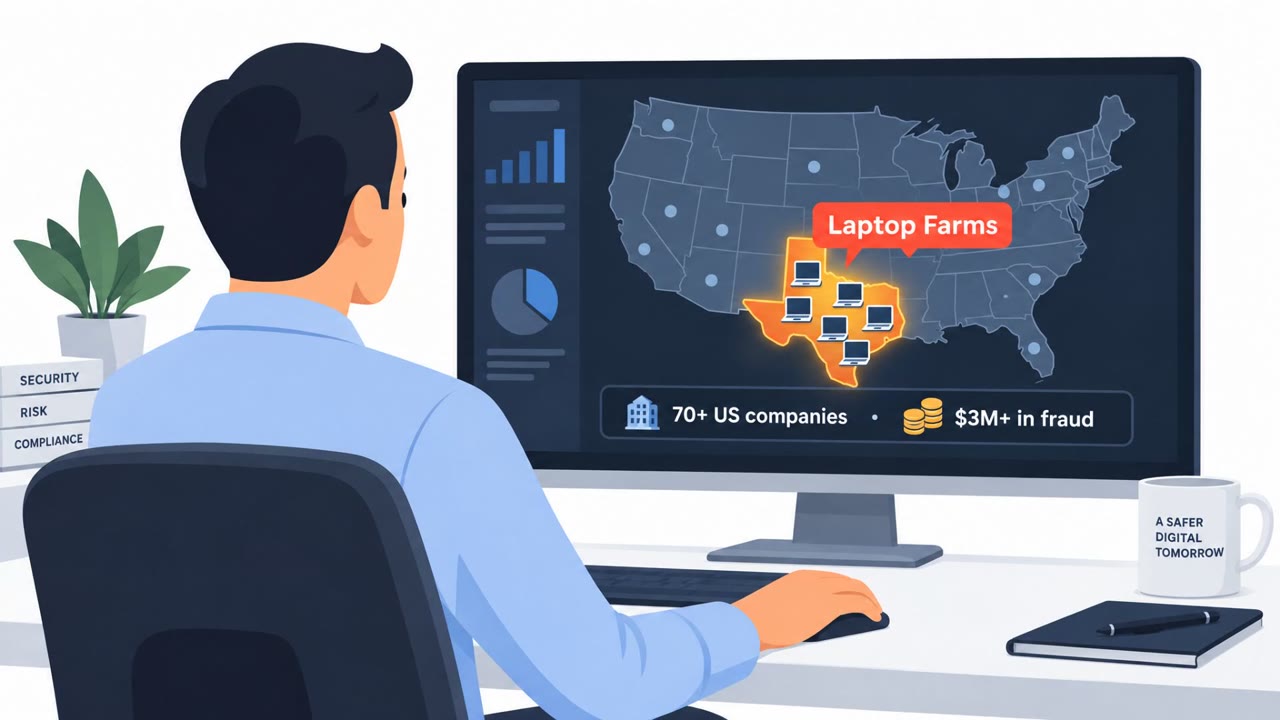
US authorities say North Korean operatives used stolen and fake identities to get hired into remote roles at more than 70 US companies, then operated company laptops from inside the US using “laptop farms.” Americans allegedly helped by receiving employer-issued laptops, keeping them online, and…

October 14, 2026
North Korean Fake IT Workers Ran US Laptop Farms

North Korean Fake IT Workers Ran US Laptop Farms

US authorities arrested two Americans accused of helping North Korean “fake IT workers” get hired remotely at US companies and route company laptops into US-based “laptop farms.” The scheme used stolen or fake identities and location-masking tools so overseas workers could appear to be working from…

October 14, 2026
MATCHBOIL Spearphish Tricks Users Into Running Script

MATCHBOIL Spearphish Tricks Users Into Running Script

ESET reports that Russia-aligned group UAC-0099 is using spearphishing emails with malicious links to deliver a downloader called MATCHBOIL. The attack relies on tricking a person into manually running a downloaded VBScript, which then fetches and installs further malware and sets up persistence…

October 9, 2026
Fake Court Summons Phish Drops MatchBoil Malware

Fake Court Summons Phish Drops MatchBoil Malware

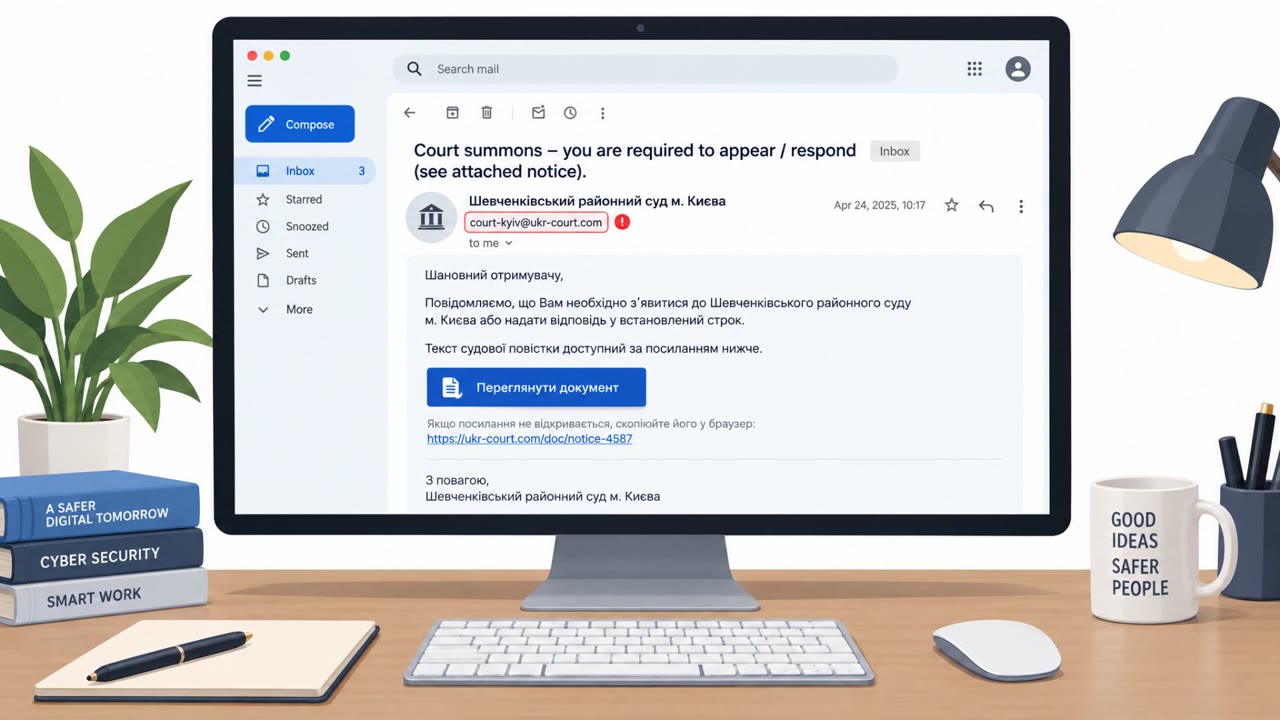
Researchers say the Russia-aligned group UAC-0099 has been phishing Ukrainian organizations with malicious links that install a data-harvesting malware called MatchBoil. The emails have included lures like fake Ukrainian court summonses, and clicking the link leads to downloading an archive that…

October 8, 2026
Wazza Phishkit Hides Adobe Device-Code Login Trap

Wazza Phishkit Hides Adobe Device-Code Login Trap

Researchers at ANY.RUN report a real-world phishing operation (“Wazza”) targeting banking, government, and manufacturing in the U.S., Europe, and Australia. The campaign uses a multi-step redirect and validation chain to filter out bots and only then shows an Adobe-branded “Device Code” sign-in…

October 8, 2026
MATCHBOIL Spearphish Drops Ukraine Spy Backdoor

MATCHBOIL Spearphish Drops Ukraine Spy Backdoor

ESET reports that the Russia-aligned group UAC-0099 used spear‑phishing emails to trick victims in Ukraine into clicking a link that downloads a malicious archive. The infection chain runs a script that installs MATCHBOIL, which then downloads a spying backdoor (MATCHWOK) and sets persistence so it…

October 8, 2026
Phishers Beat MFA With Real-Time Proxy Kits

Phishers Beat MFA With Real-Time Proxy Kits

The article describes a real phishing investigation where attackers used an adversary-in-the-middle (AiTM) proxy to relay a genuine Microsoft sign-in and steal both credentials and the victim’s live session token. The lure came from a legitimately compromised corporate mailbox, making common email…

October 8, 2026
Nikkei Email Account Hijacked to Send 9,000 Phish

Nikkei Email Account Hijacked to Send 9,000 Phish

Nikkei said an attacker took over an employee’s Microsoft 365 email account and used it to send about 9,000 phishing emails to people who had previously communicated with Nikkei staff, including journalistic sources. The messages contained links leading to malicious websites, creating a high-trust…

October 5, 2026
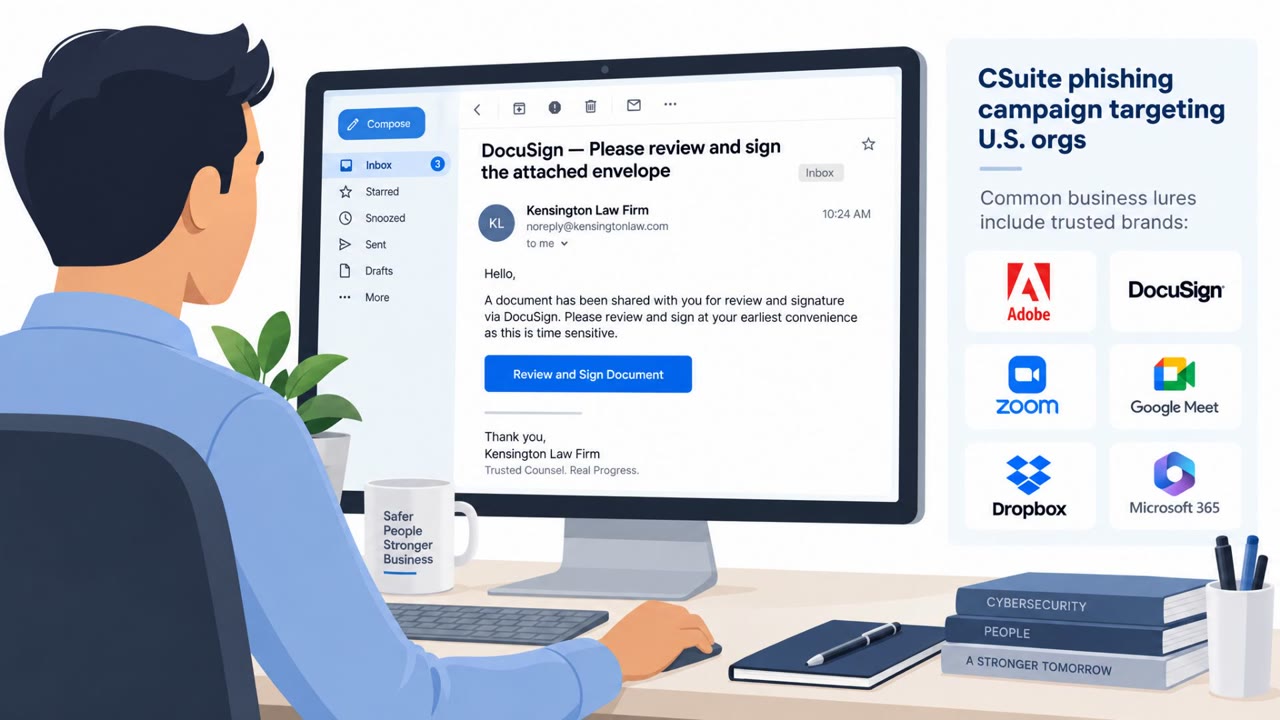
CSuite Phish Steals M365 Sessions, Installs RMM

CSuite Phish Steals M365 Sessions, Installs RMM

Researchers observed a real phishing campaign (“CSuite”) heavily targeting U.S. organizations using familiar business-themed lures (DocuSign, Adobe, Zoom/Meet, Dropbox, Microsoft 365). After a victim engages, the attackers either steal Microsoft 365 sessions (enabling mailbox takeover and fraud) or…

September 30, 2026
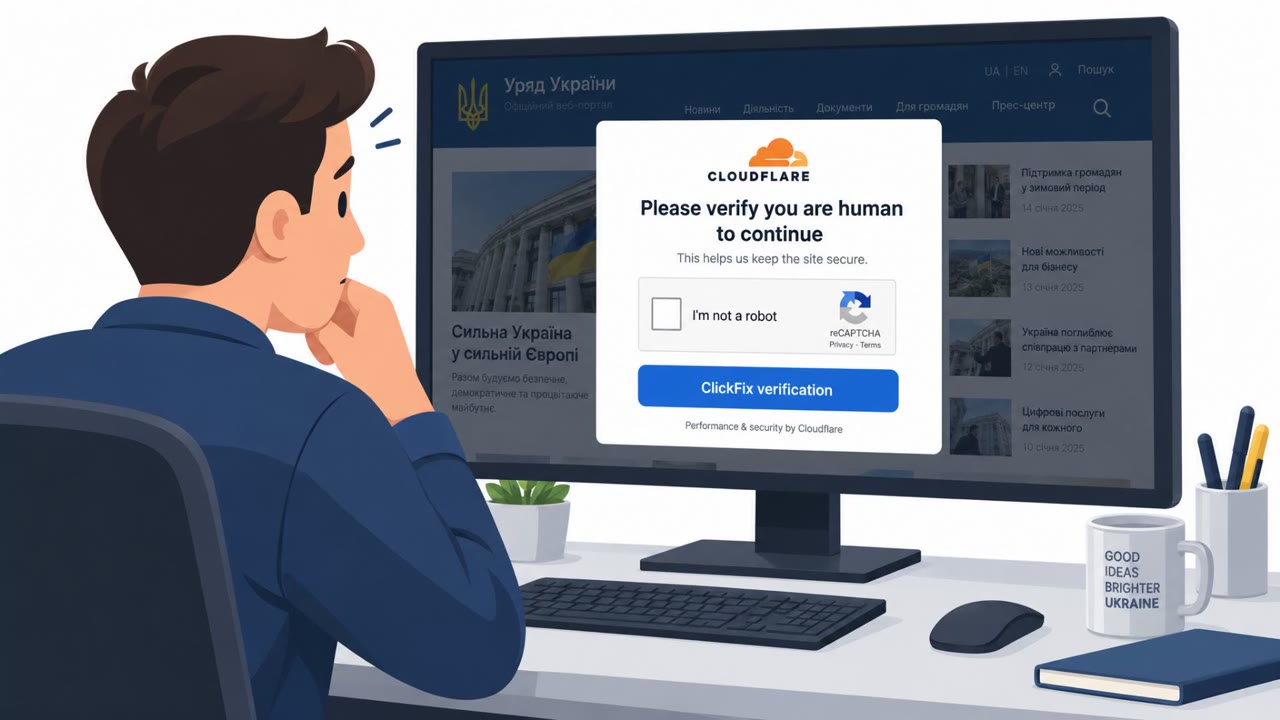
Fake CAPTCHA ‘ClickFix’ Spreads Lunex Stealer

Fake CAPTCHA ‘ClickFix’ Spreads Lunex Stealer

Attackers compromised legitimate Ukrainian websites and showed visitors a fake CAPTCHA/Cloudflare-style “verification” prompt to trick them into installing malware. The infection chain drops Lunex (aka Psychedelic Stealer), which disables security monitoring using a vulnerable AMD driver and then…

September 26, 2026
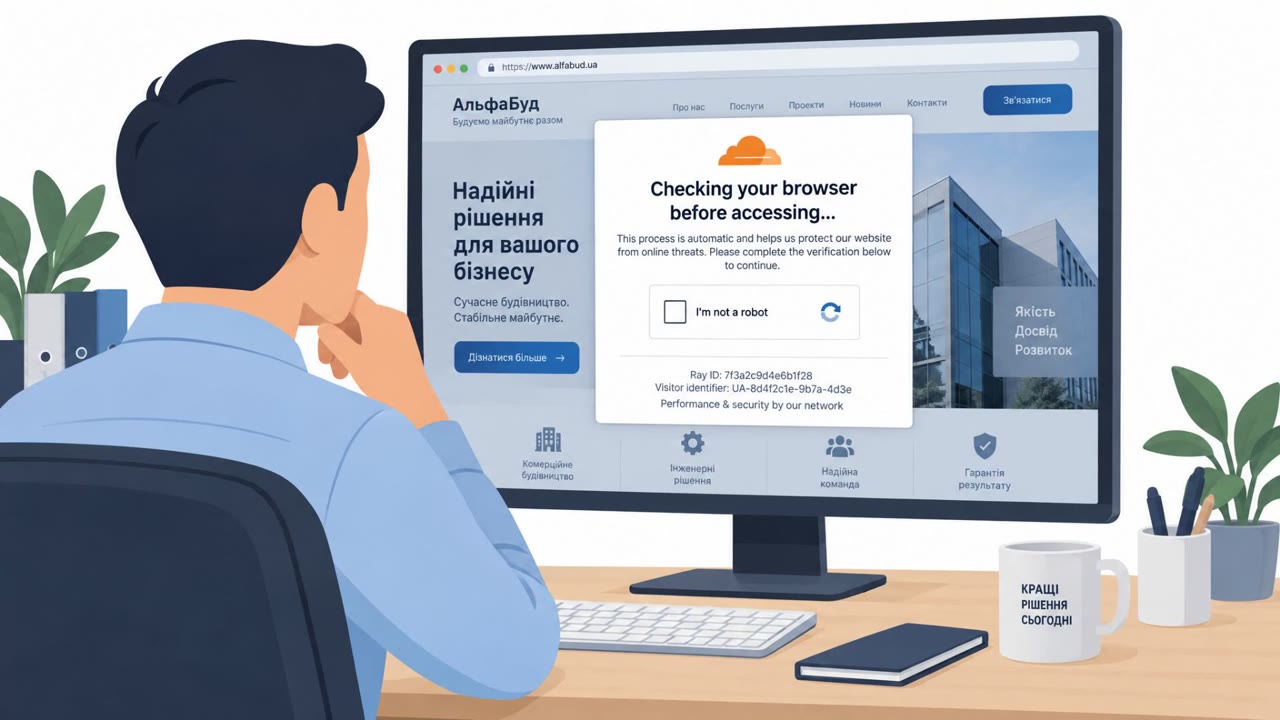
Fake Cloudflare CAPTCHA Pushes MSI Malware

Fake Cloudflare CAPTCHA Pushes MSI Malware

Attackers compromised real Ukrainian business websites and showed visitors a fake Cloudflare verification page. The lure tricks people into running a Windows Installer command (via Windows+R), which installs “Psychedelic Stealer” to steal saved browser passwords and cryptocurrency wallet data.

September 25, 2026
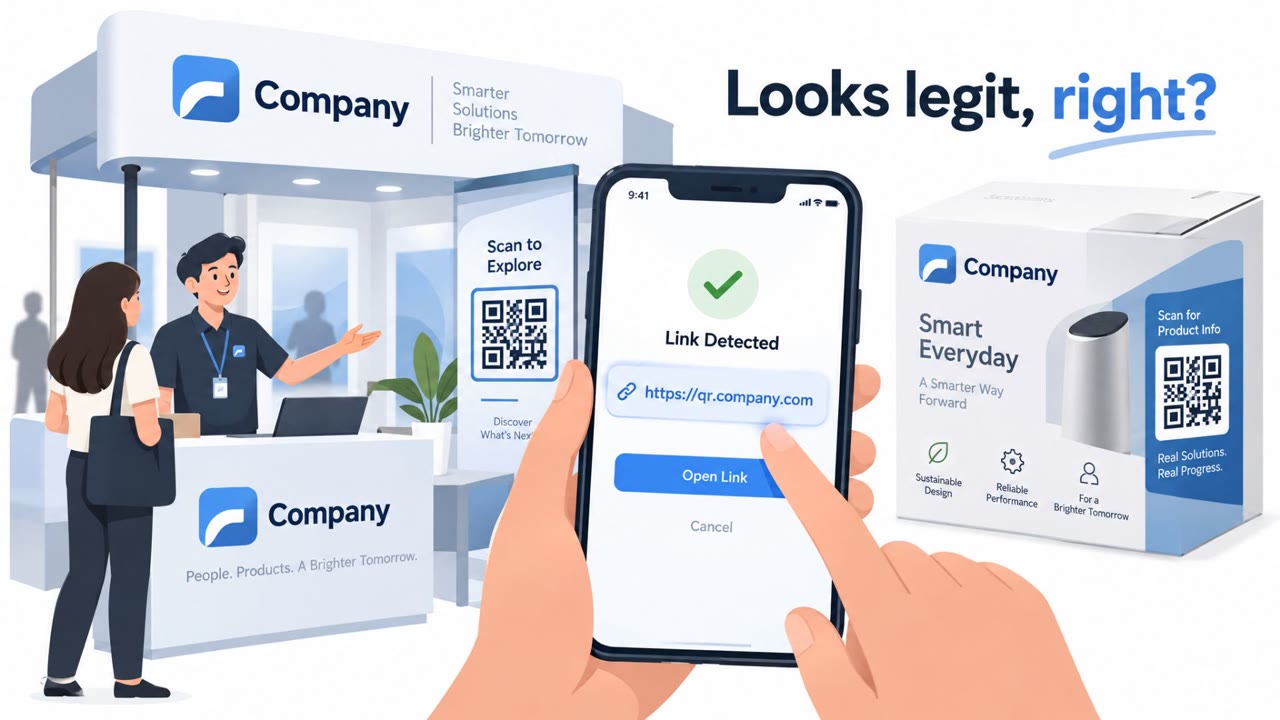
QR Codes Hijacked via Abandoned Branded Domains

QR Codes Hijacked via Abandoned Branded Domains

A researcher demonstrated that attackers can take over a company’s branded QR-code subdomain (e.g., qr.company.com) if the company stops using a QR vendor but forgets to remove the DNS record. Anyone scanning a legitimate printed QR code can then be redirected to an attacker-controlled website,…

September 25, 2026
60,000 Fake LinkedIn Jobs Used to Scam Applicants

60,000 Fake LinkedIn Jobs Used to Scam Applicants

Scammers are using realistic LinkedIn recruiter profiles and even verified company pages to post fake jobs that push people to off-platform sites or email addresses. The scams aim to take money (e.g., paid “resume help”) or collect sensitive personal data like driver’s licenses or Social Security…

September 23, 2026
Fake CEOs on LinkedIn Fuel IP & Data Theft

Fake CEOs on LinkedIn Fuel IP & Data Theft

A CSC report describes real-world scams where criminals impersonate executives and brands online to steal personal or payment information. Examples include fake CEOs contacting people on LinkedIn with bogus job offers, and lookalike “FIFA” domains used for fake ticket sales, travel offers, and…

September 22, 2026
NGOs Lured via Donation Form Into Chrome 0-Day Chain

NGOs Lured via Donation Form Into Chrome 0-Day Chain

Researchers reported two China-linked groups targeting NGOs with spear-phishing that led victims through a legitimate U.S. university website before redirecting them to attacker infrastructure. The attackers used a chained Chrome/Windows exploit to take control, then deployed different payloads,…

September 15, 2026
Trezor Users Hit by Phish via Brevo Breach

Trezor Users Hit by Phish via Brevo Breach

Attackers broke into Brevo, the email platform Trezor uses for newsletters, and sent a phishing “security warning” from Trezor’s real mailing system. The email claimed a serious hardware issue could expose wallet recovery seeds and pushed people to a malicious site/app that asked for a wallet…

September 14, 2026
Passkey Helpdesk Scam Hijacks Microsoft Accounts

Passkey Helpdesk Scam Hijacks Microsoft Accounts

Microsoft described two real-world campaigns: an invoice fraud blast impersonating executives to trick finance teams into ACH payments, and a passkey-themed helpdesk scam that steals or bypasses authentication to take over Microsoft cloud accounts. In the second campaign, victims are called or…

September 13, 2026
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

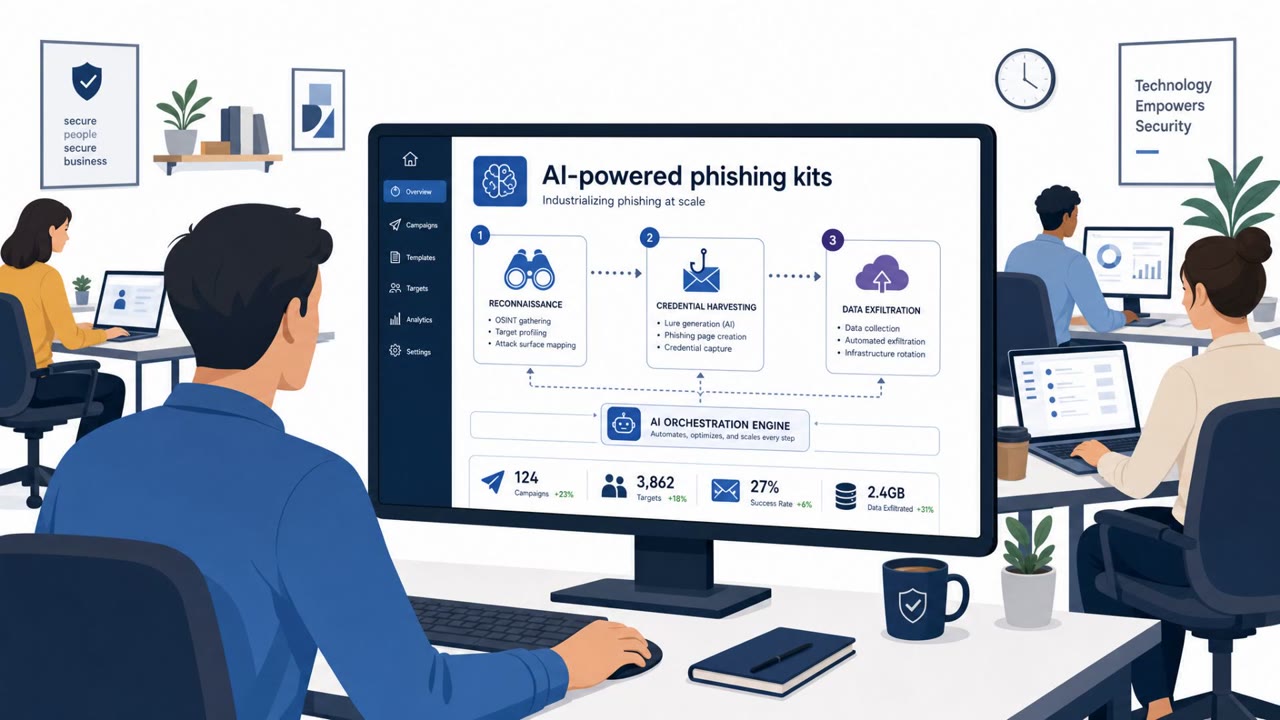
Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo