Recent Manufacturing Cyber Attacks

Page 4 of 7
Fake Recruiters Steal Enterprise Logins on Mobile

Fake Recruiters Steal Enterprise Logins on Mobile

A real “fake recruiter” phishing campaign (tracked as RecruitTrap) is targeting employees’ corporate credentials, especially on mobile devices. The scam uses lookalike recruitment domains and full-screen fake login pages that hide browser cues, and it rejects personal email addresses to focus on…

August 25, 2026
Notion Alerts Used to Steal Microsoft Tokens

Notion Alerts Used to Steal Microsoft Tokens

A financially motivated actor (“Doubloon Dredger”) abused legitimate Notion sharing notifications to trick employees into opening a PDF and completing a Microsoft device-code login flow. This allowed the attacker to harvest authentication tokens and access victim accounts without needing the…

August 24, 2026
CEO Fraud and Fake Invoices Fuel BEC Losses

CEO Fraud and Fake Invoices Fuel BEC Losses

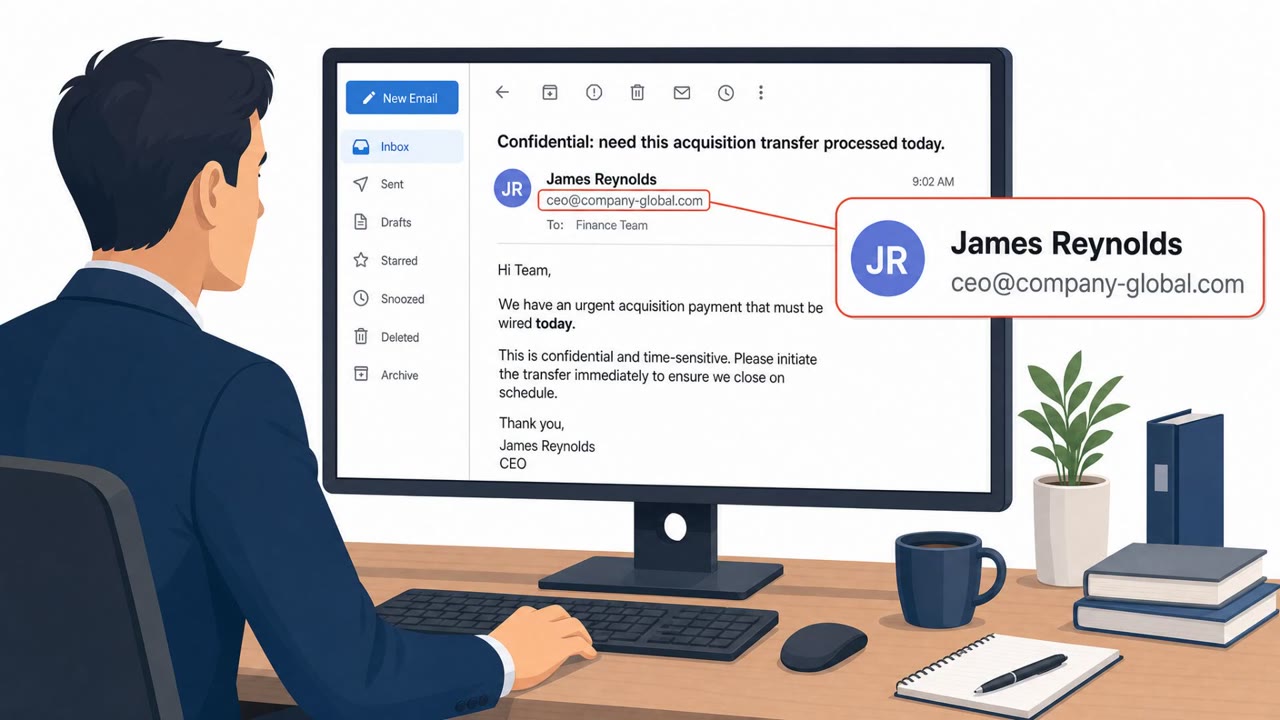
This article explains how business email compromise (BEC) scams work when attackers impersonate executives or suppliers to request urgent wire transfers, bank-detail changes, or credentials, often without malware or links. It cites real, high-loss cases (including Google/Facebook and aerospace…

August 21, 2026
Fake Conferences Fuel OAuth and WhatsApp Phish

Fake Conferences Fuel OAuth and WhatsApp Phish

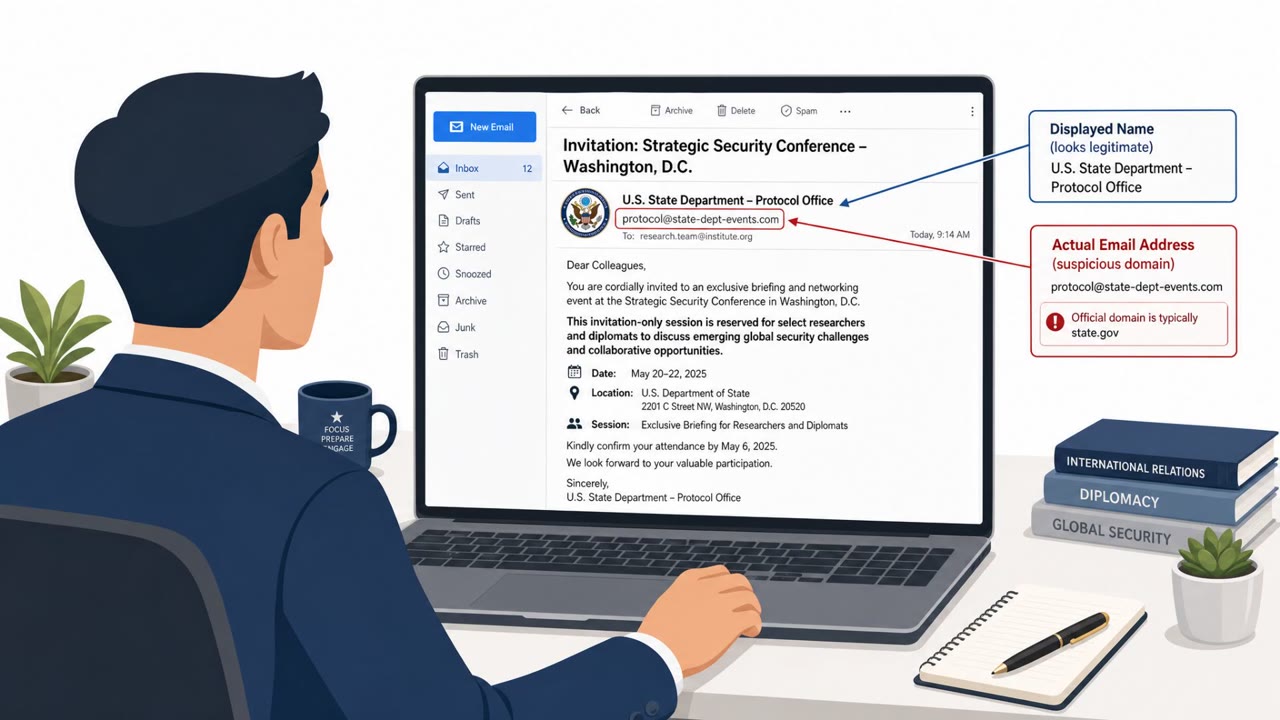
Google tracked three suspected Russia-linked groups running targeted phishing that abuses real login and authentication features (app passwords, OAuth, and device codes) to get into accounts. The lures often look like legitimate conference or diplomatic invitations, and some campaigns spoof…

August 21, 2026
Russian Spy Phish Uses Legit OAuth Logins

Russian Spy Phish Uses Legit OAuth Logins

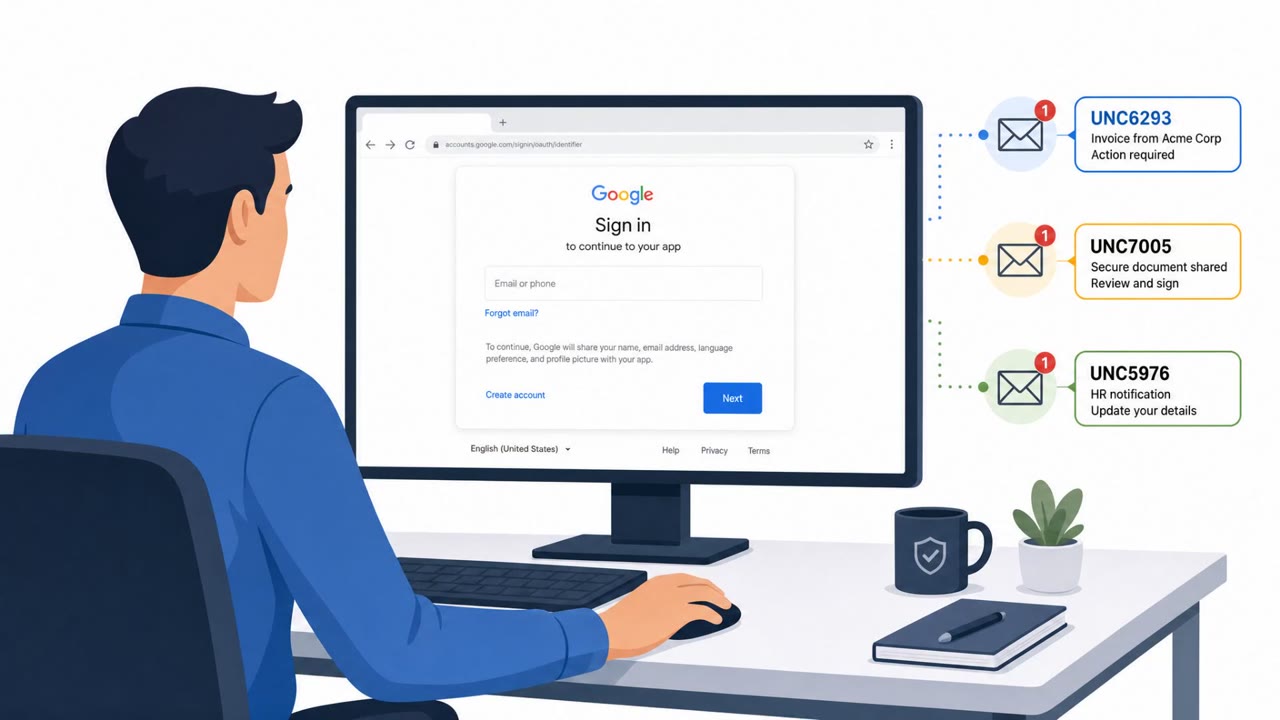
Google says three suspected Russian cyber-espionage groups are running highly targeted phishing campaigns against people in government, academia, defense, and think tanks in the US and Europe. A key theme is abusing legitimate Google/Microsoft OAuth login flows so the outreach looks real, tricking…

August 21, 2026
Russian Clusters Hijack Accounts via OAuth & WhatsApp

Russian Clusters Hijack Accounts via OAuth & WhatsApp

Google says multiple suspected Russia-linked espionage clusters targeted academics, government, and defense-related personnel by abusing legitimate sign-in features instead of using obvious fake login pages. The campaigns used realistic lures (file sharing, conference invites, and “secure WhatsApp”…

August 20, 2026
Russian Clusters Abuse Login Flows to Steal Accounts

Russian Clusters Abuse Login Flows to Steal Accounts

Google says three suspected Russian espionage clusters are targeting academics, think tanks, diplomats, and related nonprofit staff by abusing legitimate login and verification workflows that may not look like “classic phishing.” The campaigns include app-password scams, OAuth/device-code tricks,…

August 20, 2026
Attackers Phish via Teams & Slack, Not Email

Attackers Phish via Teams & Slack, Not Email

Research and incident examples show attackers increasingly using trusted collaboration tools (like Microsoft Teams and Slack) to impersonate IT/support or known community members, then push victims to phishing sites, approve MFA prompts, or run malicious files. Because messages come through…

August 20, 2026
APT Groups Lure Targets Into Fake Zoom/Teams Meets

APT Groups Lure Targets Into Fake Zoom/Teams Meets

This threat trend report describes multiple real-world APT campaigns where attackers rely on social engineering and trusted services (Zoom/Teams, Telegram, webmail, GitHub) to steal credentials and access cloud accounts. Notable examples include fake meeting lures to deliver malware, and abuse of…

August 20, 2026
Job Offer & Doc-Link Phishing Drive Real Breaches

Job Offer & Doc-Link Phishing Drive Real Breaches

This weekly threat bulletin describes real incidents where attackers used human manipulation to break in, including social engineering at Levi Strauss and a Microsoft 365 credential-theft phish at defense supplier IEH. It also highlights a Lazarus-linked campaign using fake job offers and…

August 17, 2026
SafePal Breach Spurs Phishing & Fake Support Scams

SafePal Breach Spurs Phishing & Fake Support Scams

SafePal disclosed a breach that exposed order and contact details for nearly 40,000 customers, and warned the stolen data may be used to run targeted phishing and impersonation scams. The company cautioned customers to expect fake support messages, refund offers, and firmware-update requests…

August 17, 2026
“Half-Click” Zimbra Email Attack Steals 90 Days

“Half-Click” Zimbra Email Attack Steals 90 Days

CISA warns a Russian state-sponsored group (“Laundry Bear,” tracked by Microsoft as “Void Blizzard”) is compromising some unpatched Zimbra email accounts when users merely open or preview a specially crafted email. The hidden code can steal passwords, MFA-related tokens, and up to 90 days of…

August 14, 2026
Lazarus “Dream Job” LinkedIn Recruiter Lures

Lazarus “Dream Job” LinkedIn Recruiter Lures

A North Korea-linked threat group used fake recruiter outreach on LinkedIn to target defense and aerospace companies across multiple countries. The victims were tricked into opening a trojanized PDF viewer or a malicious archive, which led to backdoor installation and deeper system compromise.

August 13, 2026
Fake Lockheed Jobs Used to Deliver Lazarus Zero-Day

Fake Lockheed Jobs Used to Deliver Lazarus Zero-Day

Check Point says North Korea’s Lazarus Group targeted defense and aerospace professionals using convincing fake job offers that led victims to download trojanized PDF software. The campaign used a Windows zero-day (now patched as CVE-2026-68820) to gain full control and hide from security tools,…

August 13, 2026
Lazarus Lures Staff With Fake Jobs to Drop Malware

Lazarus Lures Staff With Fake Jobs to Drop Malware

Researchers tied North Korea’s Lazarus Group to a real-world campaign that approaches professionals with convincing fake recruiter outreach and job offers. Victims are tricked into opening a malicious PDF or installing a fake PDF viewer from lookalike websites, which then installs backdoors and can…

August 12, 2026
Helix Extortion Hit Uber Freight via Helpdesk Vishing

Helix Extortion Hit Uber Freight via Helpdesk Vishing

Uber Freight is investigating unauthorized access after the Helix extortion group claimed it stole nearly one million files from company cloud and email repositories. Google-linked research says the broader cluster (UNC6671) commonly gets in by calling employees and posing as IT helpdesk staff…

August 12, 2026
Lazarus Job Offers Led to Windows Zero-Day

Lazarus Job Offers Led to Windows Zero-Day

North Korea’s Lazarus group targeted defense and aerospace staff using fraudulent job offers and fake websites, then deployed malware that pulled down and ran a Windows zero-day exploit. The campaign also used websites impersonating Enveil to distribute a trojanized PDF viewer that delivered a new…

August 12, 2026
Fake Recruiters Target Job Seekers With Malicious PDFs

Fake Recruiters Target Job Seekers With Malicious PDFs

North Korea-linked Lazarus Group ran a “Dream Job” campaign targeting people applying for defense and aerospace jobs by posing as recruiters on LinkedIn and other platforms. Victims were sent malicious PDF files; opening them enabled a backdoor and then an exploit for a Windows zero-day…

August 12, 2026
Freight Scammers Hijack Trucking Identities for AI Gear

Freight Scammers Hijack Trucking Identities for AI Gear

The article describes real cargo theft operations targeting high-value AI data center equipment, including cases where escort vehicles were deliberately disabled so shipments could disappear. It also explains a repeatable fraud workflow where criminals use phishing/social engineering to take over a…

August 12, 2026
BlackFile Crew Vishing Hits PE and Finance Firms

BlackFile Crew Vishing Hits PE and Finance Firms

Google and Reuters report a real vishing-led intrusion campaign tied to the extortion crew behind the retired “BlackFile” brand (tracked as UNC6671). Attackers call employees on personal phones spoofing the corporate IT help desk, push a same-day “passkey/MFA update,” and send them to a look‑alike…

August 12, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo