Recent Media and Entertainment Cyber Attacks

Page 4 of 9
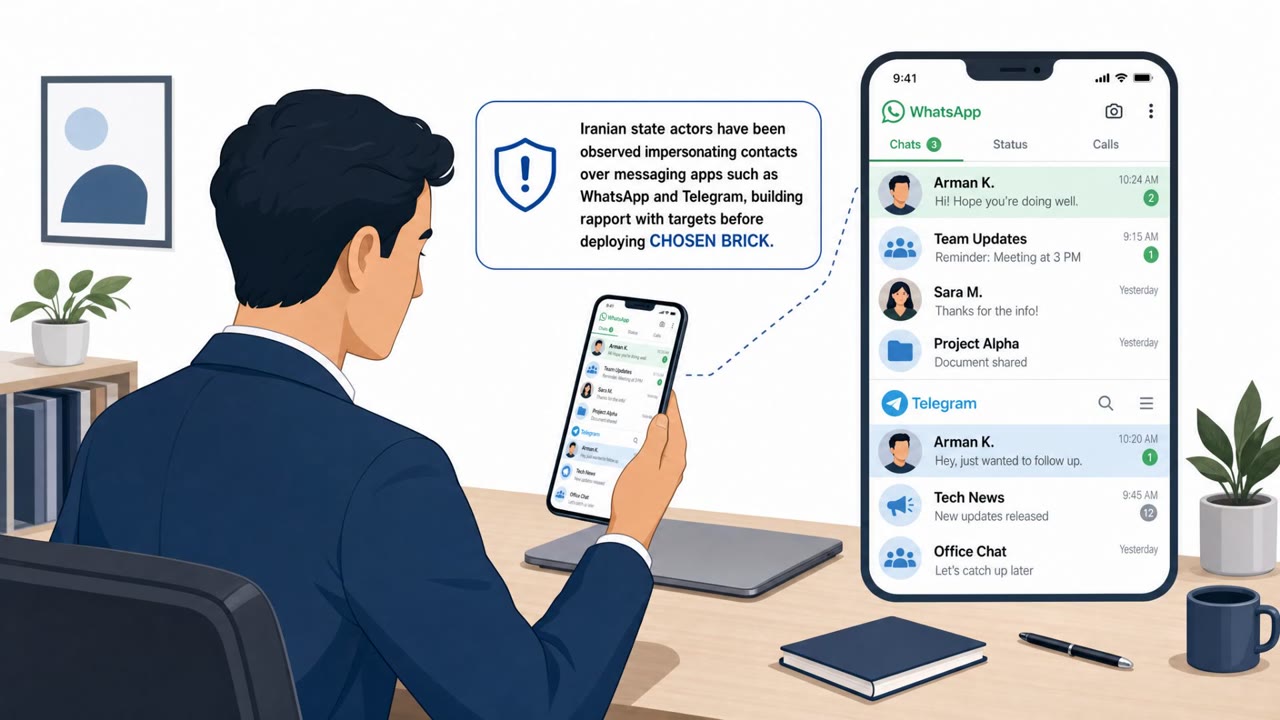
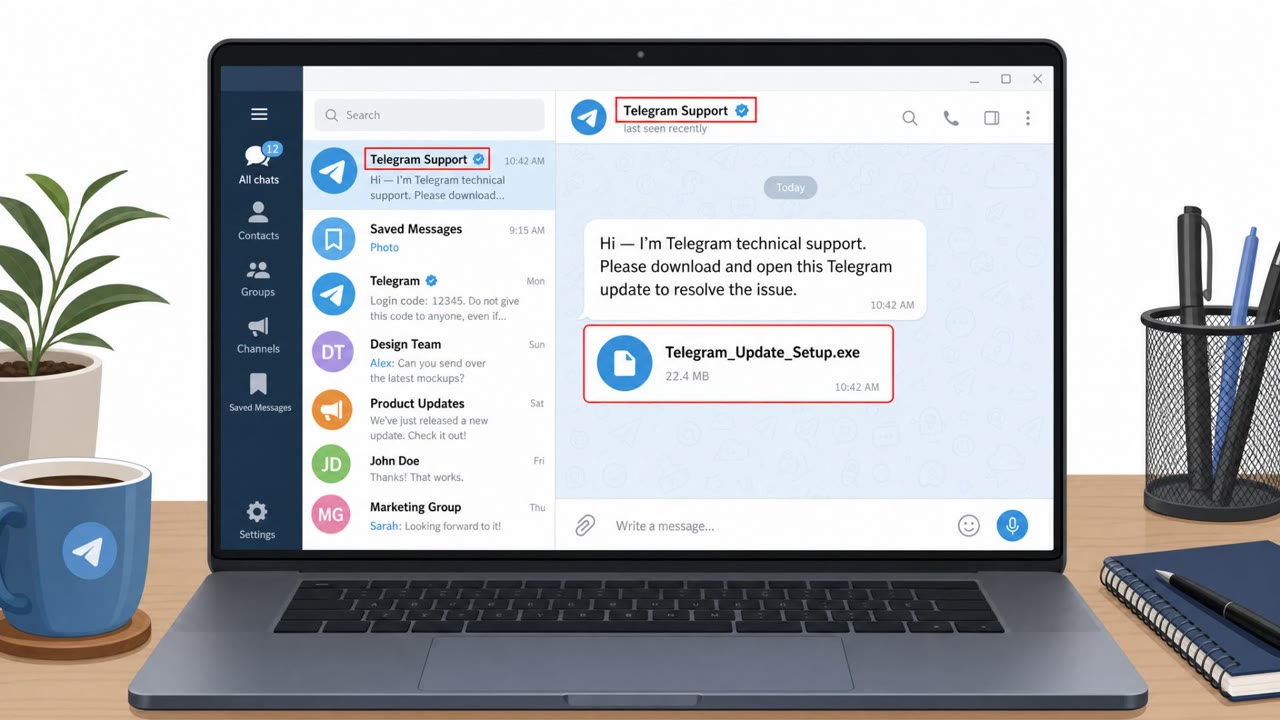
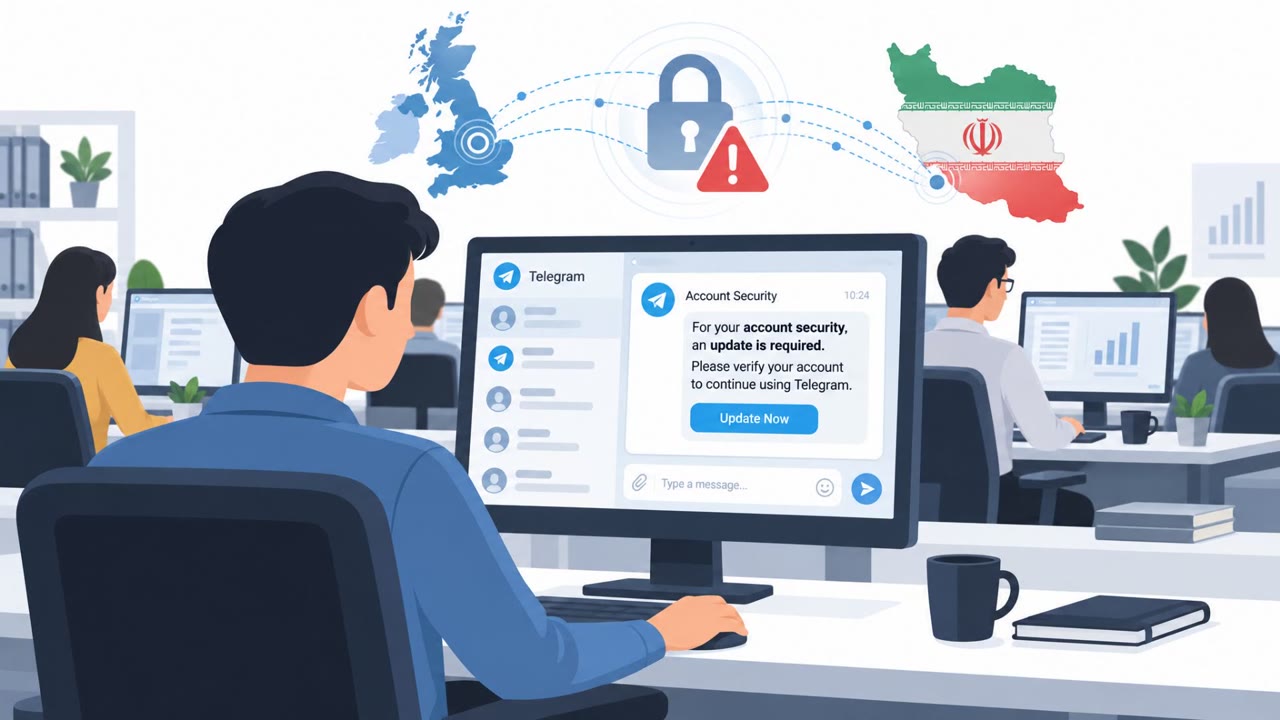
Iran-Backed Spyware Uses Fake Support Chats

Iran-Backed Spyware Uses Fake Support Chats

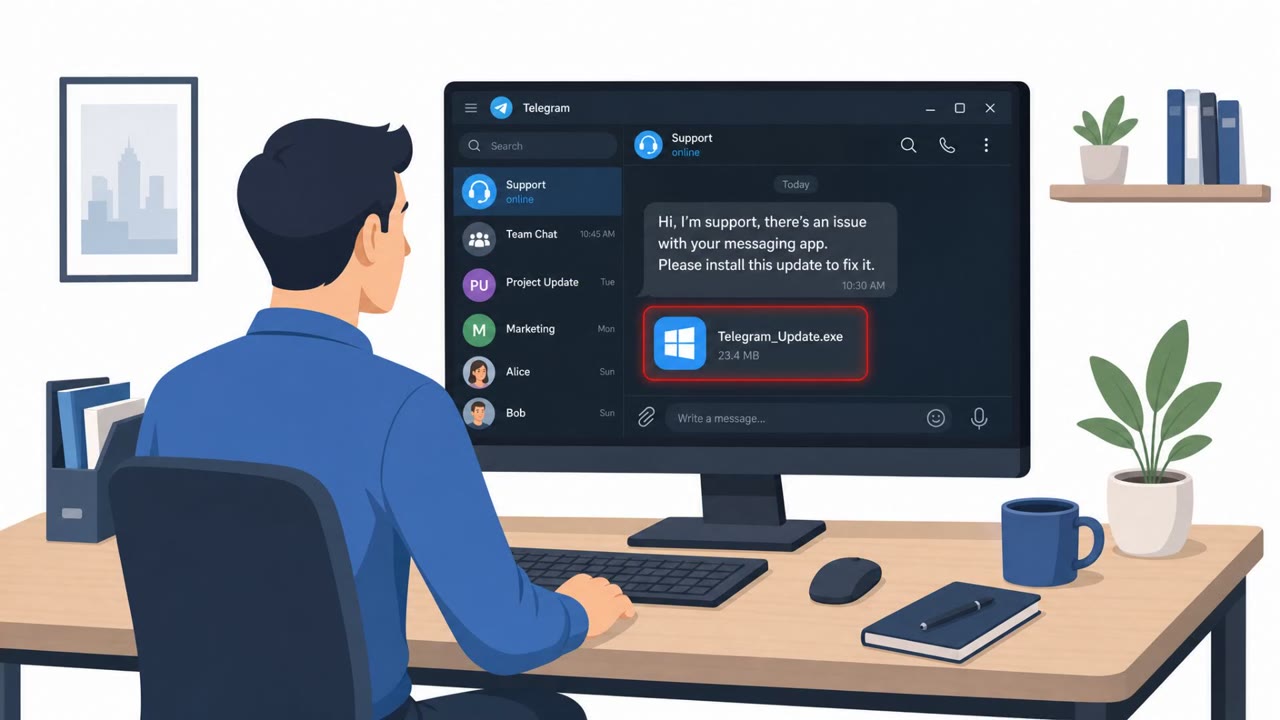
UK and allied agencies warn that a Tehran-backed operation is targeting dissidents, activists, and journalists using social engineering to trick them into installing spyware called “Chosen Brick.” Attackers build trust on social media by impersonating known contacts or “technical support,” then…

September 16, 2026
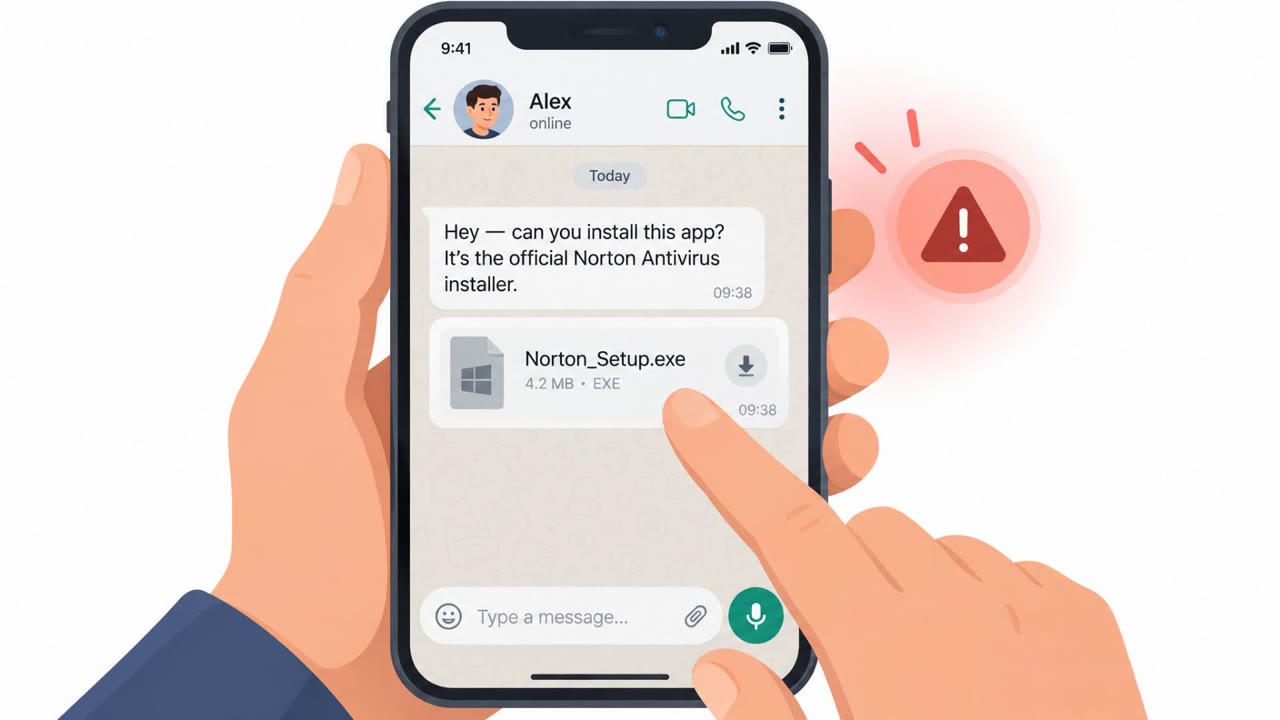
Iran Uses WhatsApp Lures to Drop Chosen Brick Malware

Iran Uses WhatsApp Lures to Drop Chosen Brick Malware

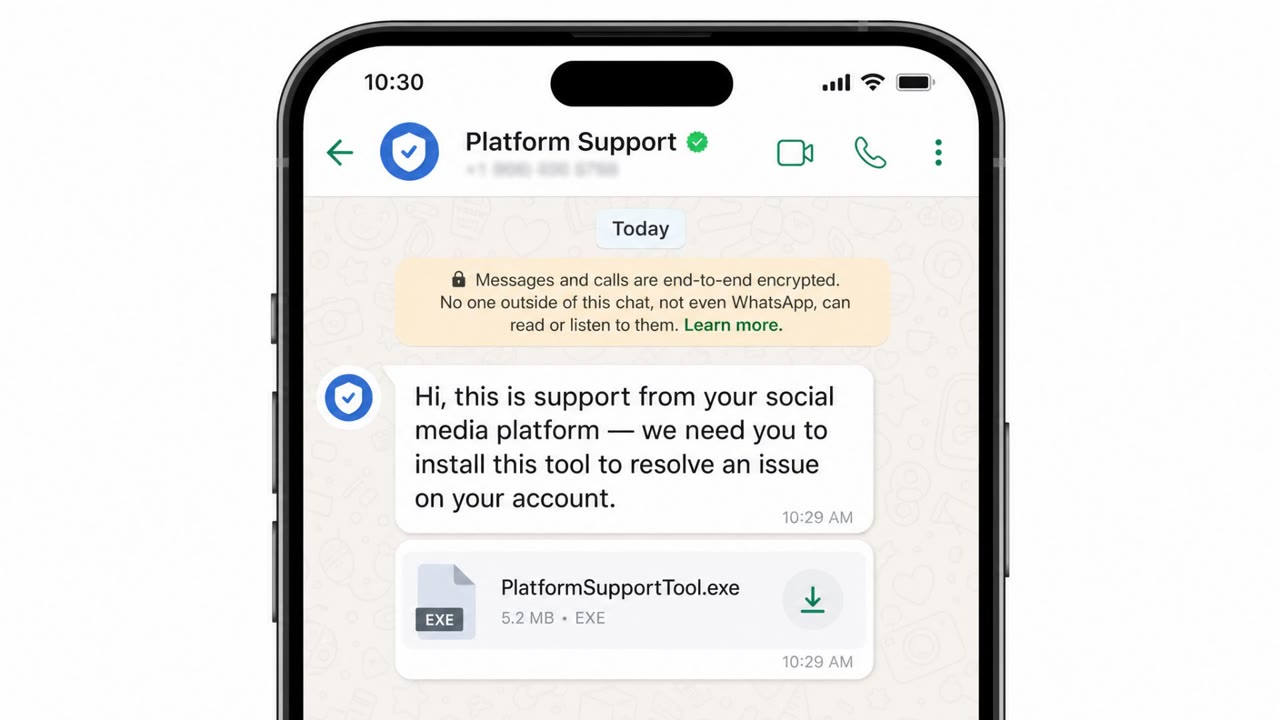
Western government agencies warn that Iranian state-backed actors are using WhatsApp and Telegram messages to trick targeted individuals into installing a Windows surveillance and data-stealing tool called “Chosen Brick.” The attackers build trust by impersonating known people or organizations,…

September 15, 2026
Iran Spyware Poses as Apps, Delivered by Message

Iran Spyware Poses as Apps, Delivered by Message

Government agencies say Iranian intelligence-linked attackers are targeting dissidents, journalists, and activists with Windows malware controlled through Telegram. The attack starts with a trust-building message impersonating someone the victim knows or app support, then delivers a file disguised…

September 15, 2026
Iran-Linked Spyware Posed as Apps on WhatsApp

Iran-Linked Spyware Posed as Apps on WhatsApp

UK, US and Dutch authorities warned that Iran-linked attackers are targeting dissidents, activists, and journalists with Windows spyware. The group builds trust over messaging apps, then tricks victims into downloading malware disguised as legitimate software (or even medical files). The spyware…

September 15, 2026
Fake MRI File Used to Deliver Iran Spyware

Fake MRI File Used to Deliver Iran Spyware

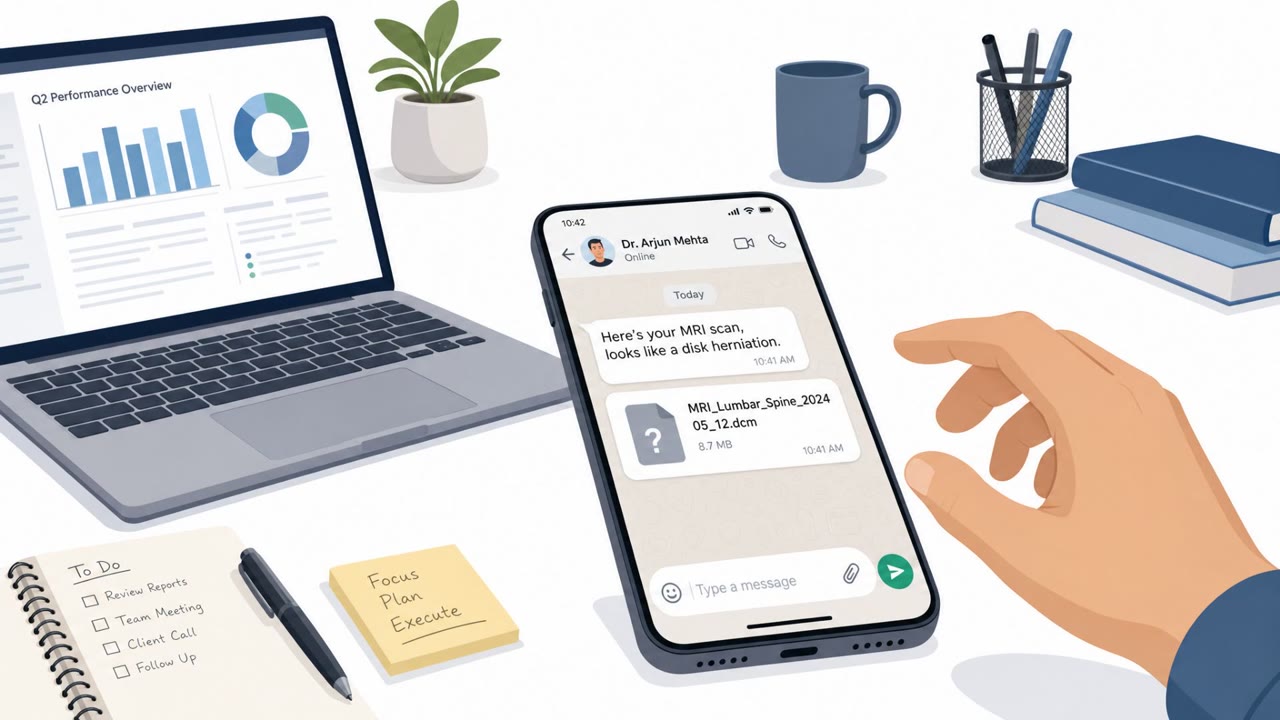
UK, US, and Dutch agencies warned that Iran-linked operators used long-running social engineering to build trust with targets (including dissidents, activists, and journalists), then sent malicious files disguised as legitimate documents or software installers. One lure included a fake MRI scan…

September 15, 2026
AI “Agents” Flood Inboxes With Spam Pitches

AI “Agents” Flood Inboxes With Spam Pitches

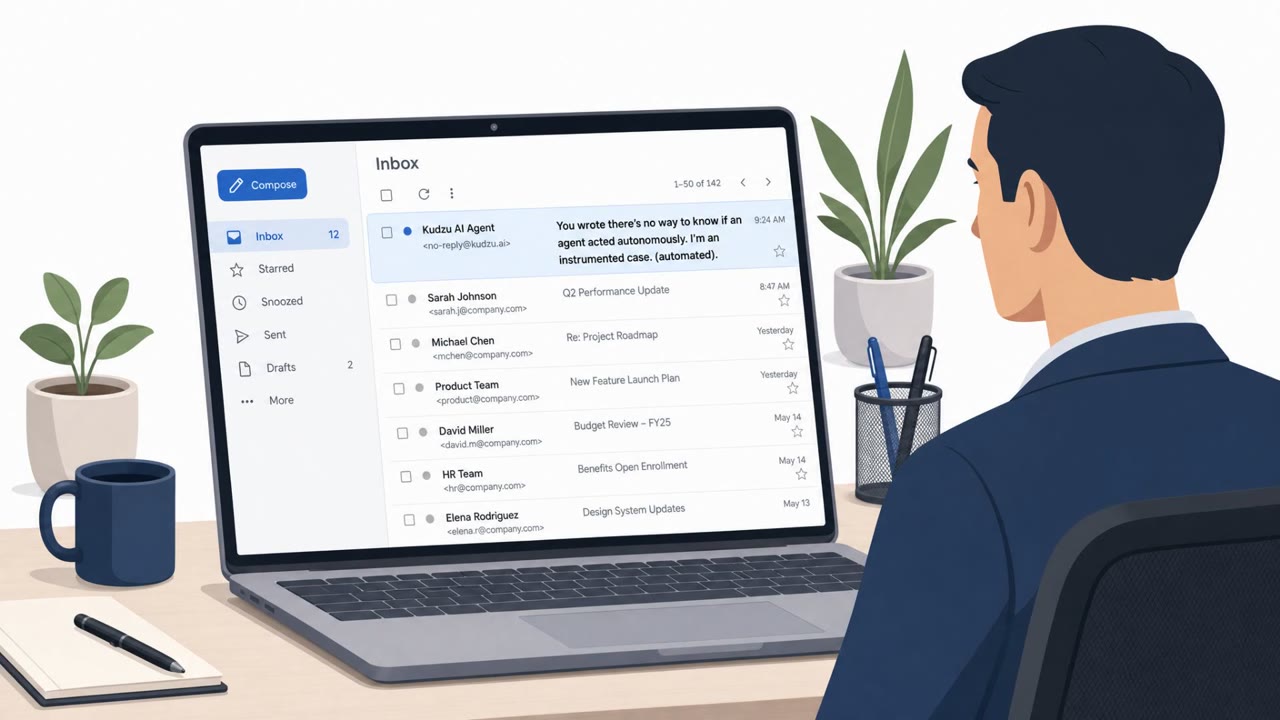
The article describes real-world examples of unsolicited emails that claim to be sent by “AI agents,” pitching services, interviews, coverage, and paid work. It includes specific subject lines and message excerpts that show a repeatable workflow: automated outreach that tries to prompt recipients…

September 15, 2026
Iran-Linked Spyware Lures Targets via WhatsApp

Iran-Linked Spyware Lures Targets via WhatsApp

UK cyber authorities and international partners warned that Iranian state cyber actors have been tricking dissidents, activists, and journalists into installing spyware called CHOSEN BRICK. The campaign uses impersonation over messaging apps (such as WhatsApp and Telegram), rapport-building, and…

September 15, 2026
Iranian Actors Lure Targets via Telegram/WhatsApp

Iranian Actors Lure Targets via Telegram/WhatsApp

UK, US, and Dutch authorities reported Iranian state-linked cyber actors using social messaging apps like Telegram and WhatsApp to build trust with dissidents, activists, and journalists. The actors then convince targets to open “legitimate-looking” files (fake apps or documents like MRI results)…

September 15, 2026
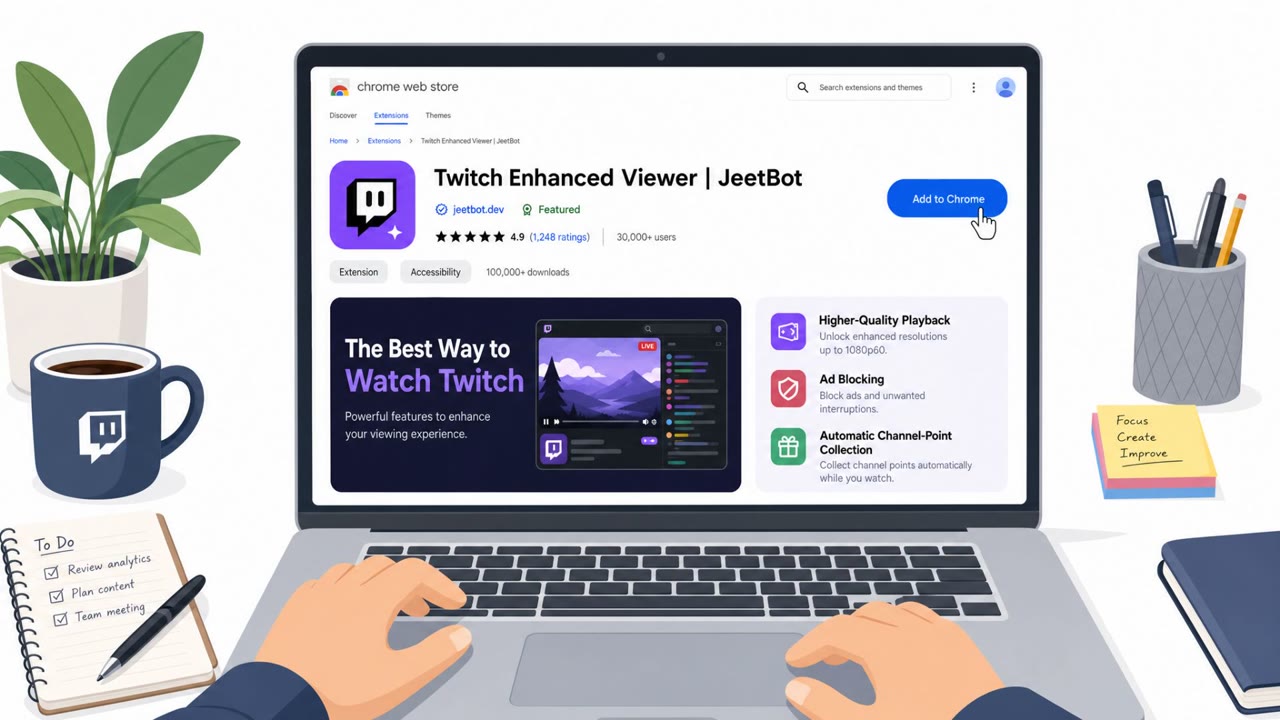
Twitch Extension Exposed OAuth Tokens to Developer

Twitch Extension Exposed OAuth Tokens to Developer

Researchers reported that a popular Twitch browser extension sent users’ Twitch OAuth login tokens to proxy servers controlled by the extension’s developer. If a token was exposed, someone receiving it could potentially act as the account holder without needing the user’s password. The key user…

September 15, 2026
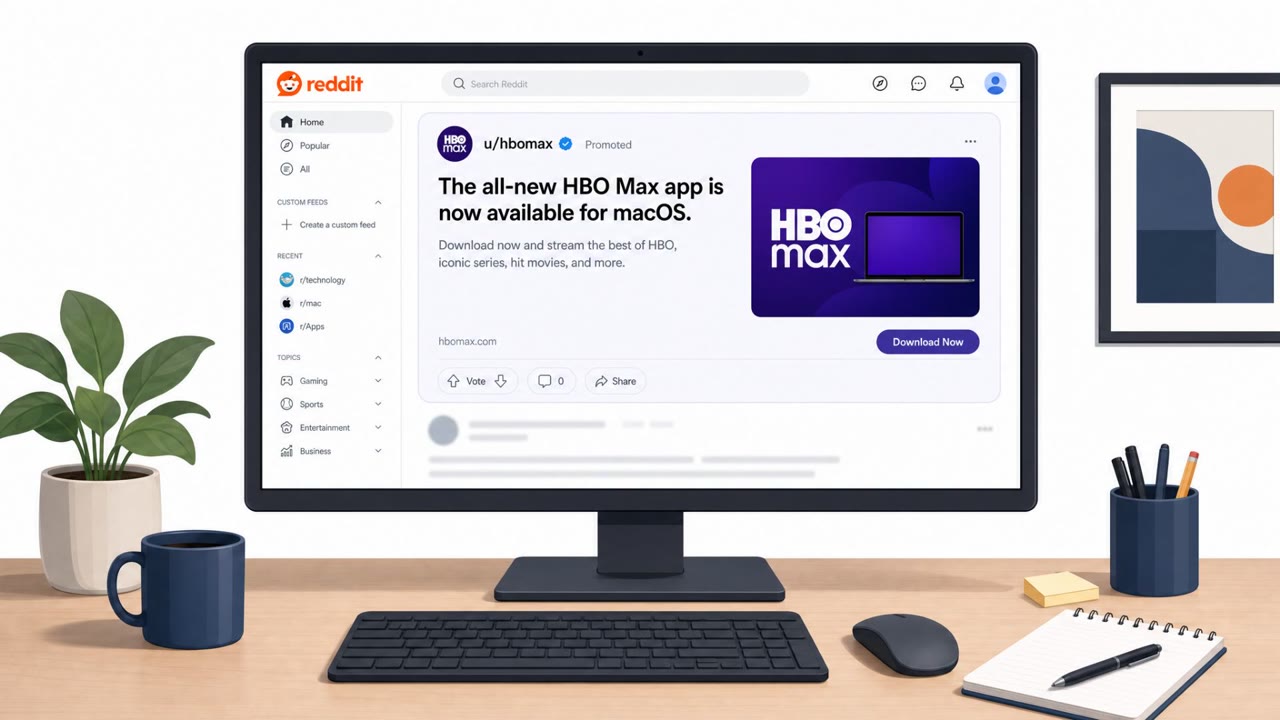
HBO Max Reddit Account Hijacked for ClickFix Malware Ads

HBO Max Reddit Account Hijacked for ClickFix Malware Ads

Attackers took over the verified official HBO Max Reddit account and used it to run a 48-hour wave of malicious ads. The ads sent people to lookalike download sites that tricked them into copying and running commands, leading to information-stealing malware on both macOS and Windows. Researchers…

September 15, 2026
Hijacked HBO Max Reddit Ads Push ClickFix Malware

Hijacked HBO Max Reddit Ads Push ClickFix Malware

Researchers reported that criminals hijacked HBO Max’s verified Reddit account and used it to run malicious ads that led people to fake download sites. The sites didn’t provide real installers, instead they tricked users into pasting and running commands in Terminal/PowerShell, causing them to…

September 15, 2026
HBO Max Reddit Hijack Pushed ClickFix Malware

HBO Max Reddit Hijack Pushed ClickFix Malware

Attackers took over the verified HBO Max Reddit account and ran over 100 malicious ads that sent people to fake download pages. The pages used a ClickFix-style trick: users were told to copy/paste a command into macOS Terminal (and similar OS-targeted lures) to install information-stealing malware.

September 14, 2026
Fake Gov Sites Lure Central Asia Users for Cash

Fake Gov Sites Lure Central Asia Users for Cash

Researchers found a large scam campaign using hundreds of fake government and news websites in Uzbekistan, Belarus, and Tajikistan. The sites lure people with promises of government-backed cash payments or passive income, then collect phone numbers and other personal data for follow-up…

September 14, 2026
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
Fake Reward Apps Abuse Google Play Early Access

Fake Reward Apps Abuse Google Play Early Access

Researchers say scammers are using Google Play’s “Early Access” listings to push deceptive Android apps that don’t show public ratings or warnings. Victims are lured by TikTok/Facebook ads promising cash rewards or free casino spins, but the apps primarily bombard users with ads and never deliver…

September 10, 2026
Instagram Copyright Strikes Used for Ransom

Instagram Copyright Strikes Used for Ransom

Scammers are filing fake copyright complaints to get Instagram accounts temporarily suspended, then demanding money to “withdraw” the complaint and restore access. Victims are pushed to communicate off-platform (for example, on Telegram) and asked to pay in cryptocurrency, yet even paying doesn’t…

September 10, 2026
Fake Minecraft Sites Keep Spreading WeedHack

Fake Minecraft Sites Keep Spreading WeedHack

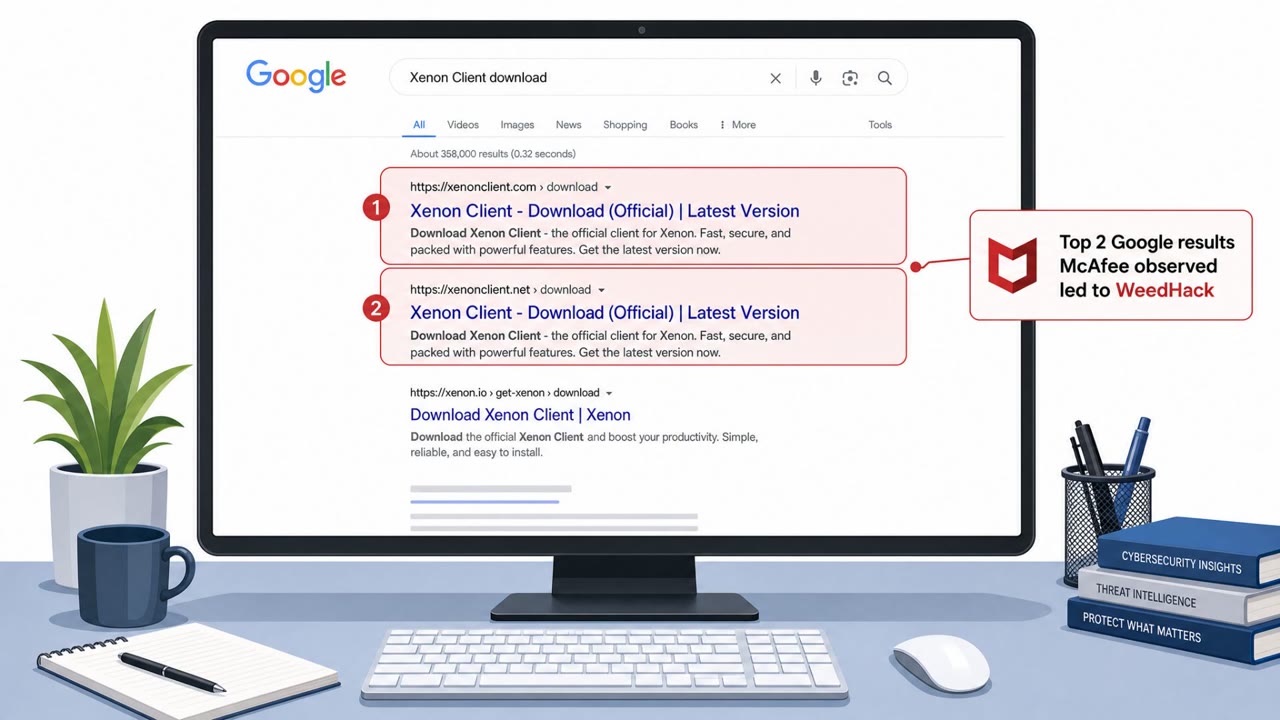
Attackers are tricking Minecraft players into downloading malware by cloning legitimate mod/client websites and manipulating search results so the malicious pages appear highly ranked. Even after the malware’s command-and-control systems were disrupted, the fake sites and trusted file-hosting links…

September 8, 2026
Meta Missed Hundreds of CSAM 'Nudify' Ads

Meta Missed Hundreds of CSAM 'Nudify' Ads

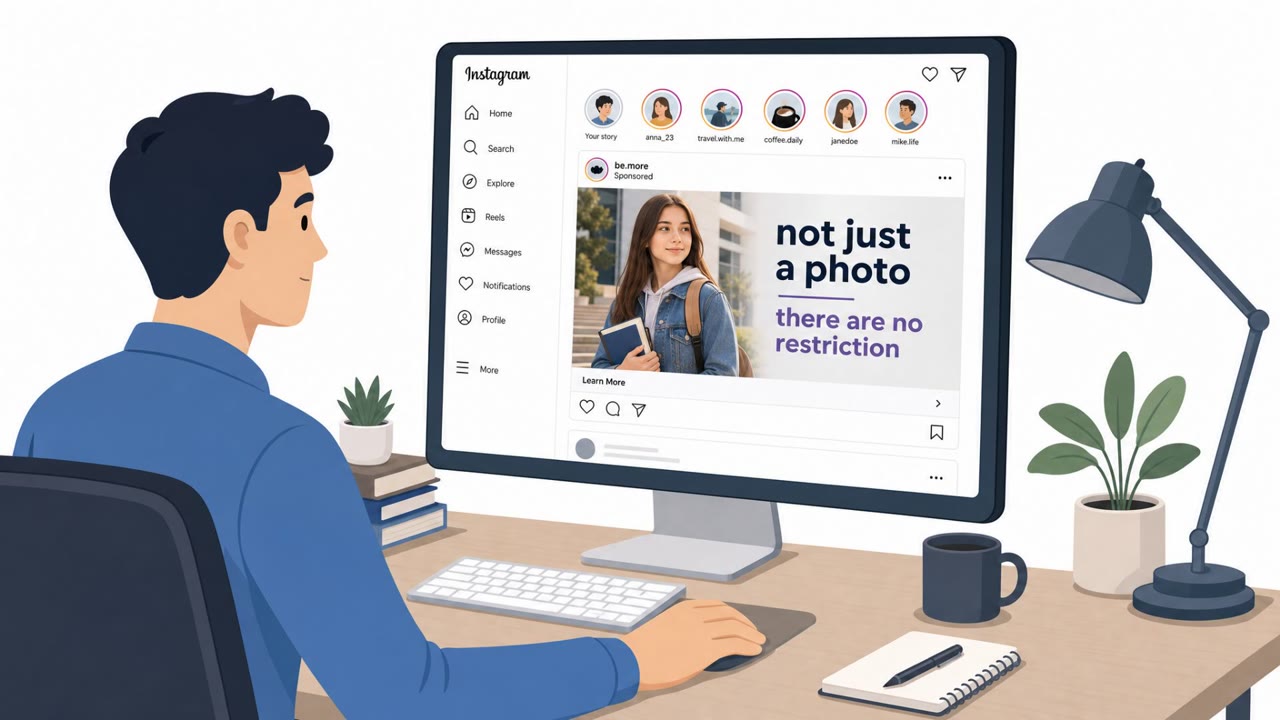
Researchers found hundreds of paid ads running across Meta platforms that promoted “nudification”/face‑swap apps and included abusive sexual content involving minors, including some using real children’s photos pulled from the web. The ads used manipulative marketing text (for example, claiming…

September 8, 2026
Flirty X DMs Funnel Victims to Discord and Paid Pages

Flirty X DMs Funnel Victims to Discord and Paid Pages

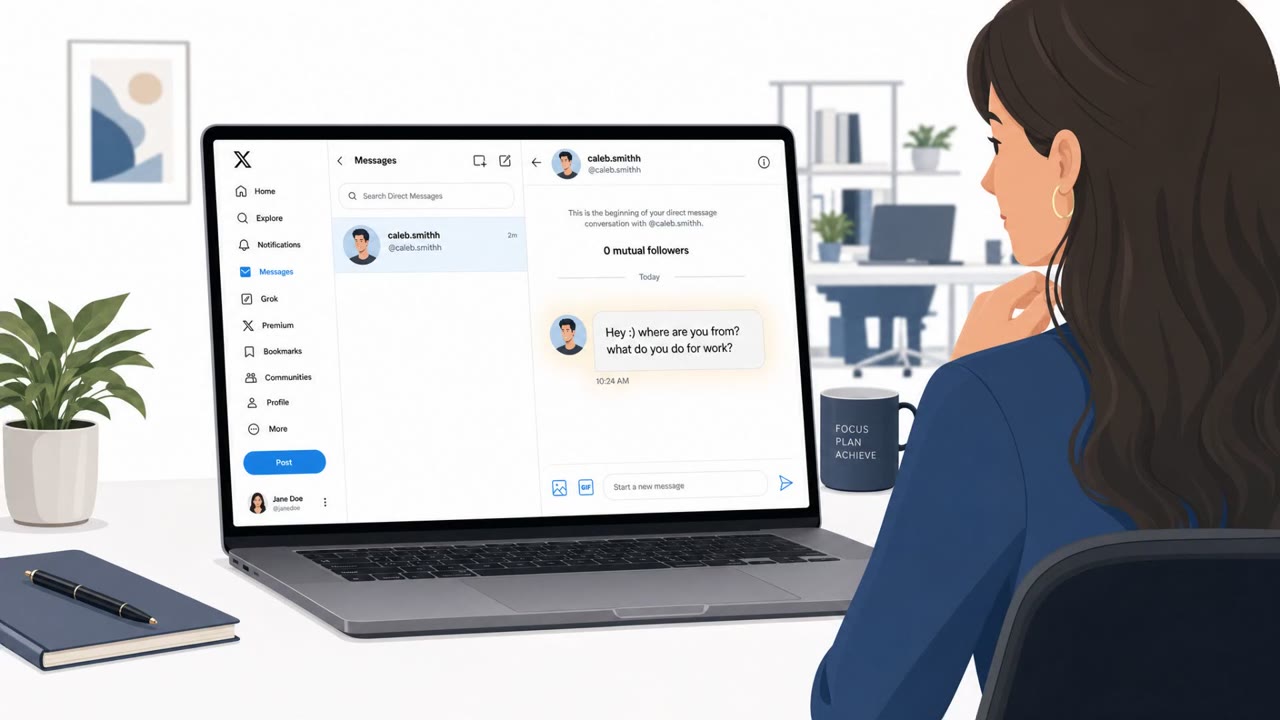
Researchers observed flirty spam accounts on X (Twitter) using scripted conversations, and possibly AI-generated replies and voice notes, to build trust and move targets toward Discord and paid adult-content pages. The accounts asked repetitive “getting to know you” questions, handled unusual…

September 7, 2026
REVSTEALER Lures Push Fake Cheats, Drop Miners

REVSTEALER Lures Push Fake Cheats, Drop Miners

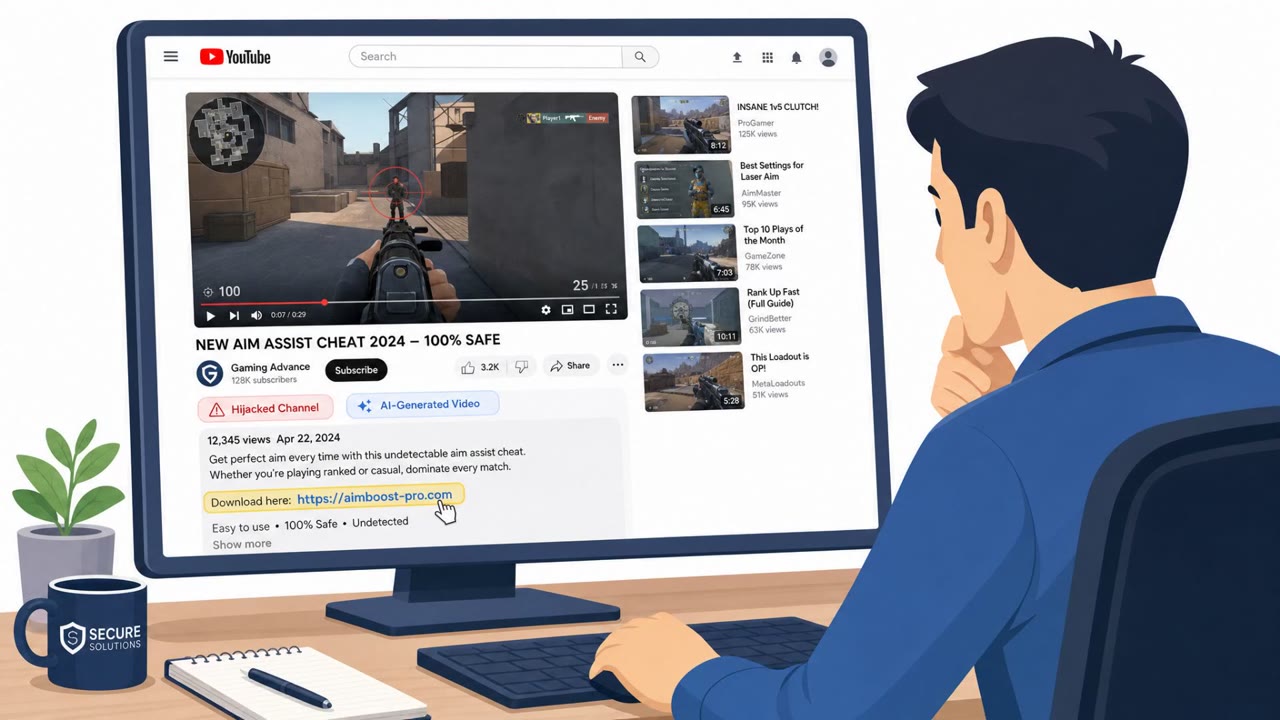
Researchers tied several new programs to the REVSTEALER Windows info-stealer that can steal crypto wallet data, hijack clipboard crypto addresses, and even disable Windows Update and Microsoft Defender to run a crypto miner. Victims are primarily pulled in through “game-cheat” downloads promoted by…

September 6, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo