Recent Telecommunications Cyber Attacks

Page 2 of 2
Half-Click OWA Emails Trigger Stealth Mailbox Takeover

Half-Click OWA Emails Trigger Stealth Mailbox Takeover

A Russia-aligned group (TA488) sent specially crafted emails that triggered malicious JavaScript simply by being viewed in Outlook Web Access (no link click or attachment needed). The implant (“OWAReaper”) can quietly change server-side mailbox permissions and abuse OAuth tokens, so attackers can…

July 30, 2026
“Half-Click” OWA Email Trap Spreads

“Half-Click” OWA Email Trap Spreads

Proofpoint reports a Russian-linked espionage group is using booby-trapped emails that infect users simply when they open the message in Outlook Web Access (OWA) on on‑premises Exchange. The attack runs malicious JavaScript inside the victim’s logged-in mail session and installs a stealthy…

July 30, 2026
“No-Action” Emails Trigger OWA Mailbox Takeover

“No-Action” Emails Trigger OWA Mailbox Takeover

Russian-linked threat actors sent generic-looking informational emails that required no clicking, but simply opening them in vulnerable Outlook Web Access (OWA) could trigger a hidden exploit. The campaign targeted government and multiple industries, then installed a stealthy browser-based implant…

July 30, 2026
Laundry Bear Uses “Half-Click” OWA Email Exploit

Laundry Bear Uses “Half-Click” OWA Email Exploit

UK and US cyber authorities and Proofpoint reported a real campaign where the Russian-linked group “Laundry Bear” (TA488) sent emails that could infect victims simply by being opened in Outlook Web Access. The email’s HTML triggers the server to run attacker code, installing a mailbox-stealing…

July 29, 2026
Telegram Dating Bot Used to Recruit Young Saboteurs

Telegram Dating Bot Used to Recruit Young Saboteurs

Russian authorities allege Telegram was used to recruit and pressure young people into real-world attacks, with “Ukrainian agents” posing as young women via a popular Telegram dating chatbot. The article describes a concrete manipulation workflow (romance/entrapment → coercion) that led to arrests…

July 29, 2026
TA488 Uses “Half-Click” OWA Emails to Persist

TA488 Uses “Half-Click” OWA Emails to Persist

Proofpoint reports a Russia-aligned espionage group (TA488) returned with a campaign that compromises on‑premises Outlook Web Access simply when a user opens an email in the reading pane. The attack uses a cross-site scripting flaw to run hidden JavaScript, install a browser-resident implant, and…

July 29, 2026
Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Researchers report Mirage Kitten (an espionage-focused threat group) targeted organizations in the Middle East and Africa using highly tailored spear‑phishing. The lures included recruitment-themed messages impersonating trusted brands/hiring sites and fake videoconferencing pages that redirected…

July 28, 2026
Survey Call Led to SIM Swap Near-Takeover

Survey Call Led to SIM Swap Near-Takeover

An attacker called the victim pretending to be their mobile carrier, built trust with a “customer satisfaction survey,” then asked the victim to read back an SMS one-time passcode and a long-standing account passcode. The attacker had already initiated (and days earlier executed) a SIM swap, then…

July 22, 2026
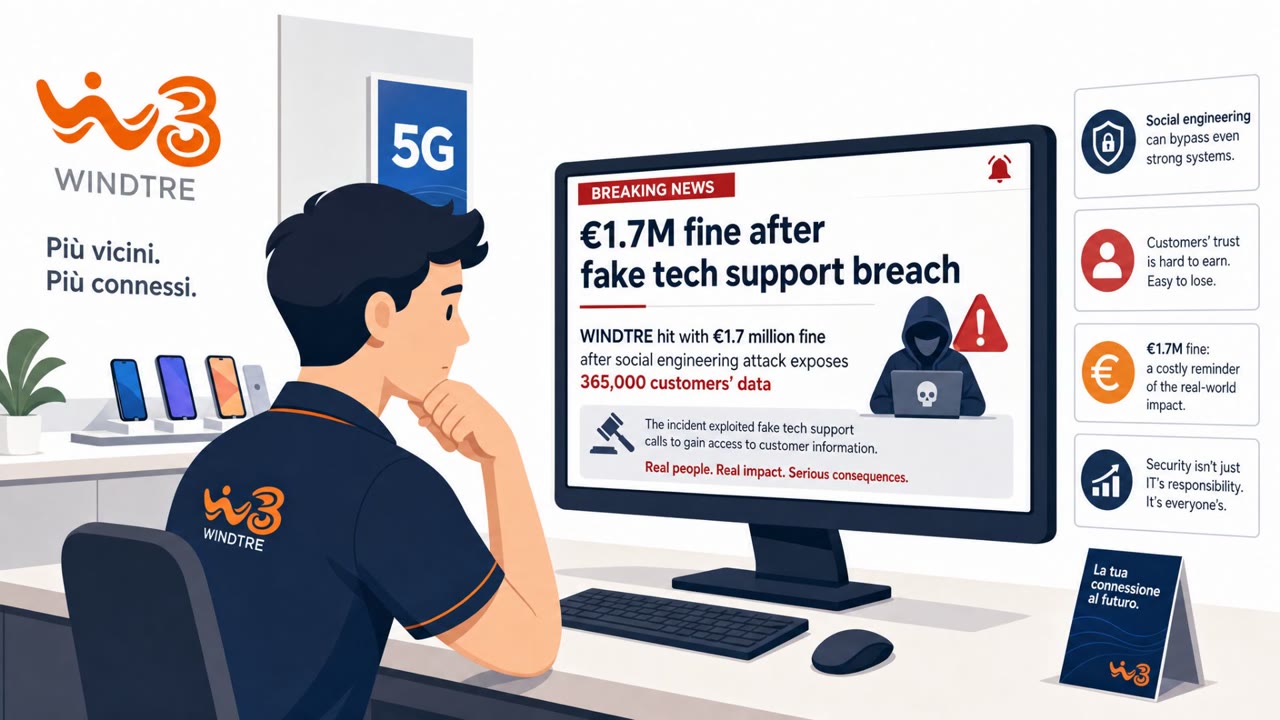
Fake Support Techs Breach WINDTRE Retail Stores

Fake Support Techs Breach WINDTRE Retail Stores

Italy’s privacy regulator fined telecom operator WINDTRE after two breaches where attackers used simple social engineering, not hacking tools. The attackers posed as support technicians and talked retail store staff into giving them system access, leading to theft of customer data. The case shows…

July 21, 2026
Fake Tech Support Trick Led to WINDTRE Breaches

Fake Tech Support Trick Led to WINDTRE Breaches

Italy’s privacy regulator fined telecom operator WINDTRE €1.7M after two breaches where attackers used social engineering, posing as support technicians, to persuade store staff to grant system access. The intruders then pulled personal data for over 365,000 customers, including payment-related…

July 20, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo