ASOS App Push Alert Used to Extort Customers

About DFIR · Medium sophistication
Last updated October 9, 2026

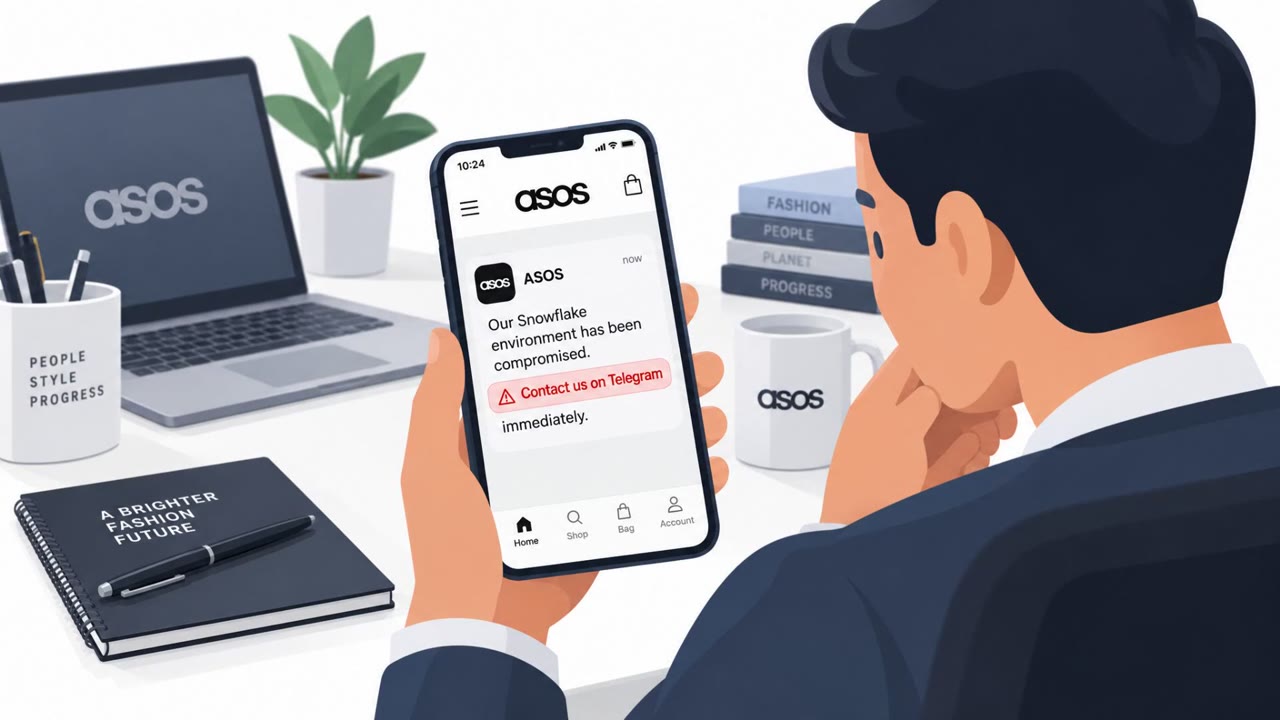
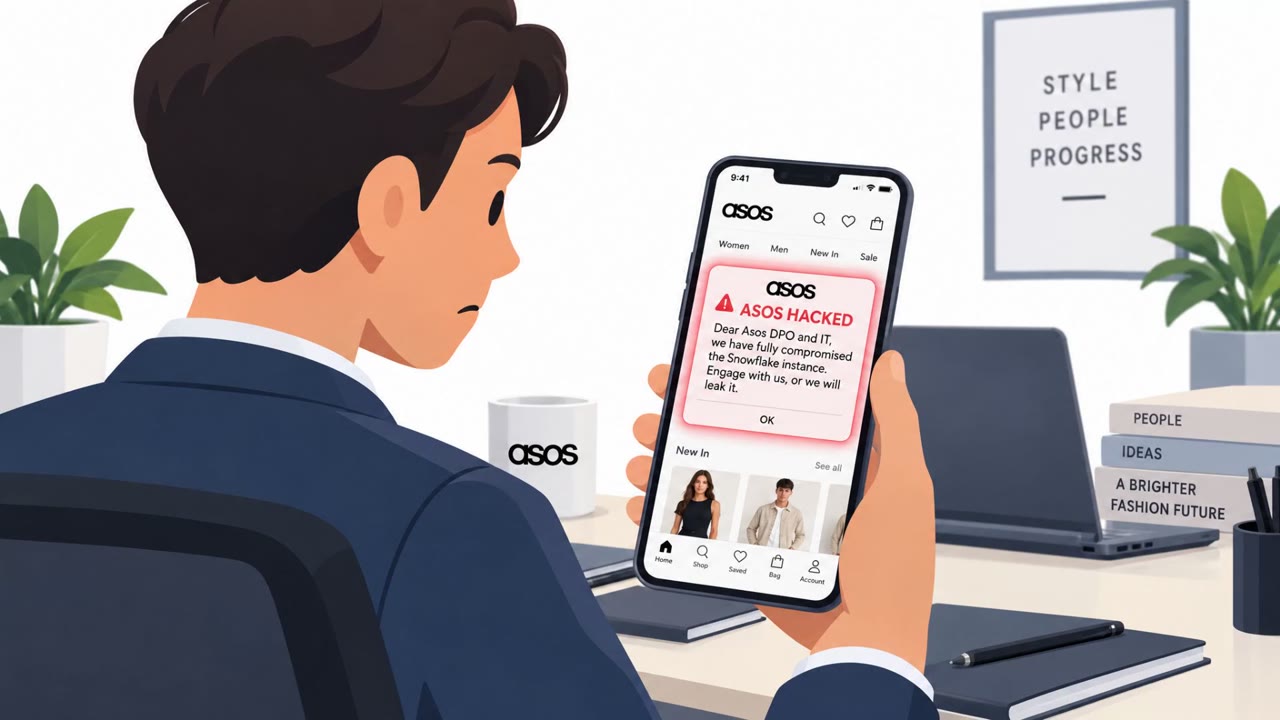
Attackers abused ASOS’s own mobile app messaging to send customers a threatening push notification claiming ASOS’s Snowflake environment was compromised and demanding engagement to avoid a data leak. ASOS confirmed the notification was unauthorized and warned customers to watch for follow-on phishing after potential exposure of names and contact details.

Key findings

  • Attackers sent a push notification to customers through ASOS’s own app, making the message appear more trustworthy than a normal email/SMS scam.
  • The message claimed a full compromise of ASOS’s Snowflake instance and threatened to leak data unless ASOS engaged with the attackers.
  • ASOS restricted access to its messaging platforms after confirming the notification was unauthorized.
  • ASOS said names and contact details may have been accessed, and advised customers to watch for follow-on phishing.

Who’s being targeted

  • Commonly targeted roles: Customer Support, Marketing/CRM, Security/Incident Response, Retail/eCommerce leadership, All employees (general awareness for follow-on phishing).
  • Affected industries: Retail / e-commerce, Financial services (mentioned in other nugget), Critical infrastructure (mentioned in other nugget), Education (mentioned in other nugget).
  • Attack channels: website.
  • Impersonated: ASOS / “hackers” speaking as a data-leak extortion group.

Awareness takeaways

  • Treat alarming ‘breach’ or ‘data leak’ messages, especially those demanding urgent engagement, as potential social engineering, even if they arrive through a trusted-looking channel like an official app notification.
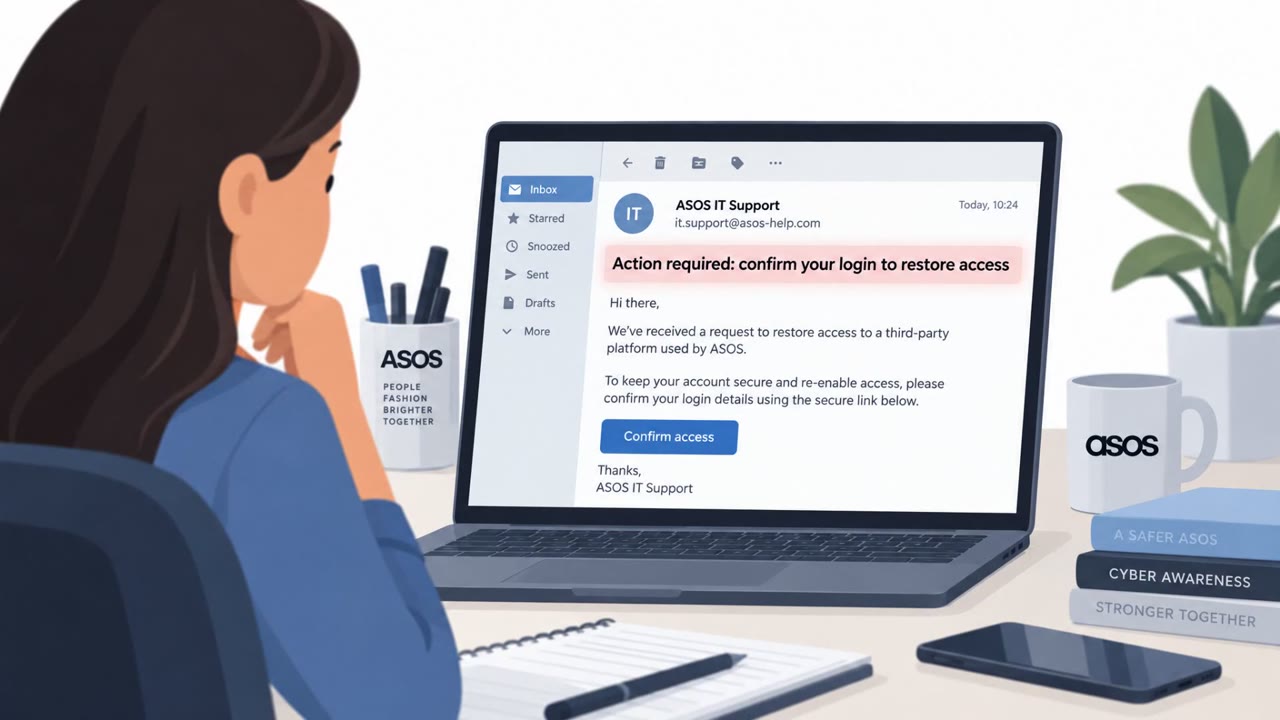
  • Expect follow-on phishing after contact details are exposed; remind users to verify any ‘ASOS support’ outreach via official channels before clicking links or sharing information.
  • Limit and tightly monitor access to customer messaging platforms (push/email/SMS), because compromise of these systems can quickly create credible mass social-engineering reach.

Red flags to watch for

  • Unexpected high-pressure message threatening a data leak unless you respond
  • Security/breach claims delivered via an unusual channel (app push) rather than official support/security channels
  • Message pushes you to ‘engage’ instead of directing you to official ASOS help pages or verified communication methods
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

Imagine this: you’re shopping on the ASOS app and a push pops up saying their Snowflake data is fully hacked and your info will be leaked unless they ‘engage’. That really happened. Attackers pushed a fake breach and extortion message through ASOS’s own app, claiming a full Snowflake compromise and threatening to leak data unless ASOS talked to them. Here’s the twist: ASOS said only names and contact details may have been exposed, not cards or passwords. That means the real risk is follow-on phishing that looks like ‘ASOS support’ emailing or texting you about this scare. If you get a breach or data-leak alert from any brand’s app, don’t tap it, go to their official website or help center yourself and check there instead.

Similar attacks

ASOS App Push Alert Claims ‘Snowflake’ Breach

ASOS App Push Alert Claims ‘Snowflake’ Breach

ASOS customers received an unexpected push notification inside the official ASOS app claiming the retailer had been hacked and demanding engagement to prevent data leaks. ASOS confirmed it was an “unauthorised customer notification” tied to third‑party messaging platforms and said it restricted…

October 6, 2026
ASOS Breach: Impersonation Stole Employee Login

ASOS Breach: Impersonation Stole Employee Login

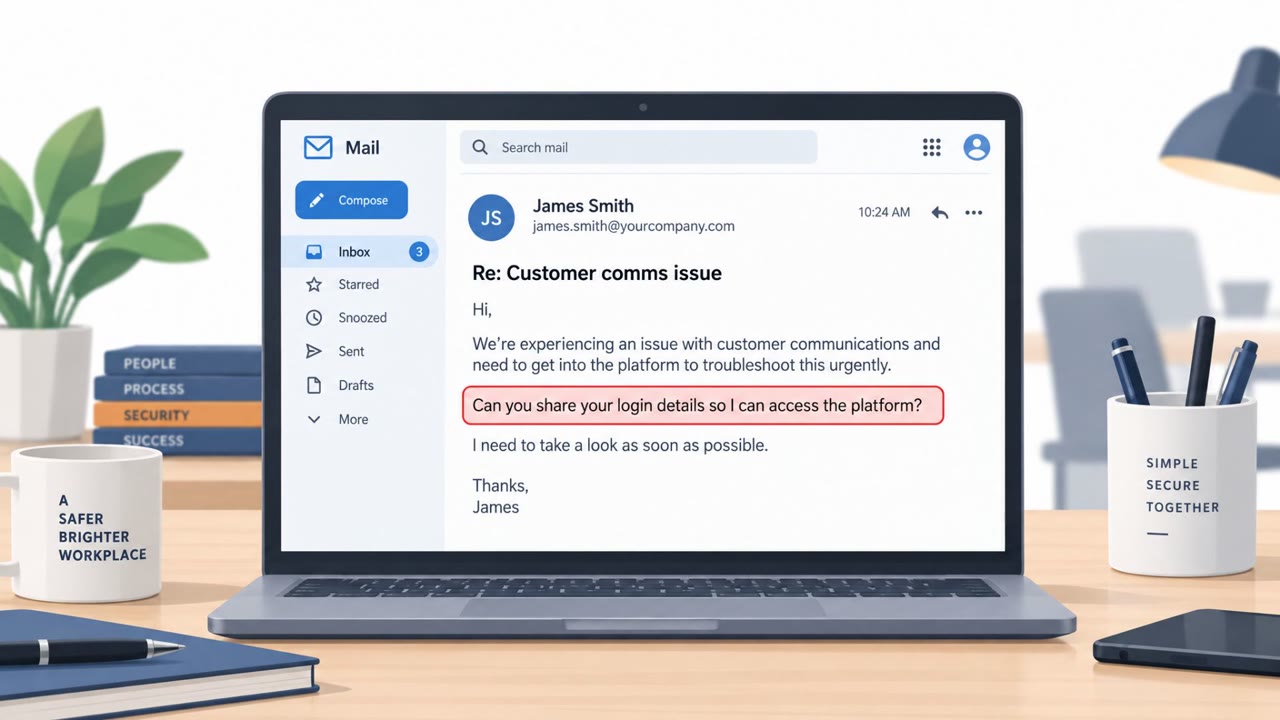
ASOS says an attacker got into an employee account by impersonating a trusted contact to steal login credentials. Those credentials were then used to access third-party platforms and send a legitimate-looking push notification to customers claiming a Snowflake hack and directing them to a Telegram…

October 8, 2026
ASOS App Push Used to Send Hack Claim

ASOS App Push Used to Send Hack Claim

ASOS customers received an unauthorized push notification sent through ASOS’s real mobile app. The message claimed ASOS’s Snowflake environment was compromised and urged recipients to contact the sender via Telegram, leveraging the trust people place in official app notifications. ASOS said it was…

October 7, 2026
ASOS App Push Alert Used for Extortion

ASOS App Push Alert Used for Extortion

Attackers used social engineering to access an ASOS employee account connected to Snowflake, then used ASOS’s own app notification system to broadcast an extortion message directly to customers. The incident also involved suspected large-scale customer data theft, which increases the risk of highly…

October 9, 2026
ASOS Breach Began With Tricked Employee Login

ASOS Breach Began With Tricked Employee Login

ASOS confirmed attackers got into customer-data systems after tricking an employee into handing over login credentials. Stolen data reportedly included not only names and contact details, but also customers’ shopping searches, which could enable highly convincing follow-on scams and phishing.…

October 9, 2026
ASOS App Push Alert Used for Extortion Threat

ASOS App Push Alert Used for Extortion Threat

ASOS confirmed an unauthorized push notification was sent to customers through its official mobile app, claiming the retailer was “hacked” and threatening to leak data unless ASOS engaged with the attackers. The message attempted to pressure ASOS’ security and privacy teams and directed the company…

October 8, 2026