Cisco Talos investigated a VYPR ransomware incident in which an attacker used a voice-phishing call to trick a user into starting a Microsoft Quick Assist remote-support session. Talos also observed IT help desk impersonation in several other incidents, showing that a seemingly routine support call can give criminals remote access and lead to ransomware.
How the attack worked
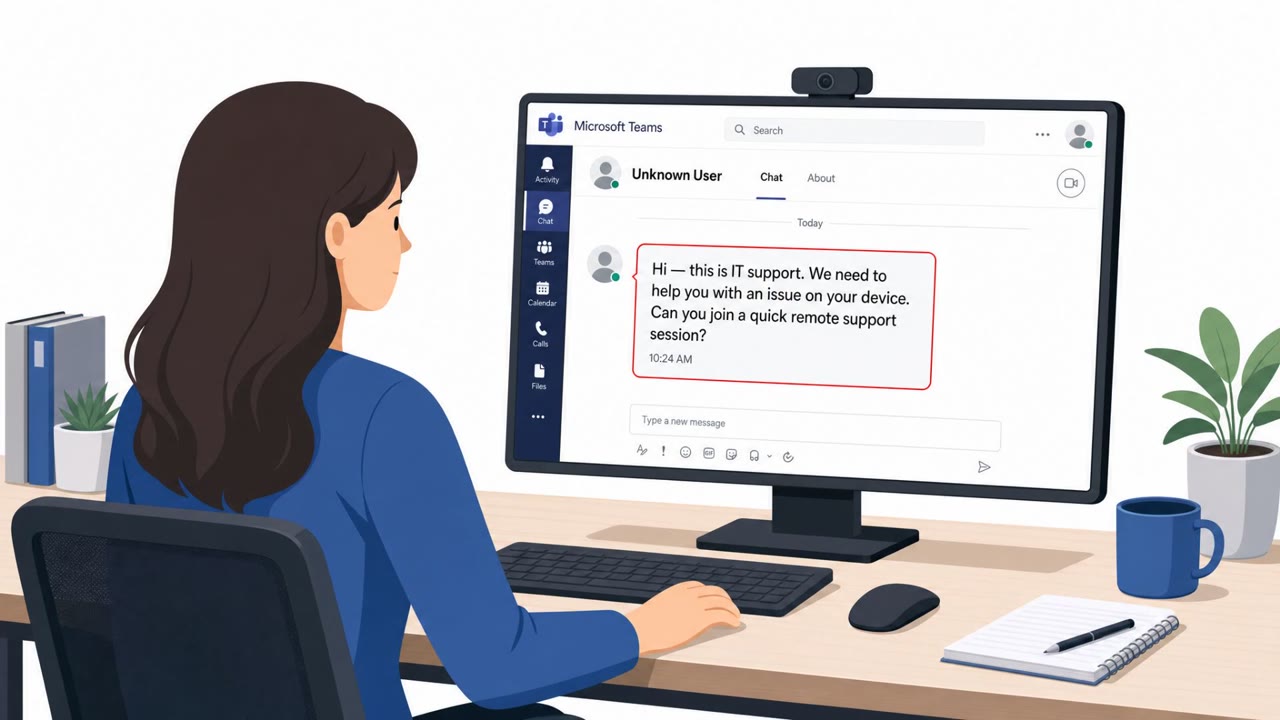
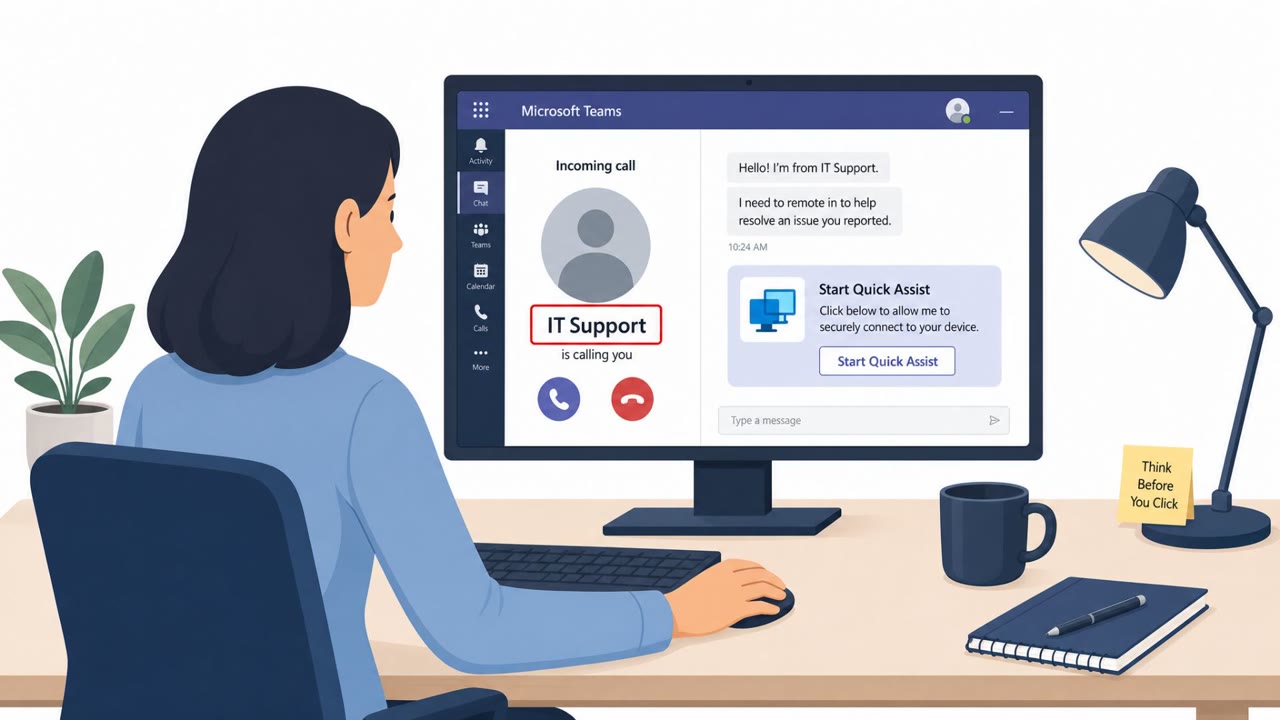
In this incident investigated by Cisco Talos, an attacker used a vishing call to impersonate IT help desk staff. The caller told the target they needed remote technical assistance and asked them to open Microsoft Quick Assist to start a remote-support session. Once the session was active, the attacker had direct remote access to the endpoint. This case was linked to a VYPR ransomware deployment, and Talos noted that IT help desk impersonation during vishing calls was observed in several other Q3 engagements, not just this one.
After establishing remote access, the actor used existing remote-management software already present in the environment to execute PowerShell commands. Those commands downloaded and installed a Microsoft Software Installer package from a remote IP address, extending the attacker's foothold beyond the initial Quick Assist session.
Why it succeeded
The pretext worked because it exploited a routine, expected interaction: an employee receiving IT support. The request to launch a remote-access tool did not look unusual on its face, especially when delivered with confidence by someone claiming to be help desk staff. Talos's broader findings put this in context. Phishing, including vishing, was the most common initial-access method across Talos IR engagements, appearing in 37 percent of cases, and ransomware and pre-ransomware incidents made up 27 percent of engagements, up from a maximum of 20 percent in the prior four quarters.
Underlying weaknesses also played a role in how far these incidents progressed. Talos identified insufficient logging, weak credential management, and missing or poorly implemented MFA as the most common security gaps across the engagements it reviewed.
What to watch for
- An unexpected phone call claiming to be from the IT help desk
- A request to open Microsoft Quick Assist or another remote-support tool
- Pressure to start the remote session quickly, before verifying the request
- The request arriving outside a known support ticket or established help desk channel
How to build resistance
Organizations can reduce the chance of this pretext succeeding by reinforcing a few habits across all employees, remote workers, and especially IT help desk staff and privileged-account holders:
- Treat unsolicited requests to launch remote-support tools as suspicious by default
- Require employees to independently verify IT support requests through a known company channel, published help desk number, or approved internal support portal before starting any remote session
- Deploy phishing-resistant MFA and ensure high-privilege accounts cannot bypass MFA through legacy authentication methods
- Encourage immediate reporting of suspected remote-access scams so security teams can respond before attackers install additional tools or move toward ransomware deployment
These incidents show that a single phone call exploiting trust in IT support can be enough to open the door to a full ransomware event, which is why verification habits and credential hygiene matter as much as technical controls.
Key findings
- Phishing was the most common initial-access method in Talos IR engagements, appearing in 37 percent of cases.
- In a VYPR ransomware incident, an attacker used vishing to persuade a user to initiate a Microsoft Quick Assist session.
- Talos observed IT help desk impersonation during vishing calls in several Q3 engagements.
- After gaining remote access, the VYPR actor used existing remote-management software to run PowerShell and install a package from a remote IP address.
- Ransomware and pre-ransomware incidents accounted for 27 percent of engagements, up from a maximum of 20 percent in the prior four quarters.
- Insufficient logging, weak credential management, and missing or poorly implemented MFA were the most common security weaknesses.
Who’s being targeted
- Commonly targeted roles: All employees, Remote workers, IT help desk staff, Service desk managers, Security operations teams, Privileged-account holders.
- Affected industries: Finance and Insurance, Public Administration, Health Care, Telecommunications.
- Attack channels: vishing.
- Impersonated: IT help desk.
Red flags to watch for
- The caller unexpectedly asks the employee to start a remote-access session.
- The request comes by an unsolicited phone call rather than through a verified support ticket or known help desk channel.
- The caller pressures the employee to enable remote access before independently verifying the request.
Frequently asked questions
How did the attacker gain initial access in this incident?
The attacker used a vishing call to impersonate IT help desk staff and convinced the user to start a Microsoft Quick Assist remote-support session, which gave the attacker remote access to the endpoint.
What did the attacker do after gaining remote access?
The actor used existing remote-management software to run PowerShell commands that downloaded and installed a Microsoft Software Installer package from a remote IP address.
Why is IT help desk impersonation an effective vishing tactic?
Talos observed this impersonation technique in several Q3 engagements because employees are conditioned to cooperate with IT support requests, making them more likely to start a remote session without independently verifying the caller.
What security gaps made these incidents more likely to succeed?
Insufficient logging, weak credential management, and missing or poorly implemented MFA were the most common weaknesses identified across these engagements.
Read the video transcript
“IT help desk here. Please start Microsoft Quick Assist.” Unexpected call? Pause. That’s vishing: someone impersonates IT to get remote access. In a VYPR ransomware case, one Quick Assist session let the caller onto an employee’s computer. Here’s the catch: a help desk name on your phone isn’t a support ticket. After access, the VYPR operator used remote-management software to run PowerShell and install a package. Before starting Quick Assist for an unexpected caller, call your help desk using the number in your company directory.