Fake Ledger “Firmware Update” Phish Spreads

Protos · Medium sophistication
Last updated October 16, 2026

Scammers are exploiting fear from a recent Ledger-related spyware incident by sending emails that push a fake “firmware update.” The email urges recipients to connect their hardware wallet and click through to a realistic-looking “Genuine check” page with an “Update Now” button, risking theft if victims follow the instructions or reveal their recovery phrase.

Key findings

  • A real-world phishing campaign is using a fake “Ledger firmware update” message to exploit panic around an $86M Ledger spyware incident.
  • The lure tells recipients to connect their hardware wallet to “protect your device against emerging spyware threats,” referencing “recent incidents in Malaysia.”
  • The phishing flow reportedly includes a realistic fake “Genuine check” page, device selection, and an “Update Now” button.
  • The warning highlights the likely end goal: trick users into clicking update links and entering their wallet recovery phrase (seed phrase).

Who’s being targeted

  • Commonly targeted roles: Finance, Executives, Employees managing corporate crypto assets, Security awareness training audience (all staff with access to company funds/accounts).
  • Affected industries: Cryptocurrency/Blockchain, Financial services (consumer financial assets), Retail consumers/individual investors.
  • Attack channels: email, website.
  • Impersonated: Ledger (or Ledger Support).

Awareness takeaways

  • Treat “security update” emails as suspicious, verify updates only through the official product/app workflow, not emailed links.
  • Never enter or share wallet recovery phrases/seed phrases, any request for it should be treated as an attempted theft.
  • Be extra cautious during high-profile incidents; attackers often exploit panic and breaking news to increase click-through rates.

Red flags to watch for

  • Creates urgency/fear by referencing a high-profile incident and “emerging spyware threats.”
  • Pushes the user to use website links/buttons for an update rather than the official app/update process.
  • Any request to enter a recovery phrase is a strong indicator of fraud.
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

You might see this soon: “Ledger firmware update required to protect against new spyware in Malaysia.” Scammers are riding the real $86 million Ledger spyware news, emailing you to plug in your wallet, click their link, and run a fake "Genuine check" with an "Update Now" button. Here’s the trap: after you click "Update Now," the site guides you step by step until it asks for your wallet recovery phrase. That’s the heist, Ledger will NEVER ask for your seed phrase on a website. If you get a “Ledger firmware update” email, ignore the link. Open Ledger Live or the official Ledger site yourself, update only from there.

Similar attacks

Fake IRS Letters Push Crypto “Compliance Portal”

Fake IRS Letters Push Crypto “Compliance Portal”

Scammers are mailing official-looking “IRS” letters to cryptocurrency holders, urging them to scan a QR code and enroll in a fake “Digital Asset Compliance Portal.” The QR code leads to a fraudulent IRS-lookalike site that gathers wallet/exchange details and then prompts victims to provide a phone…

August 4, 2026
Fake Install Guides and Helpdesk Calls Drive Attacks

Fake Install Guides and Helpdesk Calls Drive Attacks

This bulletin describes multiple real-world social engineering campaigns where attackers trick people into trusting a familiar screen, like a search result “install guide,” a recruiter outreach, or a helpdesk phone call. The lures push victims to paste commands, install fake software, or reset MFA,…

July 30, 2026
Fake Payment Offers and AI Bank Calls Hit Users

Fake Payment Offers and AI Bank Calls Hit Users

This weekly roundup describes several real social-engineering campaigns, including fake government-payment posts that compromised thousands of Bluesky accounts and mobile scams disguised as community activities. It also documents AI-generated bank-helpdesk calls that persuaded victims to install an…

October 22, 2026
Fake Poshmark Alerts Fuel Bank Login Testing

Fake Poshmark Alerts Fuel Bank Login Testing

Criminals abused an unnamed spend-management platform’s open-banking connection feature to test stolen bank logins and identify accounts with available funds. They also used the platform’s legitimate notification system to send fake Poshmark sale alerts, directing victims to counterfeit pages that…

October 21, 2026
Microsoft Busts Massive Phishing Kit Network

Microsoft Busts Massive Phishing Kit Network

Microsoft and partners disrupted a Chinese-language phishing kit ecosystem (tracked as Storm-2990) used to send over 1 billion malicious email and SMS messages to more than 75,000 organizations worldwide. The kits used common “urgent alert” scams (delivery issues, unpaid tolls, bank or tax…

October 14, 2026
Hirudo Trojan Tricks Users With Fake App Updates

Hirudo Trojan Tricks Users With Fake App Updates

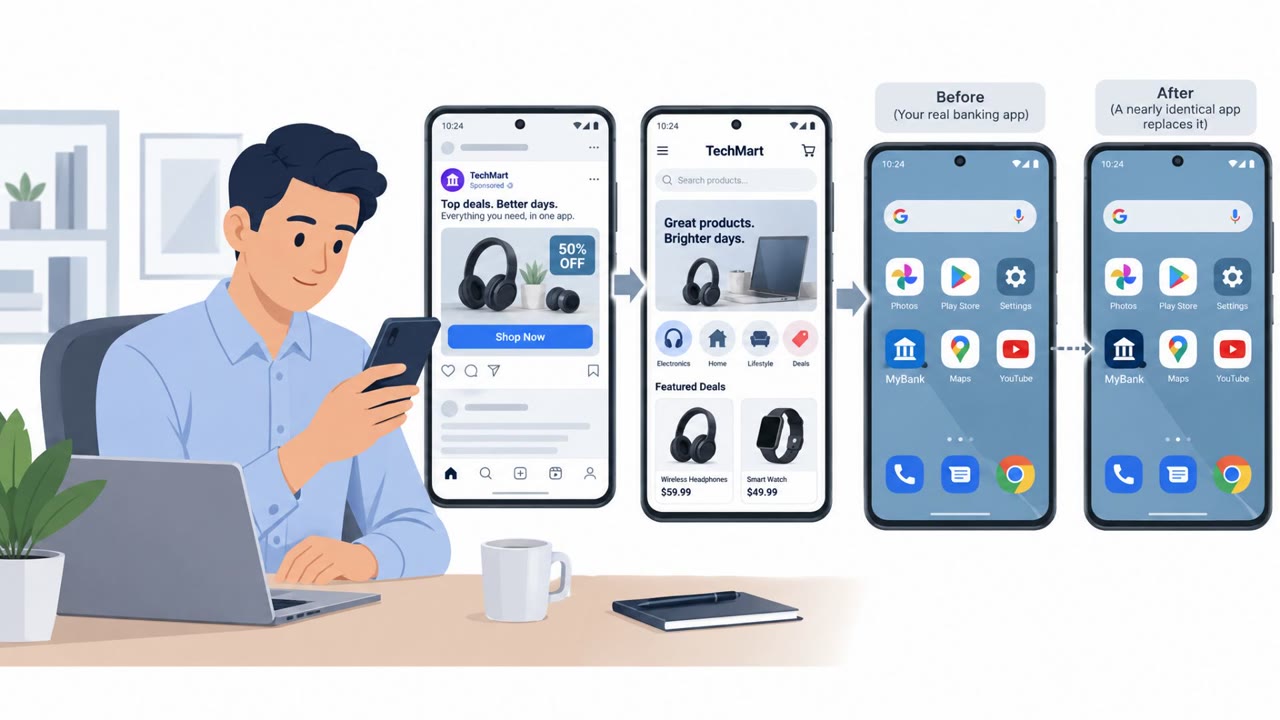
Researchers describe a real Android banking-trojan operation (Hirudo) that tricks users into installing malware through fake in-app update prompts and fake Google Play-like pages pushed via social media ads. Once installed, it can steal credentials and take over the device, and it can even replace…

October 14, 2026