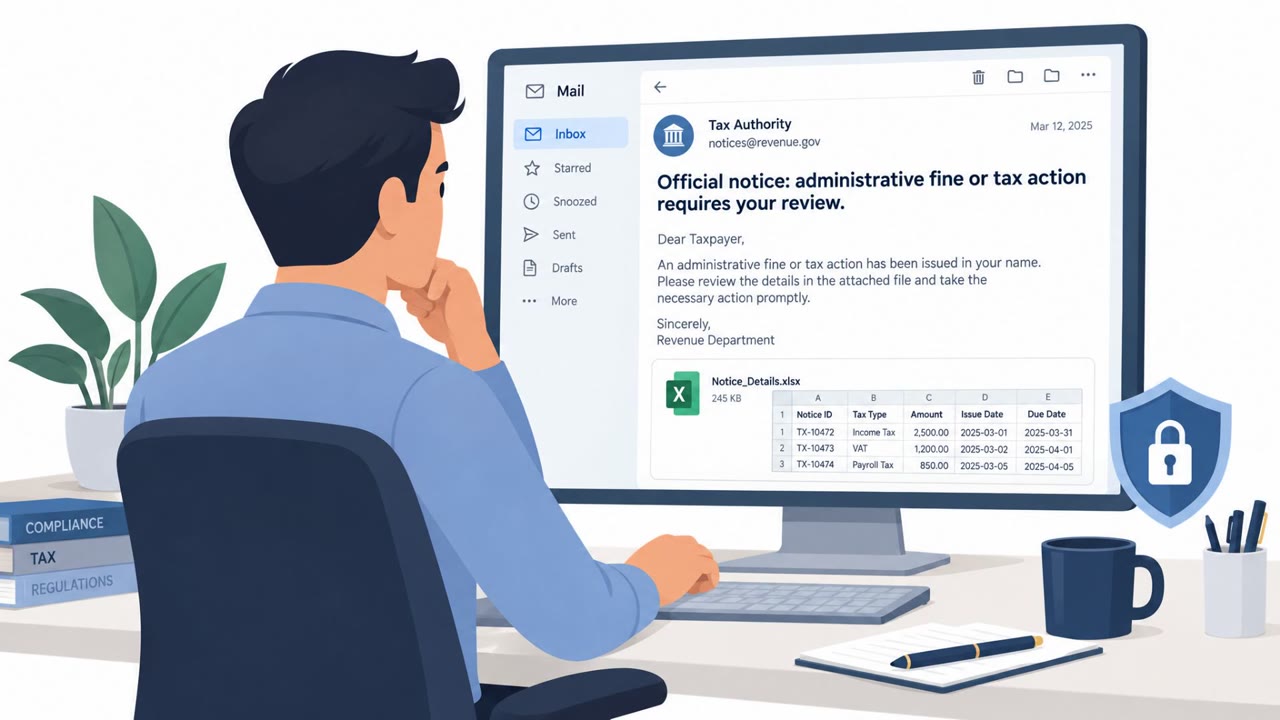
Russia-aligned group Gorbag targeted Ukrainian government, justice, defense, and military-aid transport organizations with phishing emails carrying malicious attachments. The emails were disguised as official administrative fine or tax documents, and opening them enabled theft of passwords, VPN settings, and sensitive files.
Key findings
- Gorbag has targeted Ukrainian government agencies, defense organizations, and infrastructure supporting foreign military aid since at least February 2025.
- Its primary delivery method is phishing emails with malicious attachments disguised as official administrative fine or tax documents.
- Opening an attachment can expose saved browser passwords, cookies, VPN configurations, Office documents, email records, and archives.
- The group prioritizes quickly stealing information and removing malware traces rather than maintaining long-term access.
- In early 2026, Gorbag also began exploiting CVE-2025-8088, a WinRAR vulnerability, through specially crafted archives.
Who’s being targeted
- Commonly targeted roles: Government employees, Law enforcement and judicial staff, Defense personnel, Transportation and logistics personnel, Administrative and finance staff, Employees who handle official documents or email attachments.
- Affected industries: Government, Law enforcement and judicial services, Defense, Transportation and logistics, Critical infrastructure.
- Attack channels: email.
- Impersonated: Government tax or administrative authority, Not specified in the article.
Awareness takeaways
- Treat unexpected fine, tax, and other official-document attachments as suspicious; verify the request through a known official channel before opening anything.
- Do not open unexpected archive files, especially when they arrive by email and claim to contain important official documents.
- Keep file-handling software such as WinRAR updated, because opening a malicious attachment can exploit an already-patched weakness.
- Recognize that opening one malicious attachment can expose both work credentials and sensitive organizational records.
Red flags to watch for
- An unexpected fine or tax notice arrives as an attachment.
- The sender pressures the recipient to open a file rather than use an official government portal.
- The attachment is an archive or unexpected document type.
- An unexpected archive is included with an official-looking message.
- The sender gives no independent way to verify the document.
- Opening an archive from an unsolicited message can trigger malicious code.
Read the video transcript
“Administrative fine or tax document attached.” That’s Gorbag’s bait. The email looks official, but pushes you to open an attachment, not a government portal. It may be a crafted archive exploiting WinRAR flaw CVE-2025-8088. Here’s the catch: just opening it can expose saved passwords, VPN settings, and Office files. Gorbag grabs the data fast, then removes its traces. Unexpected fine or tax attachment? Before opening it, check the notice through the government portal you already know.