INTERPOL’s Operation Serengeti III arrested 1,462 suspects across 21 countries targeting fraud, phishing, business email compromise, ransomware, and digital extortion. In Uganda, investigators found scam call centres using prepared scripts and fake trading platforms to persuade people, including pensioners, to make fraudulent investments. A separate Nigerian investment scam was promoted through messaging apps.
What Investigators Found
Interpol's Operation Serengeti III brought together law enforcement from 21 countries and led to 1,462 arrests, the disruption of 10,909 malicious networks, and the recovery of more than $105 million. Investigators identified 65,929 victims linked to losses exceeding $385 million across fraud, phishing, business email compromise, ransomware, and digital extortion cases.
In Uganda, authorities dismantled two international fraud networks running call centers that used prepared scripts and fake trading platforms to convince people to invest. Victims included pensioners who believed they were making legitimate investments through what looked like a real trading platform. A separate case in Nigeria involved an investment scam promoted through messaging apps, with proceeds laundered through cryptocurrency.
How the Scam Call Centers Worked
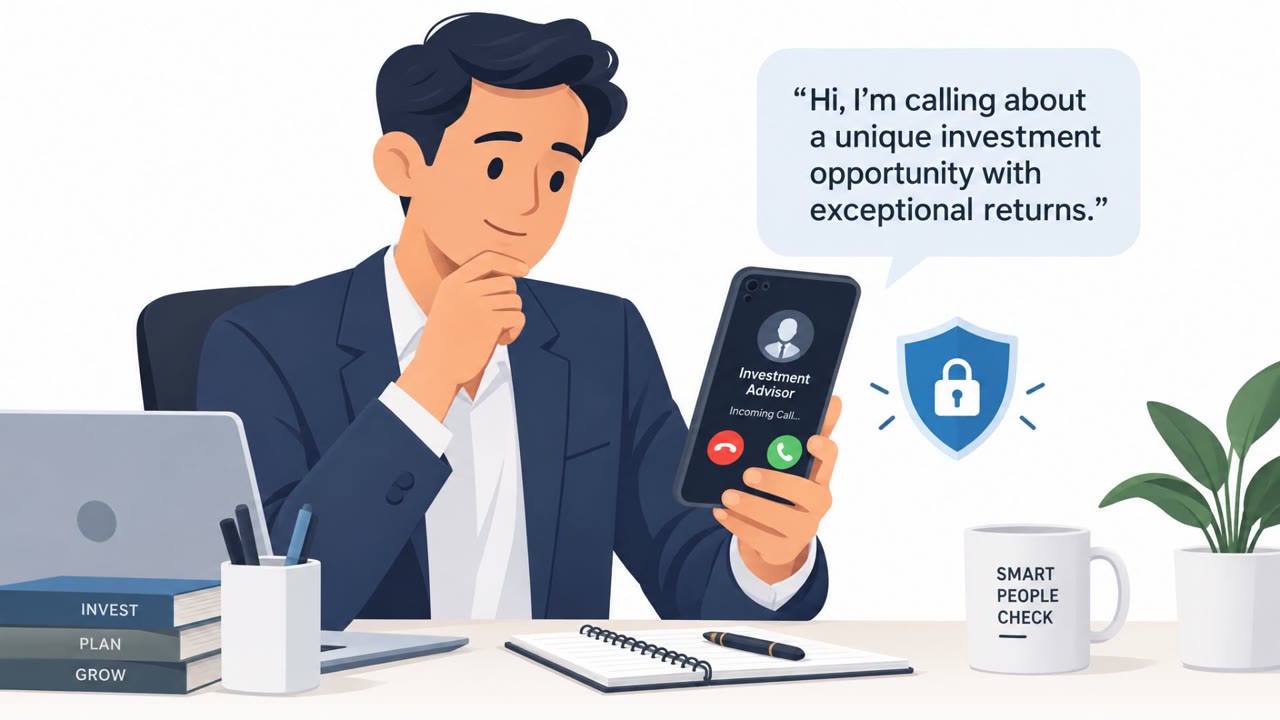
The call center model relied on staff reading from prepared scripts rather than responding naturally, a hallmark of organized vishing operations. Callers presented themselves as representatives of legitimate-looking investment or pension-growth platforms, then directed targets to open accounts and transfer funds through websites built to resemble real trading services. The messaging app variant followed a similar logic: an unsolicited investment pitch arrived through a trusted communication channel and pushed recipients toward cryptocurrency payments that are harder to trace and reverse.
Why These Scams Succeeded
Several factors made these schemes effective:
- Fake trading platforms and websites appeared professional and legitimate on the surface.
- Victims, including pensioners, believed they were engaging in genuine investment or pension-growth activity.
- Messaging app promotions exploited the trust people place in familiar communication tools.
- Cryptocurrency payment routes complicated efforts to recover funds once sent.
A separate strand of the operation also involved stolen software credentials and roughly 2.1 million harvested email addresses used to enable phishing and business email compromise, showing how credential theft can feed into broader social engineering campaigns.
What to Watch For
- Unsolicited calls or messages promoting investment or retirement-savings opportunities.
- Callers who rely on scripted pitches instead of answering specific, verifiable questions about an account or firm.
- Investment platforms that cannot be independently confirmed through official regulatory or company channels.
- Pressure to move funds quickly, particularly into cryptocurrency.
Building Resistance
Organizations and individuals can reduce exposure by verifying any investment or pension-related outreach through official channels before acting, treating unsolicited calls and messaging app investment pitches with skepticism, and protecting software and email credentials so they cannot be reused to power phishing or business email compromise campaigns. Encouraging employees nearing retirement and finance teams to report suspicious investment contact can help catch these schemes early.
Key findings
- Operation Serengeti III involved law enforcement agencies from 21 countries and resulted in 1,462 arrests, disruption of 10,909 malicious networks, and recovery of more than $105 million.
- Authorities identified 65,929 victims and linked criminal activity to losses exceeding $385 million.
- Ugandan authorities dismantled two international fraud networks allegedly operating call centres that used prepared scripts and fake trading platforms to target victims across Asia.
- The Uganda scams included investment and pension fraud aimed at people who believed they were making legitimate investments, including pensioners.
- A Nigerian suspect was arrested in connection with phishing and business email compromise involving stolen software credentials and approximately 2.1 million email addresses.
- A separate Nigerian investment scam was promoted through messaging apps and laundered much of its proceeds through cryptocurrency.
Who’s being targeted
- Commonly targeted roles: All employees, Finance and treasury teams, Employees approaching retirement, Human resources and benefits teams, Executives, Customer-facing staff.
- Affected industries: Finance and Insurance, Financial services, Retirement and pension services, Cryptocurrency services, Technology and software services.
- Attack channels: vishing, website, smishing.
- Impersonated: Representative of a legitimate-looking investment or trading platform, Investment promoter.
Red flags to watch for
- An unsolicited caller pressures the recipient to invest.
- The caller relies on a prepared sales script rather than verifiable account information.
- The trading platform or website is fake despite appearing legitimate.
- An investment offer arrives unexpectedly through a messaging app.
- The promoter provides no independently verifiable investment credentials.
- The investment opportunity uses cryptocurrency or unfamiliar payment routes.
Frequently asked questions
What was Operation Serengeti III?
It was an Interpol led operation involving law enforcement from 21 countries that resulted in 1,462 arrests, disrupted 10,909 malicious networks, and recovered more than $105 million.
How did the Uganda investment scam call centers work?
Call center staff followed prepared scripts to convince victims, including pensioners, to invest through fake trading platforms and websites presented as legitimate investment opportunities.
What role did messaging apps play in the scams?
A separate Nigerian investment scam was promoted through messaging apps, and much of the resulting proceeds were laundered through cryptocurrency.
Was credential theft involved in these cases?
Yes, a Nigerian suspect was arrested in connection with phishing and business email compromise that involved stealing software credentials and collecting about 2.1 million email addresses.
Read the video transcript
That polished trading dashboard? It could be a prop. In Uganda, scam call centres used prepared scripts: ‘I’m calling about an investment opportunity.’ Then they steered people, including pensioners, to fake trading websites. Here’s the tell: the caller can pitch returns, but can’t give you independently verifiable firm details. A slick website isn’t proof. The offer might also arrive by messaging app. Before opening an account or sending money, look up the firm yourself in your regulator’s official register.