Recent Technology Cyber Attacks

Page 3 of 16
Twitch Extension Exposed OAuth Tokens to Developer

Twitch Extension Exposed OAuth Tokens to Developer

Researchers reported that a popular Twitch browser extension sent users’ Twitch OAuth login tokens to proxy servers controlled by the extension’s developer. If a token was exposed, someone receiving it could potentially act as the account holder without needing the user’s password. The key user…

September 15, 2026
Hijacked HBO Max Reddit Ads Push ClickFix Malware

Hijacked HBO Max Reddit Ads Push ClickFix Malware

Researchers reported that criminals hijacked HBO Max’s verified Reddit account and used it to run malicious ads that led people to fake download sites. The sites didn’t provide real installers, instead they tricked users into pasting and running commands in Terminal/PowerShell, causing them to…

September 15, 2026
HBO Max Reddit Account Hijacked for ClickFix Malware Ads

HBO Max Reddit Account Hijacked for ClickFix Malware Ads

Attackers took over the verified official HBO Max Reddit account and used it to run a 48-hour wave of malicious ads. The ads sent people to lookalike download sites that tricked them into copying and running commands, leading to information-stealing malware on both macOS and Windows. Researchers…

September 15, 2026
HBO Max Reddit Hijack Pushed ClickFix Malware

HBO Max Reddit Hijack Pushed ClickFix Malware

Attackers took over the verified HBO Max Reddit account and ran over 100 malicious ads that sent people to fake download pages. The pages used a ClickFix-style trick: users were told to copy/paste a command into macOS Terminal (and similar OS-targeted lures) to install information-stealing malware.

September 14, 2026
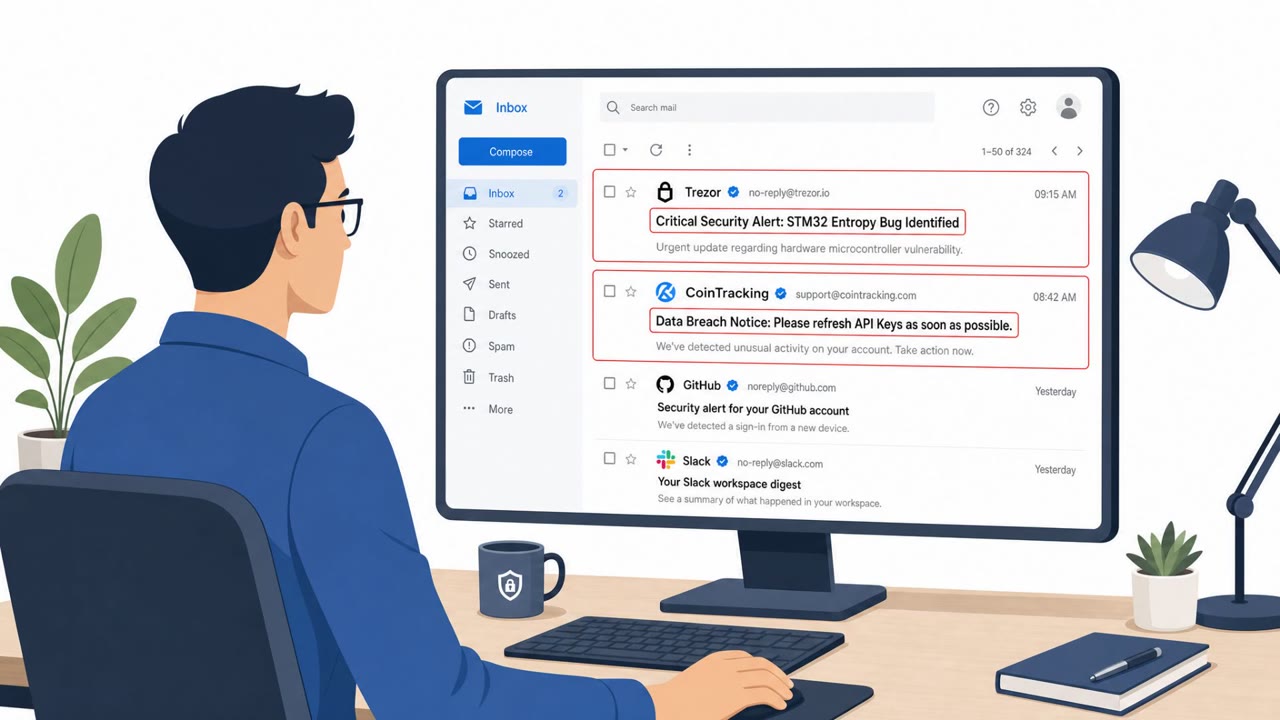
Trezor Users Hit by Phish via Brevo Breach

Trezor Users Hit by Phish via Brevo Breach

Attackers broke into Brevo, the email platform Trezor uses for newsletters, and sent a phishing “security warning” from Trezor’s real mailing system. The email claimed a serious hardware issue could expose wallet recovery seeds and pushed people to a malicious site/app that asked for a wallet…

September 14, 2026
Fake Downloads and Extensions Steal Sessions Fast

Fake Downloads and Extensions Steal Sessions Fast

The article highlights real, ongoing campaigns where attackers trick people into installing malware via fake software-download websites and a disguised browser extension. These lures are used to steal credentials, browser cookies, and authenticated sessions, letting attackers take over accounts…

September 11, 2026
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
Brevo Breach Fuels Crypto Newsletter Phishing

Brevo Breach Fuels Crypto Newsletter Phishing

Attackers abused access to Brevo (an email marketing platform) to send highly convincing phishing emails from legitimate cryptocurrency company domains to newsletter subscribers. The lures claimed urgent security issues (hardware vulnerability or data breach) and pushed victims to click links,…

September 11, 2026
N0va Device-Code Phish Steals Microsoft Sessions

N0va Device-Code Phish Steals Microsoft Sessions

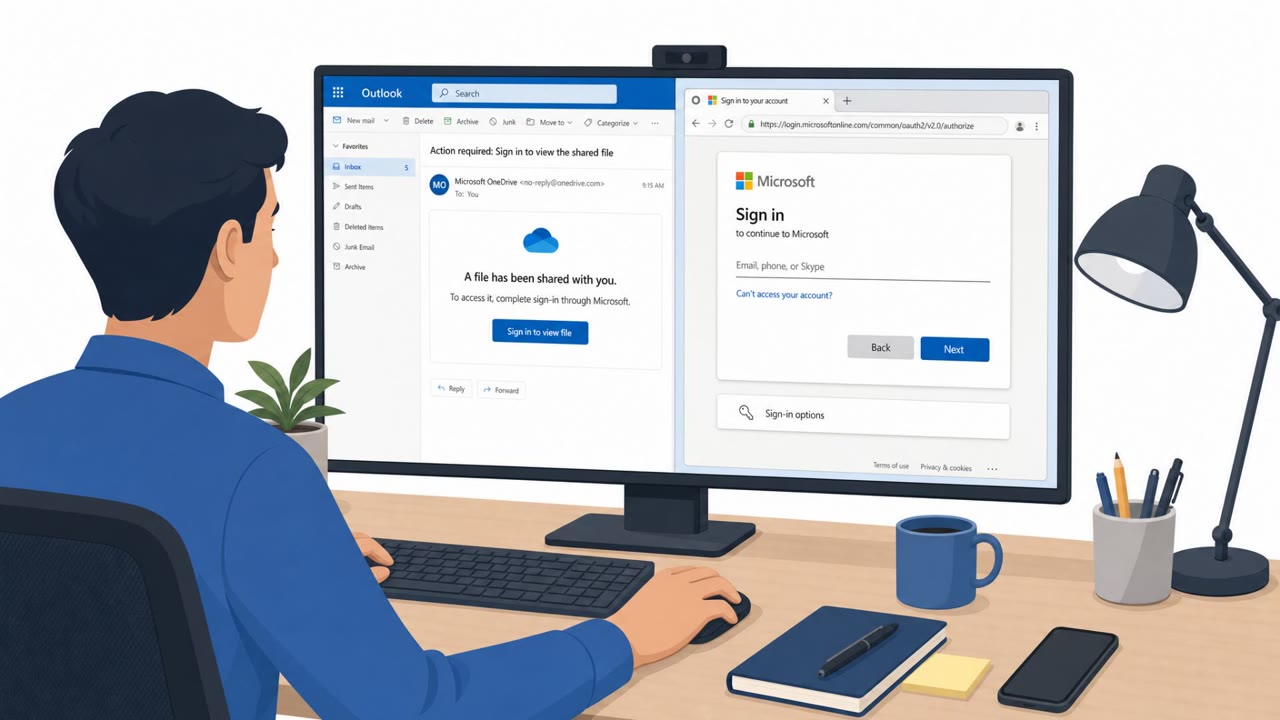
Researchers reported a real phishing operation (“N0va” phishkit) that tricks people into signing into Microsoft through a legitimate Microsoft page, but for an attacker-started session. Victims can complete MFA and still grant the attacker access and refresh tokens, letting the attacker operate as…

September 11, 2026
Iranian Hackers Use Fake Recruiter Coding Test

Iranian Hackers Use Fake Recruiter Coding Test

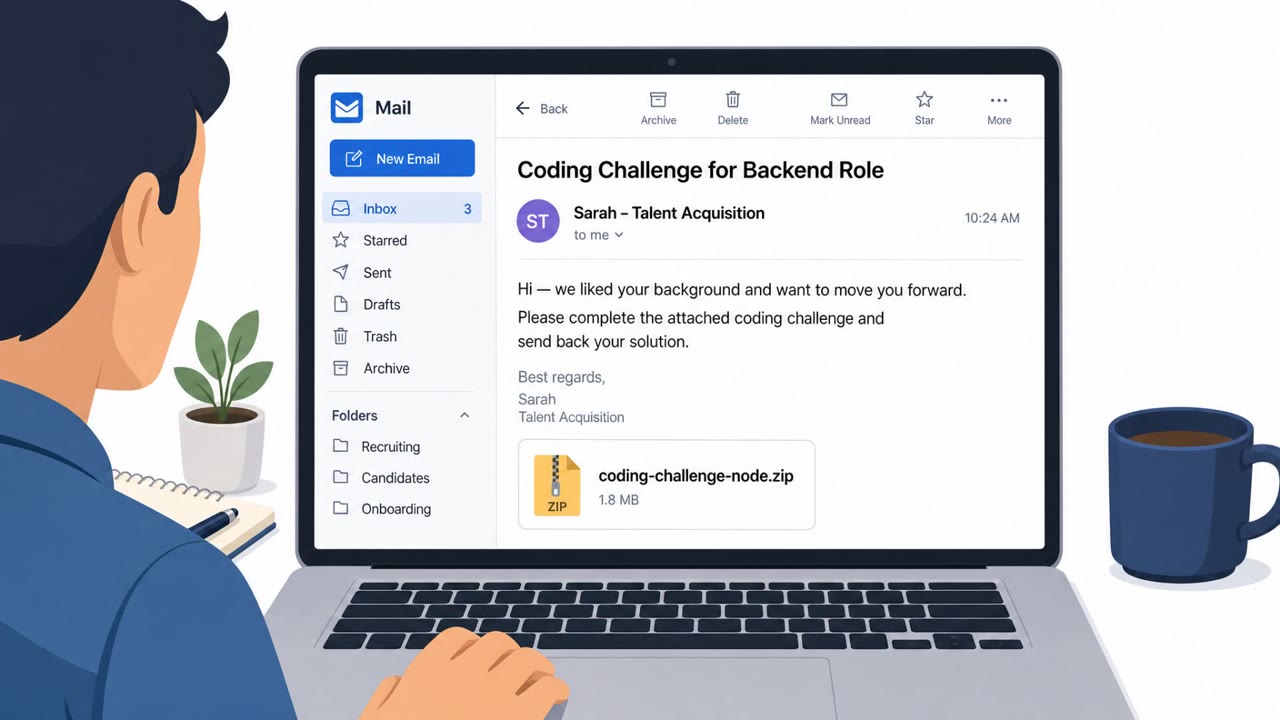
A suspected Iranian government-backed hacking group approached people while pretending to be recruiters, then used a “coding challenge” as the hook to get targets to run malicious code. Victims were sent a ZIP file containing a trojanized Node.js project that infects the machine when it’s…

September 11, 2026
Trezor Users Hit by “Critical Security Alert” Phish

Trezor Users Hit by “Critical Security Alert” Phish

Trezor reported that about 347,000 customers received phishing emails after attackers abused a breach at its third‑party email marketing provider, Brevo. The phishing message used a “Critical Security Alert” theme and linked to a malicious site that attempted to trick users into entering their…

September 11, 2026
One-Click Sogou Link Trick Dropped GRAYRABBIT

One-Click Sogou Link Trick Dropped GRAYRABBIT

Researchers reported a real intrusion where a China-linked group used a crafted link to exploit Sogou Input Method on Windows and install the GRAYRABBIT backdoor. Victims were lured into opening a special link (potentially via email or chat), which redirected Sogou’s built-in browser to an…

September 11, 2026
Fraudsters Can Remotely “Brick” Phones for $3

Fraudsters Can Remotely “Brick” Phones for $3

Researchers showed that attackers can abuse mobile carriers’ “lost/stolen phone” reporting process to get devices blocked from the cellular network, even when the devices were never lost. With only a prepaid account and a target device’s IMEI number, blocking can cost just a few dollars and take…

September 11, 2026
Crypto Newsletter Breach Triggers Fake Security Emails

Crypto Newsletter Breach Triggers Fake Security Emails

Attackers abused access to a third-party email newsletter provider to send convincing “security alert” emails from legitimate-looking crypto company domains. The emails pushed users to click links that led to phishing sites designed to look nearly identical to real platforms. Trezor, CoinTracking,…

September 10, 2026
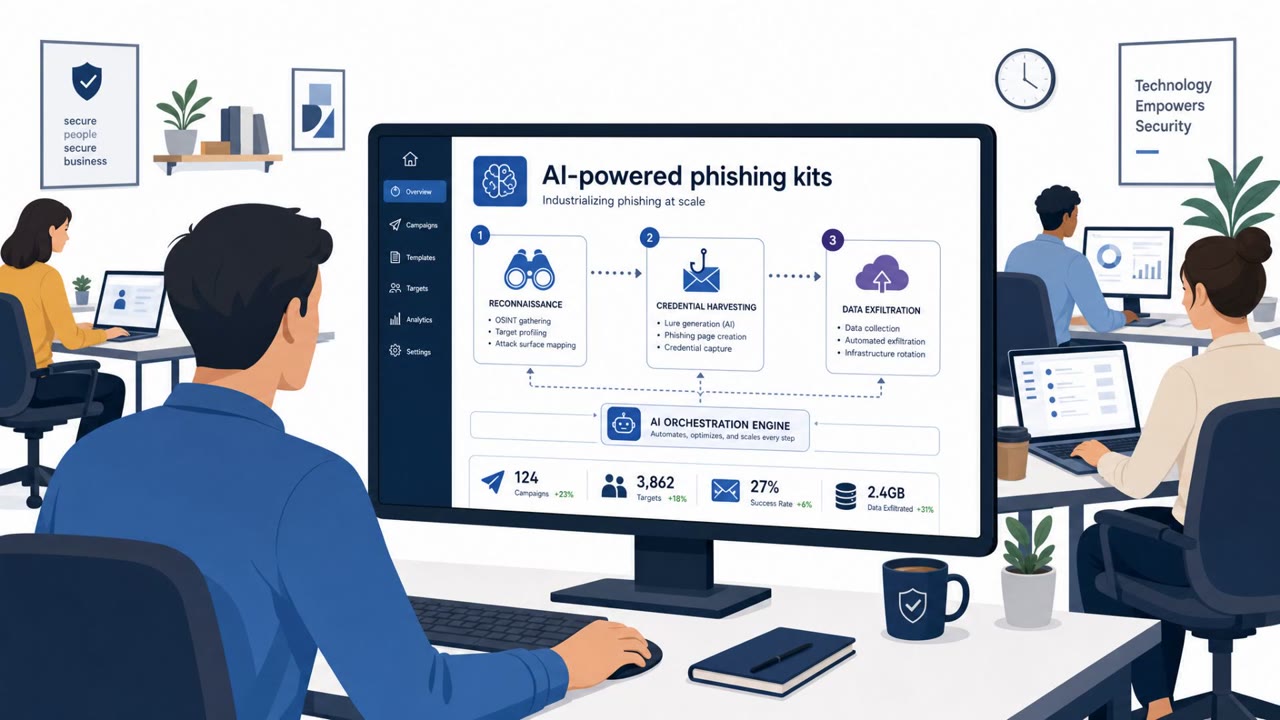
AI Brands Used as Bait in Phishing Waves

AI Brands Used as Bait in Phishing Waves

Microsoft Threat Intelligence reports real campaigns where attackers impersonate popular AI tools (like ChatGPT, Copilot, DeepSeek, and Claude) to trick people into clicking links, installing fake software, or entering payment and login details. One campaign sent up to 100,000 emails in a day to…

September 10, 2026
Poisoned GitHub Issues Hijack AI Agent Tokens

Poisoned GitHub Issues Hijack AI Agent Tokens

Researchers described a real-world style attack where text posted in a GitHub issue was treated as an instruction by an AI agent, leading the agent to use a victim’s token to access private repositories. The article also highlights common weak setups in MCP integrations, overbroad permissions,…

September 10, 2026
Early Access Loophole Floods Play Store With Scams

Early Access Loophole Floods Play Store With Scams

Researchers say criminals are abusing Google Play’s “Early Access” program to distribute deceptive apps that promise cash, rewards, or casino winnings. The apps are promoted through social media ads (including AI celebrity deepfakes) and use a “never-ending payout” loop to keep people watching ads…

September 10, 2026
Fake Reward Apps Abuse Google Play Early Access

Fake Reward Apps Abuse Google Play Early Access

Researchers say scammers are using Google Play’s “Early Access” listings to push deceptive Android apps that don’t show public ratings or warnings. Victims are lured by TikTok/Facebook ads promising cash rewards or free casino spins, but the apps primarily bombard users with ads and never deliver…

September 10, 2026
Brevo Breach Sparks Trezor Phishing Wave

Brevo Breach Sparks Trezor Phishing Wave

Trezor said attackers breached its third-party email provider (Brevo) and gained access to Trezor’s email domain, triggering phishing emails to subscribers. The scam emails used a fake “critical security alert” about a supposed microcontroller vulnerability and attempted to trick users into handing…

September 10, 2026
Instagram Copyright Strikes Used for Ransom

Instagram Copyright Strikes Used for Ransom

Scammers are filing fake copyright complaints to get Instagram accounts temporarily suspended, then demanding money to “withdraw” the complaint and restore access. Victims are pushed to communicate off-platform (for example, on Telegram) and asked to pay in cryptocurrency, yet even paying doesn’t…

September 10, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo