Recent Transportation and Logistics Cyber Attacks

Page 4 of 5
Fake IT Help Desk Calls Hit Private Equity

Fake IT Help Desk Calls Hit Private Equity

Researchers say a threat group tracked as UNC6671 is calling employees and posing as IT help desk staff to steal login credentials and multi-factor authentication (MFA) tokens. After gaining access, the attackers reportedly exfiltrate large amounts of corporate data and then issue extortion…

August 11, 2026
Ransomware Groups Impersonate IT Support on Teams

Ransomware Groups Impersonate IT Support on Teams

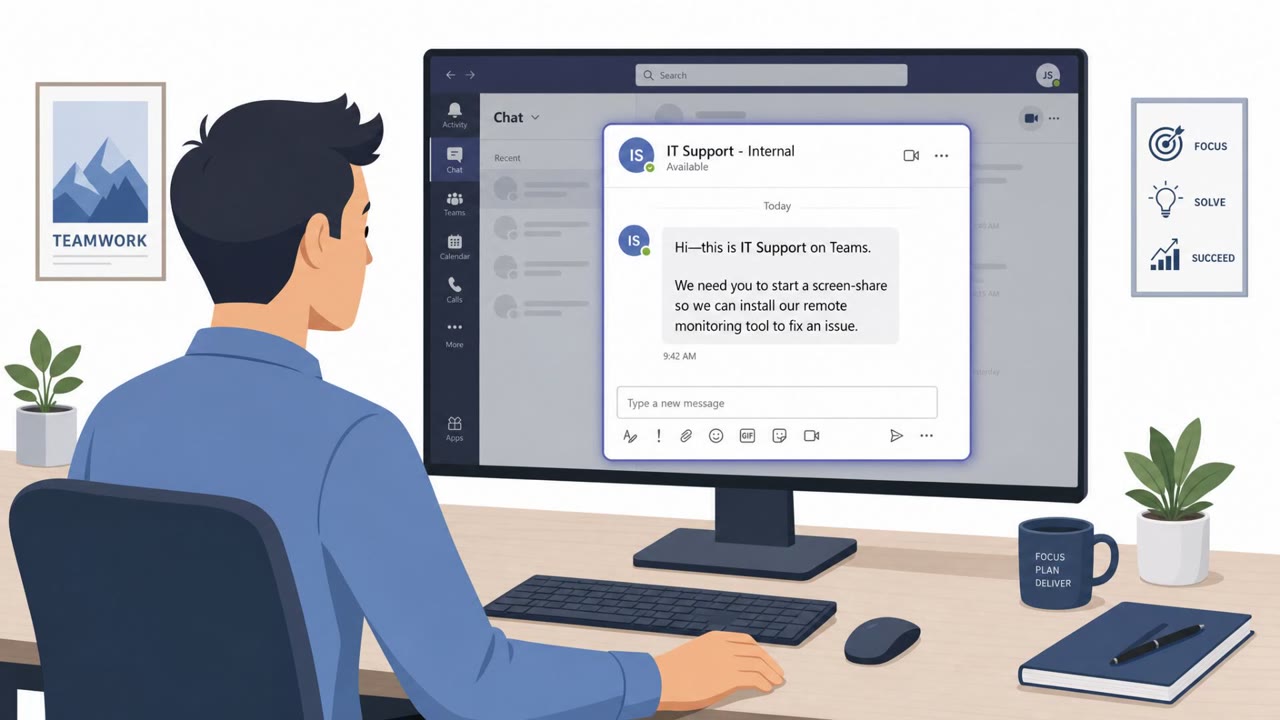
Dragos reports that ransomware operators are increasingly disrupting industrial production by targeting the business IT systems that support operations, even without touching industrial control systems. The report highlights real-world social engineering where attackers impersonate internal IT on…

August 11, 2026
UNC6671 Calls Staff to Steal SaaS Logins

UNC6671 Calls Staff to Steal SaaS Logins

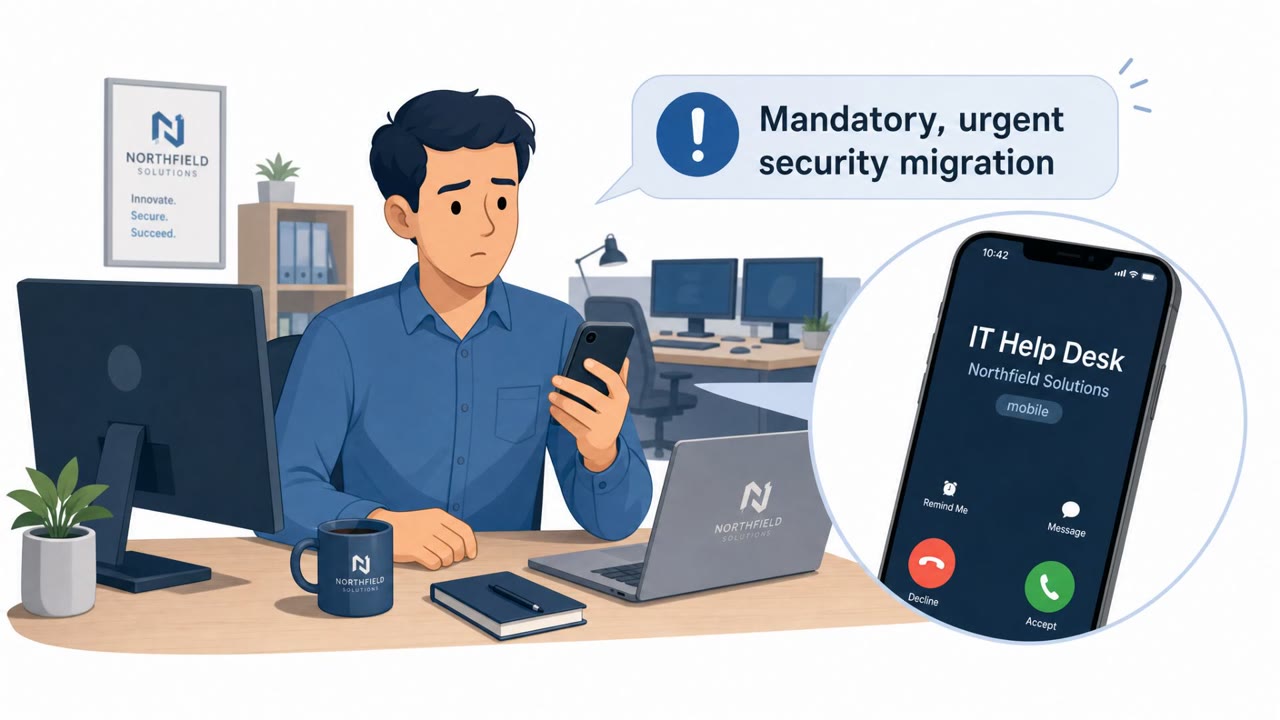
UNC6671 is running real-world voice phishing (vishing) campaigns where callers impersonate IT help desk staff and create urgency around “mandatory” security changes. Victims are pushed to spoofed login pages that capture passwords and MFA codes, enabling attackers to access and steal data from SaaS…

August 7, 2026
Phishing Hits M365; Deepfake Vishing Targets Funds

Phishing Hits M365; Deepfake Vishing Targets Funds

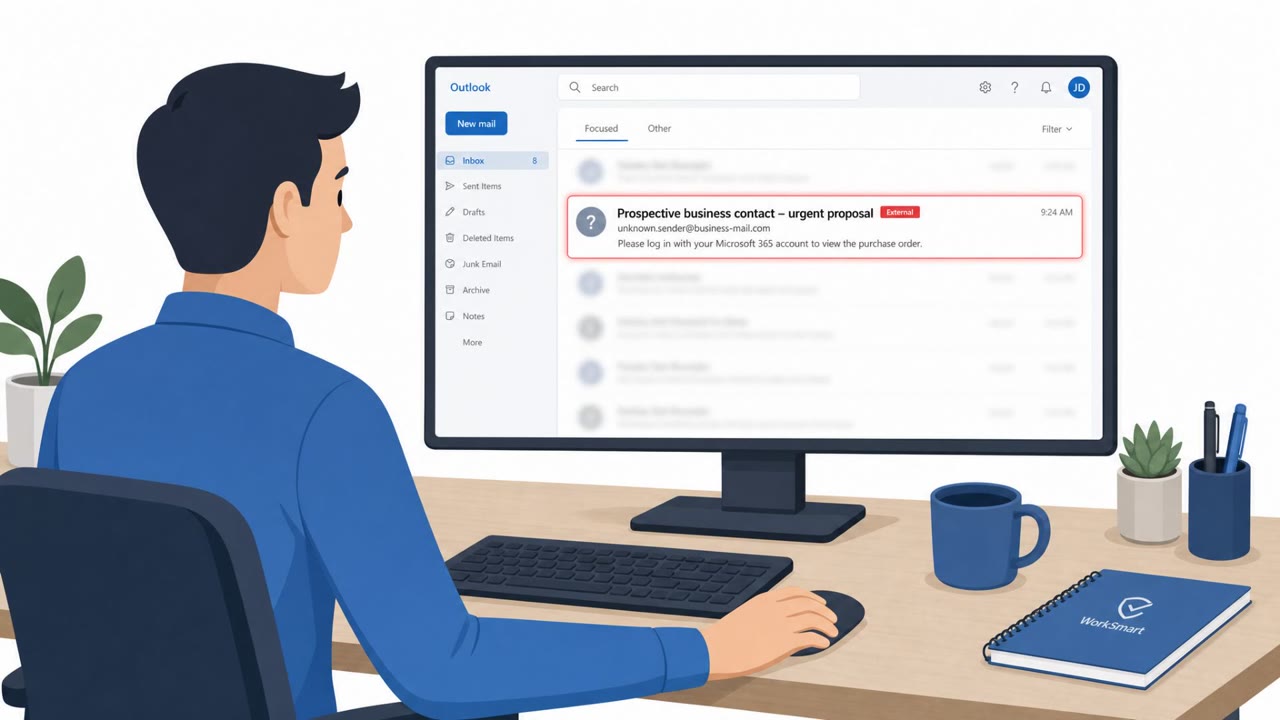
The roundup describes real social-engineering incidents: a phishing email that led an employee to enter credentials on a fake Microsoft 365 login page, and a wave of voice-phishing attempts against major hedge funds using voice-mimicking technology. Both incidents show practical lures that can be…

August 7, 2026
Redact Rebrand Uses IT Helpdesk Vishing

Redact Rebrand Uses IT Helpdesk Vishing

Google says the BlackFile extortion group (UNC6671) rebranded to “Redact” while keeping the same core scam: phone calls that impersonate IT helpdesk staff and push “urgent security migrations.” Victims are directed to spoofed login pages that steal passwords and MFA codes, enabling attackers to…

August 7, 2026
Hackers Recruit Insiders With Cash and Referrals

Hackers Recruit Insiders With Cash and Referrals

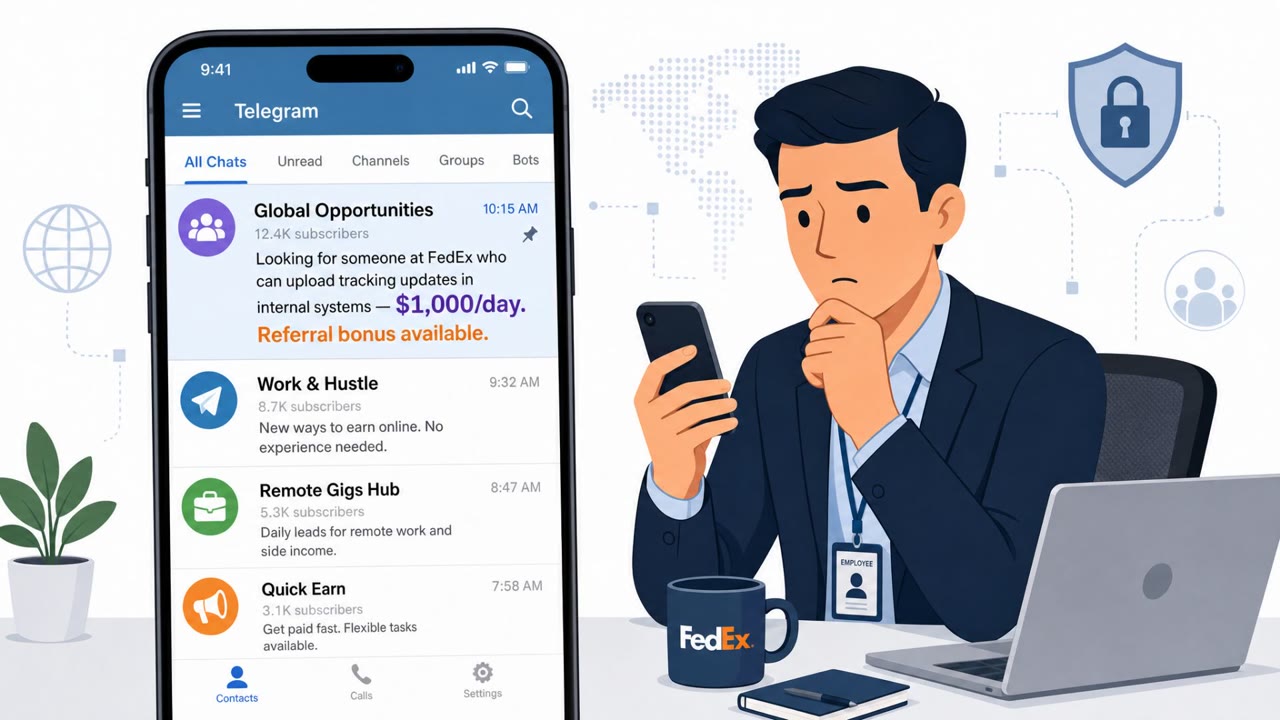
A TrendAI (Trend Micro) report describes a structured underground market where criminals recruit employees to provide access, approve transactions, and bypass controls, often via Telegram and hacking forums. The article gives concrete examples (e.g., paying a FedEx employee $1,000/day to update…

August 7, 2026
UNC6671 Vishing: Fake IT Passkey ‘Migration’ Scam

UNC6671 Vishing: Fake IT Passkey ‘Migration’ Scam

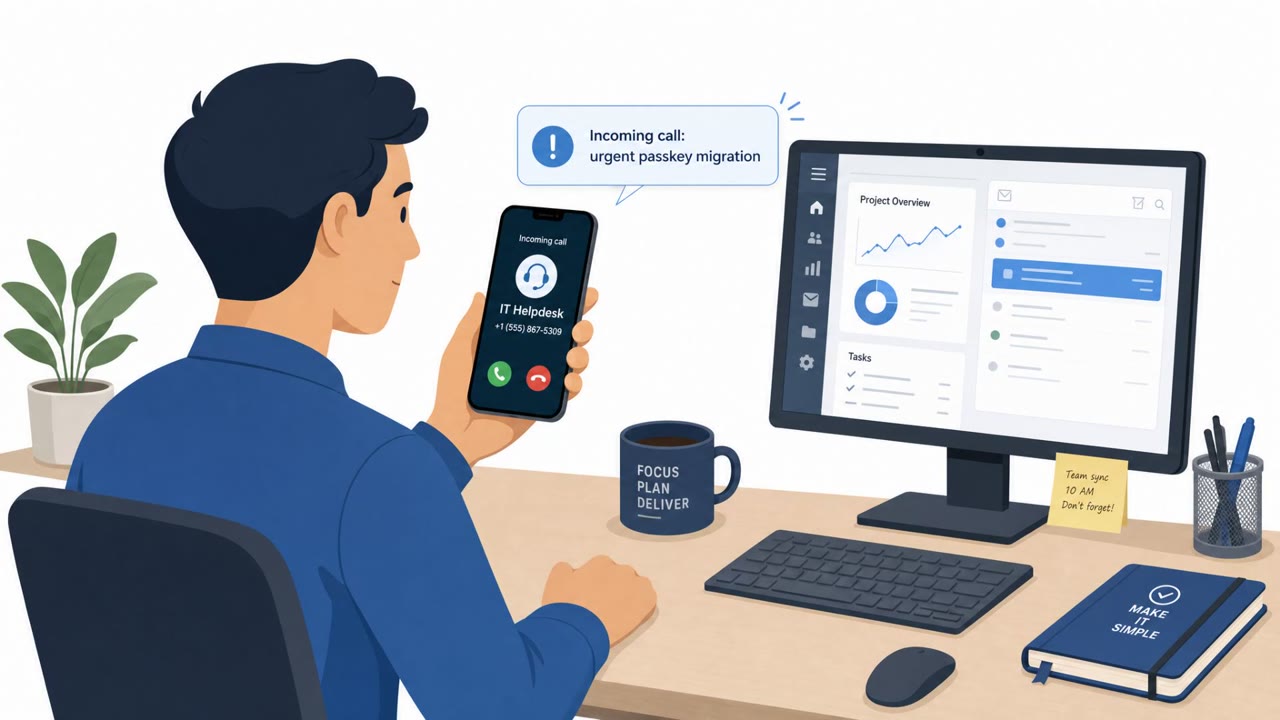
Google reports UNC6671 is still actively compromising organizations by calling employees and pretending to be IT helpdesk staff running an urgent security migration. Victims are pushed to visit lookalike login pages that steal passwords and MFA codes, which then enables data theft and extortion…

August 6, 2026
Telegram Dating Bot Used to Recruit Young Saboteurs

Telegram Dating Bot Used to Recruit Young Saboteurs

Russian authorities allege Telegram was used to recruit and pressure young people into real-world attacks, with “Ukrainian agents” posing as young women via a popular Telegram dating chatbot. The article describes a concrete manipulation workflow (romance/entrapment → coercion) that led to arrests…

July 29, 2026
Clone Websites Trick Firms Into Paying Fake Invoices

Clone Websites Trick Firms Into Paying Fake Invoices

Researchers described a long-running fraud campaign where criminals clone real Russian company websites and replace contact and bank details to intercept international business deals. Victims are lured through cold calls, phishing emails, and fake supplier websites, then sent realistic contracts…

July 29, 2026
Telegram Dating Bot Used for Romance-to-Arson Scam

Telegram Dating Bot Used for Romance-to-Arson Scam

Russia’s FSB claims Ukrainian intelligence used a Telegram dating chatbot to deceive and psychologically pressure young Russians into sharing locations, clicking phishing links, and later carrying out arson or armed attacks. The alleged scheme started with romance-style outreach and payments via…

July 29, 2026
“Work Panel” Streamlines Vishing Into One Console

“Work Panel” Streamlines Vishing Into One Console

Okta says it gained an inside look at “Work Panel,” a polished SaaS-style dashboard that helps voice-phishing (vishing) crews rapidly set up fake login sites and guide victims through password and MFA capture. The tool clones brand look-and-feel for services like Okta and Microsoft 365, then lets a…

July 29, 2026
Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Researchers report Mirage Kitten (an espionage-focused threat group) targeted organizations in the Middle East and Africa using highly tailored spear‑phishing. The lures included recruitment-themed messages impersonating trusted brands/hiring sites and fake videoconferencing pages that redirected…

July 28, 2026
Fake ShinyHunters Sextortion Demands $2,000

Fake ShinyHunters Sextortion Demands $2,000

A sextortion email campaign is using real leaked email addresses from ShinyHunters-related data dumps to make threats sound credible. The scammers impersonate the “ShinyHunters hacking group,” claim they recorded victims via webcam, and demand $2,000 in Bitcoin within 48 hours. Reporting indicates…

July 27, 2026
Zero-Click Emails Hit Zimbra Users in Espionage Push

Zero-Click Emails Hit Zimbra Users in Espionage Push

Government agencies and security firms warn that Russia-aligned hackers are using “zero-click” phishing emails to compromise organizations using Zimbra webmail. The attack hides a malicious JavaScript payload inside an email so it runs when the message is opened, aiming to steal recent email,…

July 23, 2026
Zero-Click Zimbra Webmail Phish Hits NATO Sectors

Zero-Click Zimbra Webmail Phish Hits NATO Sectors

Researchers at Unit 42 reported a real espionage campaign targeting organizations using Zimbra webmail, including government, defense, transportation and financial sectors. The attackers sent “zero-click” phishing emails disguised as news headlines, where opening/viewing the message could trigger a…

July 23, 2026
“TTF Trap” Uses Fake Font Files to Drop Malware

“TTF Trap” Uses Fake Font Files to Drop Malware

FortiGuard Labs reports an active phishing operation (“TTF Trap”) where emails posing as invoices, shipping documents, or business proposals deliver an archive that ultimately runs malware on Windows. The trick is a file ending in .ttf (TrueType font) that is actually a malicious script executed by…

July 17, 2026
Scattered Spider Duped TfL Helpdesk to Reset 2FA

Scattered Spider Duped TfL Helpdesk to Reset 2FA

UK authorities said two Scattered Spider members accessed Transport for London (TfL) by buying partial employee credentials and then tricking TfL’s helpdesk into resetting an employee password and 2FA. The attackers kept access for several days, escalated privileges, and ultimately exposed customer…

July 16, 2026
Pink Vishing Tricks Staff Into Entra Passkeys

Pink Vishing Tricks Staff Into Entra Passkeys

The “Pink” data extortion group is running a real-world voice phishing campaign targeting employees in Microsoft 365 / Entra ID environments. Callers impersonate the internal IT helpdesk and direct staff to realistic lookalike login sites timed to Microsoft’s passkey-enrollment prompts, enabling…

July 16, 2026
TfL Help Desk Tricked, Hackers Got “Keys”

TfL Help Desk Tricked, Hackers Got “Keys”

Two teen hackers linked to the Scattered Spider collective gained deep access to Transport for London (TfL) by tricking the TfL help desk into resetting remote-access authentication onto a device the attackers controlled. TfL said the intrusion could have caused catastrophic disruption, forced…

July 16, 2026
Fake “Qantas IT Help” Call Led to 5.7M Leak

Fake “Qantas IT Help” Call Led to 5.7M Leak

Australia’s Privacy Commissioner said Qantas’ 2025 breach was triggered by a tech-support phone scam targeting a contact center agent. The caller posed as “Qantas IT help” and coached the agent to take steps in the CRM that actually connected it to a data-extraction tool, enabling theft of customer…

July 16, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo