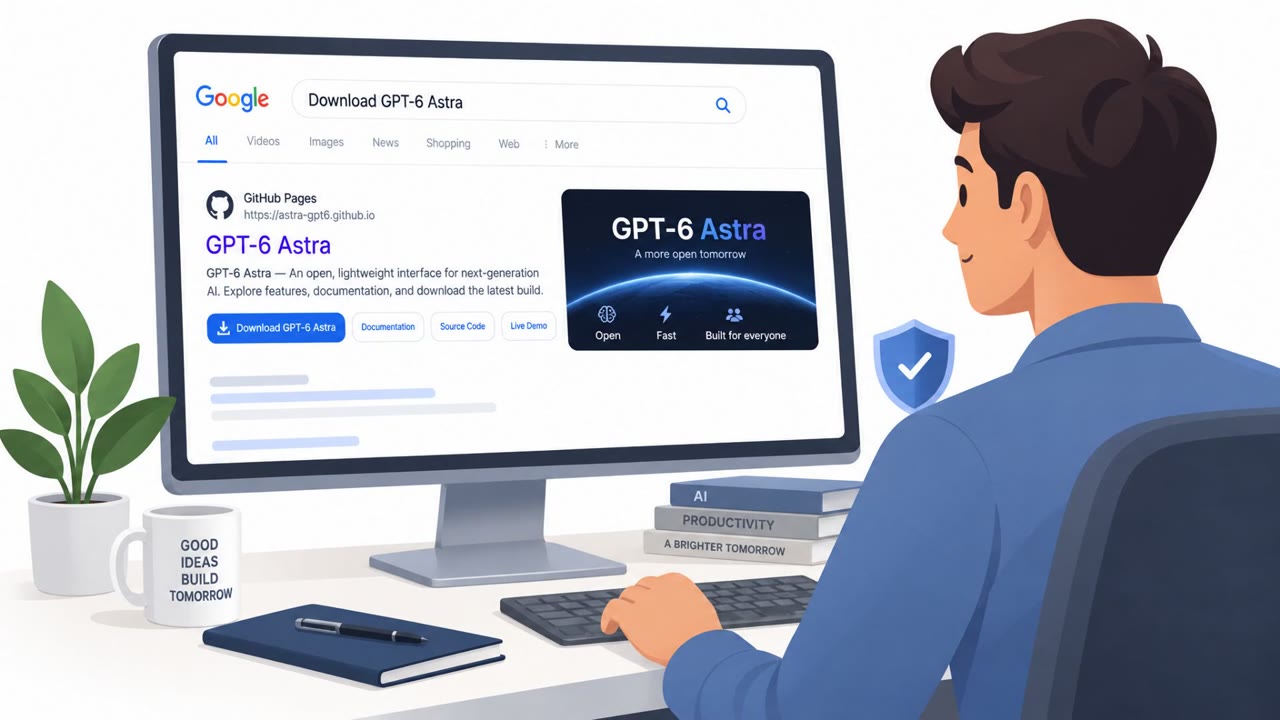
Fake AI Apps Hide Yoba Crypto Miner

Security Affairs · High sophistication
Last updated October 30, 2026

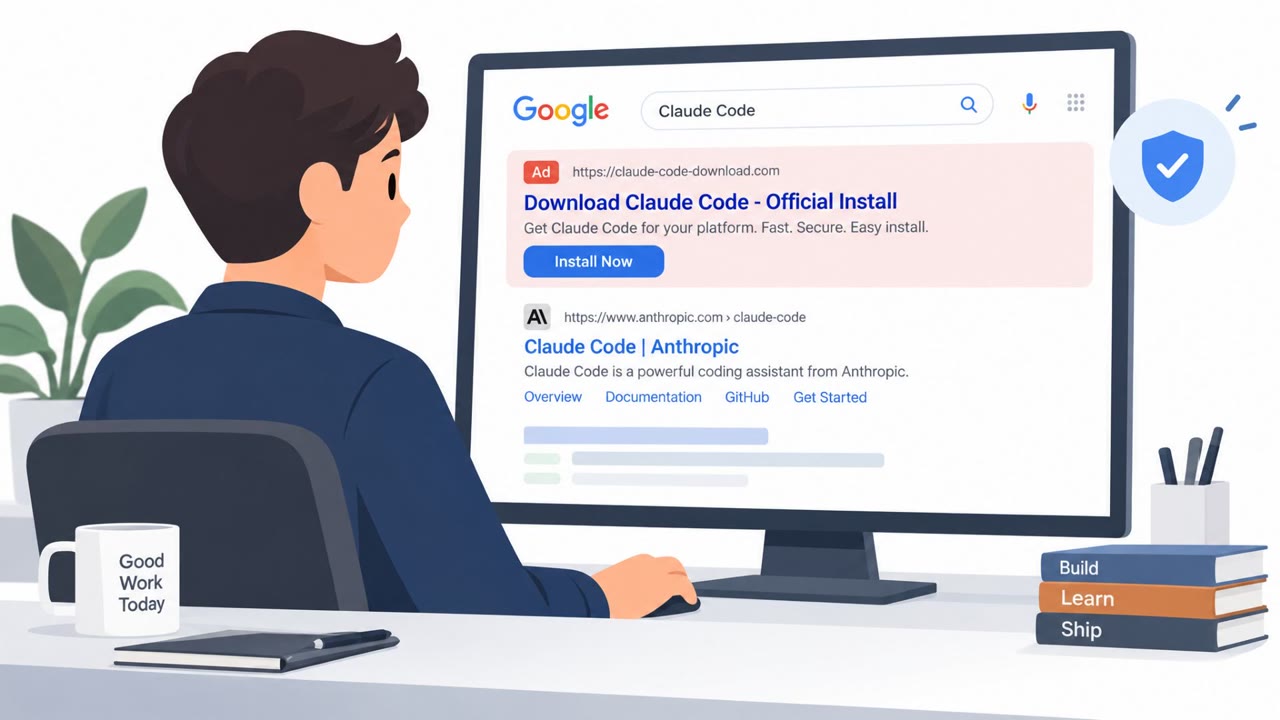
A real campaign called Yoba used fake GitHub projects for supposed ChatGPT and Claude desktop applications to lure people into downloading malicious ZIP installers. The installers included legitimate signed OpenAI or Anthropic programs alongside malicious files, ultimately installing a cryptocurrency miner and giving operators a way to deliver other malware.

Key findings

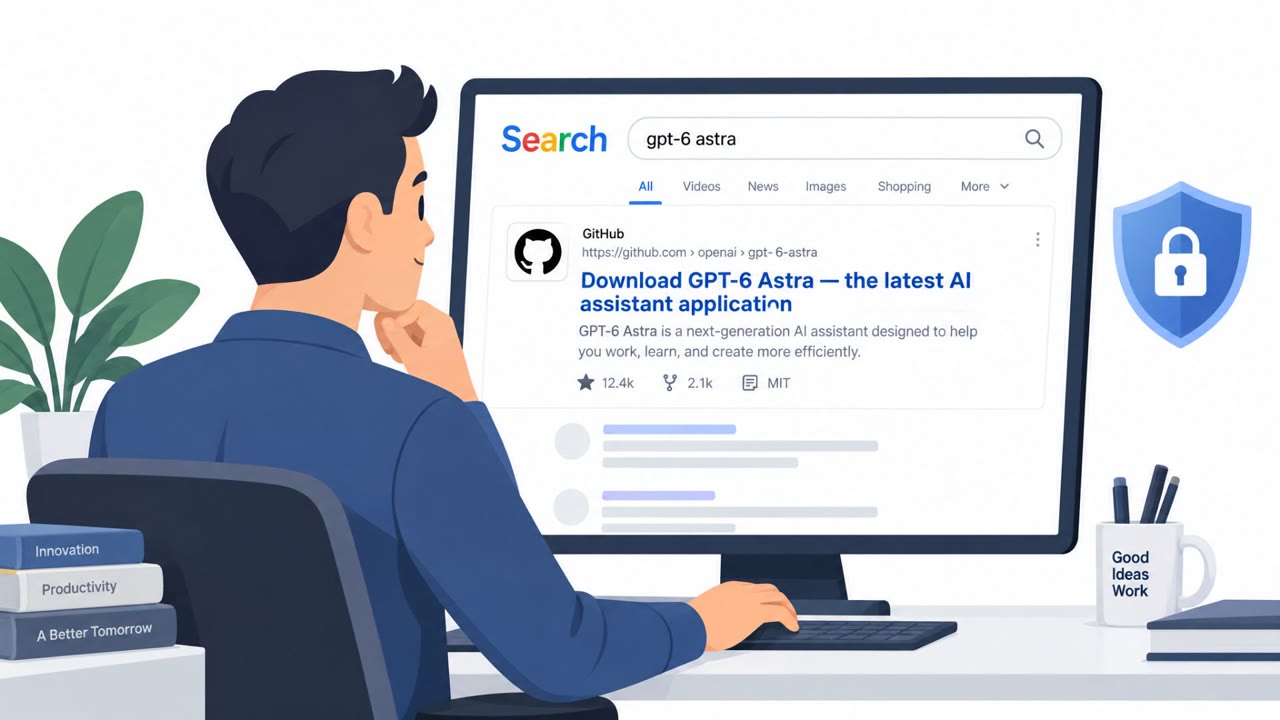
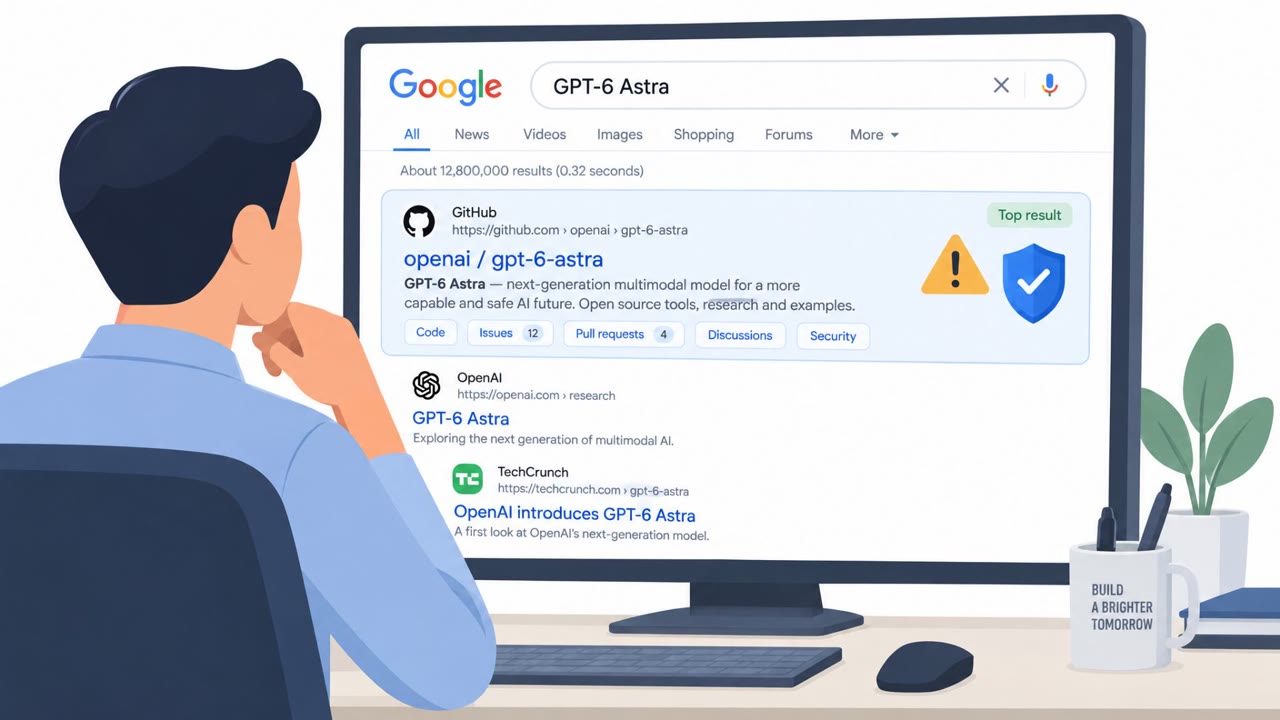
  • Attackers created fake GitHub repositories and GitHub.io pages posing as AI desktop applications, including GPT-5.6 Sol, GPT-6 Astra, and Claude Opus.
  • The fake projects ranked highly in Google search results despite having no fake stars or forks, indicating an SEO-poisoning lure.
  • Victims were led to download ZIP releases containing a legitimate signed OpenAI or Anthropic executable named Setup.exe and a malicious winmm.dll file.
  • The signed executable loaded the malicious DLL, allowing the malware to appear more trustworthy and evade some security checks.
  • The malware requested administrator rights; after a victim reran it as administrator, it established persistence with a fake Microsoft scheduled task.
  • The final payload was an XMRig cryptocurrency miner, but the delivery system can also provide other executable or PowerShell malware.

Who’s being targeted

  • Commonly targeted roles: All employees, Developers, Data analysts, Researchers, IT administrators, Software procurement teams, Security operations teams.
  • Affected industries: Technology, Professional Services, Education, Finance and Insurance, Healthcare, Government, Any organization using or evaluating AI software.
  • Attack channels: website.
  • Impersonated: OpenAI or Anthropic desktop software project, Legitimate OpenAI or Anthropic installer.

Awareness takeaways

  • Download AI tools only from the vendor's verified website or approved internal software catalog, not from search results or unknown GitHub projects.
  • Treat a request to rerun a new application as administrator as a stop-and-verify moment, especially for tools downloaded outside approved channels.
  • Do not assume a file is safe merely because it contains a signed program or uses a recognizable company name.
  • Report unfamiliar AI software downloads that cause unexplained high CPU use or appear to run in the background.

Red flags to watch for

  • The software is offered through an unfamiliar GitHub repository rather than an official vendor download page.
  • The project has no meaningful stars or forks despite appearing prominently in search results.
  • The download is a ZIP archive containing an installer rather than a clearly verified official application package.
  • A downloaded AI tool asks for administrator privileges when that level of access is not expected.
  • The ZIP pairs a trusted-looking executable with an unfamiliar DLL file.
  • The prompt says "Please run this program as Administrator." instead of using a normal, verified software-installation workflow.
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

Searching for a new AI desktop app? Watch this result. Fake GitHub projects for GPT-6 Astra and Claude Opus ranked high in search, despite having no stars or forks. Their ZIP releases offered Setup.exe. Here's the trap: Setup.exe is genuinely signed, but it loads the malicious winmm.dll beside it. Rerun it as administrator, and Yoba installs a crypto miner. A signature doesn't make the ZIP safe. Download AI apps only from the vendor's verified website or our approved software catalog.

MITRE ATT&CK techniques

T1036 - MasqueradingT1574.002 - Hijack Execution Flow: DLL Side-LoadingT1053.005 - Scheduled Task/Job: Scheduled Task · Scheduled Task/JobT1105 - Ingress Tool TransferT1071.001 - Application Layer Protocol: Web ProtocolsT1059.001 - Command and Scripting Interpreter: PowerShell · Command and Scripting InterpreterT1055 - Process InjectionT1496 - Resource Hijacking

Similar attacks

Fake AI Apps Abuse Signed ChatGPT Files

Fake AI Apps Abuse Signed ChatGPT Files

Attackers used fake ChatGPT, Claude, and Cursor AI application listings to trick Windows users into downloading malware. The downloads appeared trustworthy because they were hosted through GitHub and included real, digitally signed OpenAI or Anthropic executables, but malicious files alongside them…

October 28, 2026
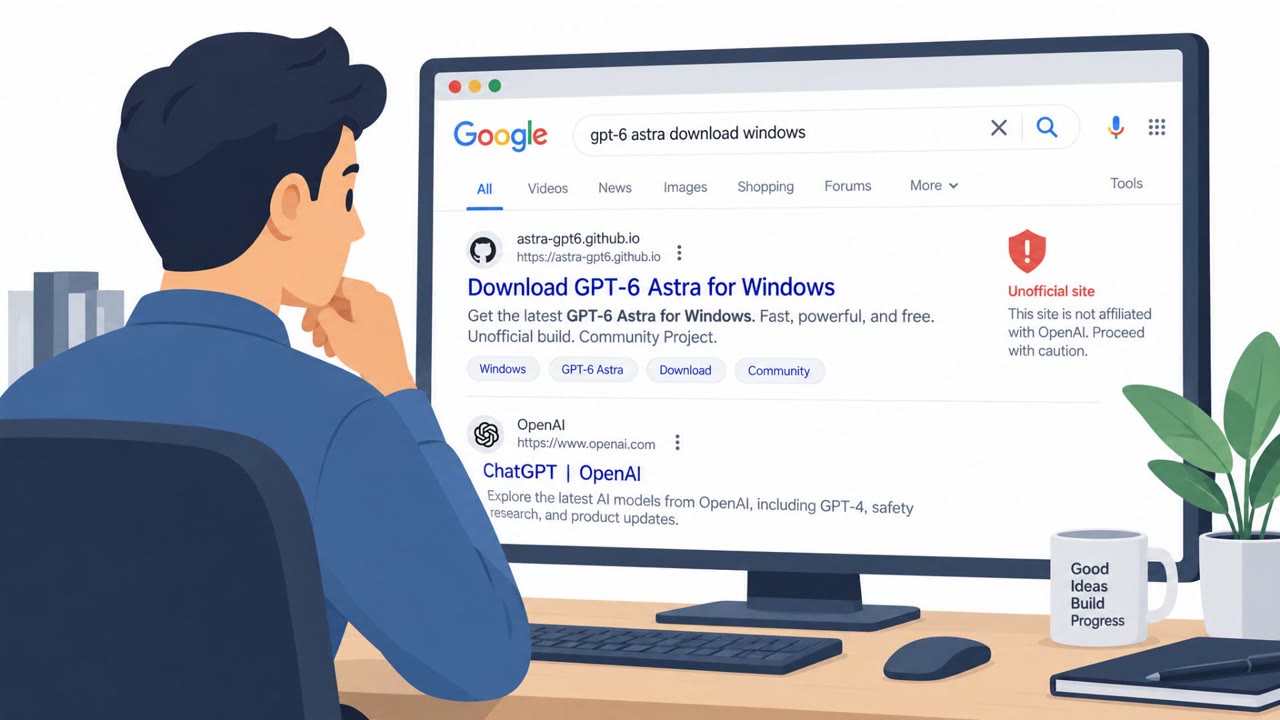
Fake ChatGPT Downloads Hide Yoba Malware

Fake ChatGPT Downloads Hide Yoba Malware

Attackers used GitHub and search results to promote counterfeit ChatGPT and Claude desktop downloads. The ZIP files bundled real signed OpenAI or Anthropic executables with malicious files, tricking Windows users into launching malware that can persist on the device and install a cryptocurrency…

October 29, 2026
Amatera Uses Fake AI Tools to Steal Data

Amatera Uses Fake AI Tools to Steal Data

Amatera is a subscription-based information stealer that affiliates distribute through fake AI-tool download pages, compromised websites, paid search ads, phishing, and deceptive ClickFix prompts. The scams convince people to copy and run a command to supposedly fix a CAPTCHA, browser error, or…

October 30, 2026
Fake AI Apps Use GitHub to Mine Crypto

Fake AI Apps Use GitHub to Mine Crypto

The Yoba malware campaign uses fake GitHub projects and search-result manipulation to make counterfeit ChatGPT and Claude downloads look trustworthy. Victims receive a real, signed installer alongside malware, so the application appears legitimate while the malicious software installs and…

October 30, 2026
Fake AI Apps on GitHub Deliver Yoba Malware

Fake AI Apps on GitHub Deliver Yoba Malware

Check Point Research identified a real campaign, tracked as Yoba, that uses fake GitHub projects and websites posing as new ChatGPT and Claude desktop applications. Victims searching for AI tools can be directed to convincing pages for supposed releases such as GPT-6 Astra and Claude Opus, then…

October 27, 2026
Fake AI Apps on GitHub Deliver Yoba Malware

Fake AI Apps on GitHub Deliver Yoba Malware

A real malware campaign called Yoba used fake GitHub projects advertising supposed ChatGPT and Claude desktop applications. Victims were lured by high-ranking Google results and download buttons, then ran ZIP-packaged installers that appeared legitimate but gave attackers control of the device. The…

October 27, 2026