Recent Cryptocurrency Cyber Attacks

Page 4 of 7
Fake AI Trading Bot Steals Crypto Wallet Passwords

Fake AI Trading Bot Steals Crypto Wallet Passwords

Researchers observed real campaigns where a fake “AI crypto trading agent” website tricked victims into downloading malware that silently replaces browser wallet extensions and steals the wallet password when it’s typed. The same reporting also describes invoice emails using QR codes to push…

September 17, 2026
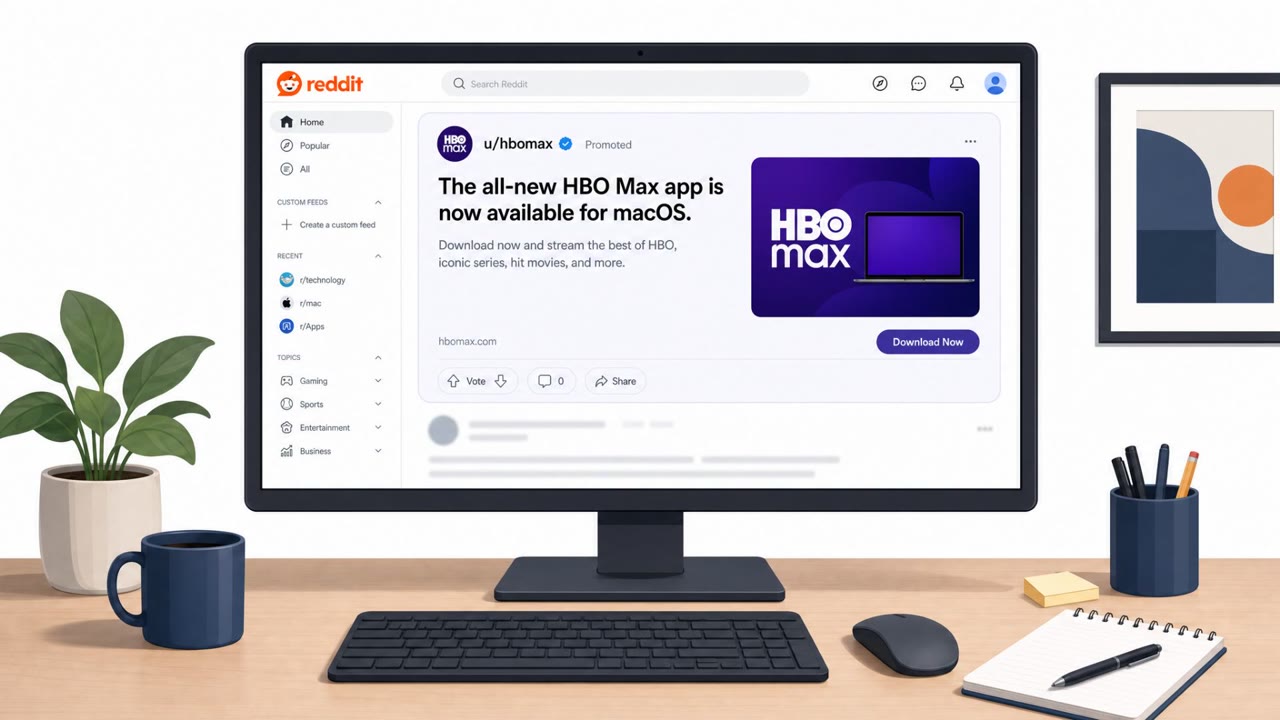
HBO Max Reddit Ads Hijacked to Spread ClickFix Malware

HBO Max Reddit Ads Hijacked to Spread ClickFix Malware

Attackers compromised HBO Max’s verified Reddit advertising account and used it to run 108 malicious ads in about 48 hours. The ads sent people to attacker-controlled websites that used “ClickFix” instructions to trick users into running commands that installed malware on Windows and macOS.

September 16, 2026
HBO Max Reddit Account Hijacked for ClickFix Malware Ads

HBO Max Reddit Account Hijacked for ClickFix Malware Ads

Attackers took over the verified official HBO Max Reddit account and used it to run a 48-hour wave of malicious ads. The ads sent people to lookalike download sites that tricked them into copying and running commands, leading to information-stealing malware on both macOS and Windows. Researchers…

September 15, 2026
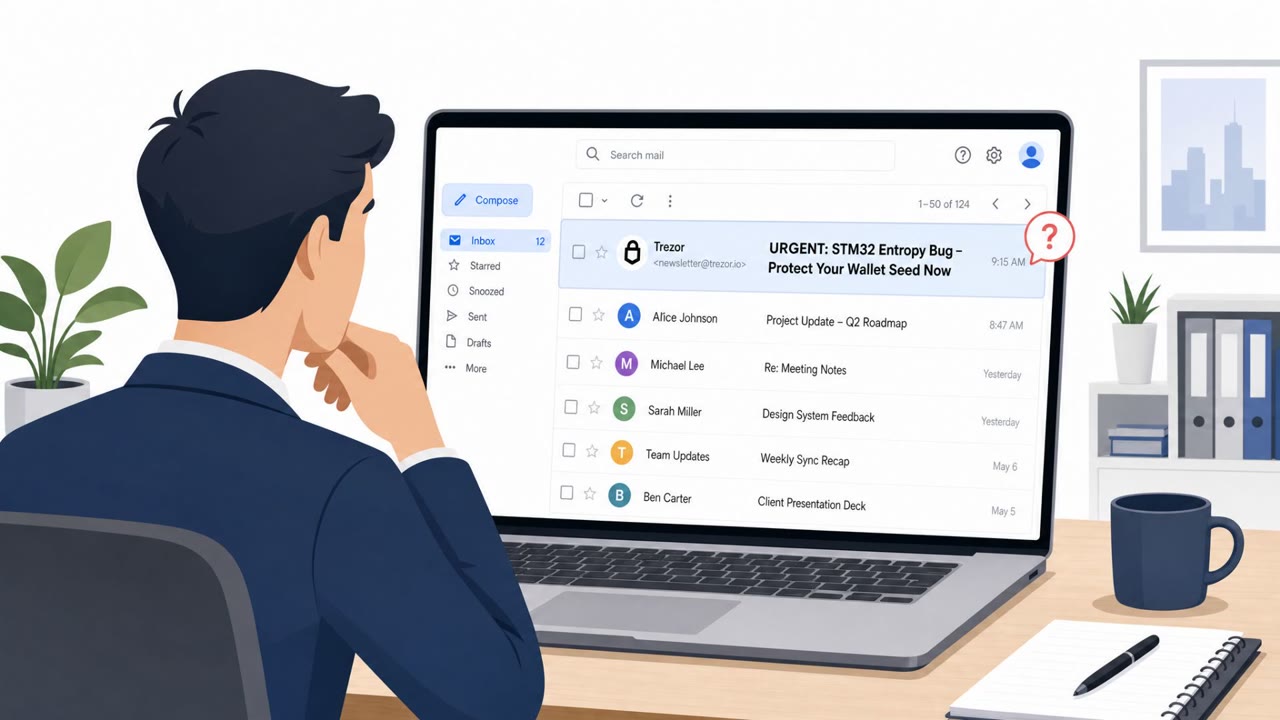
Trezor Users Hit by Phish via Brevo Breach

Trezor Users Hit by Phish via Brevo Breach

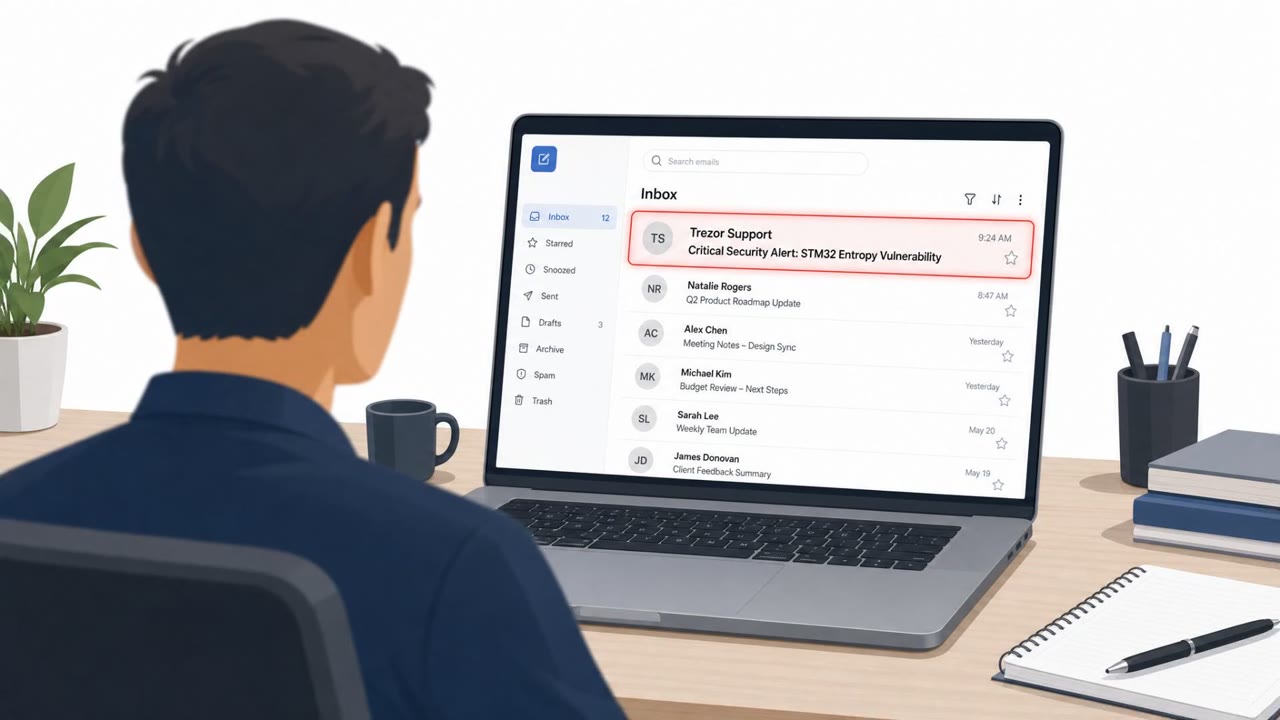
Attackers broke into Brevo, the email platform Trezor uses for newsletters, and sent a phishing “security warning” from Trezor’s real mailing system. The email claimed a serious hardware issue could expose wallet recovery seeds and pushed people to a malicious site/app that asked for a wallet…

September 14, 2026
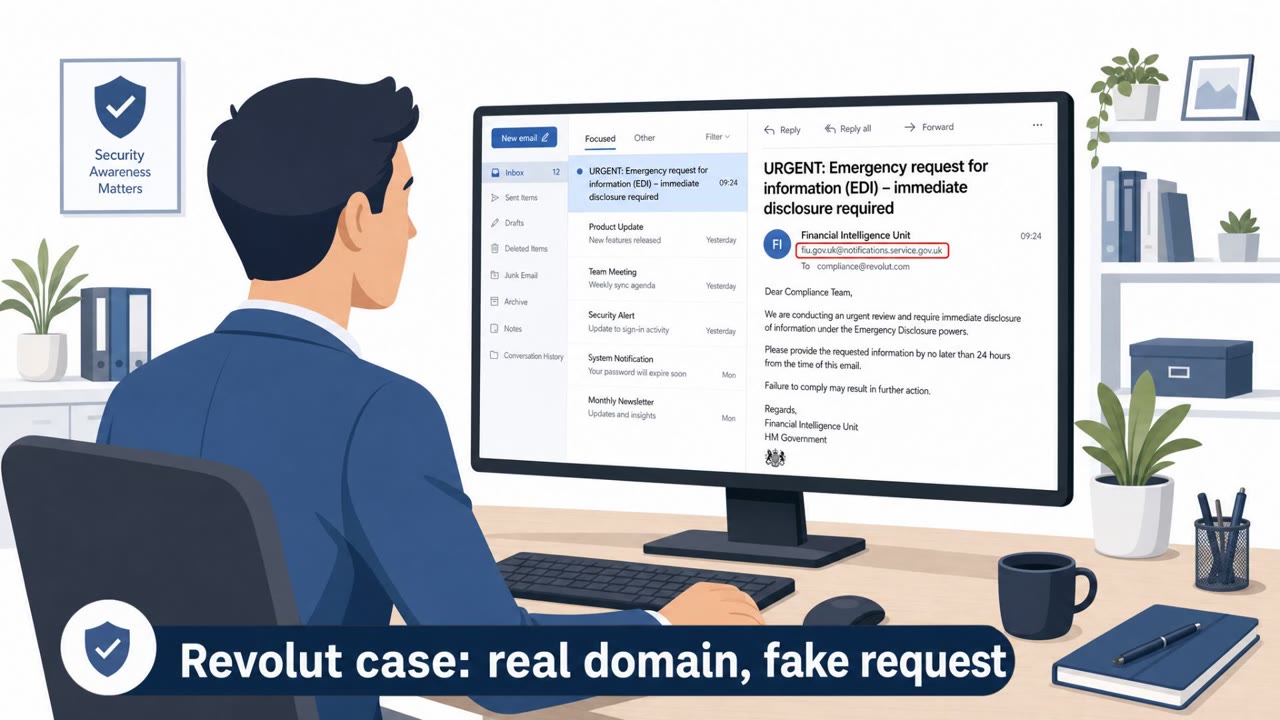
Revolut Tricked by Fake “Emergency” Data Requests

Revolut Tricked by Fake “Emergency” Data Requests

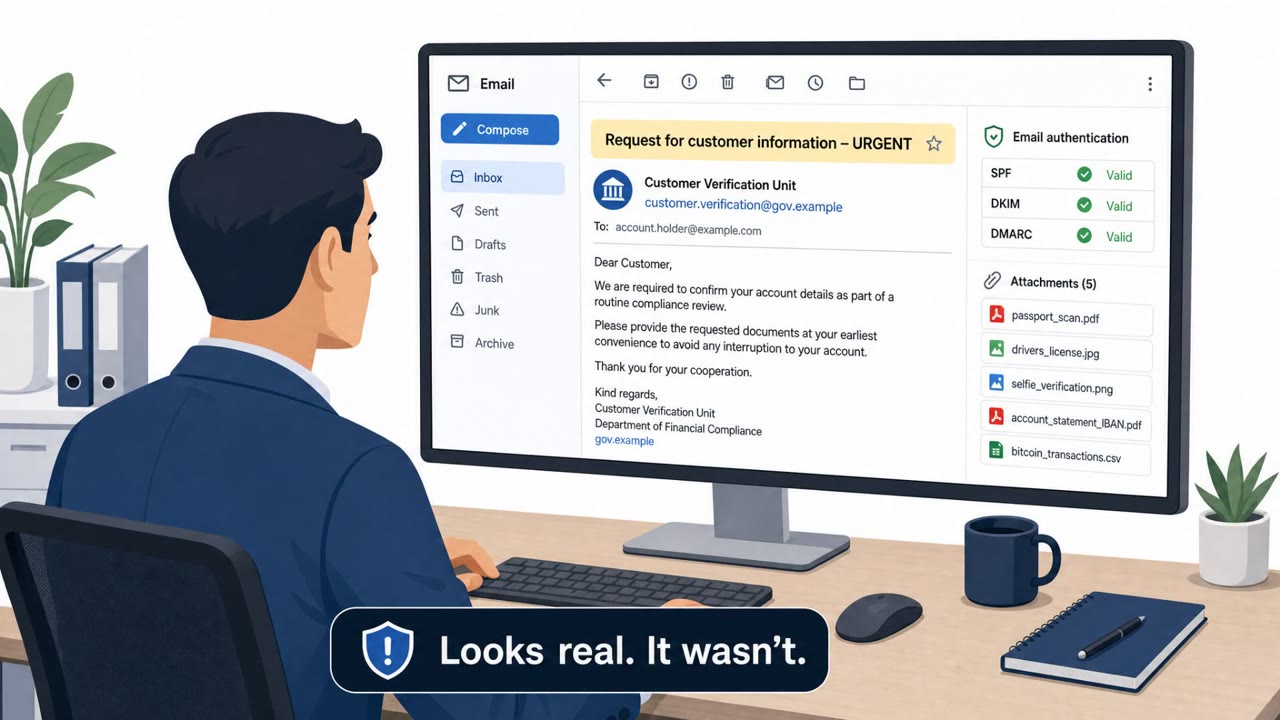
Revolut confirmed it disclosed sensitive customer information after fraudsters sent “emergency” information requests from a legitimate government email domain. The attackers appear to have targeted high-net-worth customers, including people involved in crypto, and attempted to extort Revolut to…

September 14, 2026
Revolut Tricked by Fake Government Email

Revolut Tricked by Fake Government Email

Revolut disclosed it was deceived into sharing highly sensitive customer data after receiving fraudulent information requests that appeared to come from a legitimate government email domain. The attacker’s email passed domain authentication, making it harder to detect, and the shared data may…

September 14, 2026
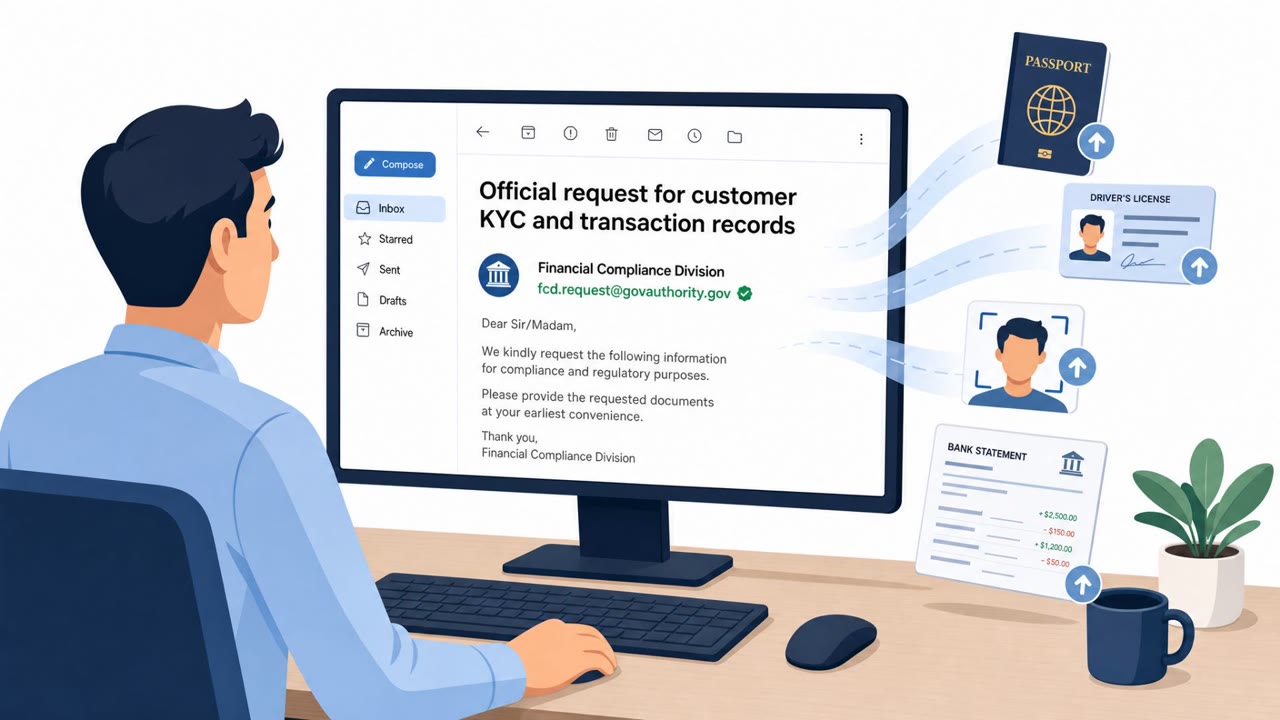
Fake Govt Email Tricked Revolut Into Sharing KYC

Fake Govt Email Tricked Revolut Into Sharing KYC

Revolut says it handed over sensitive customer identity and financial data after receiving what looked like a legitimate government information request. The email came from inside a real government agency’s email domain and passed authentication checks, so staff processed it before later…

September 12, 2026
Brevo Breach Fuels Crypto Newsletter Phishing

Brevo Breach Fuels Crypto Newsletter Phishing

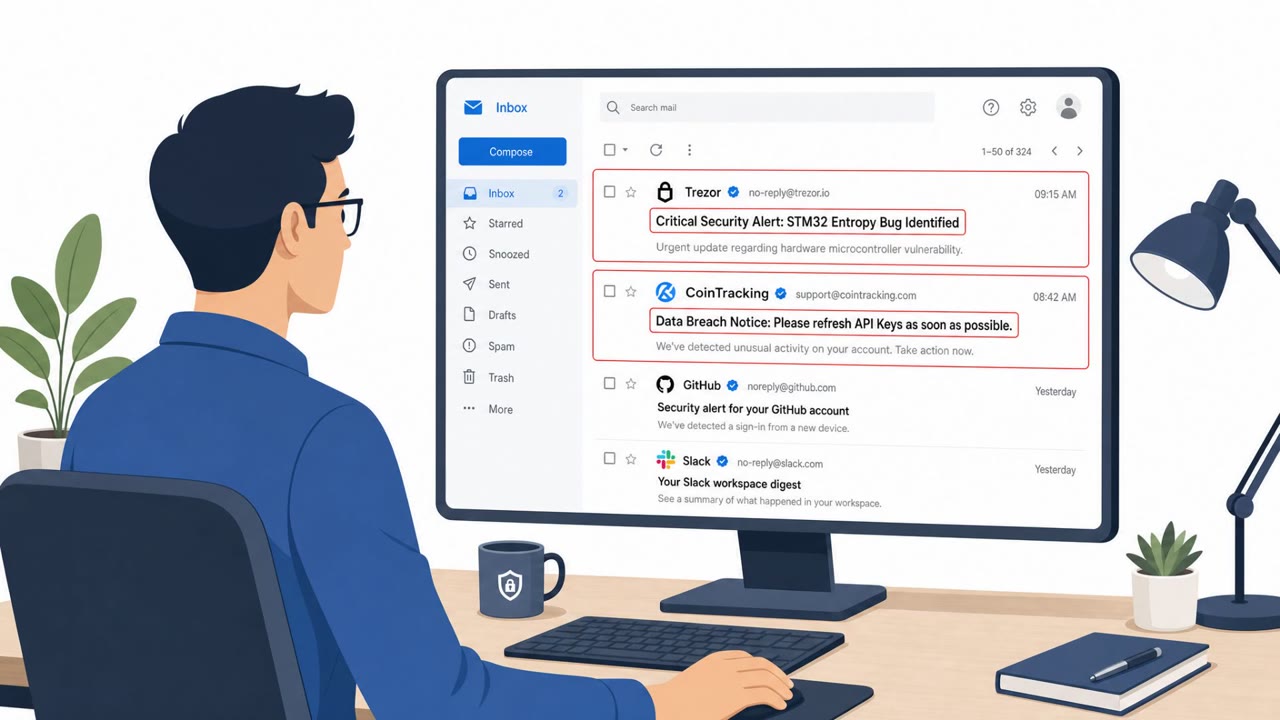
Attackers abused access to Brevo (an email marketing platform) to send highly convincing phishing emails from legitimate cryptocurrency company domains to newsletter subscribers. The lures claimed urgent security issues (hardware vulnerability or data breach) and pushed victims to click links,…

September 11, 2026
Trezor Users Hit by “Critical Security Alert” Phish

Trezor Users Hit by “Critical Security Alert” Phish

Trezor reported that about 347,000 customers received phishing emails after attackers abused a breach at its third‑party email marketing provider, Brevo. The phishing message used a “Critical Security Alert” theme and linked to a malicious site that attempted to trick users into entering their…

September 11, 2026
Pig Butchering Scams Drive $12.7B Crypto Losses

Pig Butchering Scams Drive $12.7B Crypto Losses

FinCEN reports that overseas scam centers stole about $12.7B from U.S. victims since 2023, largely through “pig butchering” style cryptocurrency investment scams. Scammers build trust using fake personas (often romance or “financial adviser” roles), then pressure victims to buy crypto and send it…

September 10, 2026
Fake M&A Wire Fraud and Trezor Phishing Alert

Fake M&A Wire Fraud and Trezor Phishing Alert

This bulletin describes multiple real-world scams where attackers manipulate trust to steal money or sensitive data. Notably, attackers impersonated executives to pressure legal teams into moving M&A discussions to WhatsApp/personal email to trigger international wire transfers, and Trezor users…

September 10, 2026
Crypto Newsletter Breach Triggers Fake Security Emails

Crypto Newsletter Breach Triggers Fake Security Emails

Attackers abused access to a third-party email newsletter provider to send convincing “security alert” emails from legitimate-looking crypto company domains. The emails pushed users to click links that led to phishing sites designed to look nearly identical to real platforms. Trezor, CoinTracking,…

September 10, 2026
Fake Google Support Bait Led to $245M Crypto Theft

Fake Google Support Bait Led to $245M Crypto Theft

A Singaporean man, Malone Lam (aliases including “Anne Hathaway”), pleaded guilty to leading a group that stole over $245 million in cryptocurrency from U.S. victims. The group used social engineering, such as posing as Google Support and using spoofed phone numbers, to trick victims into handing…

September 10, 2026
Brevo Breach Sparks Trezor Phishing Wave

Brevo Breach Sparks Trezor Phishing Wave

Trezor said attackers breached its third-party email provider (Brevo) and gained access to Trezor’s email domain, triggering phishing emails to subscribers. The scam emails used a fake “critical security alert” about a supposed microcontroller vulnerability and attempted to trick users into handing…

September 10, 2026
Crypto Scammers Posed as Apple/Google Support

Crypto Scammers Posed as Apple/Google Support

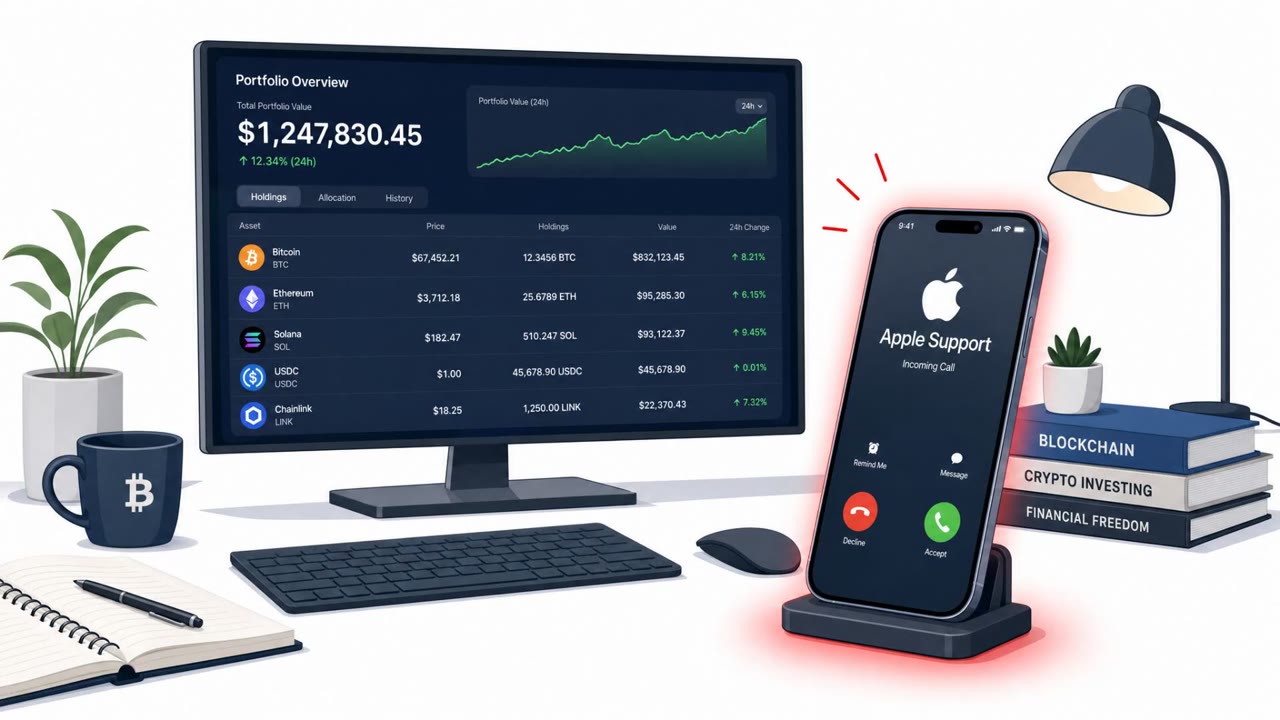
U.S. prosecutors say a group led by Malone Lam ran social engineering scams that stole over $245 million in cryptocurrency. The scammers allegedly called crypto holders while pretending to be customer support from Apple or Google, talked victims into handing over key account details, and in at…

September 8, 2026
Fake Google & Gemini Calls Led to $240M Bitcoin Heist

Fake Google & Gemini Calls Led to $240M Bitcoin Heist

A group of young scammers stole more than $240 million in bitcoin by calling a wealthy crypto investor and impersonating trusted companies. The callers claimed the victim’s accounts and wallet were under attack, then tricked him into granting access and sharing security codes that enabled the…

September 8, 2026
Trezor Users Targeted by Phishing Calls & QR Letters

Trezor Users Targeted by Phishing Calls & QR Letters

After a breach at shipping partner ShipMonk, attackers obtained Trezor customers’ contact and shipping details, increasing the risk of scams. Reports on Reddit indicate customers have already received phishing phone calls and physical letters containing QR-code phishing lures. Trezor warned…

September 8, 2026
Fake “API Exploit” Lures Users Into Self-Hacking

Fake “API Exploit” Lures Users Into Self-Hacking

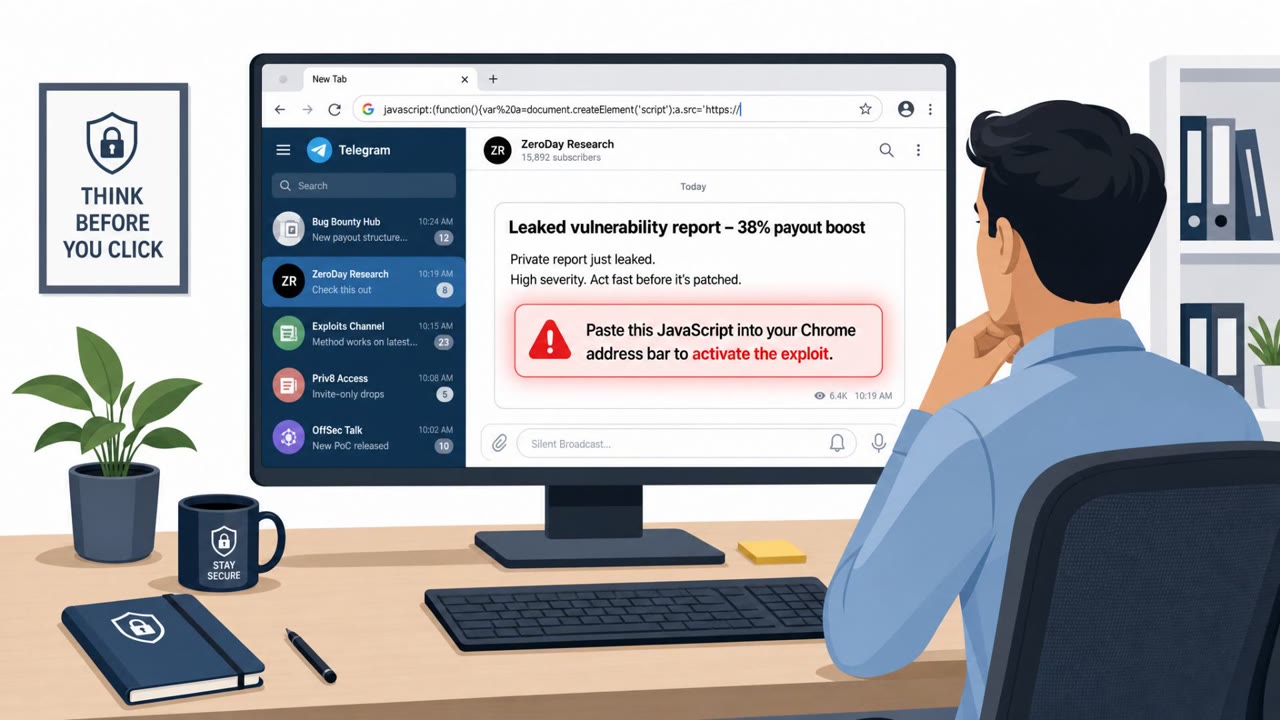
Cisco Talos reports a real cryptocurrency-theft campaign where criminals trick people into pasting JavaScript into their browser or installing it via the Tampermonkey extension. The lure pretends to be a leaked vulnerability report for crypto swap sites, but the “exploit” is fake and instead…

September 8, 2026
ClickFix Lures Users to Paste Code via Browser

ClickFix Lures Users to Paste Code via Browser

Cisco Talos described real ClickFix campaigns where attackers trick people into pasting code either into the Chrome address bar (or a browser extension) or into the Windows Run dialog. The first campaign targeted crypto swap sites and used a fake “leaked vulnerability report” to get victims to run…

September 8, 2026
REVSTEALER Lures Push Fake Cheats, Drop Miners

REVSTEALER Lures Push Fake Cheats, Drop Miners

Researchers tied several new programs to the REVSTEALER Windows info-stealer that can steal crypto wallet data, hijack clipboard crypto addresses, and even disable Windows Update and Microsoft Defender to run a crypto miner. Victims are primarily pulled in through “game-cheat” downloads promoted by…

September 6, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo