Recent Energy and Utilities Cyber Attacks

Page 2 of 2
Fake IT Support Calls in Teams Lead to Ransomware

Fake IT Support Calls in Teams Lead to Ransomware

Sophos reports a real Microsoft Teams voice-phishing campaign where attackers pretended to be IT support to convince employees to start remote-access sessions. After gaining access, the attackers ran commands to download malware and in several cases deployed Chaos ransomware within hours. The…

July 29, 2026
Telegram Dating Bot Used for Romance-to-Arson Scam

Telegram Dating Bot Used for Romance-to-Arson Scam

Russia’s FSB claims Ukrainian intelligence used a Telegram dating chatbot to deceive and psychologically pressure young Russians into sharing locations, clicking phishing links, and later carrying out arson or armed attacks. The alleged scheme started with romance-style outreach and payments via…

July 29, 2026
How Attackers Bypass MFA in the Real World

How Attackers Bypass MFA in the Real World

The article describes real-world ways attackers get around multifactor authentication (MFA), including “push bombing” (MFA fatigue), phishing pages that relay codes in real time, SIM swapping, and stealing session cookies so MFA isn’t needed again. It also cites known incidents (e.g., Uber 2022 MFA…

July 29, 2026
Hotel Wi‑Fi DNS Scam Steals Microsoft 365 Logins

Hotel Wi‑Fi DNS Scam Steals Microsoft 365 Logins

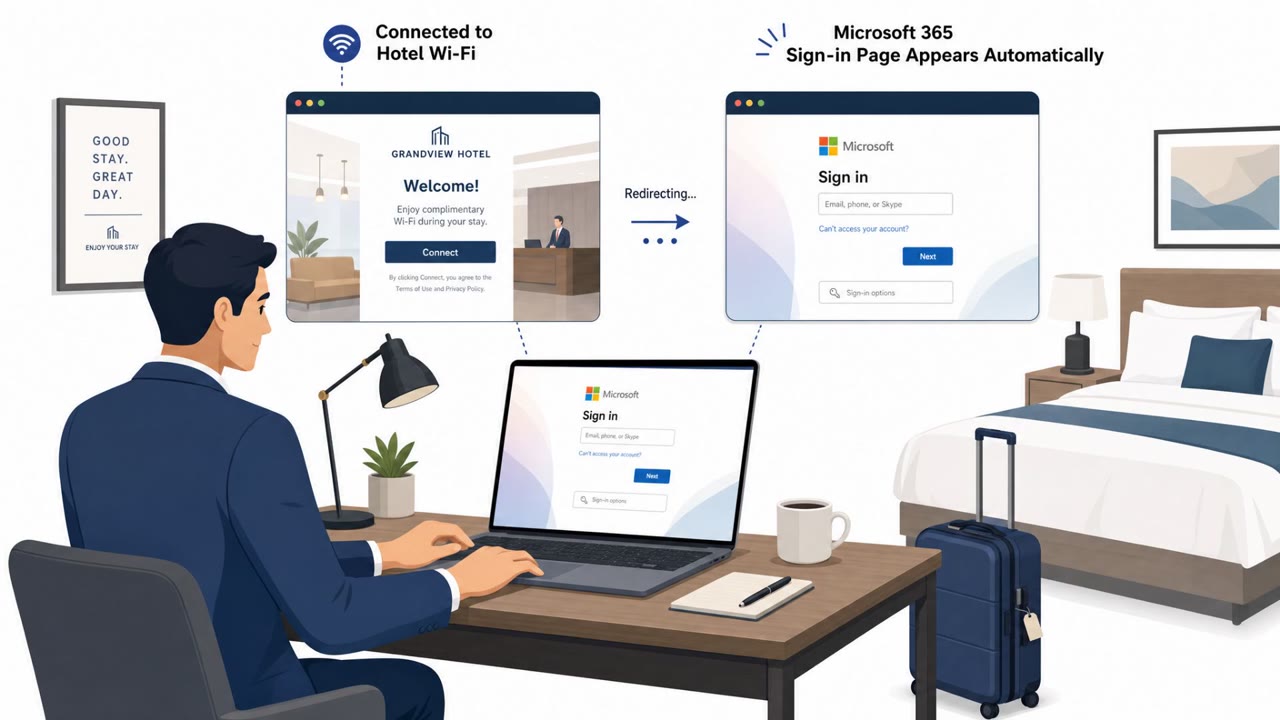
Attackers are taking over hotel and conference Wi‑Fi gateways and changing DNS settings so travelers are silently redirected to fake Microsoft 365 sign-in pages. Victims are then tricked into completing a device-code login that grants attackers a legitimate session token, often bypassing MFA. This…

July 28, 2026
Hotel Wi‑Fi DNS Hijack Steals M365 Logins

Hotel Wi‑Fi DNS Hijack Steals M365 Logins

Researchers report attackers compromising hotel and venue Wi‑Fi “captive portal” gateways to redirect Microsoft 365 sign-ins to attacker-controlled lookalike domains. Victims can have their Microsoft 365 credentials stolen without clicking a phishing link or installing malware, because the…

July 28, 2026
Hotel Wi‑Fi Hijacks Microsoft 365 Logins

Hotel Wi‑Fi Hijacks Microsoft 365 Logins

Researchers report attackers compromising hotel and conference Wi‑Fi gateway equipment to silently redirect travelers to fake Microsoft 365 sign-in pages, without sending phishing emails. In some cases, attackers also abuse Microsoft device-code login prompts so victims unintentionally approve…

July 27, 2026
Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

ReliaQuest reports attackers are compromising public Wi‑Fi “captive portal” gateways (such as in hotels and conference centers) and changing their DNS settings to redirect users to attacker-controlled pages. The goal is to harvest traveling employees’ Microsoft 365 credentials using…

July 27, 2026
Hotel Wi‑Fi DNS Trick Steals Microsoft 365 Logins

Hotel Wi‑Fi DNS Trick Steals Microsoft 365 Logins

Researchers found attackers taking over hotel and conference-center Wi‑Fi gateways and silently redirecting guests to fake Microsoft 365 sign-in pages to steal credentials. In some cases, the attackers also tried to route broader device traffic through a malicious proxy (WPAD) or trick users into…

July 26, 2026
Zimbra Zero-Day Email: Preview Triggers Espionage

Zimbra Zero-Day Email: Preview Triggers Espionage

A Russia-aligned espionage group sent specially crafted HTML emails that could compromise vulnerable Zimbra webmail servers just by being opened or previewed, no link clicks or attachments needed. The exploit ran JavaScript inside the email body to steal mailbox data and credentials, then set up…

July 24, 2026
Laundry Bear Uses Zero-Click Zimbra Email Trap

Laundry Bear Uses Zero-Click Zimbra Email Trap

A newly identified Russia-linked threat actor (“Laundry Bear”) is targeting Western organisations with a zero-click technique that can compromise Zimbra webmail simply by viewing a malicious email. The campaign has reportedly stolen sensitive data across multiple sectors and may evolve to target…

July 24, 2026
Zimbra Email View Triggers Russian Data Theft

Zimbra Email View Triggers Russian Data Theft

Government agencies say a Russian-linked group sent specially crafted HTML emails that exploit a Zimbra webmail flaw, so simply viewing the message can trigger data theft, no click required. The campaign has targeted multiple Western sectors since July 2025 and focuses on stealing email content and…

July 23, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo