Recent Energy and Utilities Cyber Attacks

Attacks on utilities, oil and gas, and energy companies, where social engineering is often the first step toward critical infrastructure. Each entry is broken down with an original video explainer, key findings, and the red flags your team should watch for. How we produce these.

VasyGrek Phishing Gang Brought Down

VasyGrek Phishing Gang Brought Down

Russian authorities arrested three suspected members of VasyGrek, also known as Fluffy Wolf, a financially motivated group that used targeted phishing to access corporate systems and steal money. In one documented case, an accounting employee opened a malicious attachment disguised as a routine…

November 3, 2026
North Korea Scales AI-Powered Job Scams

North Korea Scales AI-Powered Job Scams

Microsoft reports that North Korean threat actors are using AI to make job scams, fake recruiter outreach, fraudulent worker identities, and targeted phishing campaigns faster and more convincing. One group posed as recruiters for a spoofed AI blockchain company and scheduled software-engineer…

October 29, 2026
Fake AI Bots Scanned Servers for Secrets

Fake AI Bots Scanned Servers for Secrets

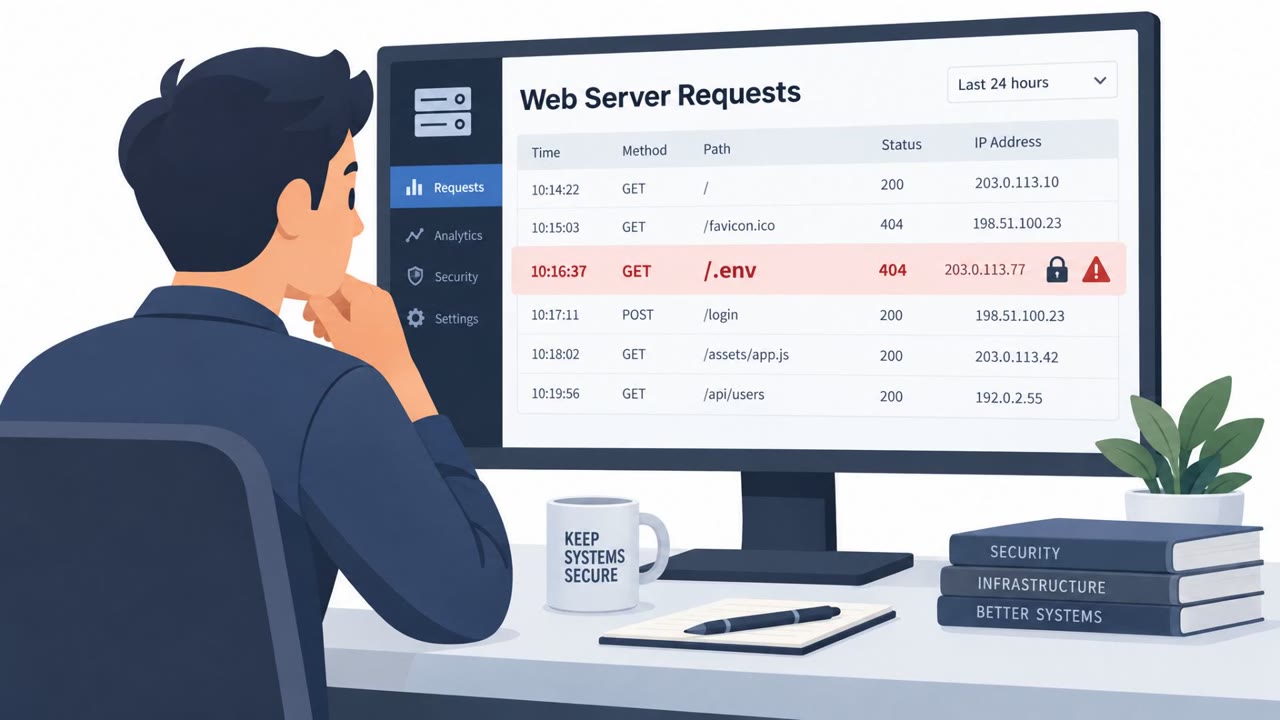
A threat actor impersonated about 32 AI bots, including ones claiming to represent OpenAI, Anthropic, Meta, and Perplexity, to probe enterprise web servers for exposed credentials and private keys. The scanner relied on easily forged bot identity labels and rapidly requested common secret-file…

October 29, 2026
MR ROBOT Fakes Bank Apps to Steal OTPs

MR ROBOT Fakes Bank Apps to Steal OTPs

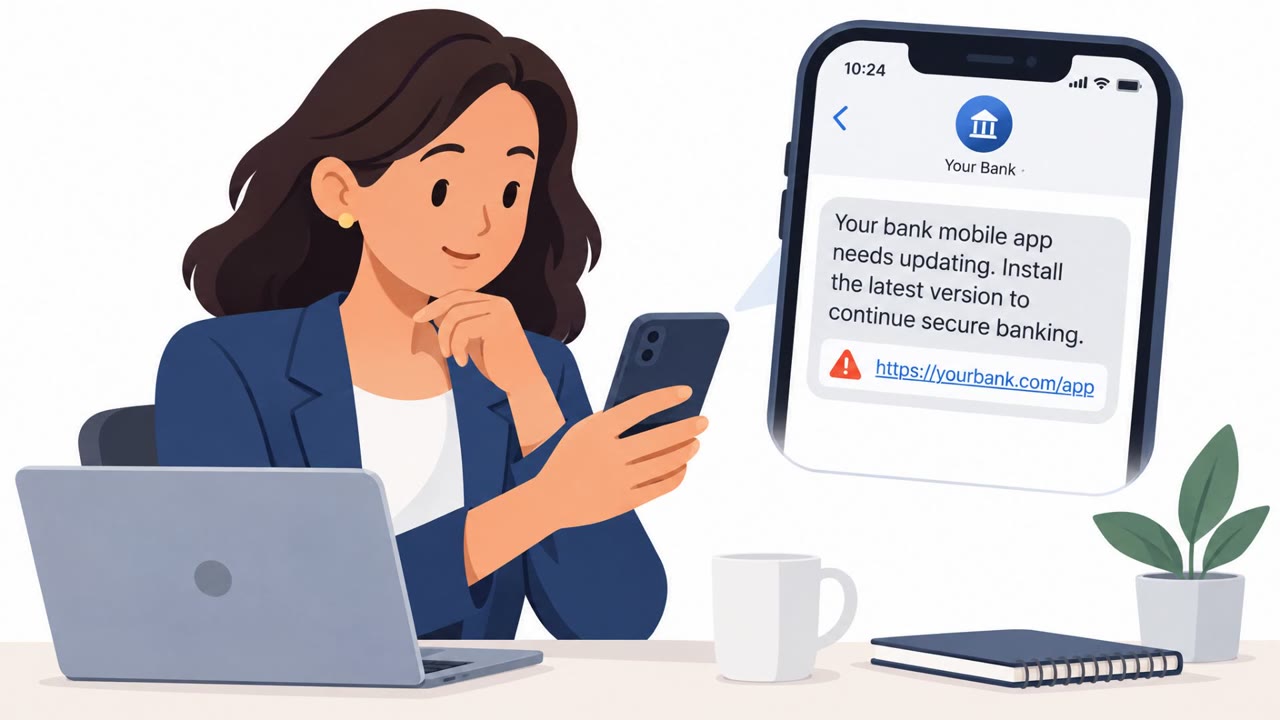
The MR ROBOT malware service rents customized fake Android banking apps to criminals targeting Indian bank customers. Victims are lured through fake Play Store-style pages and links in messaging apps, then tricked into installing apps that can steal banking details, intercept one-time passwords,…

October 29, 2026
Ransomware Crew Uses Vishing to Pressure Victims

Ransomware Crew Uses Vishing to Pressure Victims

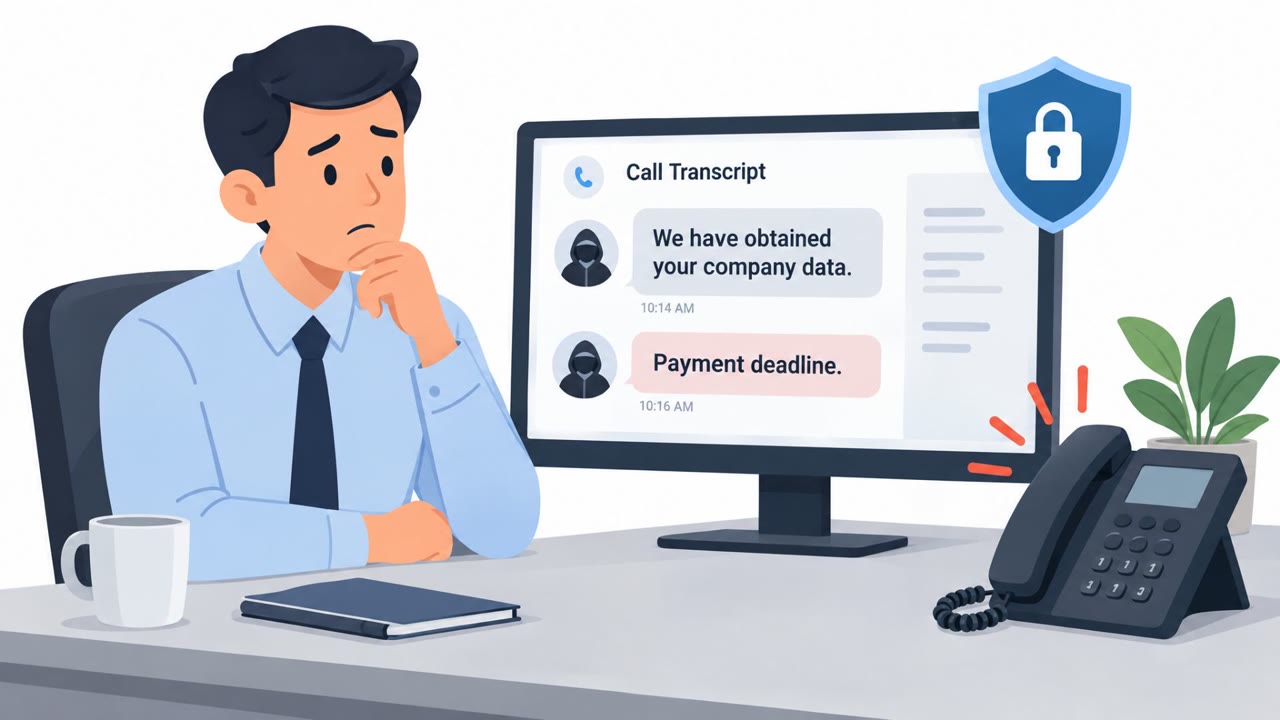
Researchers uncovered an AI-assisted ransomware operation linked to affiliates of INC and The Gentlemen. After breaking into organizations through exposed remote-access systems, the group stole sensitive files and used scripted phone calls, proof samples, and threats to contact customers or…

October 23, 2026
Phishing Opens Door to Ukraine Wiper Attack

Phishing Opens Door to Ukraine Wiper Attack

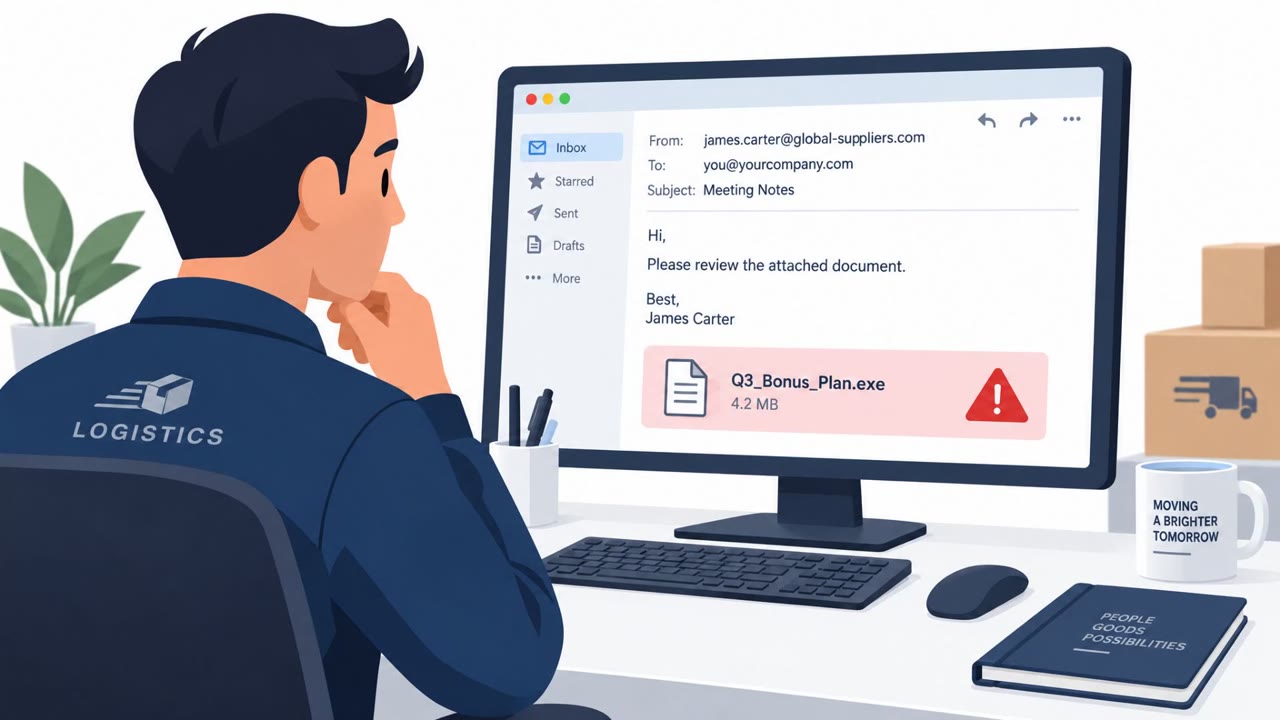
A Russia-linked operation used a spear-phishing email with a malicious attachment to gain access to a Ukrainian logistics company. UAC-0099 established access and later handed the victim environment to Sandworm, which carried out a destructive data-wiping attack more than two months later.

October 23, 2026
Silent Lynx Used Gov Emails to Lure Targets

Silent Lynx Used Gov Emails to Lure Targets

Researchers say the Kazakhstan-linked group “Silent Lynx” has run real espionage campaigns across Central Asia, targeting government bodies and energy organizations. The reported entry method relied heavily on spear‑phishing sent from compromised government email accounts, sometimes using trusted…

October 15, 2026
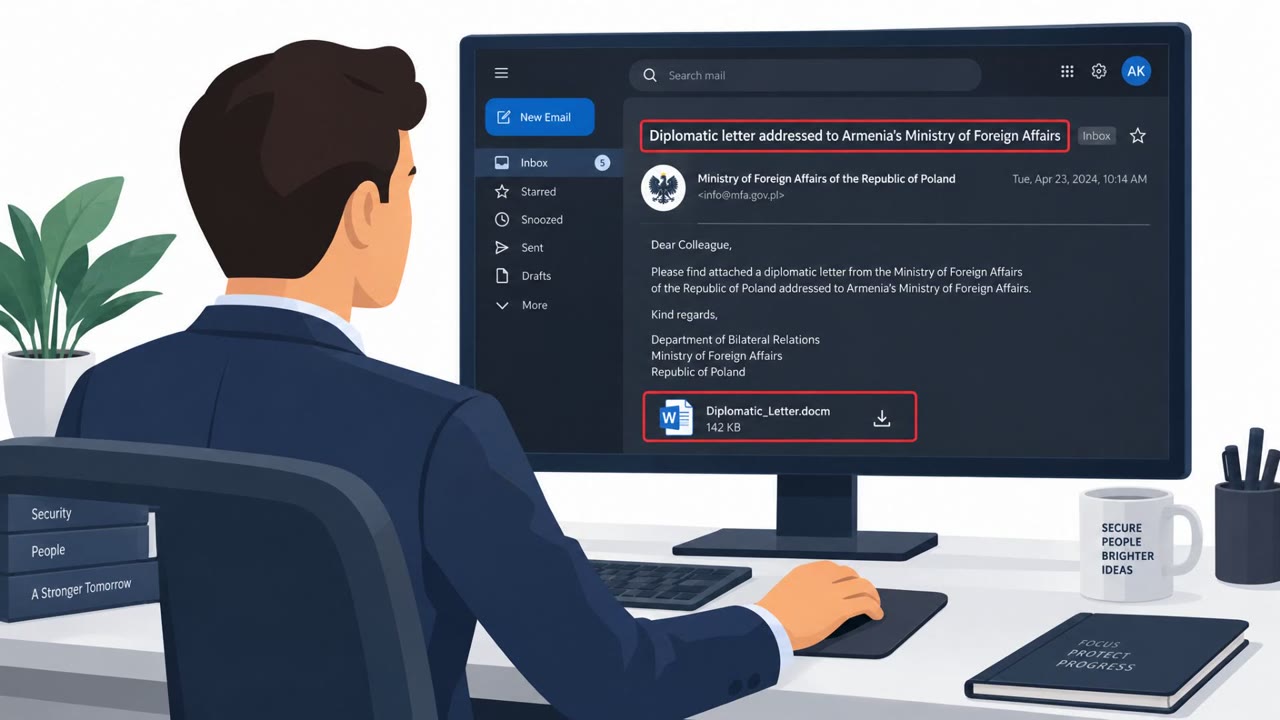
Silent Lynx Phishes CIS Govs With Decoy Documents

Silent Lynx Phishes CIS Govs With Decoy Documents

Researchers report that the threat actor Silent Lynx ran multiple real-world spear‑phishing campaigns against government organizations across Central Asia and the wider CIS region. Victims were lured with official-looking documents (e.g., diplomatic letters, airspace applications, and oil refinery…

October 15, 2026
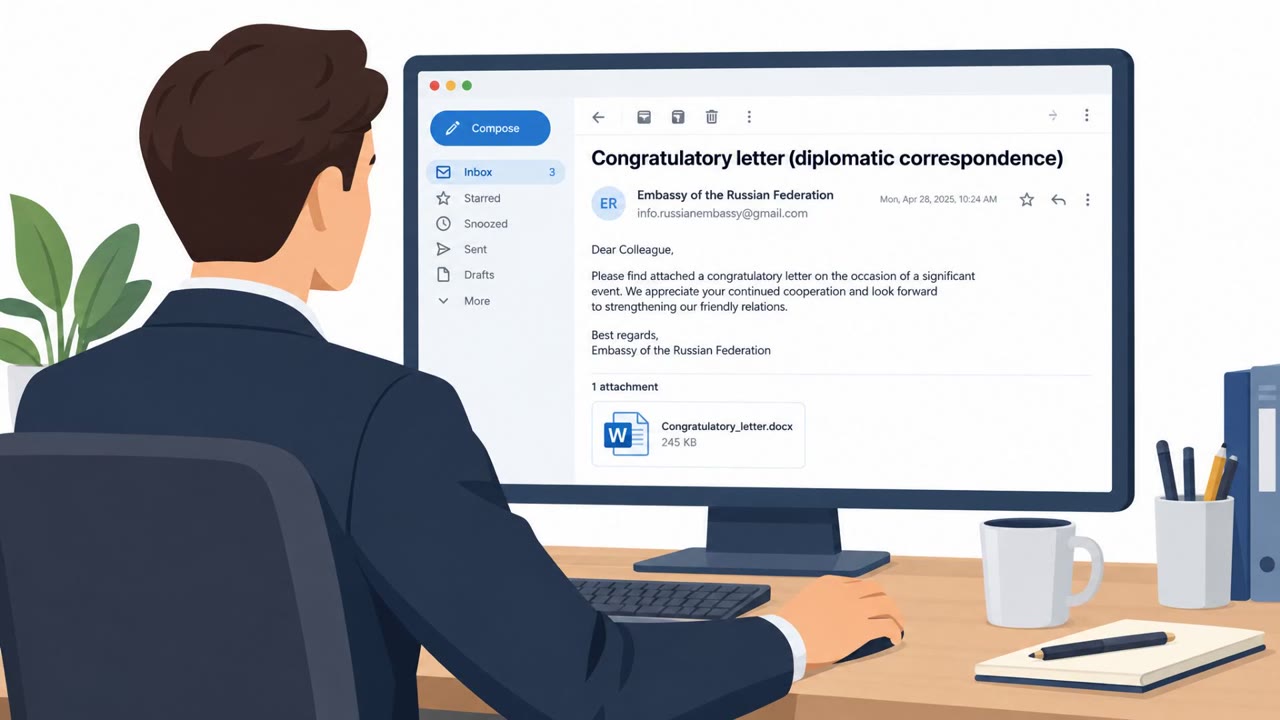
Silent Lynx Lures CIS Officials With Fake Diplomacy Docs

Silent Lynx Lures CIS Officials With Fake Diplomacy Docs

Researchers tracked Kazakhstan-nexus group UAT-6275 (TAG-193) targeting government organizations across Central Asia and the wider CIS using convincing decoy documents tied to diplomacy and energy. The campaigns used malicious files (macro-enabled Word docs, shortcuts, and a WinRAR exploit) to…

October 15, 2026
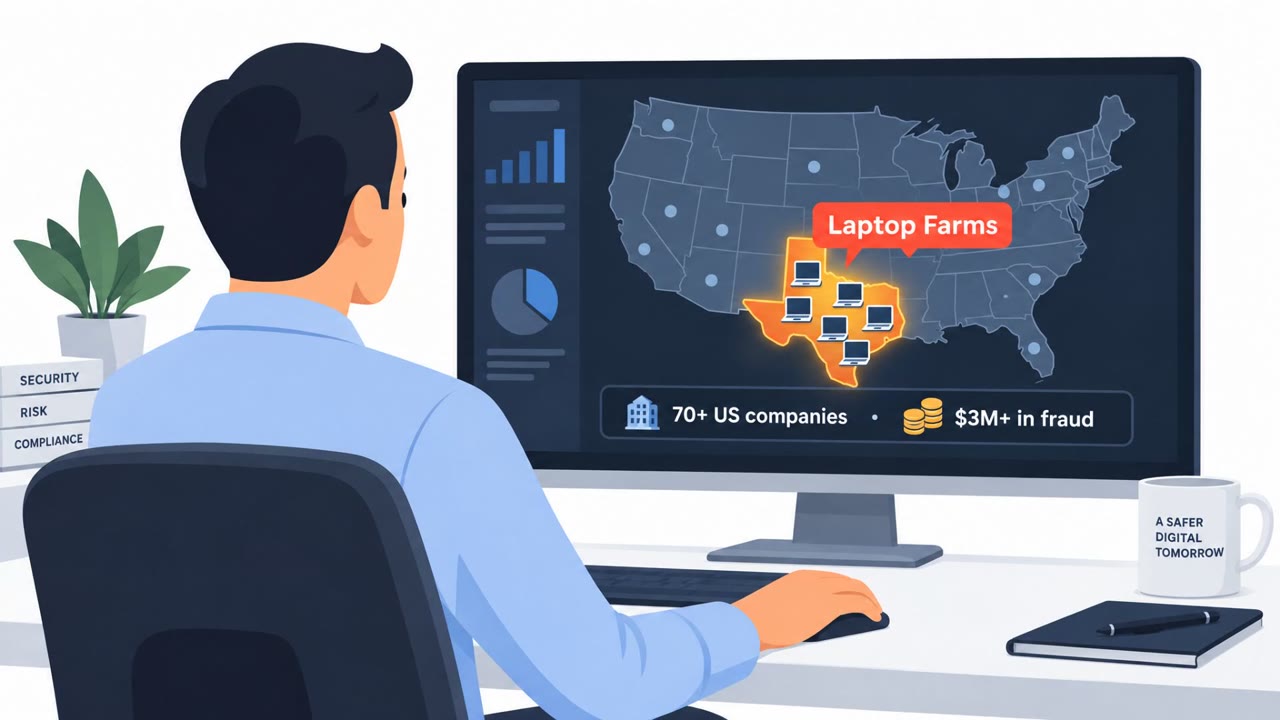
North Korean Fake IT Workers Ran US Laptop Farms

North Korean Fake IT Workers Ran US Laptop Farms

US authorities arrested two Americans accused of helping North Korean “fake IT workers” get hired remotely at US companies and route company laptops into US-based “laptop farms.” The scheme used stolen or fake identities and location-masking tools so overseas workers could appear to be working from…

October 14, 2026
Invoice-Fraud Platform Blasted Pix via Email & SMS

Invoice-Fraud Platform Blasted Pix via Email & SMS

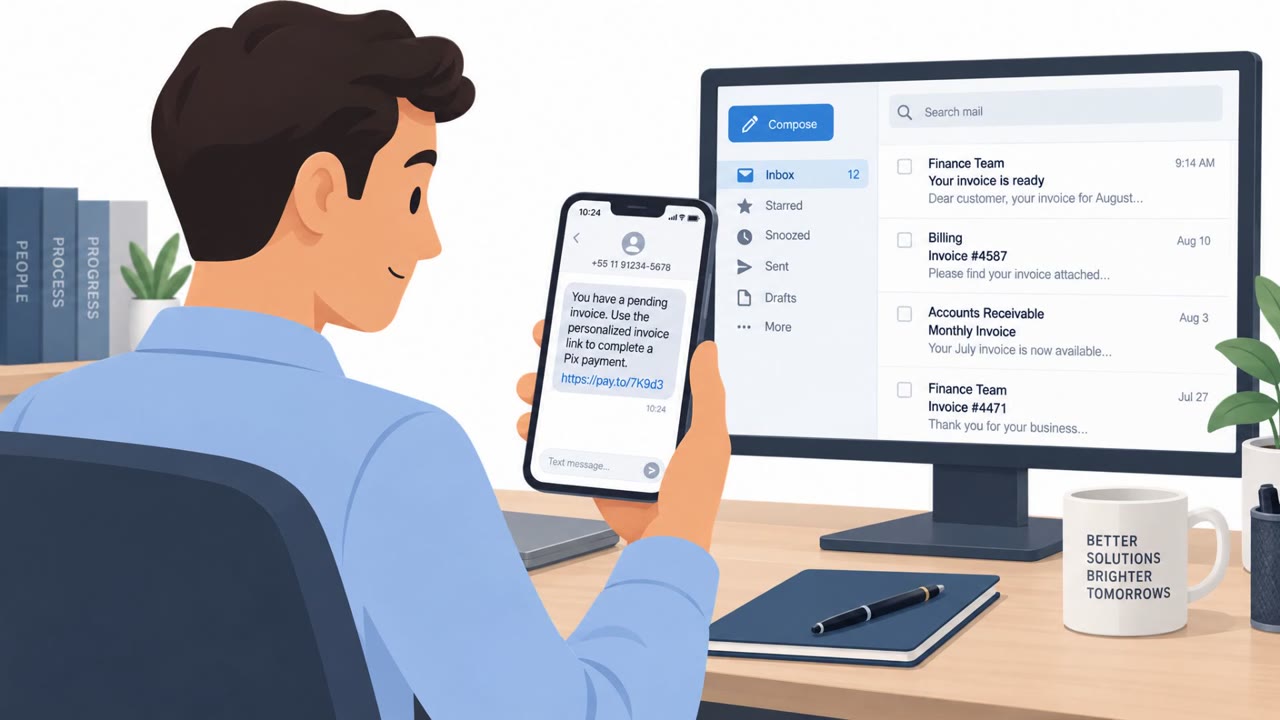
Researchers described two cybercrime operations. While one campaign focused on breaking into websites and infrastructure, a second operation (“Operation Master”) ran an automated invoice-fraud system that sent millions of messages with personalized invoice links designed to trick victims into…

October 12, 2026
China-Linked Hackers Used Fake Web Logins

China-Linked Hackers Used Fake Web Logins

U.S. and international agencies warned that China-linked actors, enabled by a China-based company (Integrity Technology Group), are breaking into organizations including U.S. critical infrastructure. A key technique described is altering legitimate webpages to show fake login prompts that steal…

October 12, 2026
MATCHBOIL Spearphish Tricks Users Into Running Script

MATCHBOIL Spearphish Tricks Users Into Running Script

ESET reports that Russia-aligned group UAC-0099 is using spearphishing emails with malicious links to deliver a downloader called MATCHBOIL. The attack relies on tricking a person into manually running a downloaded VBScript, which then fetches and installs further malware and sets up persistence…

October 9, 2026
Fake Court Summons Phish Drops MatchBoil Malware

Fake Court Summons Phish Drops MatchBoil Malware

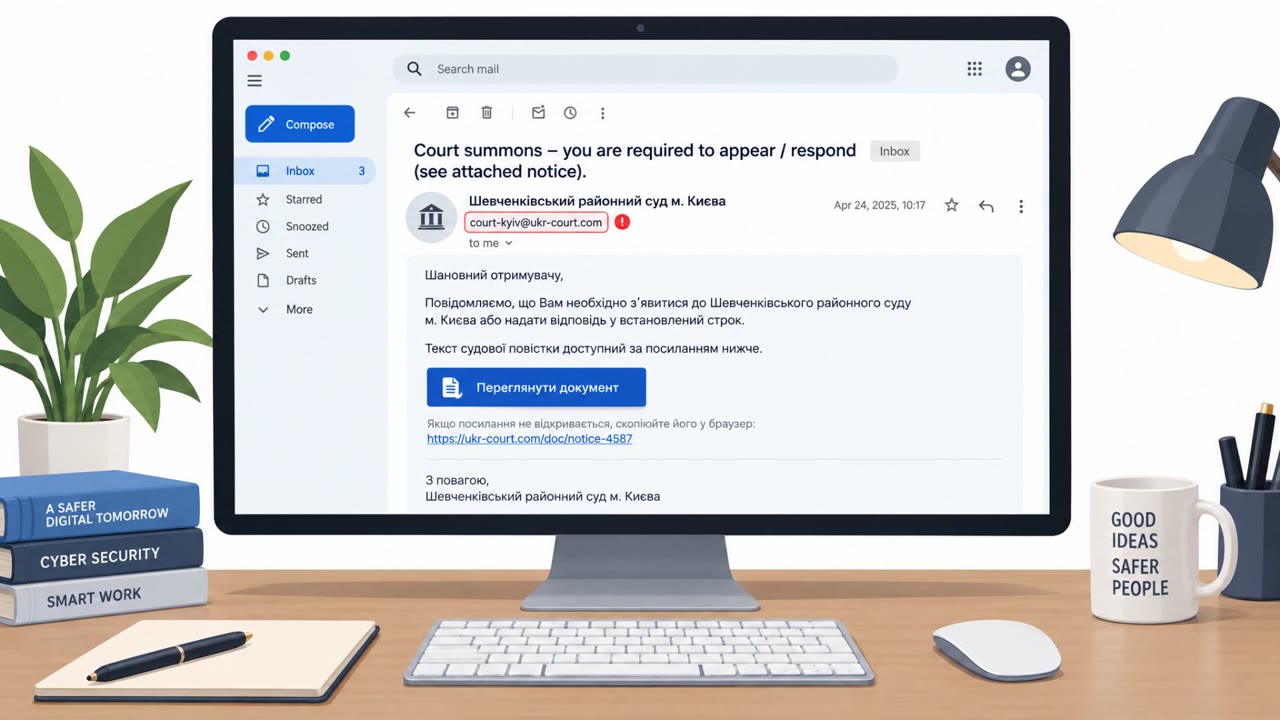
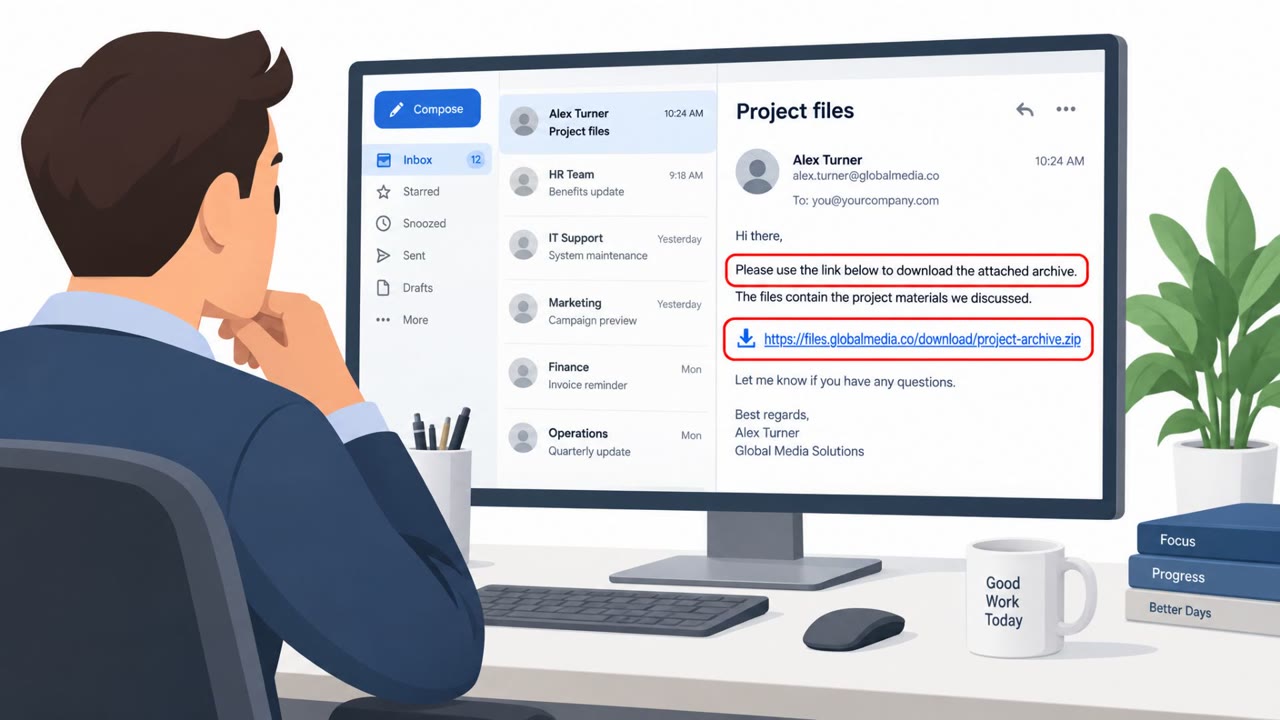
Researchers say the Russia-aligned group UAC-0099 has been phishing Ukrainian organizations with malicious links that install a data-harvesting malware called MatchBoil. The emails have included lures like fake Ukrainian court summonses, and clicking the link leads to downloading an archive that…

October 8, 2026
MATCHBOIL Spearphish Drops Ukraine Spy Backdoor

MATCHBOIL Spearphish Drops Ukraine Spy Backdoor

ESET reports that the Russia-aligned group UAC-0099 used spear‑phishing emails to trick victims in Ukraine into clicking a link that downloads a malicious archive. The infection chain runs a script that installs MATCHBOIL, which then downloads a spying backdoor (MATCHWOK) and sets persistence so it…

October 8, 2026
Fake Dubai Airports Recruiters Push Dev Malware

Fake Dubai Airports Recruiters Push Dev Malware

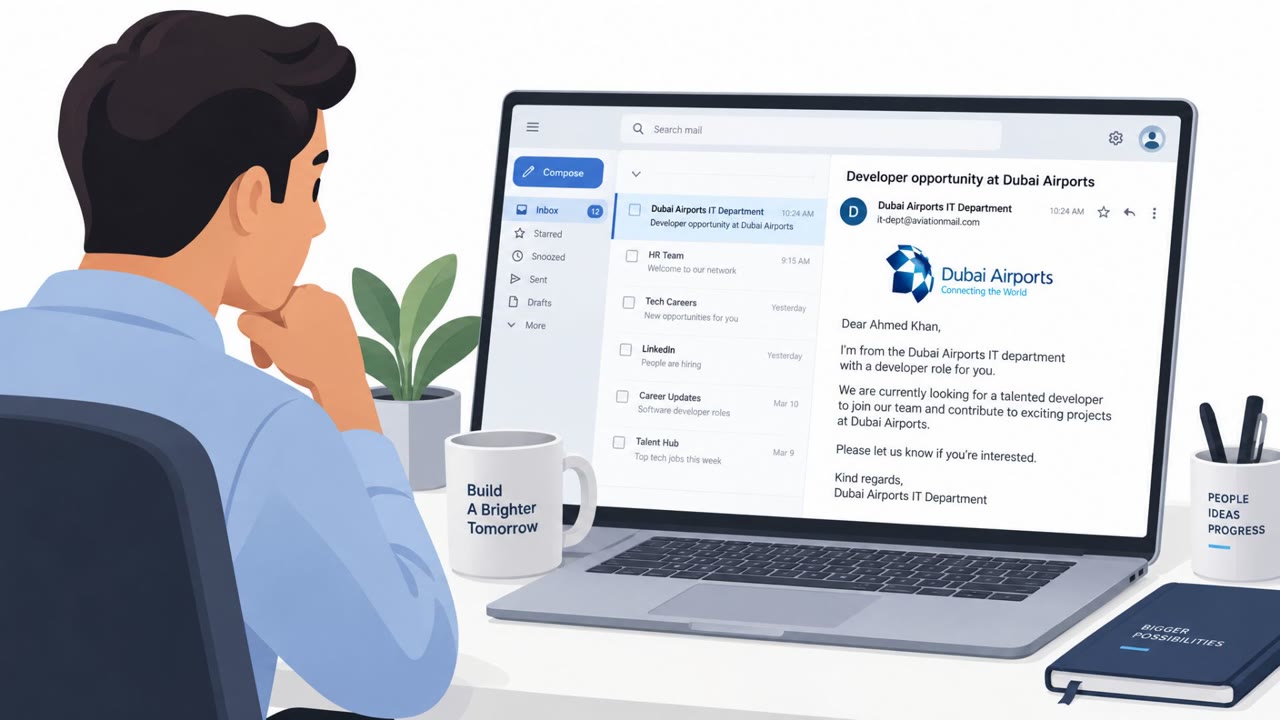
Researchers reported an Iranian state-aligned actor impersonating the Dubai Airports IT department to lure a targeted Iraqi individual into installing a fake “careers portal” and then opening a weaponized coding test. The workflow looked like a real recruitment process (HR questions, then a…

October 6, 2026
Kid Fakes Dad to Get a New Phone Line Installed

Kid Fakes Dad to Get a New Phone Line Installed

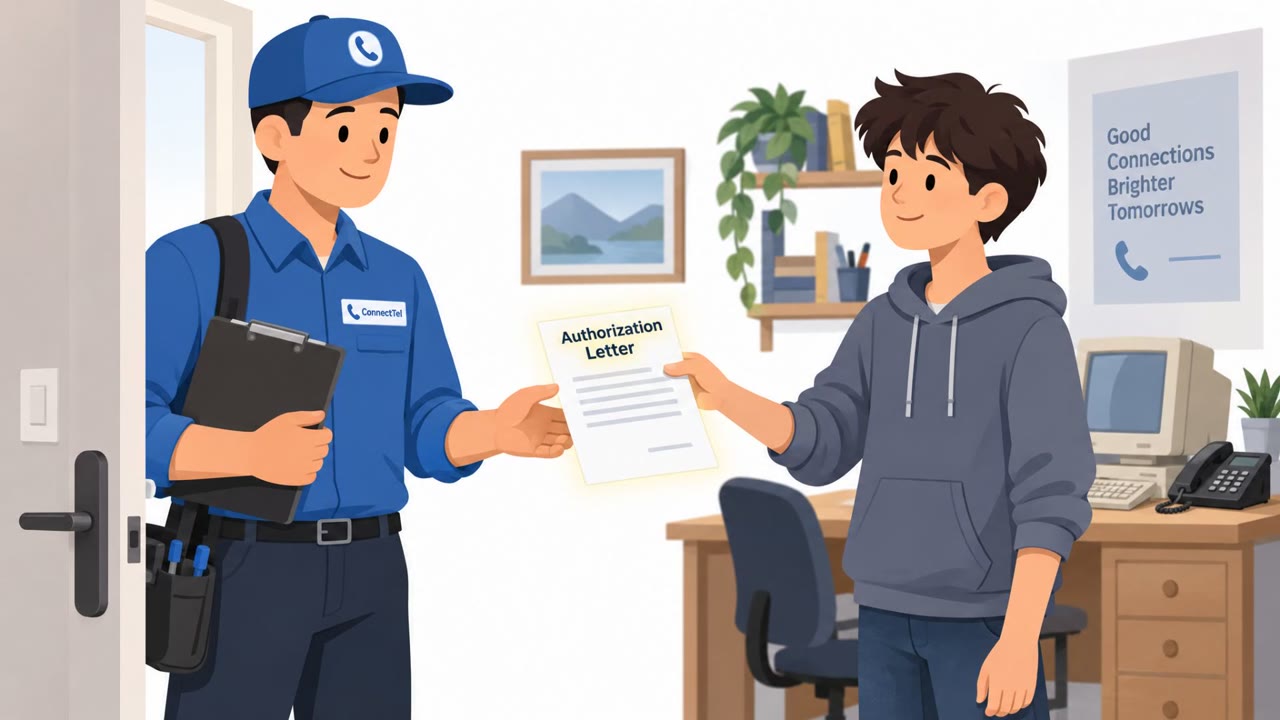
A future security executive describes how, as a young teenager, he used deception to get a phone company to install a second phone line at his home. He posed as his father using a forged letter and a believable technical-sounding request (“dedicated low-noise line for a modem”), successfully…

October 1, 2026
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

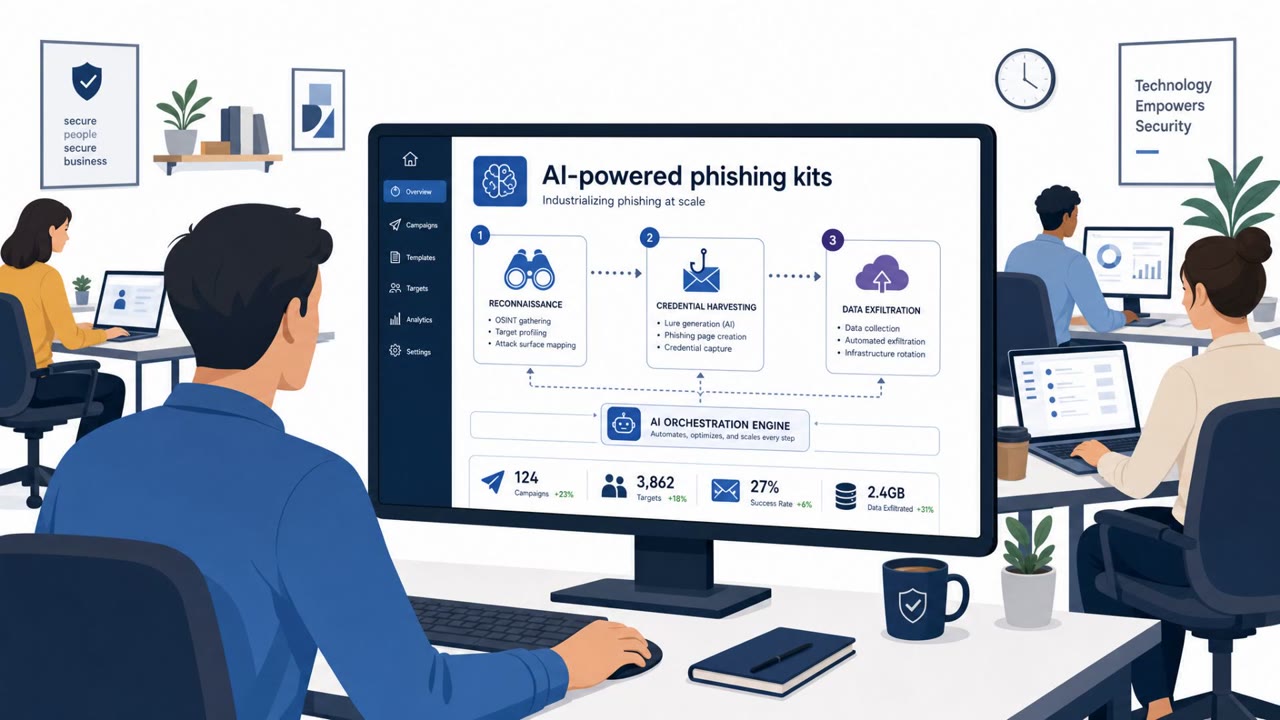
Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
Fraudsters Can Remotely “Brick” Phones for $3

Fraudsters Can Remotely “Brick” Phones for $3

Researchers showed that attackers can abuse mobile carriers’ “lost/stolen phone” reporting process to get devices blocked from the cellular network, even when the devices were never lost. With only a prepaid account and a target device’s IMEI number, blocking can cost just a few dollars and take…

September 11, 2026
China-Linked Hackers Push “Gemini” Phish With Zero-Days

China-Linked Hackers Push “Gemini” Phish With Zero-Days

Proofpoint reports multiple China-aligned espionage groups used a chained set of browser/Windows zero-days (“BlueMoon”) and delivered it through phishing emails. Victims who clicked a phishing link could end up with a malicious browser extension disguised as Google Gemini, letting attackers watch…

September 11, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo