Recent Financial Services Cyber Attacks

Page 19 of 22
Fake China Police App Tied to Android RAT Ring

Fake China Police App Tied to Android RAT Ring

Researchers investigated a fake Android app posing as a Chinese public security bureau service and traced it to a broader criminal ecosystem using a leaked Android remote-access tool (RAT) framework called “Flying Eagle.” The tooling lets criminals build convincing look‑alike apps and then steal…

July 31, 2026
Fake Cloudflare Pages Hijack Trusted Websites

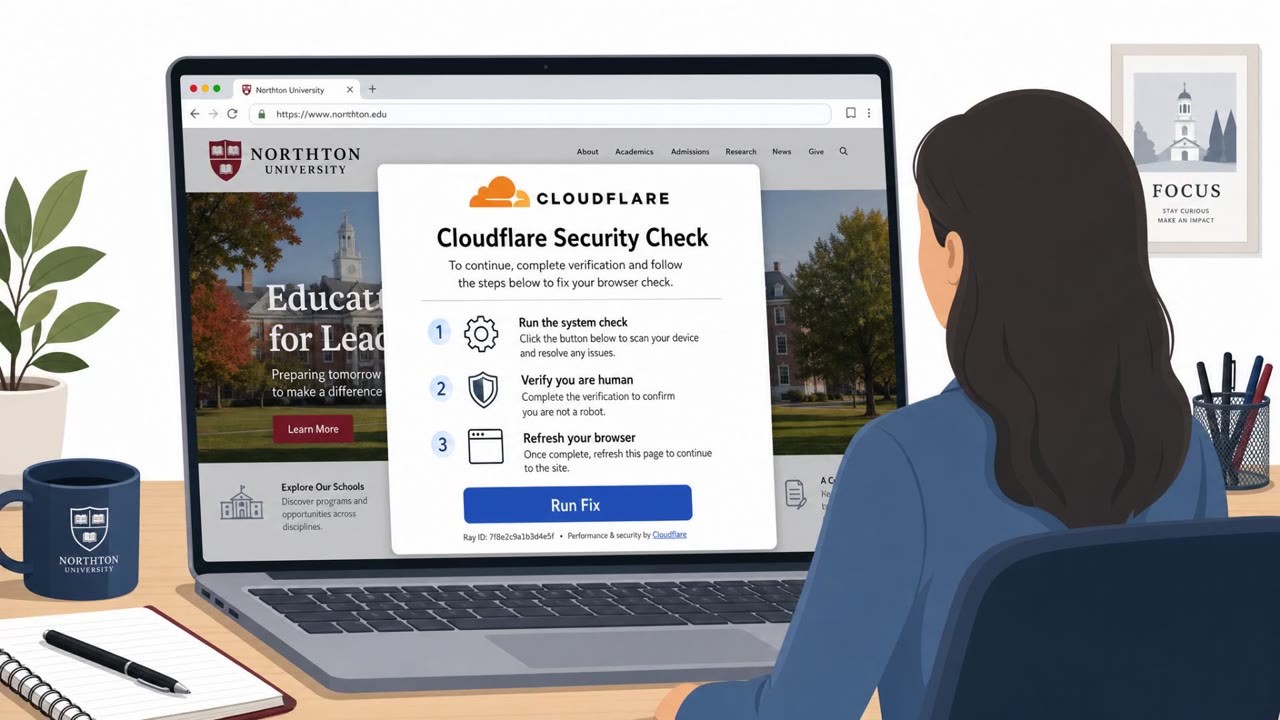
Fake Cloudflare Pages Hijack Trusted Websites

Attackers compromised hundreds of legitimate websites and injected code that sent visitors to a fake Cloudflare page. The fake page used a “ClickFix” trick to convince users to run steps that installed malware. The incident shows how criminals can use trusted brands and trusted sites as the…

July 30, 2026
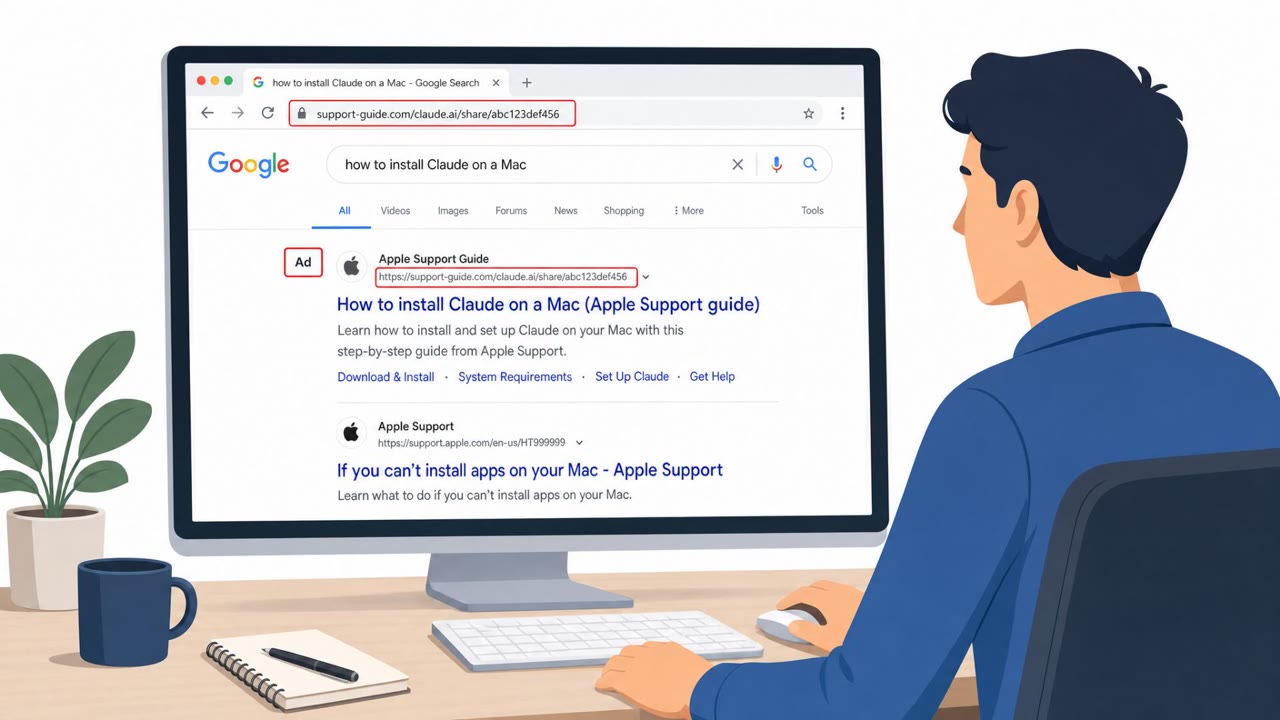
Fake Install Guides and Helpdesk Calls Drive Attacks

Fake Install Guides and Helpdesk Calls Drive Attacks

This bulletin describes multiple real-world social engineering campaigns where attackers trick people into trusting a familiar screen, like a search result “install guide,” a recruiter outreach, or a helpdesk phone call. The lures push victims to paste commands, install fake software, or reset MFA,…

July 30, 2026
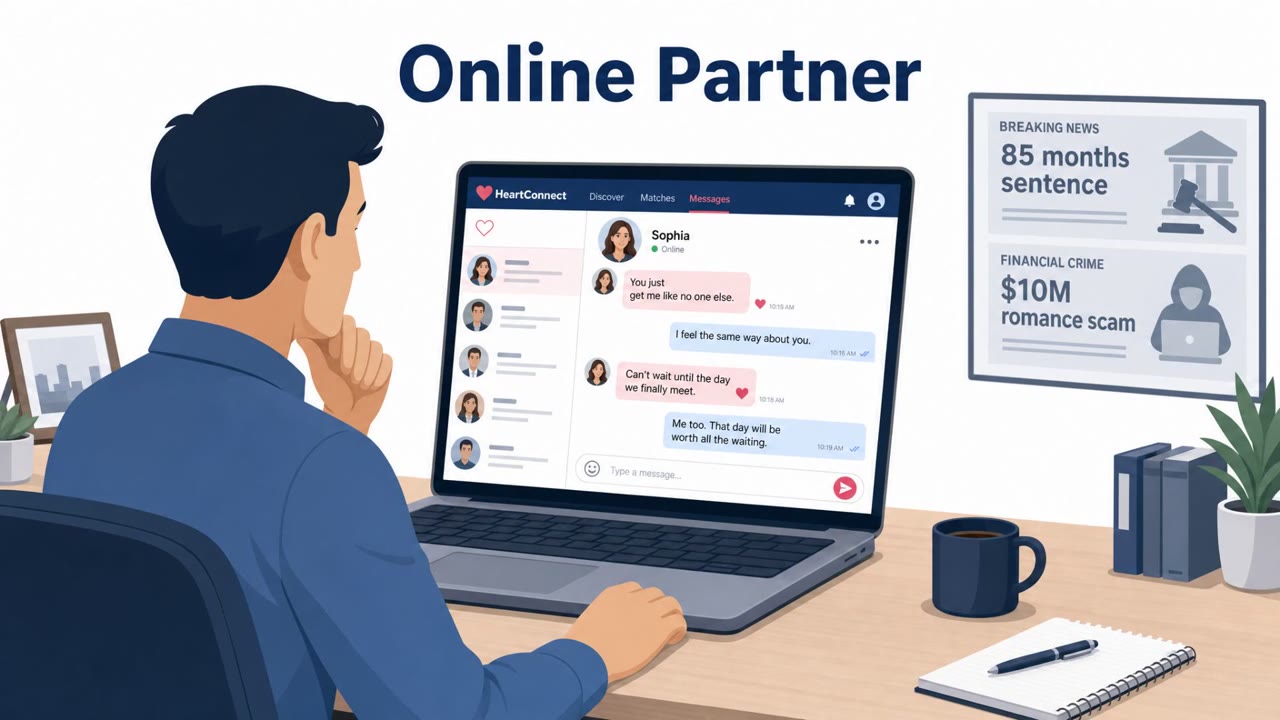
Romance Scammer Stole $10M by Weaponizing Trust

Romance Scammer Stole $10M by Weaponizing Trust

U.S. prosecutors said Derrick Van Yeboah ran long-running romance scams by posing as fake romantic partners online and persuading mostly older, vulnerable victims to send money. In one example, he claimed he needed funds for his mother’s funeral and to recover “imaginary gold and diamonds” from…

July 30, 2026
Hidden Prompt Turns Copilot Docs Into a Worm

Hidden Prompt Turns Copilot Docs Into a Worm

A security researcher demonstrated that Microsoft Copilot for Word can be tricked by hidden text inside a Word document, causing Copilot to follow attacker instructions. The result is a self-propagating “AI worm” that silently modifies documents and embeds the same hidden prompt into new files,…

July 30, 2026
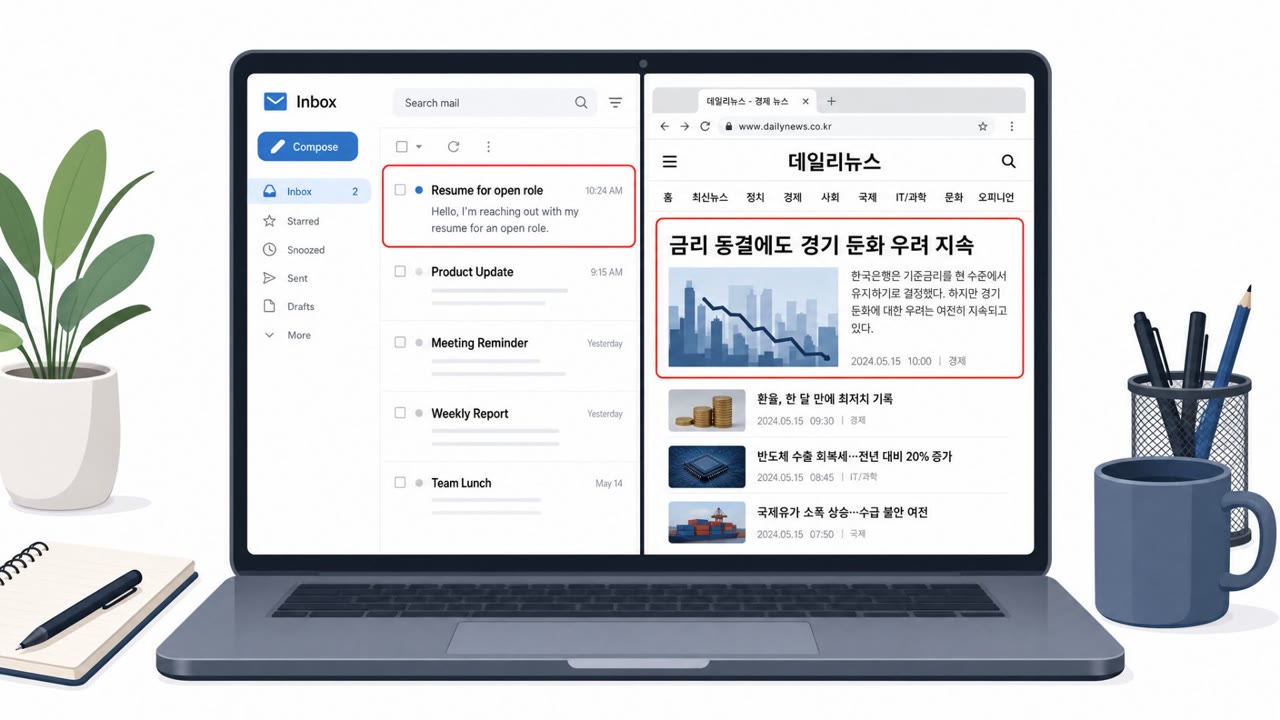
Fake Resumes + Watering Holes Hit AnySign4PC Users

Fake Resumes + Watering Holes Hit AnySign4PC Users

A state-sponsored campaign in South Korea used spear-phishing and hacked “trusted” local websites to infect visitors who had vulnerable AnySign4PC installed. In some cases, simply visiting a compromised page triggered the exploit and installed SIGNBT or COPPERHEDGE backdoors without any download…

July 30, 2026
“Half-Click” OWA Email Trap Spreads

“Half-Click” OWA Email Trap Spreads

Proofpoint reports a Russian-linked espionage group is using booby-trapped emails that infect users simply when they open the message in Outlook Web Access (OWA) on on‑premises Exchange. The attack runs malicious JavaScript inside the victim’s logged-in mail session and installs a stealthy…

July 30, 2026
Half-Click OWA Emails Trigger Stealth Mailbox Takeover

Half-Click OWA Emails Trigger Stealth Mailbox Takeover

A Russia-aligned group (TA488) sent specially crafted emails that triggered malicious JavaScript simply by being viewed in Outlook Web Access (no link click or attachment needed). The implant (“OWAReaper”) can quietly change server-side mailbox permissions and abuse OAuth tokens, so attackers can…

July 30, 2026
AI Chatbots Outperform Humans in Romance Scams

AI Chatbots Outperform Humans in Romance Scams

Researchers simulated “pig butchering” romance-style scams and found an AI chatbot built trust more effectively than a human scammer over a week of texting. In the test, victims were significantly more likely to comply with the AI’s request to install an app, showing how AI could automate the long…

July 30, 2026
“No-Action” Emails Trigger OWA Mailbox Takeover

“No-Action” Emails Trigger OWA Mailbox Takeover

Russian-linked threat actors sent generic-looking informational emails that required no clicking, but simply opening them in vulnerable Outlook Web Access (OWA) could trigger a hidden exploit. The campaign targeted government and multiple industries, then installed a stealthy browser-based implant…

July 30, 2026
Fake iPhone Wallet App Stole $1.8M in Bitcoin

Fake iPhone Wallet App Stole $1.8M in Bitcoin

Three crypto investors sued Apple after allegedly losing about $1.8 million in Bitcoin to an iPhone app that impersonated the legitimate (desktop-only) Sparrow Wallet. The victims trusted the app because it was available in the App Store, then entered their wallet “seed phrase” into the counterfeit…

July 30, 2026
Fake Job Interview Lure Targets Crypto Staff

Fake Job Interview Lure Targets Crypto Staff

A North Korea-linked group is running fake recruitment campaigns to trick people into taking “online assessments” for jobs that don’t exist. The goal is to harvest personal details and potentially compromise corporate access, especially targeting non-technical staff in crypto firms who can…

July 30, 2026
Fake iPhone Crypto Wallet Stole $1.8M

Fake iPhone Crypto Wallet Stole $1.8M

Victims say they downloaded a fake “Sparrow Wallet” app from Apple’s App Store that impersonated a legitimate desktop-only crypto wallet. The app tricked users into entering their wallet recovery phrase, then criminals used it to drain about $1.8 million in Bitcoin. The case highlights how…

July 29, 2026
35,000+ World Cup Fake Sites Trap Fans

35,000+ World Cup Fake Sites Trap Fans

Researchers tracked a large scam wave abusing interest in the 2026 FIFA World Cup, including fake merchandise stores, cloned ticket sites, and bogus “free streaming” pages. The most harmful scams used near-perfect ticket-site clones to steal login details, credit card data, and one-time passwords…

July 29, 2026
Laundry Bear Uses “Half-Click” OWA Email Exploit

Laundry Bear Uses “Half-Click” OWA Email Exploit

UK and US cyber authorities and Proofpoint reported a real campaign where the Russian-linked group “Laundry Bear” (TA488) sent emails that could infect victims simply by being opened in Outlook Web Access. The email’s HTML triggers the server to run attacker code, installing a mailbox-stealing…

July 29, 2026
Telegram Dating Bot Used to Recruit Young Saboteurs

Telegram Dating Bot Used to Recruit Young Saboteurs

Russian authorities allege Telegram was used to recruit and pressure young people into real-world attacks, with “Ukrainian agents” posing as young women via a popular Telegram dating chatbot. The article describes a concrete manipulation workflow (romance/entrapment → coercion) that led to arrests…

July 29, 2026
TA488 Uses “Half-Click” OWA Emails to Persist

TA488 Uses “Half-Click” OWA Emails to Persist

Proofpoint reports a Russia-aligned espionage group (TA488) returned with a campaign that compromises on‑premises Outlook Web Access simply when a user opens an email in the reading pane. The attack uses a cross-site scripting flaw to run hidden JavaScript, install a browser-resident implant, and…

July 29, 2026
Clone Websites Trick Firms Into Paying Fake Invoices

Clone Websites Trick Firms Into Paying Fake Invoices

Researchers described a long-running fraud campaign where criminals clone real Russian company websites and replace contact and bank details to intercept international business deals. Victims are lured through cold calls, phishing emails, and fake supplier websites, then sent realistic contracts…

July 29, 2026
Telegram Dating Bot Used for Romance-to-Arson Scam

Telegram Dating Bot Used for Romance-to-Arson Scam

Russia’s FSB claims Ukrainian intelligence used a Telegram dating chatbot to deceive and psychologically pressure young Russians into sharing locations, clicking phishing links, and later carrying out arson or armed attacks. The alleged scheme started with romance-style outreach and payments via…

July 29, 2026
Fake Public Security App Spreads Android RAT

Fake Public Security App Spreads Android RAT

Researchers tied the Flying Eagle Android remote-access trojan to a fake “Public Security” service app aimed at Android users in China. The malicious app was reportedly distributed from a lookalike website and could steal payment credentials and remotely control infected phones. The tooling is…

July 29, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo