Recent Financial Services Cyber Attacks

Page 20 of 22
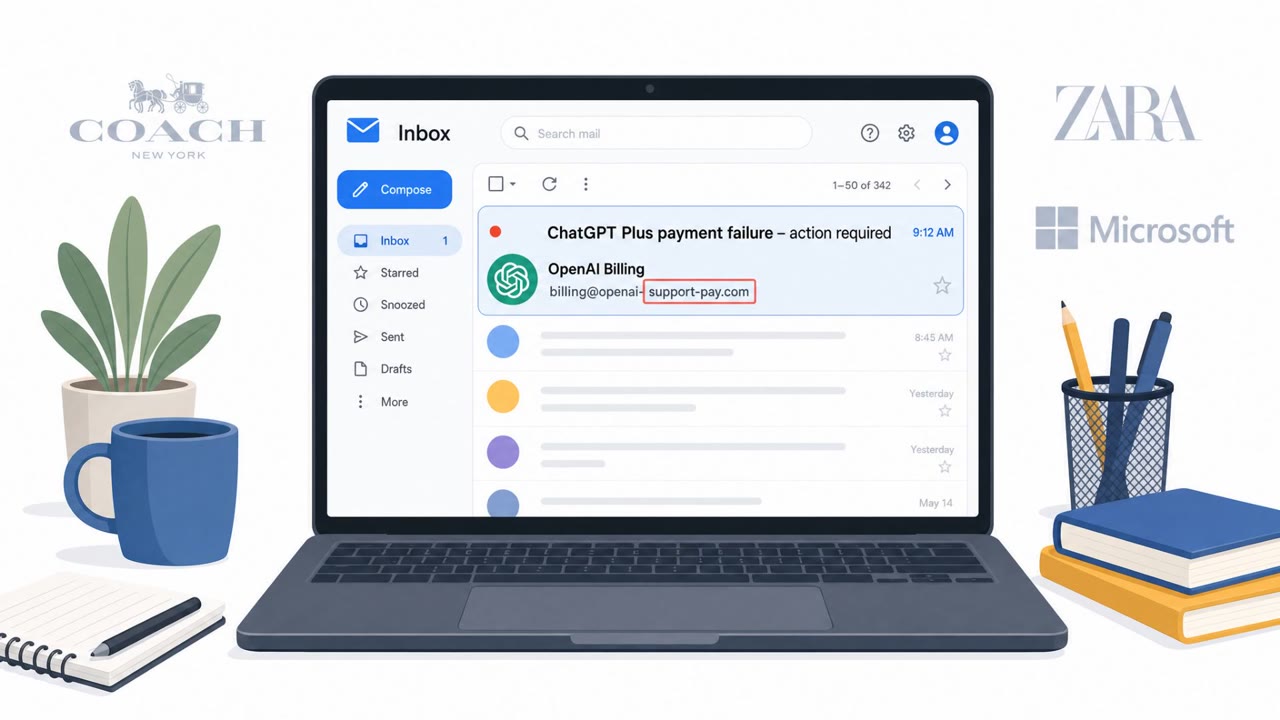
Fake ChatGPT Billing Emails Steal Card Details

Fake ChatGPT Billing Emails Steal Card Details

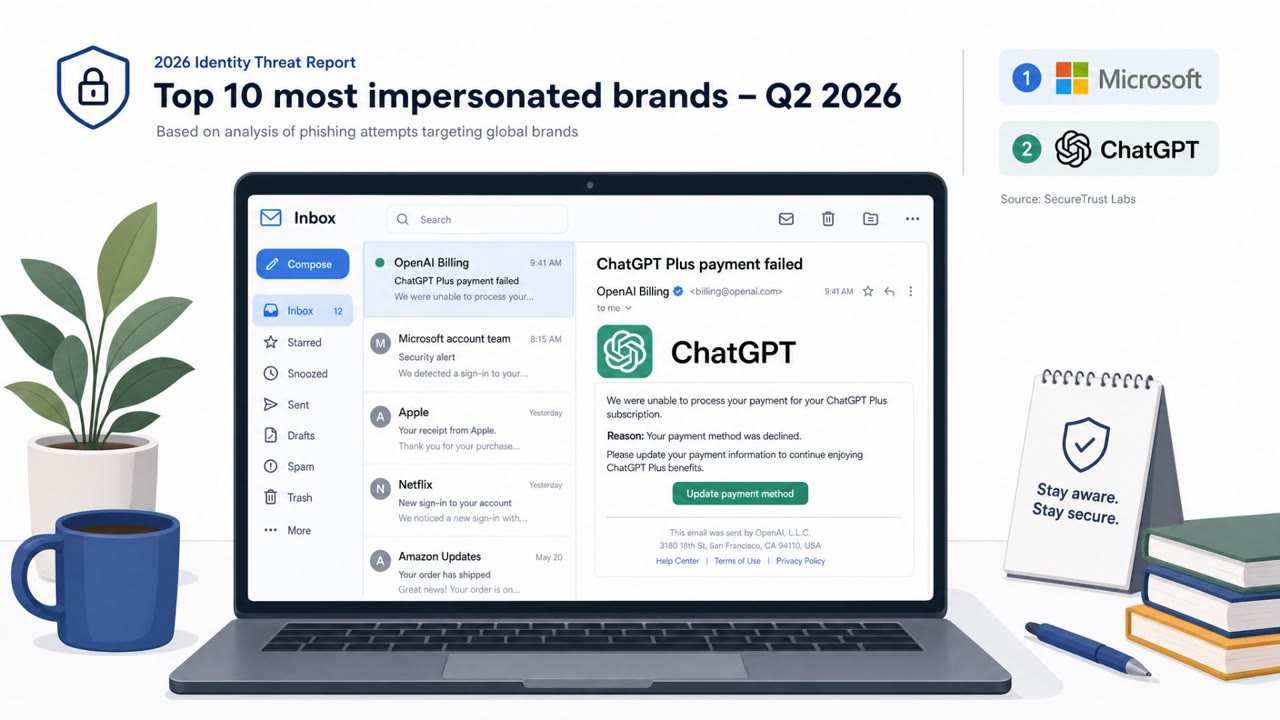
Check Point reports that scammers are now impersonating ChatGPT/OpenAI in phishing campaigns, reflecting how mainstream the service has become. One documented example used a fake “ChatGPT Plus payment failure” notice that sent victims to a fraudulent payment page designed to capture full credit…

July 28, 2026
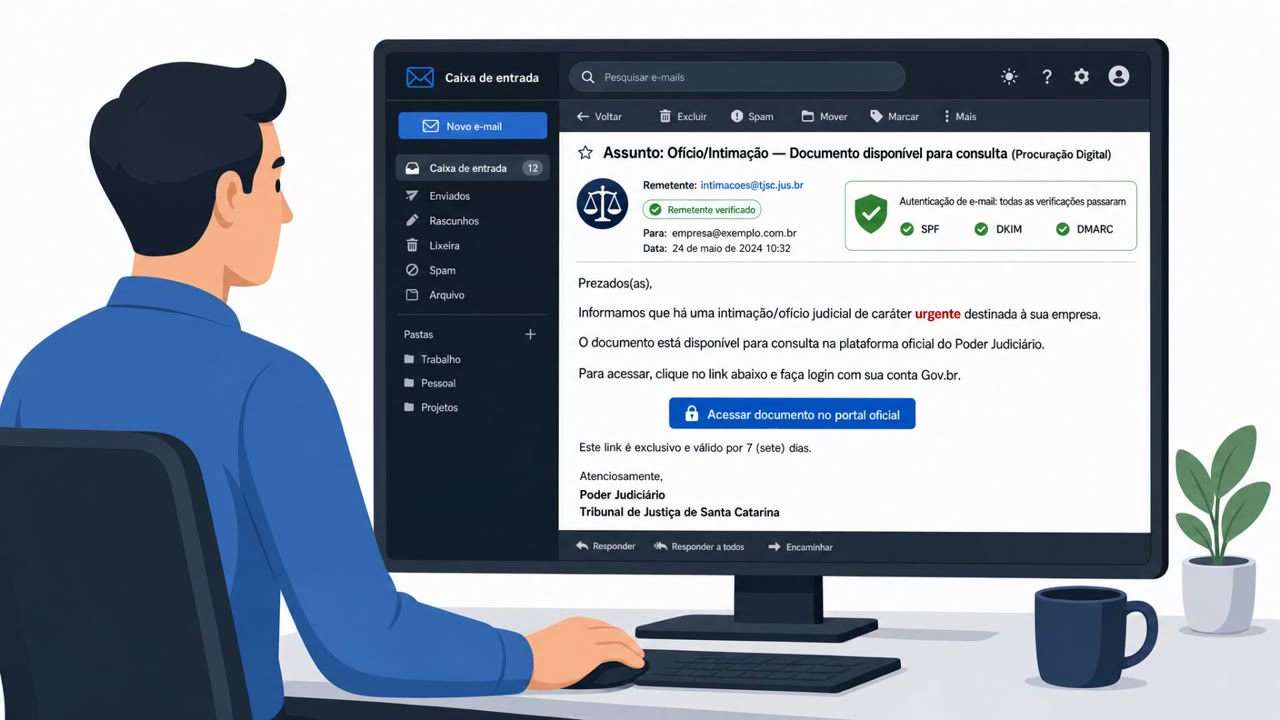
PhantomEnigma Phishes via Hijacked .gov.br Sites

PhantomEnigma Phishes via Hijacked .gov.br Sites

Researchers describe a real phishing-driven malware operation ("PhantomEnigma") that abuses compromised Brazilian government websites and mailboxes to appear trustworthy. Victims are lured with fake law-enforcement style documents (e.g., “Ofício” summons or “Procuração Digital”) and pushed to…

July 28, 2026
Hotel Wi‑Fi DNS Scam Steals Microsoft 365 Logins

Hotel Wi‑Fi DNS Scam Steals Microsoft 365 Logins

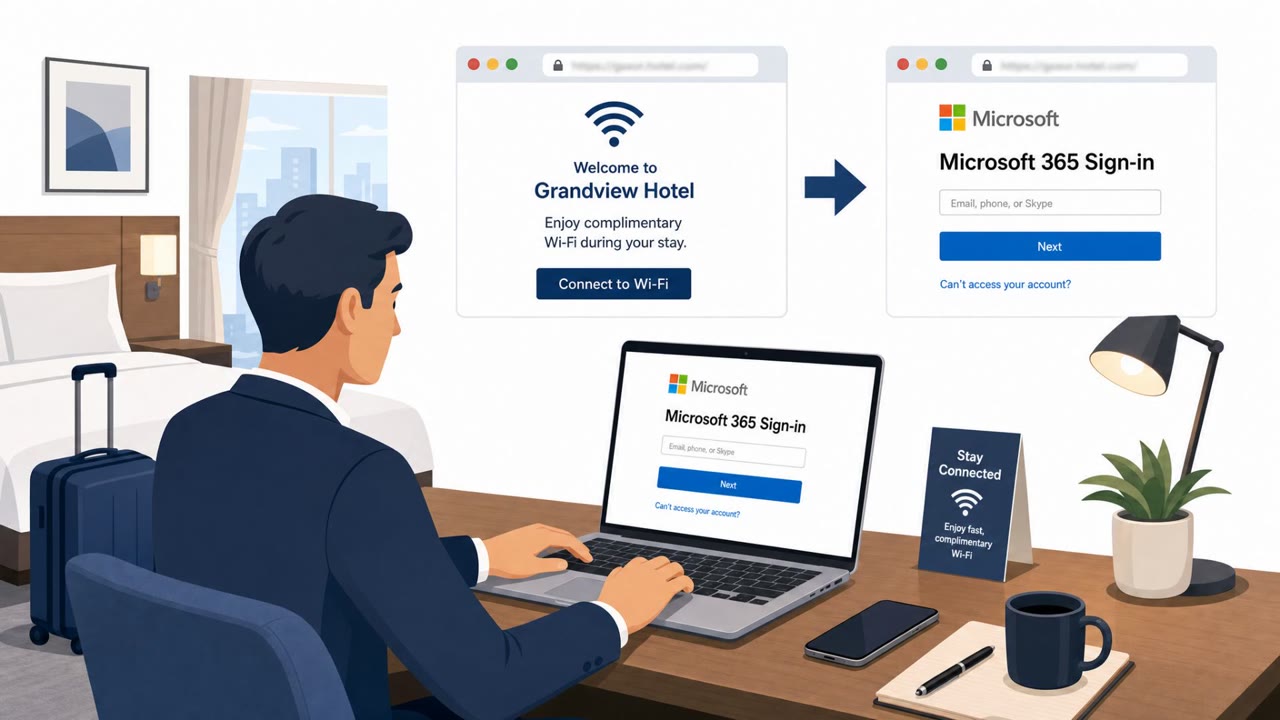
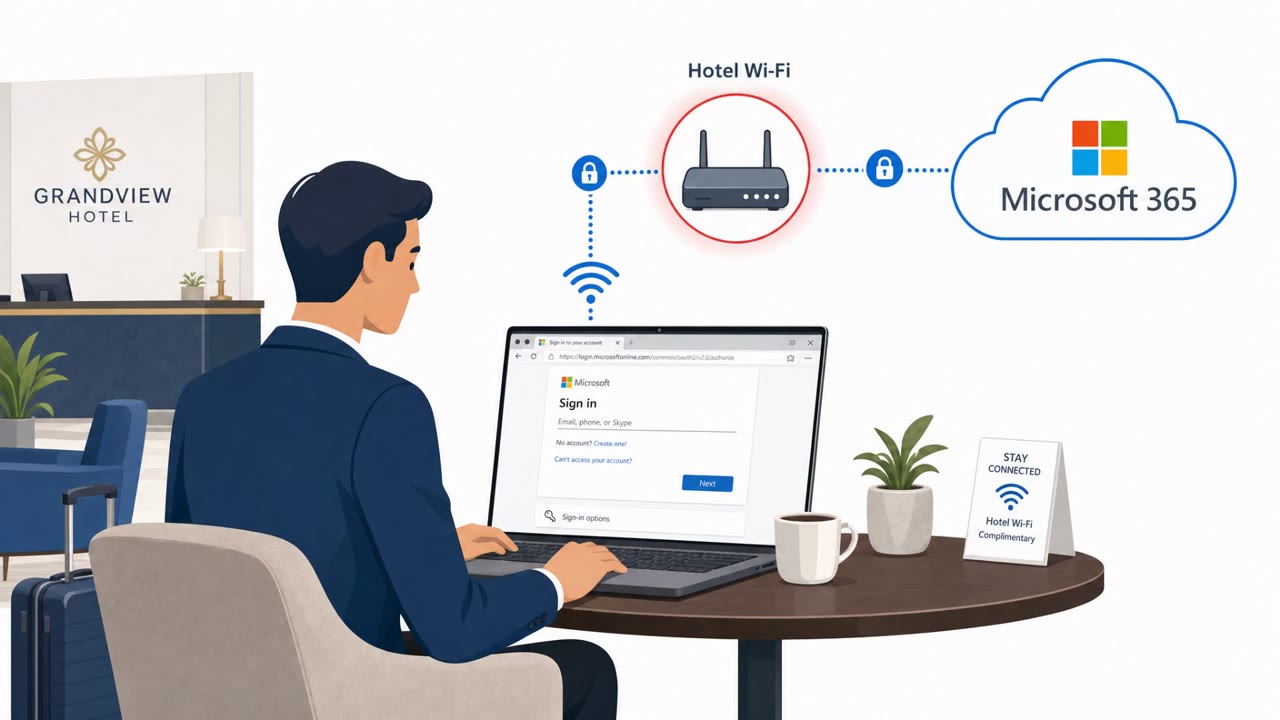
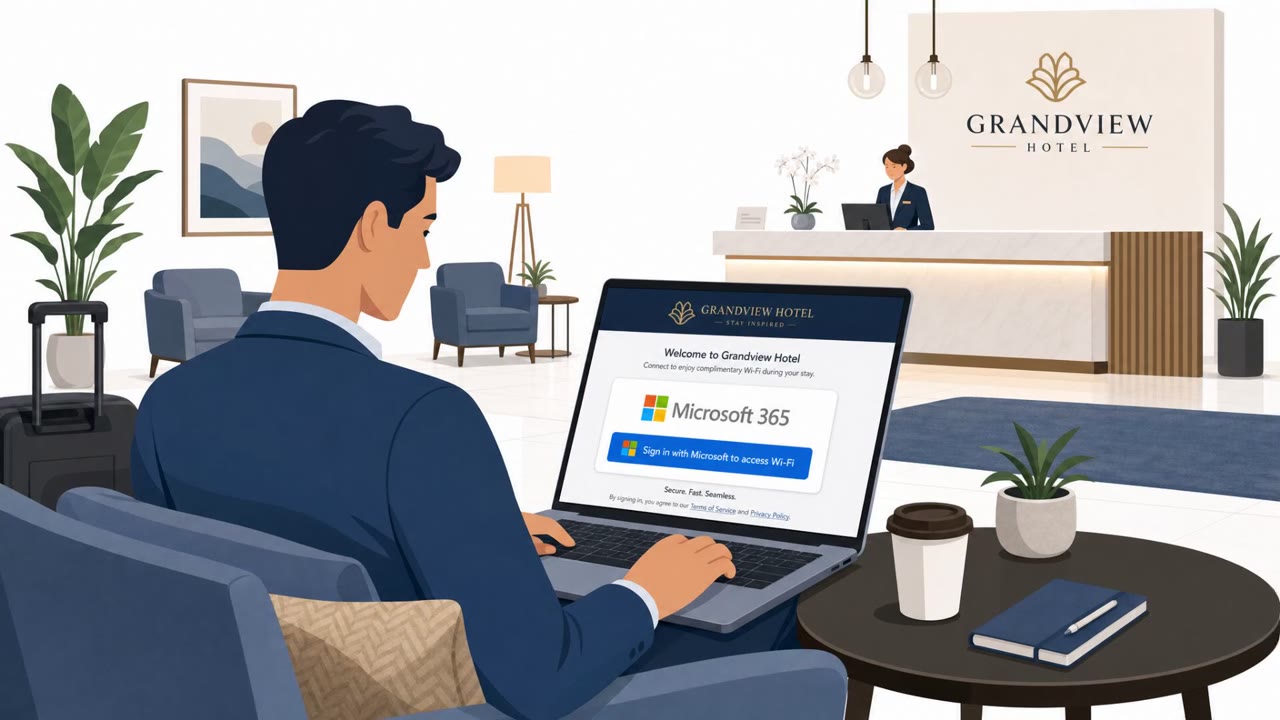
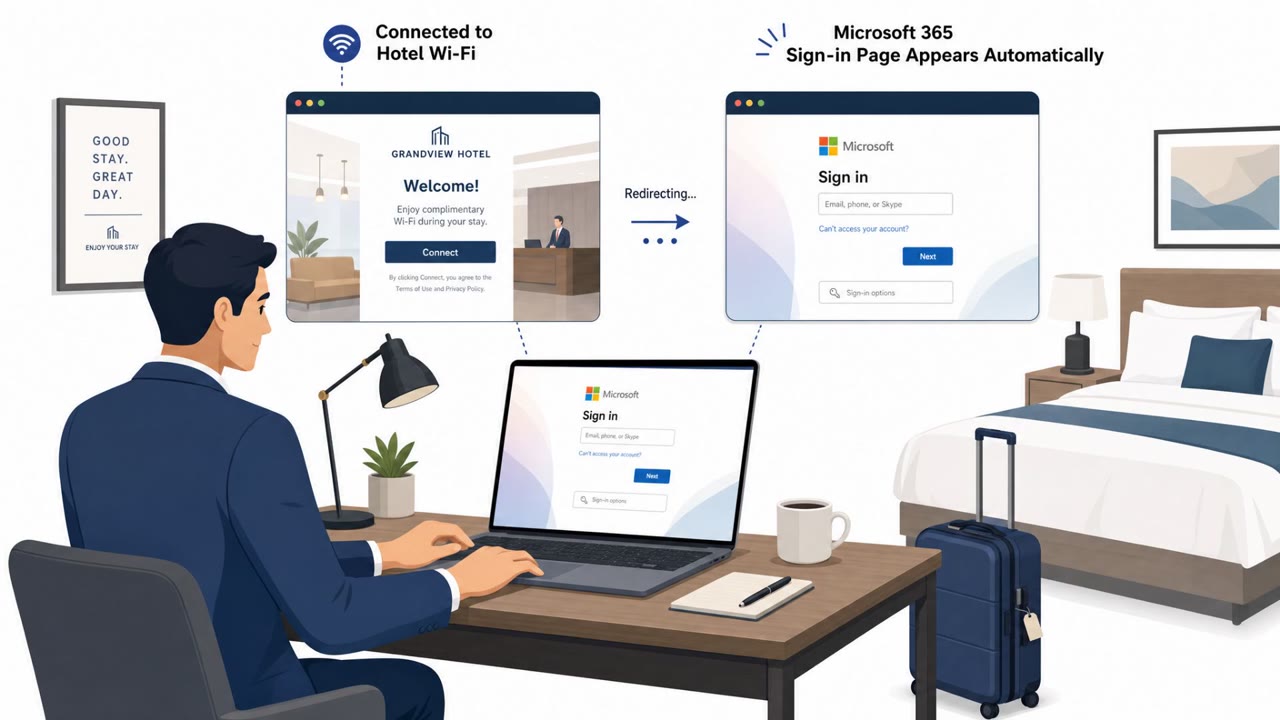
Attackers are taking over hotel and conference Wi‑Fi gateways and changing DNS settings so travelers are silently redirected to fake Microsoft 365 sign-in pages. Victims are then tricked into completing a device-code login that grants attackers a legitimate session token, often bypassing MFA. This…

July 28, 2026
Tax and SSA Lures Push Stealth Malware via Cruciferra

Tax and SSA Lures Push Stealth Malware via Cruciferra

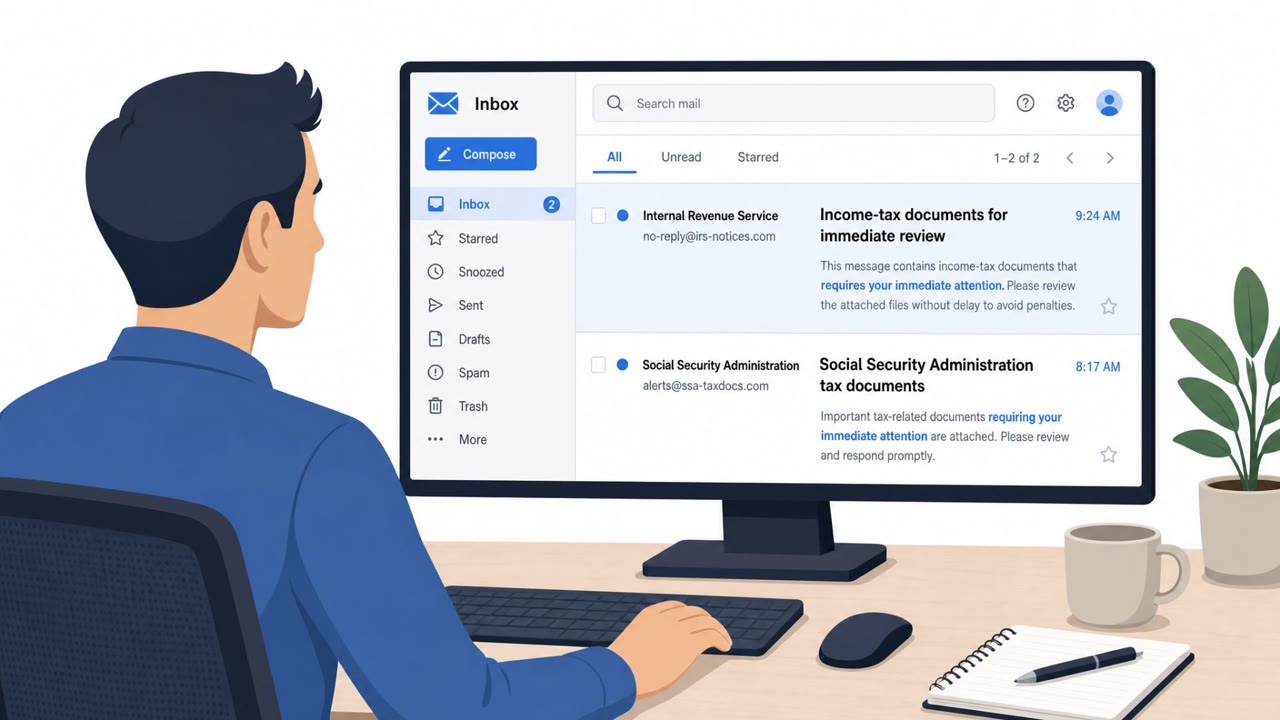
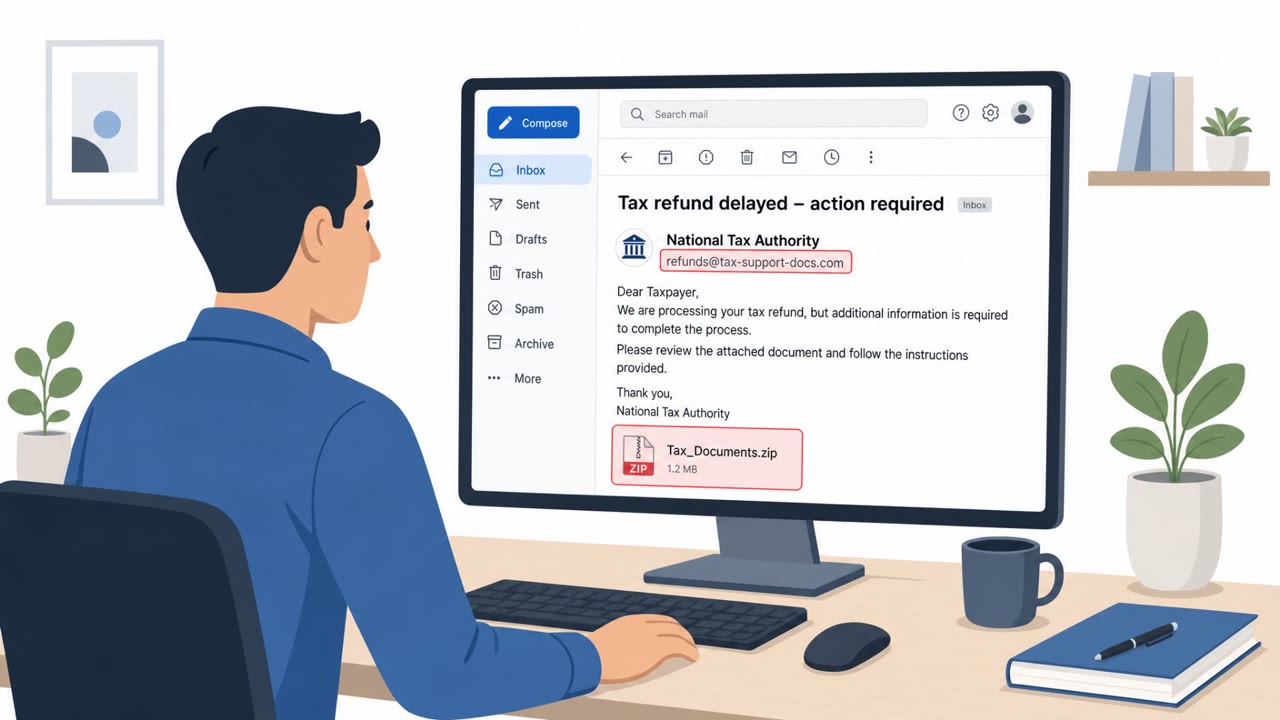
Proofpoint linked multiple real-world email campaigns to “Cruciferra,” a commercial crypter service that helps criminals hide malware from security tools. The campaigns used familiar social-engineering themes, tax documents, U.S. Social Security Administration messages, and even bed-bug complaints,…

July 28, 2026
Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Mirage Kitten Uses Fake Hiring Lures to Drop Malware

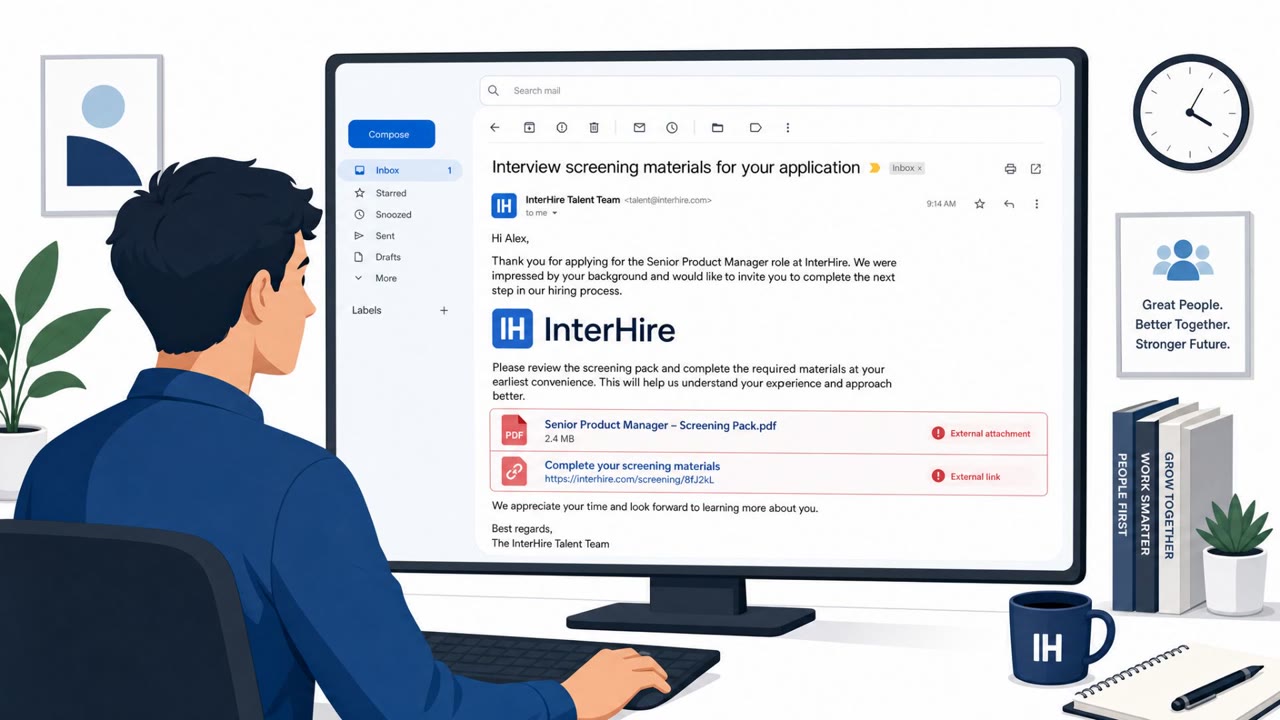
Researchers report Mirage Kitten (an espionage-focused threat group) targeted organizations in the Middle East and Africa using highly tailored spear‑phishing. The lures included recruitment-themed messages impersonating trusted brands/hiring sites and fake videoconferencing pages that redirected…

July 28, 2026
Hotel Wi‑Fi DNS Hijack Steals M365 Logins

Hotel Wi‑Fi DNS Hijack Steals M365 Logins

Researchers report attackers compromising hotel and venue Wi‑Fi “captive portal” gateways to redirect Microsoft 365 sign-ins to attacker-controlled lookalike domains. Victims can have their Microsoft 365 credentials stolen without clicking a phishing link or installing malware, because the…

July 28, 2026
Hotel Wi‑Fi Redirect Scam Steals Microsoft 365 Logins

Hotel Wi‑Fi Redirect Scam Steals Microsoft 365 Logins

Attackers are compromising hotel and conference center Wi‑Fi gateways and changing DNS settings so business travelers are silently redirected to fake Microsoft 365 login pages. When victims sign in, attackers steal passwords and potentially session tokens, allowing account takeover even when…

July 27, 2026
Fake ShinyHunters Sextortion Demands $2,000

Fake ShinyHunters Sextortion Demands $2,000

A sextortion email campaign is using real leaked email addresses from ShinyHunters-related data dumps to make threats sound credible. The scammers impersonate the “ShinyHunters hacking group,” claim they recorded victims via webcam, and demand $2,000 in Bitcoin within 48 hours. Reporting indicates…

July 27, 2026
Hotel Wi‑Fi Hijacks Microsoft 365 Logins

Hotel Wi‑Fi Hijacks Microsoft 365 Logins

Researchers report attackers compromising hotel and conference Wi‑Fi gateway equipment to silently redirect travelers to fake Microsoft 365 sign-in pages, without sending phishing emails. In some cases, attackers also abuse Microsoft device-code login prompts so victims unintentionally approve…

July 27, 2026
Voicemail Lure Drives Microsoft Device-Code Phish

Voicemail Lure Drives Microsoft Device-Code Phish

A voicemail-themed phishing campaign (“Kali365 Ringer”) targeted financial and insurance organizations using a missed-call notification and a Google Sites page to appear legitimate. Victims were redirected through multiple trusted services and instructed to approve a Microsoft device-code login…

July 27, 2026
Tax and SSA Phish Push Cruciferra Malware Loader

Tax and SSA Phish Push Cruciferra Malware Loader

Researchers report multiple real-world email phishing campaigns that used tax and government-benefit themes to trick people into downloading malware. The campaigns used a “crypter” service called Cruciferra to hide malicious files and help malware run while avoiding detection. Targets included…

July 27, 2026
Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

ReliaQuest reports attackers are compromising public Wi‑Fi “captive portal” gateways (such as in hotels and conference centers) and changing their DNS settings to redirect users to attacker-controlled pages. The goal is to harvest traveling employees’ Microsoft 365 credentials using…

July 27, 2026
Hotel Wi‑Fi DNS Trick Steals Microsoft 365 Logins

Hotel Wi‑Fi DNS Trick Steals Microsoft 365 Logins

Researchers found attackers taking over hotel and conference-center Wi‑Fi gateways and silently redirecting guests to fake Microsoft 365 sign-in pages to steal credentials. In some cases, the attackers also tried to route broader device traffic through a malicious proxy (WPAD) or trick users into…

July 26, 2026
Insurance Phish Turns OTPs Into Live Account Hijacks

Insurance Phish Turns OTPs Into Live Account Hijacks

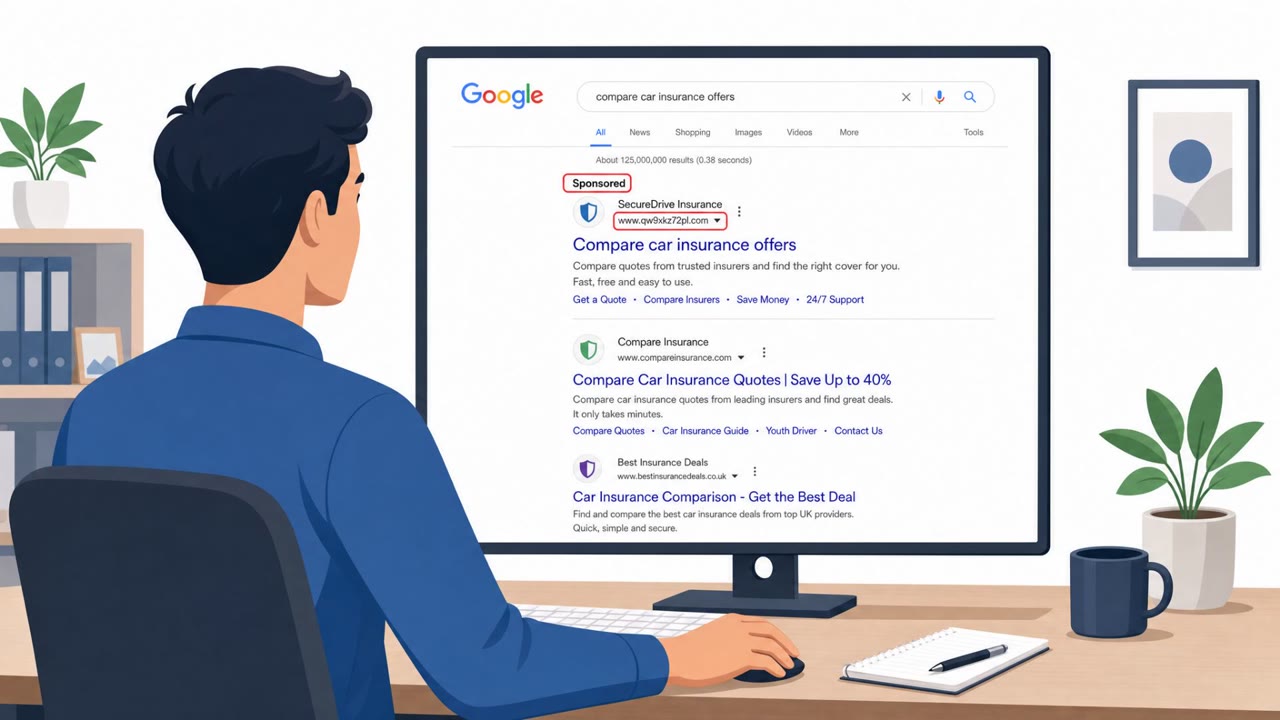
Researchers observed insurance-themed phishing that doesn’t just steal passwords, it hijacks accounts in real time while the victim is actively logging in. The attack often starts with sponsored Google ads that lead to convincing fake insurance portals, which immediately prompt victims for one-time…

July 25, 2026
Fake Zoom/Teams Calls Used to Steal Crypto Wallets

Fake Zoom/Teams Calls Used to Steal Crypto Wallets

North Korea-linked BlueNoroff is using fake Zoom and Microsoft Teams meeting pages shared from hijacked trusted contacts (often via Telegram) to trick victims into “updating” Zoom/Teams and running malicious commands. The phishing kit also fingerprints the victim’s browser to identify installed…

July 24, 2026
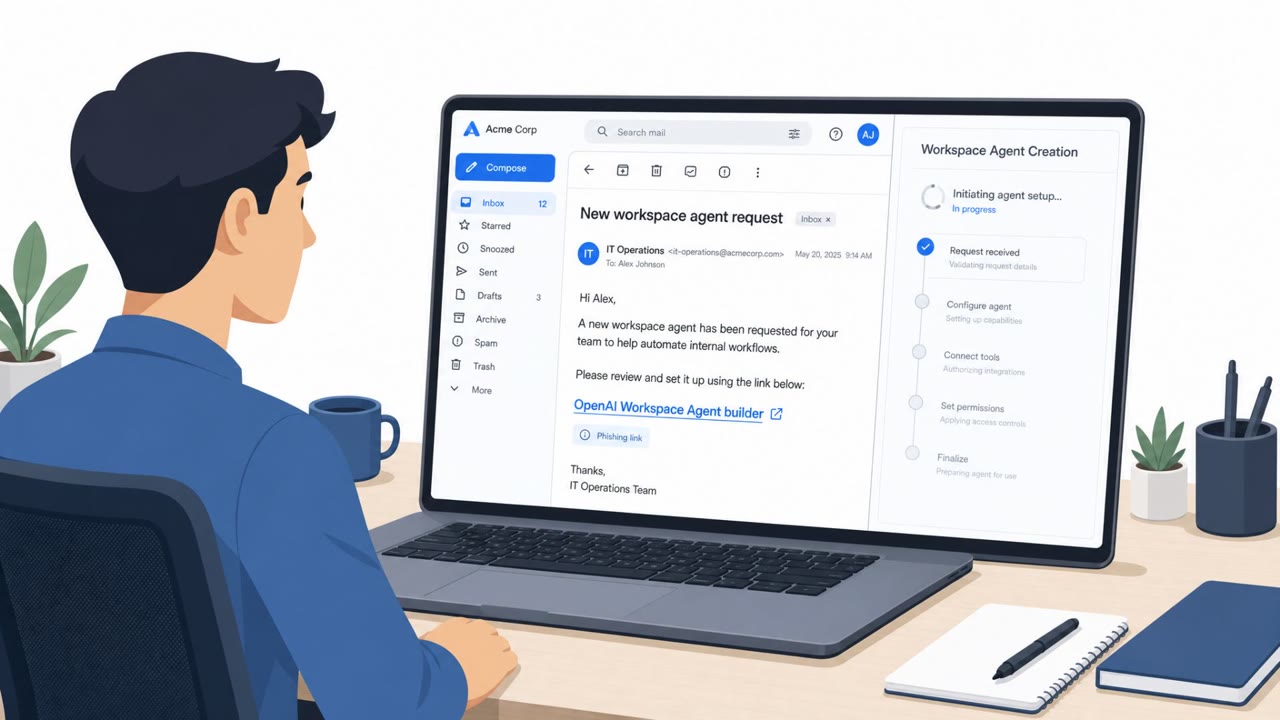
Phishing Link Could Plant a Rogue ChatGPT Agent

Phishing Link Could Plant a Rogue ChatGPT Agent

Researchers described a now-patched flaw ("AgentForger") where a single benign-looking ChatGPT link could silently create and publish an attacker-controlled Workspace Agent inside a company. If an employee was already logged in and had connected apps (like email, Drive, Slack, or Teams), the agent…

July 24, 2026
Lampion Phishing Hits Portugal With Fake Brands

Lampion Phishing Hits Portugal With Fake Brands

Researchers report that the Lampion banking Trojan is spreading in Portugal through phishing emails that impersonate legitimate private-sector entities. Victims who follow the lure end up with a credential-stealing remote-access tool (RAT) that can overlay fake login screens on banking sites to…

July 24, 2026
Fake ChatGPT Billing Emails Steal Card Details

Fake ChatGPT Billing Emails Steal Card Details

Check Point reports that OpenAI’s ChatGPT became a top-10 most impersonated brand in Q2 2026 phishing. One observed example used a fake “ChatGPT Plus payment failed” billing email to drive victims to a credit-card theft page. The report also notes other brand-impersonation scams using cloned stores…

July 24, 2026
AgentForger Turns AI Agents Into Insider Threats

AgentForger Turns AI Agents Into Insider Threats

Zenity Labs described a real phishing-based technique (“AgentForger”) that could silently create an autonomous AI agent inside an OpenAI workspace after a single click. The planted agent can keep running on a schedule, read and act across connected tools like Outlook/Slack/Drive, and execute new…

July 24, 2026
Zero-Click Emails Hit Zimbra Users in Espionage Push

Zero-Click Emails Hit Zimbra Users in Espionage Push

Government agencies and security firms warn that Russia-aligned hackers are using “zero-click” phishing emails to compromise organizations using Zimbra webmail. The attack hides a malicious JavaScript payload inside an email so it runs when the message is opened, aiming to steal recent email,…

July 23, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo