Recent Government Cyber Attacks

Page 8 of 13
Fake Recruiter Lure Drops NodeRabbit RAT

Fake Recruiter Lure Drops NodeRabbit RAT

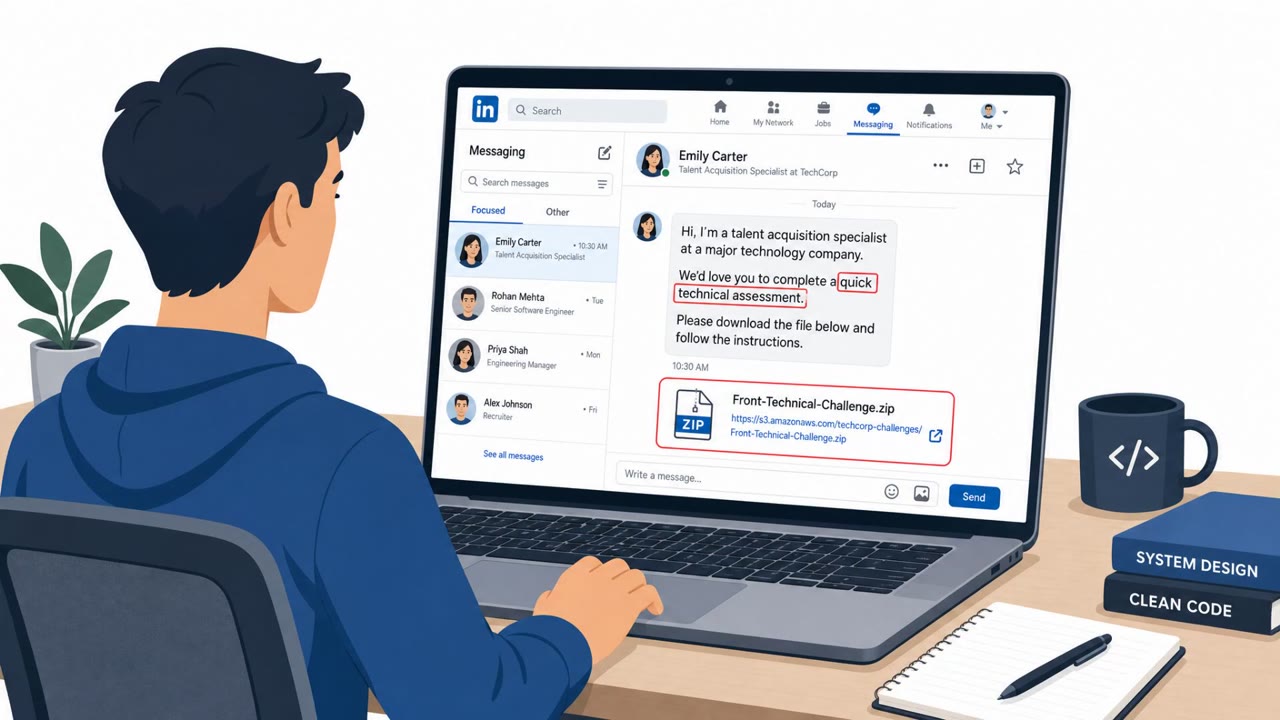
Researchers tied Mirage Kitten to a job-recruiting scam that targets developers via LinkedIn and job platforms. Victims are sent a “technical assessment” ZIP file hosted on legitimate cloud storage; running the project silently installs a remote-access trojan (NodeRabbit) that lets attackers…

September 1, 2026
Fake IT Calls Push AnyDesk in Brazil Heists

Fake IT Calls Push AnyDesk in Brazil Heists

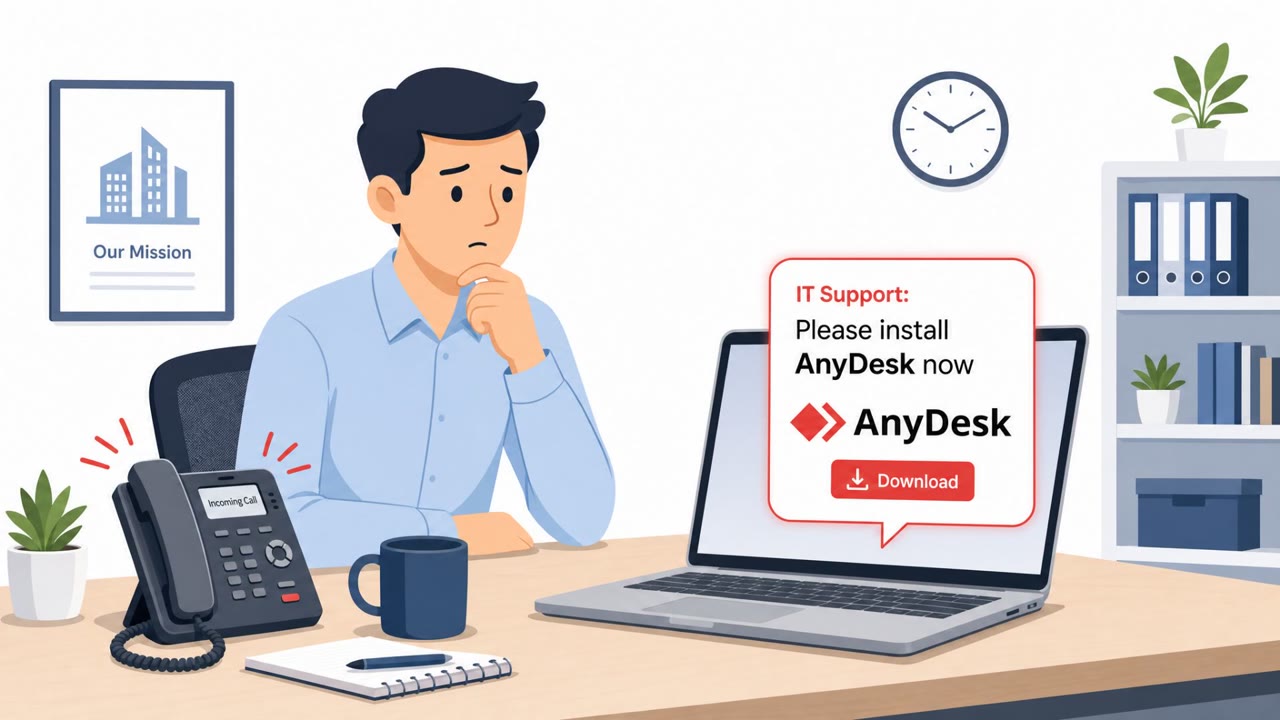
Mandiant and Google report that the financially motivated group BREEZE COMET compromised Brazilian organizations to enable fraudulent bank transfers. The actor used human manipulation (including fake IT support calls) and believable “tax/receipt” downloads hosted on trusted-looking government…

September 1, 2026
DPRK Fake Hires Spread to Healthcare & Sales

DPRK Fake Hires Spread to Healthcare & Sales

Investigations found suspected North Korean operatives getting hired into real companies by impersonating other people, including roles outside IT such as healthcare and sales/marketing. The workflow relies on fake or stolen identity documents, remote-access tooling, and deception during interviews…

August 31, 2026
Vishing + Phishing Drive Major Data Theft Claims

Vishing + Phishing Drive Major Data Theft Claims

This weekly threat bulletin highlights multiple real-world incidents, including a healthcare data breach claim where attackers reportedly used phone-based social engineering (vishing) to compromise identity accounts and access cloud apps. It also describes a large-scale “debt relief” email phishing…

August 31, 2026
DocuSign Share Lure Steals Microsoft 365 Sessions

DocuSign Share Lure Steals Microsoft 365 Sessions

Researchers described an active phishing operation using real DocuSign notifications to trick employees into opening a fake “remittance-advice” document and clicking a hidden malicious link. The attack routes victims through legitimate Microsoft/Google pages before landing on an…

August 28, 2026
DIA Insider Used Email to Offer Secrets to “Spy”

DIA Insider Used Email to Offer Secrets to “Spy”

A Defense Intelligence Agency IT specialist pleaded guilty after an FBI sting caught him trying to provide classified information to someone he believed was a foreign government spy. The case includes a clear, simulation-ready workflow: an initial outreach email offering secrets, a move to…

August 28, 2026
APT28 Lures Diplomats with Fake Ministry Docs

APT28 Lures Diplomats with Fake Ministry Docs

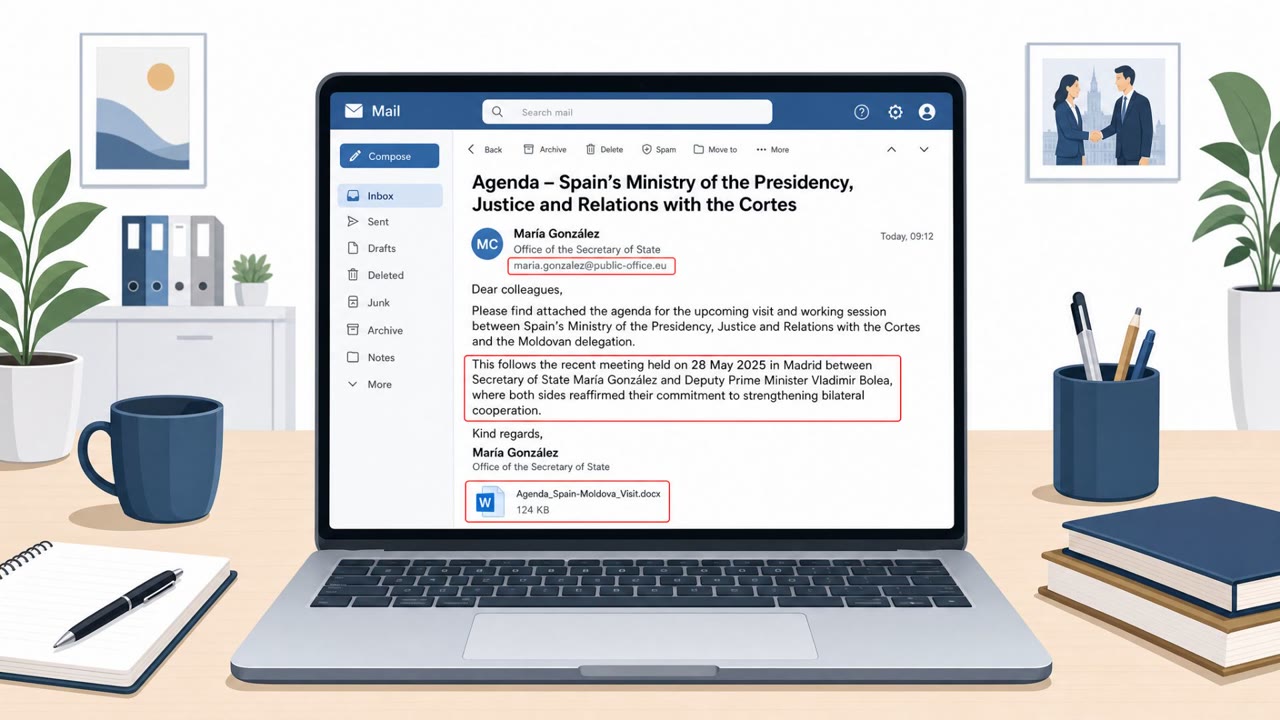
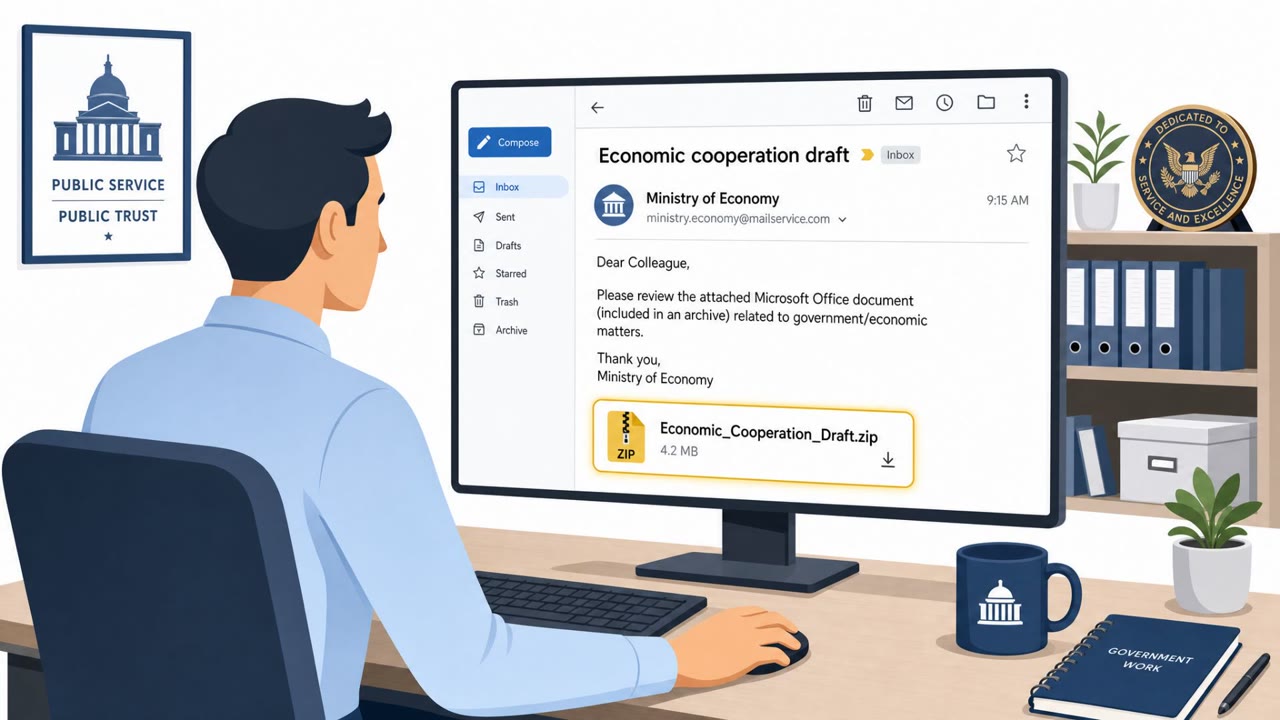
Recorded Future reports a real espionage campaign attributed to Russia-linked BlueDelta/APT28 targeting European government and diplomatic organizations. Attackers used diplomatic-themed, macro-enabled Word documents (including content impersonating Spain’s Ministry of the Presidency) to trick…

August 28, 2026
APT28 Uses Diplomatic Word Lures to Drop HOOKEDGE

APT28 Uses Diplomatic Word Lures to Drop HOOKEDGE

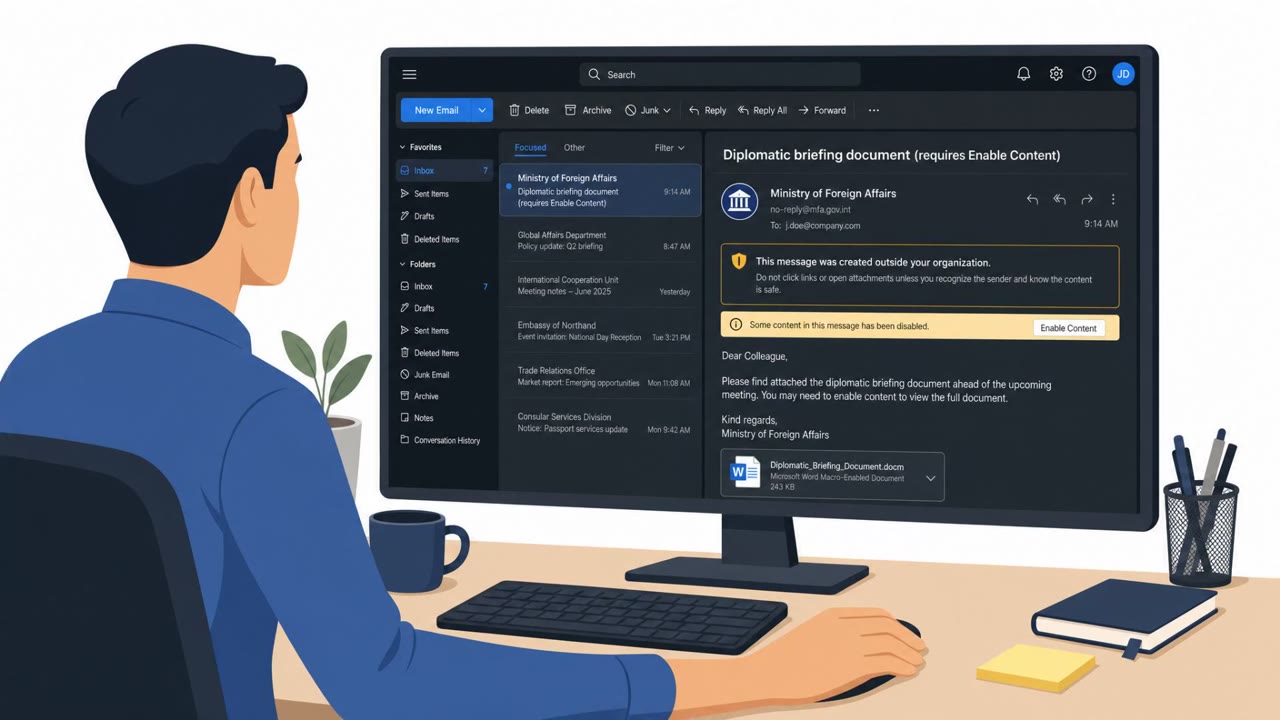
Researchers report real-world campaigns targeting European government and diplomatic organizations using diplomatic-themed Microsoft Word documents. Victims are prompted to click “Enable Content,” which runs malicious macros that install the HOOKEDGE backdoor and connect to webhook-based…

August 28, 2026
Dark Caracal Phishes Tax Lures With SVG Files

Dark Caracal Phishes Tax Lures With SVG Files

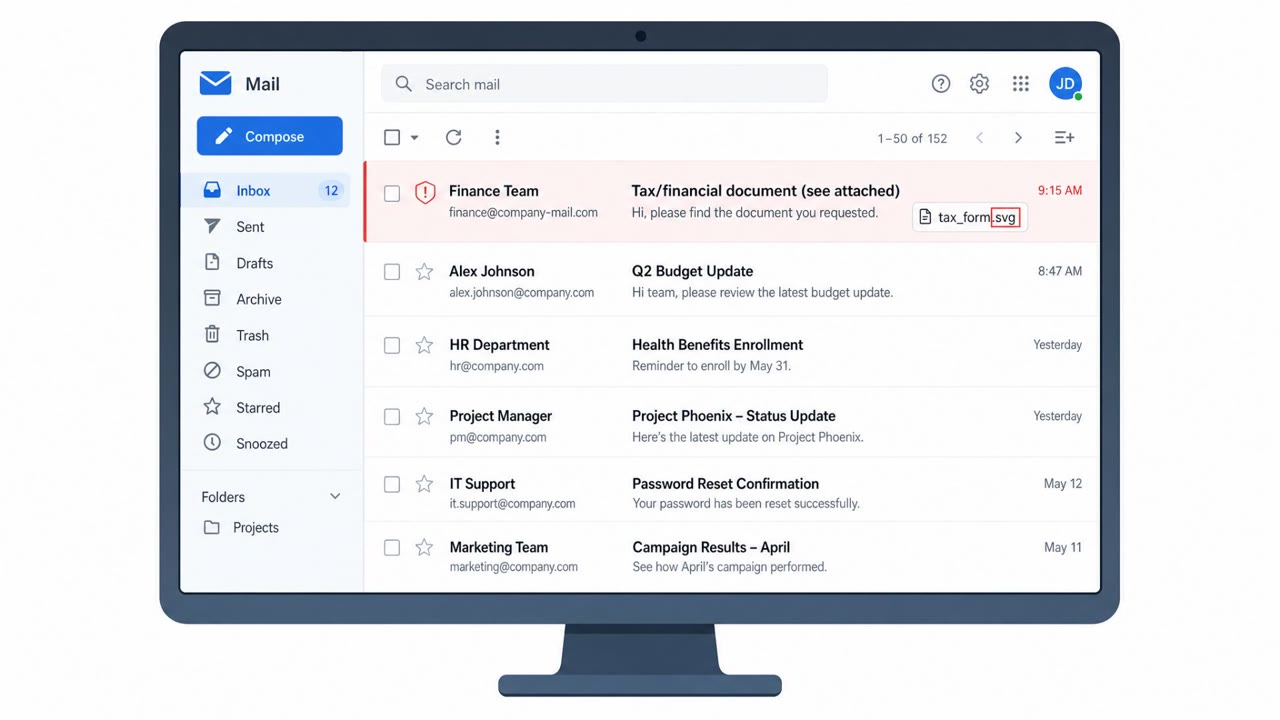
Researchers linked a June 2026 intrusion at a communications organization in Venezuela to the Dark Caracal espionage group. The attackers used phishing emails with financial/tax-themed lures and weaponized SVG attachments that redirected victims through URL shorteners to an attacker site hosting…

August 27, 2026
Spark RAT Phish Hits Cambodia With “Official” Lures

Spark RAT Phish Hits Cambodia With “Official” Lures

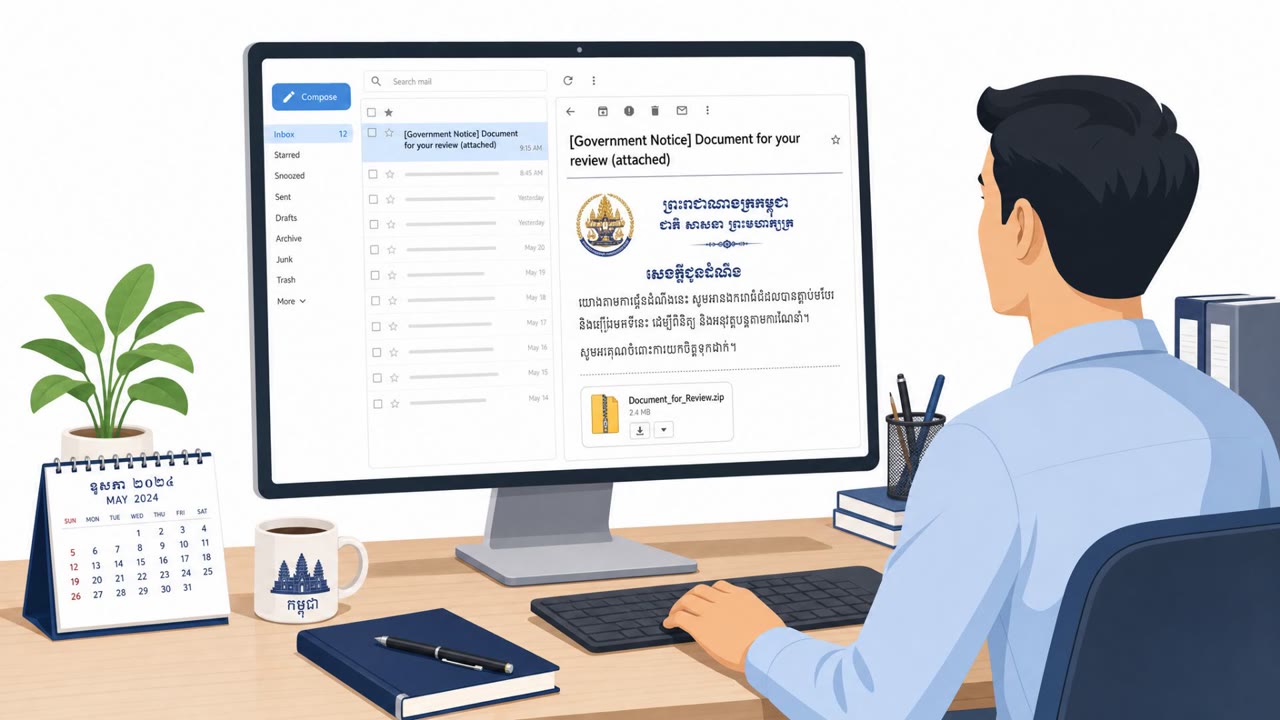
A real campaign targeting people and organizations in Cambodia uses phishing emails with localized “official-looking” themes to trick recipients into running an installer from a compressed file. Once executed, the malware chain deploys Spark RAT for remote control and uses a vulnerable OPSWAT…

August 27, 2026
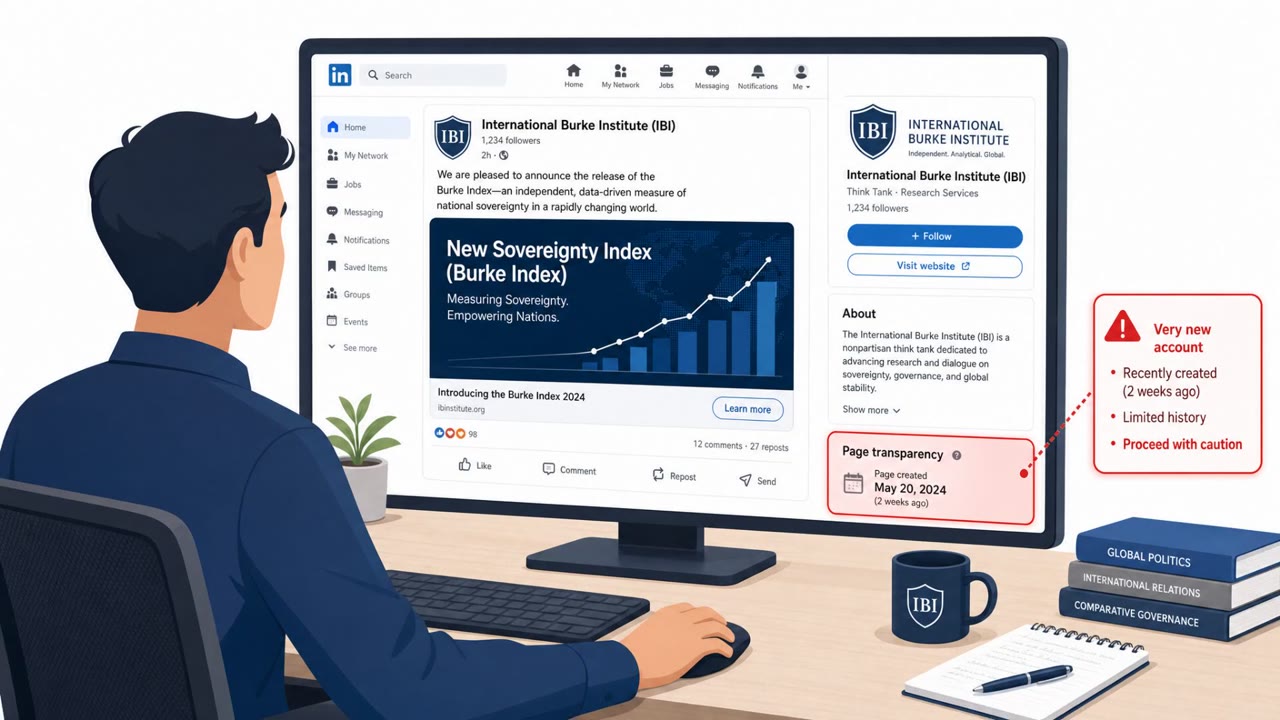
Fake Think Tank Pushed Pro‑Russia Content Using AI

Fake Think Tank Pushed Pro‑Russia Content Using AI

OpenAI says it removed Russia-linked ChatGPT accounts used to support a covert influence campaign promoting a fake think tank brand called the “International Burke Institute” (IBI). The operators used AI mainly to create and translate social media posts that looked credible and drove people to an…

August 27, 2026
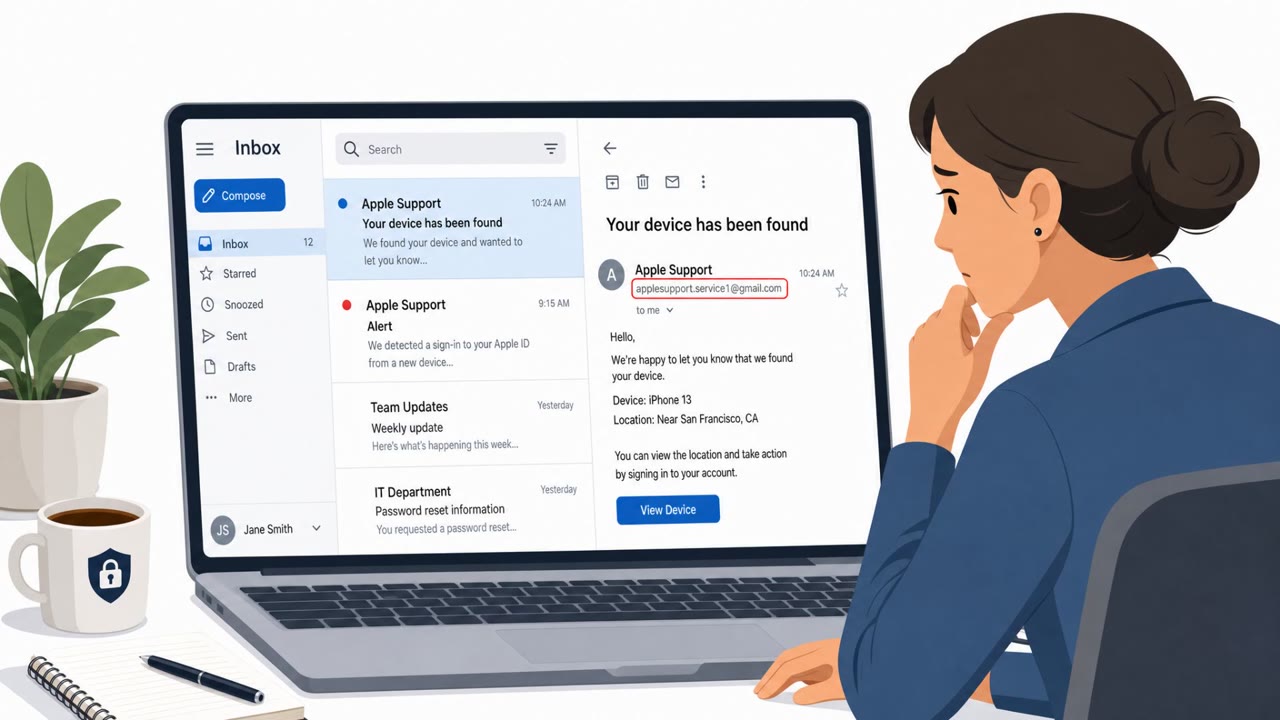
AI “Apple Support” Calls Steal Passcodes & 2FA

AI “Apple Support” Calls Steal Passcodes & 2FA

Researchers uncovered a phishing-as-a-service platform (“AnonyMousKIT”) used by phone thieves to trick victims into handing over iPhone passcodes, Apple ID passwords, and live 2FA codes so thieves can remove Apple’s Activation Lock. The operation uses Apple-branded emails/pages and AI voice agents…

August 26, 2026
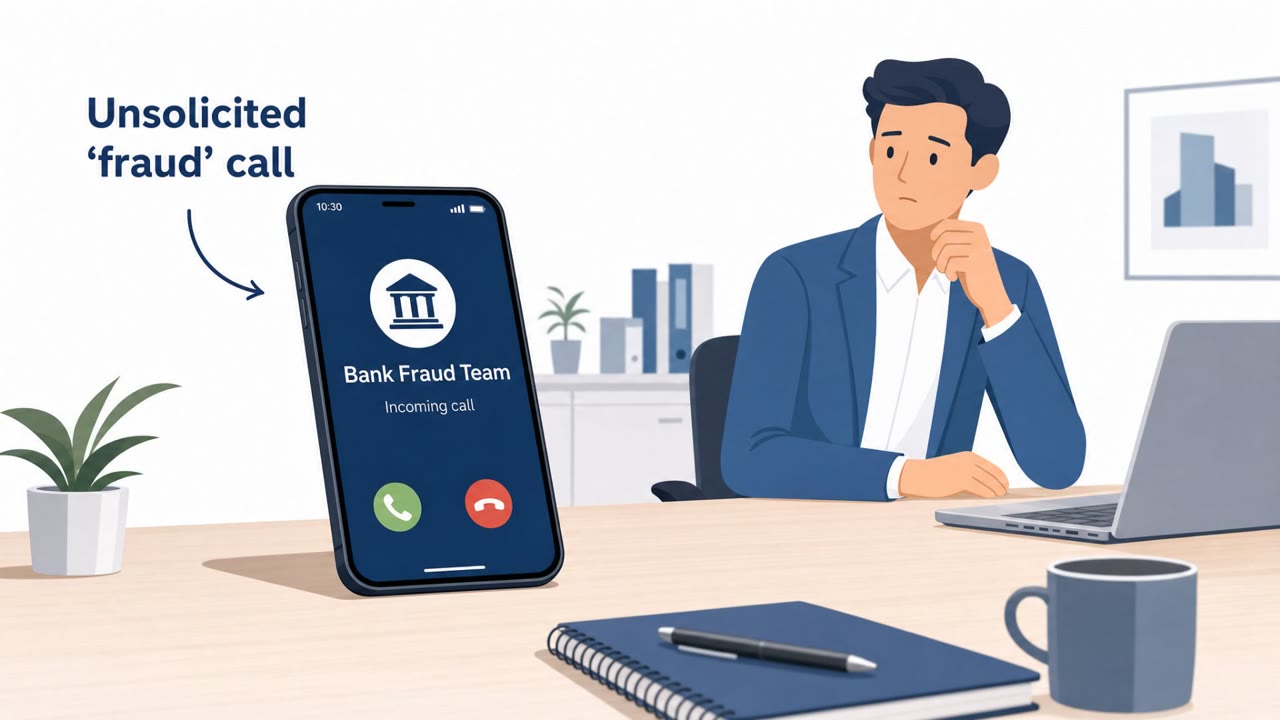
Fake Bank Calls and ClickFix Drive Data Theft

Fake Bank Calls and ClickFix Drive Data Theft

The roundup describes multiple real-world attacks where criminals manipulate people, not just systems, such as fake bank support calls that trick victims into installing phone malware, and “ClickFix” lures that convince Mac users to run malicious commands. It also highlights an AI-assisted…

August 21, 2026
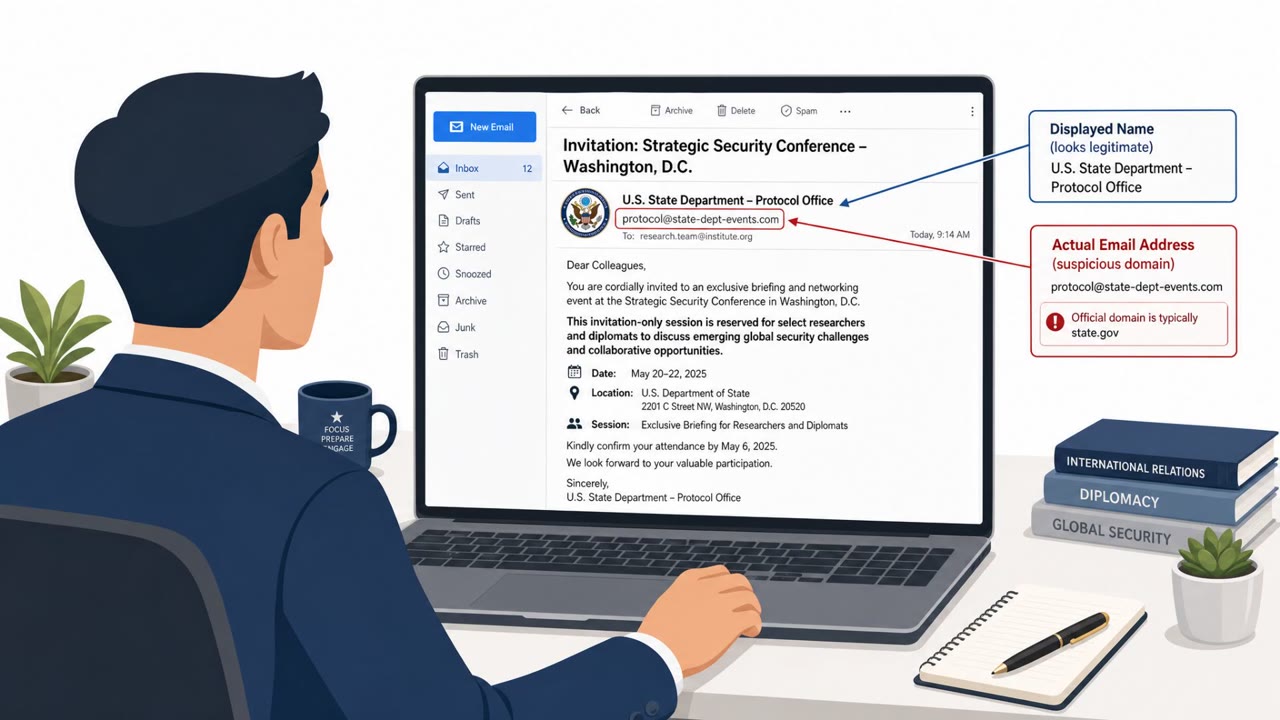
Fake Conferences Fuel OAuth and WhatsApp Phish

Fake Conferences Fuel OAuth and WhatsApp Phish

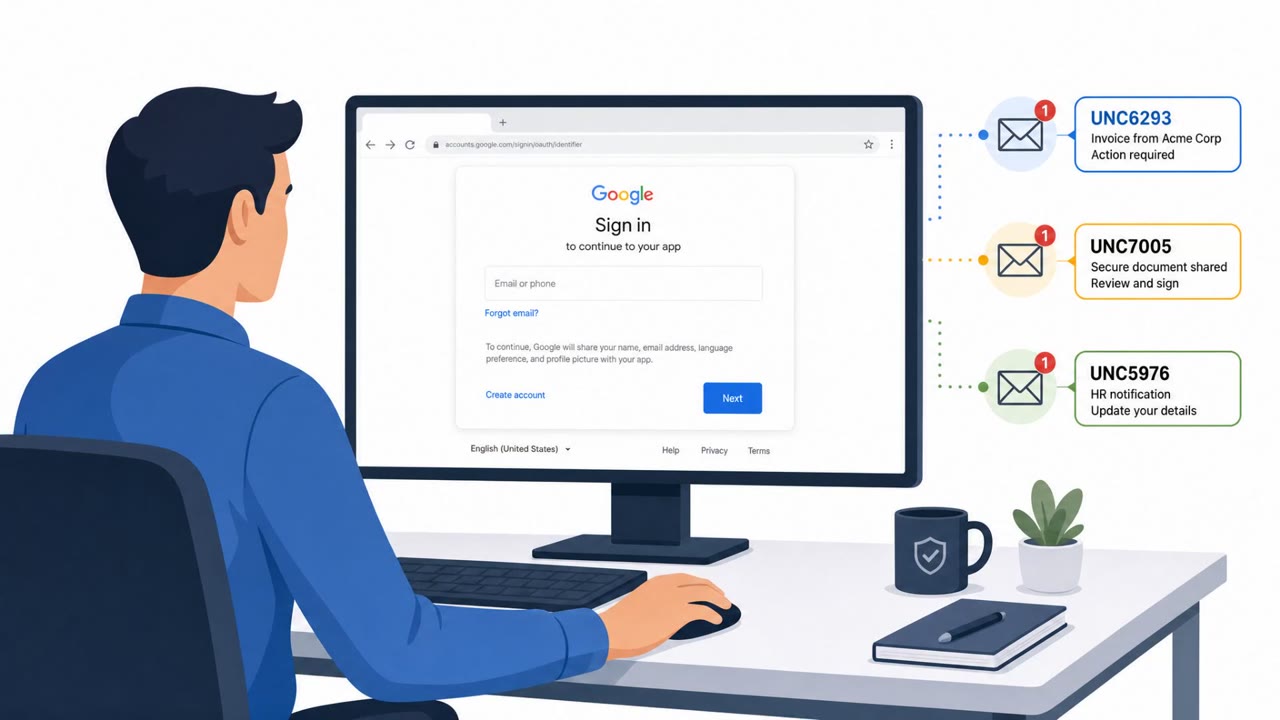
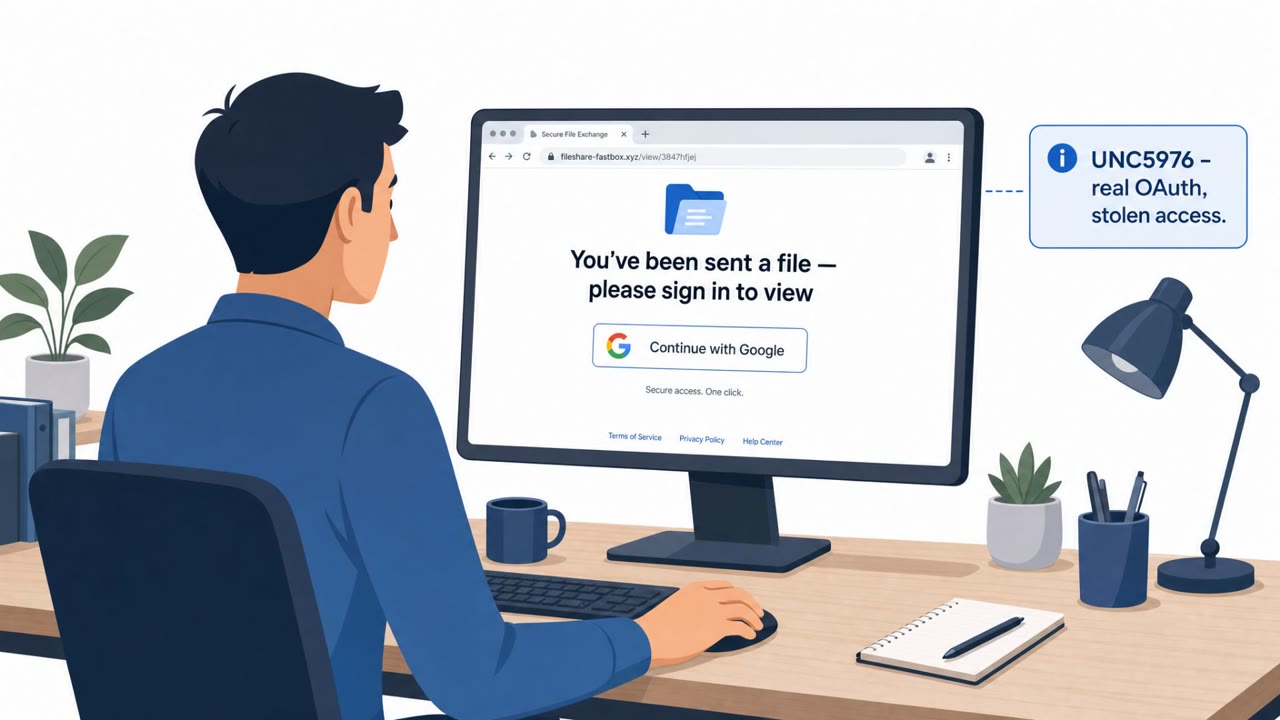
Google tracked three suspected Russia-linked groups running targeted phishing that abuses real login and authentication features (app passwords, OAuth, and device codes) to get into accounts. The lures often look like legitimate conference or diplomatic invitations, and some campaigns spoof…

August 21, 2026
Russian Spy Phish Uses Legit OAuth Logins

Russian Spy Phish Uses Legit OAuth Logins

Google says three suspected Russian cyber-espionage groups are running highly targeted phishing campaigns against people in government, academia, defense, and think tanks in the US and Europe. A key theme is abusing legitimate Google/Microsoft OAuth login flows so the outreach looks real, tricking…

August 21, 2026
Russian Clusters Hijack Accounts via OAuth & WhatsApp

Russian Clusters Hijack Accounts via OAuth & WhatsApp

Google says multiple suspected Russia-linked espionage clusters targeted academics, government, and defense-related personnel by abusing legitimate sign-in features instead of using obvious fake login pages. The campaigns used realistic lures (file sharing, conference invites, and “secure WhatsApp”…

August 20, 2026
SilkParasite Hits Central Asia via Phish Docs

SilkParasite Hits Central Asia via Phish Docs

Bitdefender reports a China-linked espionage campaign (“SilkParasite”) targeting government bodies in Central Asia using spearphishing emails carrying malicious Microsoft Office documents. The malware is designed to stay quiet and blend in, including using Google Drive as a communications channel…

August 20, 2026
Manic Malware Steals PINs With Fake Lock Prompts

Manic Malware Steals PINs With Fake Lock Prompts

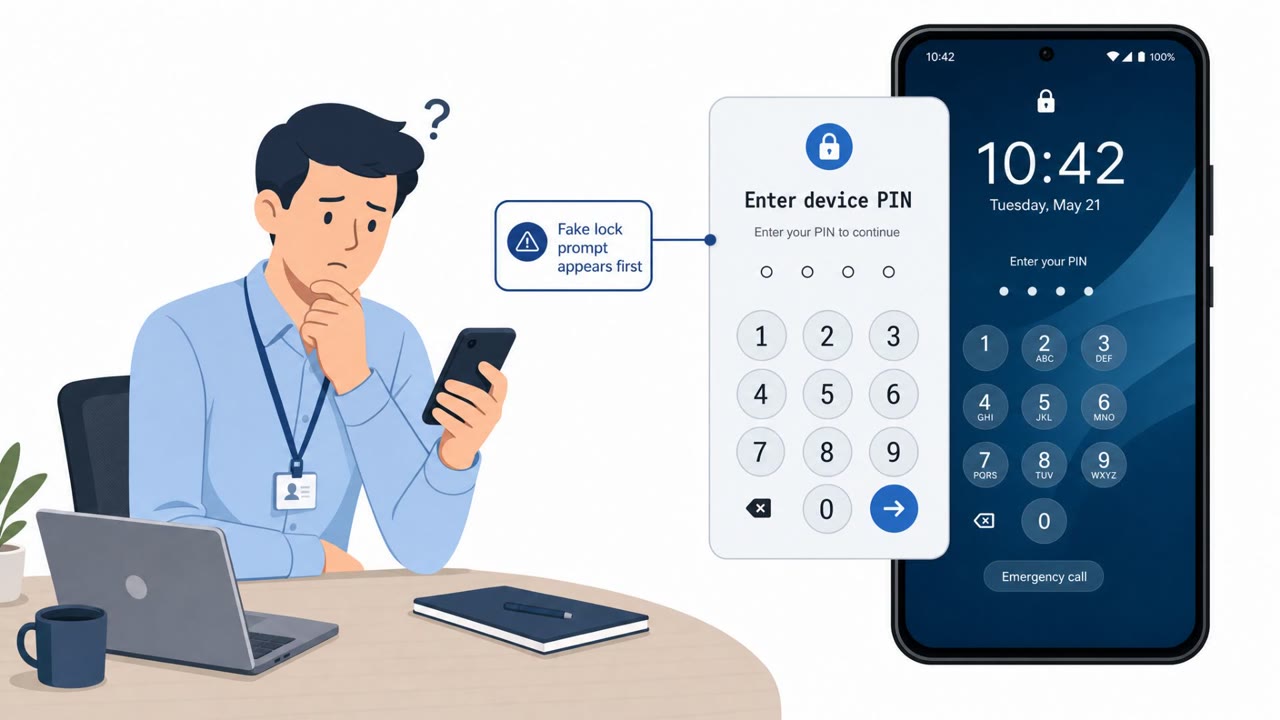
Researchers report a real Android malware operation (“Manic”) active since at least February 2026 that blends banking fraud with spyware-style surveillance. It can trick users into revealing their device PIN/pattern via a fake lock prompt and silently capture banking PIN taps, then exfiltrate…

August 20, 2026
Manic Android Spyware Uses Fake Utility Apps

Manic Android Spyware Uses Fake Utility Apps

A new Android malware family called “Manic” is being used in real campaigns targeting banking, government identity, and messaging apps, especially in Ukraine and parts of Europe. It spreads through phishing sites and “dropper” apps disguised as legitimate utilities (including a booking-app lure),…

August 20, 2026
Russian Clusters Abuse Login Flows to Steal Accounts

Russian Clusters Abuse Login Flows to Steal Accounts

Google says three suspected Russian espionage clusters are targeting academics, think tanks, diplomats, and related nonprofit staff by abusing legitimate login and verification workflows that may not look like “classic phishing.” The campaigns include app-password scams, OAuth/device-code tricks,…

August 20, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo