Recent Government Cyber Attacks

Page 9 of 13
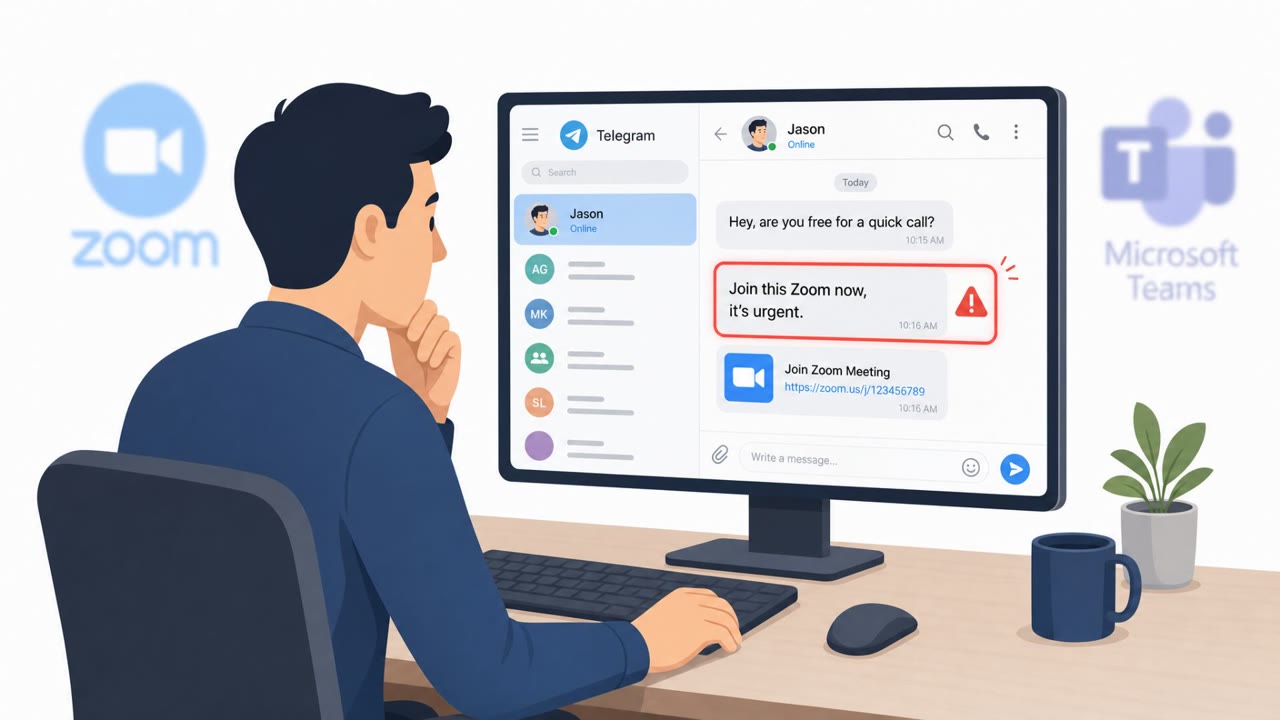
APT Groups Lure Targets Into Fake Zoom/Teams Meets

APT Groups Lure Targets Into Fake Zoom/Teams Meets

This threat trend report describes multiple real-world APT campaigns where attackers rely on social engineering and trusted services (Zoom/Teams, Telegram, webmail, GitHub) to steal credentials and access cloud accounts. Notable examples include fake meeting lures to deliver malware, and abuse of…

August 20, 2026
AI Voice Impostor Posed as Marco Rubio on Signal

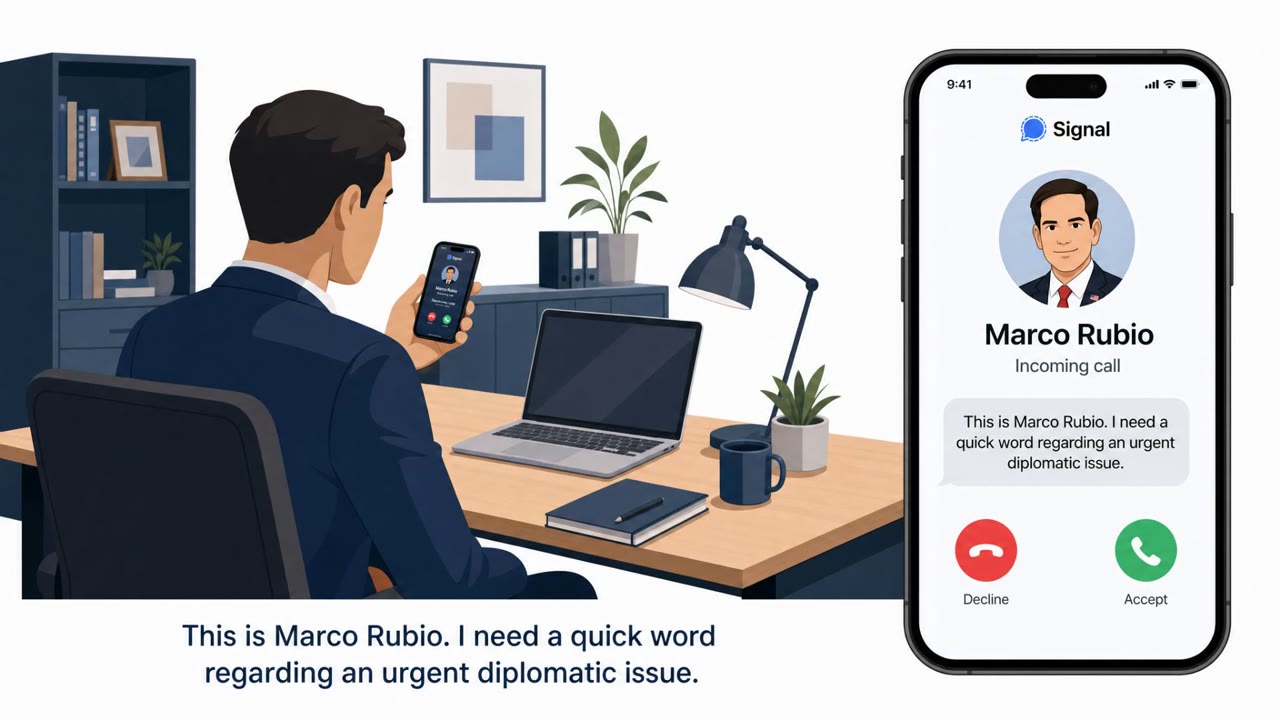
AI Voice Impostor Posed as Marco Rubio on Signal

Governments are responding to deepfakes by shifting from “detecting fakes” to building systems that prove where digital content came from and whether it was altered. The article cites real AI-impersonation activity targeting government officials, including text and AI-voice impersonation intended…

August 20, 2026
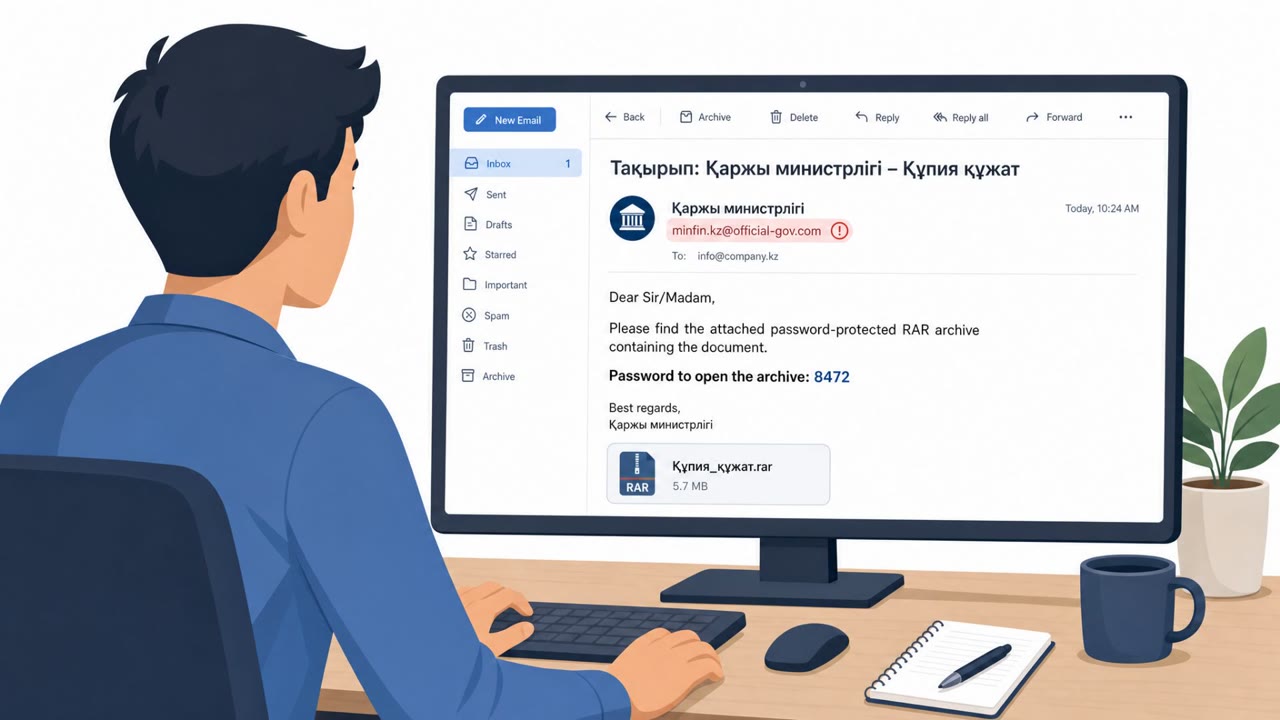
SilkParasite Uses Ministry-Themed Phishing to Drop RATs

SilkParasite Uses Ministry-Themed Phishing to Drop RATs

Researchers reported a real espionage campaign (“SilkParasite”) targeting Central Asian government bodies using spear‑phishing emails. The attack uses password‑protected RAR files containing malicious Microsoft Office documents; when opened, macros trigger a DLL sideloading chain to install remote…

August 19, 2026
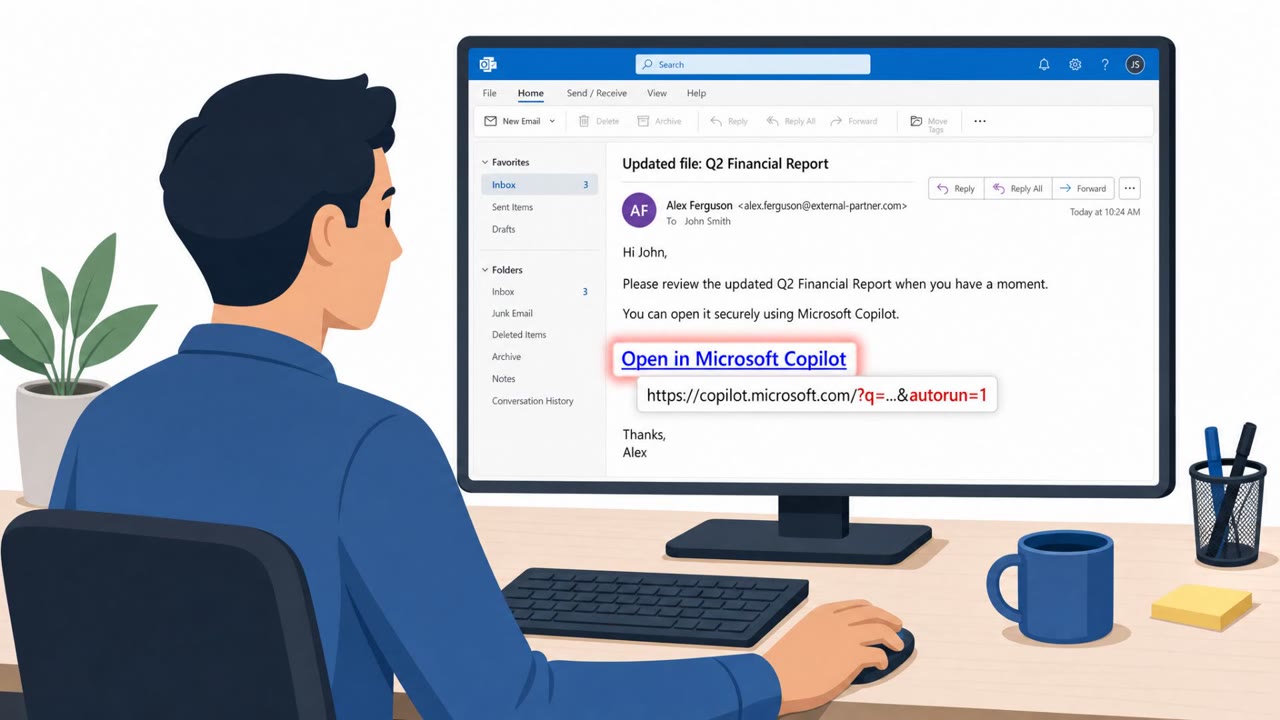
One-Click Copilot Link Triggers Data Exfil

One-Click Copilot Link Triggers Data Exfil

Researchers showed how an attacker could trick Microsoft Copilot into running a malicious prompt automatically just by getting a user to click a specially crafted link. The prompt can then make Copilot search connected accounts (like email and cloud storage) and send information to an external…

August 18, 2026
Quishing Emails Use QR Codes to Bypass Filters

Quishing Emails Use QR Codes to Bypass Filters

The article describes how attackers use QR codes in emails (“quishing”) to hide malicious links, push victims onto less-protected mobile phones, and steal credentials or MFA tokens. It also cites an FBI notice describing North Korea’s Kimsuky using QR codes in spearphishing emails targeting think…

August 18, 2026
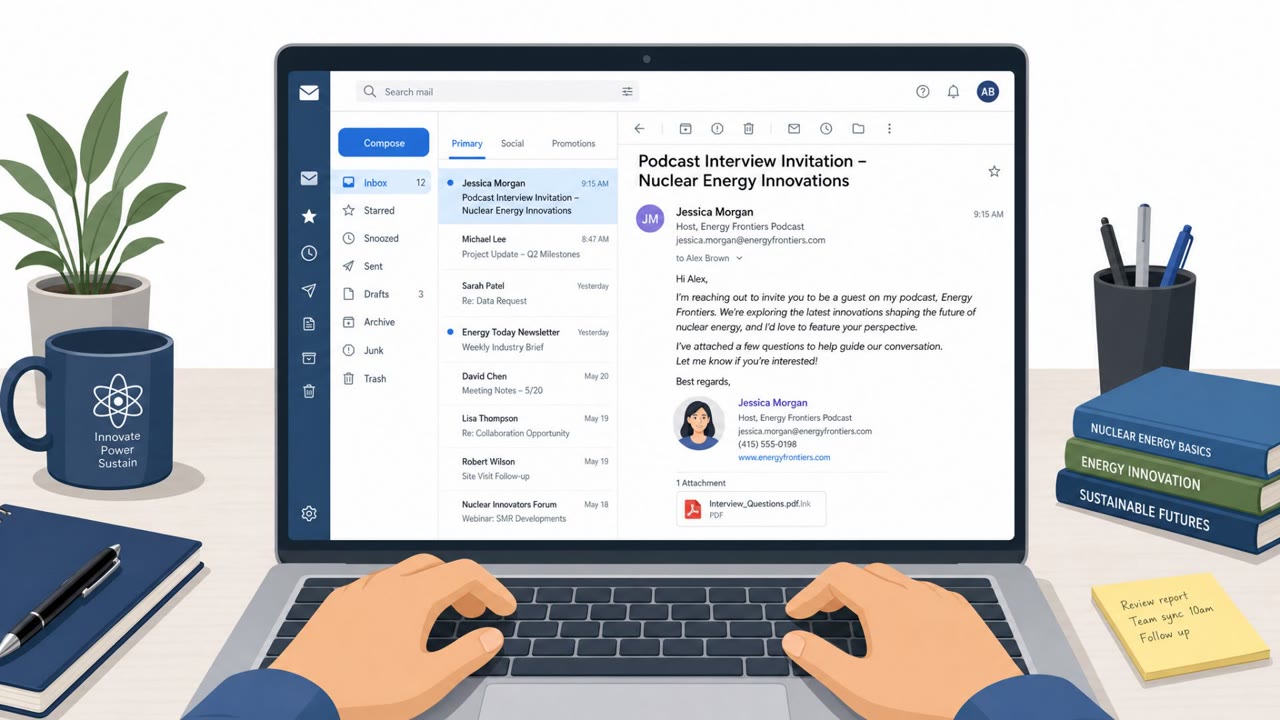
APT42 Lures Targets With Podcast Invites

APT42 Lures Targets With Podcast Invites

Researchers report Iranian-linked APT groups using legitimate cloud services to hide command-and-control traffic, and separately running spear-phishing campaigns. In the phishing cases, attackers used credible “podcast” or “interview invitation” themes to persuade targets to open a Windows shortcut…

August 17, 2026
Job Offer & Doc-Link Phishing Drive Real Breaches

Job Offer & Doc-Link Phishing Drive Real Breaches

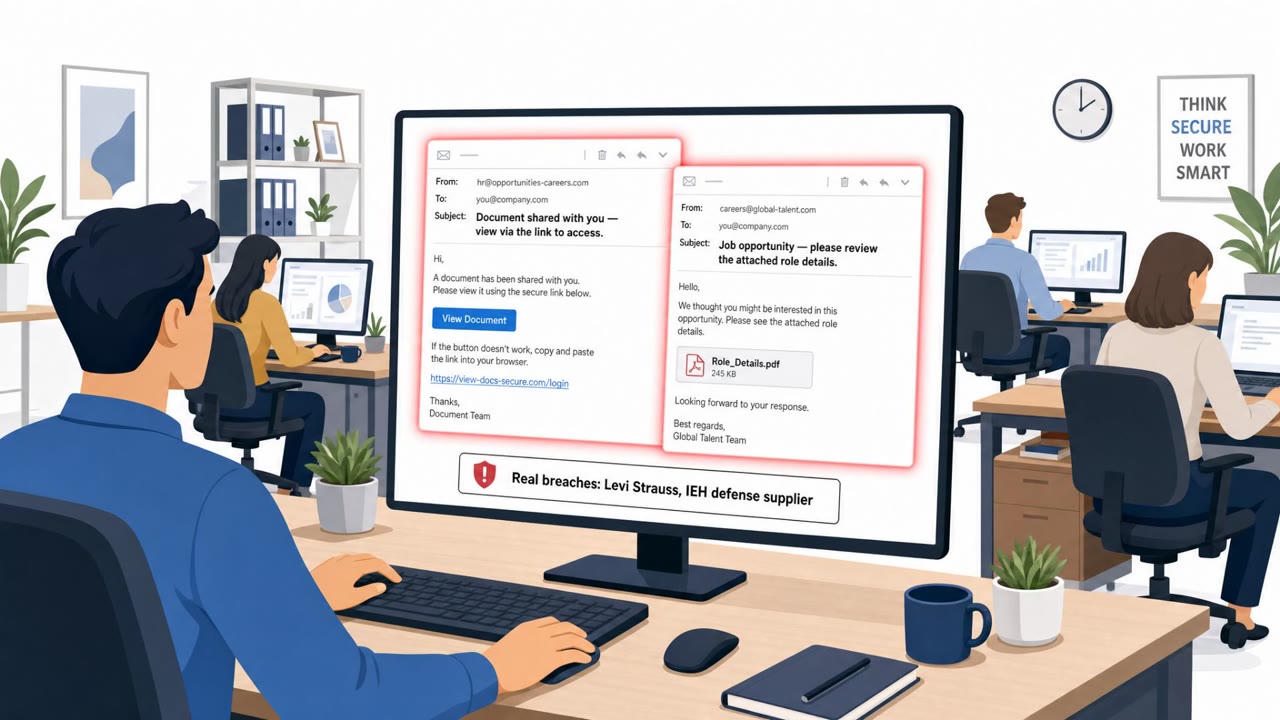
This weekly threat bulletin describes real incidents where attackers used human manipulation to break in, including social engineering at Levi Strauss and a Microsoft 365 credential-theft phish at defense supplier IEH. It also highlights a Lazarus-linked campaign using fake job offers and…

August 17, 2026
DPRK “Remote Worker” Scam Slips Into Real Jobs

DPRK “Remote Worker” Scam Slips Into Real Jobs

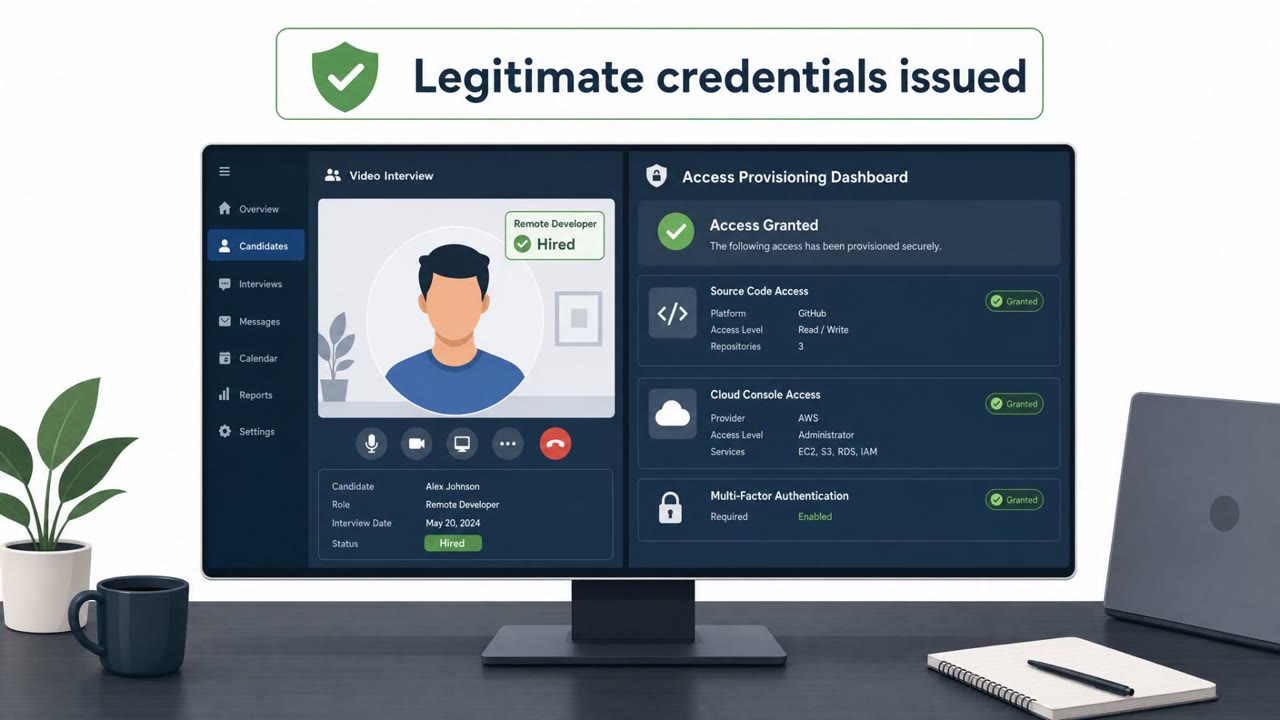
The article describes North Korean operatives posing as legitimate remote IT candidates to get hired, obtain real company credentials, and gain trusted internal access. It cites an FBI investigation into a DPRK remote IT worker at a U.S. federal agency and a research “hire-and-observe” operation…

August 17, 2026
Vishing Console + Fake CCleaner Trap Users

Vishing Console + Fake CCleaner Trap Users

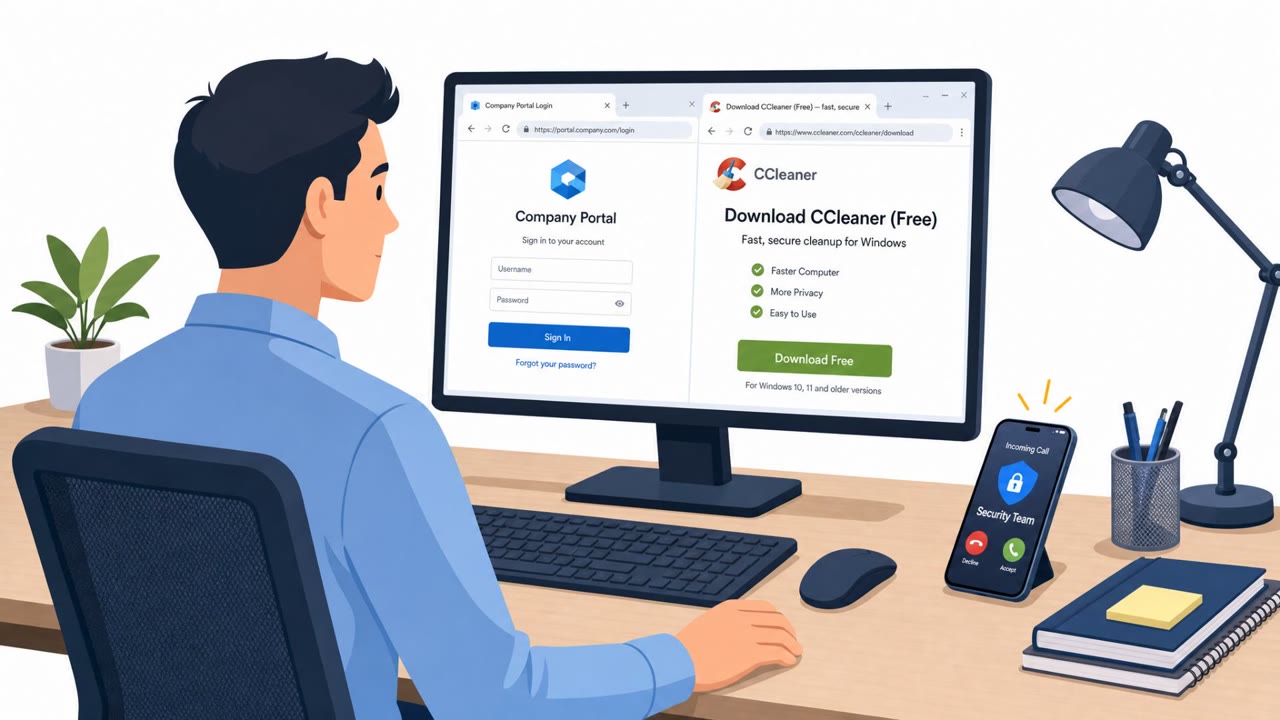
This bulletin highlights multiple real-world threats, including voice-phishing (vishing) operations that industrialize account takeovers and a fake CCleaner download site that installs spyware. The items provide concrete, repeatable lures (a vishing-driven takeover workflow and a lookalike software…

August 17, 2026
Hidden AI Prompts in Court Filing Trigger Sanctions

Hidden AI Prompts in Court Filing Trigger Sanctions

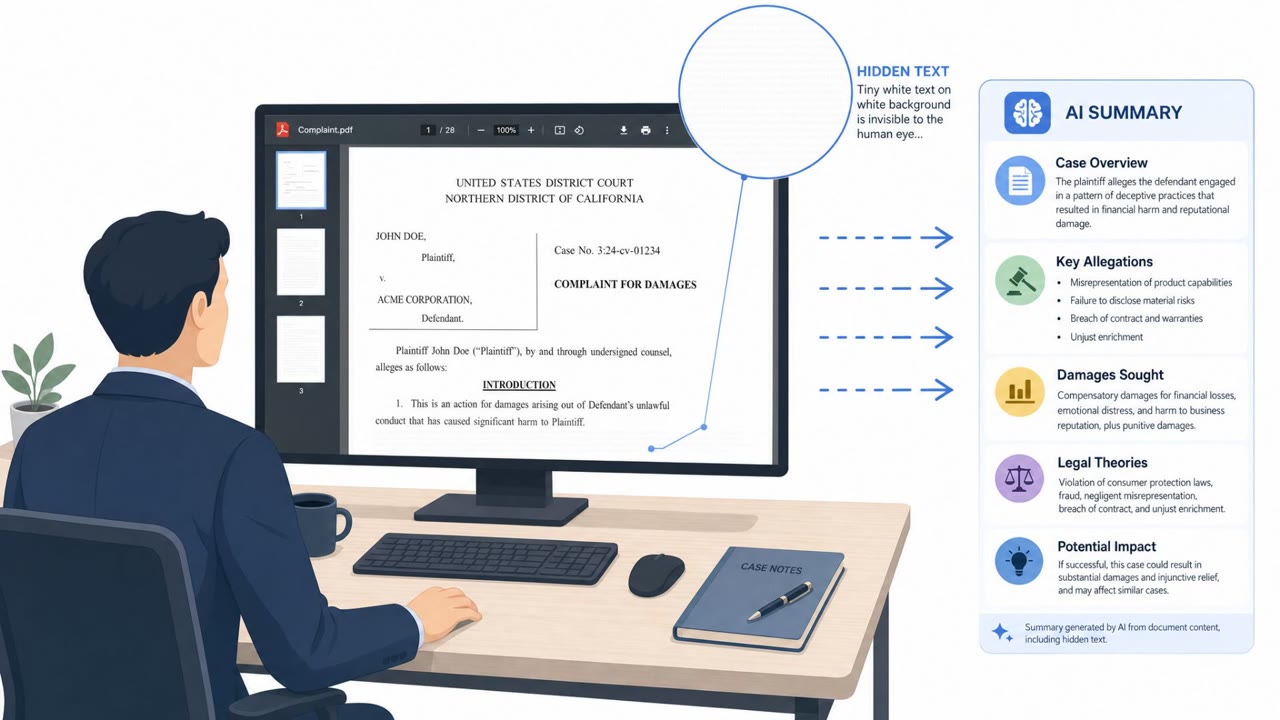
A self-represented litigant hid “prompt injection” instructions in a court filing using tiny white text, aiming to influence any AI system that might read the document into ruling in his favor. The judge identified the concealed instructions as abusive and revoked the litigant’s electronic filing…

August 17, 2026
Fake VPN Installers Hit Afghan Telecom Targets

Fake VPN Installers Hit Afghan Telecom Targets

Acronis reported a real espionage campaign delivering a backdoor (PATCHCORD) to Afghan telecom providers and South Asian critical infrastructure by tricking victims into installing look‑alike VPN and telecom tools. The operation also used cloud services like Google Sheets (and GitHub Gists) to…

August 16, 2026
Singapore Runs AI Scam Call “Fire Drills”

Singapore Runs AI Scam Call “Fire Drills”

Singapore’s Cyber Security Agency is running a national exercise where volunteers receive simulated robocalls that mimic government impersonation scams, including AI-enabled calls. The article also points to real-world cases where criminals impersonated company executives on WhatsApp and even used…

August 15, 2026
“Half-Click” Zimbra Email Attack Steals 90 Days

“Half-Click” Zimbra Email Attack Steals 90 Days

CISA warns a Russian state-sponsored group (“Laundry Bear,” tracked by Microsoft as “Void Blizzard”) is compromising some unpatched Zimbra email accounts when users merely open or preview a specially crafted email. The hidden code can steal passwords, MFA-related tokens, and up to 90 days of…

August 14, 2026
Phone Scammers Used Fear to Sell €4,000 of Fake Filters

Phone Scammers Used Fear to Sell €4,000 of Fake Filters

A real phone scam convinced an elderly woman that her drinking water was unsafe and pressured her into buying four overpriced “water filters,” costing about €4,000. The article also describes common Portugal-targeted scams, including “Hi Mum/Hi Dad, I lost my phone” money-transfer fraud and SMS…

August 14, 2026
China Tied to NZ Space Spy Bid and Fake Job Lures

China Tied to NZ Space Spy Bid and Fake Job Lures

New Zealand’s intelligence service says a China-linked organization tried to install space ground infrastructure in New Zealand that could collect militarily useful intelligence, using a local partner that likely didn’t understand the capability or who would receive the data. The same assessment…

August 14, 2026
Real-Time Smishing Tool Steals 2FA Codes Live

Real-Time Smishing Tool Steals 2FA Codes Live

Cisco Talos reported a real-time phishing framework called “JWR” that guides victims through fake checkout and login pages while attackers watch keystrokes live. It is being delivered through SMS messages that impersonate toll and postal authorities, and it can capture payment details, identity…

August 13, 2026
Deepfake Face-Swap Busted in Live Video ID Check

Deepfake Face-Swap Busted in Live Video ID Check

Spanish police arrested a suspect accused of using real-time face-swap deepfakes during live video identity checks to obtain fraudulent digital certificates for later misuse. The article describes how the attacker relied on lighting tricks and camera injection to spoof document and biometric…

August 13, 2026
Hidden AI Prompt Injection Found in Court Filing

Hidden AI Prompt Injection Found in Court Filing

A self-represented plaintiff in a Connecticut court case hid nearly invisible text in legal filings to try to influence how an AI system might summarize or evaluate the documents. The court found the concealed “prompt injection” instructions (tiny white font) and sanctioned the filer, warning that…

August 13, 2026
Fake Lockheed Jobs Used to Deliver Lazarus Zero-Day

Fake Lockheed Jobs Used to Deliver Lazarus Zero-Day

Check Point says North Korea’s Lazarus Group targeted defense and aerospace professionals using convincing fake job offers that led victims to download trojanized PDF software. The campaign used a Windows zero-day (now patched as CVE-2026-68820) to gain full control and hide from security tools,…

August 13, 2026
Lazarus Lures Staff With Fake Jobs to Drop Malware

Lazarus Lures Staff With Fake Jobs to Drop Malware

Researchers tied North Korea’s Lazarus Group to a real-world campaign that approaches professionals with convincing fake recruiter outreach and job offers. Victims are tricked into opening a malicious PDF or installing a fake PDF viewer from lookalike websites, which then installs backdoors and can…

August 12, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo