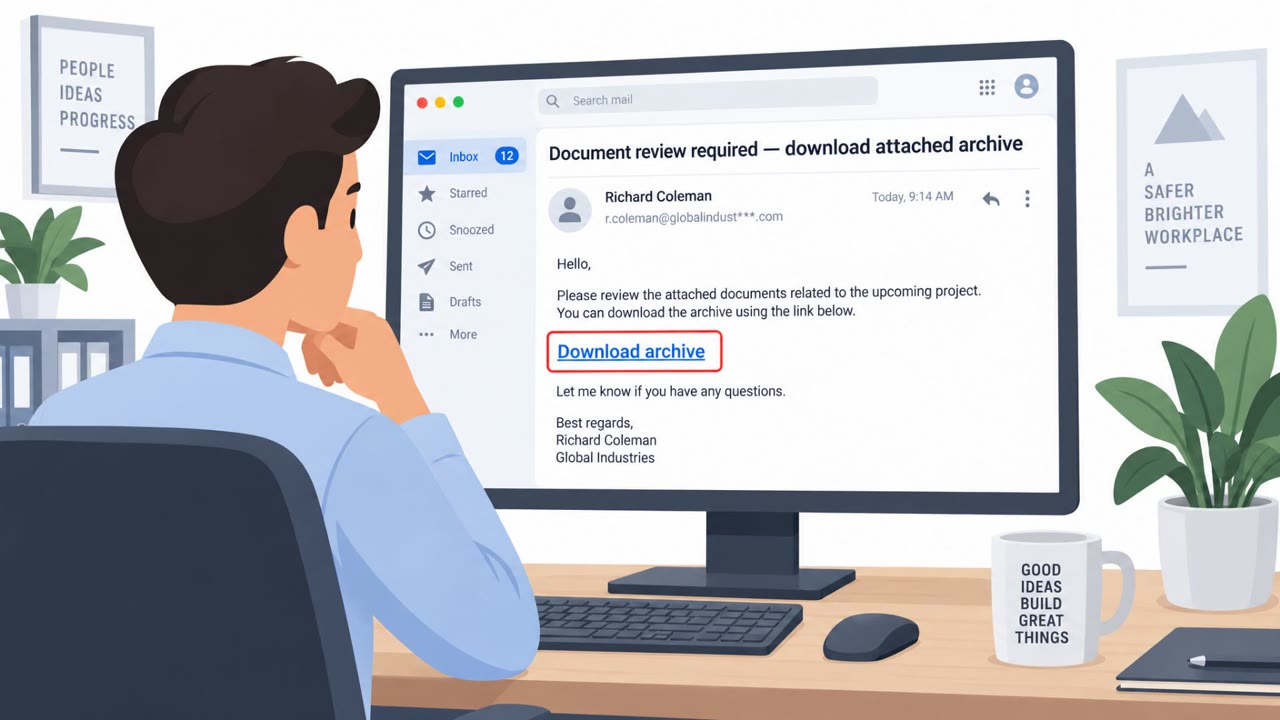
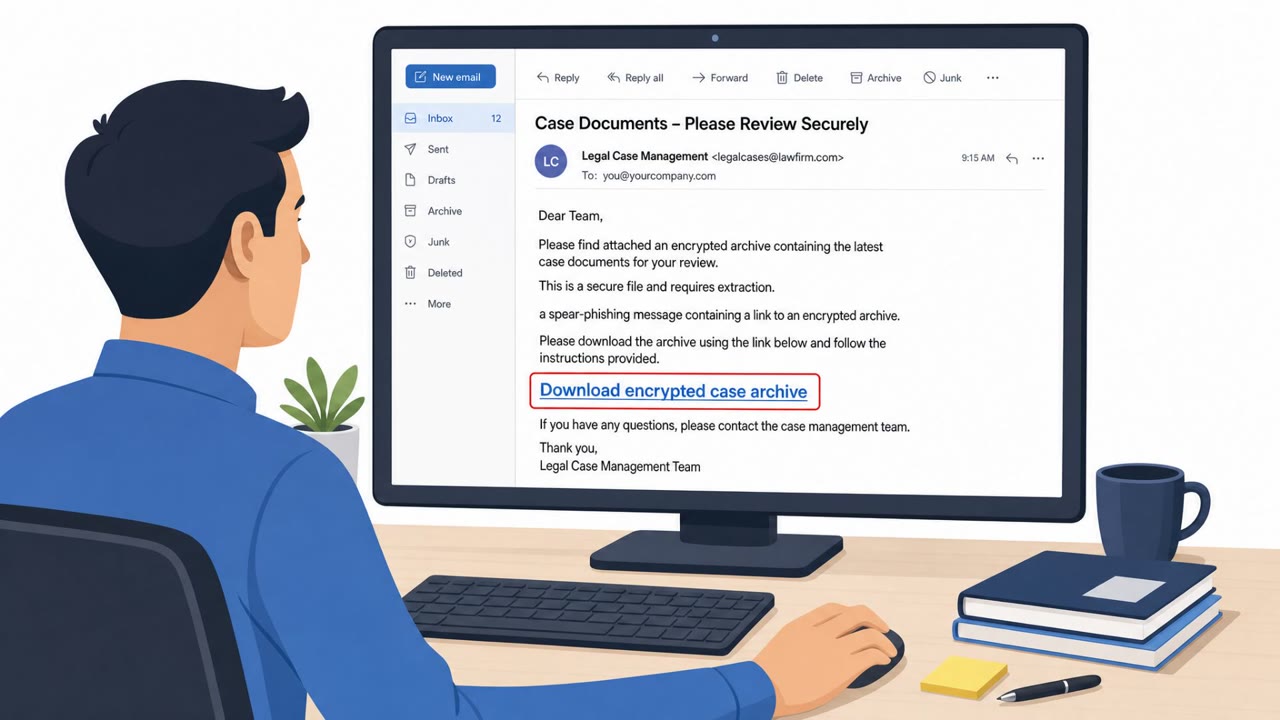
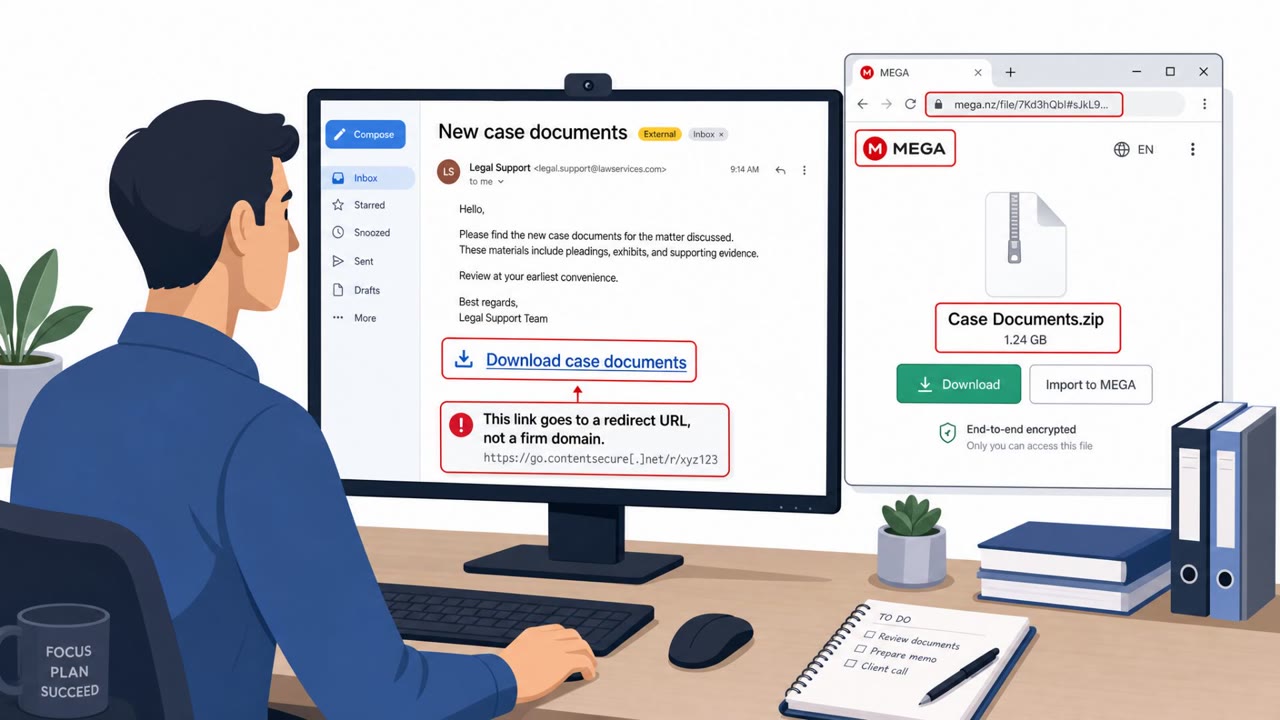
ESET reports that the Russia-aligned group UAC-0099 used spear‑phishing emails to trick victims in Ukraine into clicking a link that downloads a malicious archive. The infection chain runs a script that installs MATCHBOIL, which then downloads a spying backdoor (MATCHWOK) and sets persistence so it keeps coming back.
Key findings
- Victims observed by ESET were in Ukraine, including transportation (Jul–Aug 2025), manufacturing (Dec 2025), and energy (Jun 2026).
- Initial access starts with a spear‑phishing email containing a link that downloads an archive with a VBScript, which then installs MATCHBOIL.
- MATCHBOIL downloads and installs MATCHWOK, a C# backdoor capable of screenshots and executing PowerShell commands.
- Persistence is achieved via a scheduled task or a Windows registry run key, writing files under %LOCALAPPDATA%.
- The malware evolved its payload locations and filenames over time (e.g., DeviceMonitor; MeowCheck/MeowMeowProgramm.exe; SMTPClient/SMTPClientApplication.exe) and added sandbox checks.
Who’s being targeted
- Commonly targeted roles: All employees, Operations, Administrative staff, Transportation staff, Manufacturing staff, Energy/OT-facing corporate teams.
- Affected industries: Transportation, Manufacturing, Energy.
- Attack channels: email, website.
- Impersonated: Unknown external sender (not specified).
Awareness takeaways
- Treat unexpected email links to downloadable archives as high risk, especially when they lead to scripts or installers.
- Be suspicious when a file you open shows an unrelated ‘decoy’ screen; stop and report it rather than trying again.
- Emphasize that phishing can be used to install long-term spying tools, not just steal passwords.
Red flags to watch for
- Unexpected email asking you to download an archive via a link
- Archive contains a script file (e.g., VBScript) rather than a normal document
- Opening the file triggers unexpected behavior (e.g., decoy app window) instead of the expected content
Read the video transcript
Imagine opening an email that says, “Please use the link below to download the attached archive.” Looks boring, right? That one click can pull down an archive with a VBScript that secretly installs MATCHBOIL, which then drops a spying backdoor called MATCHWOK, taking screenshots and running PowerShell in the background. Here’s the creepy part: if you double‑click it, some versions just pop up a fake daily planner with a cat photo, window titled “Dairy,” both text boxes labeled “Today,” while MATCHWOK quietly sticks around using scheduled tasks or registry run keys. If you ever get an unexpected email link to download an archive, or a file opens a weird decoy app like that cat planner, stop right there and report it to Security, don’t click again, don’t keep testing it.