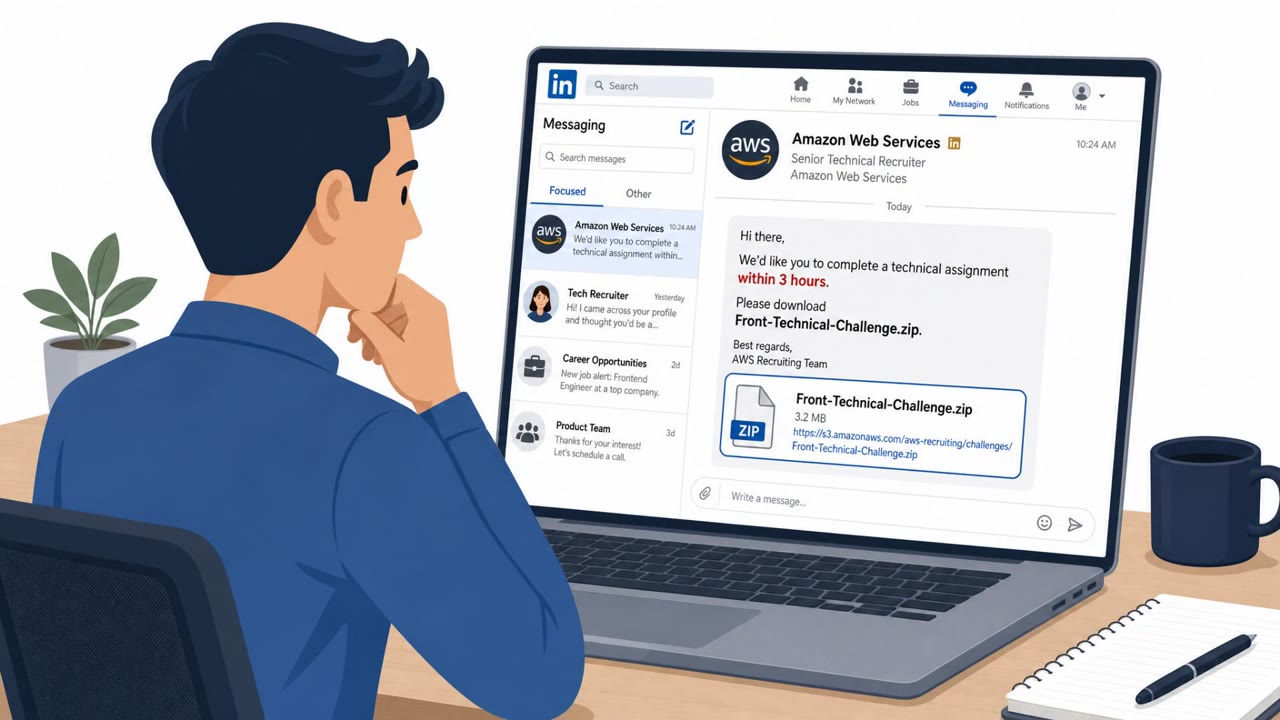
ESET reports that Russia-aligned group UAC-0099 is using spearphishing emails with malicious links to deliver a downloader called MATCHBOIL. The attack relies on tricking a person into manually running a downloaded VBScript, which then fetches and installs further malware and sets up persistence for repeat access.
Key findings
- MATCHBOIL is delivered via spearphishing emails containing malicious links.
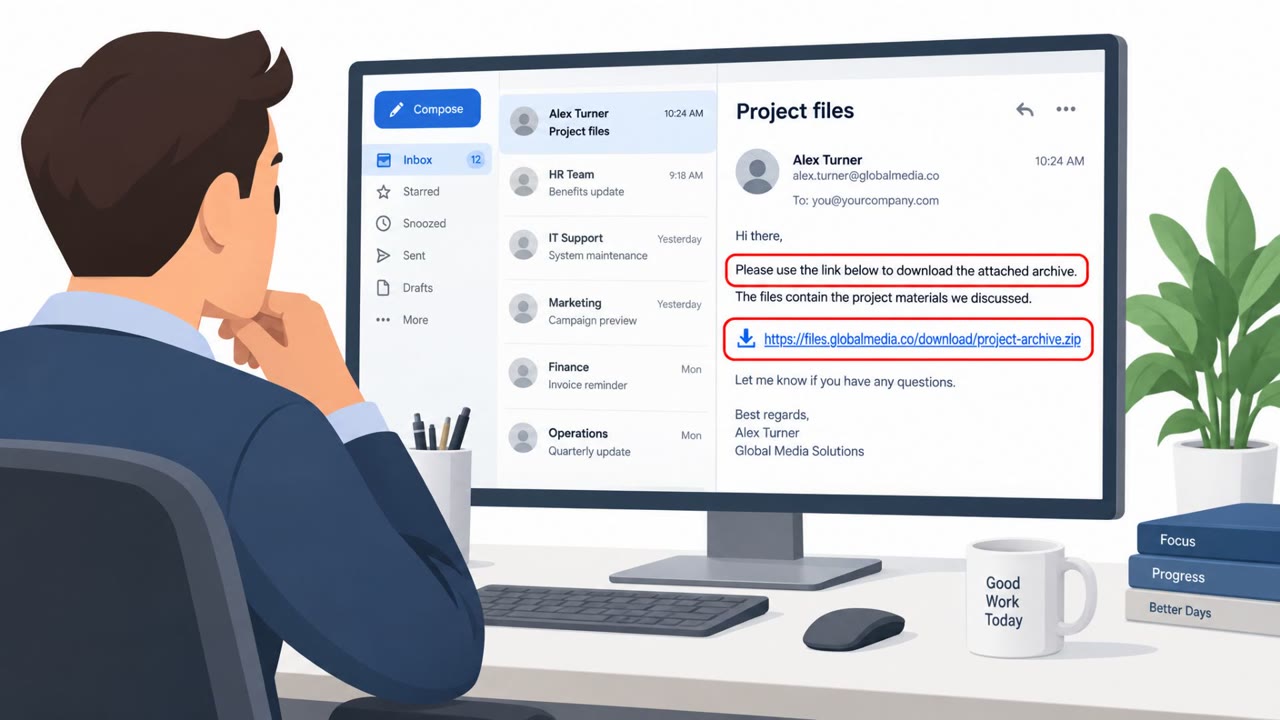
- Clicking the link downloads an archive that contains a VBScript; the user is misled into running the script manually.
- MATCHBOIL contacts a command-and-control (C&C) server over HTTPS to download and install a payload (often the MATCHWOK backdoor).
- The malware establishes persistence via Windows Registry Run keys and/or Scheduled Tasks, enabling it to survive reboots.
- ESET observed victims in Ukraine across transportation, manufacturing, and energy sectors; UAC-0099 also targets government, financial institutions, and media in Ukraine.
Who’s being targeted
- Commonly targeted roles: All staff (phishing awareness), Operations teams in transportation/manufacturing/energy, Executive assistants/administrative staff, IT helpdesk and endpoint/security teams (for recognition and response).
- Affected industries: Transportation, Manufacturing, Energy, Government, Finance/Insurance, Media.
- Attack channels: email, website.
- Impersonated: Unknown/unspecified (not stated in article).
Awareness takeaways
- Treat unexpected download links (especially to ZIP/archives) as suspicious, even if the email looks targeted.
- Never run scripts you downloaded from an email link (e.g., .vbs files). If a message asks you to run a script manually, stop and verify through official channels.
- Reinforce reporting: if someone clicked a suspicious link or ran a script, report immediately because these attacks quickly pull down additional payloads.
Red flags to watch for
- Unexpected link to download an archive file
- Instructions require manually running a script (VBScript)
- File type is a script rather than a normal document
- A download that triggers an 'installer' script rather than a trusted installer
- Untrusted archive/script obtained via link
- Behavior consistent with staged payload delivery (downloader installs another payload)
Read the video transcript
You get an email: “Document review required, download attached archive.” Looks legit, targeted, even urgent. You click. A ZIP downloads. Inside is not a document, but a .vbs script. The email tells you: “Run this script to view the files.” That’s the MATCHBOIL trap. Run it, and MATCHBOIL quietly talks over HTTPS to a remote server, pulls down the MATCHWOK backdoor, and adds itself to your Windows startup so it survives every reboot. Here’s the move: if a download from email ever wants you to run a script file like .vbs, stop and report it to security immediately, don’t run it, even once.