Recent Financial Services Cyber Attacks

Page 4 of 13
Trezor Users Targeted by Phishing Calls & QR Letters

Trezor Users Targeted by Phishing Calls & QR Letters

After a breach at shipping partner ShipMonk, attackers obtained Trezor customers’ contact and shipping details, increasing the risk of scams. Reports on Reddit indicate customers have already received phishing phone calls and physical letters containing QR-code phishing lures. Trezor warned…

September 8, 2026
Fake “API Exploit” Lures Users Into Self-Hacking

Fake “API Exploit” Lures Users Into Self-Hacking

Cisco Talos reports a real cryptocurrency-theft campaign where criminals trick people into pasting JavaScript into their browser or installing it via the Tampermonkey extension. The lure pretends to be a leaked vulnerability report for crypto swap sites, but the “exploit” is fake and instead…

September 8, 2026
BengalSEO Tricks Bing Users Into Malware & Scam Calls

BengalSEO Tricks Bing Users Into Malware & Scam Calls

Researchers uncovered a long-running “SEO poisoning” operation that manipulates Bing search results to push people onto fake support and activation pages. Victims are steered through a chain of redirects to either download a malware-laced ZIP (MayaBot) or be pressured into calling a fake…

September 8, 2026
ClickFix Lures Users to Paste Code via Browser

ClickFix Lures Users to Paste Code via Browser

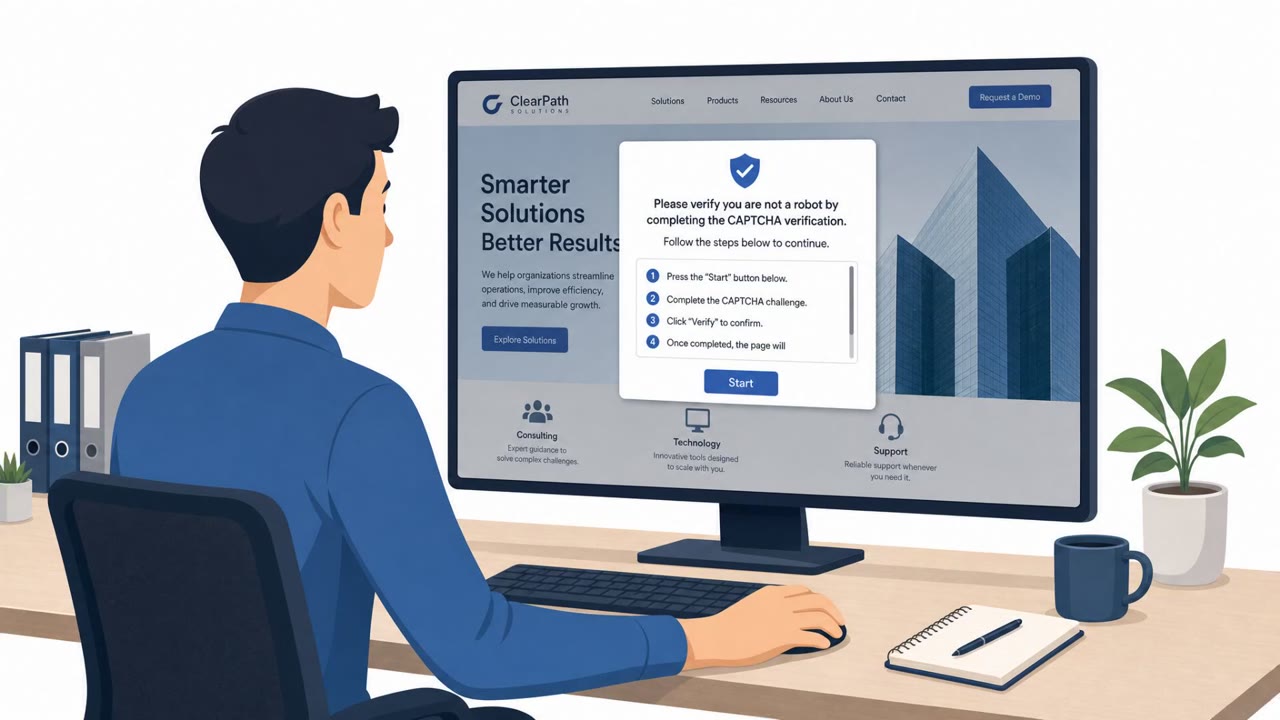
Cisco Talos described real ClickFix campaigns where attackers trick people into pasting code either into the Chrome address bar (or a browser extension) or into the Windows Run dialog. The first campaign targeted crypto swap sites and used a fake “leaked vulnerability report” to get victims to run…

September 8, 2026
Fake IT Help Desk Calls Steal M365 Data, Extort

Fake IT Help Desk Calls Steal M365 Data, Extort

Threat actors are calling employees while pretending to be internal IT/help desk staff and directing them to fake Microsoft 365 login pages. The goal is to capture credentials and MFA approvals, steal session tokens, then access and exfiltrate data from SaaS services like SharePoint, OneDrive, and…

September 7, 2026
Fake LinkedIn Tests and Job Interviews Push Malware

Fake LinkedIn Tests and Job Interviews Push Malware

This weekly threat bulletin includes real-world campaigns where attackers impersonate recruiters and use fake hiring steps to trick people into running malicious files. One campaign uses fake LinkedIn coding tests delivered via cloud links, and another uses fake job interviews with trojanized macOS…

September 7, 2026
Invisible Unicode Used to Evade Phishing Filters

Invisible Unicode Used to Evade Phishing Filters

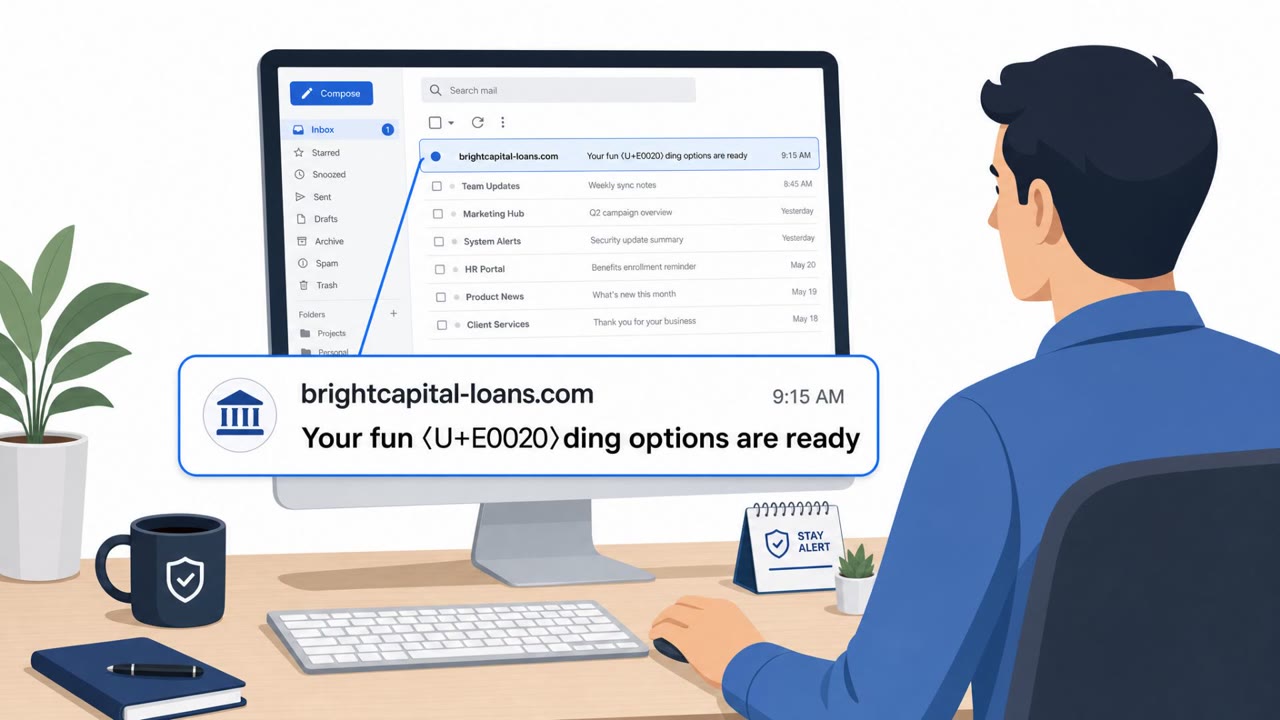
Microsoft reports criminals are using “ASCII smuggling” (invisible Unicode tag characters) to hide finance-related phishing keywords inside emails so detection rules miss them. The campaign used many disposable, finance-themed sender domains and was relayed through infrastructure tied to the…

September 7, 2026
Recruiter, RMM, and Vishing Scams Hit Hard

Recruiter, RMM, and Vishing Scams Hit Hard

This weekly roundup includes multiple real-world social-engineering and phishing-style operations, including fake recruiter outreach pushing malicious Android apps, phishing emails that trick users into installing remote management tools, and vishing that reportedly led to compromised Okta…

September 4, 2026
Phishers Hide “Funding” With Invisible Unicode

Phishers Hide “Funding” With Invisible Unicode

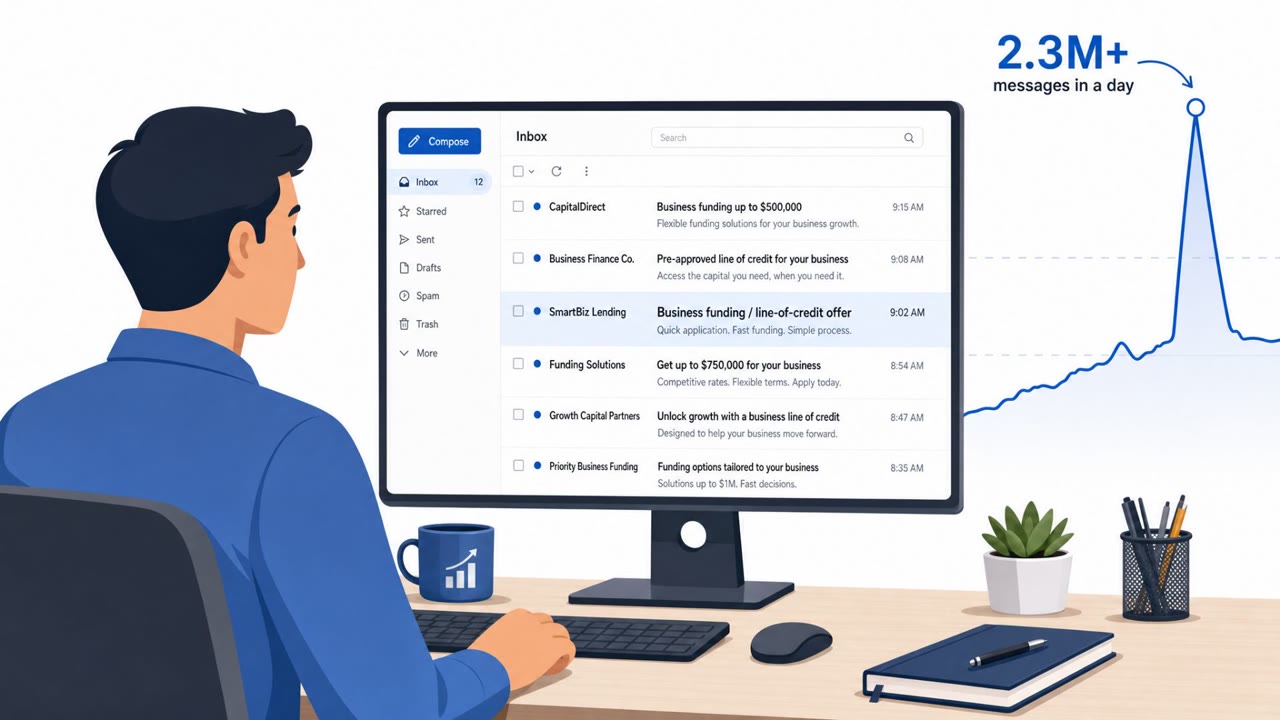
Microsoft reported a real, high-volume phishing campaign (up to millions of emails per day) that hid key “loan/funding” lure words using invisible Unicode characters to slip past email filters. The emails used disposable finance-themed domains and were often routed through ActiveCampaign…

September 4, 2026
X Users Hit by Password-Reset Email Flooding

X Users Hit by Password-Reset Email Flooding

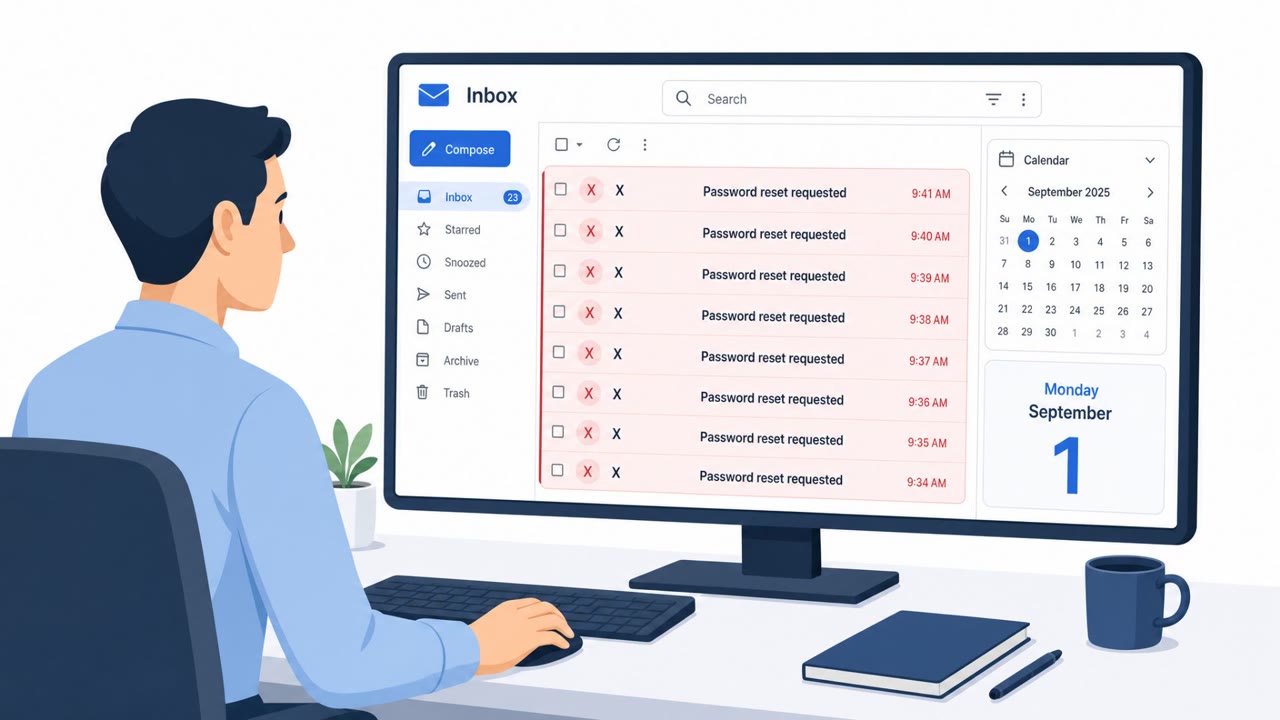
X is investigating a wave of unsolicited password-reset emails and codes being sent to users, which may be attackers trying to take over accounts as X Money becomes more available. X says it has found no evidence of a breach or successful account takeovers so far, but warns the reset-email “flood”…

September 4, 2026
X Users Hit by Password Reset Email Flood

X Users Hit by Password Reset Email Flood

Users reported getting repeated, unsolicited password-reset emails from X after the launch of X Money. The emails appear legitimate, but attackers may be using them to confuse users and then send follow-up phishing messages that lead to fake X login pages to steal credentials. There is no confirmed…

September 3, 2026
Fake IT Helpdesk Tricks Users Into Remote Access

Fake IT Helpdesk Tricks Users Into Remote Access

This bulletin describes multiple real-world social engineering campaigns where attackers impersonate IT support or use trusted-looking sharing and “Allow” prompts to gain access. Several campaigns abuse Microsoft Teams and document-sharing lures to trick employees into installing remote tools or…

September 3, 2026
Invisible Unicode Used to Evade Finance Phishing Filters

Invisible Unicode Used to Evade Finance Phishing Filters

Microsoft researchers reported a real, high-volume phishing campaign that used invisible Unicode “tag” characters to break up finance-related lure words (like “funding”) so email filters wouldn’t detect them. The emails looked normal to recipients but contained hidden characters in the underlying…

September 3, 2026
Fake Streaming Ads Push StreamRat Android Trojan

Fake Streaming Ads Push StreamRat Android Trojan

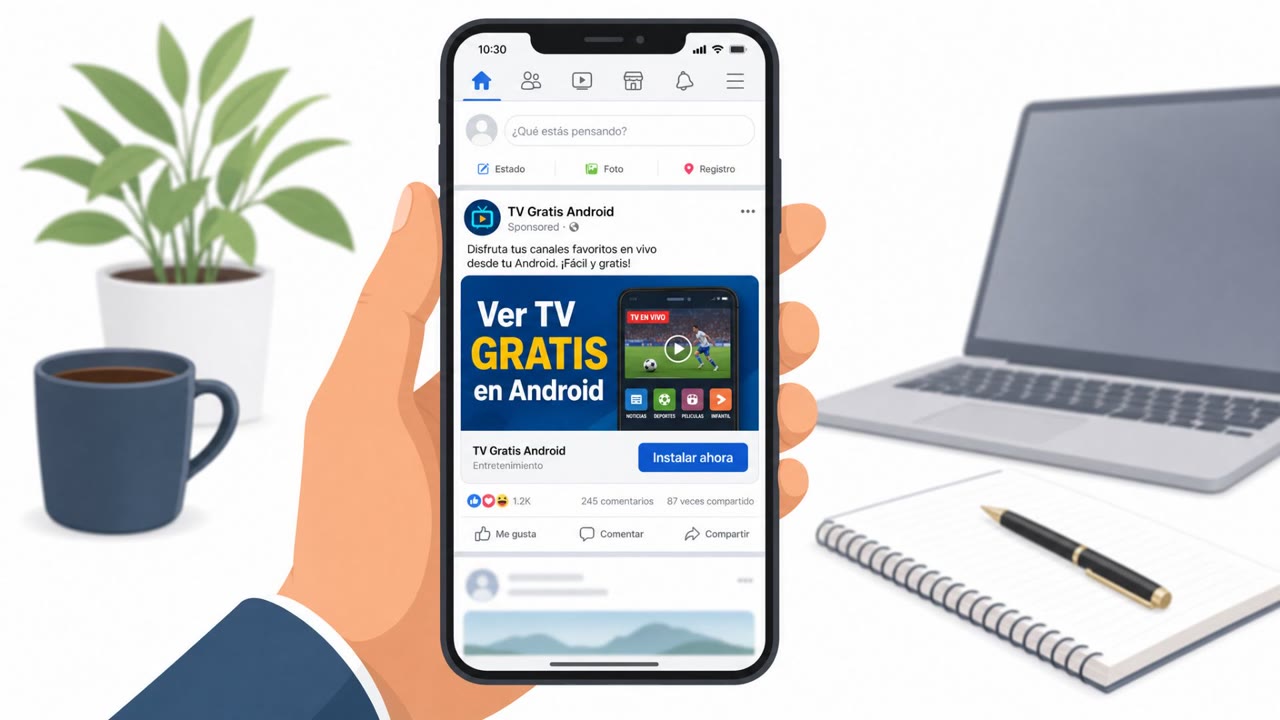
Researchers found a real malicious ad campaign on Meta platforms (and reused on TikTok) that pushed a fake “free TV streaming” service to Spanish-speaking users, mainly in Spain. Clicking the ad led to a tailored website that coached Android users through installing an app from outside Google Play,…

September 3, 2026
Phishing PDF Drops Malware Via Fake Edge Loader

Phishing PDF Drops Malware Via Fake Edge Loader

Researchers describe BraZetsu, a Windows malware framework used by an initial-access broker to turn infected PCs into "access for sale" on a criminal marketplace. While the malware itself is technical, the article includes real-world delivery details pointing to phishing: victims are tricked into…

September 3, 2026
Smishing Kit Rebounds After Major Takedown

Smishing Kit Rebounds After Major Takedown

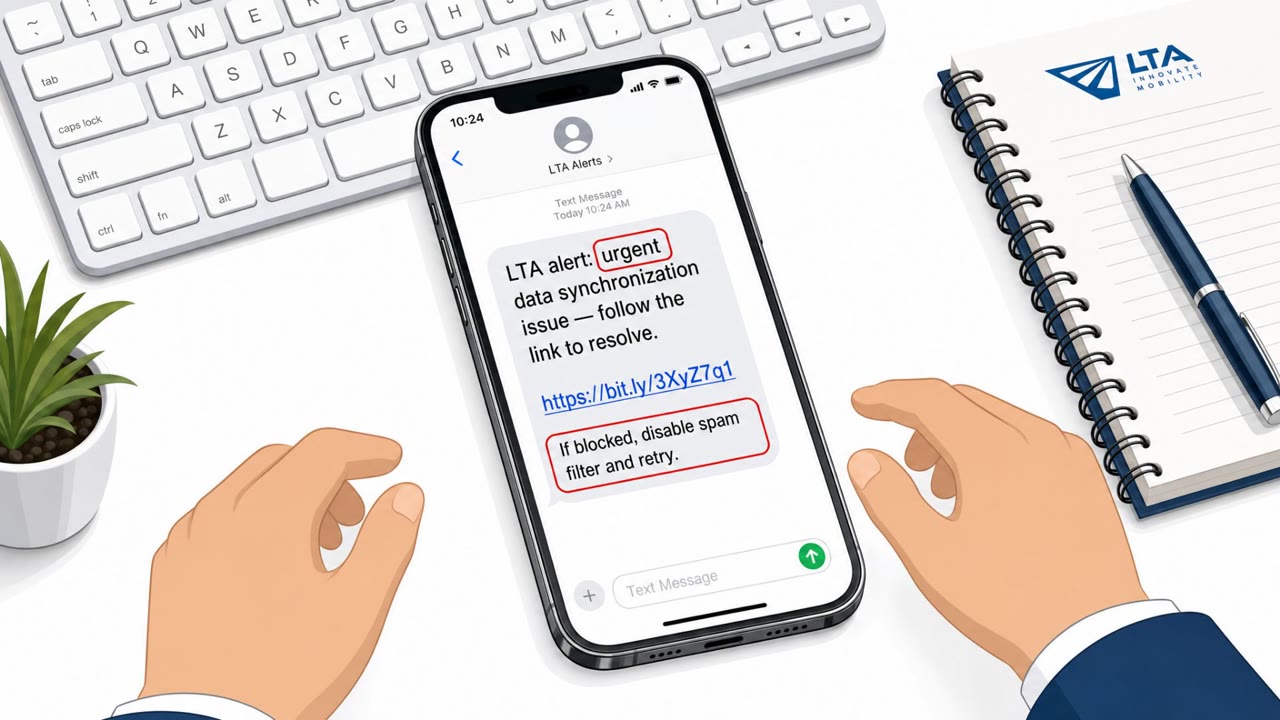
Researchers say a “phishing-as-a-service” kit called Outsider kept generating new scam pages even after a major law-enforcement and industry takedown. The kit supports SMS-based lures that impersonate trusted brands and can capture payment details and MFA codes in real time using…

September 3, 2026
RMM Phish Uses Tax & UPS Lures in 46 Countries

RMM Phish Uses Tax & UPS Lures in 46 Countries

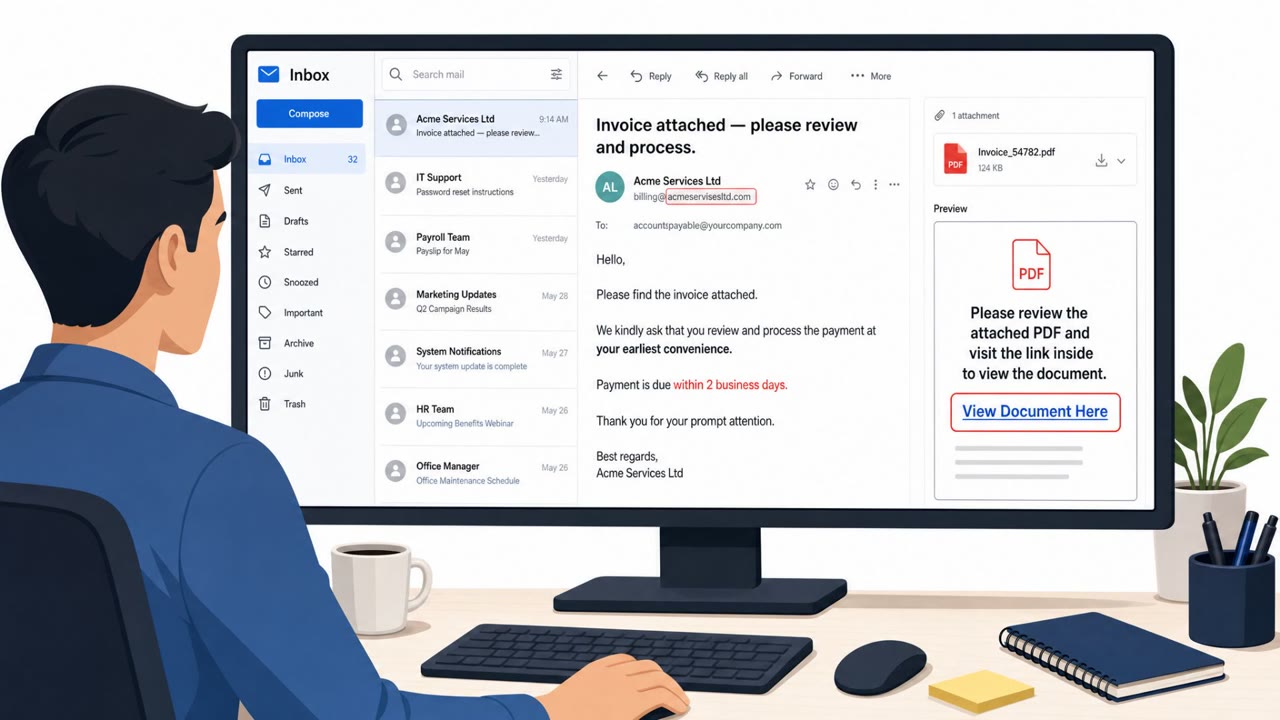
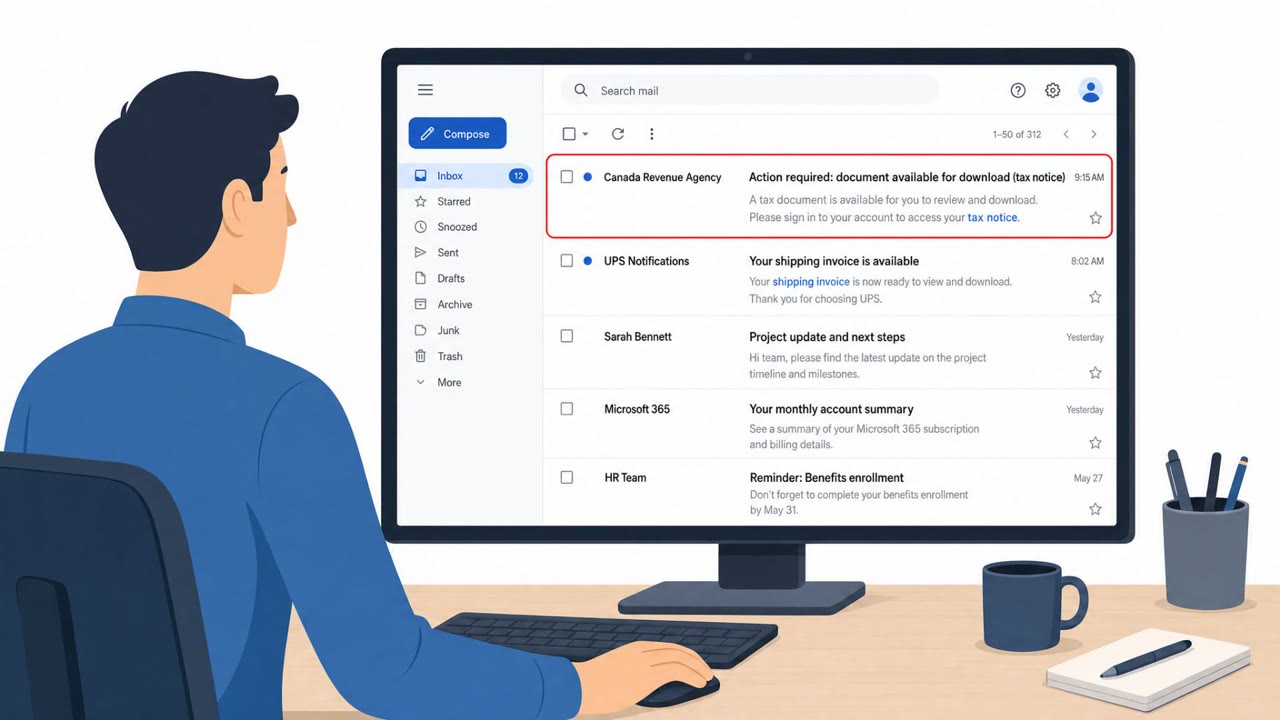
Researchers describe a real phishing operation that tricks people into installing legitimate remote monitoring and management (RMM) tools so attackers can remotely control devices. The campaign uses familiar-looking documents (tax forms, UPS/shipping notices, Adobe PDFs, invoices, and Social…

September 3, 2026
Fake CAPTCHA “Fix” Tricks Users Into Running Malware

Fake CAPTCHA “Fix” Tricks Users Into Running Malware

Multiple real-world intrusions used a ClickFix-style lure where victims visiting compromised websites saw fake CAPTCHA prompts and were tricked into running a command themselves. Separately, attackers also abused the legitimate, signed Node.js runtime (node.exe) to run malicious JavaScript while…

September 3, 2026
Resume Phish Hit Brazil Banks; AI Aided Ops

Resume Phish Hit Brazil Banks; AI Aided Ops

Two real, ongoing intrusion campaigns targeted organizations in Latin America, including a Mexican transportation organization and Brazil’s financial sector. In the Brazil campaign, attackers reportedly got in via a resume-themed phishing attachment, then attempted to download and run tunneling…

September 3, 2026
Fake Bank Calls Drain £180k From Revolut Users

Fake Bank Calls Drain £180k From Revolut Users

Jersey Police report a surge of scam phone calls where criminals impersonate bank fraud/security teams or Revolut support. Victims are pressured with warnings about “suspicious transactions” and then tricked into handing over security details or moving money, leading to about £180,000 in losses in…

September 2, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo