Recent Financial Services Cyber Attacks

Page 9 of 22
Device-Code Phishing Service Hit After 12K Breaches

Device-Code Phishing Service Hit After 12K Breaches

Microsoft and partners disrupted “EvilTokens,” a phishing-as-a-service platform Microsoft links to over 12,000 compromised inboxes across more than 10,000 organizations. The service used deceptive emails to trick people into pasting a “device code” into Microsoft’s real sign-in page…

September 22, 2026
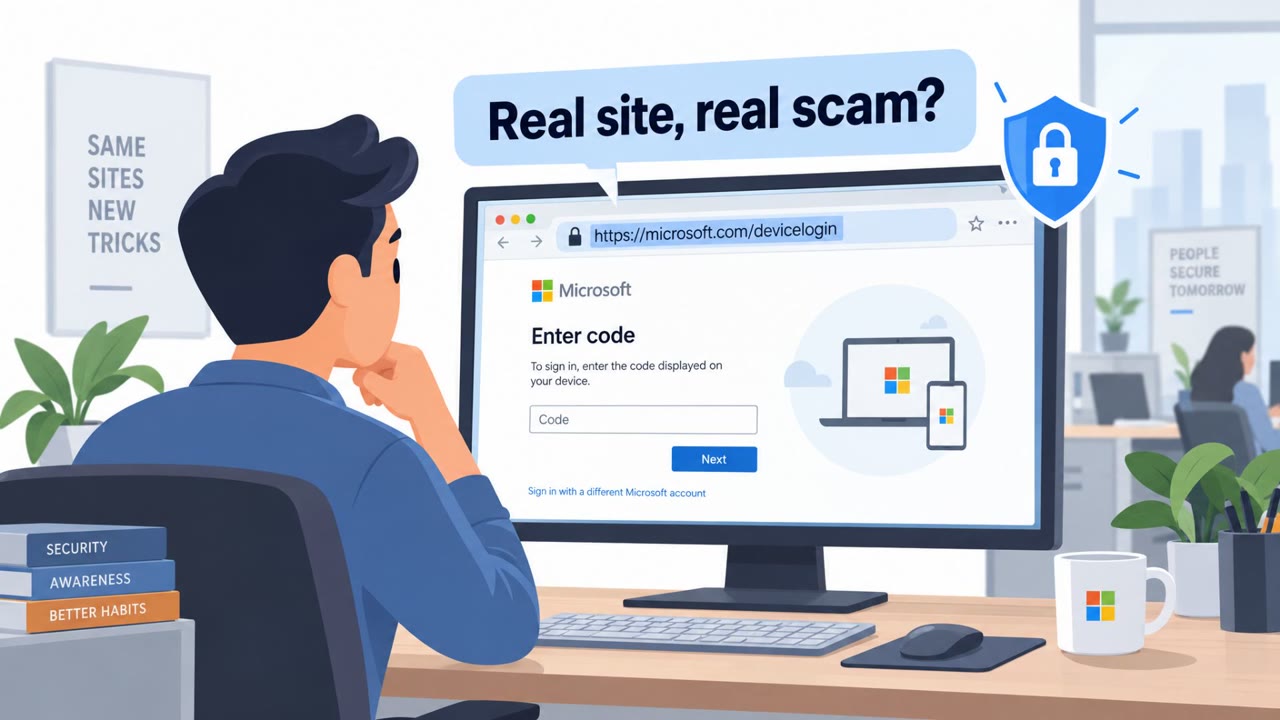
EvilTokens Uses Device Codes to Bypass MFA

EvilTokens Uses Device Codes to Bypass MFA

Microsoft reports that the EvilTokens phishing-as-a-service platform helped criminals compromise thousands of organizations by tricking users into completing a legitimate Microsoft “device code” login. The lure drives victims to enter a short code at microsoft.com/devicelogin, which unknowingly…

September 22, 2026
Deepfake CFO Video Call Triggers $25M Transfer

Deepfake CFO Video Call Triggers $25M Transfer

The article highlights that deepfakes are being used in real social-engineering incidents, including audio and video calls that impersonate trusted leaders. It cites a well-known 2024 Hong Kong case where scammers used a fake video meeting to pose as a company’s CFO and colleagues, leading an…

September 22, 2026
Deepfake Video Call Fooled Staff into $25M Transfers

Deepfake Video Call Fooled Staff into $25M Transfers

The article describes how criminals are using AI-generated video (“deepfakes”) to impersonate executives and trusted colleagues on live video calls. A real 2024 case at engineering firm Arup shows how a finance employee was convinced by a deepfake CFO and colleagues to send about $25 million across…

September 22, 2026
NK Fake Recruiters Trick Job Seekers Into Malware

NK Fake Recruiters Trick Job Seekers Into Malware

Authorities say a North Korean group posed as recruiters and ran fake technical interviews to convince job seekers to execute malicious code. The operation infected over 30,000 devices, led to thousands of compromised cryptocurrency wallets, and allegedly generated over $10 million for North Korea.

September 21, 2026
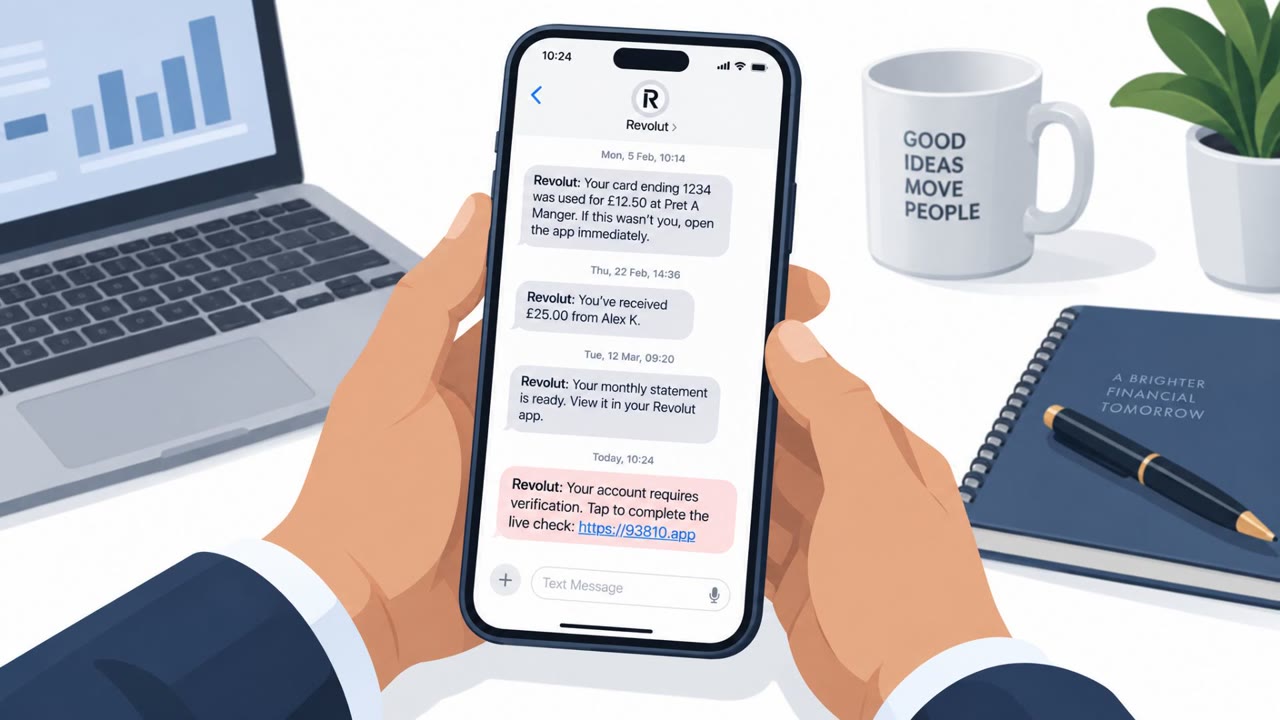
Revolut Smishing Uses Fake Identity Check

Revolut Smishing Uses Fake Identity Check

Following a Revolut data breach, scammers sent text messages that appeared to come from the same message thread as legitimate Revolut texts. The texts pushed victims to click a link for a fake identity “liveness check,” request camera access, and then capture passwords, information that could be…

September 21, 2026
Fake Job Interview Repo Tricks DevOps Into Malware

Fake Job Interview Repo Tricks DevOps Into Malware

North Korea–linked "Jade Sleet" used job interview-style coding projects to trick developers into running malicious infrastructure code. The lure involved GitHub repositories that contained a weaponized Terraform file, leading to downloads from attacker-controlled domains and installation of macOS…

September 21, 2026
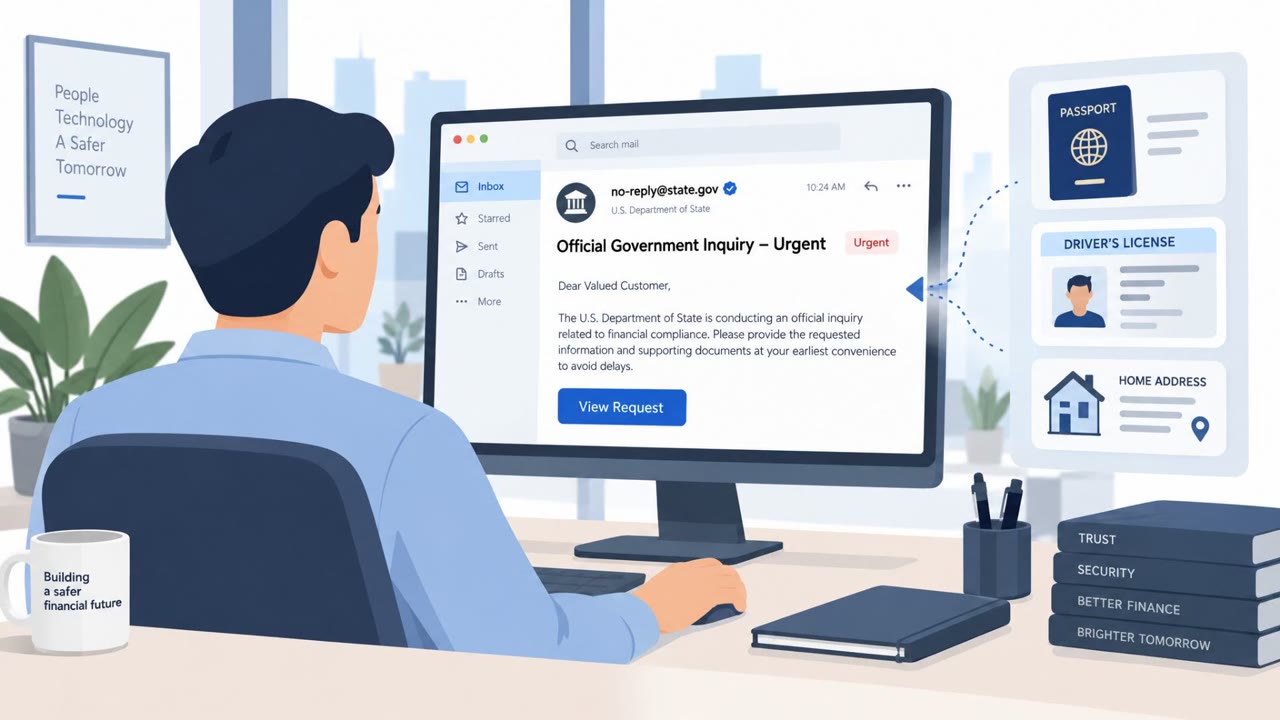
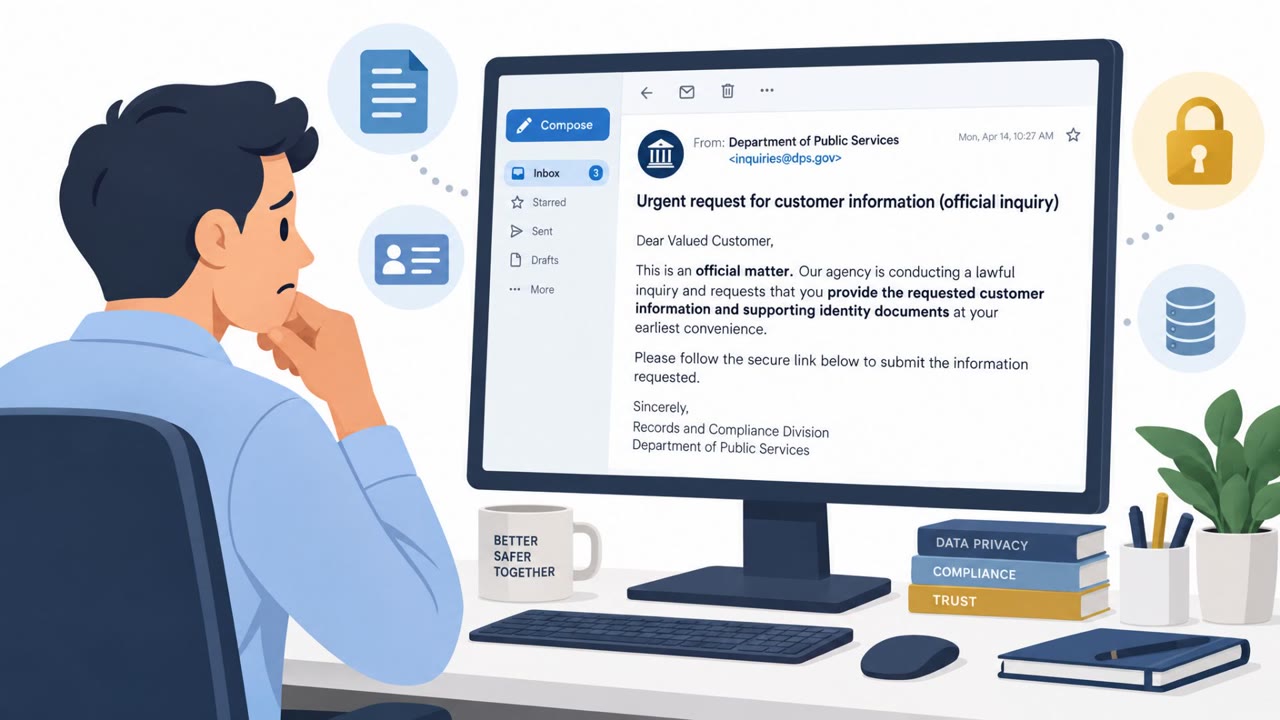
Revolut Fooled by Govt Impersonation Email

Revolut Fooled by Govt Impersonation Email

A person posing as a government agency used an email address on that agency’s real domain to obtain sensitive customer records from Revolut. The same weekly roundup also describes a fake antivirus renewal web page impersonating Avast, telling victims their subscription renewed for €129.99 and…

September 20, 2026
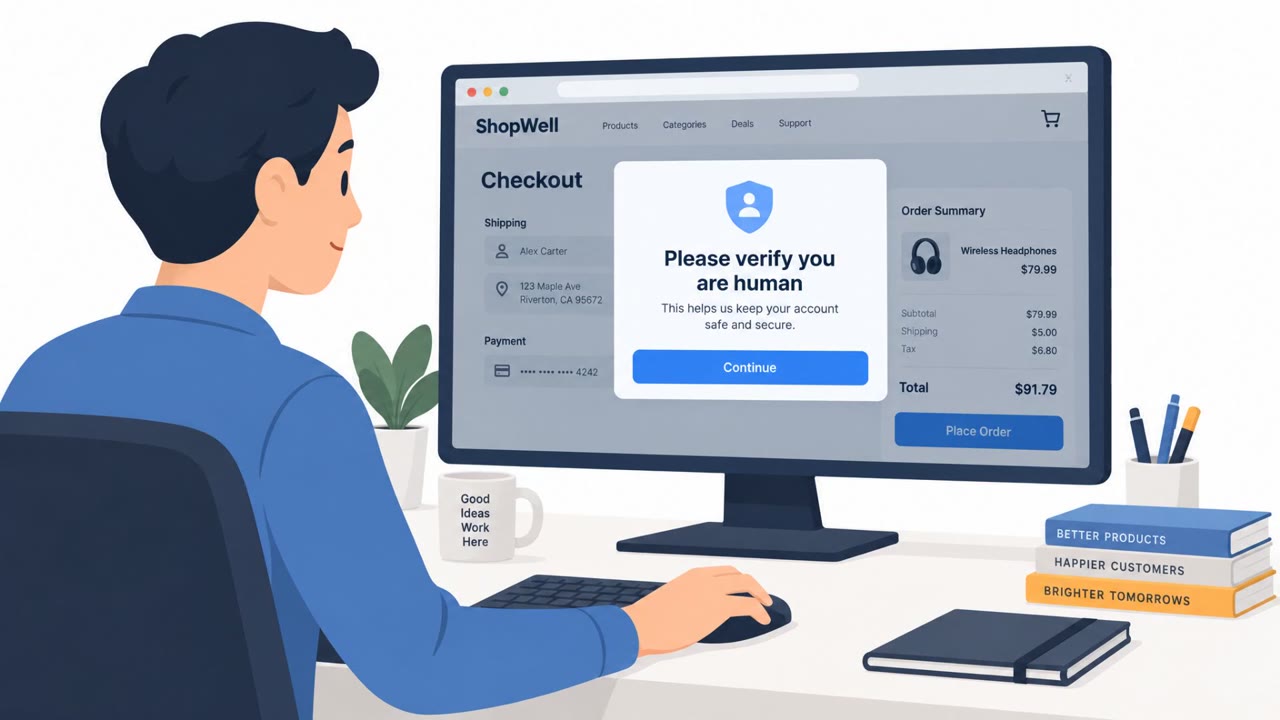
Brevo Breach Spread Malware via ‘Prove You’re Human’

Brevo Breach Spread Malware via ‘Prove You’re Human’

Attackers breached Brevo and used a stolen Cloudflare API key to inject malicious code into Brevo-hosted scripts that thousands of customer websites load. Visitors saw a fake “prove you’re human” prompt meant to trick them into running a command, and logged-in WordPress admins risked having a…

September 18, 2026
Trusted Channels Hijacked for Phishing and Malware

Trusted Channels Hijacked for Phishing and Malware

The article describes multiple real-world social engineering operations this week, including phishing sent from a legitimate Trezor newsletter channel and malware pushed through a verified HBO Max Reddit ad account. It also highlights a large-scale network of fake online stores impersonating real…

September 18, 2026
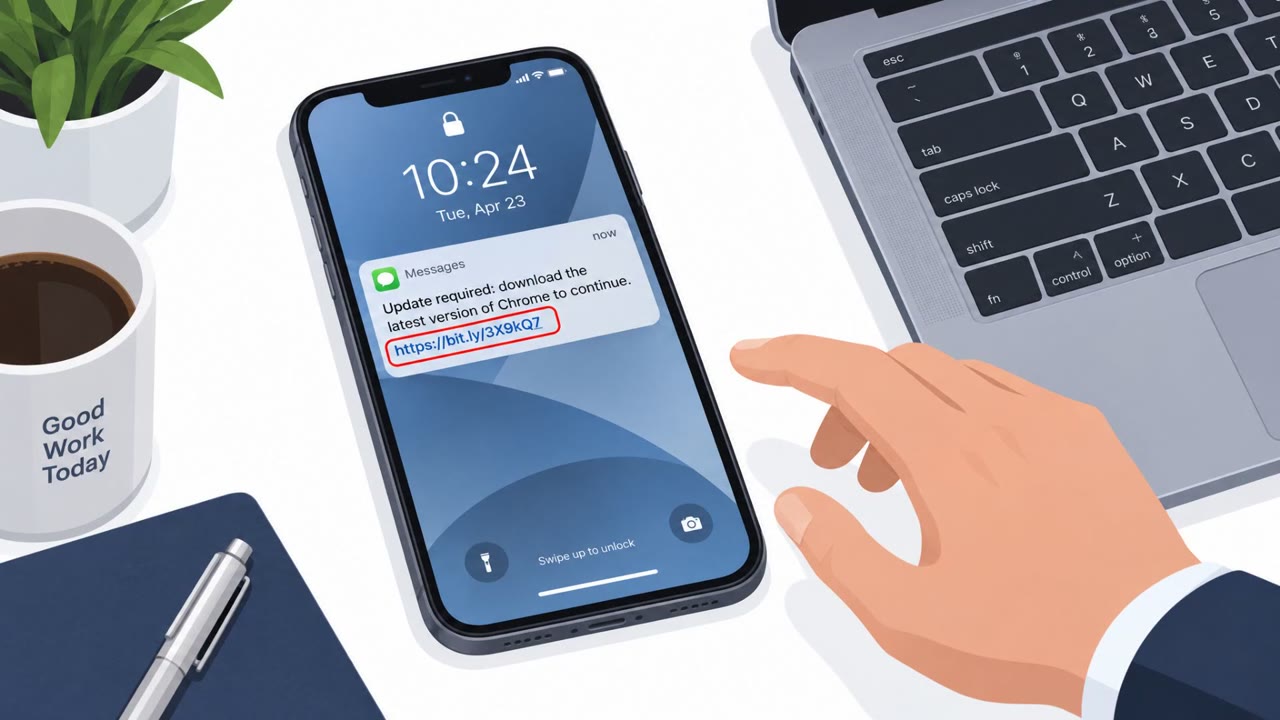
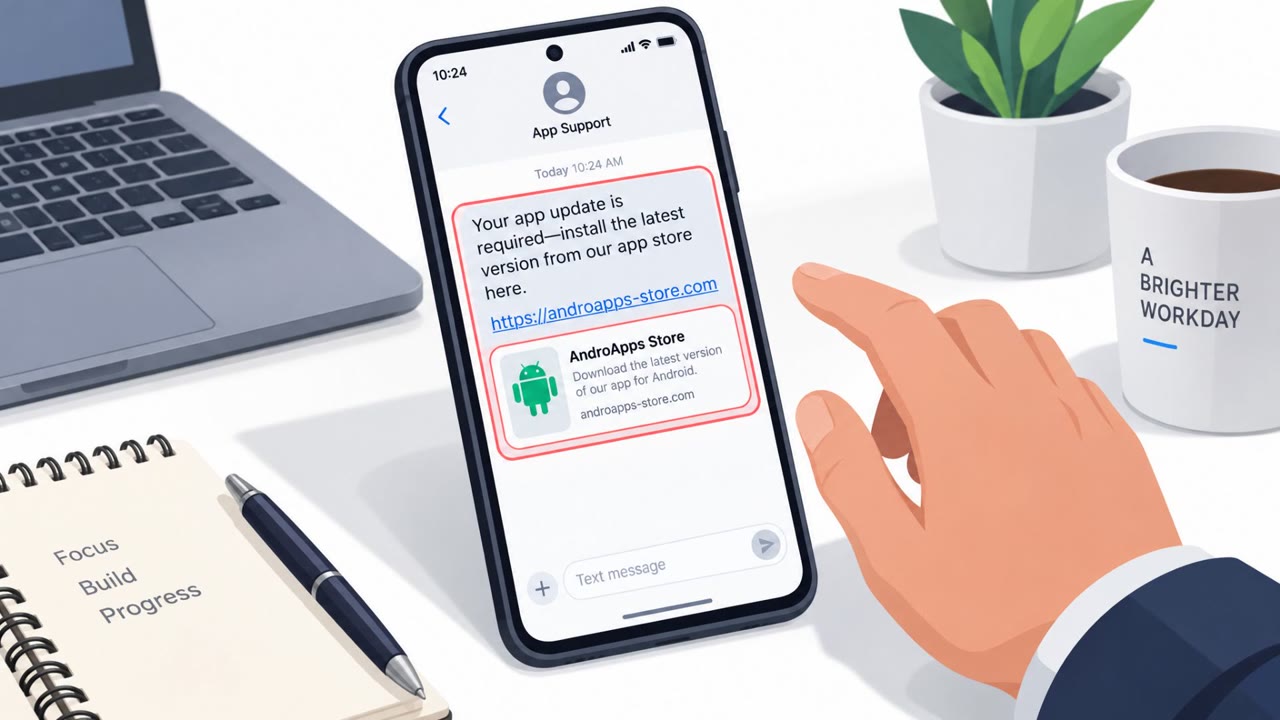
RatHat Smishing Lure Pushes Android Sideloading

RatHat Smishing Lure Pushes Android Sideloading

Researchers described an Android Trojan (“RatHat”) that starts with scam texts or malicious ads and tricks people into installing a fake app from a bogus download page. After installation, it pressures victims to grant Accessibility permissions using fake excuses or incentives, then uses those…

September 18, 2026
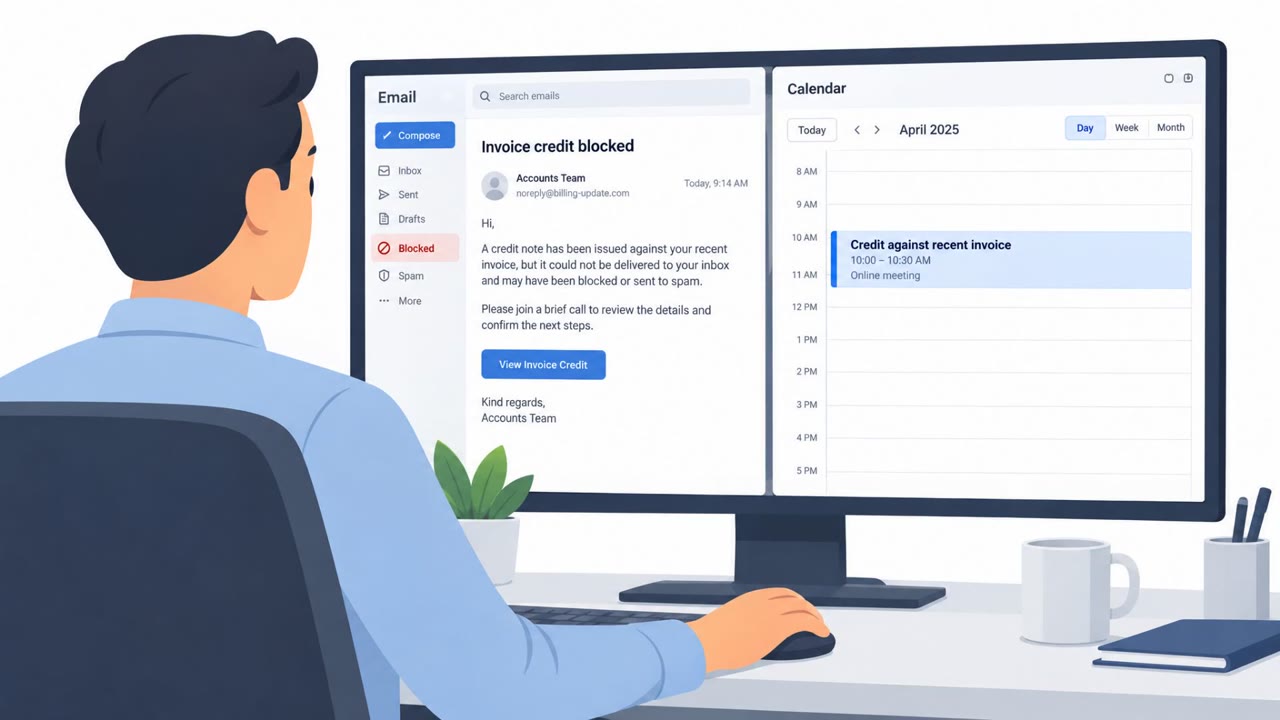
Malicious Calendar Invites Surge With Malware Links

Malicious Calendar Invites Surge With Malware Links

Attackers are sending fake calendar meeting invites that can be automatically added to a victim’s calendar, even if the email is blocked. A documented example used a Google Calendar invite with a financial “invoice credit” lure to drive victims to a hosted webpage and download a malicious…

September 18, 2026
Abandoned CDN Domain Hijack Risks Web Users

Abandoned CDN Domain Hijack Risks Web Users

A previously abandoned CDN domain was re-registered, and thousands of websites still reference hostnames under it, meaning a new, unknown owner can control what those sites load without any change on the sites themselves. The article also describes a real, recent “ClickFix” social-engineering…

September 18, 2026
Revolut Tricked by Spoofed Government Email

Revolut Tricked by Spoofed Government Email

Revolut confirmed a customer data breach after attackers used a compromised government agency domain to submit fake “official” requests for customer information. Revolut provided sensitive details (including IDs like passports and driver’s licenses) based on those email requests, raising questions…

September 18, 2026
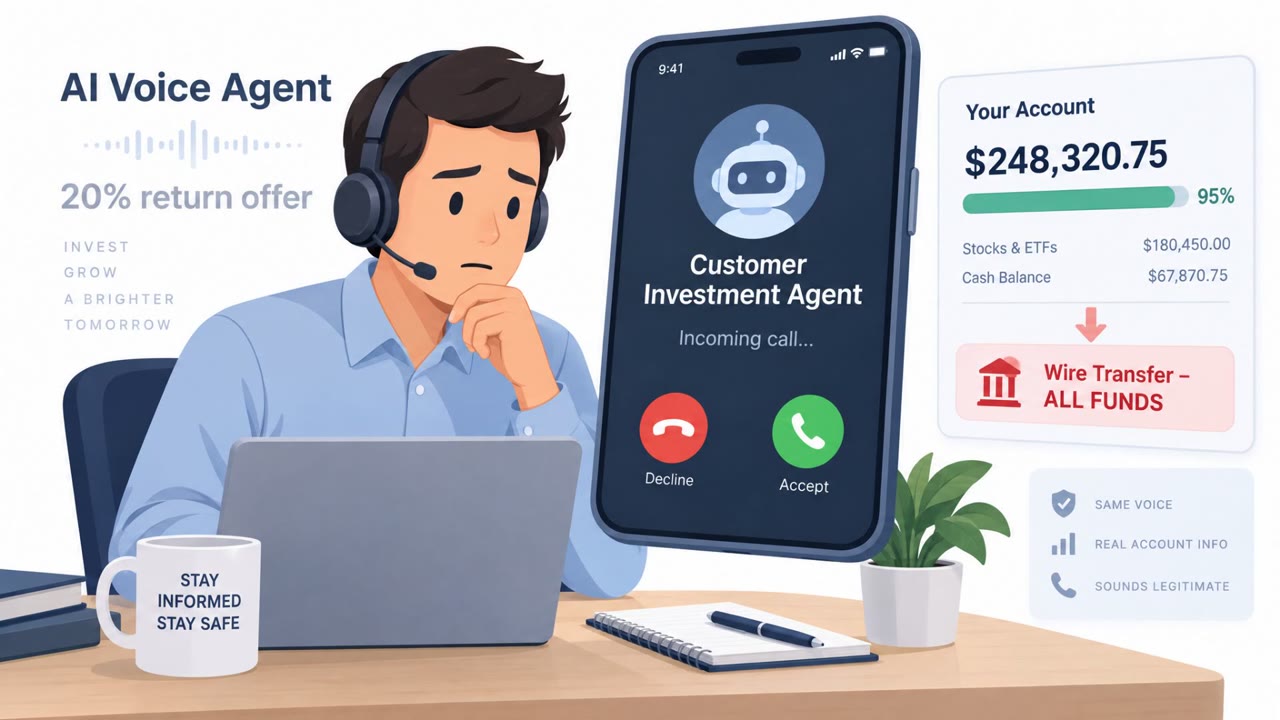
AI Voice Agents Fuel New Phone Fraud Wave

AI Voice Agents Fuel New Phone Fraud Wave

The article describes real-world cases where AI agents interacted with banks and contact centers, including an investment agent that nearly wired out a customer’s funds after encountering a scam offer. It also highlights AI voice agents calling enterprises at high volume, sometimes lying about…

September 18, 2026
RatHat Lures Users to Install Fake Android Apps

RatHat Lures Users to Install Fake Android Apps

Researchers describe RatHat, an Android trojan linked to China-based operators, that spreads via smishing, malvertising, and fake app stores to trick people into installing a malicious APK. Once installed, it pushes for Accessibility permissions and then uses that access to take deep control of the…

September 18, 2026
Revolut Tricked by Stolen Govt Email

Revolut Tricked by Stolen Govt Email

Attackers used a compromised government email account to pose as authorities and request customer records from Revolut. Employees believed the requests were legitimate and voluntarily sent sensitive customer information, exposing data for nearly 700 people. The incident highlights how “trusted”…

September 18, 2026
Revolut Users Hit With SMS Phish After Breach

Revolut Users Hit With SMS Phish After Breach

Days after Revolut disclosed that customer records were shared with an unauthorized party, some customers reported receiving phishing texts that appeared in the same SMS thread as real Revolut messages. The link led to a fake site that asked for camera access to mimic Revolut’s identity “liveness”…

September 17, 2026
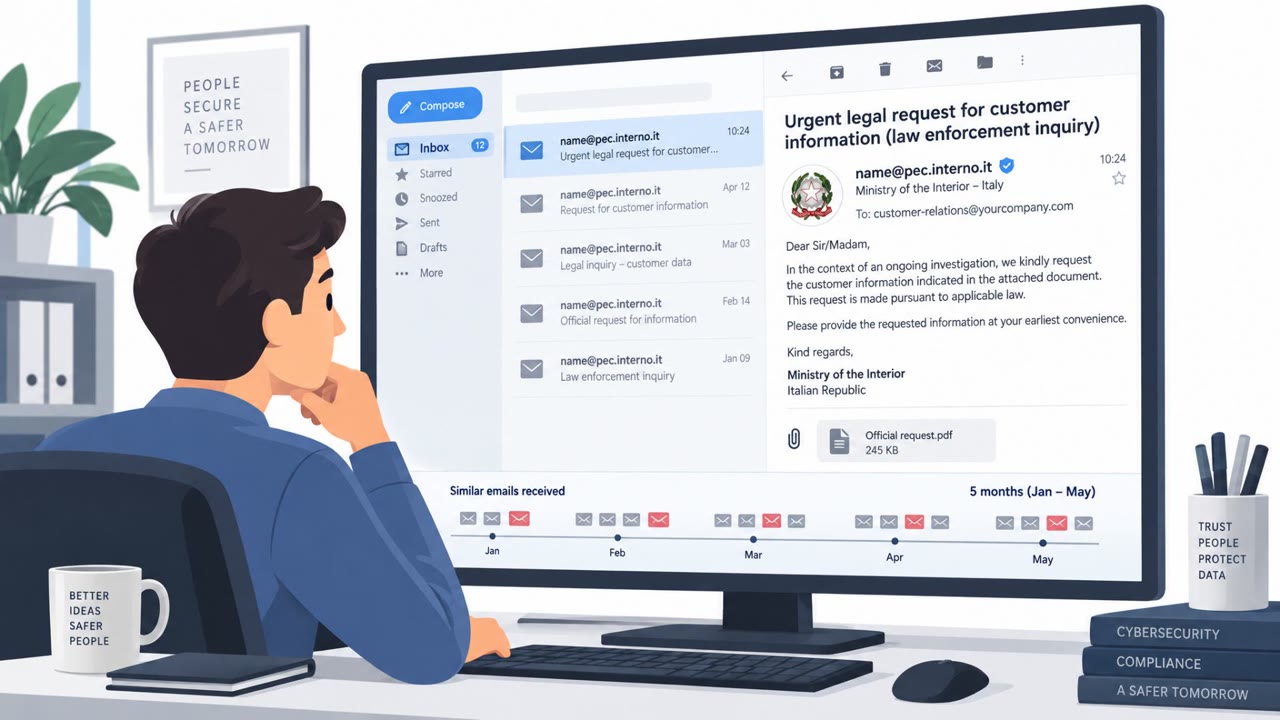
Revolut Tricked by Fake Govt Requests for Months

Revolut Tricked by Fake Govt Requests for Months

Attackers allegedly stole Revolut customer data by sending fraudulent “government” legal requests for roughly five months. The requests appeared legitimate because they came from a compromised government employee email account, leading Revolut to comply and disclose sensitive personal and financial…

September 17, 2026
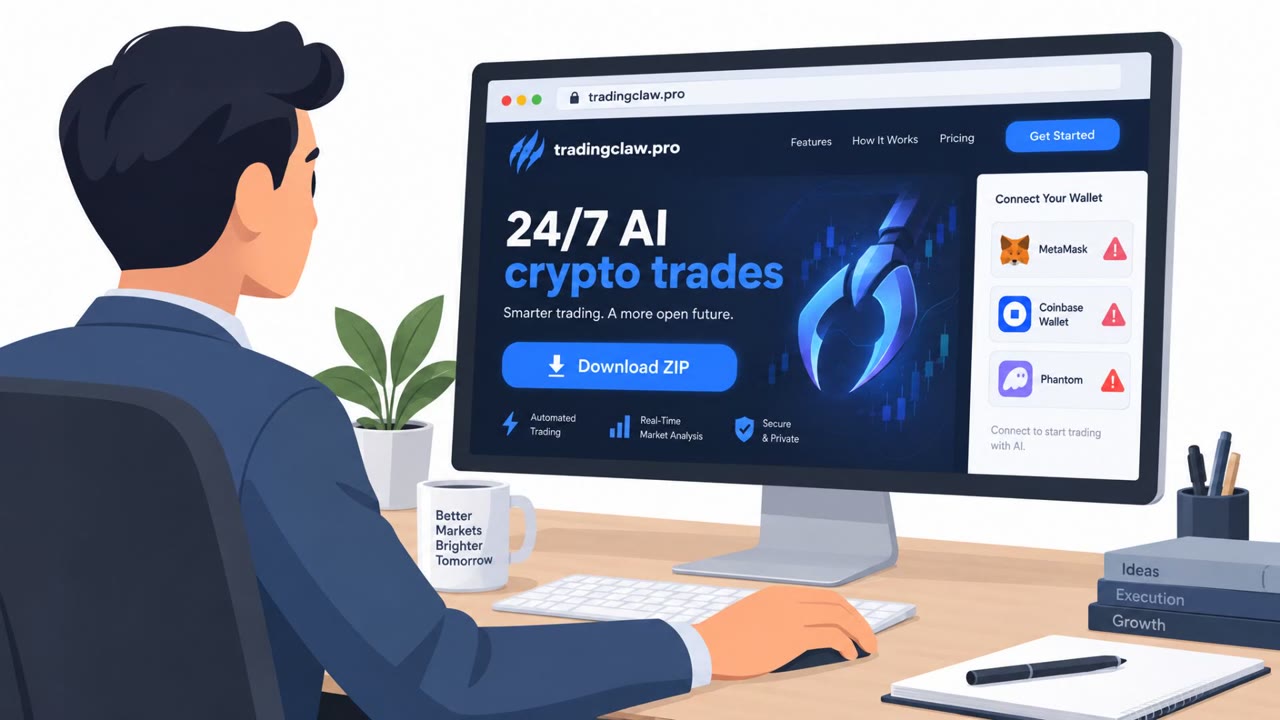
Fake AI Trading Bot Steals Crypto Wallet Passwords

Fake AI Trading Bot Steals Crypto Wallet Passwords

Researchers observed real campaigns where a fake “AI crypto trading agent” website tricked victims into downloading malware that silently replaces browser wallet extensions and steals the wallet password when it’s typed. The same reporting also describes invoice emails using QR codes to push…

September 17, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo