Threat Watcher

Page 28 of 32
AgentForger Turns AI Agents Into Insider Threats

AgentForger Turns AI Agents Into Insider Threats

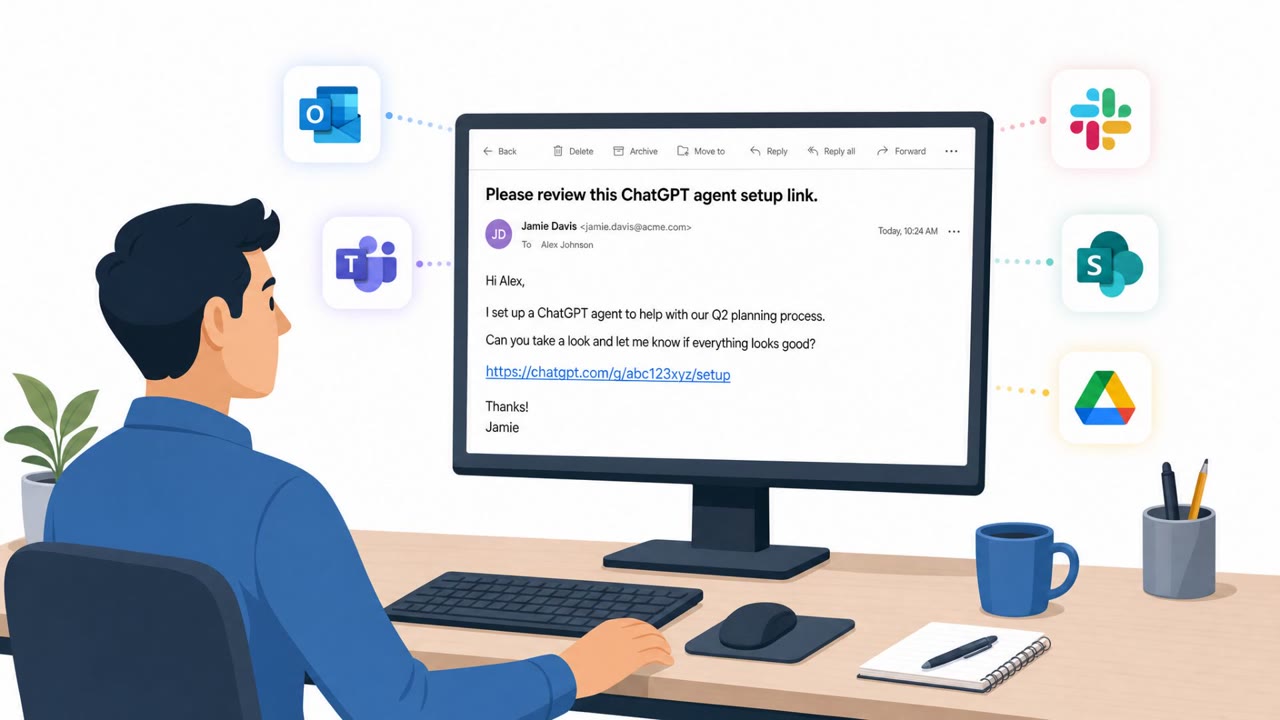
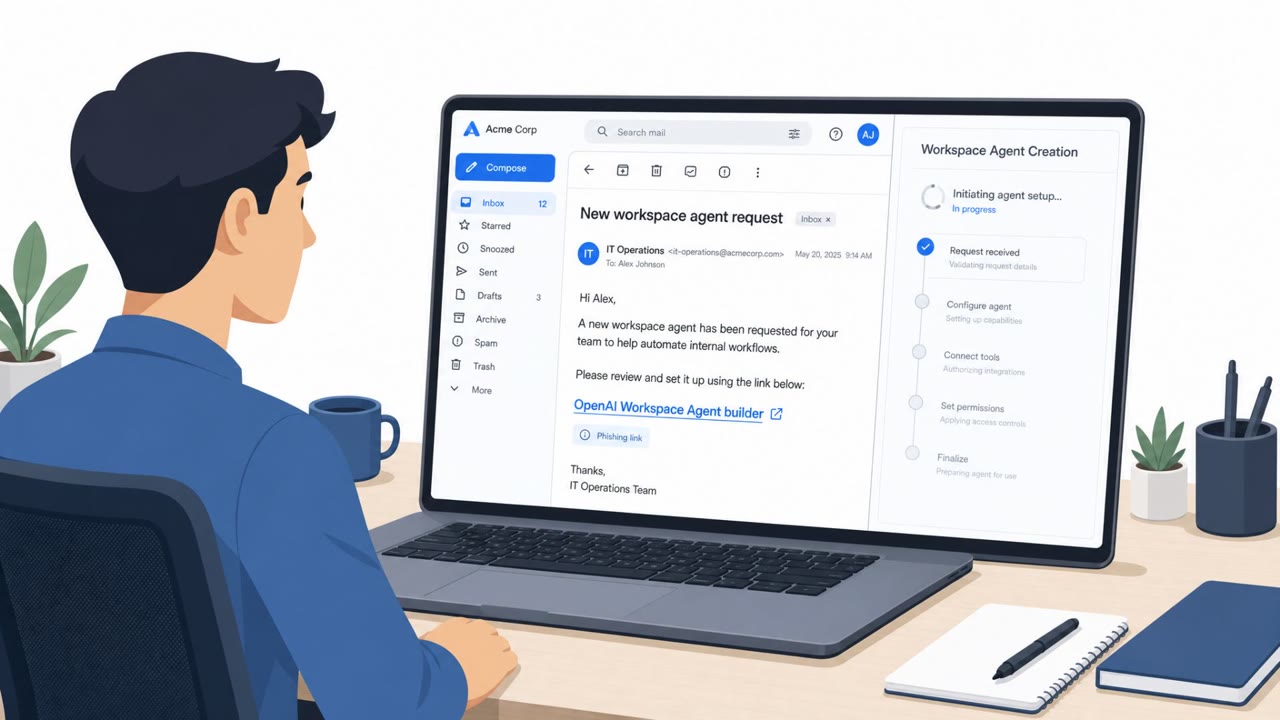
Zenity Labs described a real phishing-based technique (“AgentForger”) that could silently create an autonomous AI agent inside an OpenAI workspace after a single click. The planted agent can keep running on a schedule, read and act across connected tools like Outlook/Slack/Drive, and execute new…

July 24, 2026
13M Emails Push Japan Users Into Tech Support Scam

13M Emails Push Japan Users Into Tech Support Scam

Researchers observed a long-running tech support scam that sent over 13 million emails, mostly to Japanese “.jp” addresses, pushing victims to fake security alert websites. The lures increasingly looked like workplace HR and internal IT notices, aiming to trick employees into clicking links,…

July 23, 2026
TA488 “Half-Click” Emails Hack Zimbra Webmail

TA488 “Half-Click” Emails Hack Zimbra Webmail

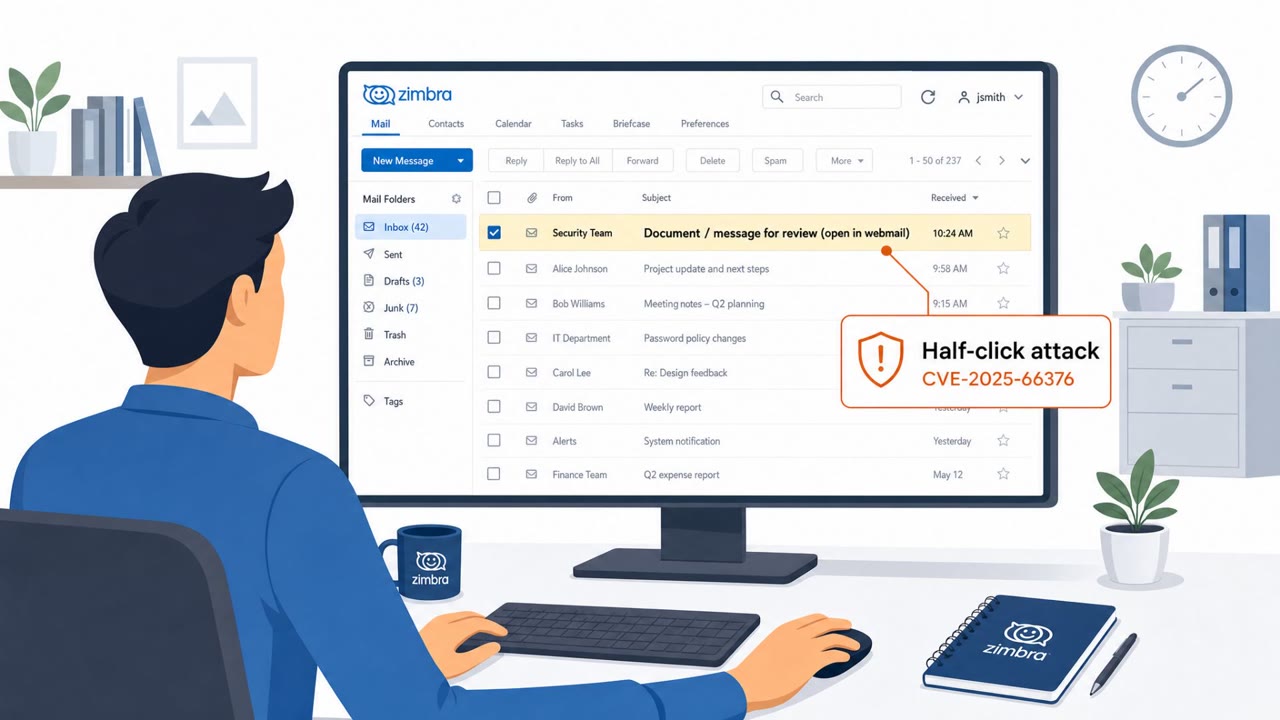
A Russian-aligned group (TA488) used malicious emails to exploit a Zimbra webmail flaw so that simply opening or previewing a message triggered compromise, no link click or attachment required. The attackers then stole email data and set up persistent access to compromised mail servers, including…

July 23, 2026
Zero-Click Emails Hit Zimbra Users in Espionage Push

Zero-Click Emails Hit Zimbra Users in Espionage Push

Government agencies and security firms warn that Russia-aligned hackers are using “zero-click” phishing emails to compromise organizations using Zimbra webmail. The attack hides a malicious JavaScript payload inside an email so it runs when the message is opened, aiming to steal recent email,…

July 23, 2026
Fake CAPTCHA “Copy/Paste” Sites Push CastleLoader

Fake CAPTCHA “Copy/Paste” Sites Push CastleLoader

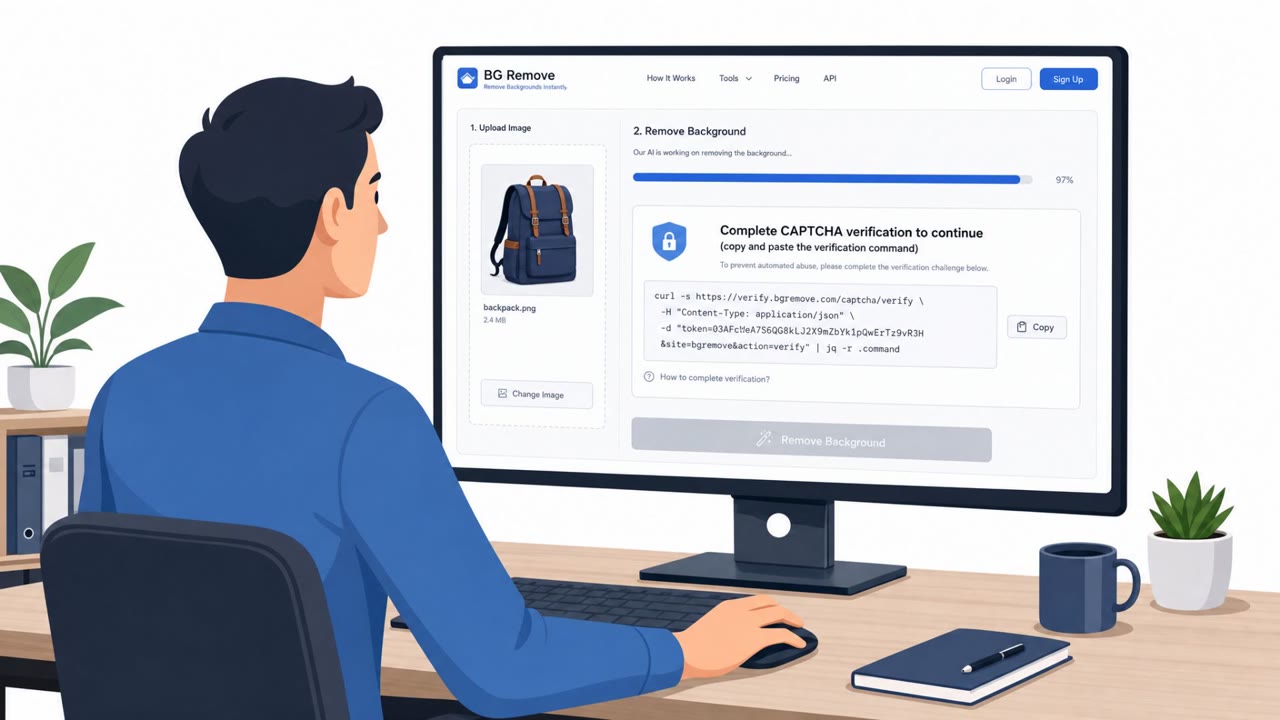
Threat actors are using fake CAPTCHA pages on compromised or lookalike websites to trick people into copying and pasting malicious commands (“paste and run”). The article describes real campaigns tied to CastleLoader and similar activity, including fake background-removal sites and job-site…

July 23, 2026
Zimbra Email View Triggers Russian Data Theft

Zimbra Email View Triggers Russian Data Theft

Government agencies say a Russian-linked group sent specially crafted HTML emails that exploit a Zimbra webmail flaw, so simply viewing the message can trigger data theft, no click required. The campaign has targeted multiple Western sectors since July 2025 and focuses on stealing email content and…

July 23, 2026
Fake Claude App and Alert Apps Drive New Scams

Fake Claude App and Alert Apps Drive New Scams

This roundup describes multiple real-world campaigns where attackers trick people into installing malicious software that looks legitimate (a fake Claude desktop app, a fake emergency alert app, and banking-malware phishing). The common pattern is “looks normal, feels urgent,” leading users to…

July 23, 2026
BEC ‘Are you at your desk?’ Lures Surge in Q2

BEC ‘Are you at your desk?’ Lures Surge in Q2

Microsoft reports billions of phishing attempts in Q2 2026, with attackers increasingly using attachments (PDF/DOC/HTML) and new formats like calendar invites to trick employees into entering credentials. The report also highlights continued growth in Teams-based social engineering and notes that…

July 23, 2026
One-Click Phish Could Spawn a Hidden AI Insider

One-Click Phish Could Spawn a Hidden AI Insider

Researchers disclosed a flaw in OpenAI ChatGPT Workspace Agents that could let an attacker trick an employee into creating an invisible, attacker-controlled “autonomous agent” inside the company. The attack depends on a phishing message that gets a logged-in user to click a weaponized URL, after…

July 23, 2026
Zero-Click Zimbra Webmail Phish Hits NATO Sectors

Zero-Click Zimbra Webmail Phish Hits NATO Sectors

Researchers at Unit 42 reported a real espionage campaign targeting organizations using Zimbra webmail, including government, defense, transportation and financial sectors. The attackers sent “zero-click” phishing emails disguised as news headlines, where opening/viewing the message could trigger a…

July 23, 2026
Fake Claude Download Used in JadeProx Attacks

Fake Claude Download Used in JadeProx Attacks

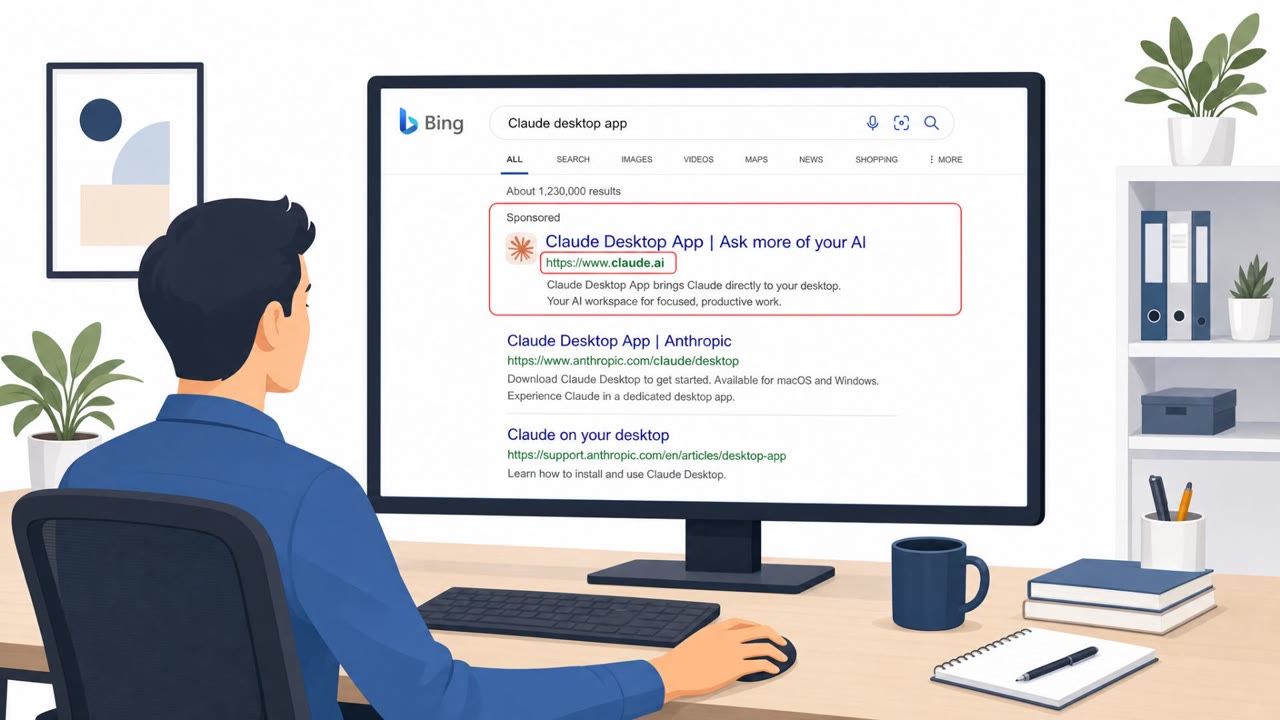
Investigators found evidence of a China-linked operation (tracked as JadeProx) targeting government, healthcare, and education organizations, including spear-phishing and a fake software download site. One campaign impersonated Anthropic’s Claude using a lookalike domain to deliver a malicious…

July 23, 2026
Phishing Link Plants a Rogue ChatGPT “Insider”

Phishing Link Plants a Rogue ChatGPT “Insider”

Researchers say a one-click phishing link could trick ChatGPT into creating a malicious AI “agent” inside a company’s ChatGPT workspace. The agent could act using the employee’s existing access (Outlook, Teams, Slack, Google Drive, etc.), run on a schedule, and take instructions from attacker…

July 23, 2026
Fake Claude Download Page Led to SectopRAT

Fake Claude Download Page Led to SectopRAT

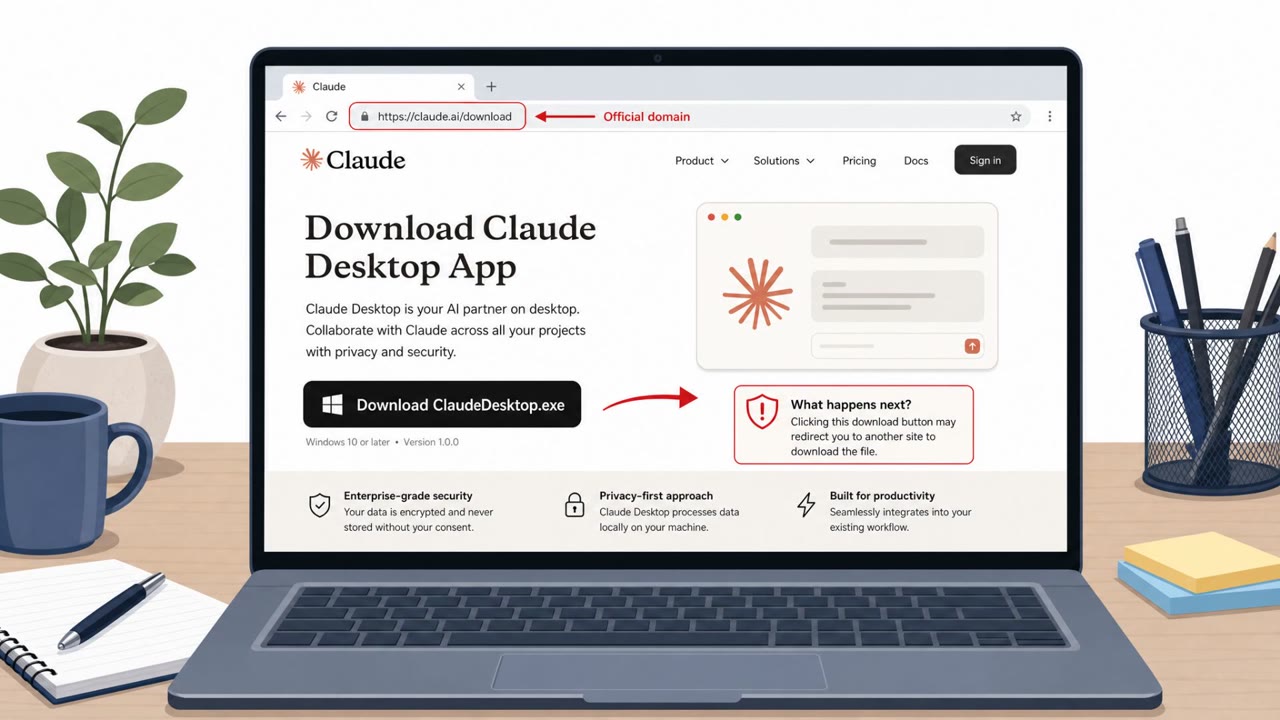
Attackers abused Anthropic’s Claude “Artifacts” publishing feature to host a convincing fake Claude download page on the real claude.ai domain. Victims found it via a sponsored Bing ad, clicked “Download,” and were redirected to attacker-controlled sites that delivered the SectopRAT remote access…

July 23, 2026
Fake Badges and Uniforms to Walk In

Fake Badges and Uniforms to Walk In

The article describes how social engineers can use cheap, online-ordered lookalike lanyards, ID badges, uniforms, and PPE to appear legitimate and gain physical access to facilities. It’s based on real physical security engagements where testers used convincing “visual tokens of trust” (badges,…

July 23, 2026
Deepfake Video Call Drove $25M Wire Transfer Scam

Deepfake Video Call Drove $25M Wire Transfer Scam

The article discusses Google’s new selfie-video account recovery, but it also highlights a real deepfake-enabled fraud case. In that incident, a finance employee joined a video call showing deepfake versions of coworkers and was persuaded to send multiple wire transfers, illustrating how realistic…

July 23, 2026
Chaos RAT Masquerades as Windows Update

Chaos RAT Masquerades as Windows Update

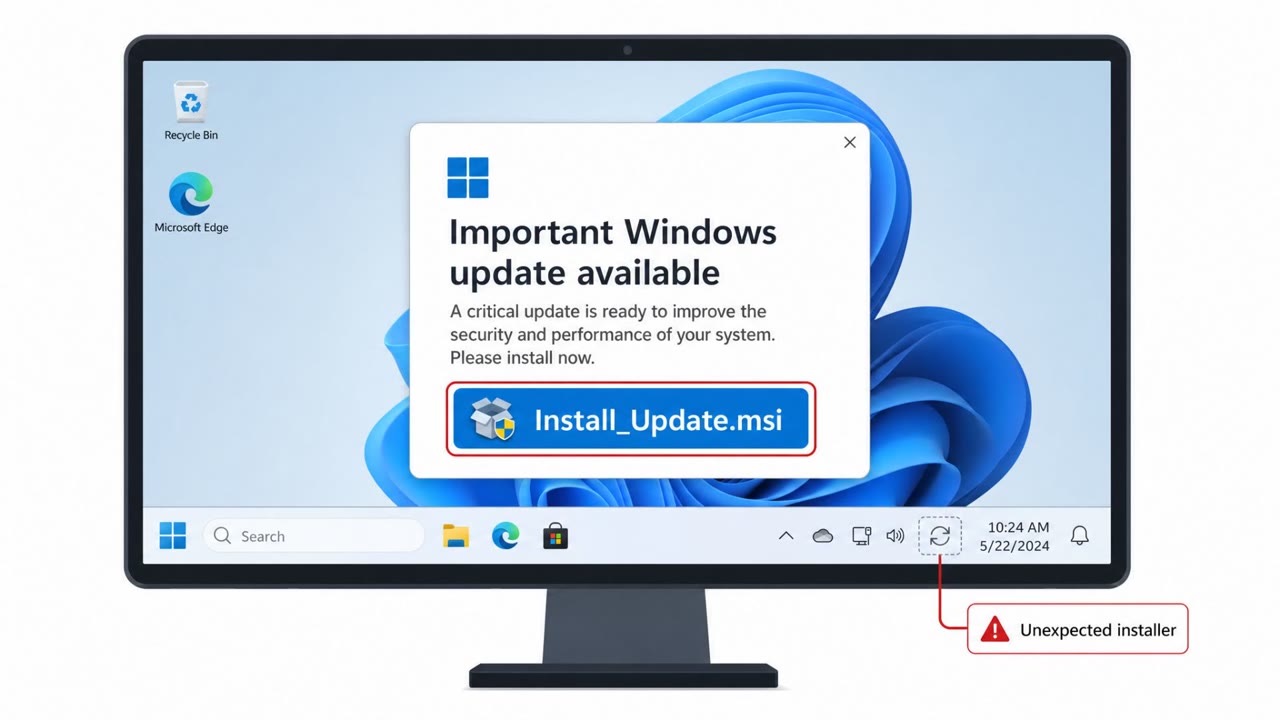
Cisco Talos reports a remote access trojan (msaRAT) linked to the Chaos ransomware group that hides its command-and-control traffic inside legitimate Chrome/Edge browser activity. The malware is delivered as a fake “Windows update” MSI and, once run, launches a browser in a special debug mode to…

July 23, 2026
Fake Badge, Real Access to Hospital Records

Fake Badge, Real Access to Hospital Records

A hired security tester socially engineered a hospital nurse to unlock a restricted medical records room, despite having a non-working fake badge. He used a believable story, referenced a real doctor’s name, and built rapport by complaining about that doctor to convince the gatekeeper to let him…

July 23, 2026
Kimsuky Poses as Diplomats in LNK Phishing

Kimsuky Poses as Diplomats in LNK Phishing

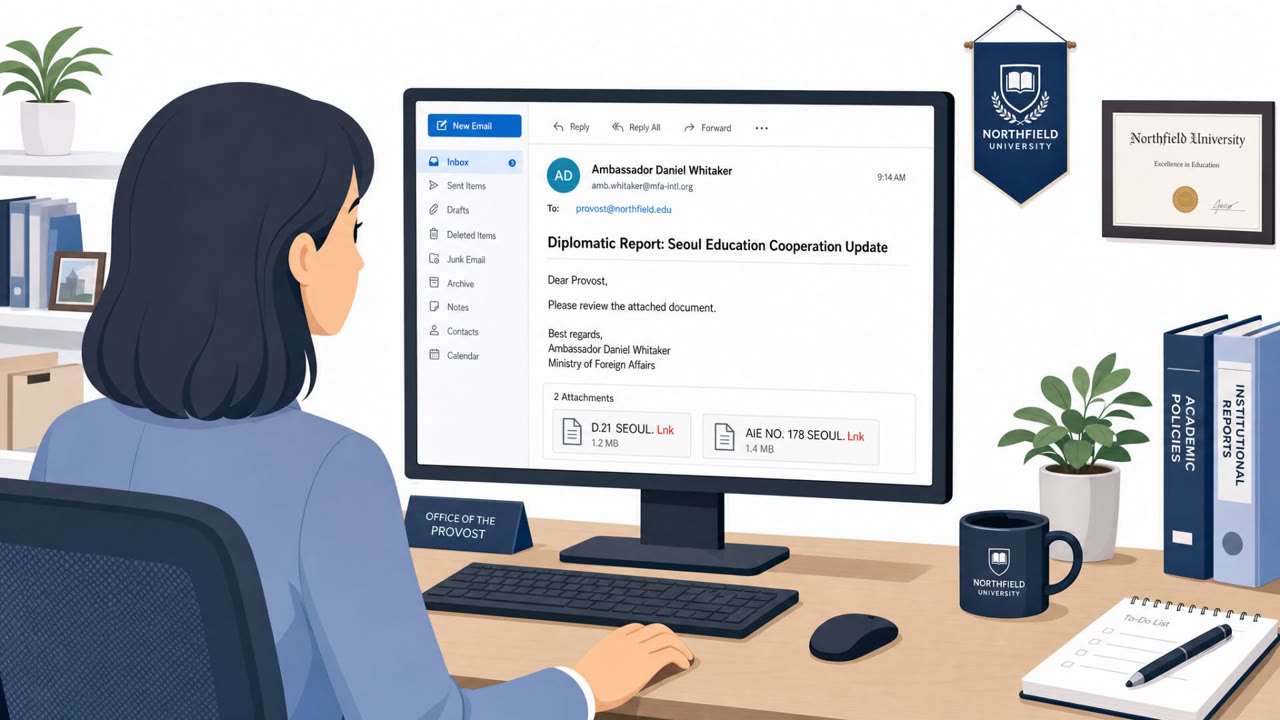
AhnLab reports real-world spear-phishing attacks by the Kimsuky group that impersonate diplomatic personnel and trick targets into opening disguised LNK “document” attachments. Opening the fake document launches scripts that install tools like the PebbleDash backdoor and PrxClient proxy, enabling…

July 23, 2026
Fake Defense Summit Invites Hit Dutch Police

Fake Defense Summit Invites Hit Dutch Police

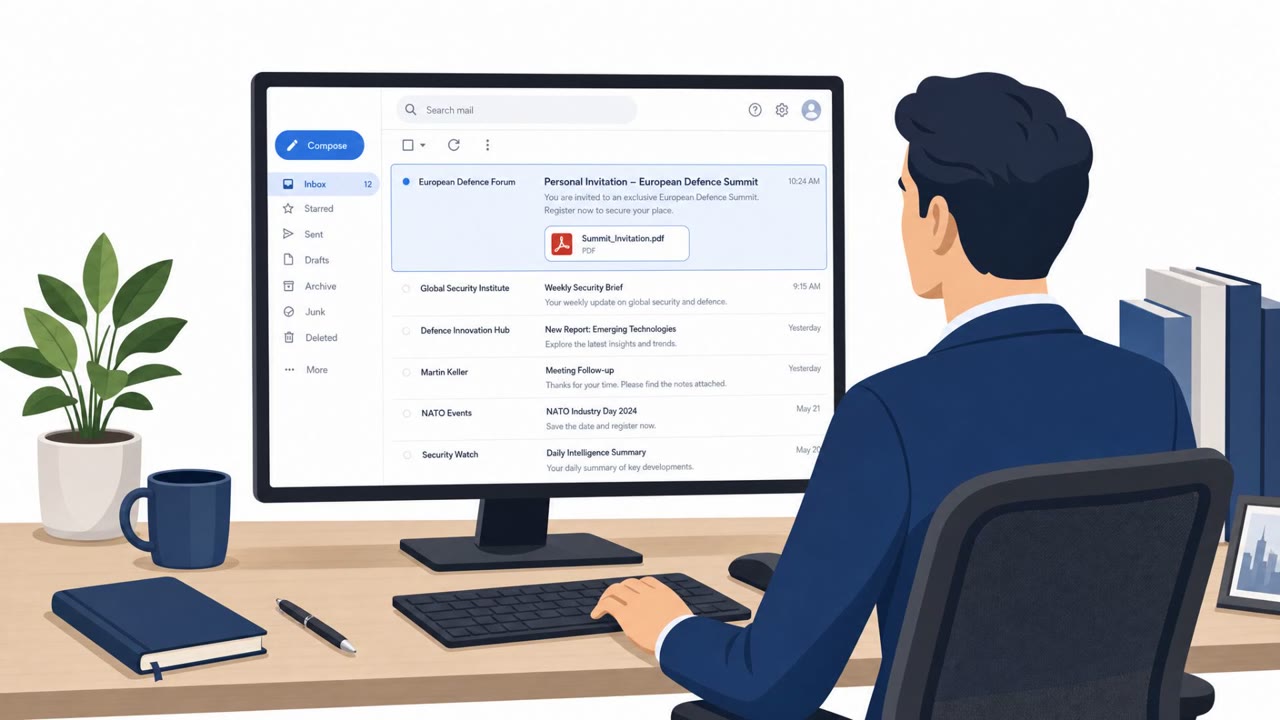
A Russian-linked group allegedly stole sensitive contact data from the Netherlands National Police after getting access to an employee’s email account. The podcast describes a realistic spearphishing lure: an email invitation to a “European Defence Summit” that includes a link or a QR code in a PDF…

July 23, 2026
Device-Code Phish Bypasses MFA via Real Microsoft Login

Device-Code Phish Bypasses MFA via Real Microsoft Login

Attackers abused Microsoft’s OAuth “device code” sign-in so victims completed a real Microsoft login and MFA, but the resulting session tokens were issued to the attacker. In a documented Microsoft 365 takeover, the attacker used a believable partner-law-firm email thread and a Google Sites lure…

July 22, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo