Fake IT Support Calls Fueled $40.5M Ransomware Haul

Help Net Security · High sophistication
Last updated November 19, 2026

Ukrainian police arrested four alleged members of a ransomware group that reportedly extorted more than $40.5 million from at least 28 companies. The group researched targets, then called employees while posing as IT support to obtain login credentials or persuade them to install remote-access software. The article also describes a separate Scattered Spider case involving SMS messages impersonating companies or their IT and BPO suppliers.

Key findings

  • The ransomware group researched each target's finances, assets, employees and IT weaknesses before contacting staff.
  • Attackers impersonated IT support by phone and sought either employee login credentials or installation of remote-access software.
  • One attacker reportedly kept the employee on a call while another entered company systems; the call ended after the intrusion was confirmed.
  • The group used AI-generated voice messages on its own platform.
  • After access, attackers stole data, encrypted files, disrupted operations and threatened to publish stolen information unless paid in cryptocurrency.
  • The group targeted oil and gas, pharmaceutical, industrial, logistics, finance and infrastructure organizations.
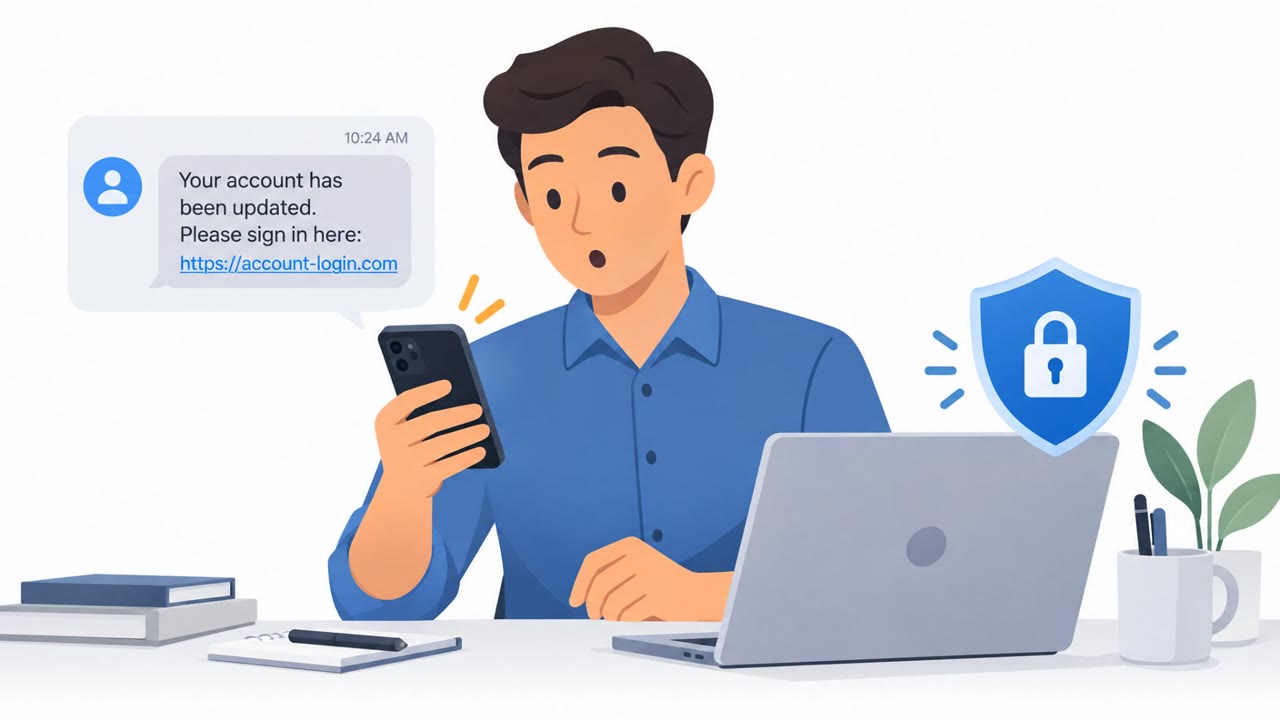
  • In a separate Scattered Spider case, attackers sent SMS phishing messages impersonating victim companies or their IT and BPO suppliers, directing employees to credential-harvesting sites.

Who’s being targeted

  • Commonly targeted roles: All employees, IT helpdesk and support teams, Finance employees, Operations staff, Employees in oil and gas, pharmaceutical, industrial, logistics, financial and infrastructure organizations, Mobile-device users.
  • Affected industries: Oil and gas, Pharmaceuticals, Industrial companies, Logistics, Financial institutions, Infrastructure facilities, Healthcare, Government, Education.
  • Attack channels: vishing, smishing, website.
  • Impersonated: IT support specialists, Victim company or its IT and BPO suppliers.

Awareness takeaways

  • Do not provide passwords or other login credentials to an unsolicited caller, even if the caller claims to be IT support. End the call and verify the request through the organization’s known IT-support channel.
  • Treat unexpected requests to install remote-access software as high risk, especially when the request is made over the phone. Confirm with the IT team using a trusted contact method before installing anything.
  • Do not sign in through links sent by unexpected text messages, even when the message appears to come from your employer, IT provider or outsourcing supplier.
  • Report suspected social-engineering contacts quickly. A short call or text interaction can be enough for attackers to gain access and deploy ransomware.

Red flags to watch for

  • Unsolicited IT-support call
  • Request for passwords or other login credentials
  • Pressure to install remote-access software during a call
  • Unexpected text claiming to be from IT or an outsourcing supplier
  • Link in an SMS directing the recipient to sign in
  • A request for work credentials through an unverified page
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

IT calls out of nowhere: “I can fix that, stay on the line.” This is vishing. After researching your company, the caller asks for your password or remote-access software. While you talk, someone else may enter the system. That’s the tell: they keep you talking until access works. In a separate case, fake company and IT-supplier texts sent employees to password-stealing sign-in pages. Unsolicited IT call or text? Stop there. Contact IT using the number you already know.

MITRE ATT&CK techniques

T1656 - ImpersonationT1566 - PhishingT1566.002 - Phishing: Spearphishing Link · PhishingT1598 - Phishing for InformationT1204.001 - User Execution: Malicious Link · User ExecutionT1563.002 - Remote Services: Remote Access SoftwareT1486 - Data Encrypted for ImpactT1567 - Exfiltration Over Web Service

Similar attacks

Scattered Spider Text Lures Fueled $11.6M Theft

Scattered Spider Text Lures Fueled $11.6M Theft

A Scattered Spider member was sentenced for a campaign that sent hundreds of phishing text messages to employees at technology, telecom, entertainment, cloud communications, and cryptocurrency companies. Victims who entered their details on linked phishing sites had their credentials stolen; the…

November 18, 2026
Russian Spies Reuse Trust to Phish New Victims

Russian Spies Reuse Trust to Phish New Victims

Google says the Russian-linked COLD RELIC group used access to one organization to impersonate its employees and approach people in their trusted professional networks. The attackers used encrypted-message conversations and context-relevant document links to steal Microsoft Entra ID credentials and…

November 19, 2026
AI-Crafted Emails Hide the Usual Warning Signs

AI-Crafted Emails Hide the Usual Warning Signs

Proofpoint described real campaigns where attackers used highly tailored, AI-style messages to make phishing and payment fraud requests appear routine. Examples included property enquiries that led to malicious meeting invitations, device-code phishing pages disguised as business services, and fake…

October 21, 2026
Star Blizzard Uses Trusted Contacts to Phish US Target

Star Blizzard Uses Trusted Contacts to Phish US Target

Russia-linked Star Blizzard breached a second US organization by posing as an employee of an organization it had already compromised. The group used relationship information stolen from the first victim to make its phishing approach appear trustworthy, then stole credentials and identity-session…

November 18, 2026
BO Team Phish Staff After Server Takeover

BO Team Phish Staff After Server Takeover

After defenders cut off BO Team’s access to a Russian software developer, the group launched a credential-stealing phishing campaign against employees. The email claimed the recipient’s mail account had been disconnected and directed them to a fake password-change page made to resemble the…

November 16, 2026
Attackers Hide Malware in Trusted Email Threads

Attackers Hide Malware in Trusted Email Threads

Threat actors are hijacking existing email conversations, or patiently starting new ones, to build trust before sending a malicious reply. The final message commonly poses as a meeting invitation, secure message, shared file, or important document and leads to credential theft or remote-access…

October 21, 2026