Recent Financial Services Cyber Attacks

Page 2 of 13
Revolut Fooled by Fake Government Data Requests

Revolut Fooled by Fake Government Data Requests

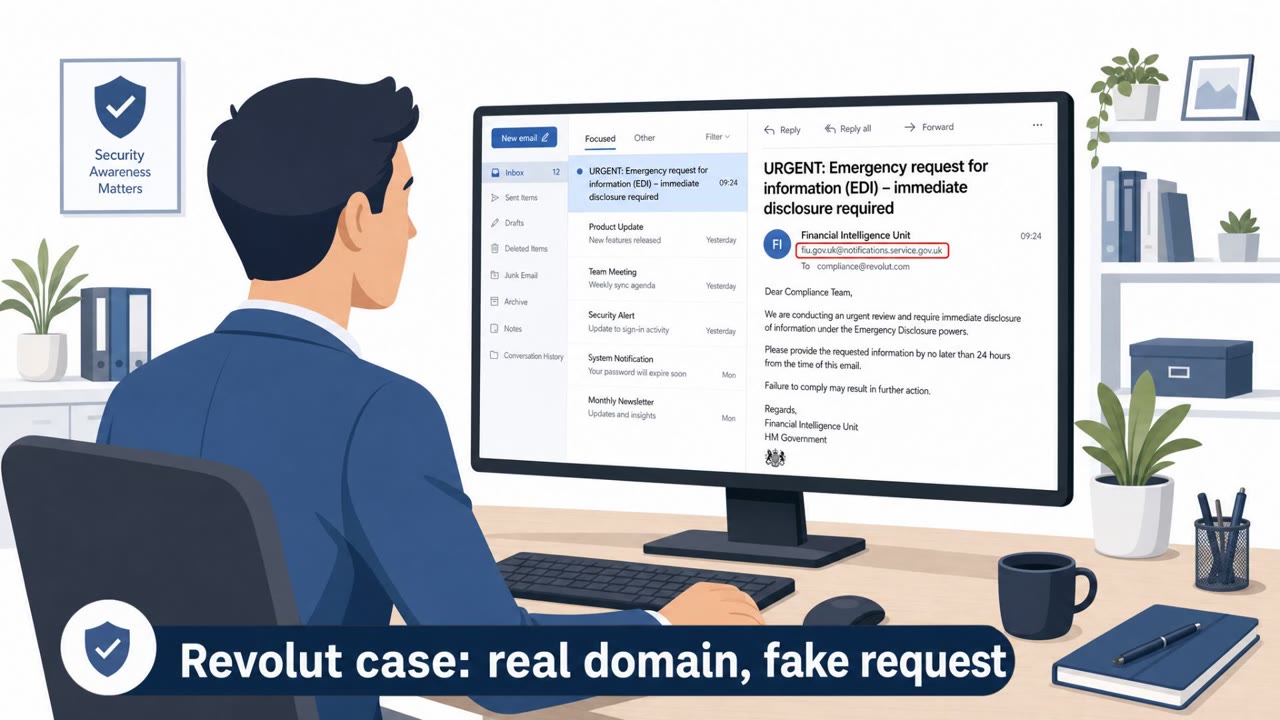
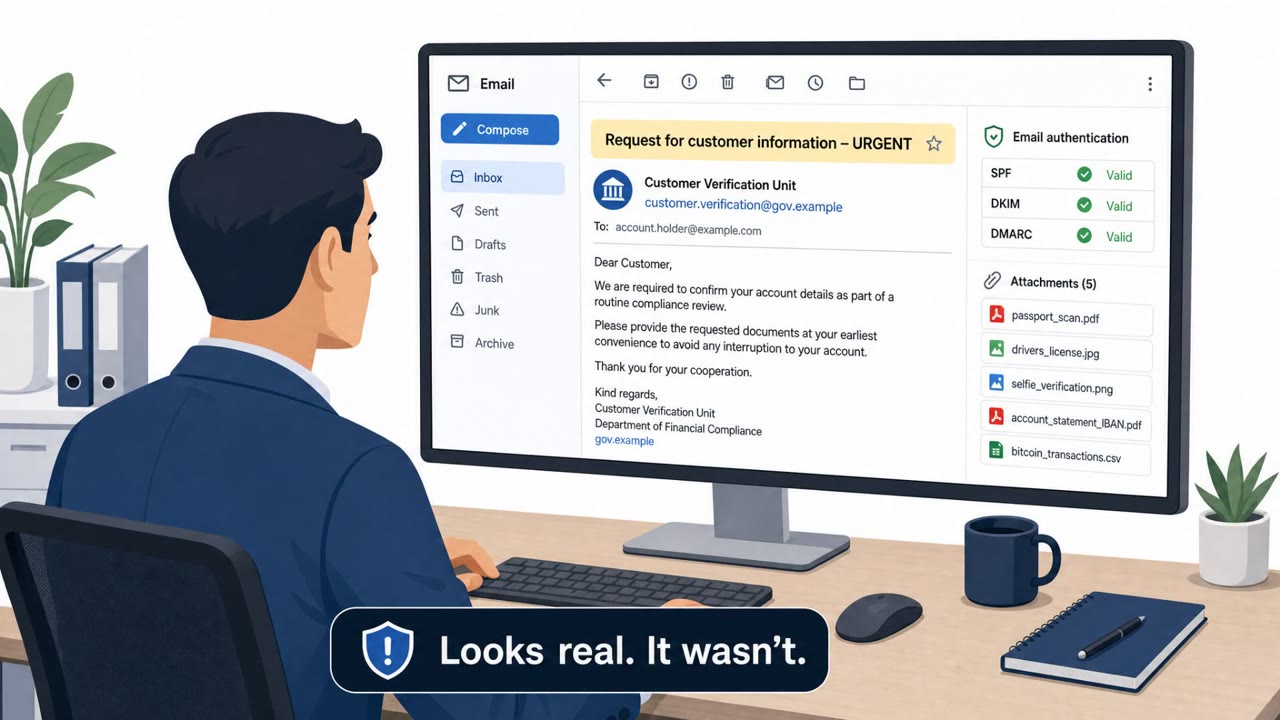
Revolut says it disclosed sensitive customer information after receiving fraudulent information requests that appeared to come from a real government agency email domain. The company framed it as a sophisticated impersonation scam, not a technical break-in, showing how “legitimate-looking” requests…

September 15, 2026
AT&T Insider Aided SIM-Swap Bank Heists

AT&T Insider Aided SIM-Swap Bank Heists

A former AT&T retail employee helped a SIM-swap crew hijack customers’ phone numbers, letting the criminals intercept SMS two-factor codes and reset online banking passwords. The gang then attempted (and in one case succeeded) to wire large sums from victims’ bank accounts, often to accounts in…

September 15, 2026
Black Axe Romance Scam Leaders Extradited

Black Axe Romance Scam Leaders Extradited

U.S. prosecutors say five alleged leaders of Black Axe’s Cape Town group ran long-running online romance and “advance fee” scams that tricked U.S. victims into sending money. The scammers allegedly used fake identities to pose as love interests or trusted contacts, then pushed for payments using…

September 14, 2026
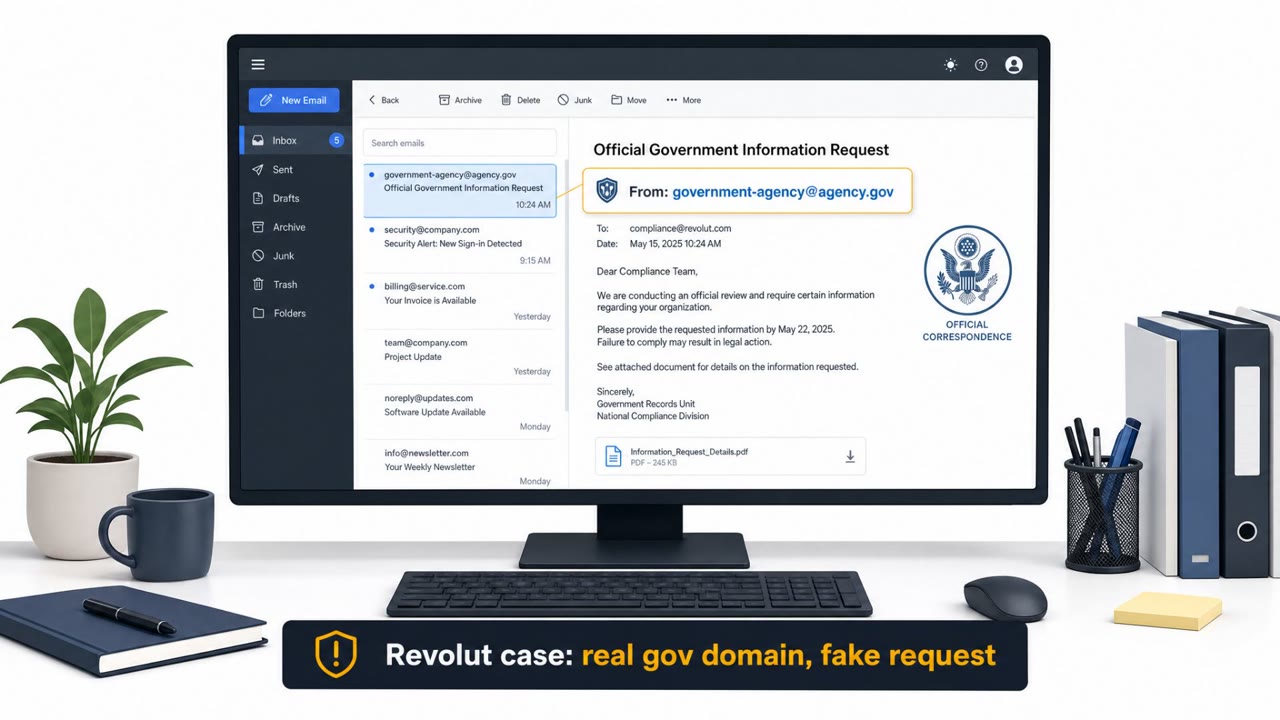
Revolut Hit by Govt-Agency Email Impersonation

Revolut Hit by Govt-Agency Email Impersonation

Revolut says a third party posing as a government agency tricked the company into disclosing some customers’ personal and financial data. The attacker used an email address on a legitimate government agency domain, causing the request to be treated as a real legal inquiry. Revolut says customer…

September 14, 2026
Fraudulent Gov Email and Passkey Lures Hit Orgs

Fraudulent Gov Email and Passkey Lures Hit Orgs

The bulletin describes real-world social engineering where staff were tricked into disclosing sensitive data or access. In one case, Revolut employees responded to fraudulent information requests sent from a real government-domain email account, exposing extensive customer records. Separately,…

September 14, 2026
Revolut Tricked by Fake “Emergency” Data Requests

Revolut Tricked by Fake “Emergency” Data Requests

Revolut confirmed it disclosed sensitive customer information after fraudsters sent “emergency” information requests from a legitimate government email domain. The attackers appear to have targeted high-net-worth customers, including people involved in crypto, and attempted to extort Revolut to…

September 14, 2026
Revolut Fooled by Fake Government Data Requests

Revolut Fooled by Fake Government Data Requests

Revolut confirmed it shared sensitive customer information with an unauthorized party after accepting fraudulent “government” information requests sent from an email address on a legitimate government domain. The company says this was an external impersonation scam (not a system hack) and that…

September 14, 2026
Revolut Tricked by Fake Government Email Requests

Revolut Tricked by Fake Government Email Requests

Revolut confirmed a breach after an attacker impersonated a government agency and sent fraudulent data requests from what appeared to be a legitimate government email domain. Employees processed the requests as normal legal-compliance work, leading to exposure of sensitive customer identity and…

September 14, 2026
Revolut Tricked by Fake Government Email

Revolut Tricked by Fake Government Email

Revolut disclosed it was deceived into sharing highly sensitive customer data after receiving fraudulent information requests that appeared to come from a legitimate government email domain. The attacker’s email passed domain authentication, making it harder to detect, and the shared data may…

September 14, 2026
Fake Government Email Tricked Revolut for Data

Fake Government Email Tricked Revolut for Data

Revolut confirmed that an attacker impersonated a government agency using an email address on that agency’s real domain to obtain sensitive customer records. Revolut says only a limited number of customers were affected and that customer funds and Revolut systems were not accessed.

September 14, 2026
Fake Govt Email Tricked Revolut Into Sharing KYC

Fake Govt Email Tricked Revolut Into Sharing KYC

Revolut says it handed over sensitive customer identity and financial data after receiving what looked like a legitimate government information request. The email came from inside a real government agency’s email domain and passed authentication checks, so staff processed it before later…

September 12, 2026
AI-Polished CEO Invoice Scam Hits 1M+ Emails

AI-Polished CEO Invoice Scam Hits 1M+ Emails

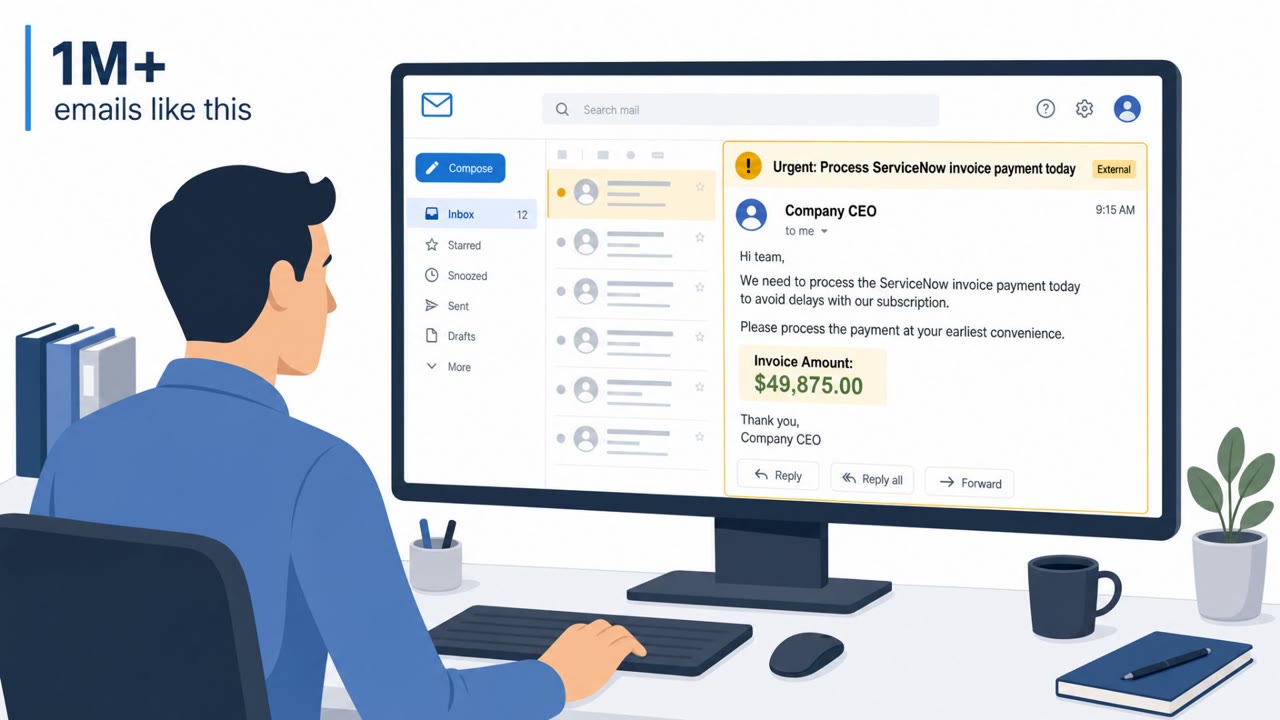
Microsoft reports a large business email compromise campaign where criminals impersonated company executives and used fake vendor branding to pressure accounts payable teams into paying nearly $50,000. The emails looked more believable by embedding a fabricated forwarded email chain (including a…

September 11, 2026
Brevo Breach Fuels Crypto Newsletter Phishing

Brevo Breach Fuels Crypto Newsletter Phishing

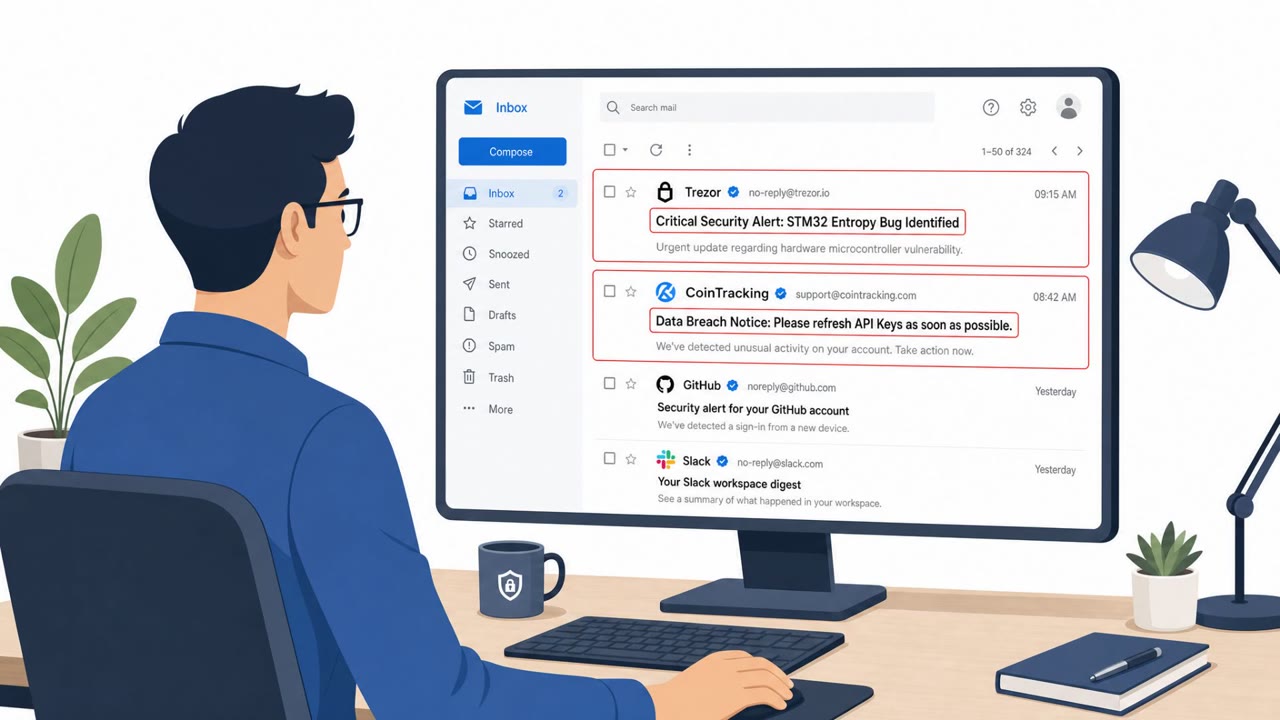
Attackers abused access to Brevo (an email marketing platform) to send highly convincing phishing emails from legitimate cryptocurrency company domains to newsletter subscribers. The lures claimed urgent security issues (hardware vulnerability or data breach) and pushed victims to click links,…

September 11, 2026
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

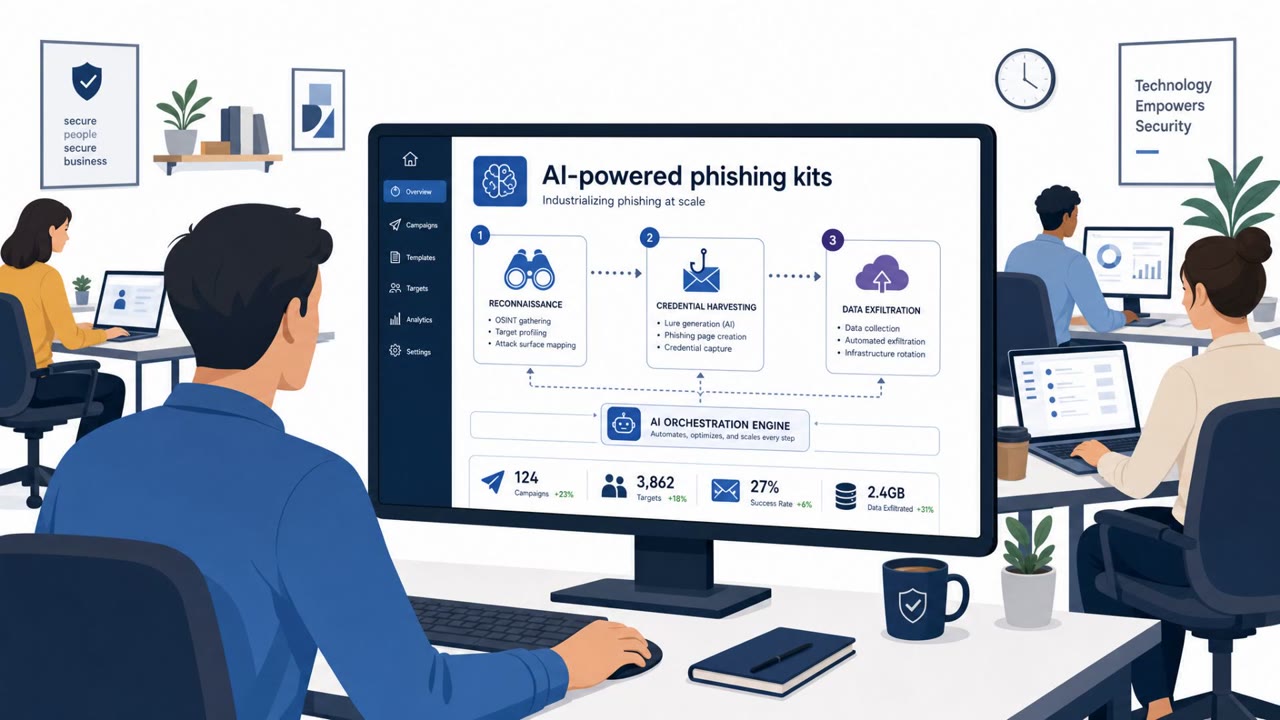
Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
FBI Warns of OAuth Consent Phishing Tricks

FBI Warns of OAuth Consent Phishing Tricks

A SecurityWeek roundup highlights multiple real-world scams and campaigns where attackers trick people rather than “hack” systems directly. Notable items include OAuth “consent phishing” (getting users to approve a malicious app’s access), and phishing-evasion using invisible Unicode characters…

September 11, 2026
Trezor Users Hit by “Critical Security Alert” Phish

Trezor Users Hit by “Critical Security Alert” Phish

Trezor reported that about 347,000 customers received phishing emails after attackers abused a breach at its third‑party email marketing provider, Brevo. The phishing message used a “Critical Security Alert” theme and linked to a malicious site that attempted to trick users into entering their…

September 11, 2026
Gigabud Clones Banking Apps in Hidden Work Profile

Gigabud Clones Banking Apps in Hidden Work Profile

Researchers say the Android banking Trojan “Gigabud” can trick victims into installing a fake app, then create a separate Android work profile and run a cloned banking app inside it. Attackers can perform fraudulent transactions from that cloned app, which may reduce the chance that bank defenses…

September 11, 2026
One-Click Sogou Link Trick Dropped GRAYRABBIT

One-Click Sogou Link Trick Dropped GRAYRABBIT

Researchers reported a real intrusion where a China-linked group used a crafted link to exploit Sogou Input Method on Windows and install the GRAYRABBIT backdoor. Victims were lured into opening a special link (potentially via email or chat), which redirected Sogou’s built-in browser to an…

September 11, 2026
China-Linked Hackers Push “Gemini” Phish With Zero-Days

China-Linked Hackers Push “Gemini” Phish With Zero-Days

Proofpoint reports multiple China-aligned espionage groups used a chained set of browser/Windows zero-days (“BlueMoon”) and delivered it through phishing emails. Victims who clicked a phishing link could end up with a malicious browser extension disguised as Google Gemini, letting attackers watch…

September 11, 2026
Pig Butchering Scams Drive $12.7B Crypto Losses

Pig Butchering Scams Drive $12.7B Crypto Losses

FinCEN reports that overseas scam centers stole about $12.7B from U.S. victims since 2023, largely through “pig butchering” style cryptocurrency investment scams. Scammers build trust using fake personas (often romance or “financial adviser” roles), then pressure victims to buy crypto and send it…

September 10, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo