Recent Government Cyber Attacks

Page 11 of 13
Criminals Trick AI Guardrails With “Split Tasks”

Criminals Trick AI Guardrails With “Split Tasks”

Cisco Talos reports criminals are bypassing safety controls in popular AI coding tools by splitting harmful work into small, seemingly harmless requests and by claiming they are authorized owners of the systems being targeted. The research is based on real prompt logs recovered from threat actor…

August 4, 2026
Hotel Wi‑Fi Lures Steal M365 Logins, Drop Malware

Hotel Wi‑Fi Lures Steal M365 Logins, Drop Malware

Microsoft says Russian-linked threat actors compromised hotel and conference guest Wi‑Fi “captive portal” networks to redirect travelers to fake Microsoft 365 sign-in pages, device-code phishing, or fake update pages. The goal was to steal cloud credentials (including Entra ID device codes) and…

August 4, 2026
Fake IRS Letters Push Crypto Users to QR Scam

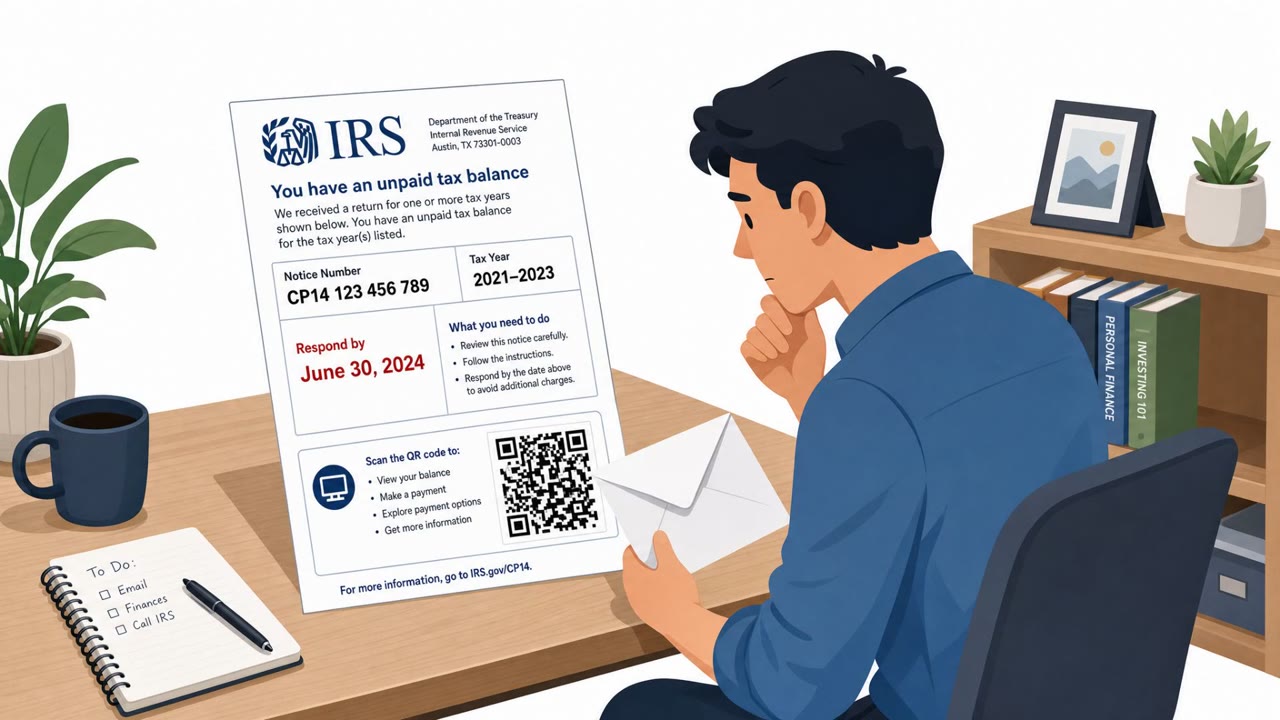
Fake IRS Letters Push Crypto Users to QR Scam

Scammers are mailing physical letters that mimic official IRS notices and pressure cryptocurrency holders to “enroll” in a fake Digital Asset Compliance Portal. Victims are driven to scan a QR code, enter details about their exchange and holdings, and provide a phone number for a follow-up call.…

August 4, 2026
Consent Phishing and Hijacked Hotel Wi‑Fi Portals

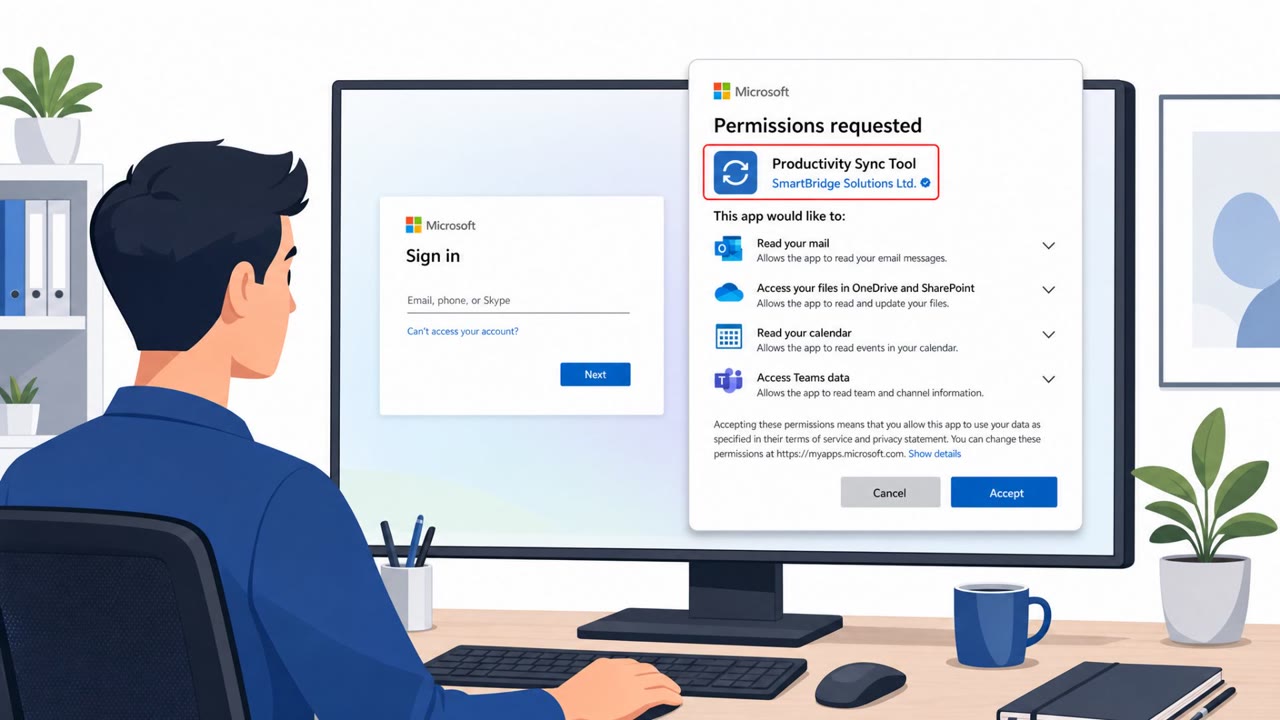
Consent Phishing and Hijacked Hotel Wi‑Fi Portals

This weekly threat bulletin summarizes multiple real-world incidents, including phishing that abuses Microsoft’s legitimate app login/consent screens and a campaign that hijacks hotel Wi‑Fi captive portals. In both cases, the goal is to trick people into granting access or capturing Microsoft…

August 3, 2026
Ransomware Crew Poses as “Ransomware Help”

Ransomware Crew Poses as “Ransomware Help”

After exploiting SonicWall SMA 1000 VPN appliances, attackers tied to INC Ransomware reportedly contacted victims directly using emails and phone calls claiming they could help with “ransomware issues.” One caller said he was “from a group of hackers,” asserted the network was compromised, and…

August 1, 2026
DNC Staffer Fooled by Chair Impersonation Scam

DNC Staffer Fooled by Chair Impersonation Scam

A scammer impersonated the Democratic National Committee chair and convinced a staffer to send nearly $29,000. The DNC detected the issue within minutes, but only recovered part of the funds. This is a classic business email compromise (BEC) pattern: a trusted executive identity is used to pressure…

August 1, 2026
Korea Flags Job-Offer Phish + Watering Holes

Korea Flags Job-Offer Phish + Watering Holes

South Korean agencies warned that a state-backed hacking group is actively targeting citizens and businesses using job-themed phishing emails and “watering hole” attacks on legitimate websites. The phishing lures include fake job applicants sending resume links and impersonated recruiters sending…

July 31, 2026
Fake China Police App Tied to Android RAT Ring

Fake China Police App Tied to Android RAT Ring

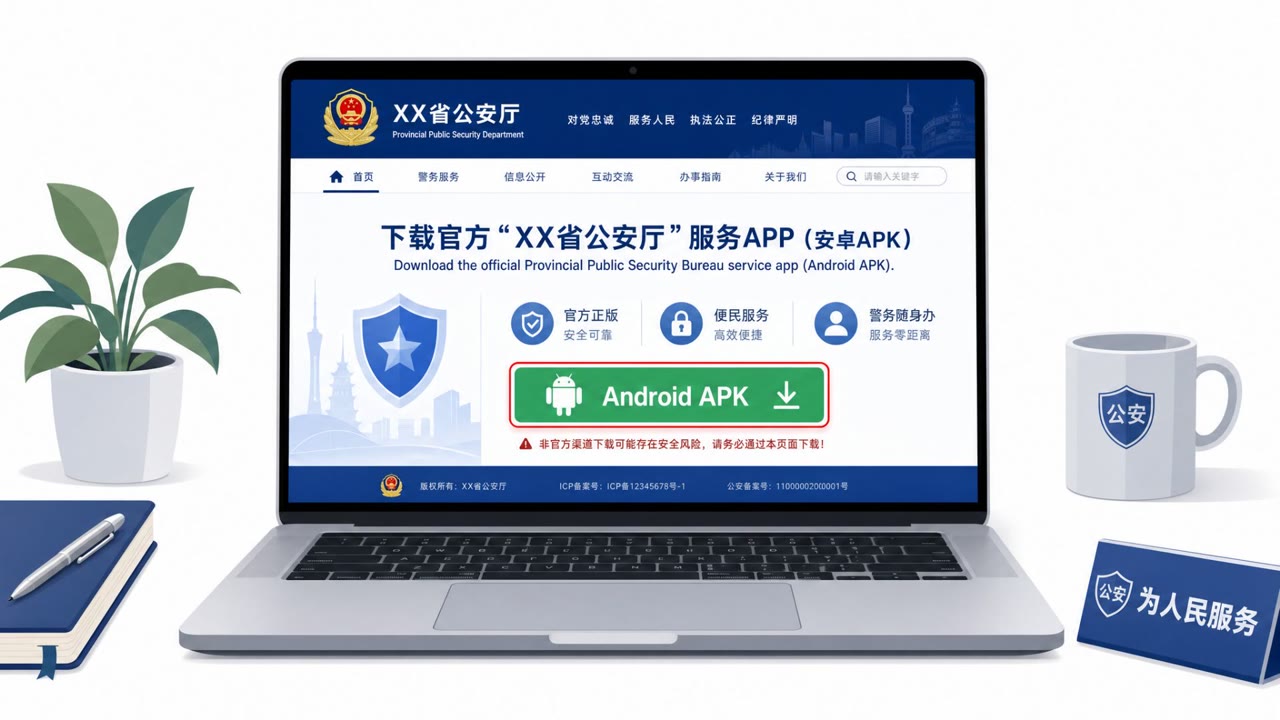
Researchers investigated a fake Android app posing as a Chinese public security bureau service and traced it to a broader criminal ecosystem using a leaked Android remote-access tool (RAT) framework called “Flying Eagle.” The tooling lets criminals build convincing look‑alike apps and then steal…

July 31, 2026
Lazarus-Linked Lures Hit Korea via Surveys & Sites

Lazarus-Linked Lures Hit Korea via Surveys & Sites

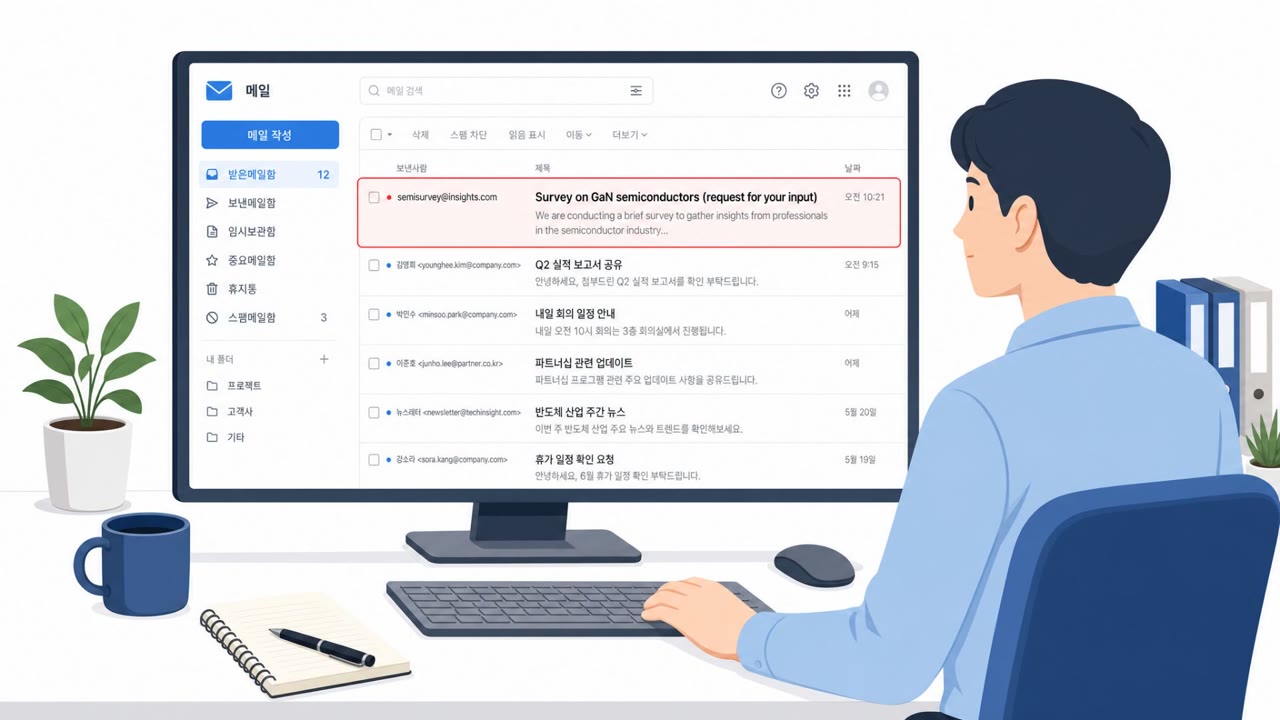
South Korean agencies and AhnLab warn that tools tied to North Korea’s Lazarus Group appear to be shared with the Gunra ransomware operation targeting South Korean organizations. The campaign used compromised legitimate websites (watering-hole attacks) and spearphishing emails, including messages…

July 30, 2026
TA488 “Half-Click” Email Triggers OWA Exploit

TA488 “Half-Click” Email Triggers OWA Exploit

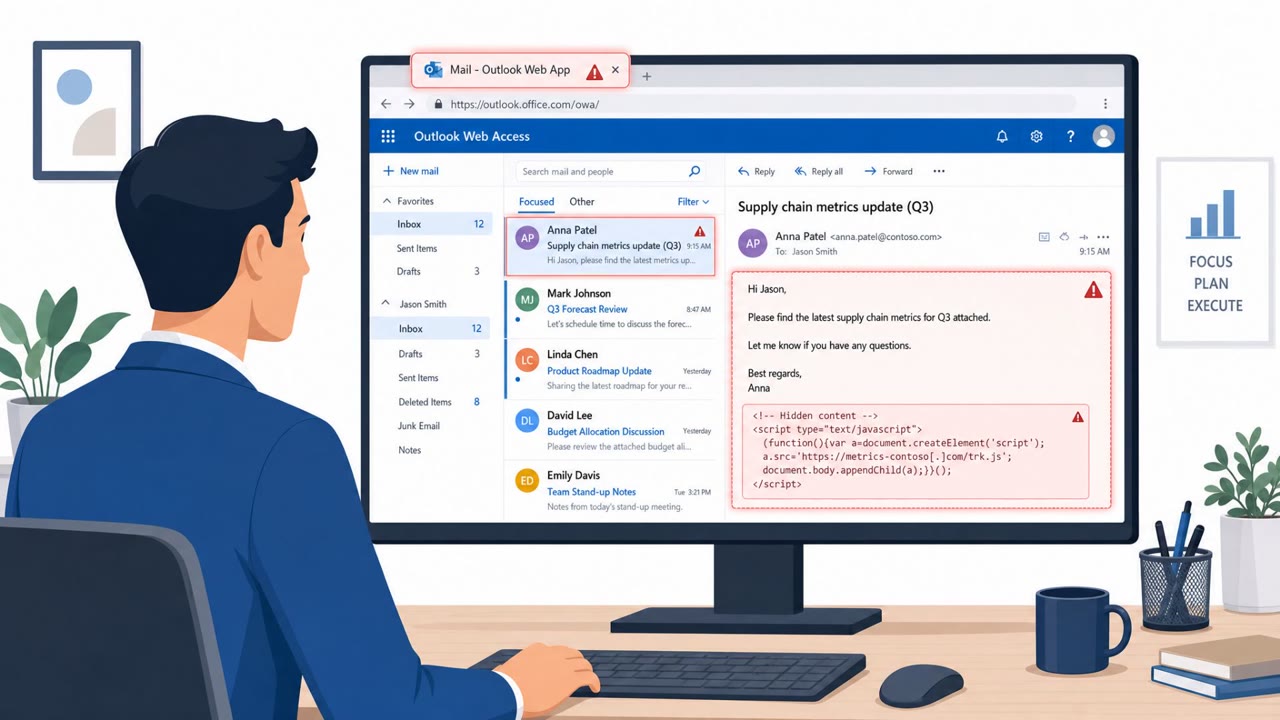
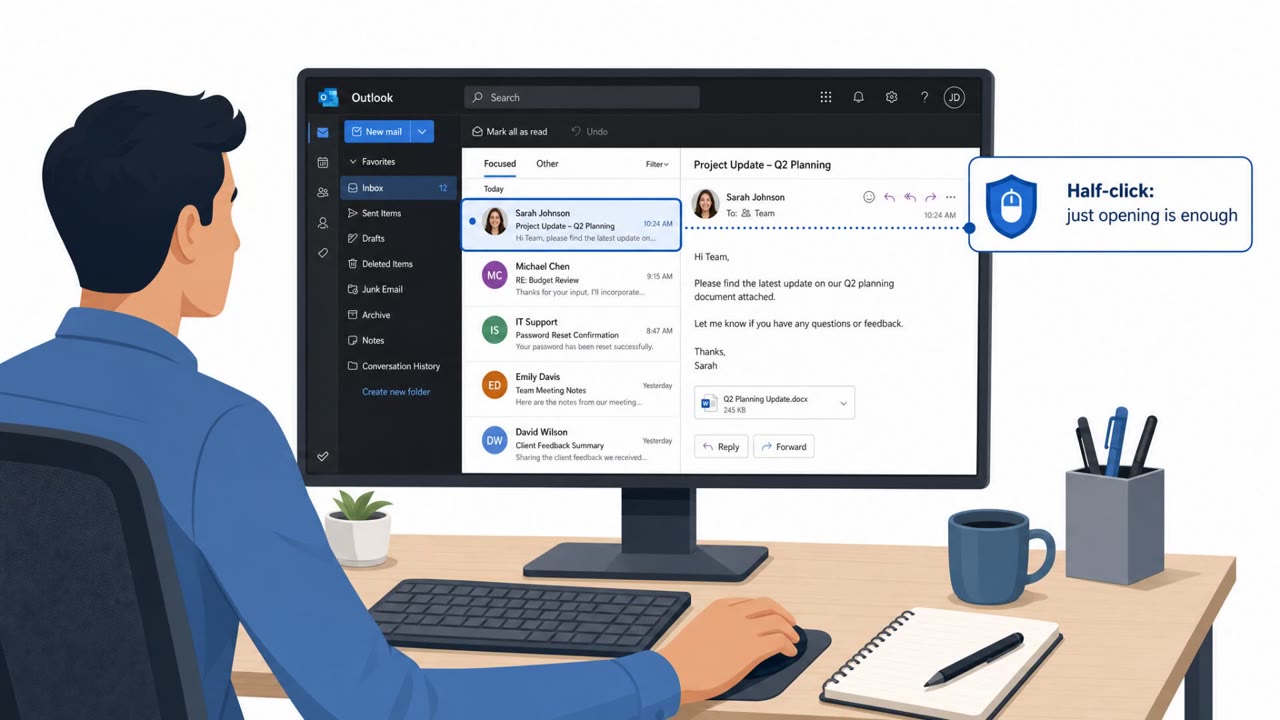
Researchers reported a real TA488 campaign where a specially crafted email exploits an Outlook Web Access (OWA) flaw and runs malicious JavaScript as soon as the user opens the message. The attack relies on normal-looking business topics to get people to quickly view the email, and then uses…

July 30, 2026
Hidden Prompt Turns Copilot Docs Into a Worm

Hidden Prompt Turns Copilot Docs Into a Worm

A security researcher demonstrated that Microsoft Copilot for Word can be tricked by hidden text inside a Word document, causing Copilot to follow attacker instructions. The result is a self-propagating “AI worm” that silently modifies documents and embeds the same hidden prompt into new files,…

July 30, 2026
“Half-Click” OWA Email Trap Spreads

“Half-Click” OWA Email Trap Spreads

Proofpoint reports a Russian-linked espionage group is using booby-trapped emails that infect users simply when they open the message in Outlook Web Access (OWA) on on‑premises Exchange. The attack runs malicious JavaScript inside the victim’s logged-in mail session and installs a stealthy…

July 30, 2026
Half-Click OWA Emails Trigger Stealth Mailbox Takeover

Half-Click OWA Emails Trigger Stealth Mailbox Takeover

A Russia-aligned group (TA488) sent specially crafted emails that triggered malicious JavaScript simply by being viewed in Outlook Web Access (no link click or attachment needed). The implant (“OWAReaper”) can quietly change server-side mailbox permissions and abuse OAuth tokens, so attackers can…

July 30, 2026
“No-Action” Emails Trigger OWA Mailbox Takeover

“No-Action” Emails Trigger OWA Mailbox Takeover

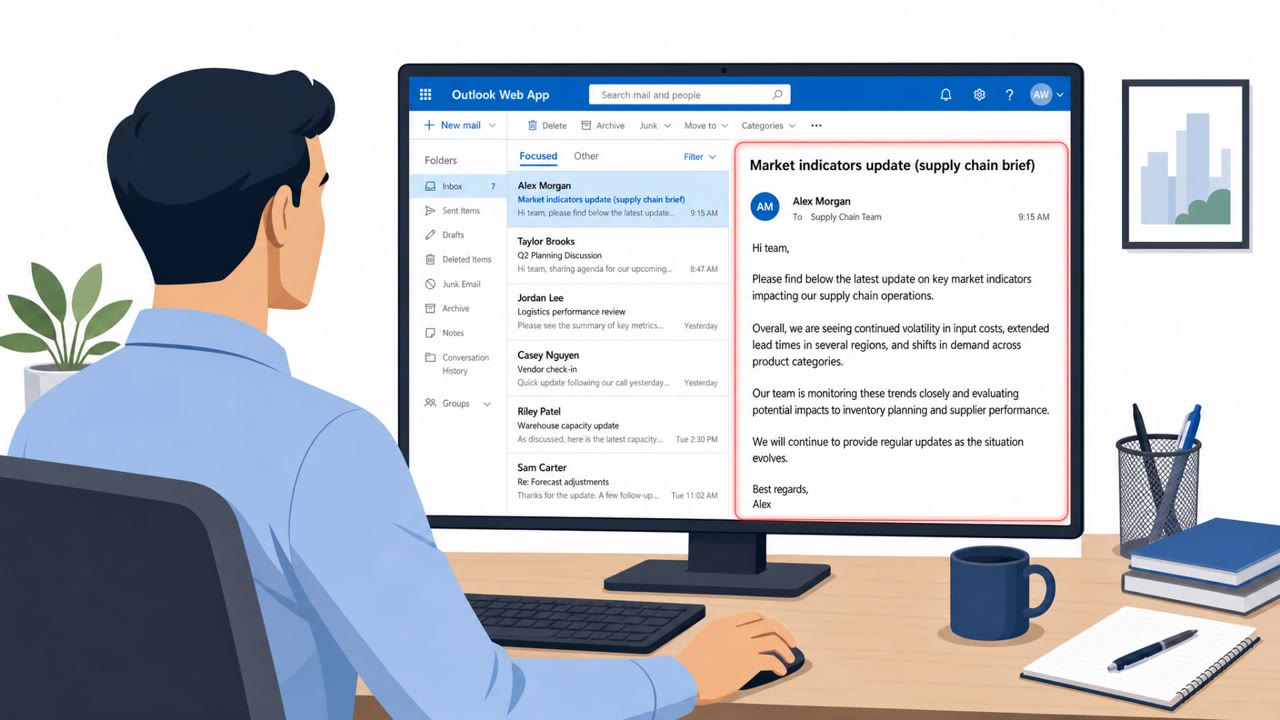
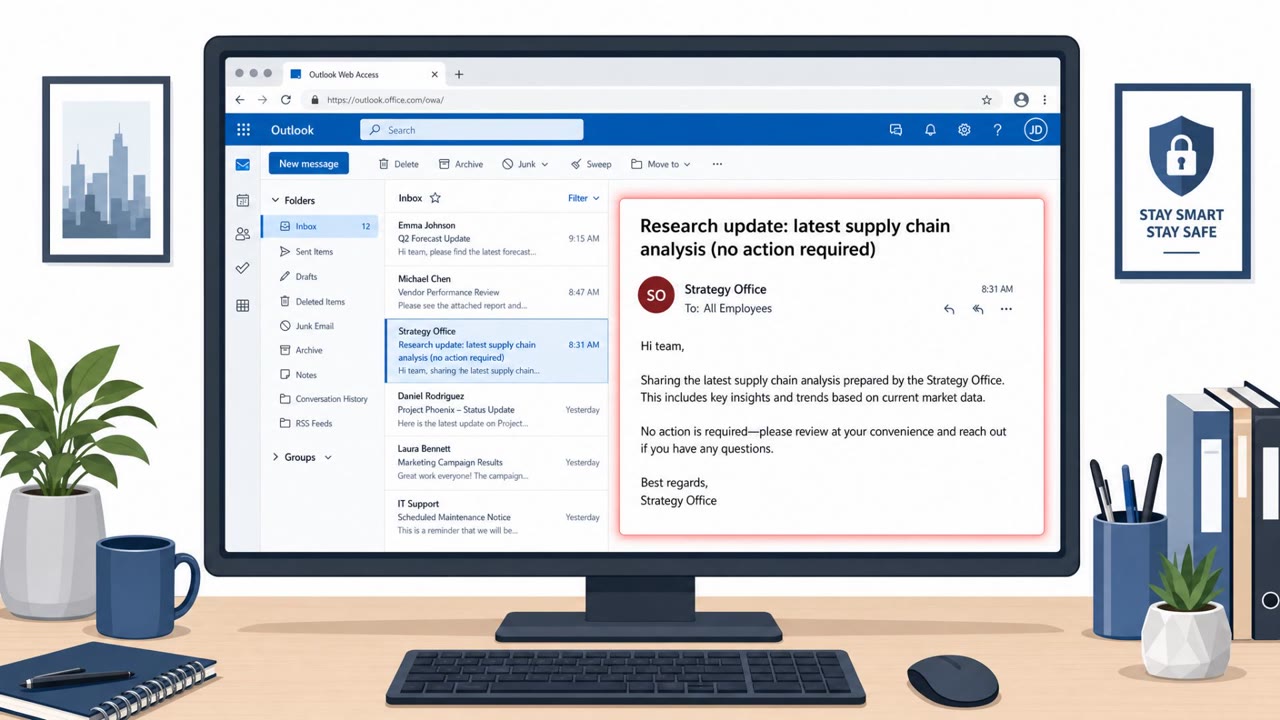
Russian-linked threat actors sent generic-looking informational emails that required no clicking, but simply opening them in vulnerable Outlook Web Access (OWA) could trigger a hidden exploit. The campaign targeted government and multiple industries, then installed a stealthy browser-based implant…

July 30, 2026
Laundry Bear Uses “Half-Click” OWA Email Exploit

Laundry Bear Uses “Half-Click” OWA Email Exploit

UK and US cyber authorities and Proofpoint reported a real campaign where the Russian-linked group “Laundry Bear” (TA488) sent emails that could infect victims simply by being opened in Outlook Web Access. The email’s HTML triggers the server to run attacker code, installing a mailbox-stealing…

July 29, 2026
Telegram Dating Bot Used to Recruit Young Saboteurs

Telegram Dating Bot Used to Recruit Young Saboteurs

Russian authorities allege Telegram was used to recruit and pressure young people into real-world attacks, with “Ukrainian agents” posing as young women via a popular Telegram dating chatbot. The article describes a concrete manipulation workflow (romance/entrapment → coercion) that led to arrests…

July 29, 2026
TA488 Uses “Half-Click” OWA Emails to Persist

TA488 Uses “Half-Click” OWA Emails to Persist

Proofpoint reports a Russia-aligned espionage group (TA488) returned with a campaign that compromises on‑premises Outlook Web Access simply when a user opens an email in the reading pane. The attack uses a cross-site scripting flaw to run hidden JavaScript, install a browser-resident implant, and…

July 29, 2026
Dating Bot Used to Recruit Teens for Sabotage

Dating Bot Used to Recruit Teens for Sabotage

Russian authorities claim Ukrainian intelligence used Telegram, including a Tinder-like dating bot, to recruit Russians (including teenagers) for sabotage and arson inside Russia. The alleged approach involved operatives posing as young women online, building relationships, and then persuading or…

July 29, 2026
Telegram Dating Bot Used for Romance-to-Arson Scam

Telegram Dating Bot Used for Romance-to-Arson Scam

Russia’s FSB claims Ukrainian intelligence used a Telegram dating chatbot to deceive and psychologically pressure young Russians into sharing locations, clicking phishing links, and later carrying out arson or armed attacks. The alleged scheme started with romance-style outreach and payments via…

July 29, 2026
Fake Public Security App Spreads Android RAT

Fake Public Security App Spreads Android RAT

Researchers tied the Flying Eagle Android remote-access trojan to a fake “Public Security” service app aimed at Android users in China. The malicious app was reportedly distributed from a lookalike website and could steal payment credentials and remotely control infected phones. The tooling is…

July 29, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo