Recent Manufacturing Cyber Attacks

Page 6 of 7
Fake Install Guides and Helpdesk Calls Drive Attacks

Fake Install Guides and Helpdesk Calls Drive Attacks

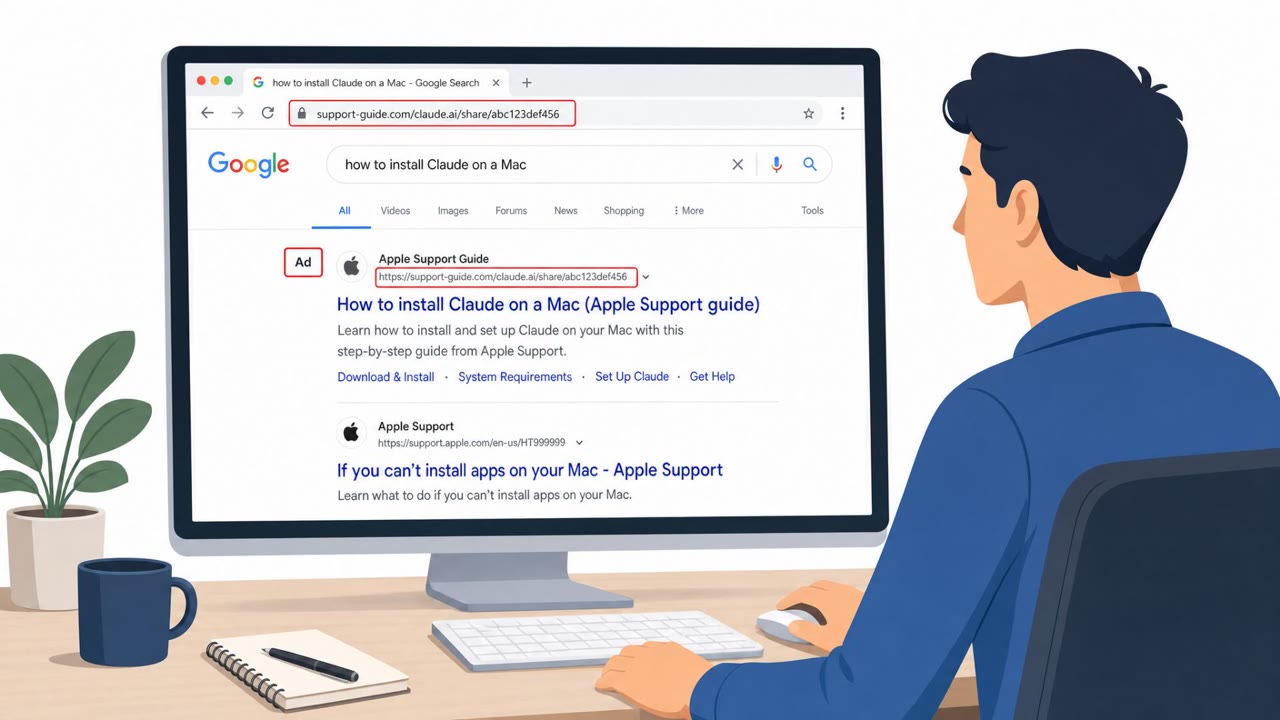
This bulletin describes multiple real-world social engineering campaigns where attackers trick people into trusting a familiar screen, like a search result “install guide,” a recruiter outreach, or a helpdesk phone call. The lures push victims to paste commands, install fake software, or reset MFA,…

July 30, 2026
Fake IT Support Hits Teams to Drop Ransomware

Fake IT Support Hits Teams to Drop Ransomware

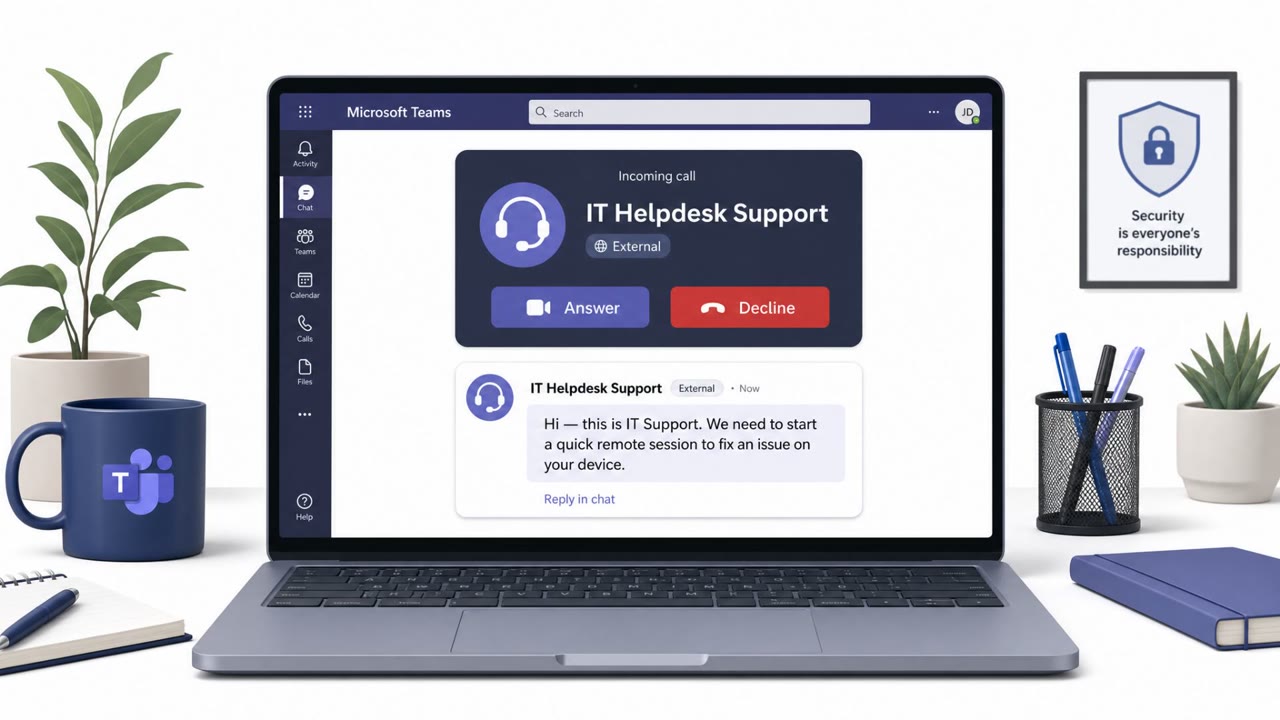
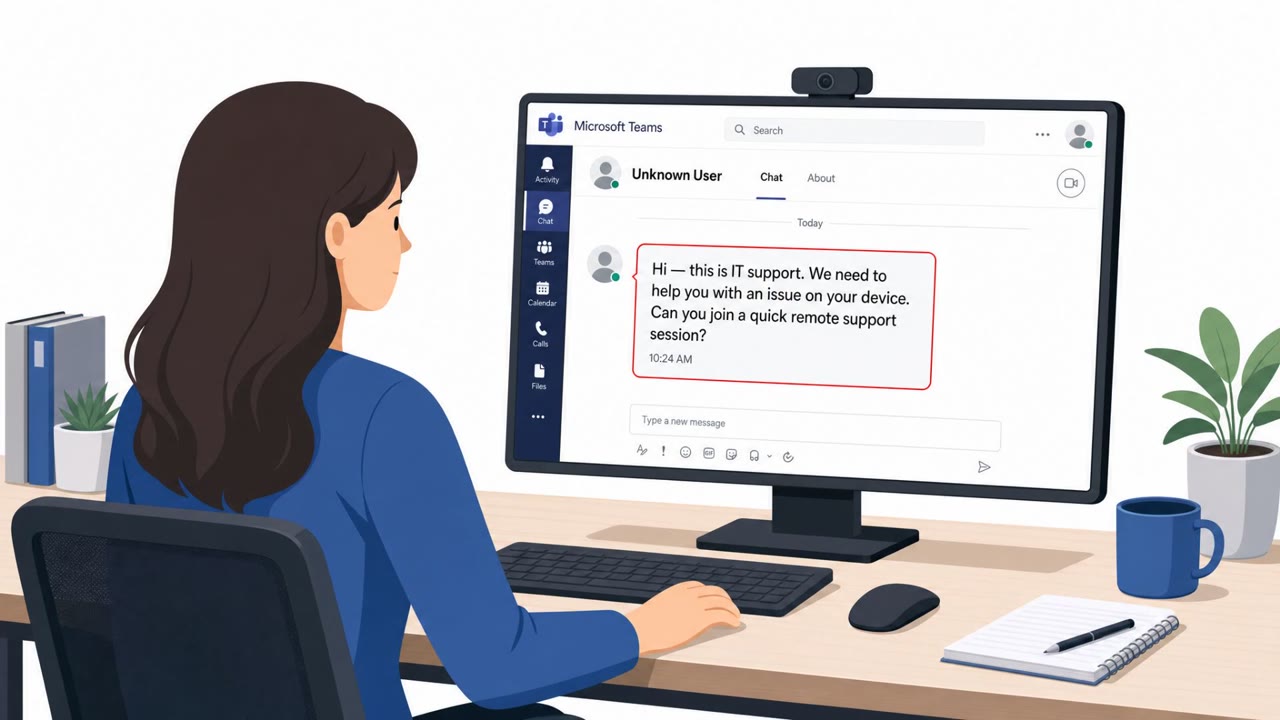
Researchers reported a months-long campaign where attackers used Microsoft Teams chats/calls while pretending to be IT/help desk support. Victims were talked into starting remote-control sessions (Quick Assist or RemSupp), after which the attackers used PowerShell to maintain access and, in some…

July 30, 2026
Lazarus-Linked Lures Hit Korea via Surveys & Sites

Lazarus-Linked Lures Hit Korea via Surveys & Sites

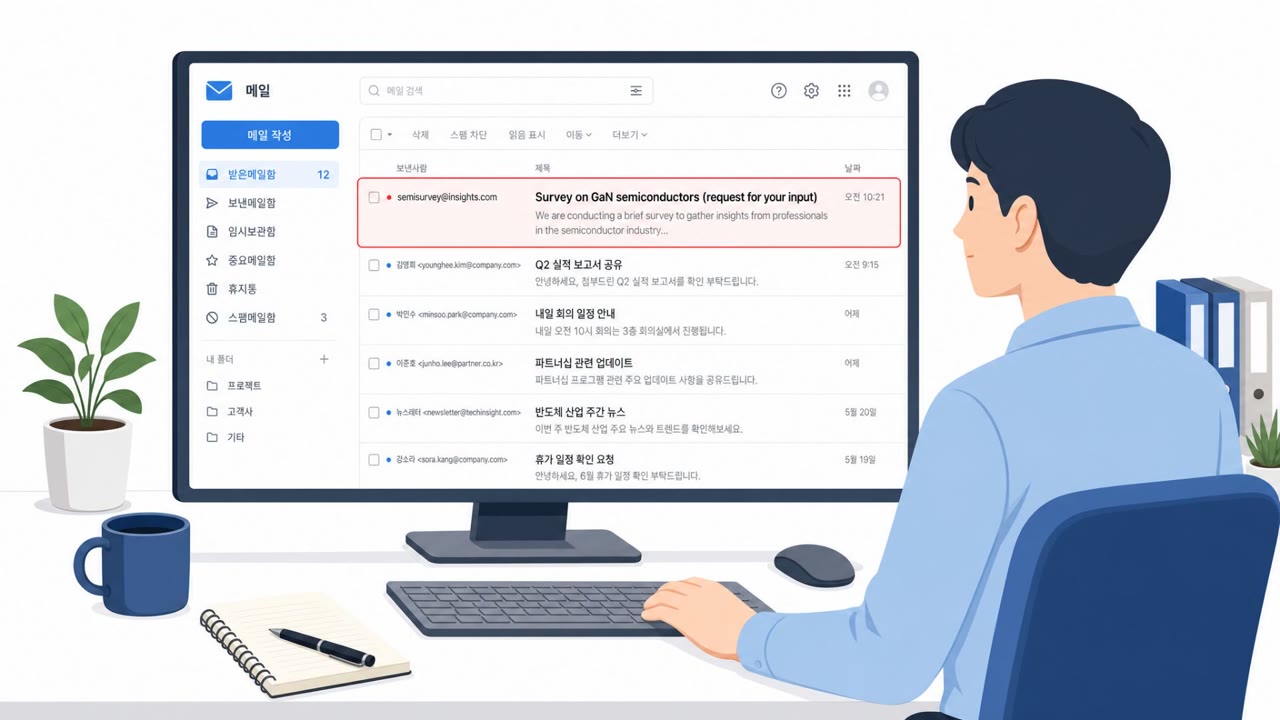
South Korean agencies and AhnLab warn that tools tied to North Korea’s Lazarus Group appear to be shared with the Gunra ransomware operation targeting South Korean organizations. The campaign used compromised legitimate websites (watering-hole attacks) and spearphishing emails, including messages…

July 30, 2026
Teams HR Phish Used Real Microsoft Login Flow

Teams HR Phish Used Real Microsoft Login Flow

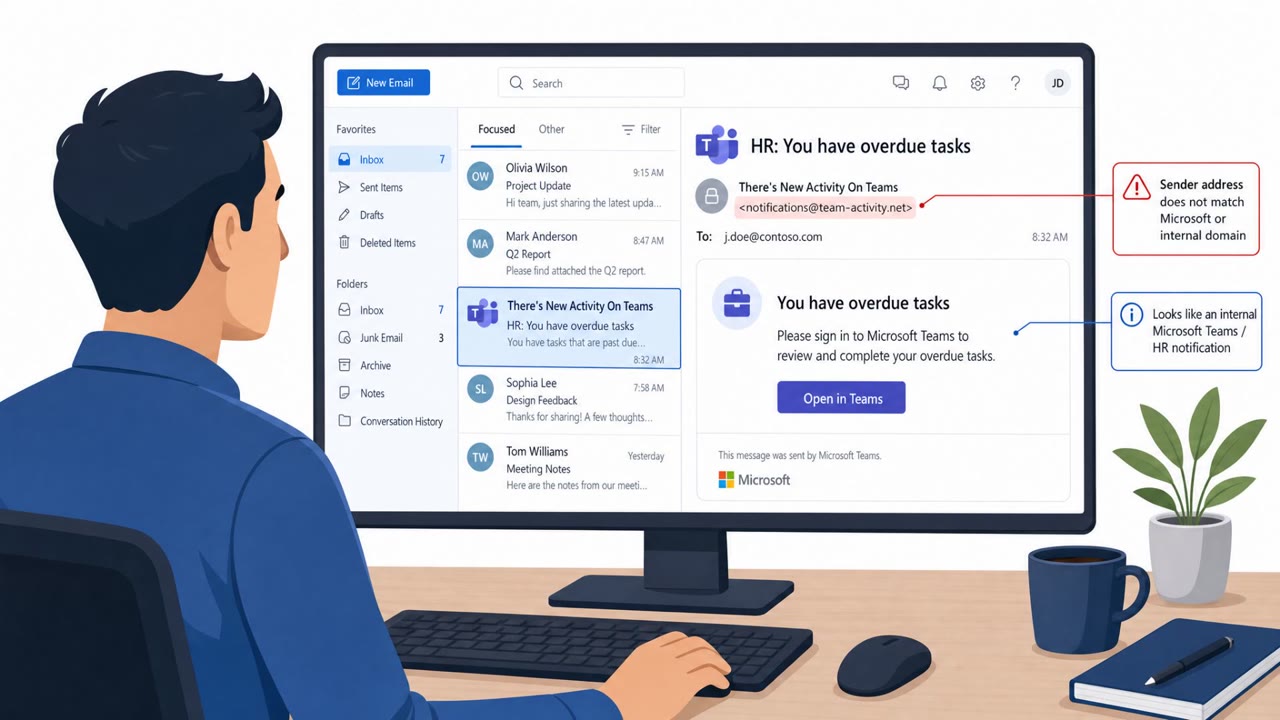
Attackers sent emails that looked like Microsoft Teams/HR notifications and pushed users through Microsoft’s real sign-in and OAuth consent screens. When victims approved the requested permissions, the attackers obtained an authorization token and could access Microsoft 365 data like Outlook,…

July 30, 2026
Fake Resumes + Watering Holes Hit AnySign4PC Users

Fake Resumes + Watering Holes Hit AnySign4PC Users

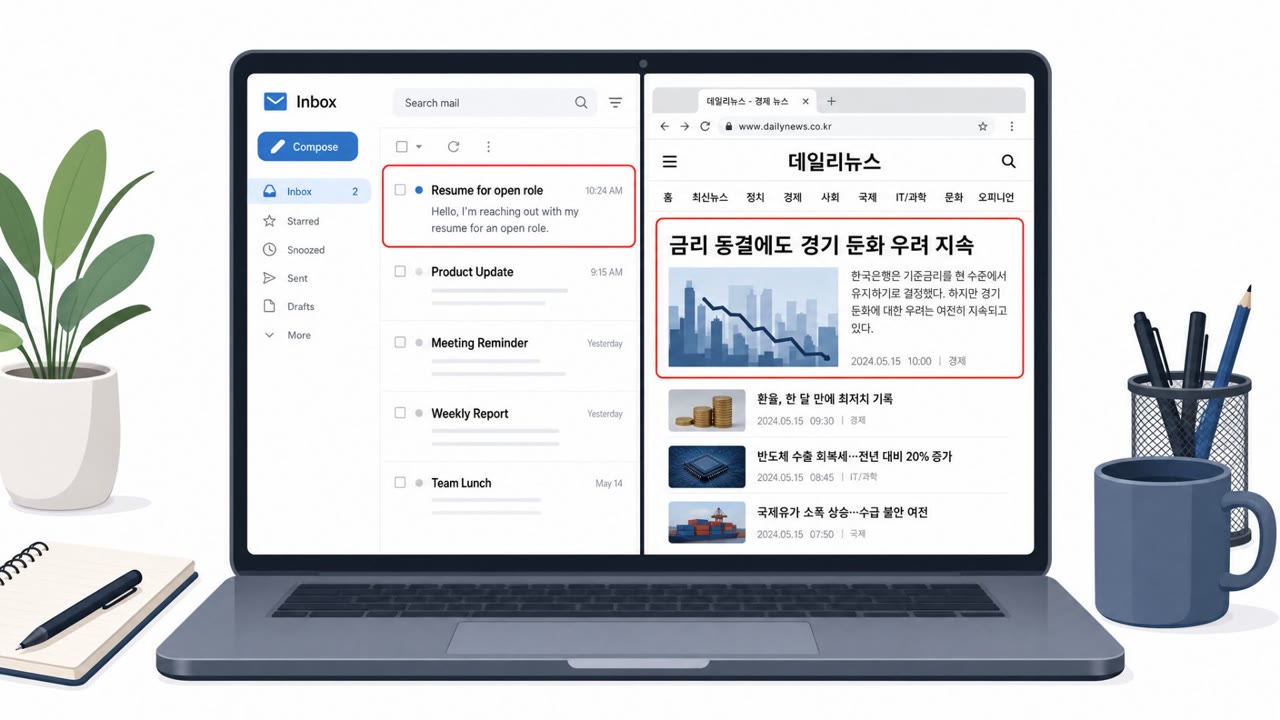
A state-sponsored campaign in South Korea used spear-phishing and hacked “trusted” local websites to infect visitors who had vulnerable AnySign4PC installed. In some cases, simply visiting a compromised page triggered the exploit and installed SIGNBT or COPPERHEDGE backdoors without any download…

July 30, 2026
Invoice Phish Drops ValleyRAT via BYOVD Drivers

Invoice Phish Drops ValleyRAT via BYOVD Drivers

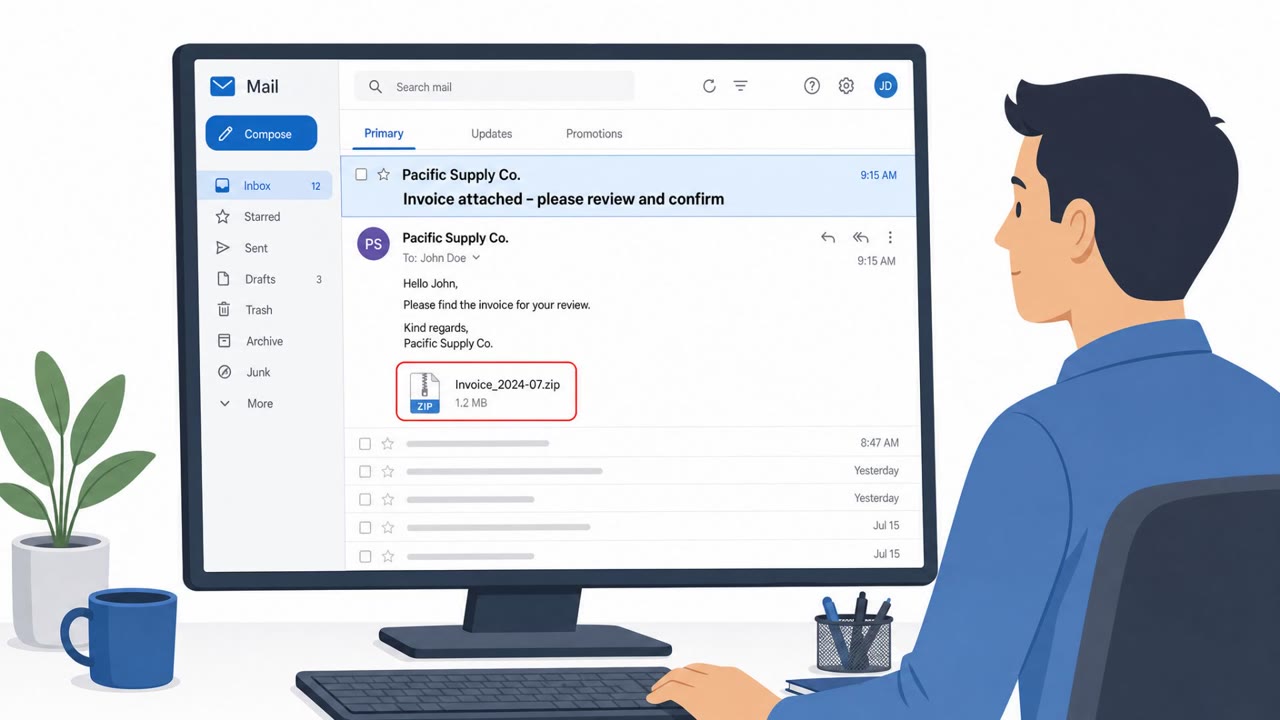
Researchers reported a real campaign by the China-based Silver Fox group against a Japanese industrial manufacturer. The attack starts with an invoice-themed phishing message that leads victims to open a ZIP file, triggering a DLL sideloading chain and installing ValleyRAT for persistent remote…

July 30, 2026
“Half-Click” OWA Email Trap Spreads

“Half-Click” OWA Email Trap Spreads

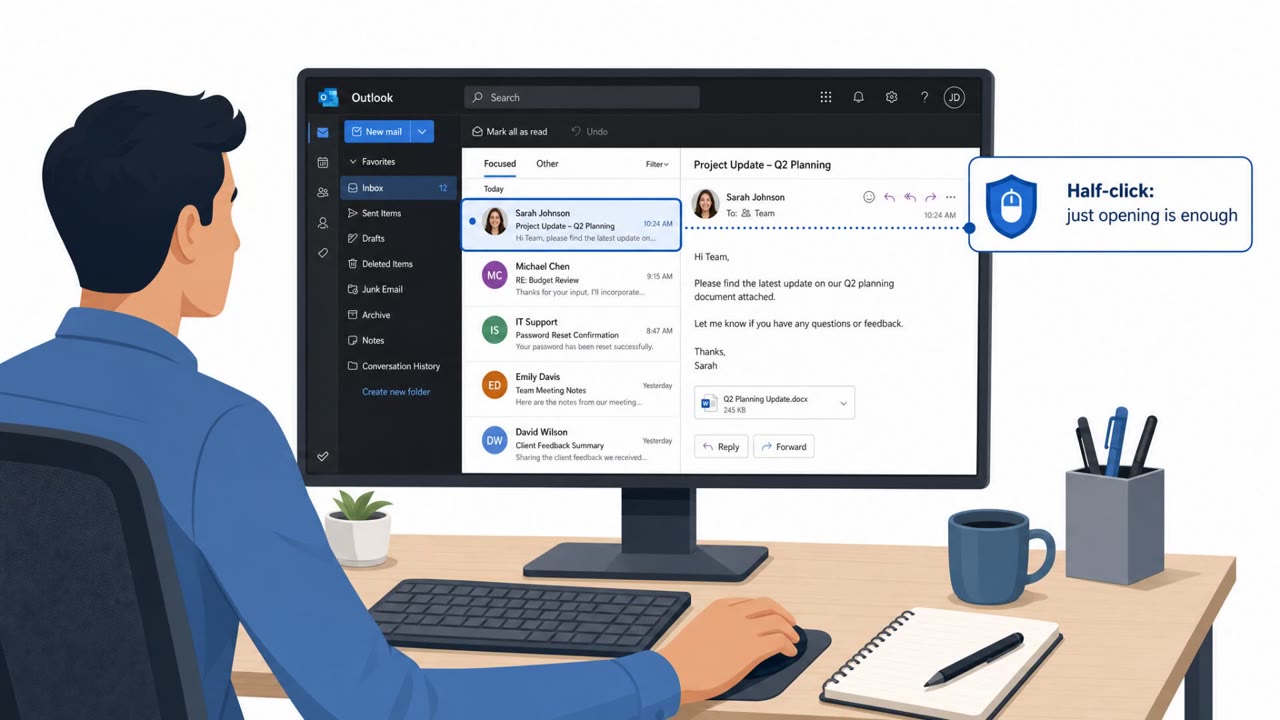
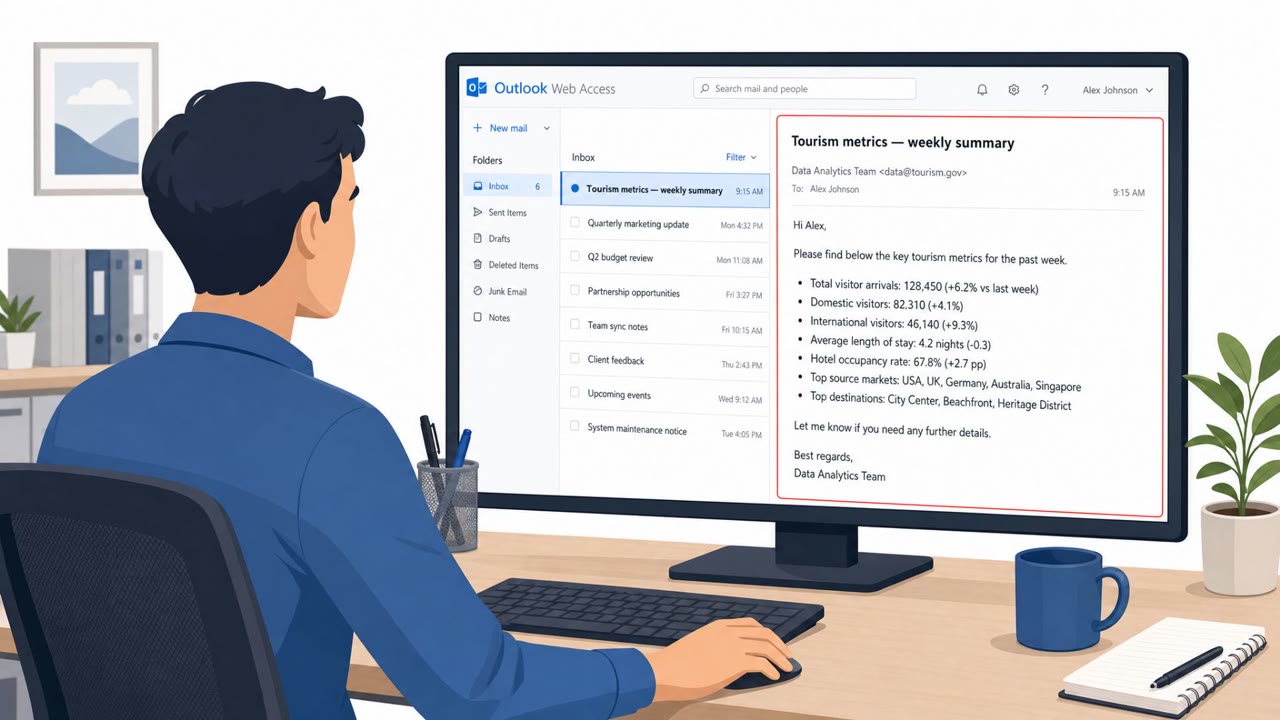
Proofpoint reports a Russian-linked espionage group is using booby-trapped emails that infect users simply when they open the message in Outlook Web Access (OWA) on on‑premises Exchange. The attack runs malicious JavaScript inside the victim’s logged-in mail session and installs a stealthy…

July 30, 2026
Half-Click OWA Emails Trigger Stealth Mailbox Takeover

Half-Click OWA Emails Trigger Stealth Mailbox Takeover

A Russia-aligned group (TA488) sent specially crafted emails that triggered malicious JavaScript simply by being viewed in Outlook Web Access (no link click or attachment needed). The implant (“OWAReaper”) can quietly change server-side mailbox permissions and abuse OAuth tokens, so attackers can…

July 30, 2026
“No-Action” Emails Trigger OWA Mailbox Takeover

“No-Action” Emails Trigger OWA Mailbox Takeover

Russian-linked threat actors sent generic-looking informational emails that required no clicking, but simply opening them in vulnerable Outlook Web Access (OWA) could trigger a hidden exploit. The campaign targeted government and multiple industries, then installed a stealthy browser-based implant…

July 30, 2026
Laundry Bear Uses “Half-Click” OWA Email Exploit

Laundry Bear Uses “Half-Click” OWA Email Exploit

UK and US cyber authorities and Proofpoint reported a real campaign where the Russian-linked group “Laundry Bear” (TA488) sent emails that could infect victims simply by being opened in Outlook Web Access. The email’s HTML triggers the server to run attacker code, installing a mailbox-stealing…

July 29, 2026
TA488 Uses “Half-Click” OWA Emails to Persist

TA488 Uses “Half-Click” OWA Emails to Persist

Proofpoint reports a Russia-aligned espionage group (TA488) returned with a campaign that compromises on‑premises Outlook Web Access simply when a user opens an email in the reading pane. The attack uses a cross-site scripting flaw to run hidden JavaScript, install a browser-resident implant, and…

July 29, 2026
Clone Websites Trick Firms Into Paying Fake Invoices

Clone Websites Trick Firms Into Paying Fake Invoices

Researchers described a long-running fraud campaign where criminals clone real Russian company websites and replace contact and bank details to intercept international business deals. Victims are lured through cold calls, phishing emails, and fake supplier websites, then sent realistic contracts…

July 29, 2026
Fake IT Support Calls in Teams Lead to Ransomware

Fake IT Support Calls in Teams Lead to Ransomware

Sophos reports a real Microsoft Teams voice-phishing campaign where attackers pretended to be IT support to convince employees to start remote-access sessions. After gaining access, the attackers ran commands to download malware and in several cases deployed Chaos ransomware within hours. The…

July 29, 2026
QR-PDF Phishing Hits M365, MFA Bypass Surges

QR-PDF Phishing Hits M365, MFA Bypass Surges

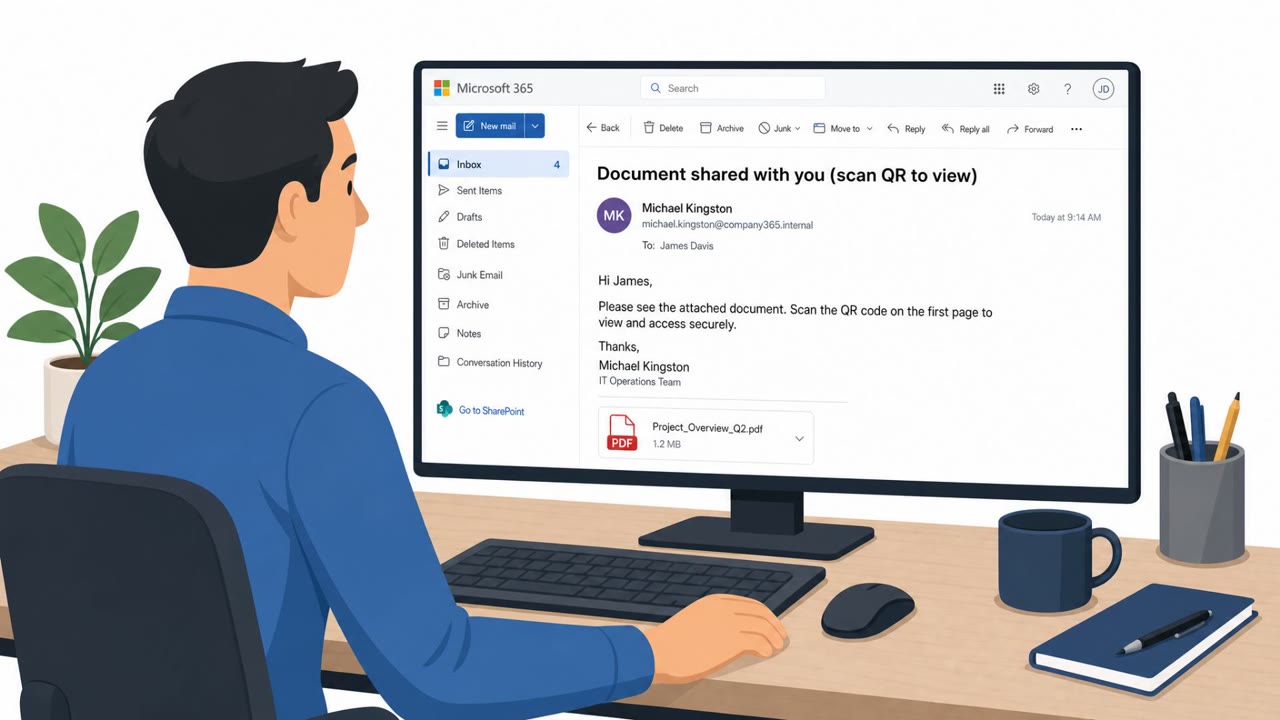
Cisco Talos Incident Response reports that phishing drove initial access in over half of Q2 2026 cases, often using QR codes in PDF attachments and trusted cloud hosting to evade email defenses. Attackers frequently bypassed multi-factor authentication using adversary-in-the-middle proxies,…

July 28, 2026
Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Mirage Kitten Uses Fake Hiring Lures to Drop Malware

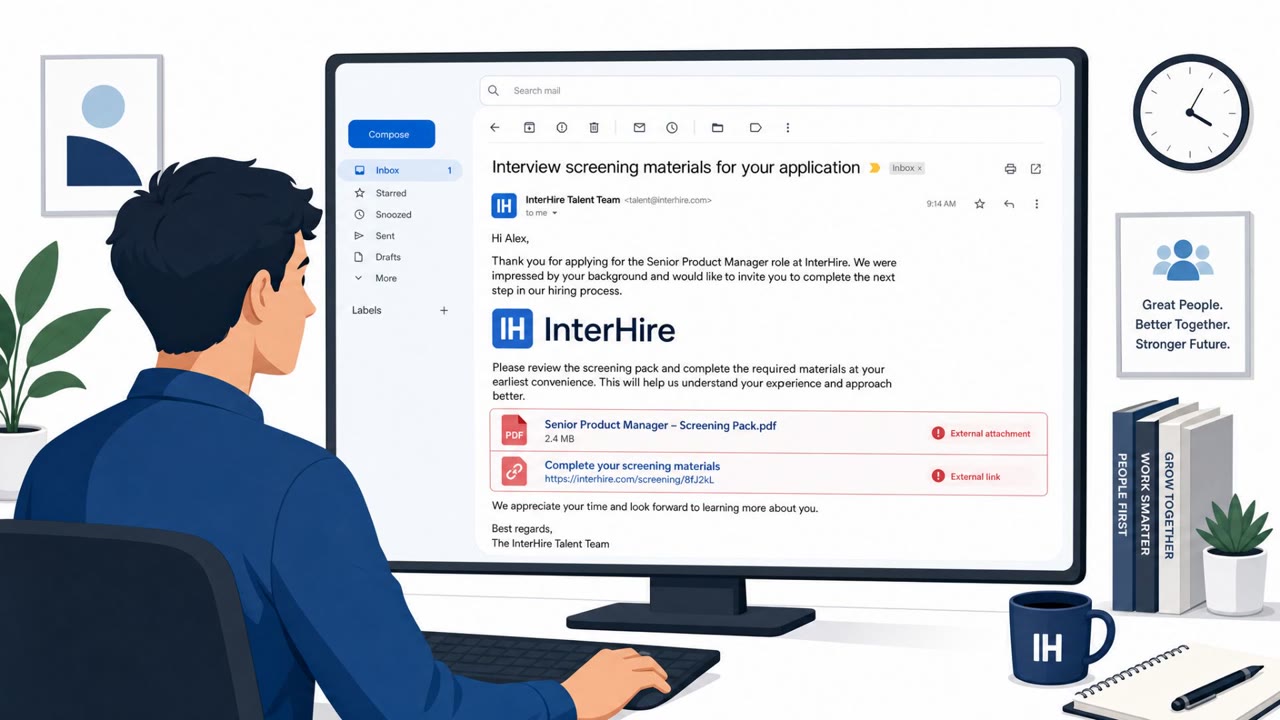
Researchers report Mirage Kitten (an espionage-focused threat group) targeted organizations in the Middle East and Africa using highly tailored spear‑phishing. The lures included recruitment-themed messages impersonating trusted brands/hiring sites and fake videoconferencing pages that redirected…

July 28, 2026
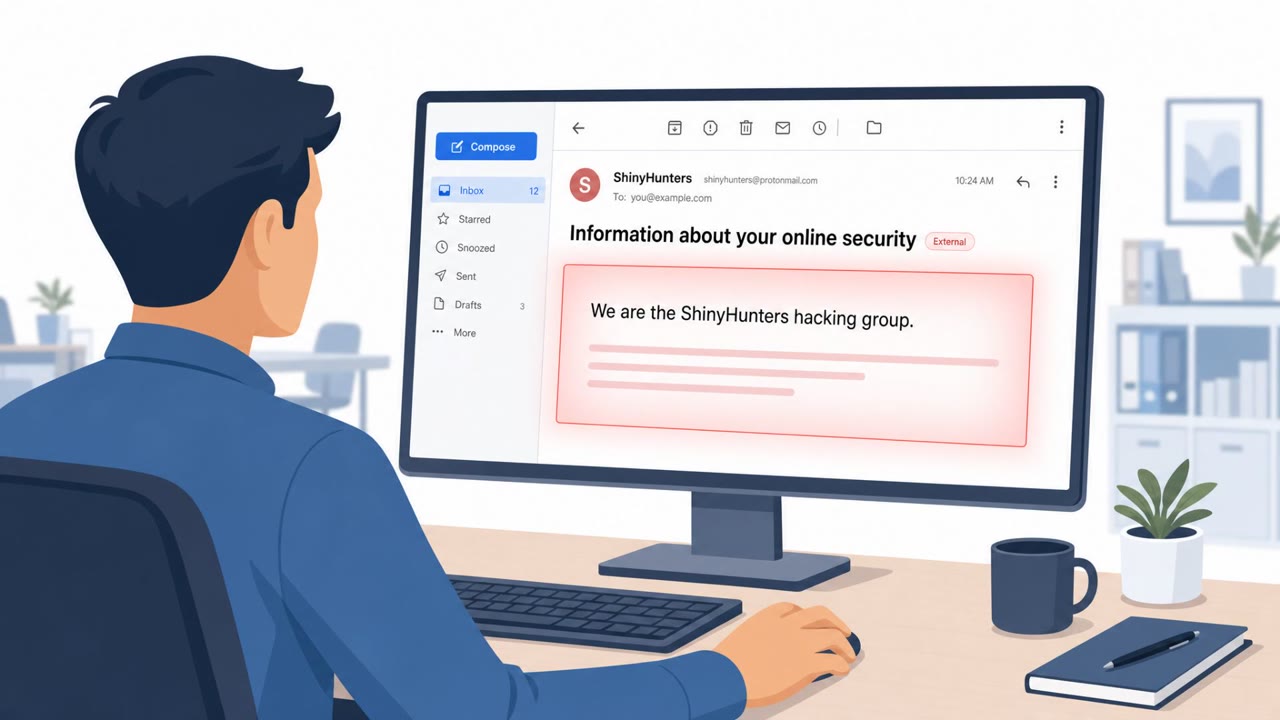
Fake ShinyHunters Sextortion Demands $2,000

Fake ShinyHunters Sextortion Demands $2,000

A sextortion email campaign is using real leaked email addresses from ShinyHunters-related data dumps to make threats sound credible. The scammers impersonate the “ShinyHunters hacking group,” claim they recorded victims via webcam, and demand $2,000 in Bitcoin within 48 hours. Reporting indicates…

July 27, 2026
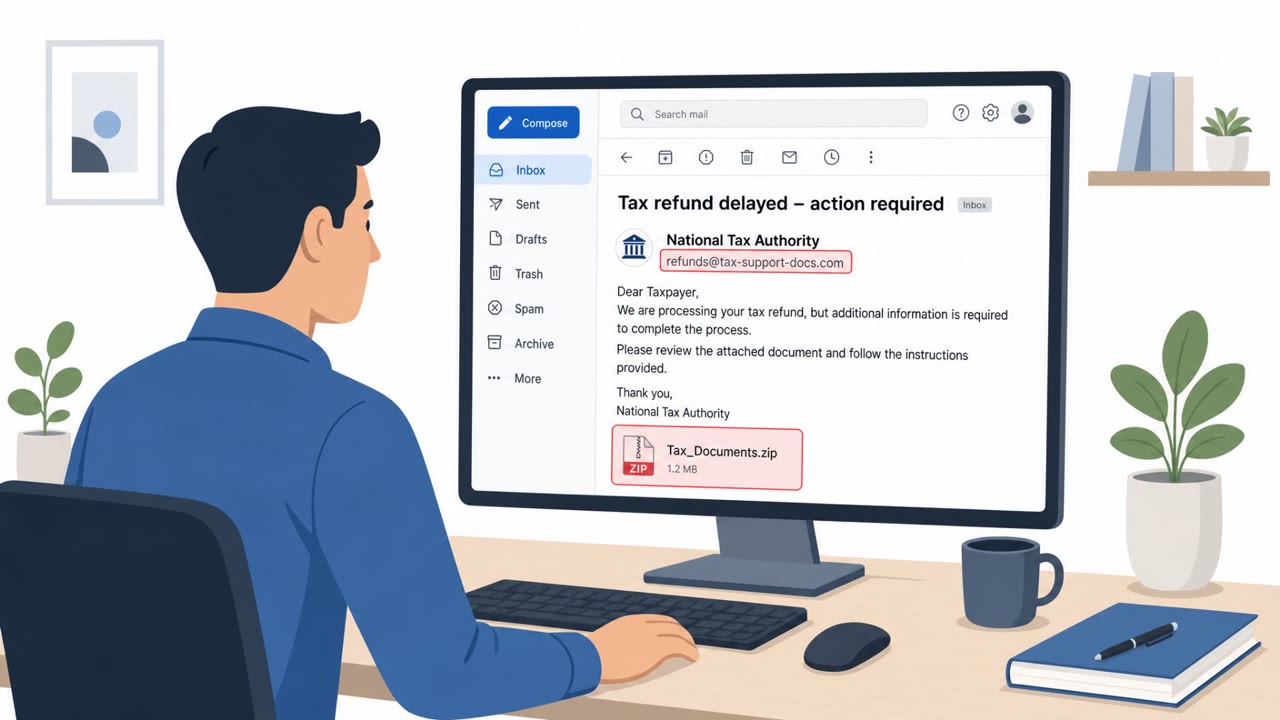
Tax and SSA Phish Push Cruciferra Malware Loader

Tax and SSA Phish Push Cruciferra Malware Loader

Researchers report multiple real-world email phishing campaigns that used tax and government-benefit themes to trick people into downloading malware. The campaigns used a “crypter” service called Cruciferra to hide malicious files and help malware run while avoiding detection. Targets included…

July 27, 2026
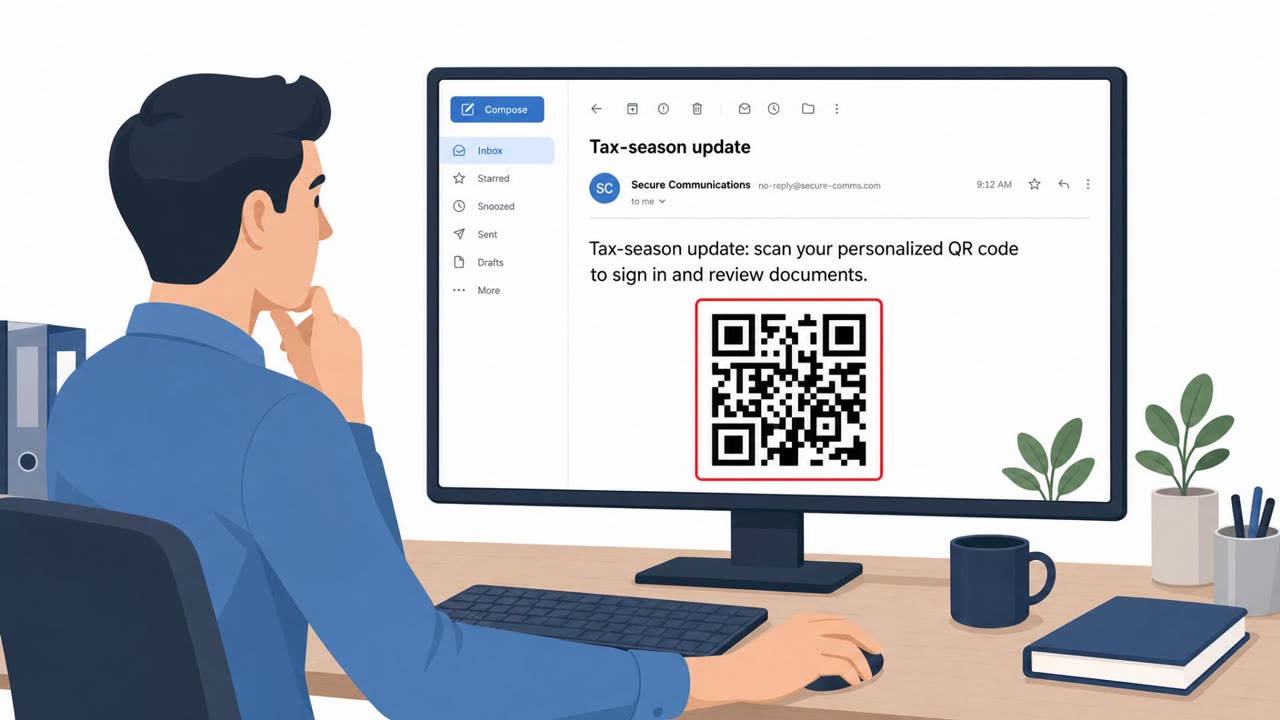
Kratos PhaaS Fueled MFA-Bypass Phishing

Kratos PhaaS Fueled MFA-Bypass Phishing

Authorities dismantled “Kratos,” a phishing-as-a-service platform used at scale to steal Microsoft account credentials and even bypass MFA by stealing session cookies. The article also describes a real campaign using tax-season lures and personalized QR codes to trick users into visiting fake…

July 24, 2026
Zimbra Email View Triggers Russian Data Theft

Zimbra Email View Triggers Russian Data Theft

Government agencies say a Russian-linked group sent specially crafted HTML emails that exploit a Zimbra webmail flaw, so simply viewing the message can trigger data theft, no click required. The campaign has targeted multiple Western sectors since July 2025 and focuses on stealing email content and…

July 23, 2026
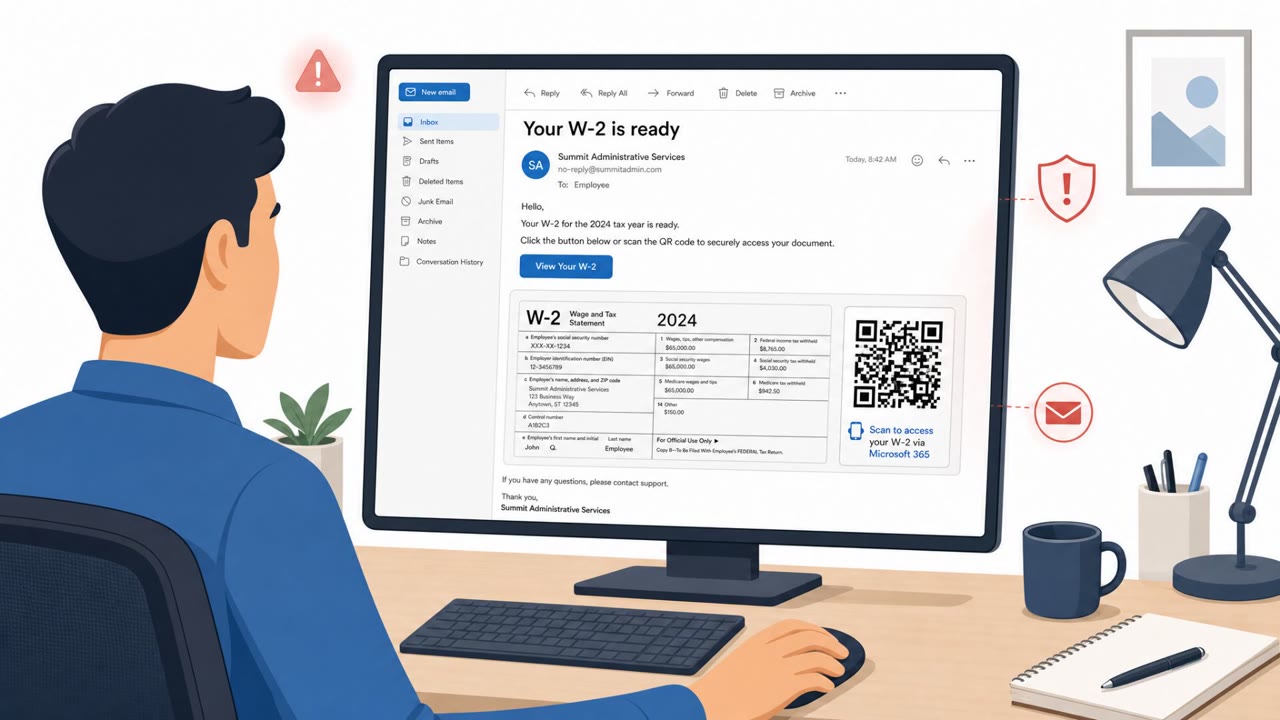
Kratos Kit Used W-2 QR Phish to Hijack M365

Kratos Kit Used W-2 QR Phish to Hijack M365

Law enforcement dismantled the infrastructure behind Kratos, a widely used phishing kit that helped criminals steal Microsoft 365 credentials and, in some cases, capture session cookies to bypass MFA. The article describes a real, observed campaign using tax-themed W-2 QR-code emails that led…

July 22, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo