Threat Watcher

Page 17 of 51
Iran-Linked Spyware Posed as Apps on WhatsApp

Iran-Linked Spyware Posed as Apps on WhatsApp

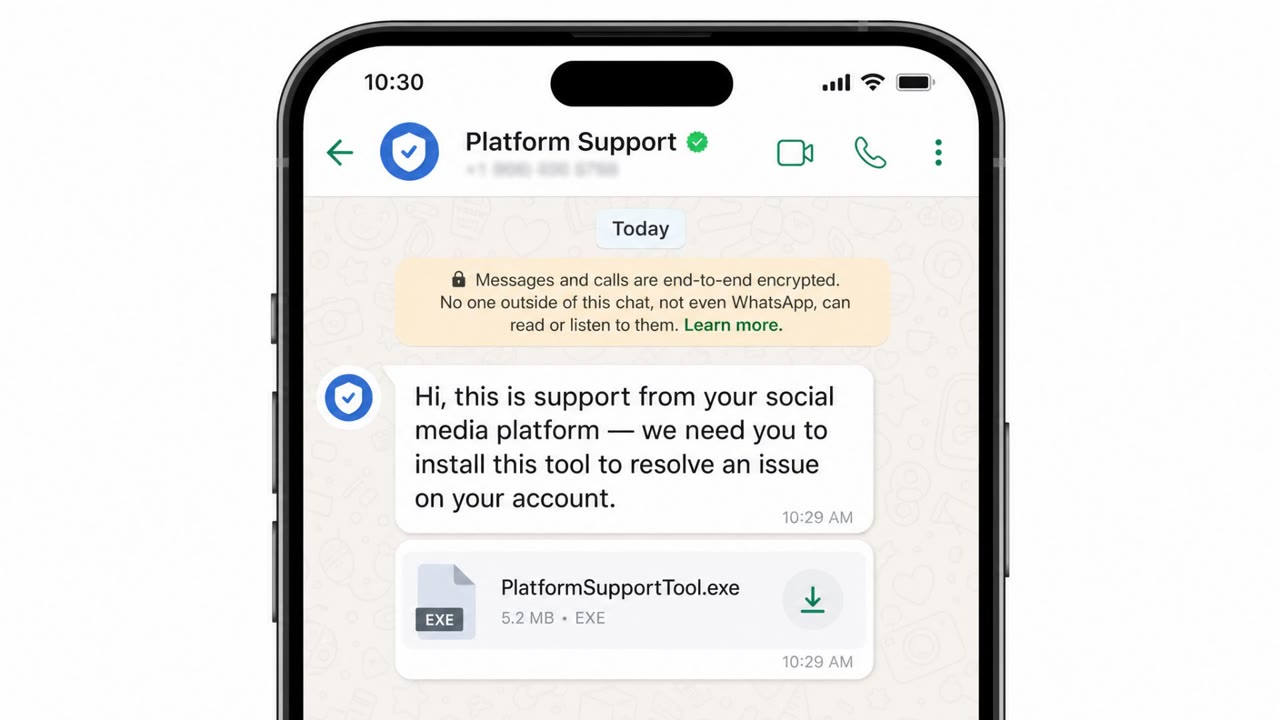
UK, US and Dutch authorities warned that Iran-linked attackers are targeting dissidents, activists, and journalists with Windows spyware. The group builds trust over messaging apps, then tricks victims into downloading malware disguised as legitimate software (or even medical files). The spyware…

September 15, 2026
Fake MRI File Used to Deliver Iran Spyware

Fake MRI File Used to Deliver Iran Spyware

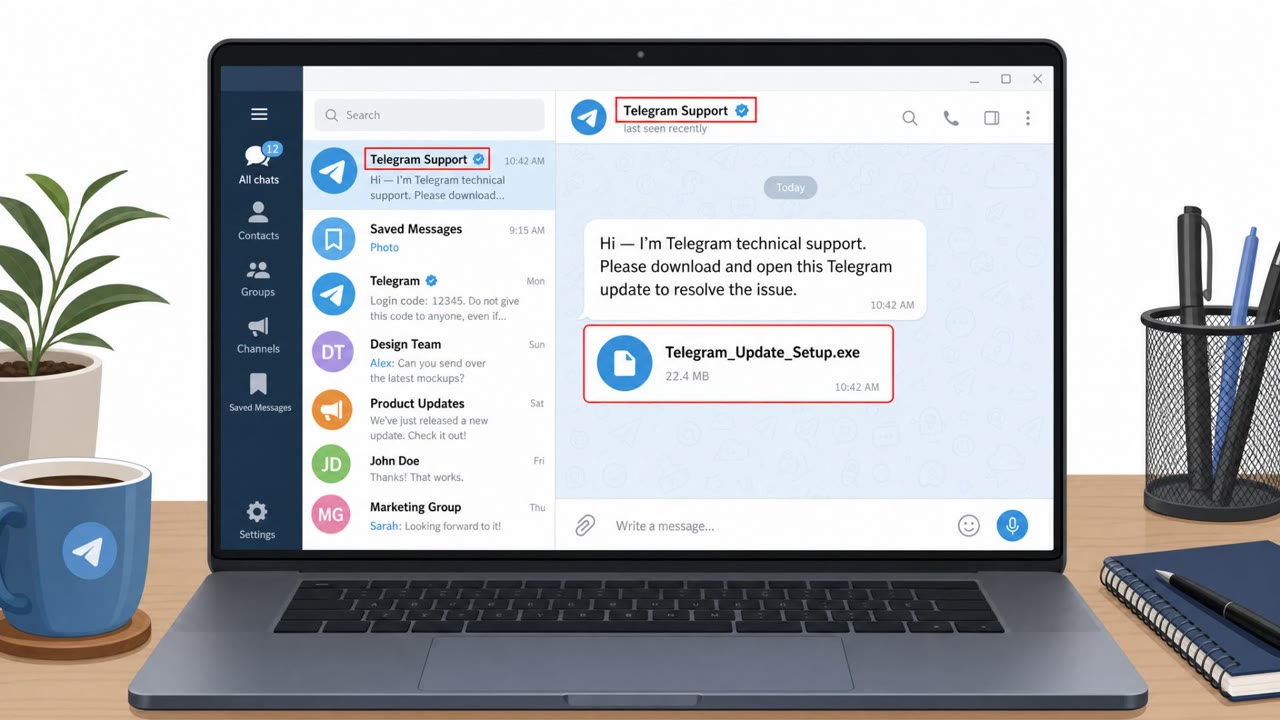
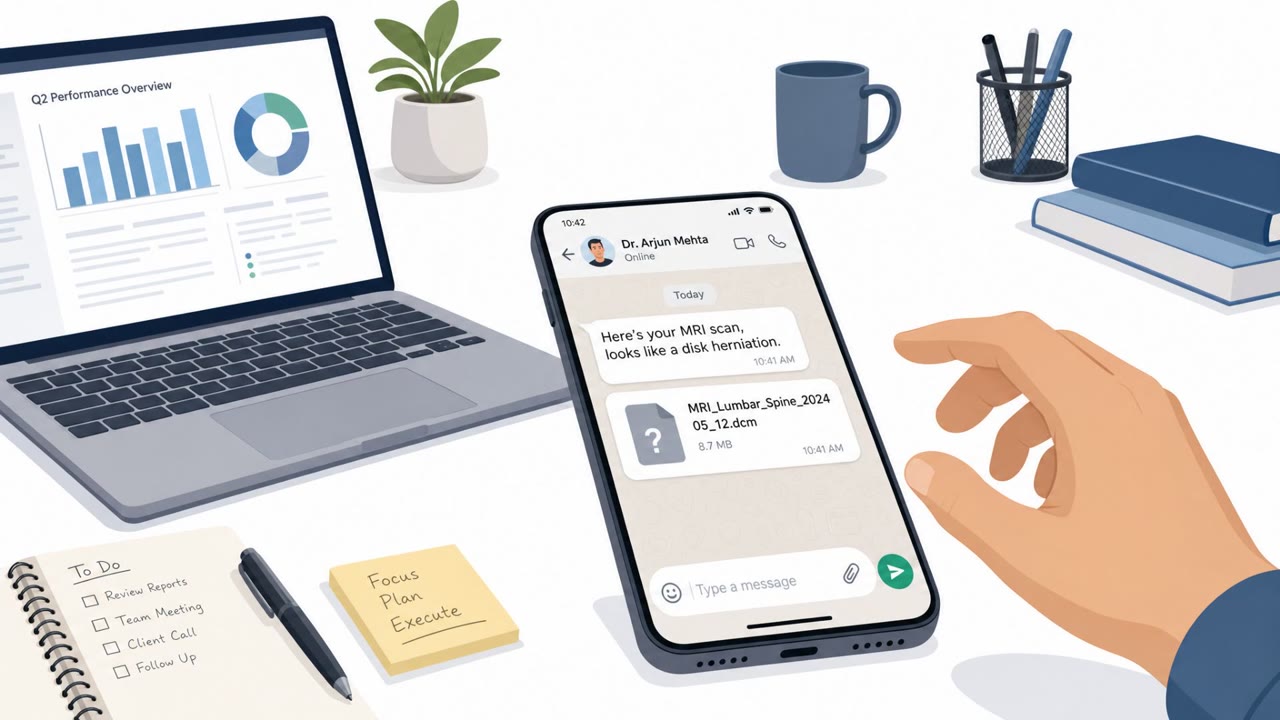
UK, US, and Dutch agencies warned that Iran-linked operators used long-running social engineering to build trust with targets (including dissidents, activists, and journalists), then sent malicious files disguised as legitimate documents or software installers. One lure included a fake MRI scan…

September 15, 2026
AI “Agents” Flood Inboxes With Spam Pitches

AI “Agents” Flood Inboxes With Spam Pitches

The article describes real-world examples of unsolicited emails that claim to be sent by “AI agents,” pitching services, interviews, coverage, and paid work. It includes specific subject lines and message excerpts that show a repeatable workflow: automated outreach that tries to prompt recipients…

September 15, 2026
Iran-Linked Spyware Lures Targets via WhatsApp

Iran-Linked Spyware Lures Targets via WhatsApp

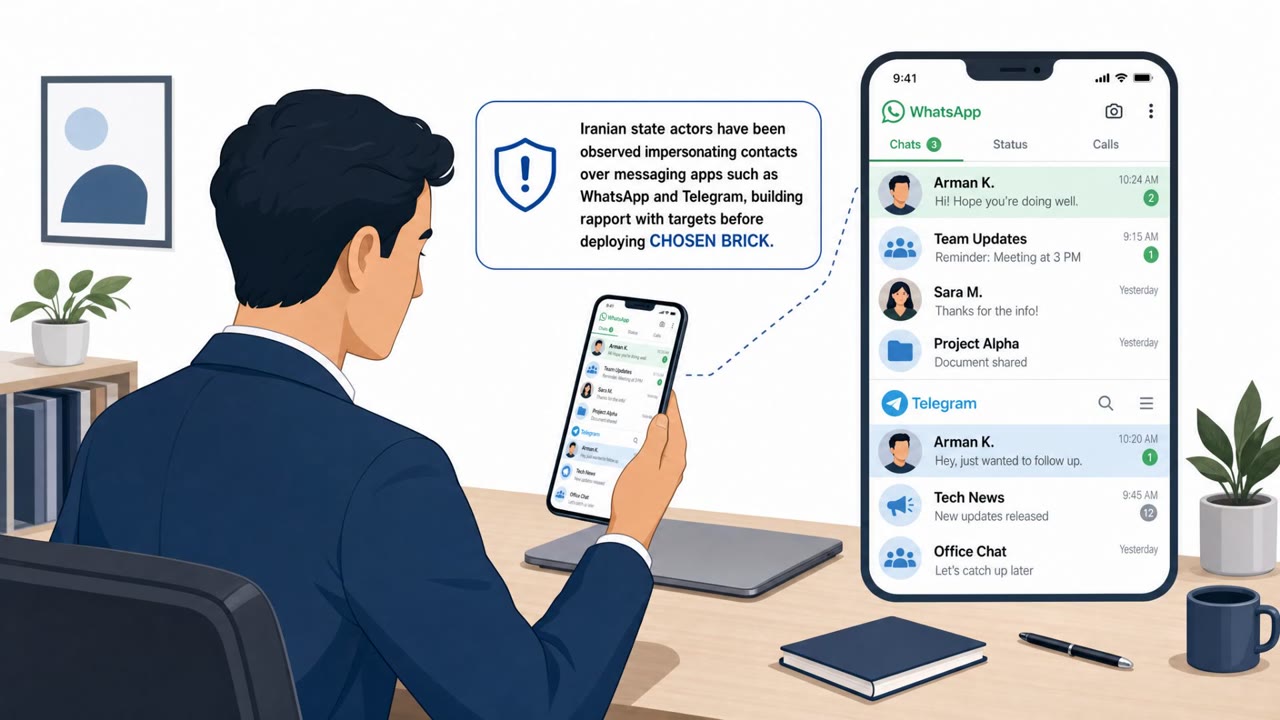
UK cyber authorities and international partners warned that Iranian state cyber actors have been tricking dissidents, activists, and journalists into installing spyware called CHOSEN BRICK. The campaign uses impersonation over messaging apps (such as WhatsApp and Telegram), rapport-building, and…

September 15, 2026
Iranian Actors Lure Targets via Telegram/WhatsApp

Iranian Actors Lure Targets via Telegram/WhatsApp

UK, US, and Dutch authorities reported Iranian state-linked cyber actors using social messaging apps like Telegram and WhatsApp to build trust with dissidents, activists, and journalists. The actors then convince targets to open “legitimate-looking” files (fake apps or documents like MRI results)…

September 15, 2026
Black Axe Romance Scam Scripts Exposed

Black Axe Romance Scam Scripts Exposed

US prosecutors say alleged Black Axe leaders ran long-running romance scams that used social media and dating sites to build trust with victims, then demanded money using a consistent “working in South Africa” story. When victims hesitated, the group allegedly threatened to leak sensitive photos to…

September 15, 2026
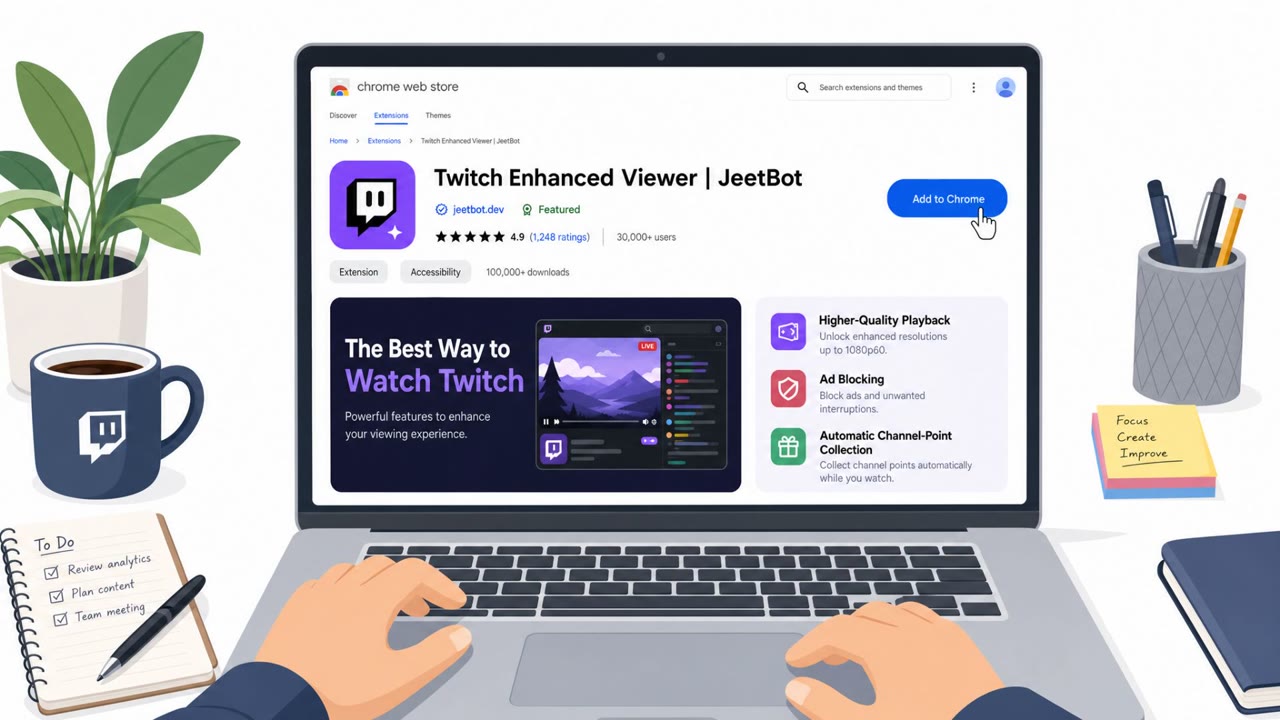
Twitch Extension Exposed OAuth Tokens to Developer

Twitch Extension Exposed OAuth Tokens to Developer

Researchers reported that a popular Twitch browser extension sent users’ Twitch OAuth login tokens to proxy servers controlled by the extension’s developer. If a token was exposed, someone receiving it could potentially act as the account holder without needing the user’s password. The key user…

September 15, 2026
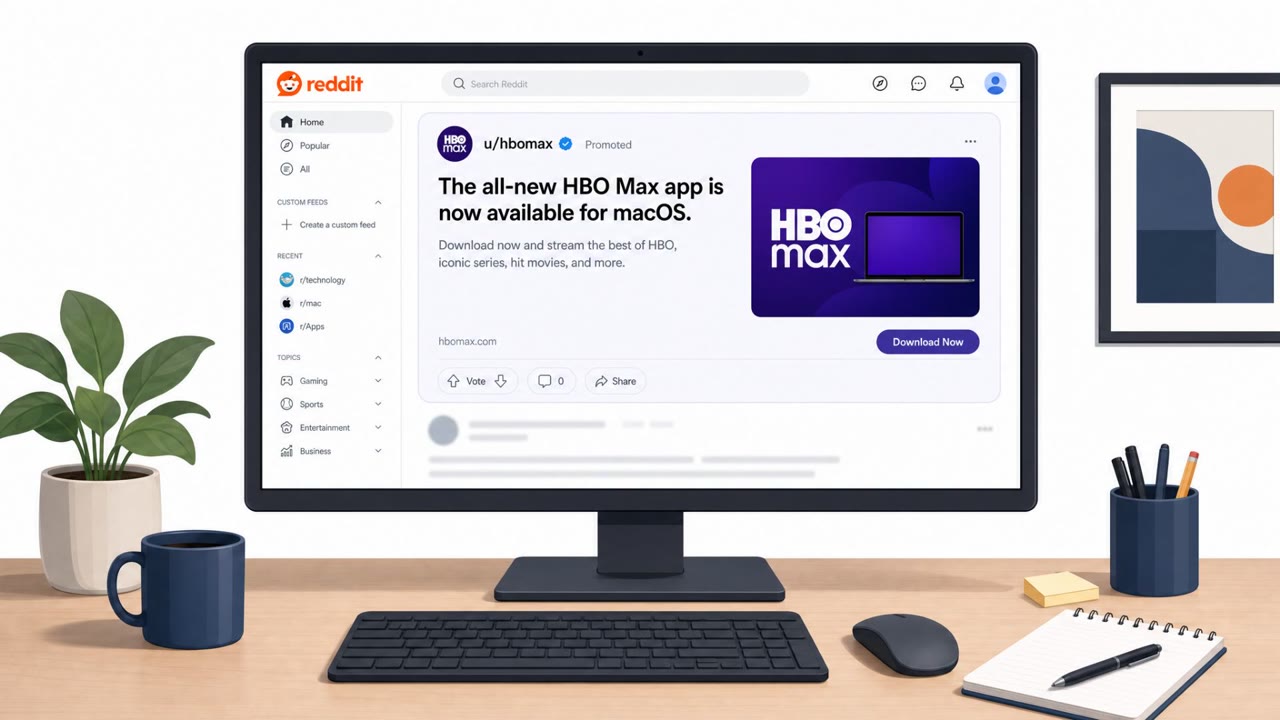
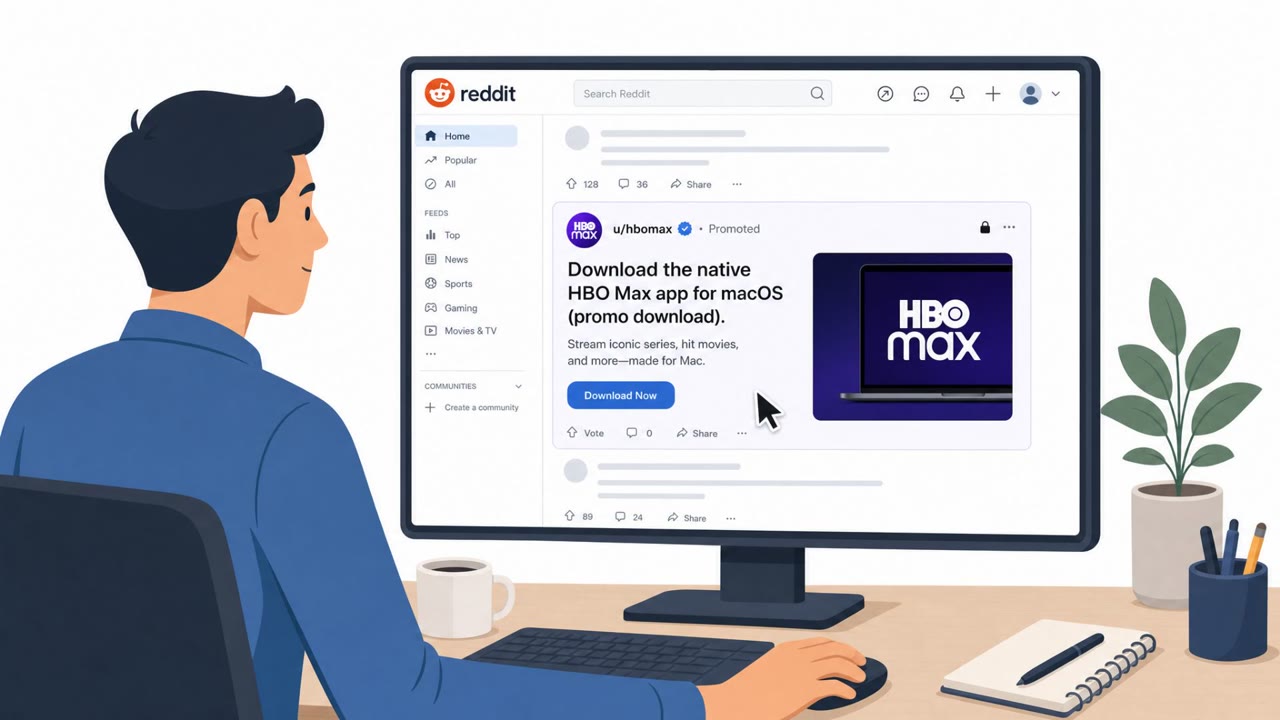
HBO Max Reddit Account Hijacked for ClickFix Malware Ads

HBO Max Reddit Account Hijacked for ClickFix Malware Ads

Attackers took over the verified official HBO Max Reddit account and used it to run a 48-hour wave of malicious ads. The ads sent people to lookalike download sites that tricked them into copying and running commands, leading to information-stealing malware on both macOS and Windows. Researchers…

September 15, 2026
Hijacked HBO Max Reddit Ads Push ClickFix Malware

Hijacked HBO Max Reddit Ads Push ClickFix Malware

Researchers reported that criminals hijacked HBO Max’s verified Reddit account and used it to run malicious ads that led people to fake download sites. The sites didn’t provide real installers, instead they tricked users into pasting and running commands in Terminal/PowerShell, causing them to…

September 15, 2026
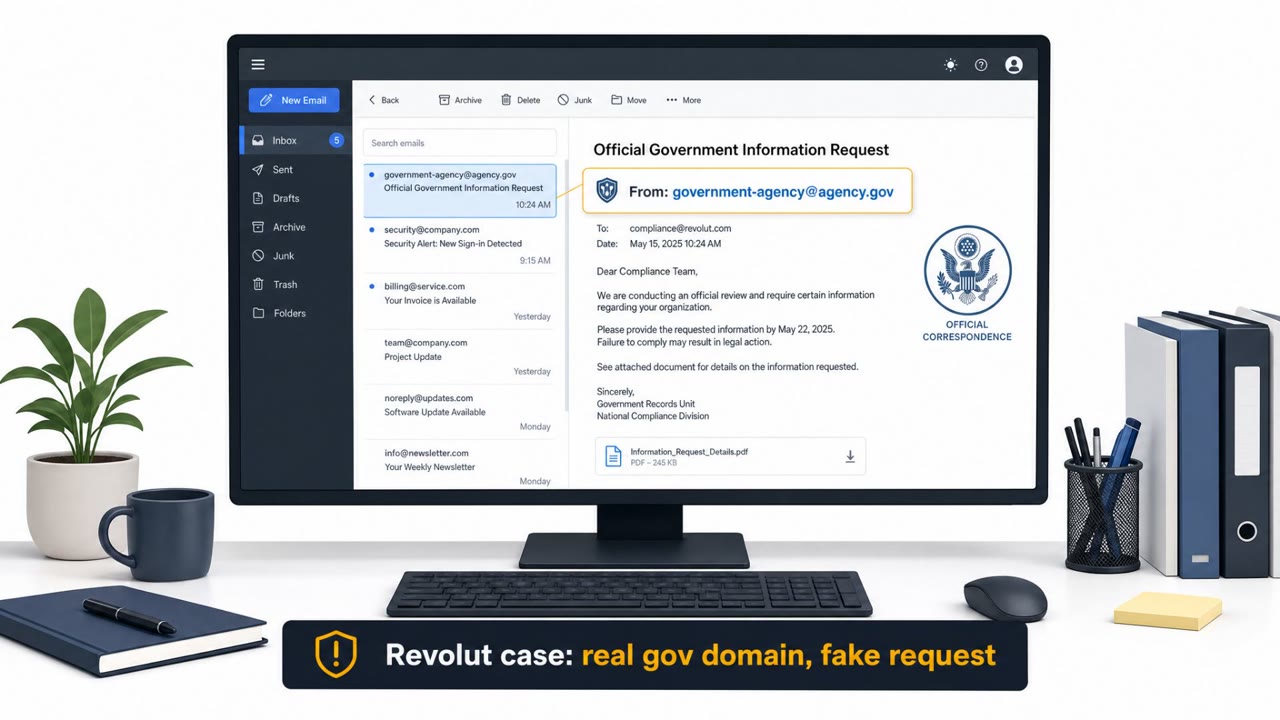
Revolut Fooled by Fake Government Data Requests

Revolut Fooled by Fake Government Data Requests

Revolut says it disclosed sensitive customer information after receiving fraudulent information requests that appeared to come from a real government agency email domain. The company framed it as a sophisticated impersonation scam, not a technical break-in, showing how “legitimate-looking” requests…

September 15, 2026
NGOs Lured via Donation Form Into Chrome 0-Day Chain

NGOs Lured via Donation Form Into Chrome 0-Day Chain

Researchers reported two China-linked groups targeting NGOs with spear-phishing that led victims through a legitimate U.S. university website before redirecting them to attacker infrastructure. The attackers used a chained Chrome/Windows exploit to take control, then deployed different payloads,…

September 15, 2026
AT&T Insider Aided SIM-Swap Bank Heists

AT&T Insider Aided SIM-Swap Bank Heists

A former AT&T retail employee helped a SIM-swap crew hijack customers’ phone numbers, letting the criminals intercept SMS two-factor codes and reset online banking passwords. The gang then attempted (and in one case succeeded) to wire large sums from victims’ bank accounts, often to accounts in…

September 15, 2026
Fake Bitrefill Sites Steal Crypto via Search Results

Fake Bitrefill Sites Steal Crypto via Search Results

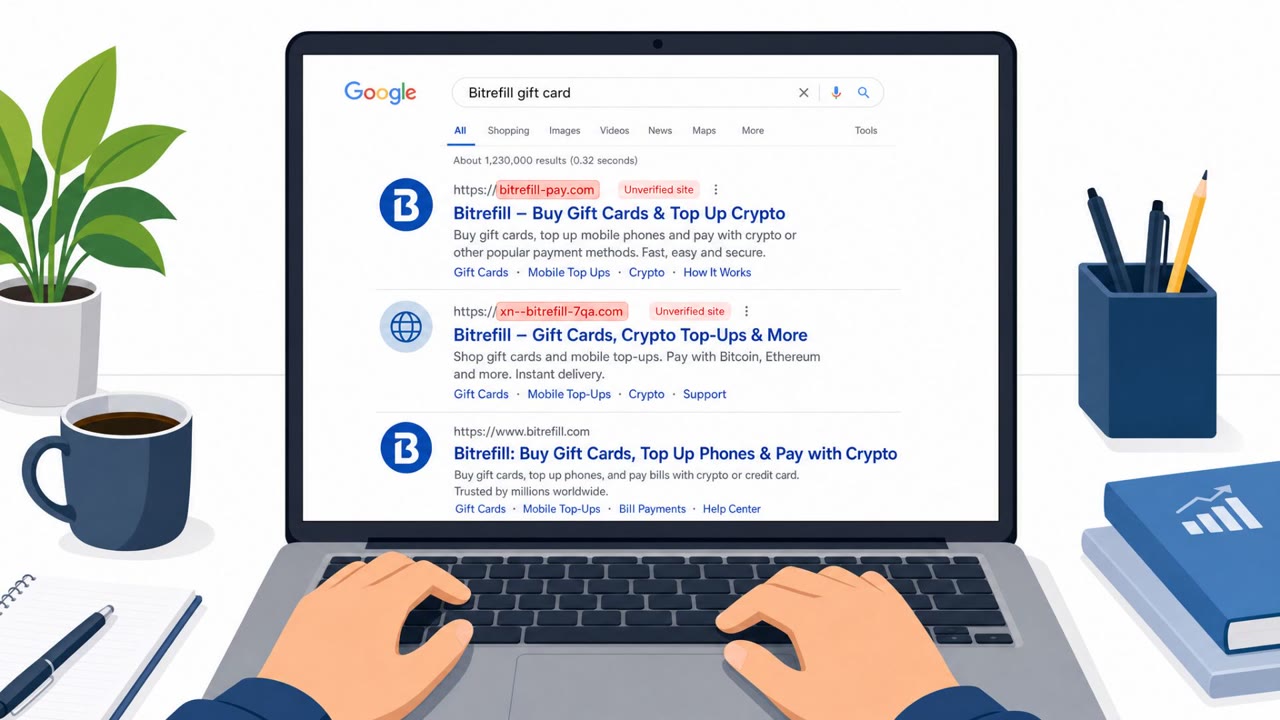
Scammers are using lookalike Bitrefill domains that appear in search results to trick people into buying gift cards or top-ups. The fake sites copy Bitrefill’s branding and checkout flow, then display a QR code and crypto address so victims unknowingly pay the scammers instead of Bitrefill. Because…

September 15, 2026
Spear-Phishing Link Triggers Chrome-Windows Exploit

Spear-Phishing Link Triggers Chrome-Windows Exploit

China-linked attackers targeted NGOs with spear-phishing emails that urged recipients to click a link to a legitimate U.S. university website. The link path abused a website flaw to silently redirect victims to attacker infrastructure, which then exploited Chrome and Windows to install malware…

September 15, 2026
Trezor Users Hit by Phish via Brevo Breach

Trezor Users Hit by Phish via Brevo Breach

Attackers broke into Brevo, the email platform Trezor uses for newsletters, and sent a phishing “security warning” from Trezor’s real mailing system. The email claimed a serious hardware issue could expose wallet recovery seeds and pushed people to a malicious site/app that asked for a wallet…

September 14, 2026
HBO Max Reddit Hijack Pushed ClickFix Malware

HBO Max Reddit Hijack Pushed ClickFix Malware

Attackers took over the verified HBO Max Reddit account and ran over 100 malicious ads that sent people to fake download pages. The pages used a ClickFix-style trick: users were told to copy/paste a command into macOS Terminal (and similar OS-targeted lures) to install information-stealing malware.

September 14, 2026
Passkey-Themed Phishing Hits Microsoft 365

Passkey-Themed Phishing Hits Microsoft 365

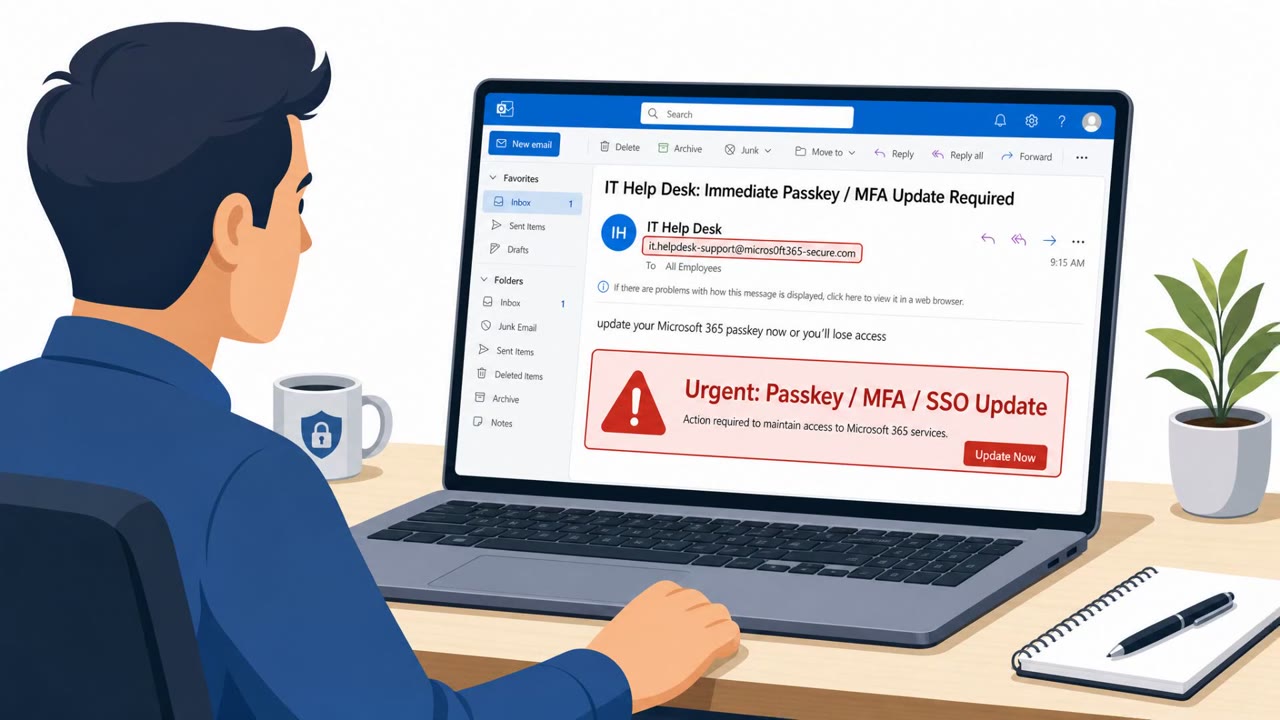
Microsoft warns of an active social engineering campaign where attackers pose as an IT help desk and pressure employees to “update” passkeys/MFA/SSO. Victims are sent to fake Microsoft sign-in pages or tricked into approving access via device-code login, enabling attackers to add their own MFA…

September 14, 2026
Black Axe Romance Scam Leaders Extradited

Black Axe Romance Scam Leaders Extradited

U.S. prosecutors say five alleged leaders of Black Axe’s Cape Town group ran long-running online romance and “advance fee” scams that tricked U.S. victims into sending money. The scammers allegedly used fake identities to pose as love interests or trusted contacts, then pushed for payments using…

September 14, 2026
Fake CAPTCHA Pop-ups Trick Users Into Running Commands

Fake CAPTCHA Pop-ups Trick Users Into Running Commands

Researchers warn that “ClickFix” attacks are spreading on both Windows and Mac by showing fake pop-ups over trusted websites and instructing people to copy/paste and run hidden commands. Attackers are also compromising legitimate websites so the scam appears on pages users already trust, increasing…

September 14, 2026
Fake Gov Sites Lure Central Asia Users for Cash

Fake Gov Sites Lure Central Asia Users for Cash

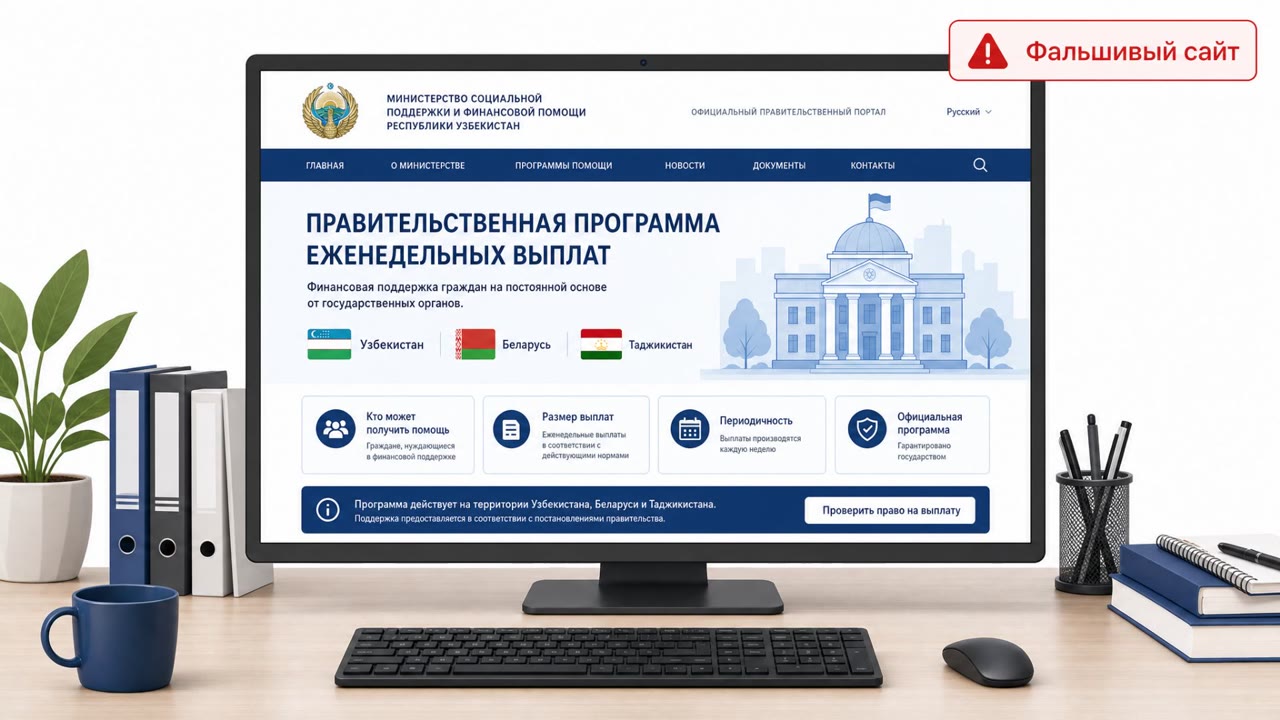
Researchers found a large scam campaign using hundreds of fake government and news websites in Uzbekistan, Belarus, and Tajikistan. The sites lure people with promises of government-backed cash payments or passive income, then collect phone numbers and other personal data for follow-up…

September 14, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo