Threat Watcher

Page 18 of 51
Revolut Hit by Govt-Agency Email Impersonation

Revolut Hit by Govt-Agency Email Impersonation

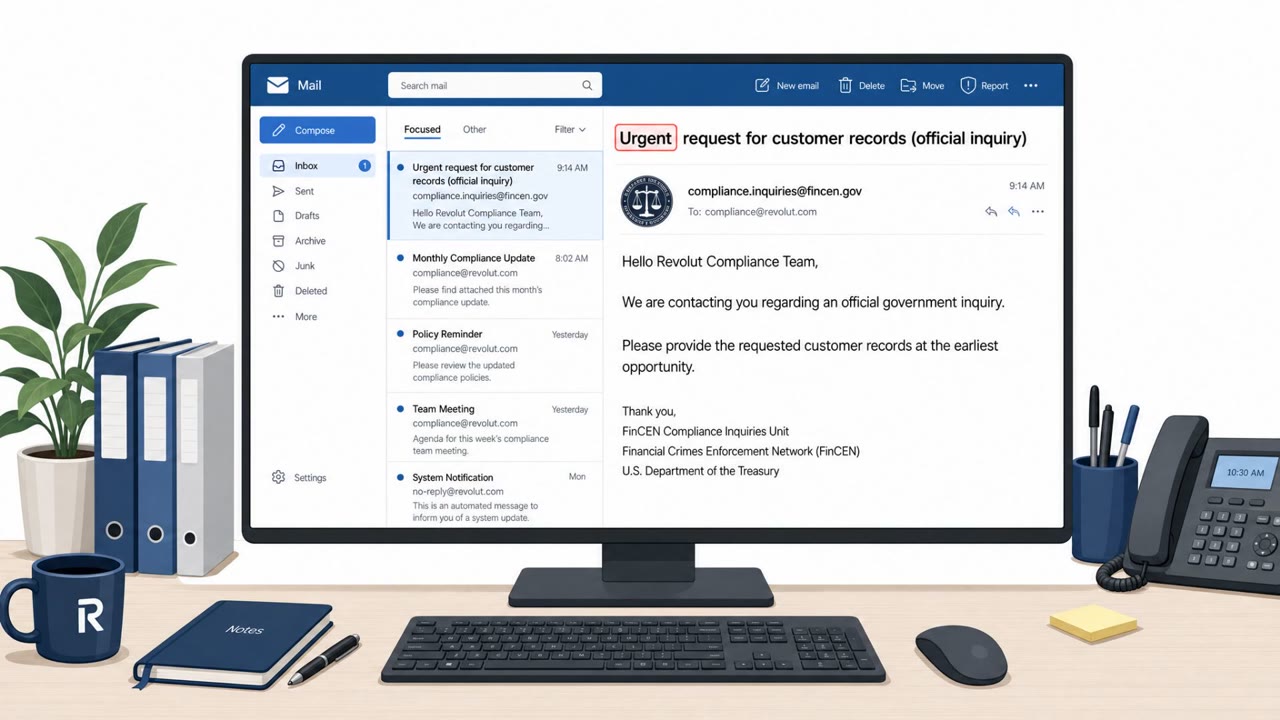
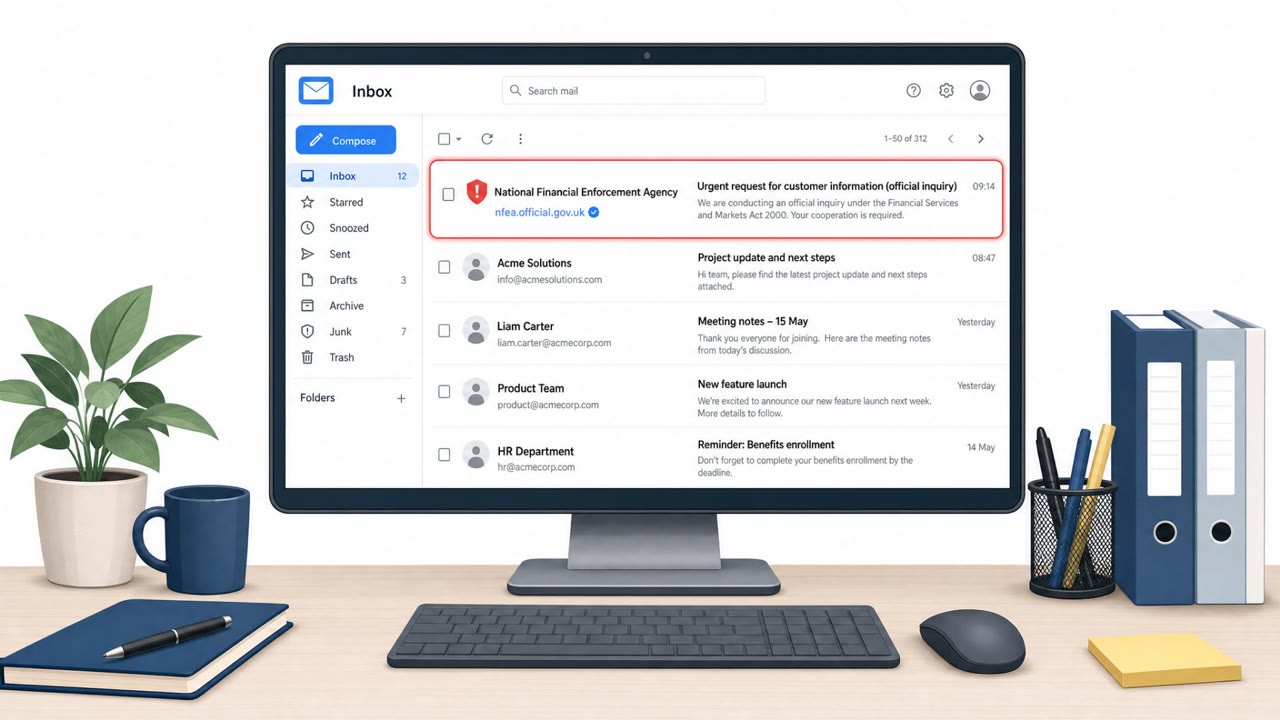
Revolut says a third party posing as a government agency tricked the company into disclosing some customers’ personal and financial data. The attacker used an email address on a legitimate government agency domain, causing the request to be treated as a real legal inquiry. Revolut says customer…

September 14, 2026
Revolut Tricked by Fake “Emergency” Data Requests

Revolut Tricked by Fake “Emergency” Data Requests

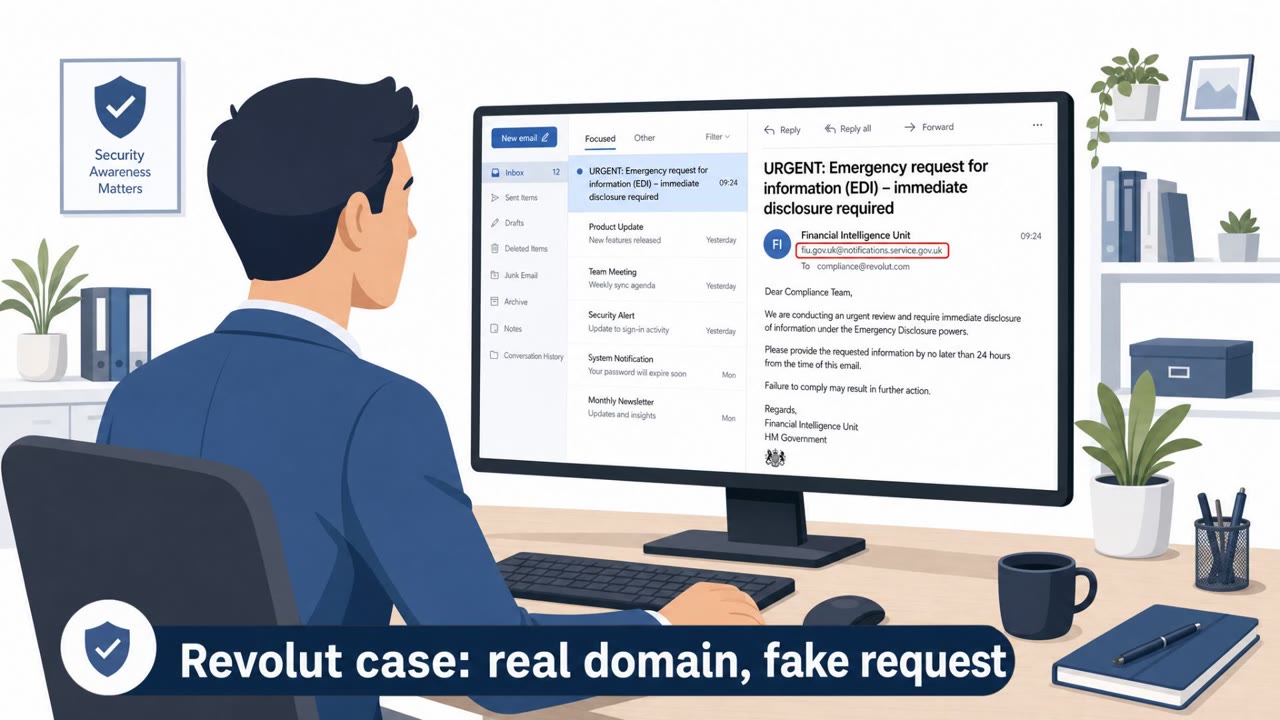
Revolut confirmed it disclosed sensitive customer information after fraudsters sent “emergency” information requests from a legitimate government email domain. The attackers appear to have targeted high-net-worth customers, including people involved in crypto, and attempted to extort Revolut to…

September 14, 2026
Fraudulent Gov Email and Passkey Lures Hit Orgs

Fraudulent Gov Email and Passkey Lures Hit Orgs

The bulletin describes real-world social engineering where staff were tricked into disclosing sensitive data or access. In one case, Revolut employees responded to fraudulent information requests sent from a real government-domain email account, exposing extensive customer records. Separately,…

September 14, 2026
Revolut Fooled by Fake Government Data Requests

Revolut Fooled by Fake Government Data Requests

Revolut confirmed it shared sensitive customer information with an unauthorized party after accepting fraudulent “government” information requests sent from an email address on a legitimate government domain. The company says this was an external impersonation scam (not a system hack) and that…

September 14, 2026
Revolut Tricked by Fake Government Email Requests

Revolut Tricked by Fake Government Email Requests

Revolut confirmed a breach after an attacker impersonated a government agency and sent fraudulent data requests from what appeared to be a legitimate government email domain. Employees processed the requests as normal legal-compliance work, leading to exposure of sensitive customer identity and…

September 14, 2026
Revolut Tricked by Fake Government Email

Revolut Tricked by Fake Government Email

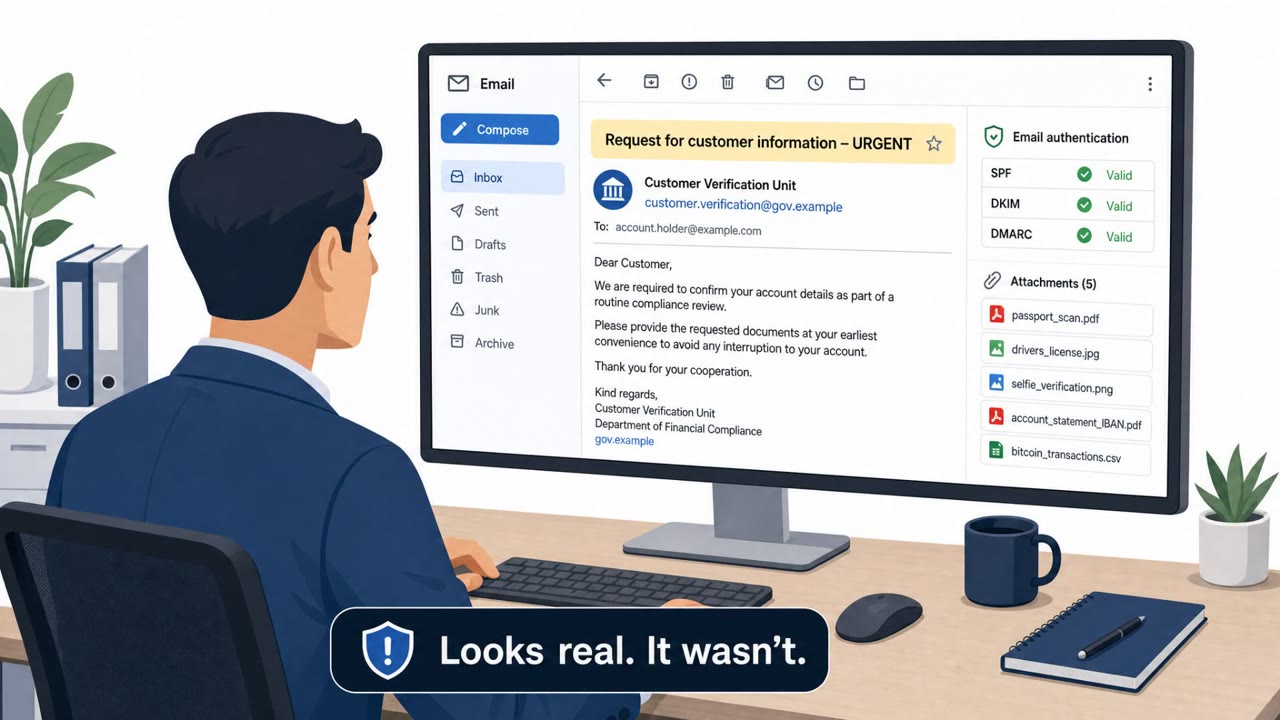
Revolut disclosed it was deceived into sharing highly sensitive customer data after receiving fraudulent information requests that appeared to come from a legitimate government email domain. The attacker’s email passed domain authentication, making it harder to detect, and the shared data may…

September 14, 2026
M365 “Direct Send” Abused for Internal-Looking Phish

M365 “Direct Send” Abused for Internal-Looking Phish

Researchers observed a real phishing campaign that abused Microsoft 365’s Direct Send feature to make emails look like they came from the victim organization’s own domain, without compromising an employee account. The campaign was timed to mimic human sending patterns during U.S. Eastern business…

September 14, 2026
Rogue ScreenConnect Clients Spread Worm-Like Attack

Rogue ScreenConnect Clients Spread Worm-Like Attack

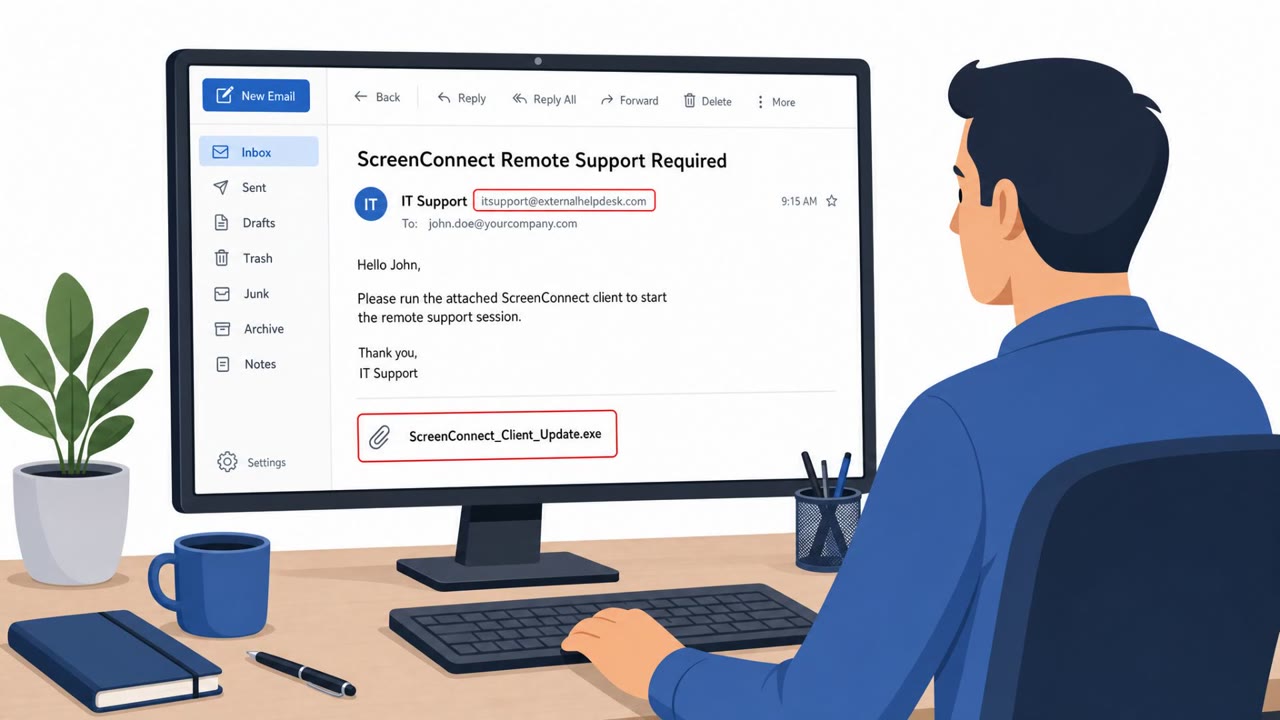
Attackers exploited a critical flaw in ConnectWise ScreenConnect and used social engineering to trick people into running a modified (rogue) ScreenConnect client. Once executed, the rogue client looked for active remote sessions and pushed VBScript files to connected systems to spread further.…

September 14, 2026
Fake Government Email Tricked Revolut for Data

Fake Government Email Tricked Revolut for Data

Revolut confirmed that an attacker impersonated a government agency using an email address on that agency’s real domain to obtain sensitive customer records. Revolut says only a limited number of customers were affected and that customer funds and Revolut systems were not accessed.

September 14, 2026
Passkey Helpdesk Scam Hijacks Microsoft Accounts

Passkey Helpdesk Scam Hijacks Microsoft Accounts

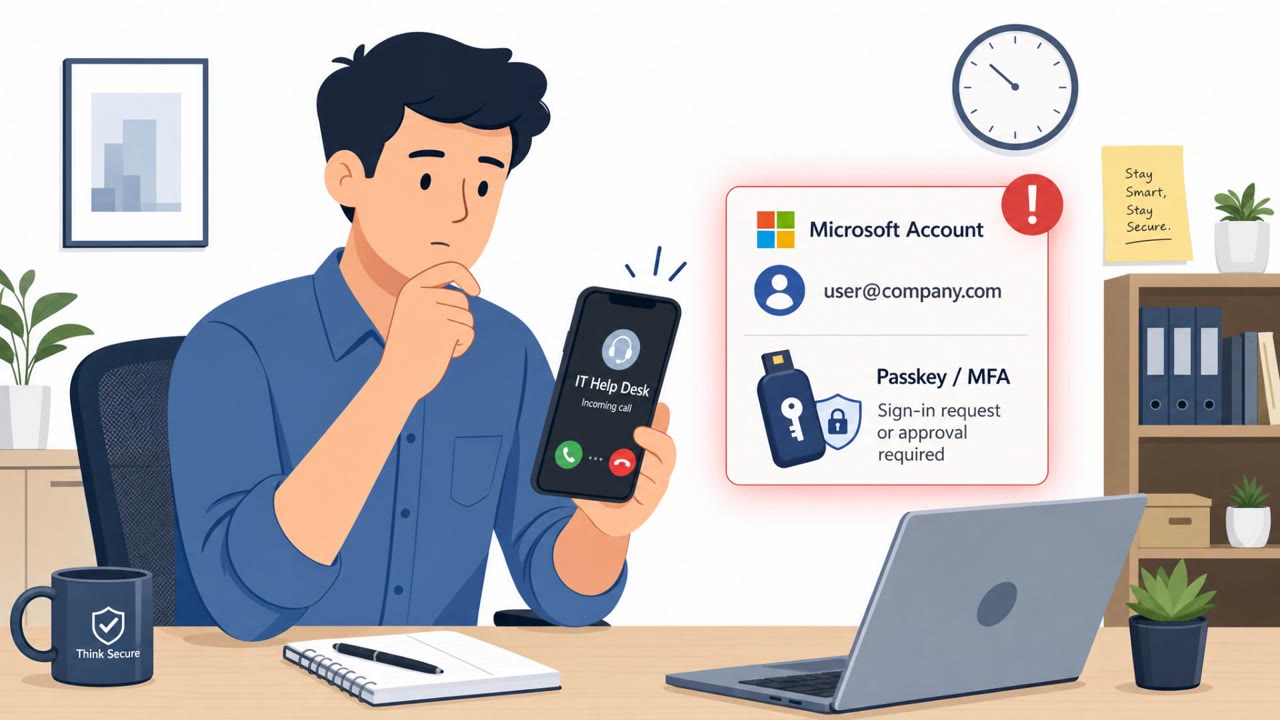
Microsoft described two real-world campaigns: an invoice fraud blast impersonating executives to trick finance teams into ACH payments, and a passkey-themed helpdesk scam that steals or bypasses authentication to take over Microsoft cloud accounts. In the second campaign, victims are called or…

September 13, 2026
Fake Govt Email Tricked Revolut Into Sharing KYC

Fake Govt Email Tricked Revolut Into Sharing KYC

Revolut says it handed over sensitive customer identity and financial data after receiving what looked like a legitimate government information request. The email came from inside a real government agency’s email domain and passed authentication checks, so staff processed it before later…

September 12, 2026
AI Brand Phish: Fake Anthropic, Gemini, OpenAI

AI Brand Phish: Fake Anthropic, Gemini, OpenAI

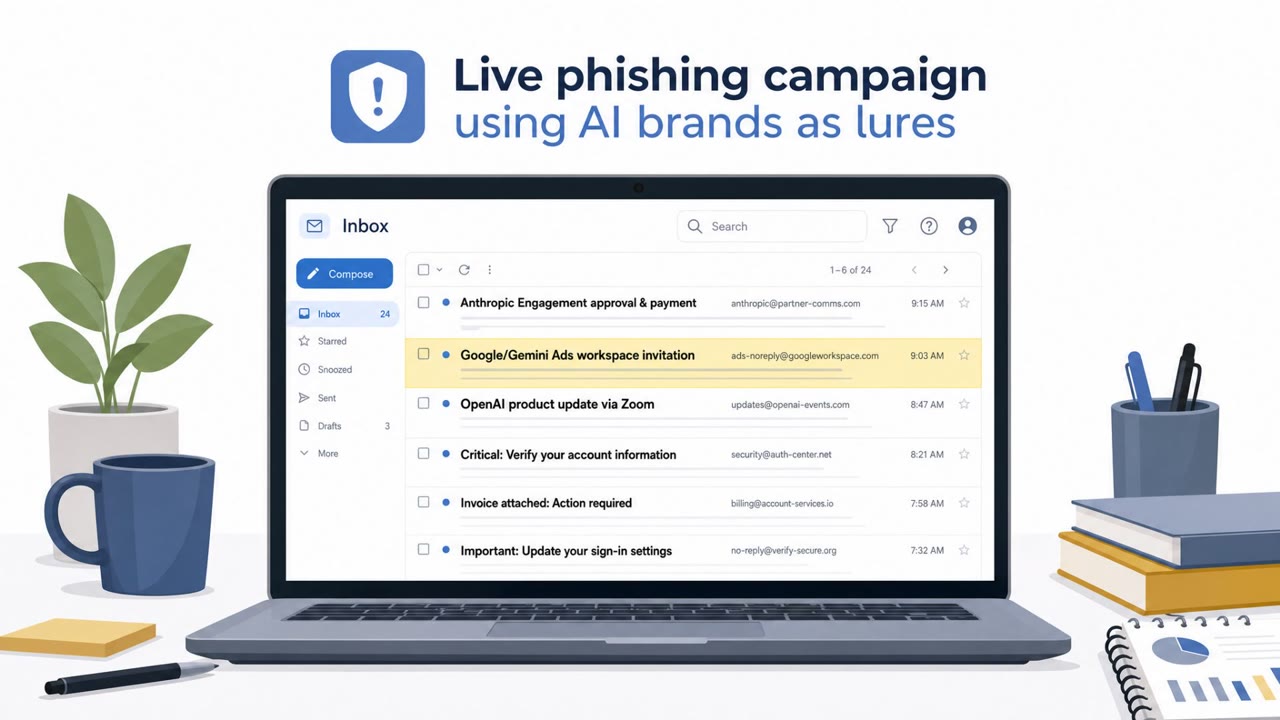
The article describes real phishing activity seen across multiple enterprise customers, where attackers used well-known AI brands as lures because employees now expect routine AI-related emails. It includes concrete subject lines, a suspicious impersonation domain, and an example of abusing…

September 12, 2026
Fake Downloads and Extensions Steal Sessions Fast

Fake Downloads and Extensions Steal Sessions Fast

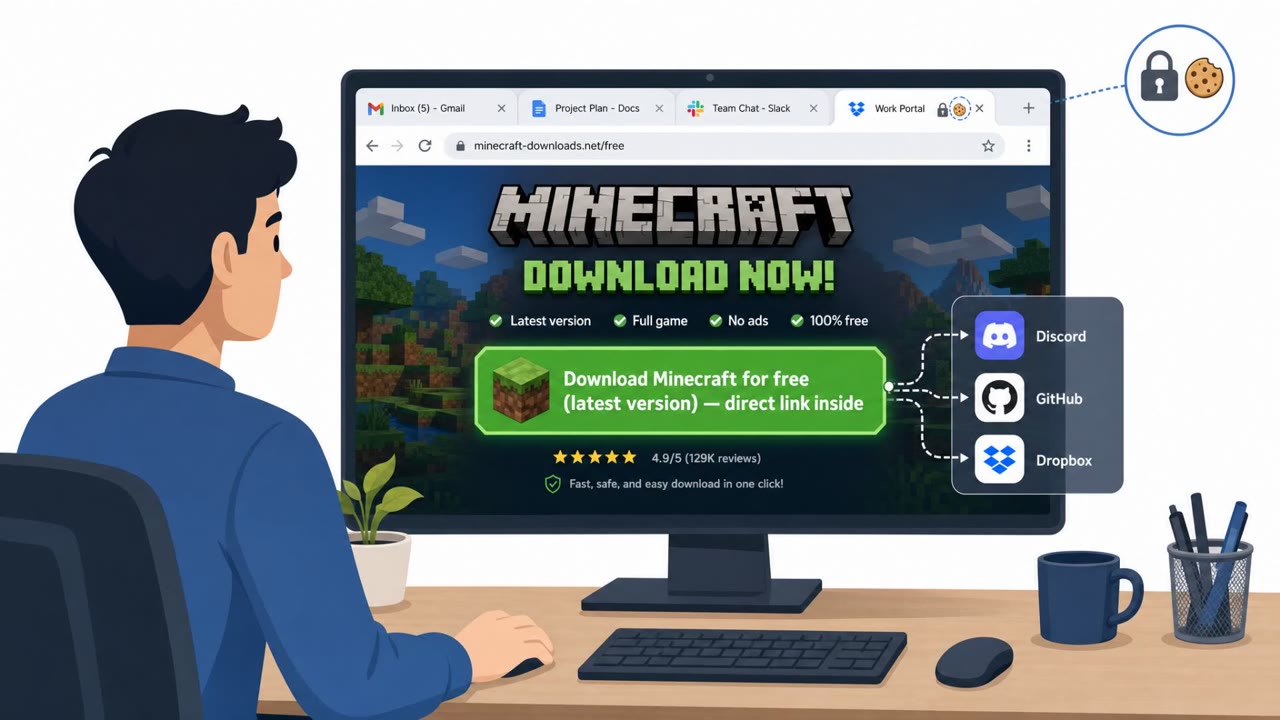
The article highlights real, ongoing campaigns where attackers trick people into installing malware via fake software-download websites and a disguised browser extension. These lures are used to steal credentials, browser cookies, and authenticated sessions, letting attackers take over accounts…

September 11, 2026
AI-Polished CEO Invoice Scam Hits 1M+ Emails

AI-Polished CEO Invoice Scam Hits 1M+ Emails

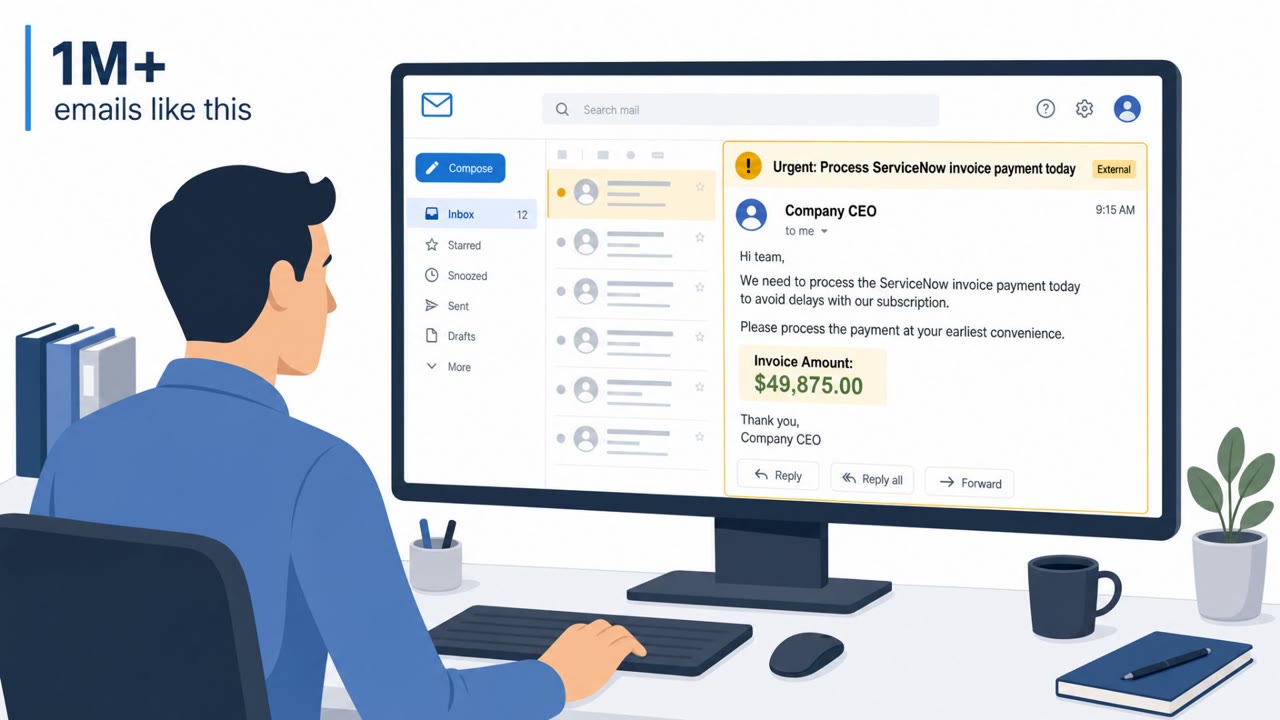
Microsoft reports a large business email compromise campaign where criminals impersonated company executives and used fake vendor branding to pressure accounts payable teams into paying nearly $50,000. The emails looked more believable by embedding a fabricated forwarded email chain (including a…

September 11, 2026
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
Russian Hackers Used AI to Evolve Phishing & Malware

Russian Hackers Used AI to Evolve Phishing & Malware

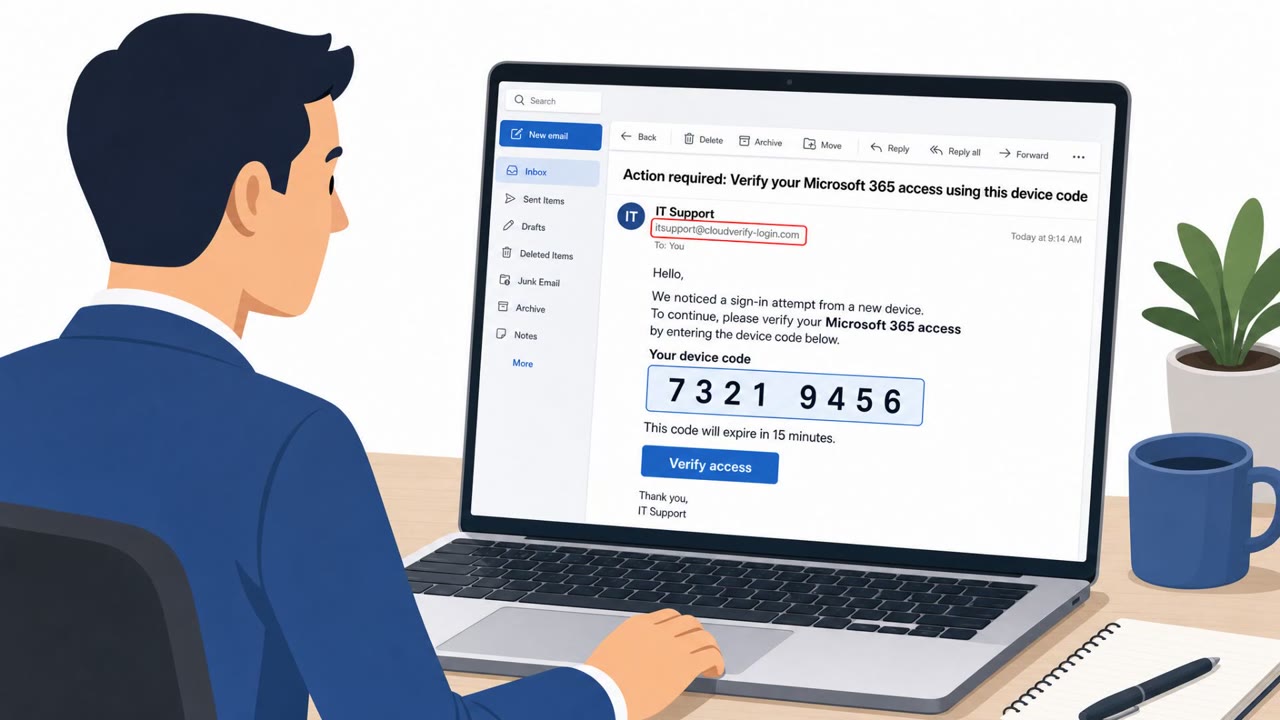
Anthropic says it disrupted a Russian state-linked campaign that used Claude to continuously rebuild malware when security tools detected it. The group (GTG-20006, linked to Midnight Blizzard/APT29) ran phishing and other human-targeted schemes, including device-code token theft against Microsoft…

September 11, 2026
Brevo Breach Fuels Crypto Newsletter Phishing

Brevo Breach Fuels Crypto Newsletter Phishing

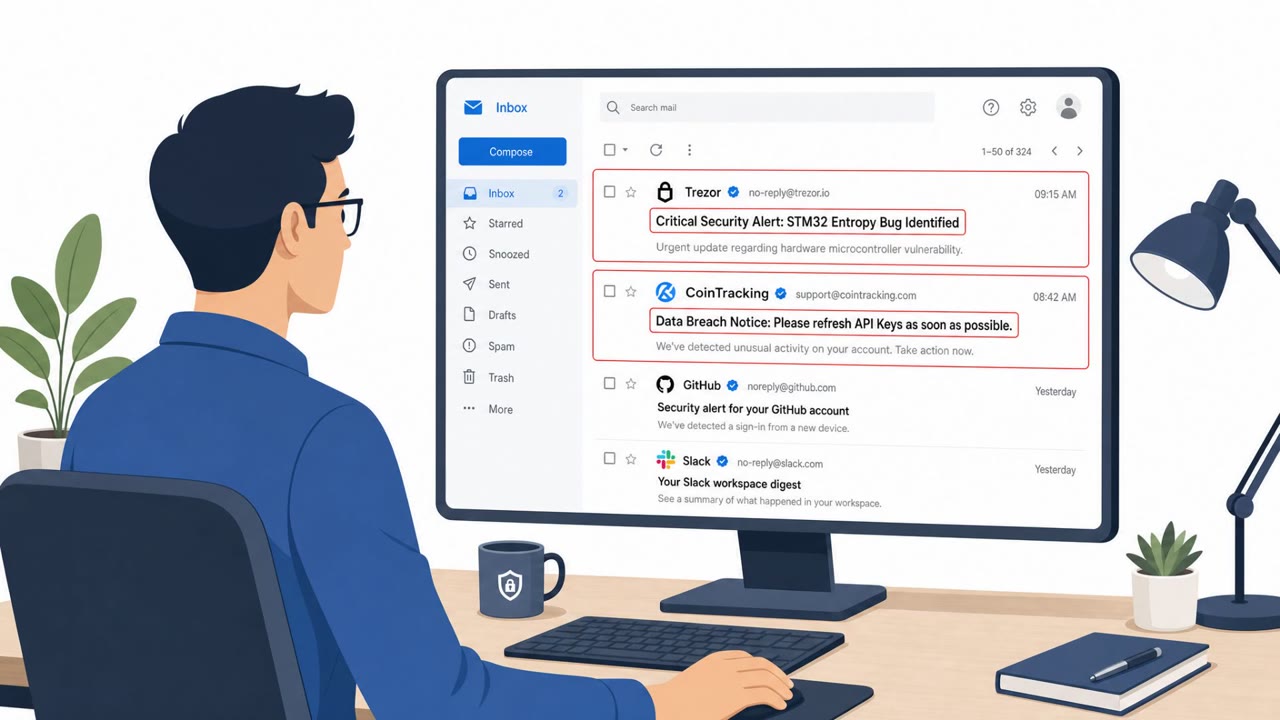
Attackers abused access to Brevo (an email marketing platform) to send highly convincing phishing emails from legitimate cryptocurrency company domains to newsletter subscribers. The lures claimed urgent security issues (hardware vulnerability or data breach) and pushed victims to click links,…

September 11, 2026
N0va Device-Code Phish Steals Microsoft Sessions

N0va Device-Code Phish Steals Microsoft Sessions

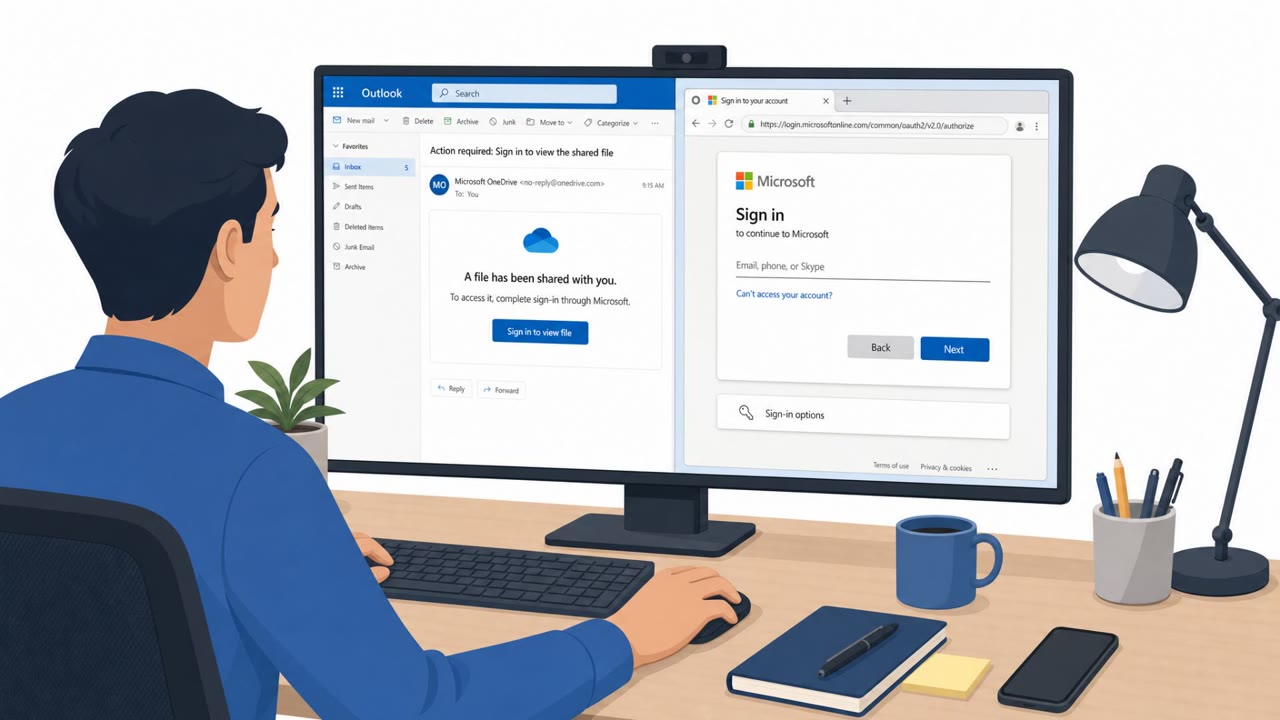
Researchers reported a real phishing operation (“N0va” phishkit) that tricks people into signing into Microsoft through a legitimate Microsoft page, but for an attacker-started session. Victims can complete MFA and still grant the attacker access and refresh tokens, letting the attacker operate as…

September 11, 2026
FBI Warns of OAuth Consent Phishing Tricks

FBI Warns of OAuth Consent Phishing Tricks

A SecurityWeek roundup highlights multiple real-world scams and campaigns where attackers trick people rather than “hack” systems directly. Notable items include OAuth “consent phishing” (getting users to approve a malicious app’s access), and phishing-evasion using invisible Unicode characters…

September 11, 2026
M365 Direct Send Spoofs Internal HR & Finance

M365 Direct Send Spoofs Internal HR & Finance

Researchers observed a real phishing campaign that abused Microsoft 365’s “Direct Send” feature to deliver messages that looked like they came from trusted internal addresses (HR, accounting, admin). The emails commonly used familiar business lures like invoices, payment approvals, voicemail…

September 11, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo