Recent Cryptocurrency Cyber Attacks

Page 2 of 5
Crypto Newsletter Breach Triggers Fake Security Emails

Crypto Newsletter Breach Triggers Fake Security Emails

Attackers abused access to a third-party email newsletter provider to send convincing “security alert” emails from legitimate-looking crypto company domains. The emails pushed users to click links that led to phishing sites designed to look nearly identical to real platforms. Trezor, CoinTracking,…

September 10, 2026
Fake Google Support Bait Led to $245M Crypto Theft

Fake Google Support Bait Led to $245M Crypto Theft

A Singaporean man, Malone Lam (aliases including “Anne Hathaway”), pleaded guilty to leading a group that stole over $245 million in cryptocurrency from U.S. victims. The group used social engineering, such as posing as Google Support and using spoofed phone numbers, to trick victims into handing…

September 10, 2026
Brevo Breach Sparks Trezor Phishing Wave

Brevo Breach Sparks Trezor Phishing Wave

Trezor said attackers breached its third-party email provider (Brevo) and gained access to Trezor’s email domain, triggering phishing emails to subscribers. The scam emails used a fake “critical security alert” about a supposed microcontroller vulnerability and attempted to trick users into handing…

September 10, 2026
Crypto Scammers Posed as Apple/Google Support

Crypto Scammers Posed as Apple/Google Support

U.S. prosecutors say a group led by Malone Lam ran social engineering scams that stole over $245 million in cryptocurrency. The scammers allegedly called crypto holders while pretending to be customer support from Apple or Google, talked victims into handing over key account details, and in at…

September 8, 2026
Fake Google & Gemini Calls Led to $240M Bitcoin Heist

Fake Google & Gemini Calls Led to $240M Bitcoin Heist

A group of young scammers stole more than $240 million in bitcoin by calling a wealthy crypto investor and impersonating trusted companies. The callers claimed the victim’s accounts and wallet were under attack, then tricked him into granting access and sharing security codes that enabled the…

September 8, 2026
Trezor Users Targeted by Phishing Calls & QR Letters

Trezor Users Targeted by Phishing Calls & QR Letters

After a breach at shipping partner ShipMonk, attackers obtained Trezor customers’ contact and shipping details, increasing the risk of scams. Reports on Reddit indicate customers have already received phishing phone calls and physical letters containing QR-code phishing lures. Trezor warned…

September 8, 2026
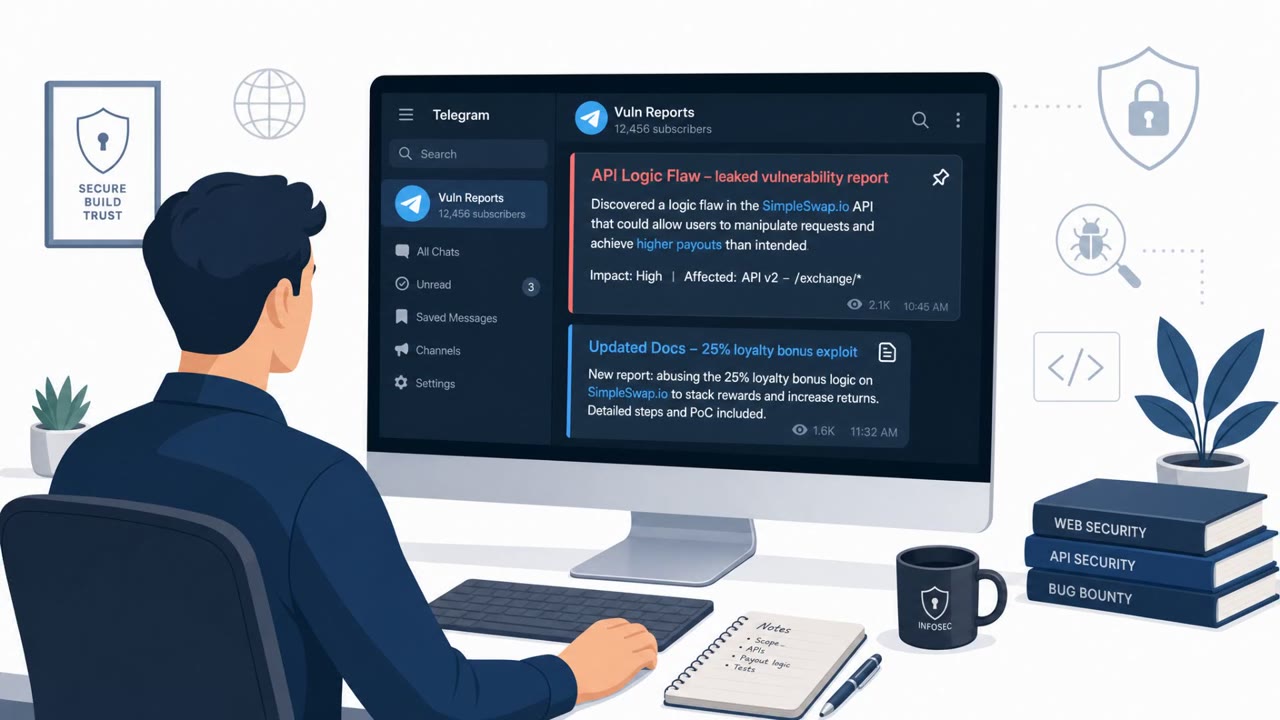
Fake “API Exploit” Lures Users Into Self-Hacking

Fake “API Exploit” Lures Users Into Self-Hacking

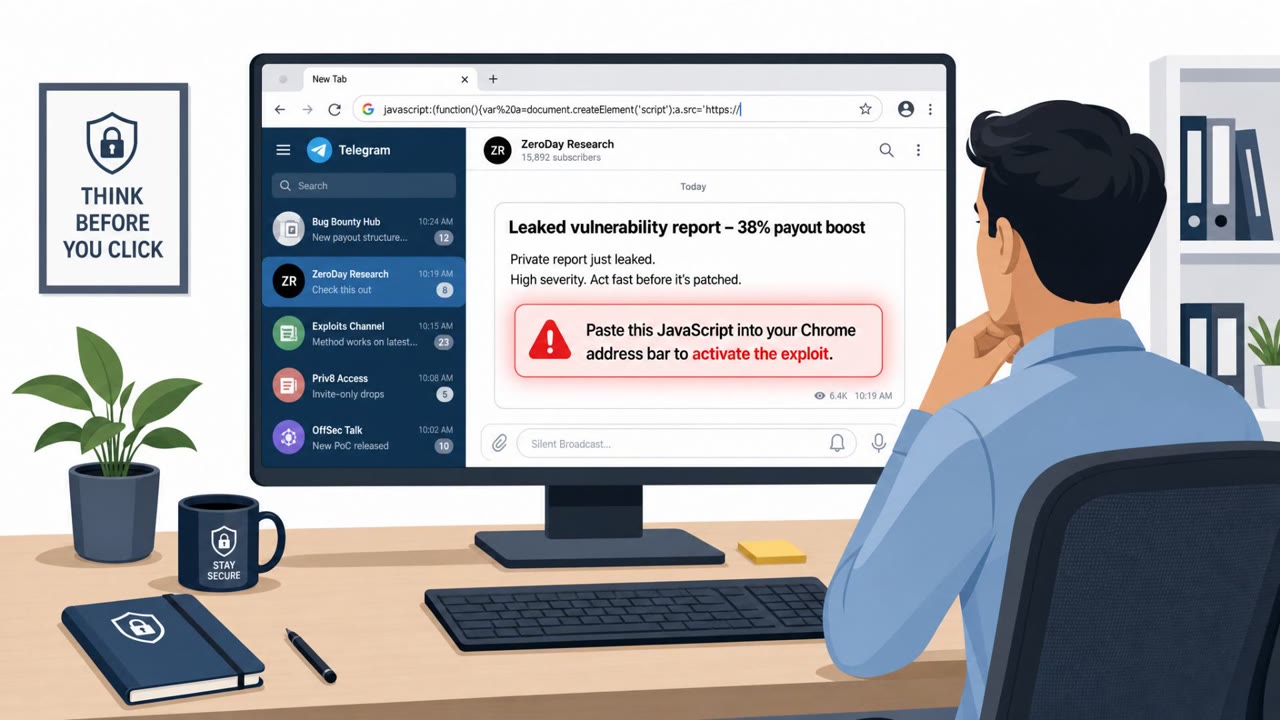
Cisco Talos reports a real cryptocurrency-theft campaign where criminals trick people into pasting JavaScript into their browser or installing it via the Tampermonkey extension. The lure pretends to be a leaked vulnerability report for crypto swap sites, but the “exploit” is fake and instead…

September 8, 2026
ClickFix Lures Users to Paste Code via Browser

ClickFix Lures Users to Paste Code via Browser

Cisco Talos described real ClickFix campaigns where attackers trick people into pasting code either into the Chrome address bar (or a browser extension) or into the Windows Run dialog. The first campaign targeted crypto swap sites and used a fake “leaked vulnerability report” to get victims to run…

September 8, 2026
REVSTEALER Lures Push Fake Cheats, Drop Miners

REVSTEALER Lures Push Fake Cheats, Drop Miners

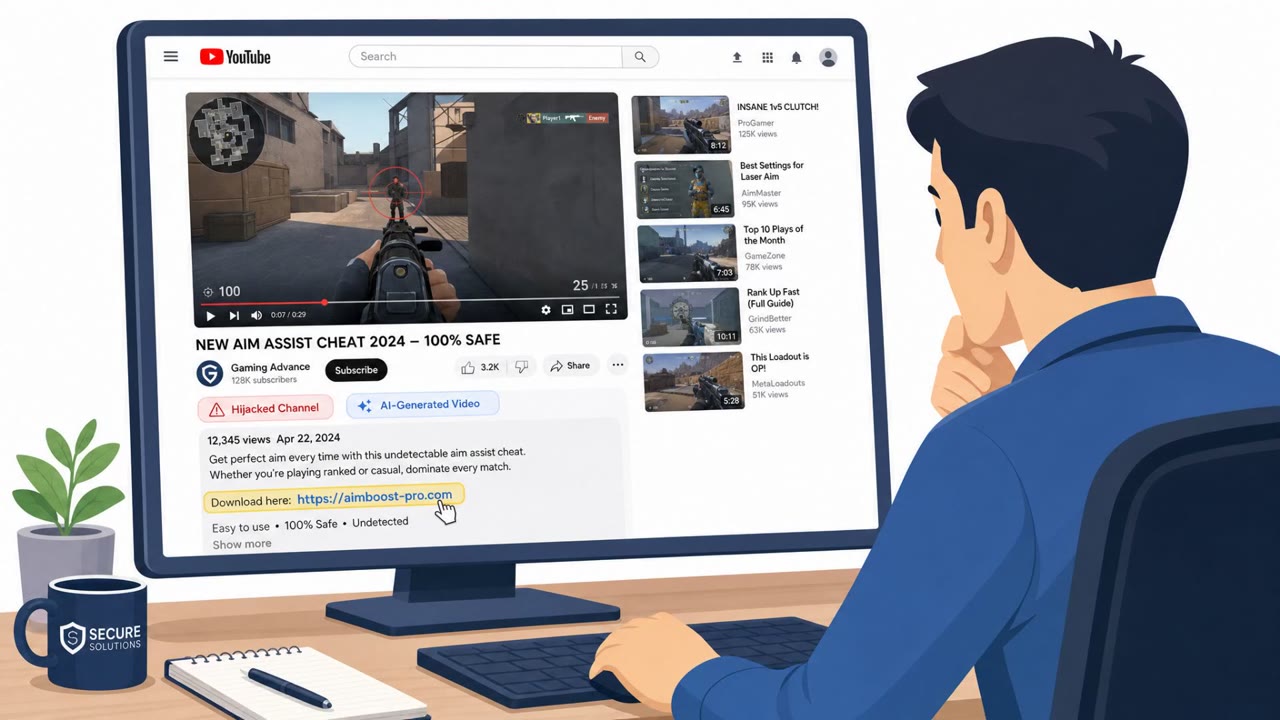
Researchers tied several new programs to the REVSTEALER Windows info-stealer that can steal crypto wallet data, hijack clipboard crypto addresses, and even disable Windows Update and Microsoft Defender to run a crypto miner. Victims are primarily pulled in through “game-cheat” downloads promoted by…

September 6, 2026
Fake GTA 6 “Leaked Copy” Site Drains Wallets

Fake GTA 6 “Leaked Copy” Site Drains Wallets

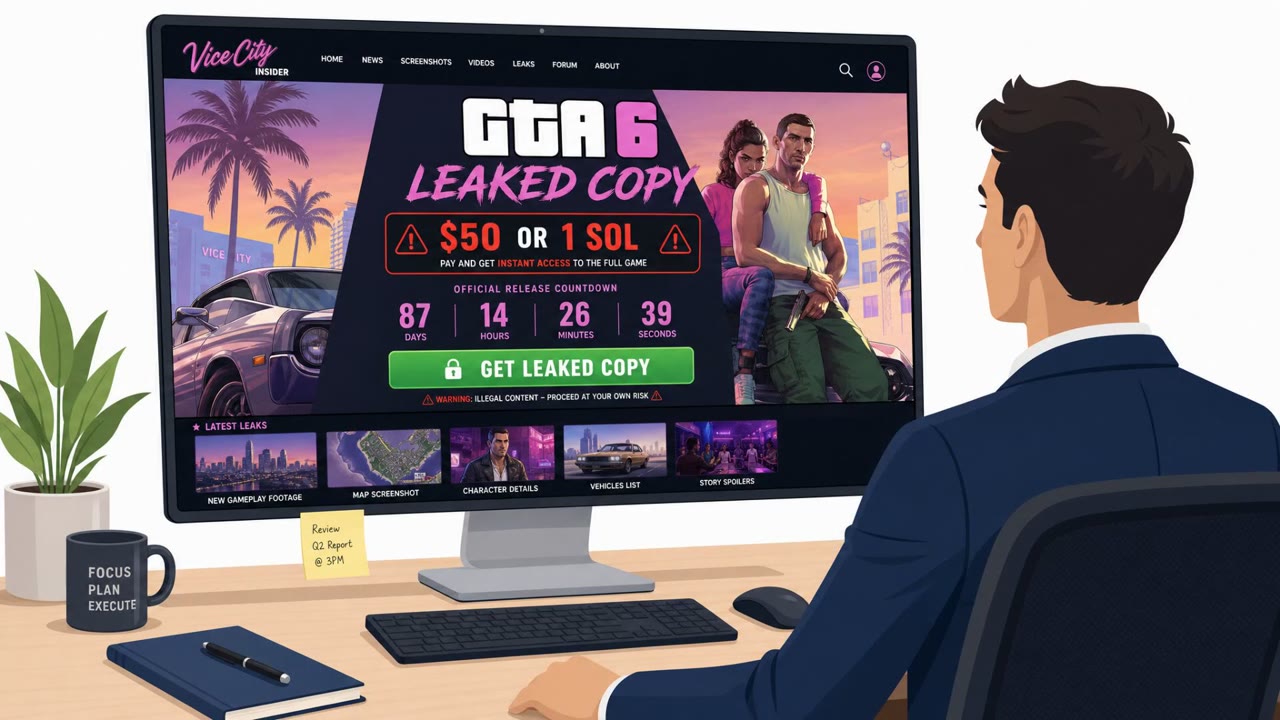
A scam website posing as a GTA 6 fan countdown page tricks visitors into buying a “leaked copy” and then prompts them to connect a crypto wallet. Once connected, it generates transactions/approvals designed to transfer the victim’s cryptocurrency (and potentially NFTs) to the attacker. The site…

September 1, 2026
Fake “Claude Opus 5” GitHub Drops RevStealer

Fake “Claude Opus 5” GitHub Drops RevStealer

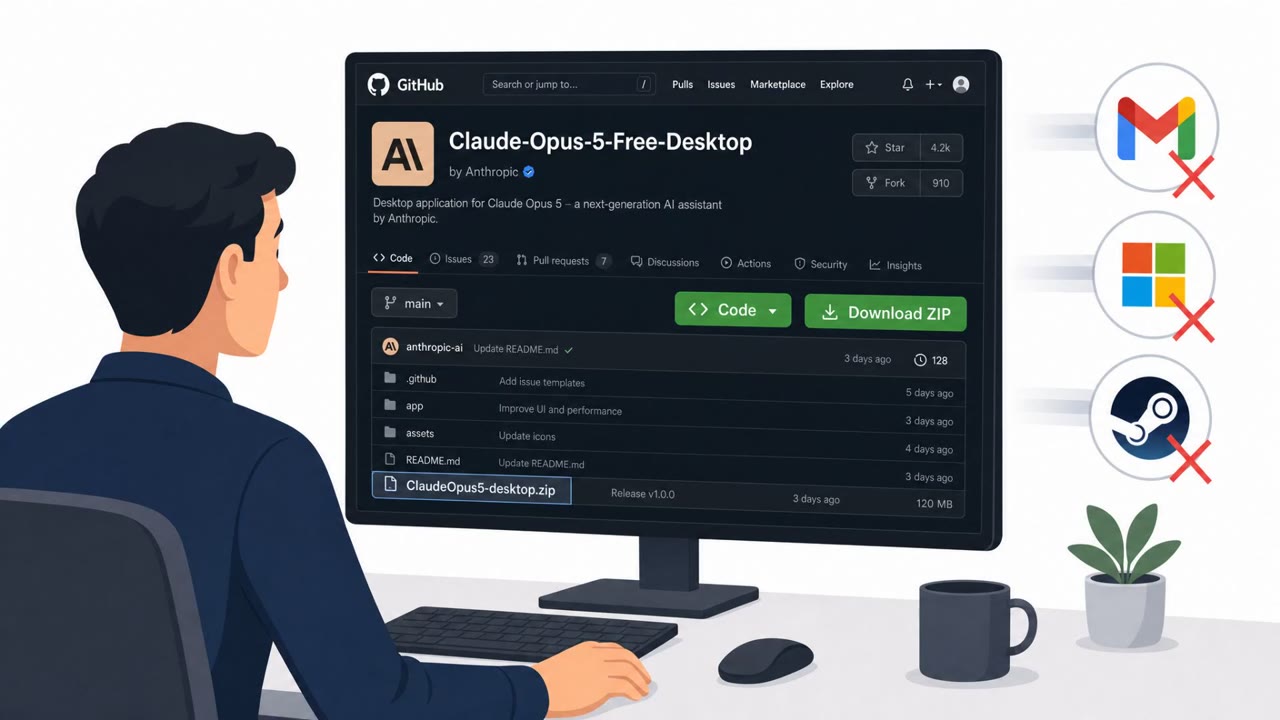
A malicious GitHub repository impersonating Anthropic advertised a “free” Claude Opus 5 desktop app and tricked users into downloading a ZIP that silently installed RevStealer. Victims reported account takeovers after running it, and the malware is designed to steal passwords, crypto wallet data,…

September 1, 2026
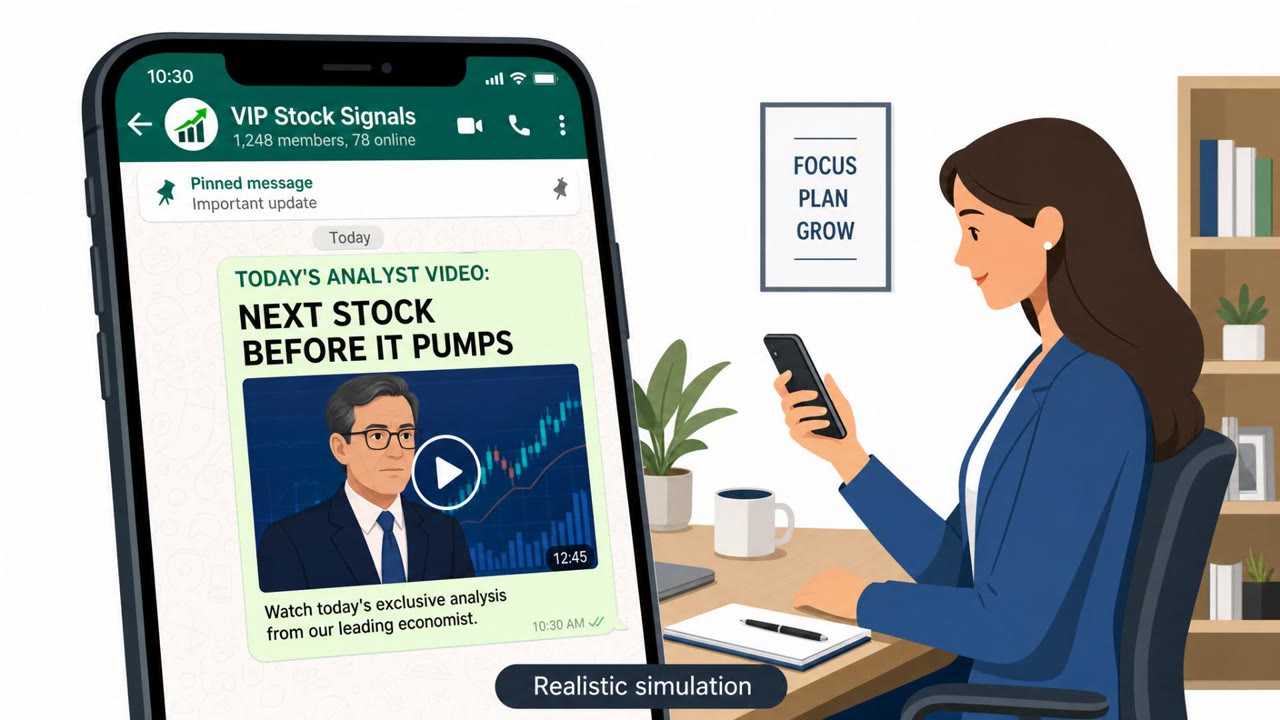
Deepfake Stock Tips Pushed via WhatsApp

Deepfake Stock Tips Pushed via WhatsApp

Group-IB warns that organized investment fraud is using deepfake video “endorsements,” WhatsApp groups, and professional-looking fake crypto platforms to trick victims into sending money. The models described (“GoldBull” and “CoinLure”) include pump-and-dump stock manipulation and a large network…

August 27, 2026
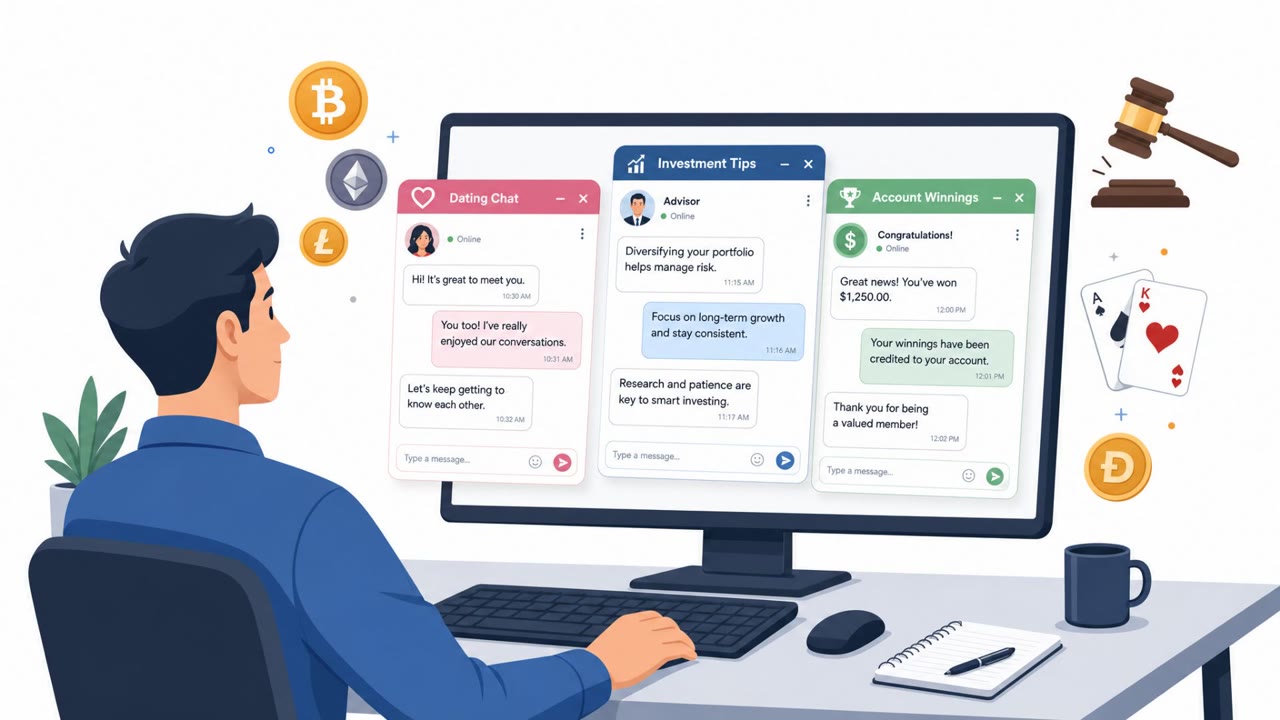
ChatGPT-Enabled Scam Network Disrupted

ChatGPT-Enabled Scam Network Disrupted

A Cambodia-based scam network used ChatGPT to run multiple social-engineering schemes at once, including romance scams that pivoted into fake crypto/gold investments. The same operators also posed as online gambling reps offering fake winnings and as law enforcement demanding “fines,” using forged…

August 27, 2026
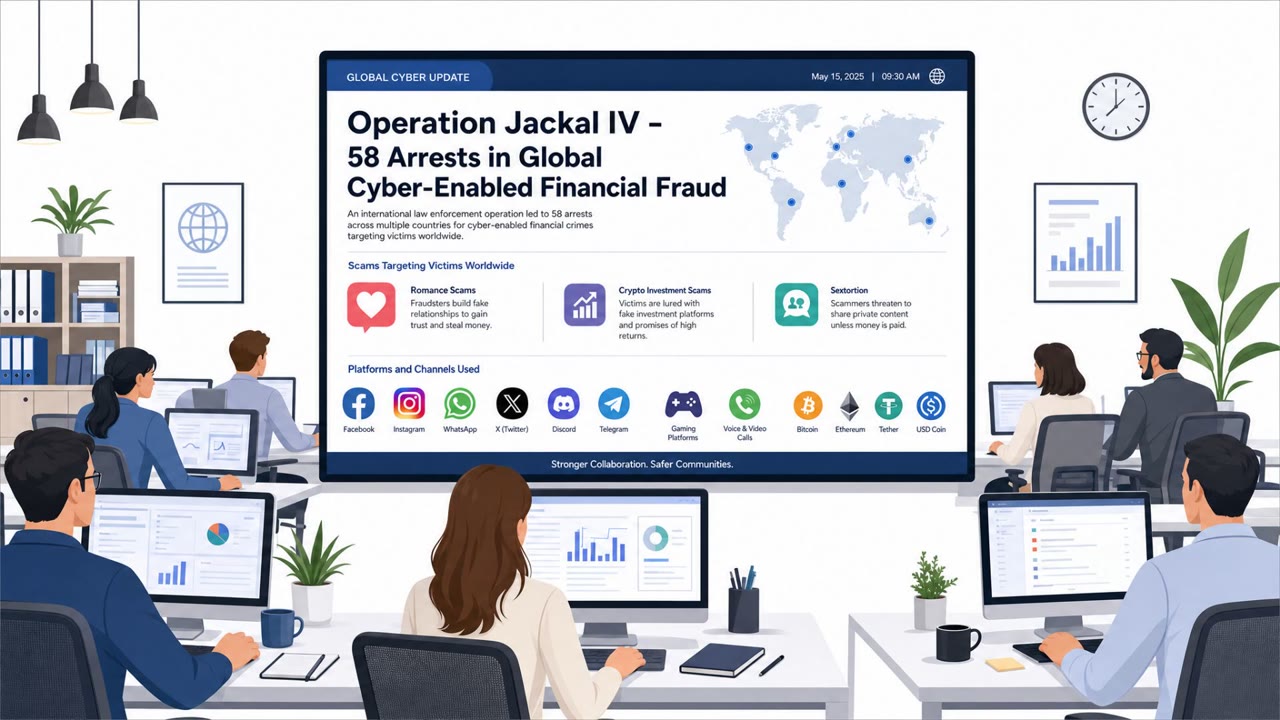
Interpol Busts Romance, Crypto & Sextortion Rings

Interpol Busts Romance, Crypto & Sextortion Rings

Interpol said an eight-month operation across 22 countries led to 58 arrests tied to cyber-enabled financial fraud, including romance scams, cryptocurrency/investment scams, and business email compromise. Authorities described how scammers build trust with victims (including minors) on social and…

August 25, 2026
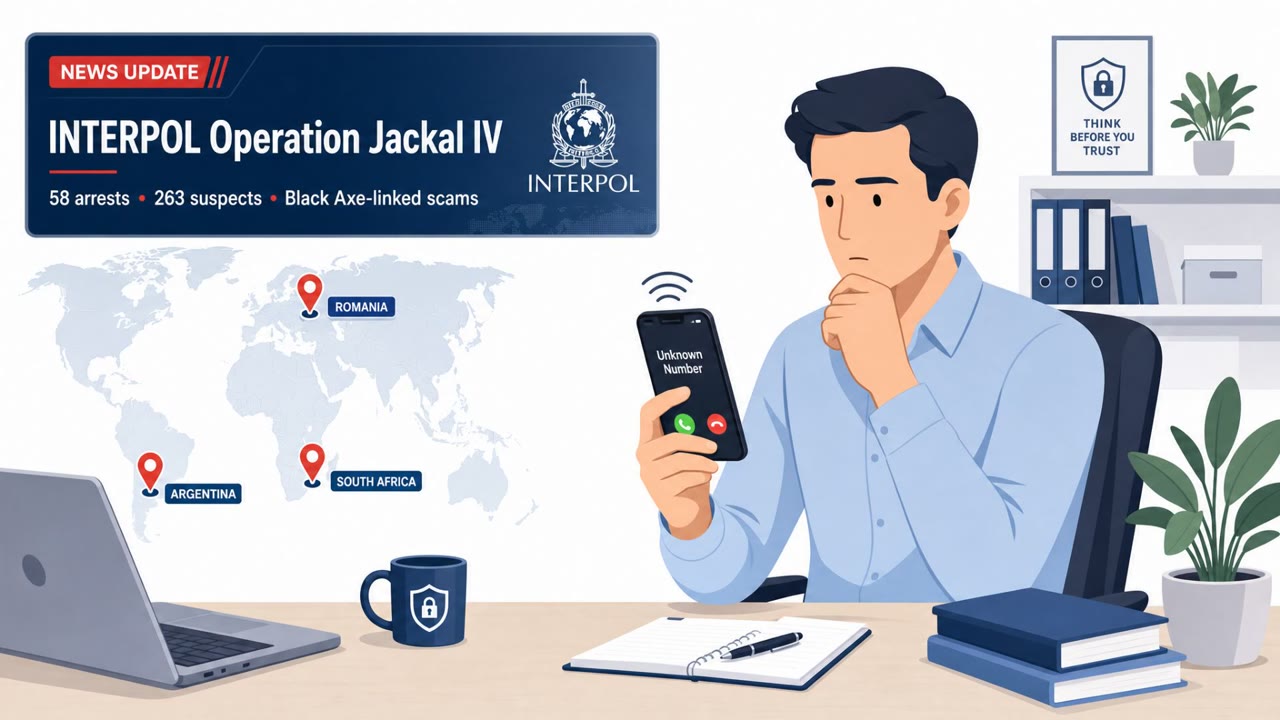
Interpol Sting Hits Black Axe Scam Networks

Interpol Sting Hits Black Axe Scam Networks

Interpol said Operation Jackal IV arrested dozens and disrupted West Africa–linked criminal networks tied to scams and money laundering, including Black Axe. The cases described include a call-center “investment” scam, romance/investment scams targeting retirees, and sextortion of teenagers on…

August 25, 2026
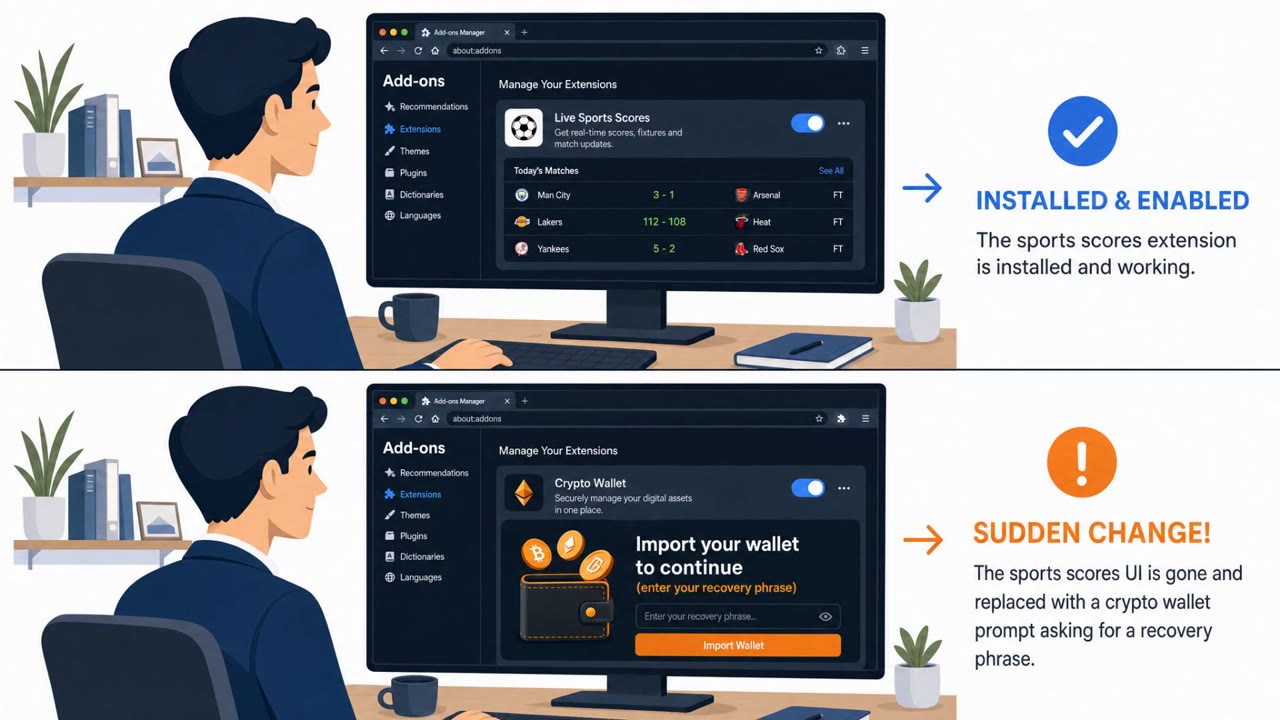
Fake Firefox Wallet Add-ons Steal Seed Phrases

Fake Firefox Wallet Add-ons Steal Seed Phrases

Researchers found a campaign of malicious Firefox add-ons that look like legitimate crypto wallets, VPNs, or utilities but are designed to trick people into entering wallet recovery phrases or exposing credentials. The add-ons can switch from harmless decoys (like a notepad or sports scores) to a…

August 24, 2026
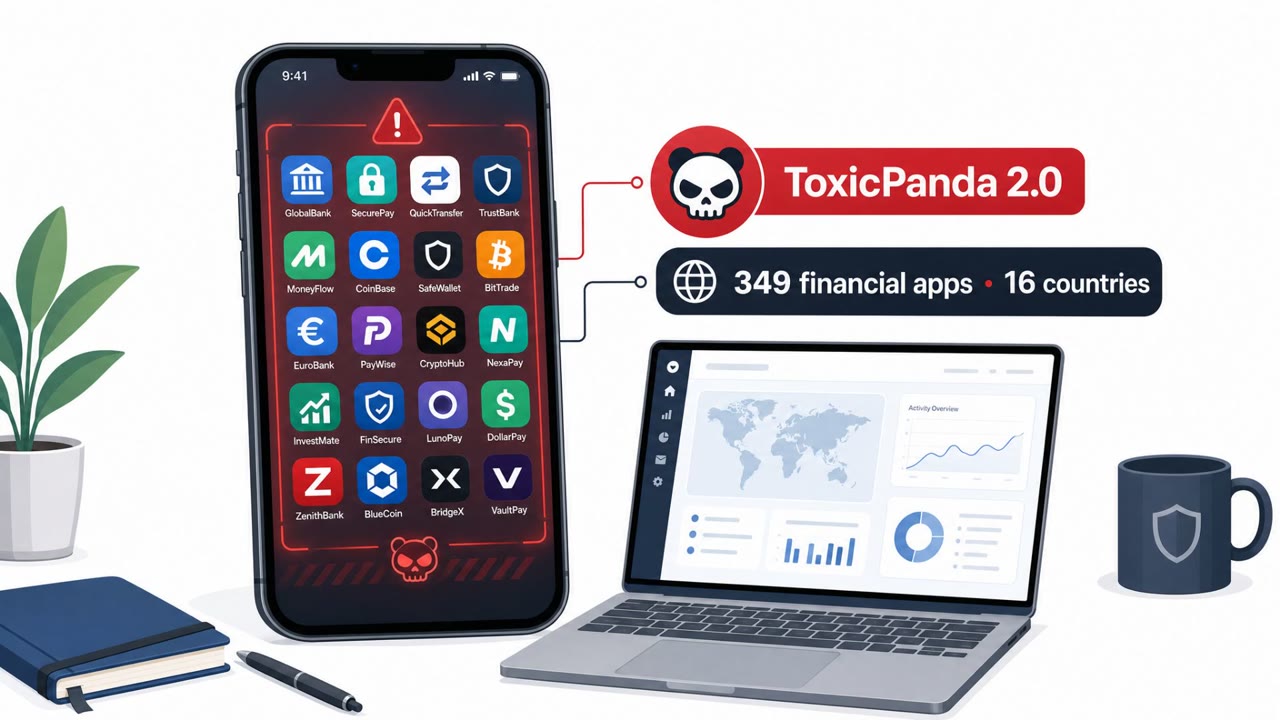
ToxicPanda 2.0 Tricks Users, Steals Bank Logins

ToxicPanda 2.0 Tricks Users, Steals Bank Logins

Zimperium reports ToxicPanda 2.0 is a mobile banking trojan that targets 349 financial apps across 16 countries by impersonating legitimate screens and prompts to trick users into granting permissions. After installation, it uses Android Accessibility and Wireless Debugging to gain deeper control…

August 22, 2026
Fake Bank Calls and ClickFix Drive Data Theft

Fake Bank Calls and ClickFix Drive Data Theft

The roundup describes multiple real-world attacks where criminals manipulate people, not just systems, such as fake bank support calls that trick victims into installing phone malware, and “ClickFix” lures that convince Mac users to run malicious commands. It also highlights an AI-assisted…

August 21, 2026
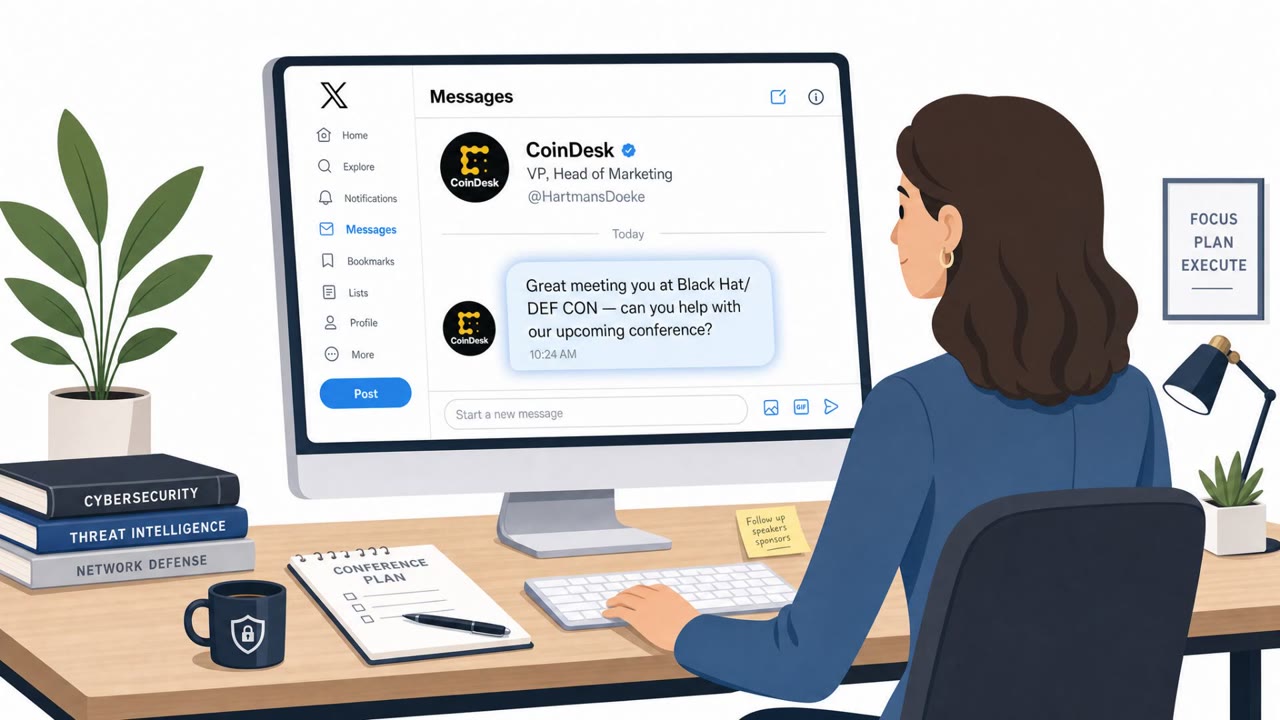
DEF CON Attendees Hit With Fake CoinDesk DMs

DEF CON Attendees Hit With Fake CoinDesk DMs

After Black Hat/DEF CON, cybercriminals allegedly targeted conference attendees by impersonating a CoinDesk executive over X direct messages. Victims were pushed into a realistic workflow using Google Docs and a fake Dropbox DocSend installer to trick them into running malware on macOS or Windows.

August 21, 2026
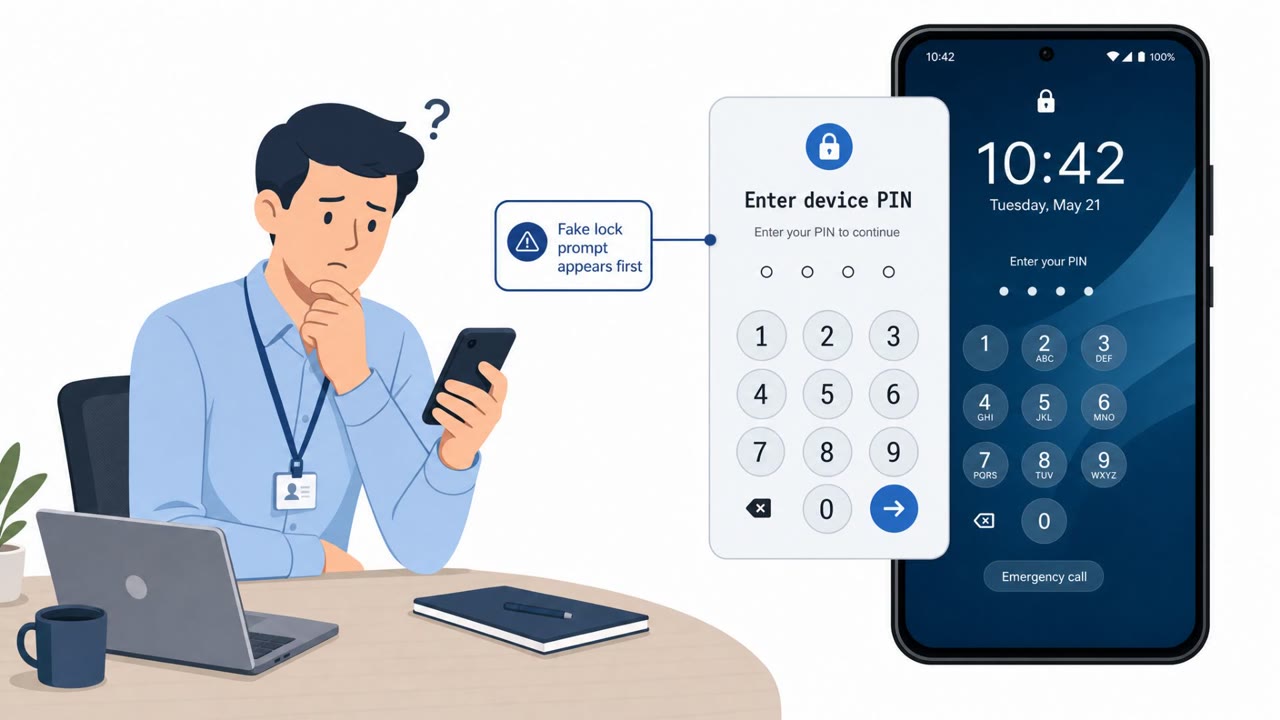
Manic Malware Steals PINs With Fake Lock Prompts

Manic Malware Steals PINs With Fake Lock Prompts

Researchers report a real Android malware operation (“Manic”) active since at least February 2026 that blends banking fraud with spyware-style surveillance. It can trick users into revealing their device PIN/pattern via a fake lock prompt and silently capture banking PIN taps, then exfiltrate…

August 20, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo