Recent Financial Services Cyber Attacks

Page 11 of 13
TA488 Uses “Half-Click” OWA Emails to Persist

TA488 Uses “Half-Click” OWA Emails to Persist

Proofpoint reports a Russia-aligned espionage group (TA488) returned with a campaign that compromises on‑premises Outlook Web Access simply when a user opens an email in the reading pane. The attack uses a cross-site scripting flaw to run hidden JavaScript, install a browser-resident implant, and…

July 29, 2026
Clone Websites Trick Firms Into Paying Fake Invoices

Clone Websites Trick Firms Into Paying Fake Invoices

Researchers described a long-running fraud campaign where criminals clone real Russian company websites and replace contact and bank details to intercept international business deals. Victims are lured through cold calls, phishing emails, and fake supplier websites, then sent realistic contracts…

July 29, 2026
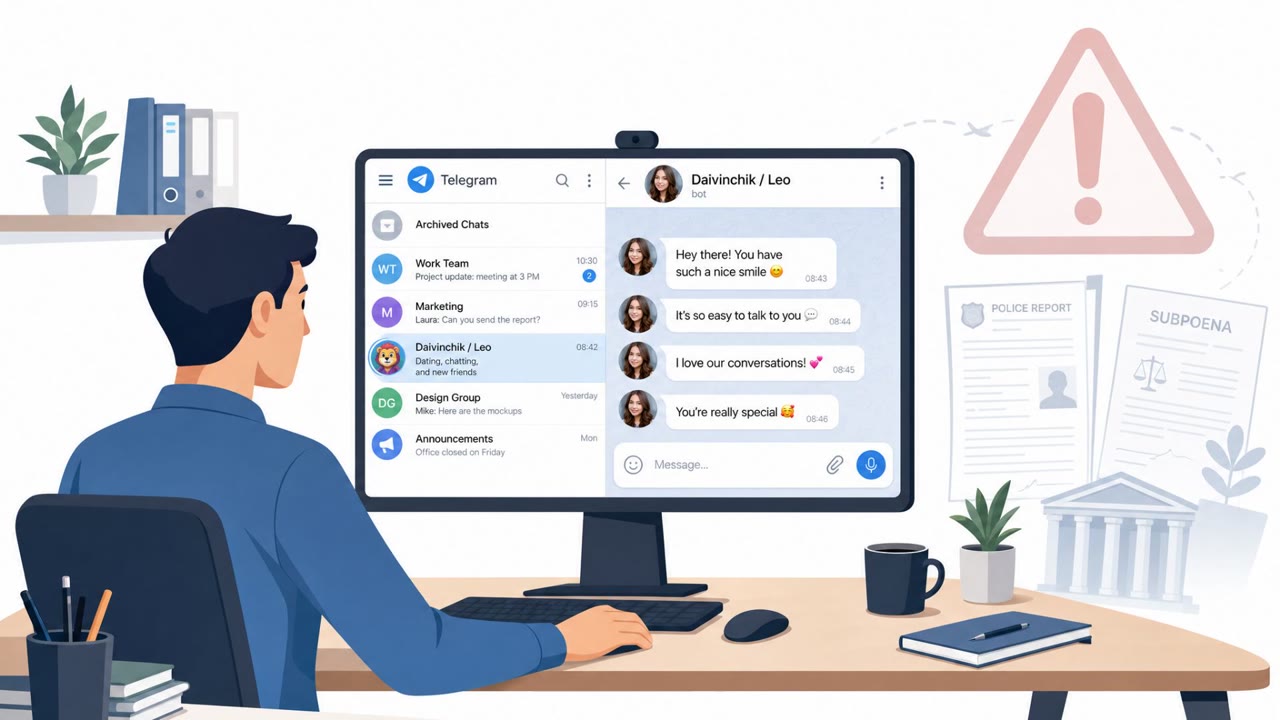
Telegram Dating Bot Used for Romance-to-Arson Scam

Telegram Dating Bot Used for Romance-to-Arson Scam

Russia’s FSB claims Ukrainian intelligence used a Telegram dating chatbot to deceive and psychologically pressure young Russians into sharing locations, clicking phishing links, and later carrying out arson or armed attacks. The alleged scheme started with romance-style outreach and payments via…

July 29, 2026
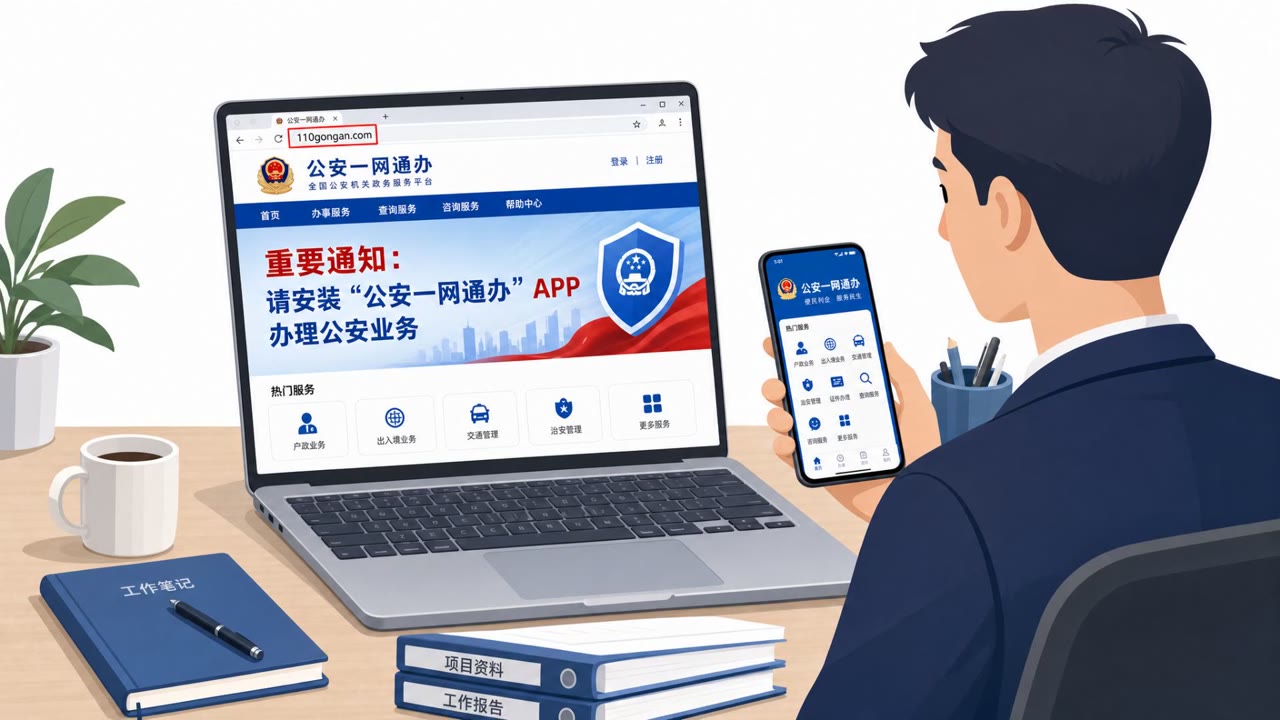
Fake Public Security App Spreads Android RAT

Fake Public Security App Spreads Android RAT

Researchers tied the Flying Eagle Android remote-access trojan to a fake “Public Security” service app aimed at Android users in China. The malicious app was reportedly distributed from a lookalike website and could steal payment credentials and remotely control infected phones. The tooling is…

July 29, 2026
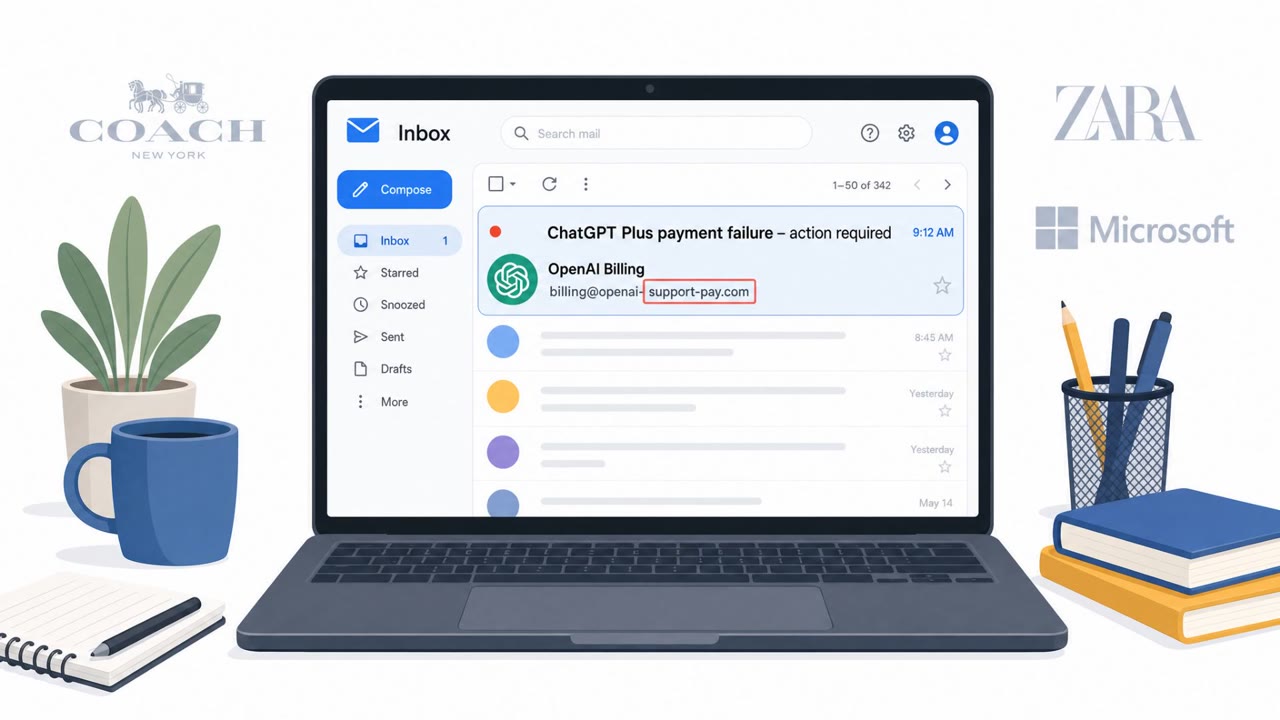
Fake ChatGPT Billing Emails Steal Card Details

Fake ChatGPT Billing Emails Steal Card Details

Check Point reports that scammers are now impersonating ChatGPT/OpenAI in phishing campaigns, reflecting how mainstream the service has become. One documented example used a fake “ChatGPT Plus payment failure” notice that sent victims to a fraudulent payment page designed to capture full credit…

July 28, 2026
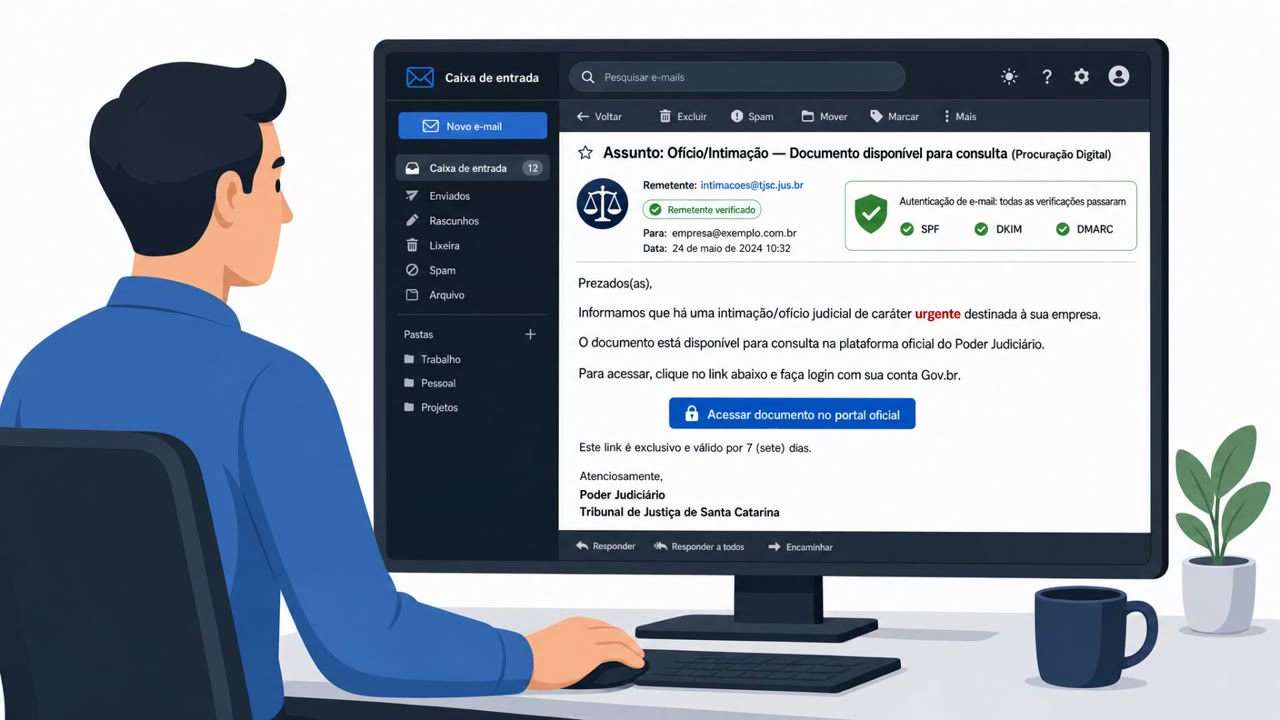
PhantomEnigma Phishes via Hijacked .gov.br Sites

PhantomEnigma Phishes via Hijacked .gov.br Sites

Researchers describe a real phishing-driven malware operation ("PhantomEnigma") that abuses compromised Brazilian government websites and mailboxes to appear trustworthy. Victims are lured with fake law-enforcement style documents (e.g., “Ofício” summons or “Procuração Digital”) and pushed to…

July 28, 2026
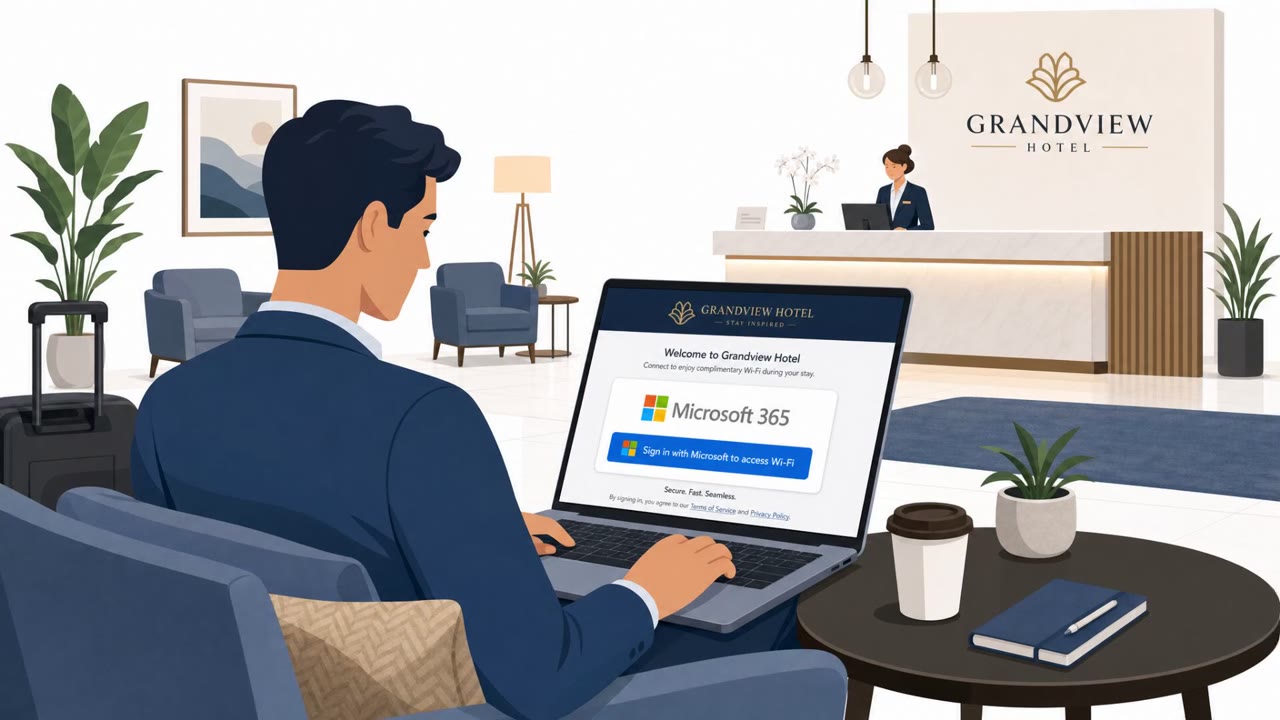
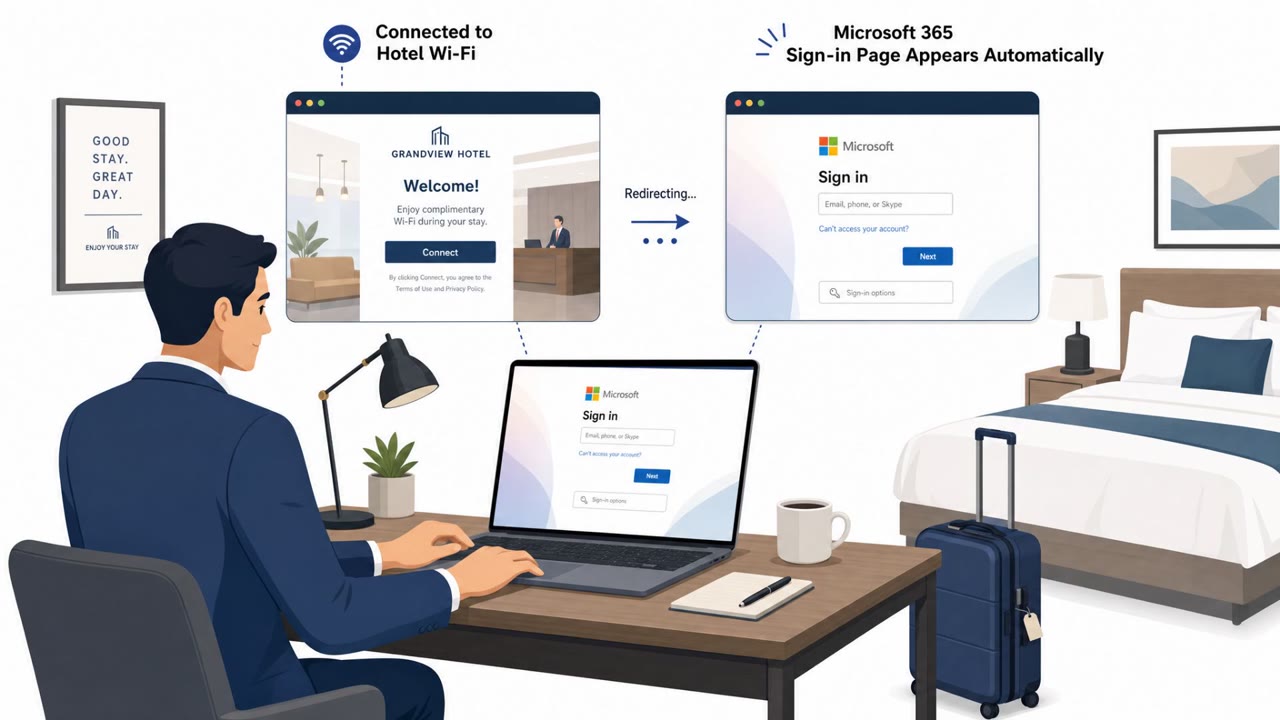
Hotel Wi‑Fi DNS Scam Steals Microsoft 365 Logins

Hotel Wi‑Fi DNS Scam Steals Microsoft 365 Logins

Attackers are taking over hotel and conference Wi‑Fi gateways and changing DNS settings so travelers are silently redirected to fake Microsoft 365 sign-in pages. Victims are then tricked into completing a device-code login that grants attackers a legitimate session token, often bypassing MFA. This…

July 28, 2026
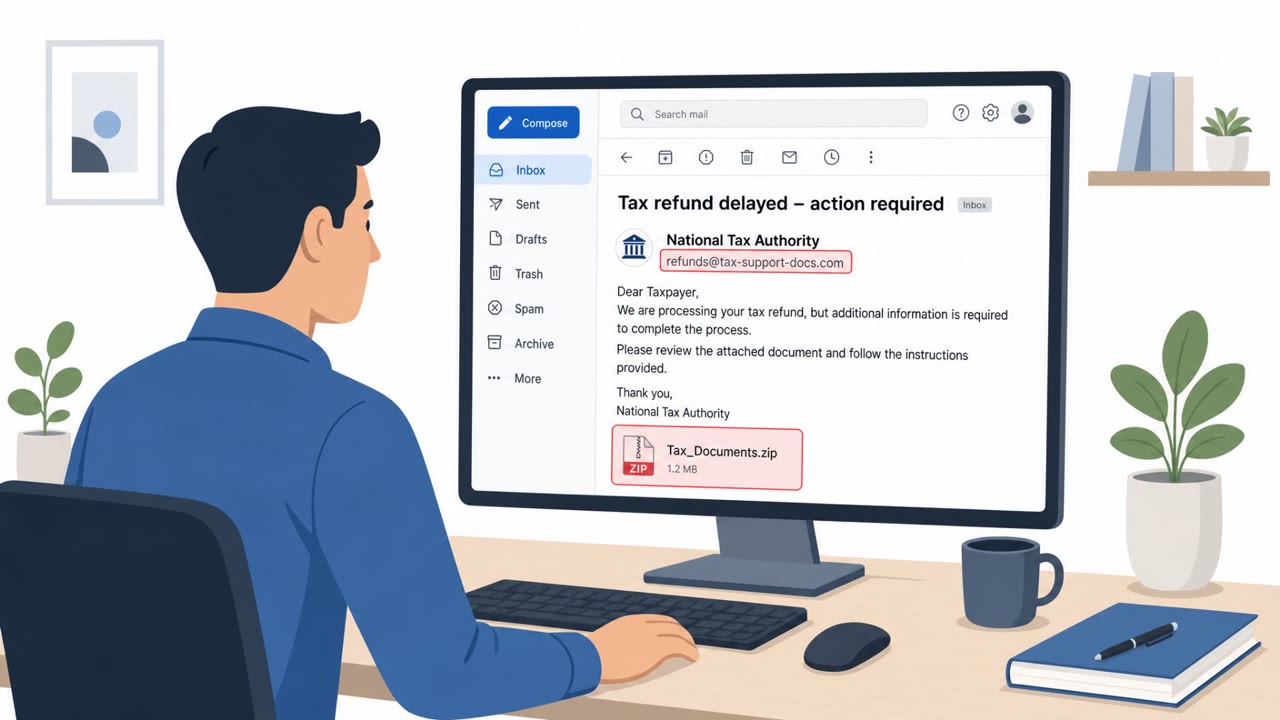
Tax and SSA Lures Push Stealth Malware via Cruciferra

Tax and SSA Lures Push Stealth Malware via Cruciferra

Proofpoint linked multiple real-world email campaigns to “Cruciferra,” a commercial crypter service that helps criminals hide malware from security tools. The campaigns used familiar social-engineering themes, tax documents, U.S. Social Security Administration messages, and even bed-bug complaints,…

July 28, 2026
Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Researchers report Mirage Kitten (an espionage-focused threat group) targeted organizations in the Middle East and Africa using highly tailored spear‑phishing. The lures included recruitment-themed messages impersonating trusted brands/hiring sites and fake videoconferencing pages that redirected…

July 28, 2026
Hotel Wi‑Fi DNS Hijack Steals M365 Logins

Hotel Wi‑Fi DNS Hijack Steals M365 Logins

Researchers report attackers compromising hotel and venue Wi‑Fi “captive portal” gateways to redirect Microsoft 365 sign-ins to attacker-controlled lookalike domains. Victims can have their Microsoft 365 credentials stolen without clicking a phishing link or installing malware, because the…

July 28, 2026
Hotel Wi‑Fi Redirect Scam Steals Microsoft 365 Logins

Hotel Wi‑Fi Redirect Scam Steals Microsoft 365 Logins

Attackers are compromising hotel and conference center Wi‑Fi gateways and changing DNS settings so business travelers are silently redirected to fake Microsoft 365 login pages. When victims sign in, attackers steal passwords and potentially session tokens, allowing account takeover even when…

July 27, 2026
Fake ShinyHunters Sextortion Demands $2,000

Fake ShinyHunters Sextortion Demands $2,000

A sextortion email campaign is using real leaked email addresses from ShinyHunters-related data dumps to make threats sound credible. The scammers impersonate the “ShinyHunters hacking group,” claim they recorded victims via webcam, and demand $2,000 in Bitcoin within 48 hours. Reporting indicates…

July 27, 2026
Voicemail Lure Drives Microsoft Device-Code Phish

Voicemail Lure Drives Microsoft Device-Code Phish

A voicemail-themed phishing campaign (“Kali365 Ringer”) targeted financial and insurance organizations using a missed-call notification and a Google Sites page to appear legitimate. Victims were redirected through multiple trusted services and instructed to approve a Microsoft device-code login…

July 27, 2026
Hotel Wi‑Fi Hijacks Microsoft 365 Logins

Hotel Wi‑Fi Hijacks Microsoft 365 Logins

Researchers report attackers compromising hotel and conference Wi‑Fi gateway equipment to silently redirect travelers to fake Microsoft 365 sign-in pages, without sending phishing emails. In some cases, attackers also abuse Microsoft device-code login prompts so victims unintentionally approve…

July 27, 2026
Tax and SSA Phish Push Cruciferra Malware Loader

Tax and SSA Phish Push Cruciferra Malware Loader

Researchers report multiple real-world email phishing campaigns that used tax and government-benefit themes to trick people into downloading malware. The campaigns used a “crypter” service called Cruciferra to hide malicious files and help malware run while avoiding detection. Targets included…

July 27, 2026
Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

ReliaQuest reports attackers are compromising public Wi‑Fi “captive portal” gateways (such as in hotels and conference centers) and changing their DNS settings to redirect users to attacker-controlled pages. The goal is to harvest traveling employees’ Microsoft 365 credentials using…

July 27, 2026
Hotel Wi‑Fi DNS Trick Steals Microsoft 365 Logins

Hotel Wi‑Fi DNS Trick Steals Microsoft 365 Logins

Researchers found attackers taking over hotel and conference-center Wi‑Fi gateways and silently redirecting guests to fake Microsoft 365 sign-in pages to steal credentials. In some cases, the attackers also tried to route broader device traffic through a malicious proxy (WPAD) or trick users into…

July 26, 2026
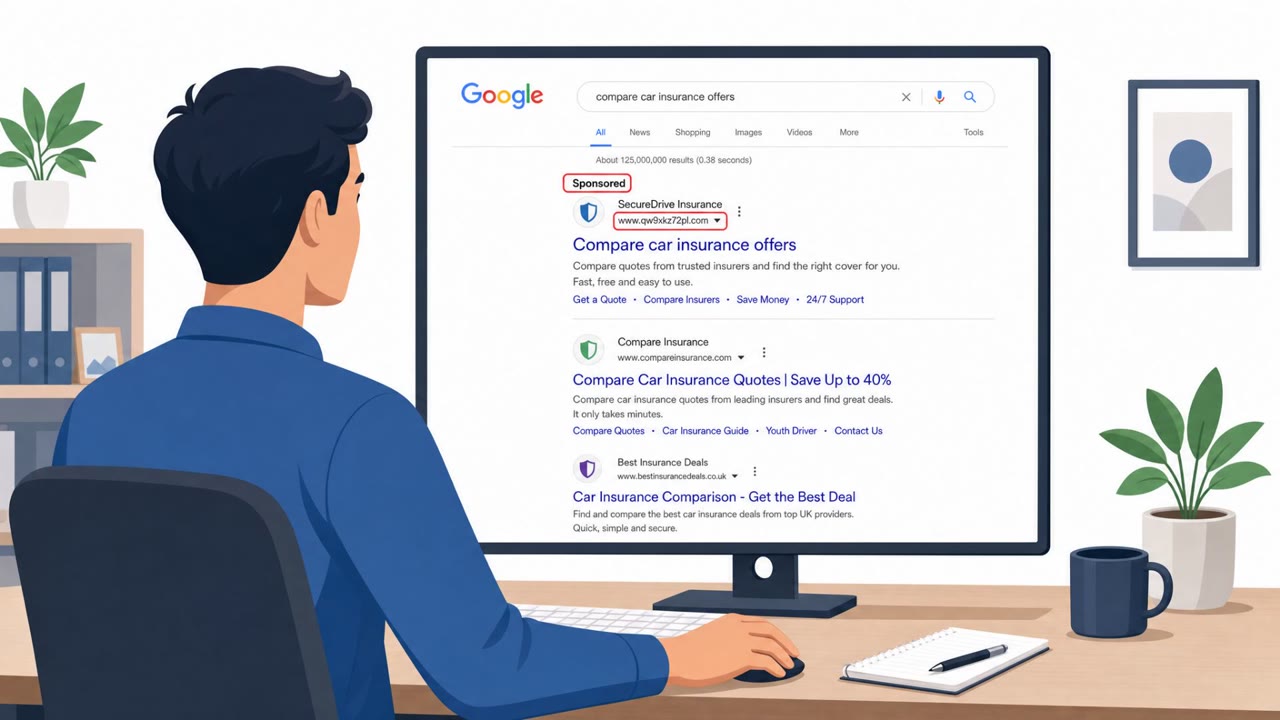
Insurance Phish Turns OTPs Into Live Account Hijacks

Insurance Phish Turns OTPs Into Live Account Hijacks

Researchers observed insurance-themed phishing that doesn’t just steal passwords, it hijacks accounts in real time while the victim is actively logging in. The attack often starts with sponsored Google ads that lead to convincing fake insurance portals, which immediately prompt victims for one-time…

July 25, 2026
Fake Zoom/Teams Calls Used to Steal Crypto Wallets

Fake Zoom/Teams Calls Used to Steal Crypto Wallets

North Korea-linked BlueNoroff is using fake Zoom and Microsoft Teams meeting pages shared from hijacked trusted contacts (often via Telegram) to trick victims into “updating” Zoom/Teams and running malicious commands. The phishing kit also fingerprints the victim’s browser to identify installed…

July 24, 2026
Phishing Link Could Plant a Rogue ChatGPT Agent

Phishing Link Could Plant a Rogue ChatGPT Agent

Researchers described a now-patched flaw ("AgentForger") where a single benign-looking ChatGPT link could silently create and publish an attacker-controlled Workspace Agent inside a company. If an employee was already logged in and had connected apps (like email, Drive, Slack, or Teams), the agent…

July 24, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo