Recent Government Cyber Attacks

Page 5 of 13
ShinyHunters Talked Into Odido via Spoofed Login

ShinyHunters Talked Into Odido via Spoofed Login

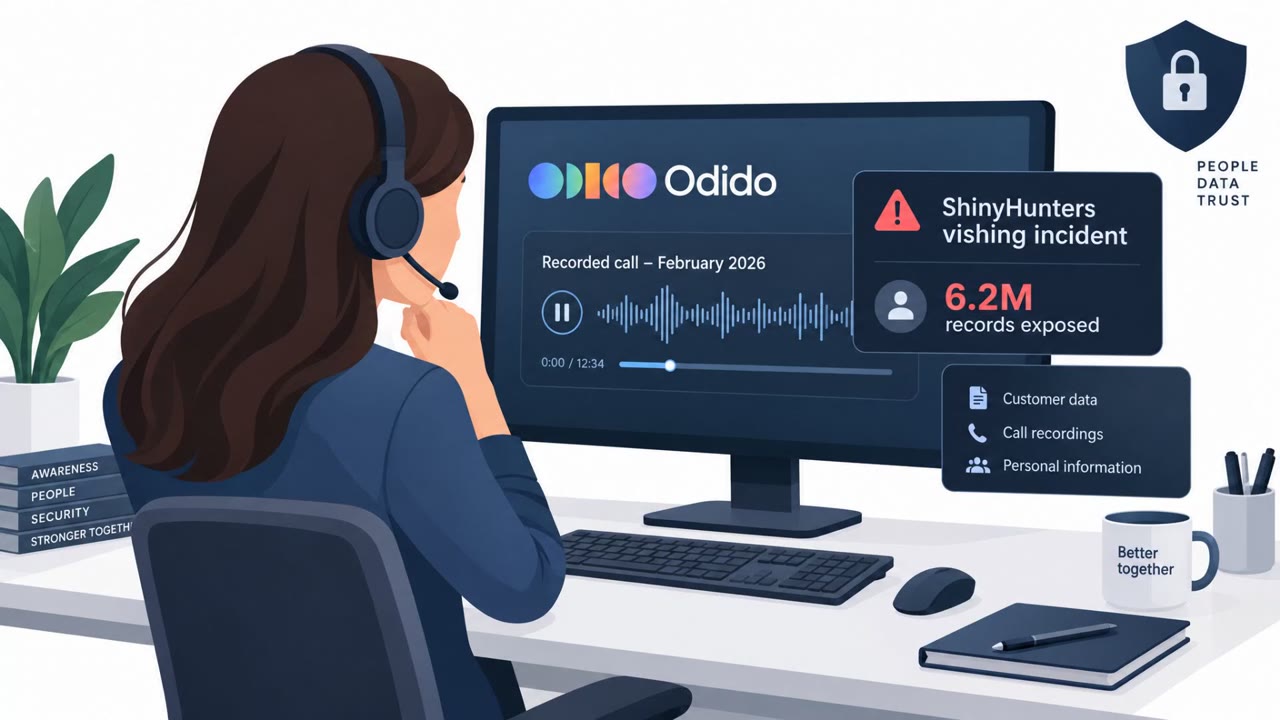
Dutch police are investigating ShinyHunters after a phone-based social engineering incident helped attackers break into Odido, the Netherlands’ largest mobile provider. Investigators say the caller persuaded an employee to log into a spoofed website, which was then used to steal data on more than…

September 28, 2026
Device-Code Phishing and “ClickFix” Lures Spread

Device-Code Phishing and “ClickFix” Lures Spread

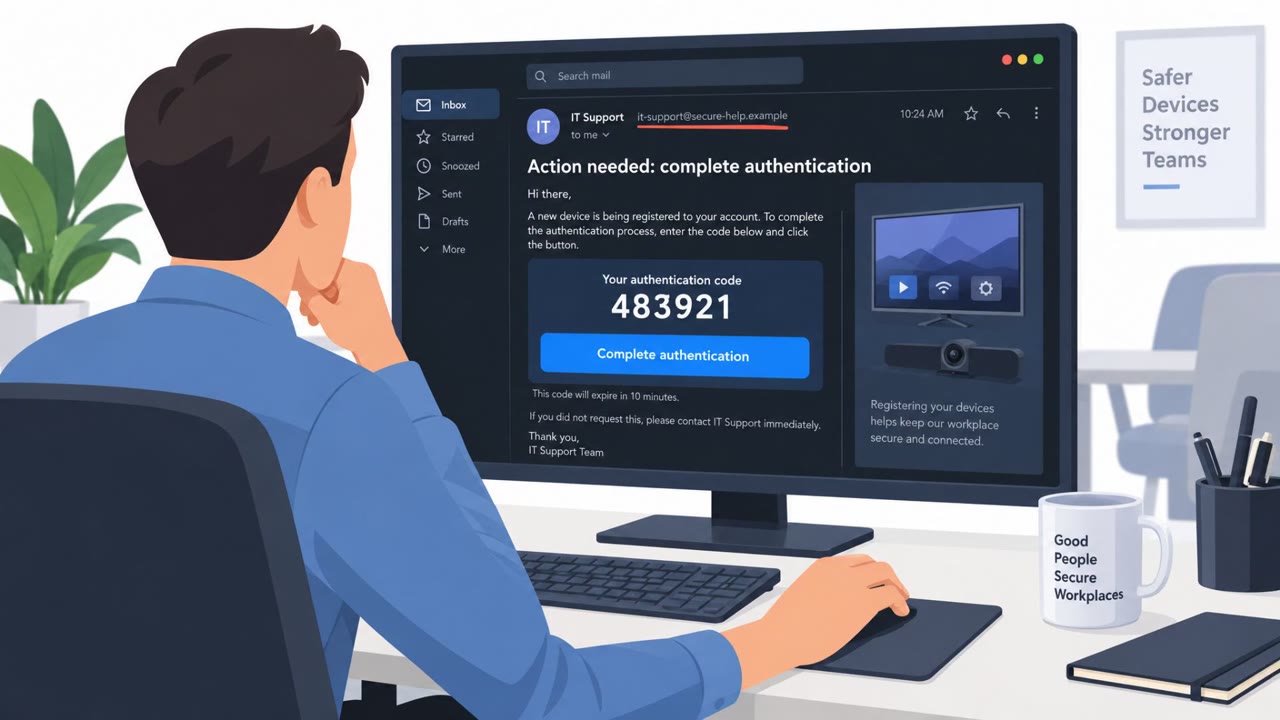
This weekly recap highlights multiple real-world campaigns where attackers trick users into taking actions that grant access, without needing to steal passwords directly. Notable examples include “device code” phishing (victims are instructed to enter a short code to approve an attacker session)…

September 28, 2026
Fake Bank Cards in the Mail Still Work

Fake Bank Cards in the Mail Still Work

Criminals in parts of Europe have been mailing fake “replacement” bank cards or letters claiming a card is expiring, pushing victims to scan a QR code or visit a URL to “activate” the card. The QR code redirects to a fake banking site that harvests login and account details, potentially giving…

September 26, 2026
Soldier Used Others’ Email to Get Exploit Help

Soldier Used Others’ Email to Get Exploit Help

A U.S. Army soldier ("Kiberphant0m") tied to major telecom data thefts was sentenced to 70 months in prison. Prosecutors say that while jailed, he used other inmates’ email accounts to get someone on the outside to ask commercial AI tools for vulnerability details and even “real world working”…

September 25, 2026
Rust Maintainers Phished via Fake “Conference Call”

Rust Maintainers Phished via Fake “Conference Call”

An unknown group suspected to be North Korean state hackers targeted Rust language team members and high-profile package (“crate”) maintainers with phishing that lures victims into a fake conference call. When the victim tries to join, they are told they must install a “video codec” or update…

September 25, 2026
AI Search Results Turn Into Phishing Traps

AI Search Results Turn Into Phishing Traps

This bulletin describes multiple real-world scams where attackers make fake pages and messages look like routine, trusted experiences (search answers, Google login pop-ups, “giveaways,” and official-sounding calls). Examples include a fake Claude Max giveaway using a convincing fake Google sign-in…

September 24, 2026
Fake NGO Sites Lure Victims Into Chrome 0-Day Chain

Fake NGO Sites Lure Victims Into Chrome 0-Day Chain

China-linked actor UTA0565 sent phishing emails that pushed recipients to click spoofed links to fake media/NGO websites. Visiting the sites triggered a Chrome-to-Windows zero-day exploit chain that escaped the browser sandbox and installed CLEANGULP malware for remote control.

September 23, 2026
China-Linked Phish Uses Fake Sites to Exploit Chrome

China-Linked Phish Uses Fake Sites to Exploit Chrome

Researchers say a China-aligned group (UTA0565) sent phishing emails to government targets and used multiple fake websites to lure victims into visiting pages that triggered a Chrome-and-Windows zero-day exploit chain. The messages used political advocacy themes and spoofed well-known organizations…

September 22, 2026
SideCopy Phishes Indian Universities With Fake Docs

SideCopy Phishes Indian Universities With Fake Docs

Pakistan-linked APT group SideCopy expanded from targeting Indian government entities to targeting Indian academic institutions using spear-phishing. The emails deliver a weaponized ZIP containing a fake “document” shortcut that launches mshta.exe to pull down and run malware, ultimately installing…

September 22, 2026
Fake AI Recruiters Hit 30K Devices Worldwide

Fake AI Recruiters Hit 30K Devices Worldwide

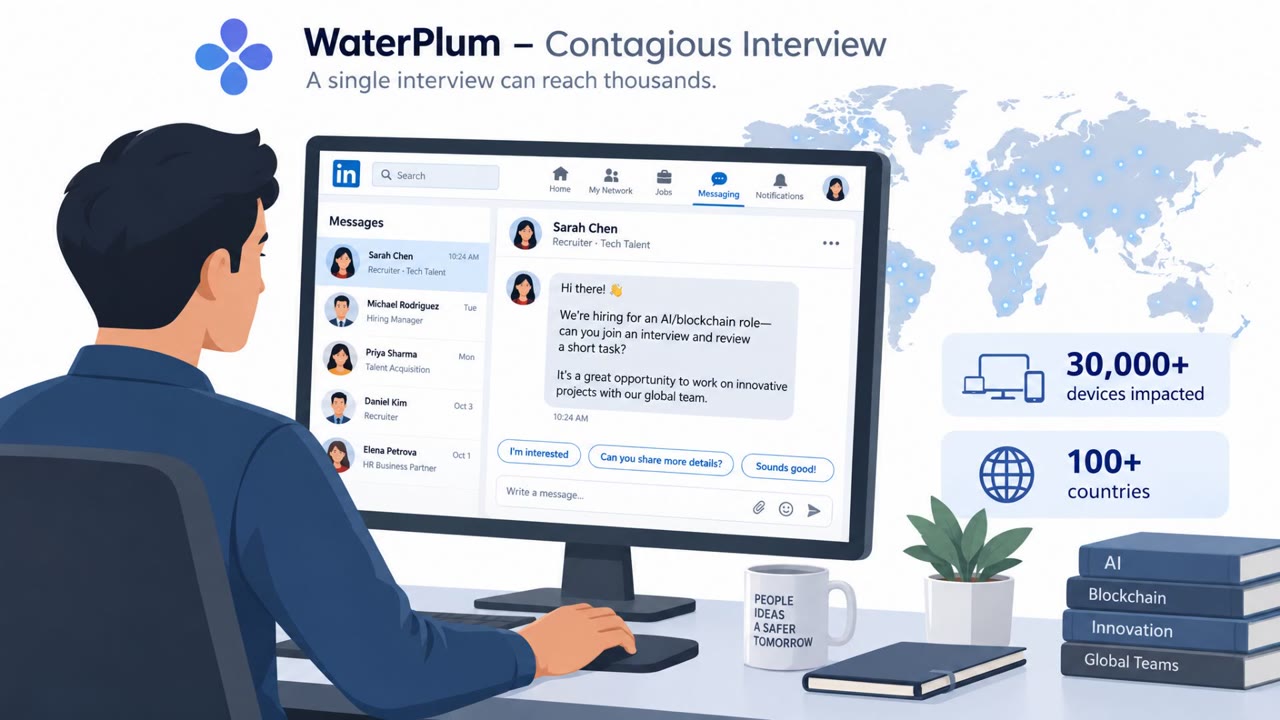
A weekly threat bulletin highlights a North Korea–linked campaign where attackers posed as AI or blockchain employers to trick IT professionals into getting infected and losing cryptocurrency. It also notes a phishing kit that abuses Microsoft’s legitimate device login flow to gain long-lasting…

September 22, 2026
Trusted Channels Hijacked for Phishing and Malware

Trusted Channels Hijacked for Phishing and Malware

The article describes multiple real-world social engineering operations this week, including phishing sent from a legitimate Trezor newsletter channel and malware pushed through a verified HBO Max Reddit ad account. It also highlights a large-scale network of fake online stores impersonating real…

September 18, 2026
Revolut Tricked by Fake Govt Requests for Months

Revolut Tricked by Fake Govt Requests for Months

Attackers allegedly stole Revolut customer data by sending fraudulent “government” legal requests for roughly five months. The requests appeared legitimate because they came from a compromised government employee email account, leading Revolut to comply and disclose sensitive personal and financial…

September 17, 2026
Fake Movie Torrent Drops MovieReaper Trojan

Fake Movie Torrent Drops MovieReaper Trojan

A real malware campaign dubbed “MovieReaper” infected users who tried to download popular movies from torrent trackers. Attackers abused a compromised public torrent-file repository so that magnet links returned a different torrent that downloaded a Windows .exe disguised as a movie file, which…

September 17, 2026
Iranian “Chosen Brick” Lures Sent via Telegram

Iranian “Chosen Brick” Lures Sent via Telegram

UK, US, and Dutch agencies warned that Iranian state-linked actors used social messaging apps to build trust with dissidents, journalists, and activists before sending disguised files that install Windows malware. The attackers often impersonated someone the target already knows or “technical…

September 17, 2026
Fake Helpdesk Passkey Setup Steals Cloud Access

Fake Helpdesk Passkey Setup Steals Cloud Access

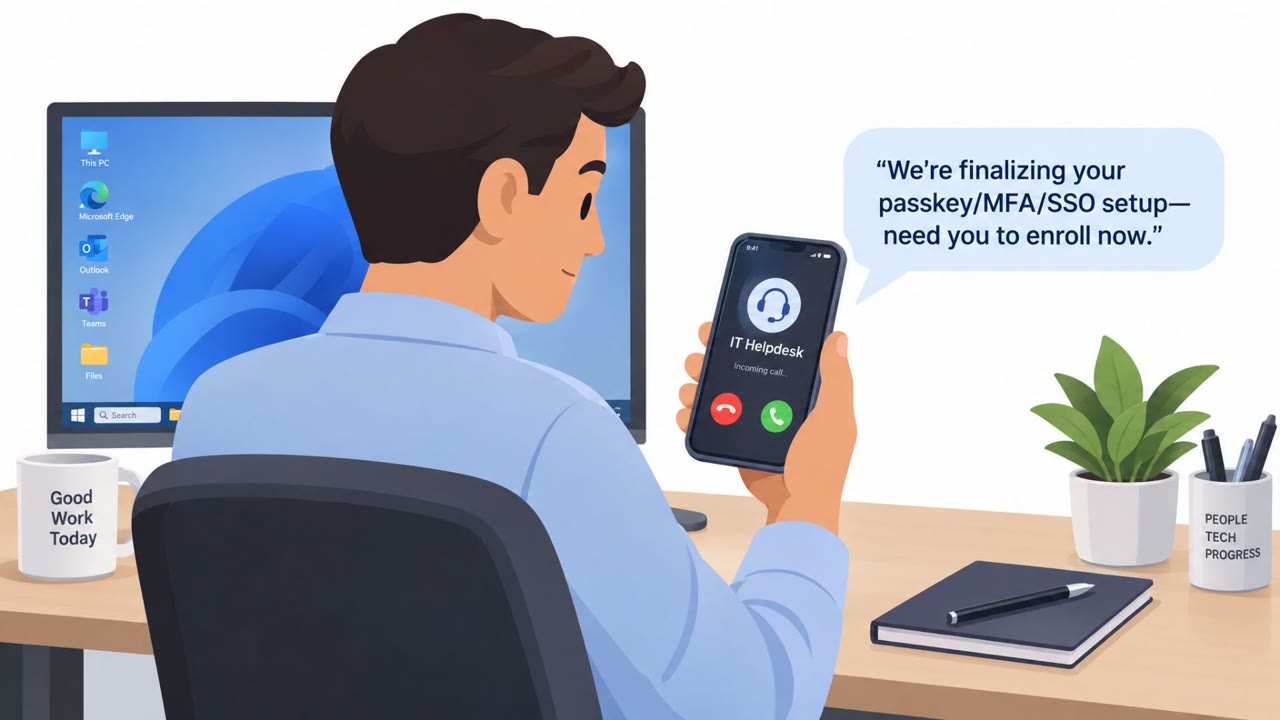
The article describes real intrusions where attackers impersonate a company helpdesk and lure employees into "passkey, MFA, or SSO setup" steps. Victims are sent links via text (often to personal phones), leading to account takeover through adversary-in-the-middle phishing or device-code…

September 16, 2026
Fake Police Emails Tricked Revolut Into Sharing Data

Fake Police Emails Tricked Revolut Into Sharing Data

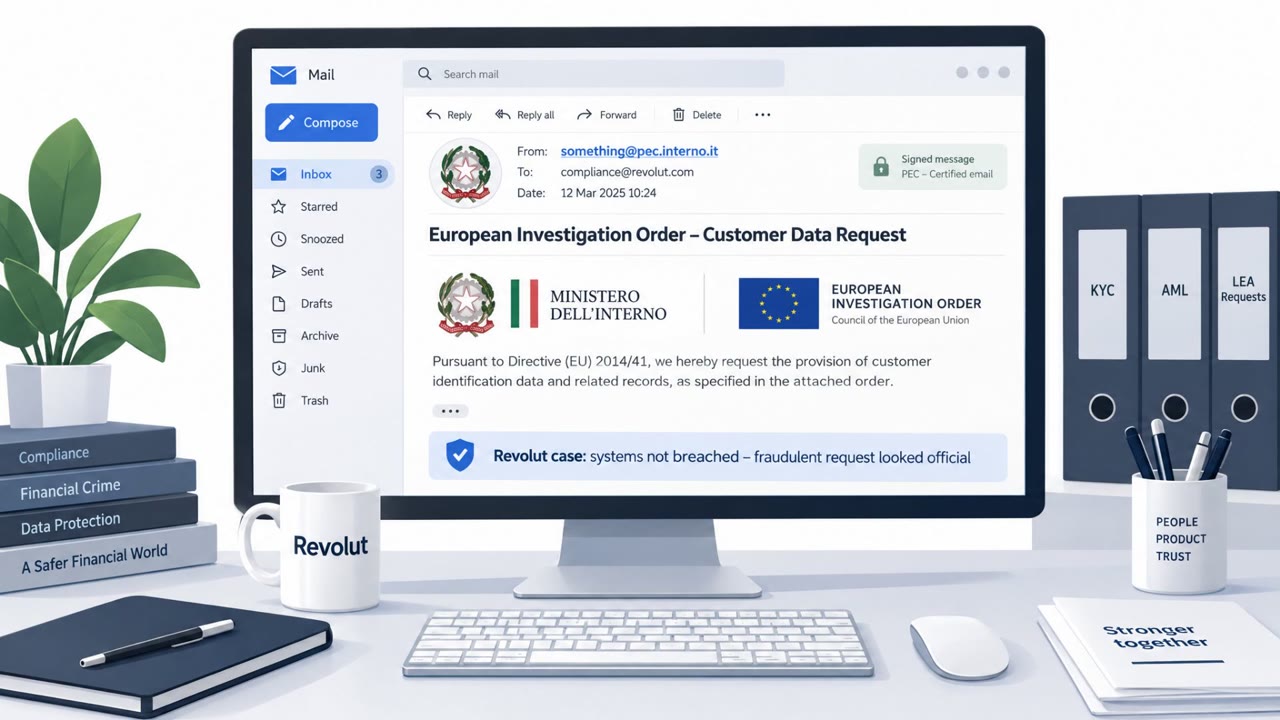
Threat actors allegedly used a compromised Italian government PEC email account to impersonate law enforcement and send fraudulent information requests to Revolut. Revolut says its systems were not breached, but it received requests that appeared to come from a legitimate government domain and…

September 16, 2026
N0va Phishkit Uses Trusted Apps to Steal SSO Access

N0va Phishkit Uses Trusted Apps to Steal SSO Access

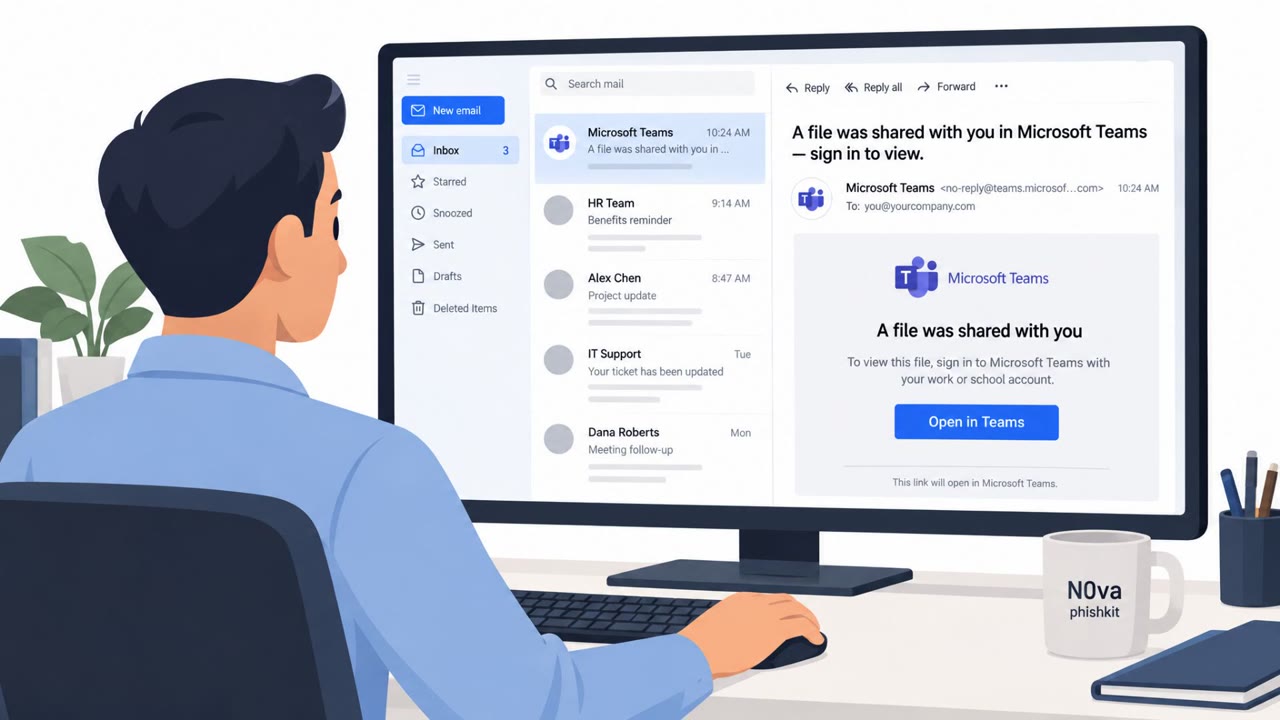
A phishing kit dubbed N0va is targeting organizations in North America and Europe by impersonating familiar business services (like Microsoft Teams/SharePoint and DocuSign) and pushing victims through legitimate sign-in flows. By capturing authentication tokens rather than dropping obvious malware,…

September 16, 2026
Iranian Spies Lure Targets via WhatsApp to Drop Malware

Iranian Spies Lure Targets via WhatsApp to Drop Malware

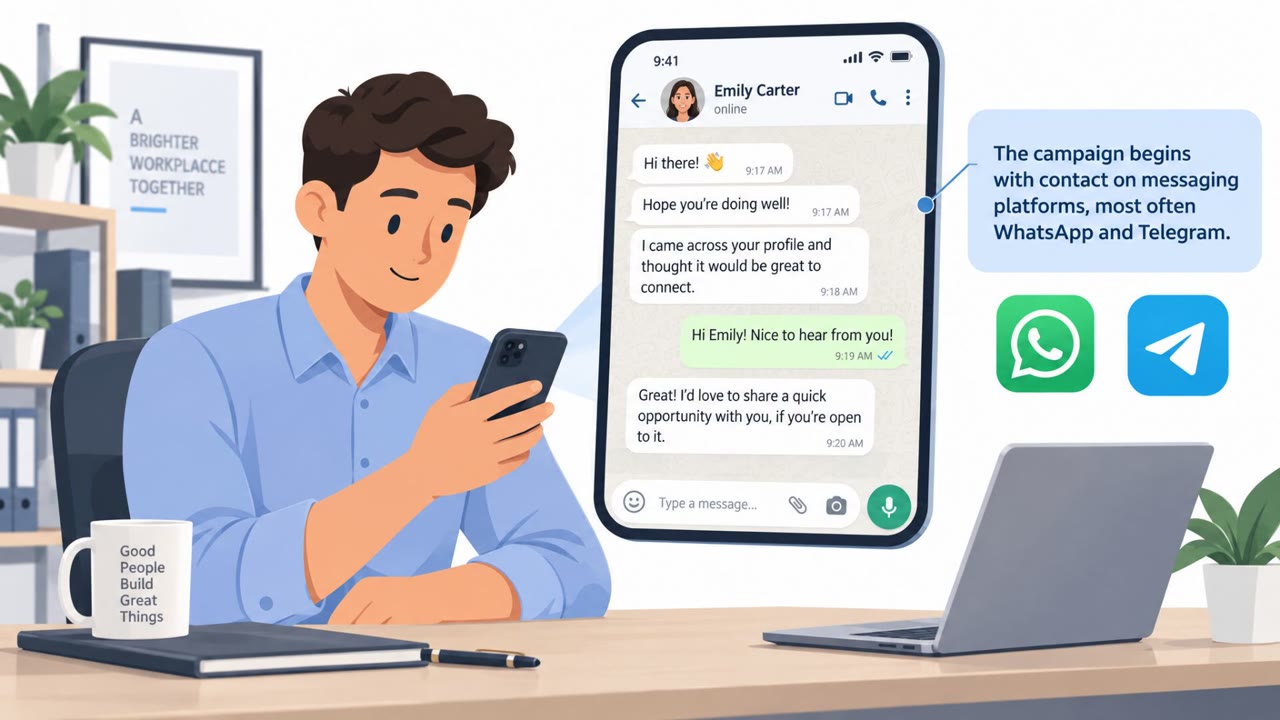
A joint UK-US-Dutch advisory warns Iranian state-backed cyber actors are targeting dissidents, activists, and journalists by first contacting them on WhatsApp or Telegram and building trust. The attackers then persuade victims to open a malicious file disguised as legitimate software (or even MRI…

September 16, 2026
Iran-Backed Spyware Uses Fake Support Chats

Iran-Backed Spyware Uses Fake Support Chats

UK and allied agencies warn that a Tehran-backed operation is targeting dissidents, activists, and journalists using social engineering to trick them into installing spyware called “Chosen Brick.” Attackers build trust on social media by impersonating known contacts or “technical support,” then…

September 16, 2026
Iran Uses WhatsApp Lures to Drop Chosen Brick Malware

Iran Uses WhatsApp Lures to Drop Chosen Brick Malware

Western government agencies warn that Iranian state-backed actors are using WhatsApp and Telegram messages to trick targeted individuals into installing a Windows surveillance and data-stealing tool called “Chosen Brick.” The attackers build trust by impersonating known people or organizations,…

September 15, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo