Recent Government Cyber Attacks

Page 3 of 13
Ransomware Crew Used Trusted IT Referral

Ransomware Crew Used Trusted IT Referral

Federal investigators are examining alleged links between ShinyHunters and ransomware negotiation executives. The article also documents a real Dharma ransomware exchange in which the attacker steered a victim toward an alleged Canadian IT intermediary, using a reassuring “guarantees” offer to keep…

October 19, 2026
Deepfake Election Video Told Voters Not to Vote

Deepfake Election Video Told Voters Not to Vote

A real deepfake during Ireland’s 2025 presidential election falsely depicted candidate Catherine Connolly saying the election was cancelled, that she was withdrawing, and that her supporters should not vote. The UK Electoral Commission is developing a rapid detection system because similar false…

October 19, 2026
Copilot Flaw Turned AI Into Data Exfiltration Tool

Copilot Flaw Turned AI Into Data Exfiltration Tool

Researchers disclosed SearchLeak, a Microsoft 365 Copilot Enterprise vulnerability chain that reportedly let a single crafted-link click turn a user’s AI assistant into a tool for collecting and sending out sensitive data. The attack abused prompt injection and trusted Microsoft infrastructure,…

October 19, 2026
Hijacked Irish Police Accounts Push Crypto Scam

Hijacked Irish Police Accounts Push Crypto Scam

Attackers hijacked two official Irish police X/Twitter accounts and used the trusted accounts to promote a fake cryptocurrency airdrop. The posts directed followers to a link that could trick them into giving up cryptocurrency-wallet keys, allowing criminals to drain their funds.

October 18, 2026
Hijacked CDU Mailbox Sends 6,500 Phishing Emails

Hijacked CDU Mailbox Sends 6,500 Phishing Emails

Attackers broke into the email account of a CDU Heilbronn district executive and used the trusted mailbox to send roughly 6,500 fake messages. The emails used an event invitation as a lure and directed recipients to a link for a supposed document, making this a credible internal-email phishing…

October 17, 2026
Fake Sudo Prompt Steals Gov Admin Passwords

Fake Sudo Prompt Steals Gov Admin Passwords

Unit 42 reported an espionage-focused intrusion cluster (CL-UNK-1211) targeting government and state-affiliated Linux infrastructure from Oct 2025 to Apr 2026. While much of the campaign is technical (web shells, RATs and reverse shells), it also includes credential theft that relies on deceiving…

October 15, 2026
Silent Lynx Used Gov Emails to Lure Targets

Silent Lynx Used Gov Emails to Lure Targets

Researchers say the Kazakhstan-linked group “Silent Lynx” has run real espionage campaigns across Central Asia, targeting government bodies and energy organizations. The reported entry method relied heavily on spear‑phishing sent from compromised government email accounts, sometimes using trusted…

October 15, 2026
Silent Lynx Phishes CIS Govs With Decoy Documents

Silent Lynx Phishes CIS Govs With Decoy Documents

Researchers report that the threat actor Silent Lynx ran multiple real-world spear‑phishing campaigns against government organizations across Central Asia and the wider CIS region. Victims were lured with official-looking documents (e.g., diplomatic letters, airspace applications, and oil refinery…

October 15, 2026
Microsoft Busts Phishing Kits Behind 1B Scams

Microsoft Busts Phishing Kits Behind 1B Scams

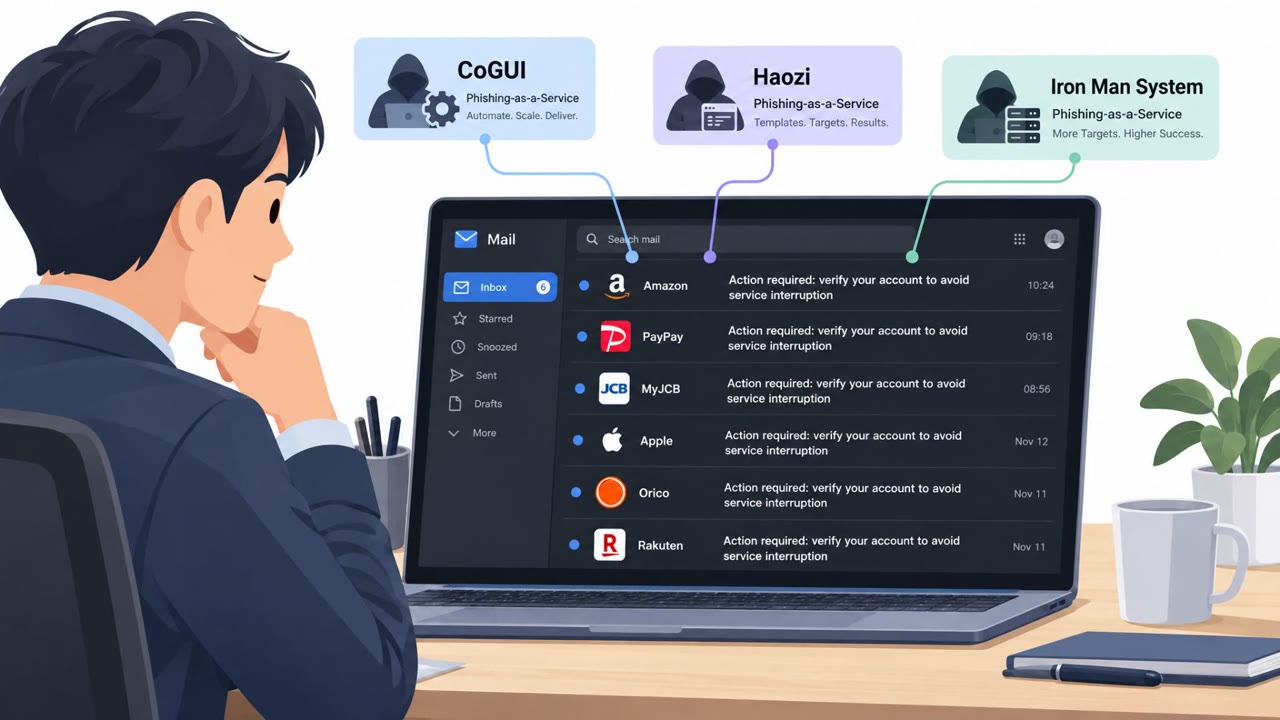
Microsoft and partners disrupted three "phishing-as-a-service" kits that enabled criminals to send more than a billion phishing emails and SMS messages worldwide. The kits provided ready-made fake brand pages (government, finance, logistics, consumer brands) designed to steal login credentials and…

October 15, 2026
Silent Lynx Lures CIS Officials With Fake Diplomacy Docs

Silent Lynx Lures CIS Officials With Fake Diplomacy Docs

Researchers tracked Kazakhstan-nexus group UAT-6275 (TAG-193) targeting government organizations across Central Asia and the wider CIS using convincing decoy documents tied to diplomacy and energy. The campaigns used malicious files (macro-enabled Word docs, shortcuts, and a WinRAR exploit) to…

October 15, 2026
Iron Man Phishing Kit Hits 130 Countries

Iron Man Phishing Kit Hits 130 Countries

Researchers uncovered a commercial phishing-kit-as-a-service called “Iron Man System” that lets criminals quickly deploy fake brand pages (postal/courier, toll fines, tax, banks, telecoms, loyalty programs) to steal victim data. The operation appears active and professionally maintained, with…

October 14, 2026
Microsoft Disrupts 3 Massive Phishing Platforms

Microsoft Disrupts 3 Massive Phishing Platforms

Microsoft says it used a U.S. court order to seize and redirect domains tied to three Chinese-run phishing platforms that helped send hundreds of millions of scam messages worldwide. The platforms provided ready-made fake pages and messages impersonating trusted organizations, mainly to steal…

October 14, 2026
Microsoft Takes Down 1B-Message Phishing Bazaar

Microsoft Takes Down 1B-Message Phishing Bazaar

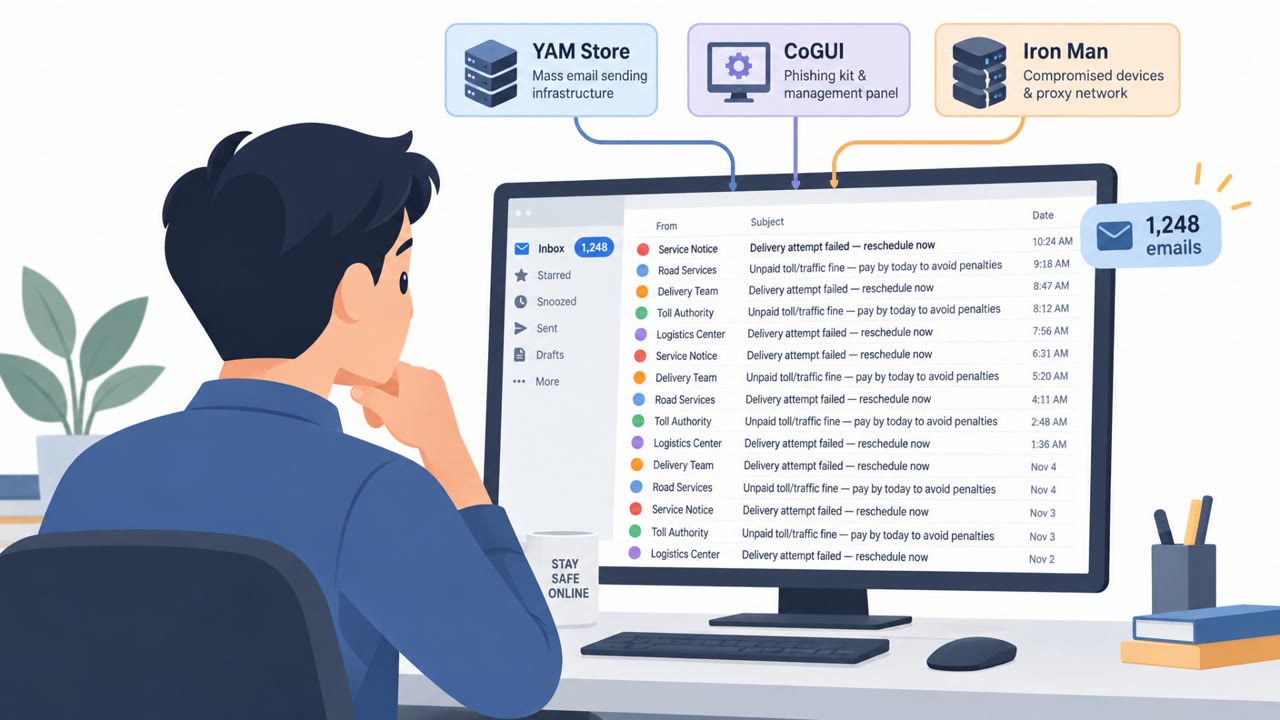
Microsoft and Health-ISAC disrupted a Chinese-language phishing marketplace ecosystem (YAM Store, CoGUI, and Iron Man) that enabled criminals to send over a billion malicious messages globally. The services sold phishing kits, compromised accounts, and infrastructure, and were frequently used to…

October 14, 2026
Microsoft Busts Massive Phishing Kit Network

Microsoft Busts Massive Phishing Kit Network

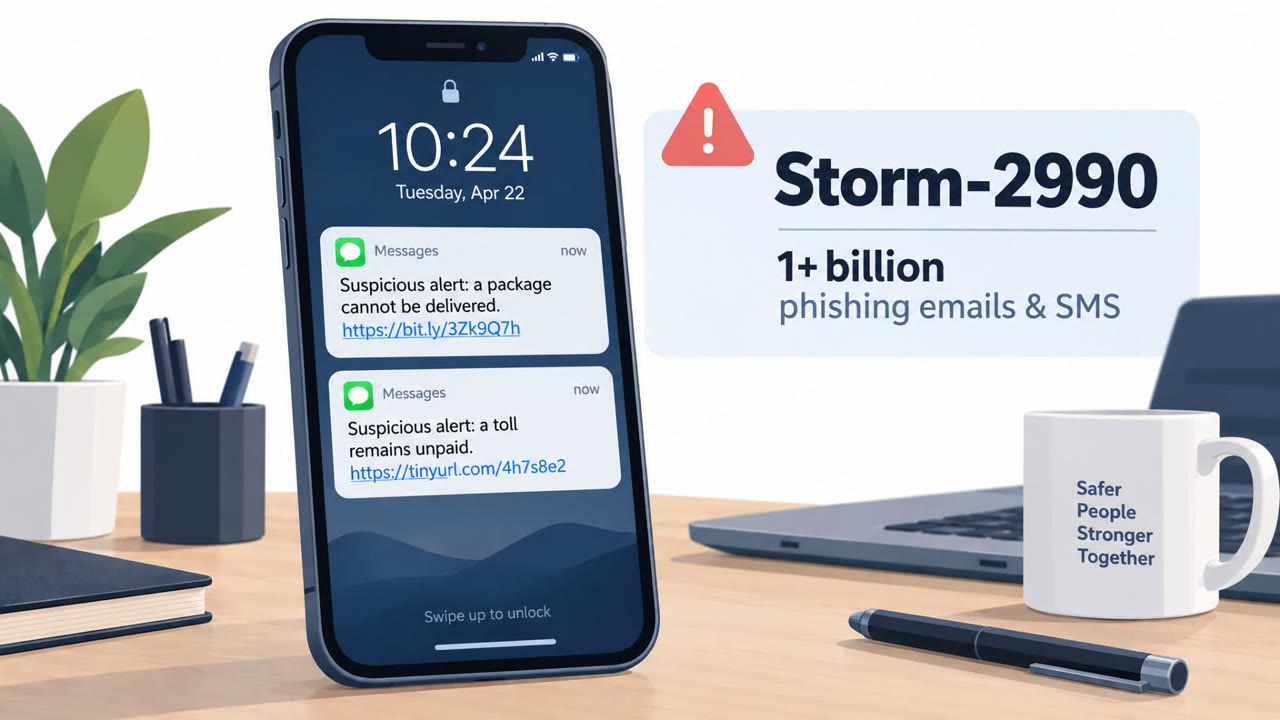
Microsoft and partners disrupted a Chinese-language phishing kit ecosystem (tracked as Storm-2990) used to send over 1 billion malicious email and SMS messages to more than 75,000 organizations worldwide. The kits used common “urgent alert” scams (delivery issues, unpaid tolls, bank or tax…

October 14, 2026
North Korean Fake IT Workers Ran US Laptop Farms

North Korean Fake IT Workers Ran US Laptop Farms

US authorities arrested two Americans accused of helping North Korean “fake IT workers” get hired remotely at US companies and route company laptops into US-based “laptop farms.” The scheme used stolen or fake identities and location-masking tools so overseas workers could appear to be working from…

October 14, 2026
ShinyHunters Used Phone Pretexts to Bypass MFA

ShinyHunters Used Phone Pretexts to Bypass MFA

A Register podcast transcript describes real-world activity linked to the ShinyHunters cyber extortion crew, including an FBI-related breach and subsequent arrests. It also notes the group’s reliance on social engineering phone calls where attackers impersonate locked-out contractors or employees…

October 12, 2026
Fake Dubai Airports Recruiters Target Developers

Fake Dubai Airports Recruiters Target Developers

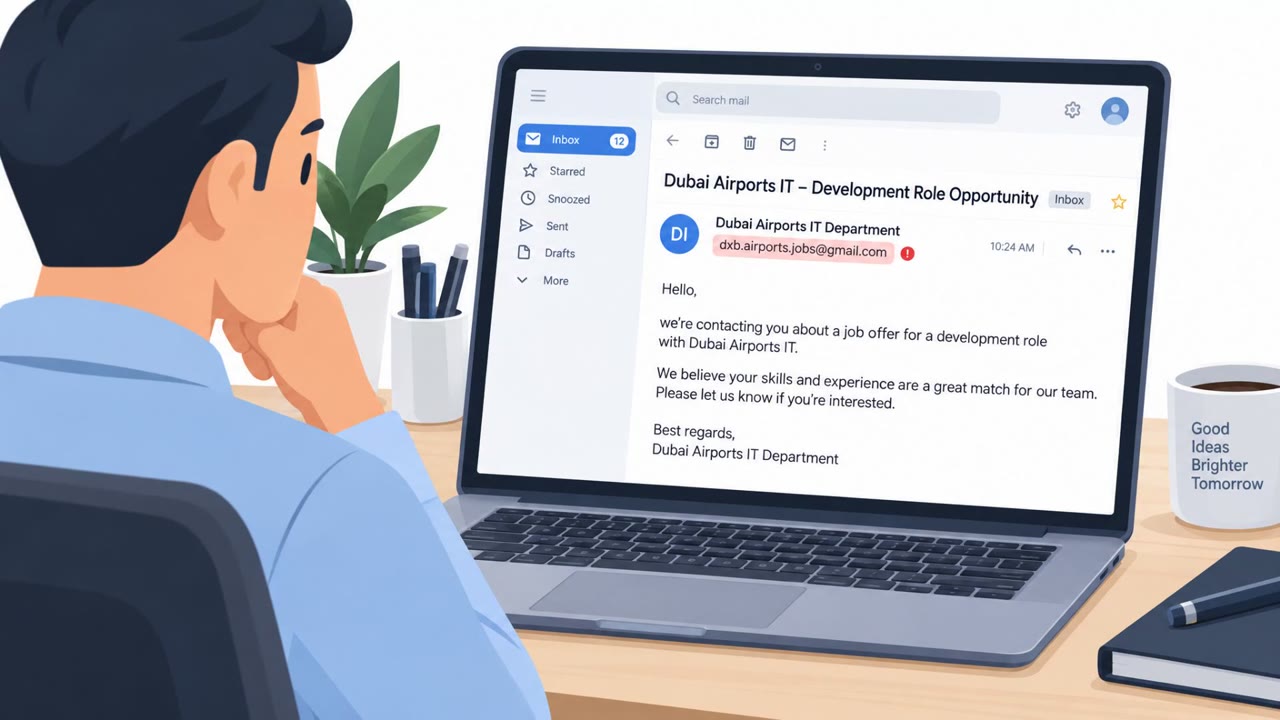
Researchers linked an Iran-aligned campaign to recruitment-themed social engineering that tricked a targeted Iraqi software engineer into downloading a fake "Dubai Airports" careers portal and then opening a trojanized Visual Studio coding test. The lure abused normal developer workflows so malware…

October 10, 2026
MATCHBOIL Spearphish Tricks Users Into Running Script

MATCHBOIL Spearphish Tricks Users Into Running Script

ESET reports that Russia-aligned group UAC-0099 is using spearphishing emails with malicious links to deliver a downloader called MATCHBOIL. The attack relies on tricking a person into manually running a downloaded VBScript, which then fetches and installs further malware and sets up persistence…

October 9, 2026
Fake Police Reply Lures Ukraine Officials

Fake Police Reply Lures Ukraine Officials

Russia-aligned actor UAC-0099 targeted Ukrainian government personnel using malware (ASHVEIN) that steals credentials and enables remote control. A key lure described is a malicious .NET file that shows a decoy Microsoft Word document pretending to be an official response from Ukraine’s National…

October 8, 2026
Fake Court Summons Phish Drops MatchBoil Malware

Fake Court Summons Phish Drops MatchBoil Malware

Researchers say the Russia-aligned group UAC-0099 has been phishing Ukrainian organizations with malicious links that install a data-harvesting malware called MatchBoil. The emails have included lures like fake Ukrainian court summonses, and clicking the link leads to downloading an archive that…

October 8, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo