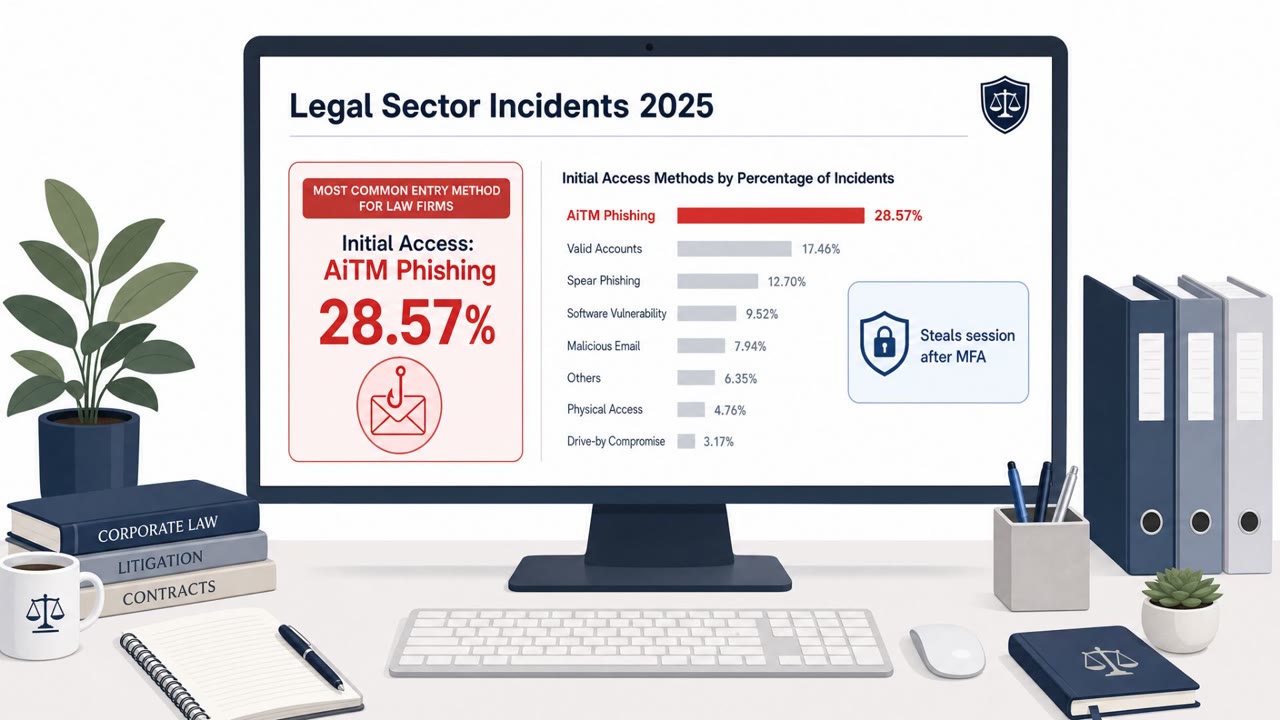
AiTM Phishing Now #1 Break-In Method for Law Firms
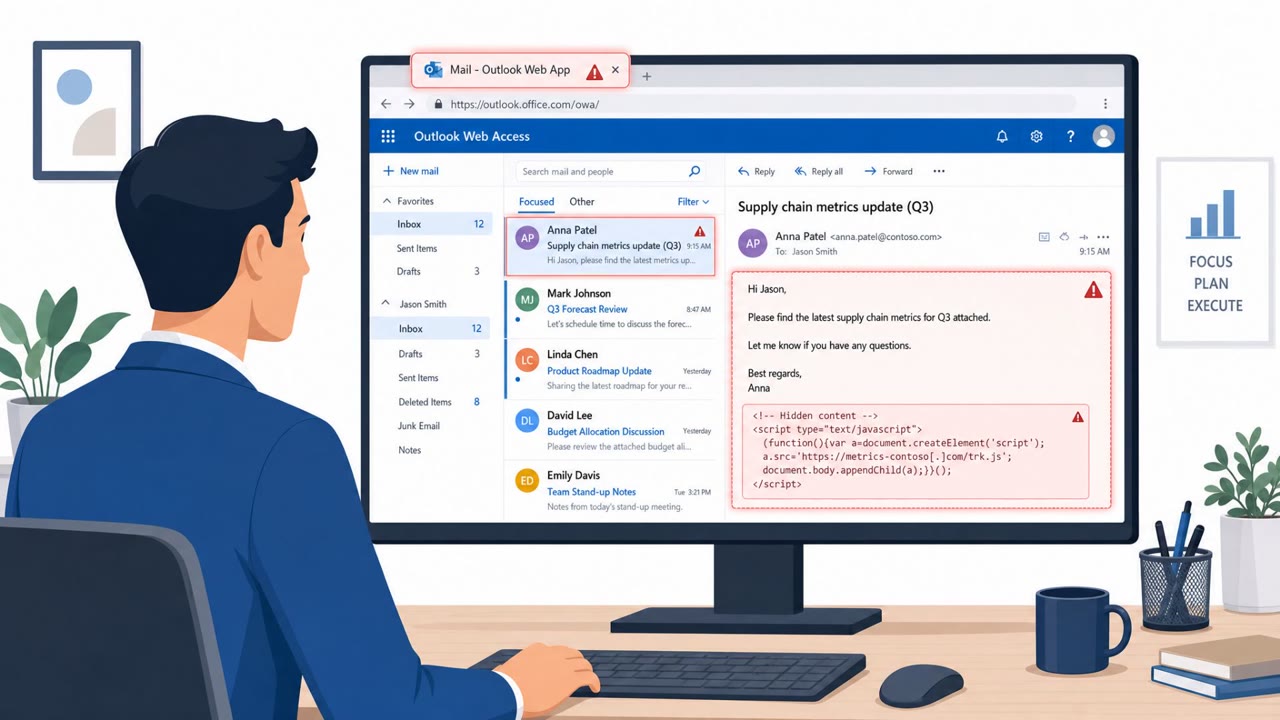
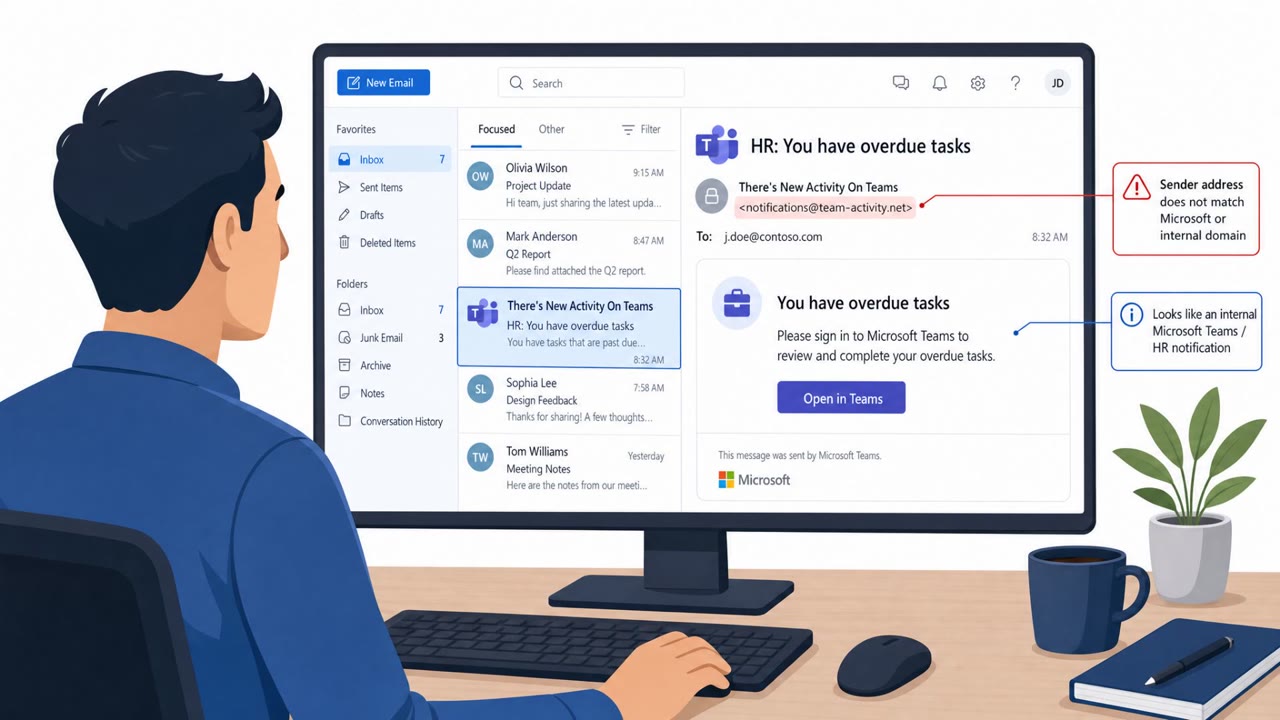
A legal-sector threat intel report says adversary-in-the-middle (AiTM) phishing is now the most common way attackers gain initial access to law firms, because it can bypass MFA by stealing valid session cookies. The report highlights deadline-driven lures (fake document/court portal errors) and…
July 31, 2026