Threat Watcher

Page 41 of 51
“Adult TikTok” Search Lures Drive Scam Funnels

“Adult TikTok” Search Lures Drive Scam Funnels

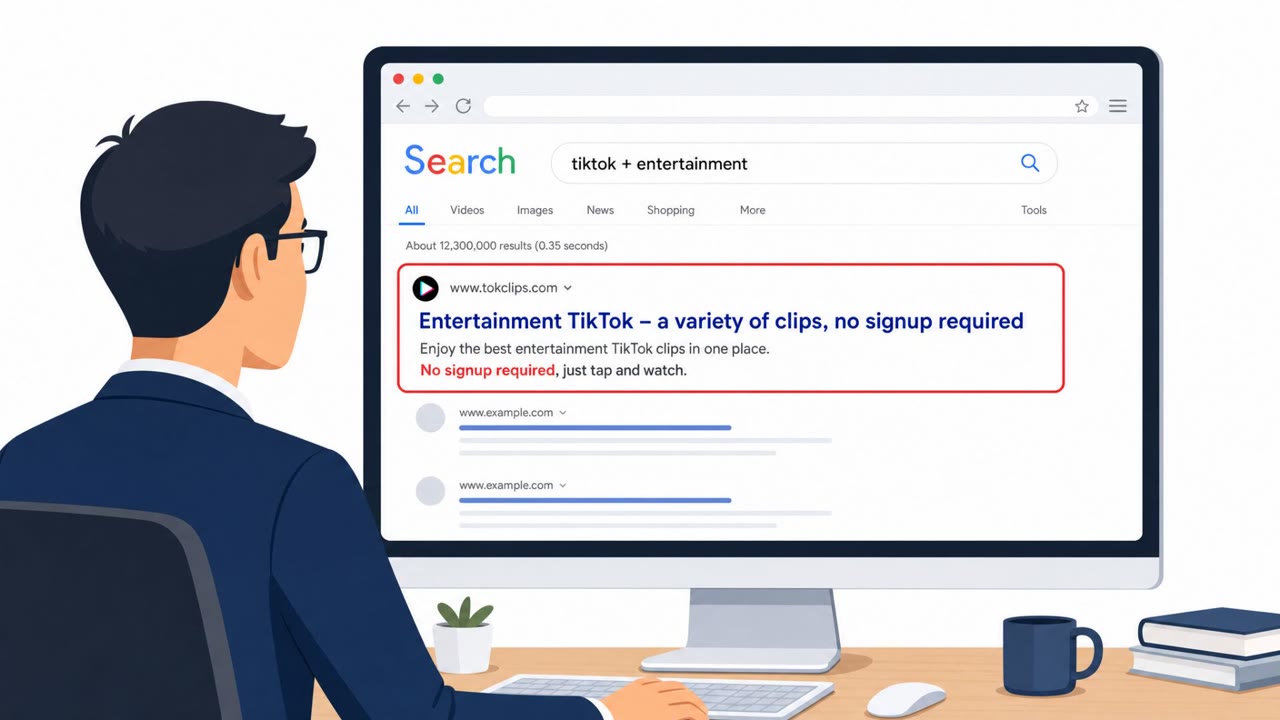
Scammers are using fake webpages that appear in search results for “TikTok” plus adult terms, promising “exclusive” explicit videos. Instead of any real content, the pages push visitors into an ad/affiliate funnel that collects emails, payment cards for fake “age verification,” or tricks people…

August 3, 2026
Poisoned PRs Let One AI Agent Control Another

Poisoned PRs Let One AI Agent Control Another

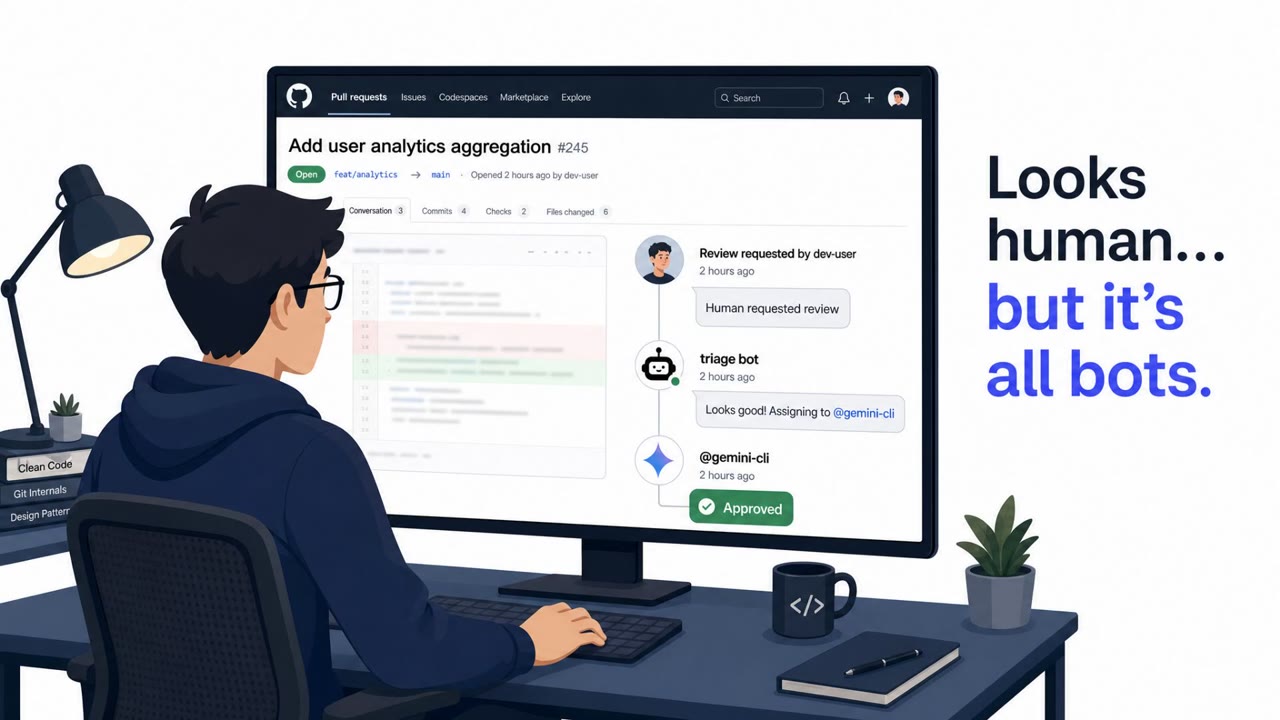
Researchers found a real-world workflow flaw in Google’s Agent Development Kit (Python) repo where a low-privilege AI triage bot could be manipulated with prompt injection to trigger a higher-privilege maintainer agent. The attack uses “poisoned” pull requests to create a believable review/approval…

August 3, 2026
Deepfake Job Interviews and Vishing Hit Enterprises

Deepfake Job Interviews and Vishing Hit Enterprises

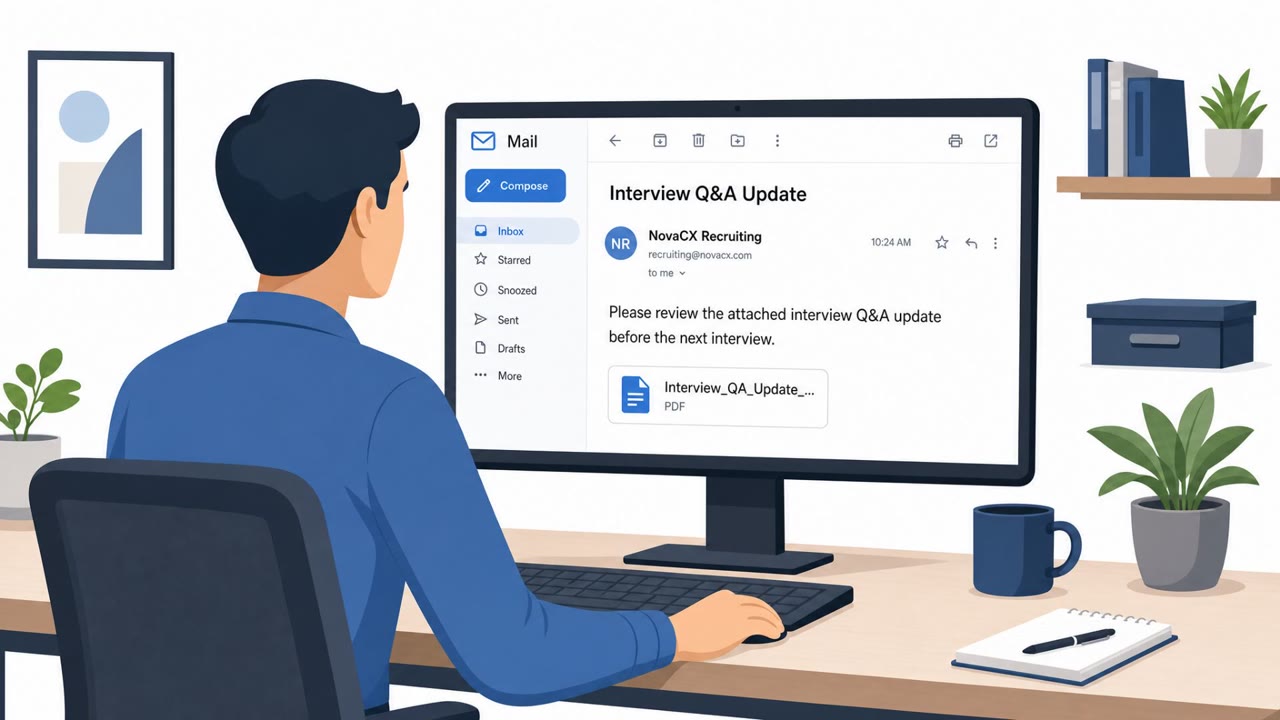
CrowdStrike warns that attackers are using AI to make social engineering faster and more convincing, including AI-generated resumes and deepfake job interviews to infiltrate companies. The report also describes vishing campaigns that quickly pivot from stealing accounts to stealing data from SaaS…

August 3, 2026
SVR Hijacks Hotel Wi‑Fi to Push Malware

SVR Hijacks Hotel Wi‑Fi to Push Malware

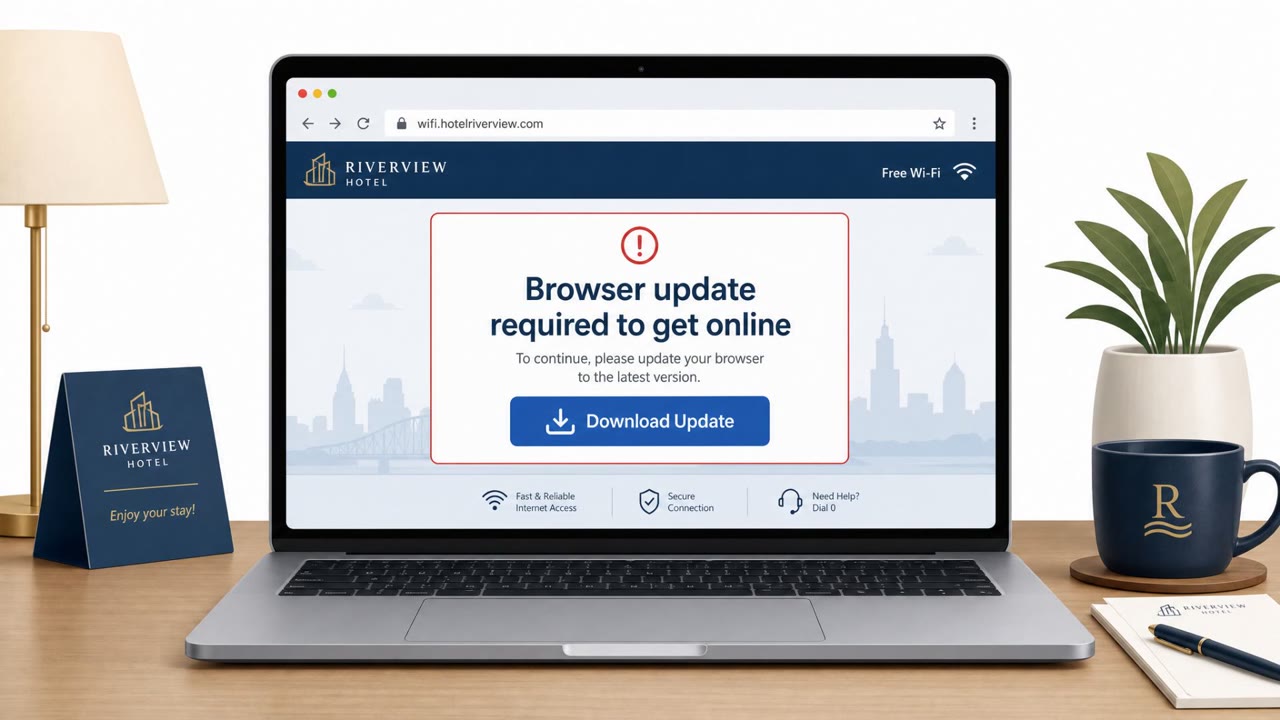
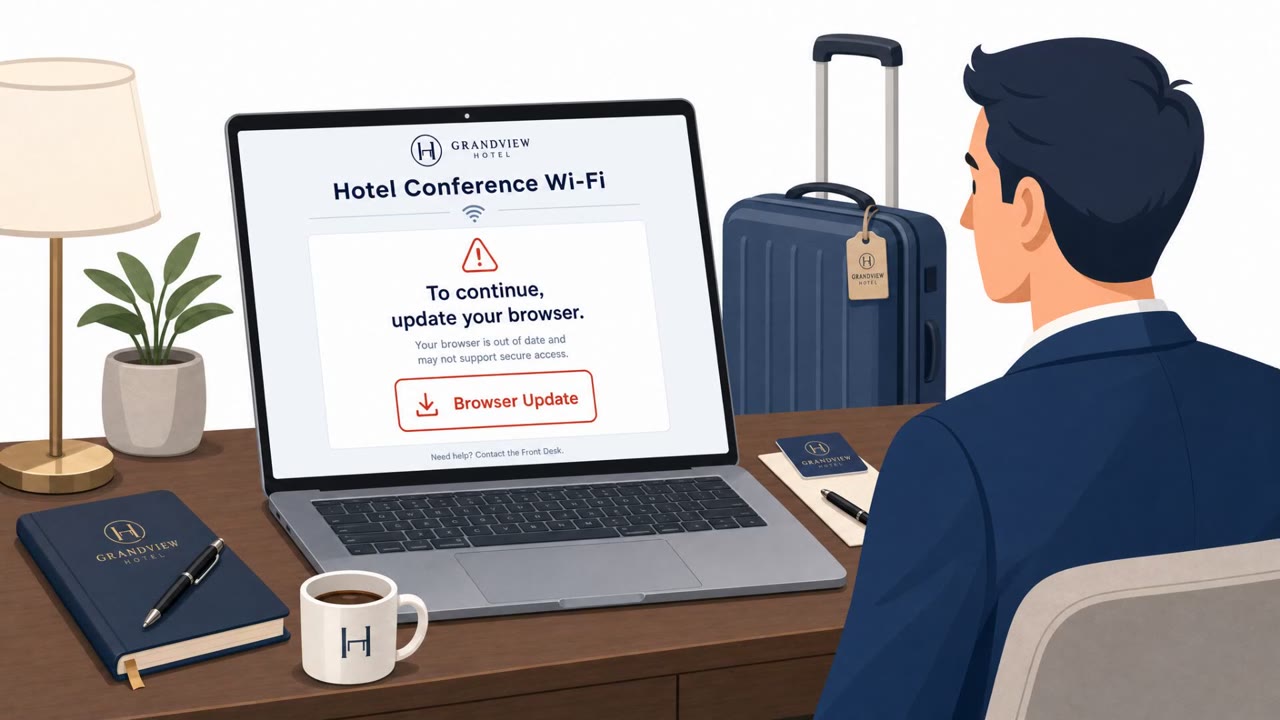
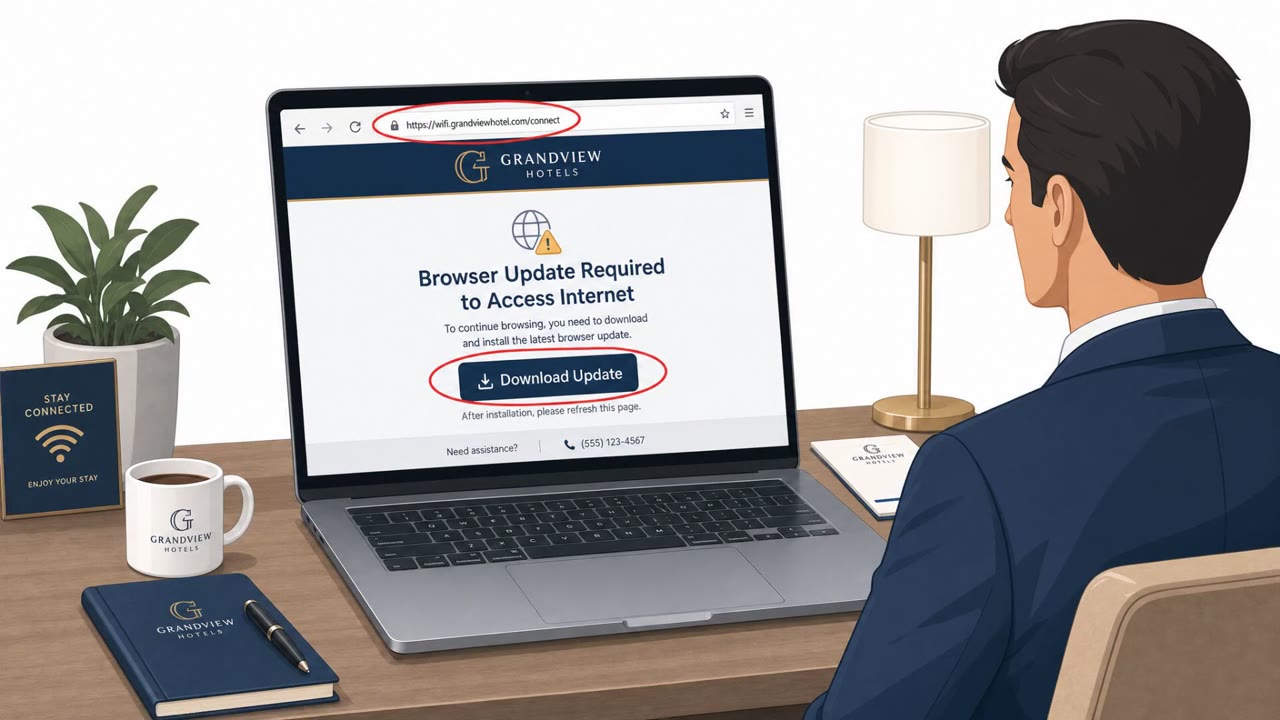
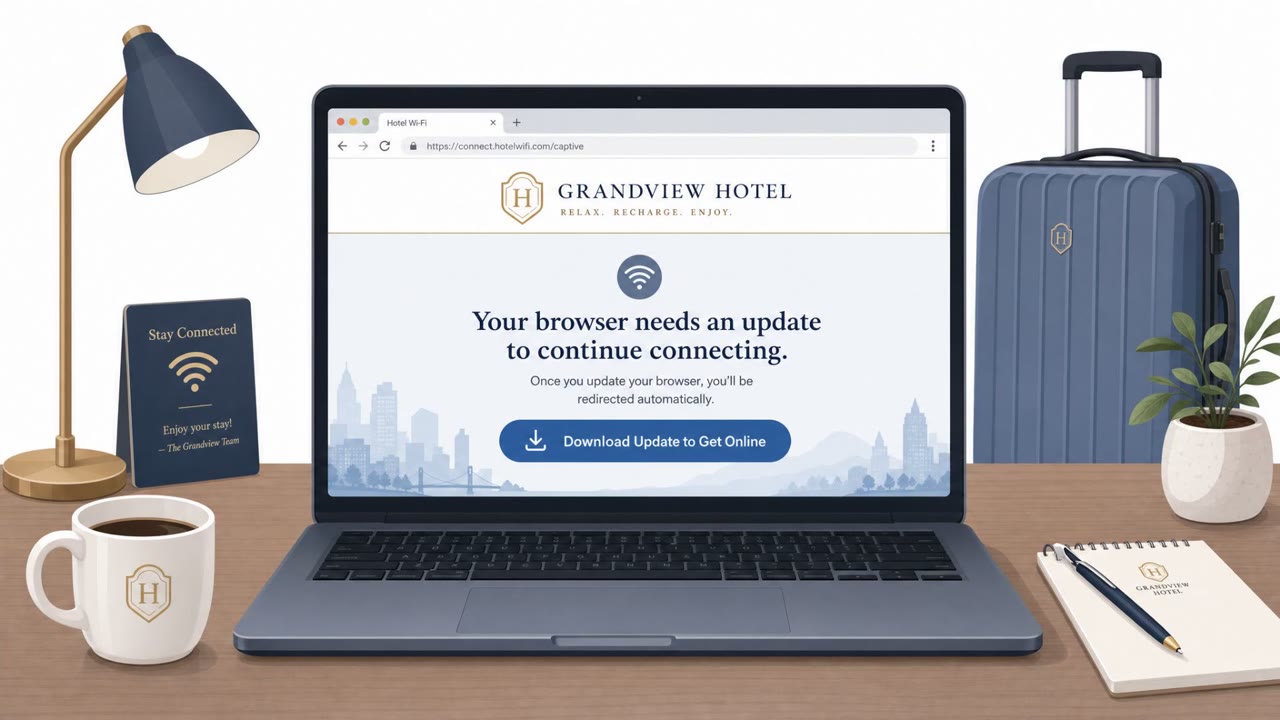
Microsoft says Russian SVR operators (Storm-2945/Midnight Blizzard) are compromising public Wi‑Fi captive portals in hotels and conference venues to redirect users to attacker-controlled pages. Those pages use fake “fix/verification/update” prompts to trick travelers into installing malware or…

August 3, 2026
Fake Repo Trust Triggers Code Before First Prompt

Fake Repo Trust Triggers Code Before First Prompt

Researchers describe how attackers can trick developers into cloning and “trusting” a repository in a coding agent, causing code to run automatically before the user even types a prompt. The post highlights real-world use of this pattern in fake job interview scams, and shows two concrete execution…

August 3, 2026
Hotel Wi‑Fi Hijack Pushes Fake Updates & Phishing

Hotel Wi‑Fi Hijack Pushes Fake Updates & Phishing

Microsoft reported a campaign where attackers abused hotel Wi‑Fi captive portals to manipulate DNS/HTTP traffic and redirect people to attacker-controlled phishing pages. Victims were tricked into installing malware disguised as browser/operating system updates, and some pages redirected users into…

August 3, 2026
Hackers Hijack Hotel Wi‑Fi to Push Fake Updates

Hackers Hijack Hotel Wi‑Fi to Push Fake Updates

Microsoft says attackers hijacked captive portals on hotel and conference Wi‑Fi to redirect travelers through attacker infrastructure. Victims were shown fake browser/OS update prompts (and sometimes “paste-and-run” instructions) to install malware, and later were pushed into Microsoft device-code…

August 3, 2026
Consent Phishing and Hijacked Hotel Wi‑Fi Portals

Consent Phishing and Hijacked Hotel Wi‑Fi Portals

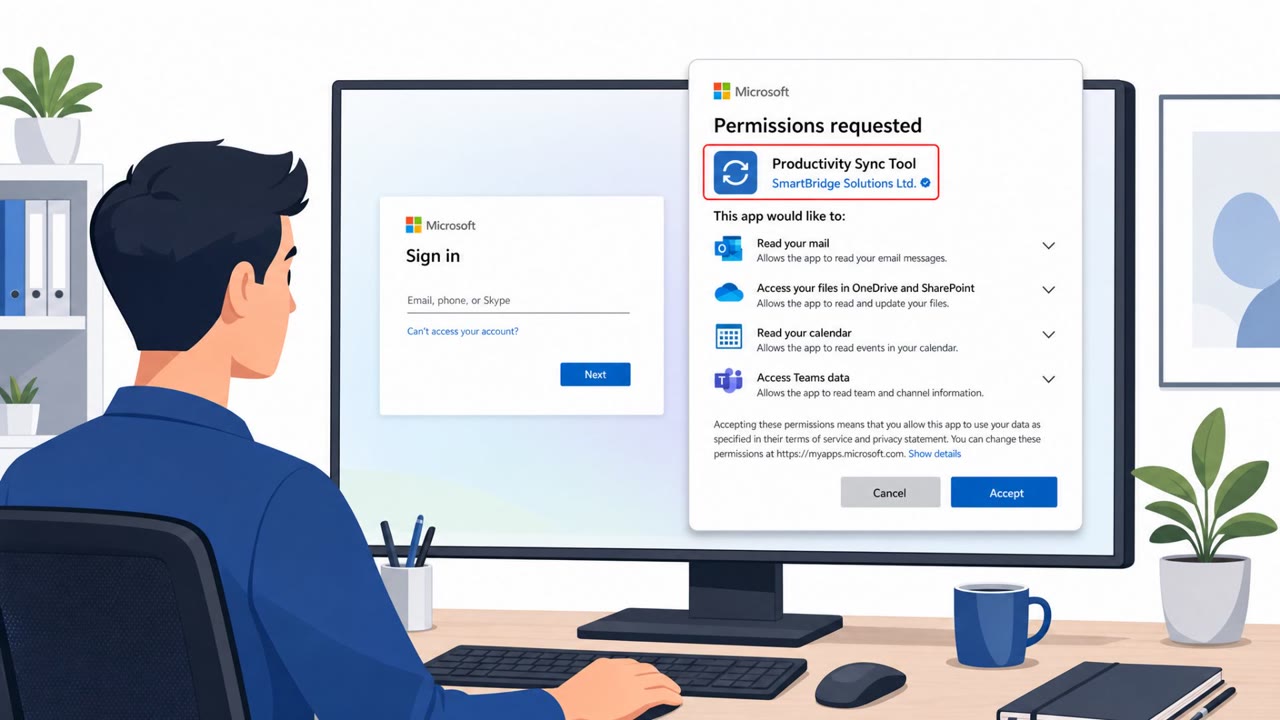
This weekly threat bulletin summarizes multiple real-world incidents, including phishing that abuses Microsoft’s legitimate app login/consent screens and a campaign that hijacks hotel Wi‑Fi captive portals. In both cases, the goal is to trick people into granting access or capturing Microsoft…

August 3, 2026
Hackers Hijack Hotel Wi‑Fi to Steal M365 Logins

Hackers Hijack Hotel Wi‑Fi to Steal M365 Logins

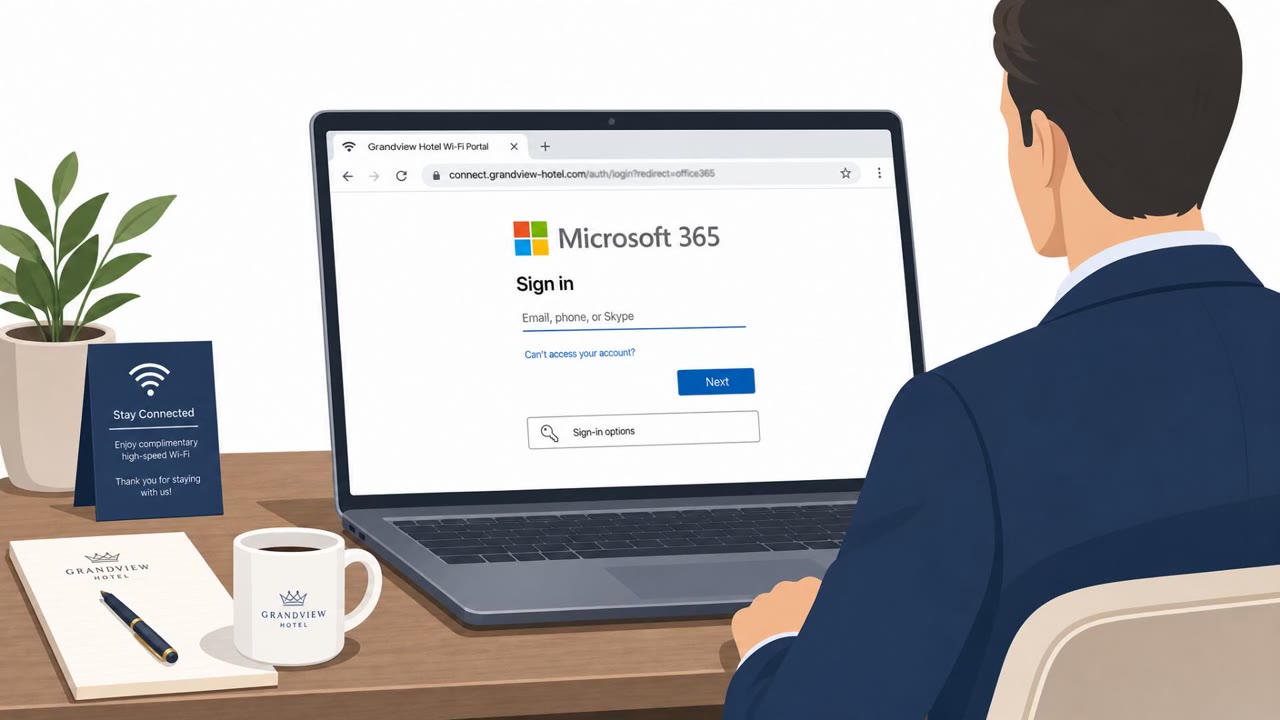
Microsoft and ReliaQuest report a real campaign where Russian-linked hackers compromised hotel Wi‑Fi networks and redirected travelers to fake Microsoft login pages or fake update screens. The goal was to steal Microsoft 365 credentials and/or trick victims into installing espionage malware,…

August 3, 2026
Law Firm Hit by Phish Using Fake Python Runtime

Law Firm Hit by Phish Using Fake Python Runtime

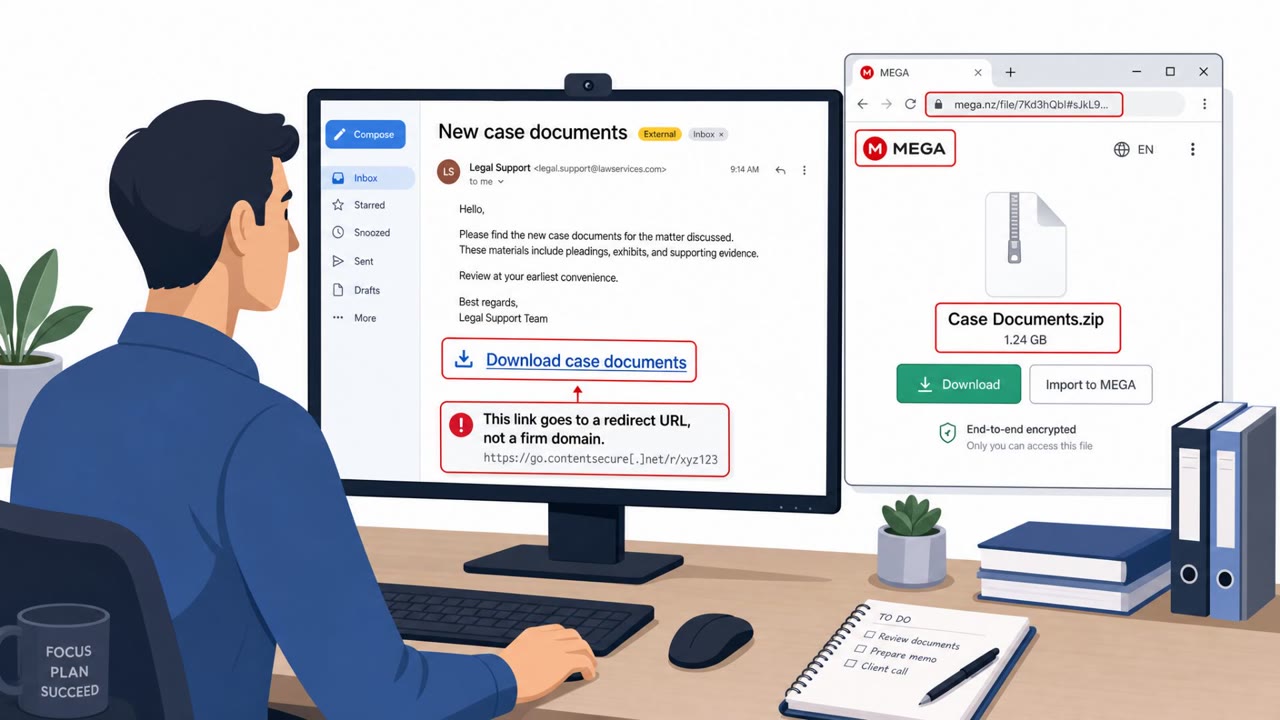
Researchers say a law firm was targeted with a spear‑phishing email that led staff to download an encrypted archive containing a Windows shortcut labeled like legal case files. After the user ran it and approved admin rights, the malware told Microsoft Defender to ignore a folder and a fake…

August 3, 2026
Fake AWS & Apple ID Pages Push iOS Spyware

Fake AWS & Apple ID Pages Push iOS Spyware

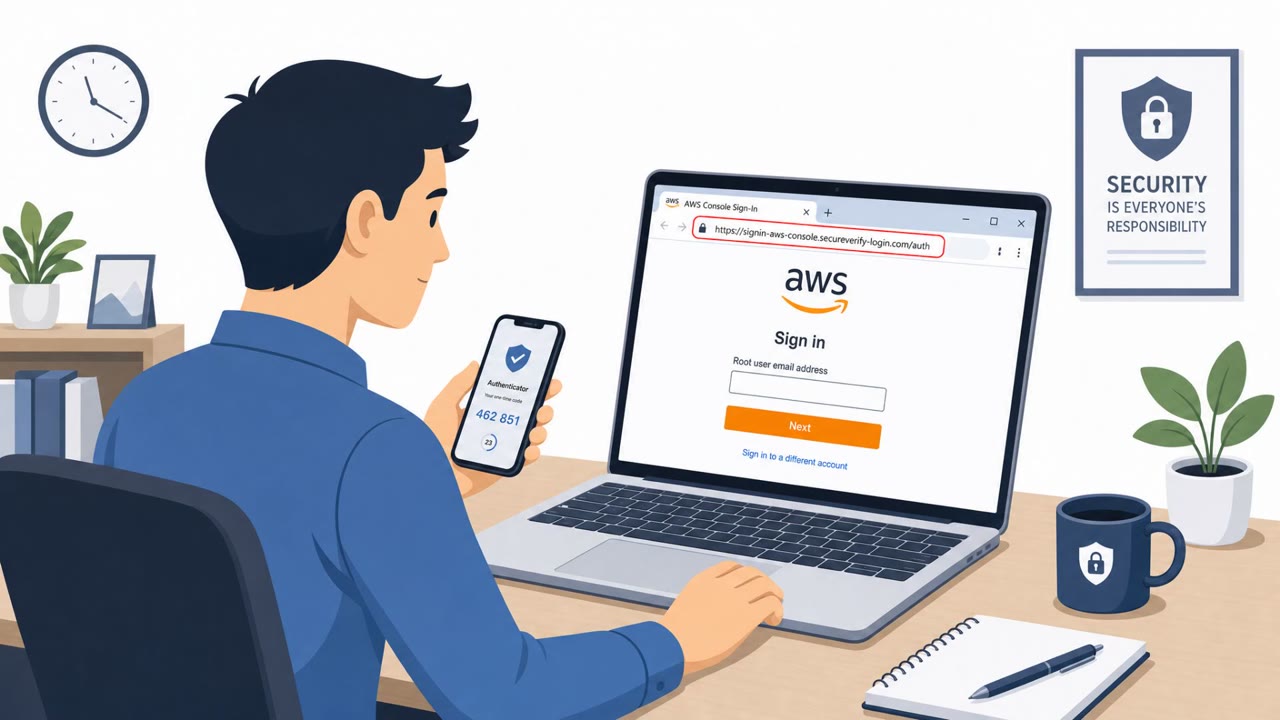
Researchers found an active campaign using fake AWS sign-in pages and an Apple ID decoy page to pull victims onto attacker-controlled websites. Visiting these pages can trigger an iOS exploit chain that installs GHOSTBLADE and steals sensitive data like iCloud, Keychain, and Wi‑Fi credentials.

August 3, 2026
Hacked Wi‑Fi Portals Steal M365 Logins

Hacked Wi‑Fi Portals Steal M365 Logins

Microsoft and ReliaQuest report a real campaign where attackers tampered with public Wi‑Fi captive portal networks (hotels/conference venues) to redirect users to attacker-controlled pages. The goal was to steal Microsoft 365 credentials (and sometimes deliver malware) by using…

August 3, 2026
OpenAI: ChatGPT Aided Cambodia Scam Network

OpenAI: ChatGPT Aided Cambodia Scam Network

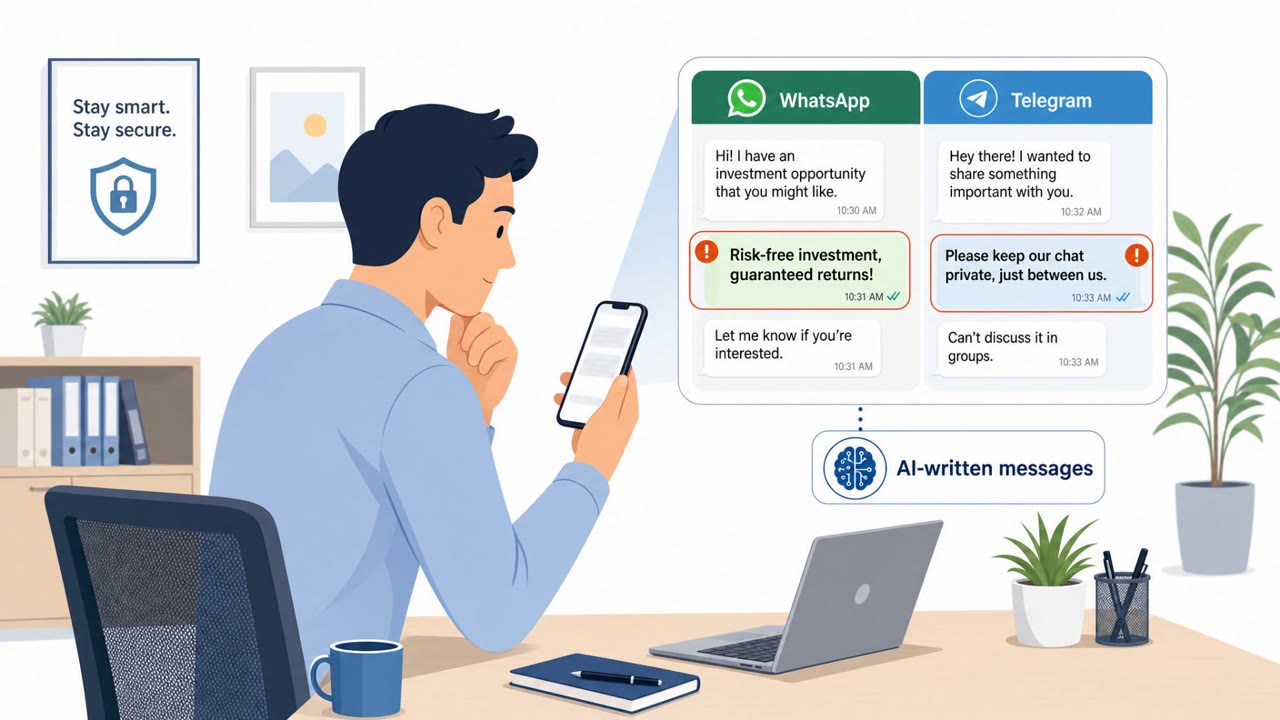
OpenAI says it shut down a coordinated network of ChatGPT accounts linked to Cambodia that supported multiple real-world scams, including investment, romance, gambling, and law-enforcement impersonation. The group used AI to create fake personas, translate and generate persuasive messages on…

August 3, 2026
Larva-24009 Lures Firms With Fake Doc Attachments

Larva-24009 Lures Firms With Fake Doc Attachments

AhnLab reports Larva-24009 has continued phishing campaigns through 2026, sending emails that trick employees into opening fake “document” attachments that are actually shortcut (LNK) files. When opened, the attachment runs hidden PowerShell commands, shows a decoy document, and silently downloads…

August 3, 2026
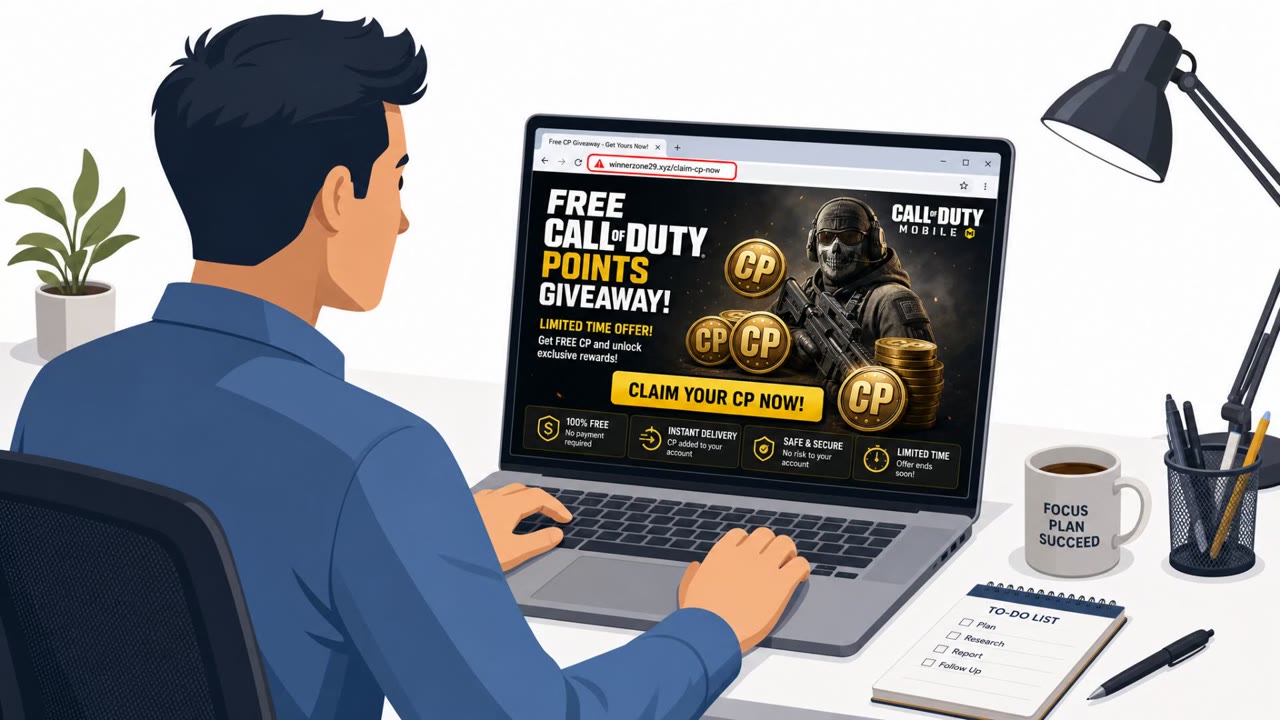
Fake Free COD Points Scam Steals Logins and 2FA

Fake Free COD Points Scam Steals Logins and 2FA

A real phishing campaign targeted Call of Duty Mobile players by promising free in-game currency. Victims were tricked into entering their email and password, then providing a 2FA code on a follow-up page, enabling attackers to take over accounts.

August 2, 2026
Ransomware Crew Poses as “Ransomware Help”

Ransomware Crew Poses as “Ransomware Help”

After exploiting SonicWall SMA 1000 VPN appliances, attackers tied to INC Ransomware reportedly contacted victims directly using emails and phone calls claiming they could help with “ransomware issues.” One caller said he was “from a group of hackers,” asserted the network was compromised, and…

August 1, 2026
Hotel Wi‑Fi Captive Portals Used to Steal M365

Hotel Wi‑Fi Captive Portals Used to Steal M365

Microsoft reported a real campaign where Russian-linked attackers tampered with hotel and conference Wi‑Fi “captive portals” to redirect travelers to attacker-controlled pages. Victims were tricked into installing malware or completing a Microsoft “device code” sign-in that granted the attacker…

August 1, 2026
DNC Staffer Fooled by Chair Impersonation Scam

DNC Staffer Fooled by Chair Impersonation Scam

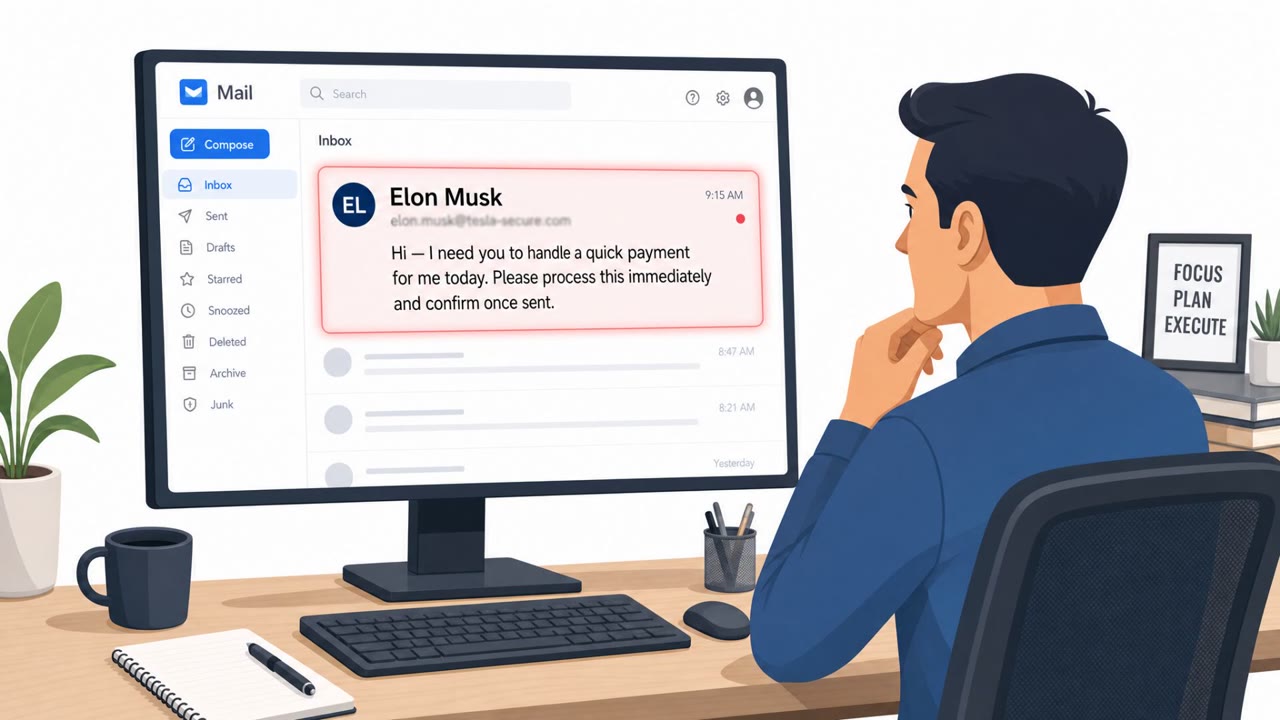
A scammer impersonated the Democratic National Committee chair and convinced a staffer to send nearly $29,000. The DNC detected the issue within minutes, but only recovered part of the funds. This is a classic business email compromise (BEC) pattern: a trusted executive identity is used to pressure…

August 1, 2026
Hijacked Hotel Wi‑Fi Serves Fake Updates

Hijacked Hotel Wi‑Fi Serves Fake Updates

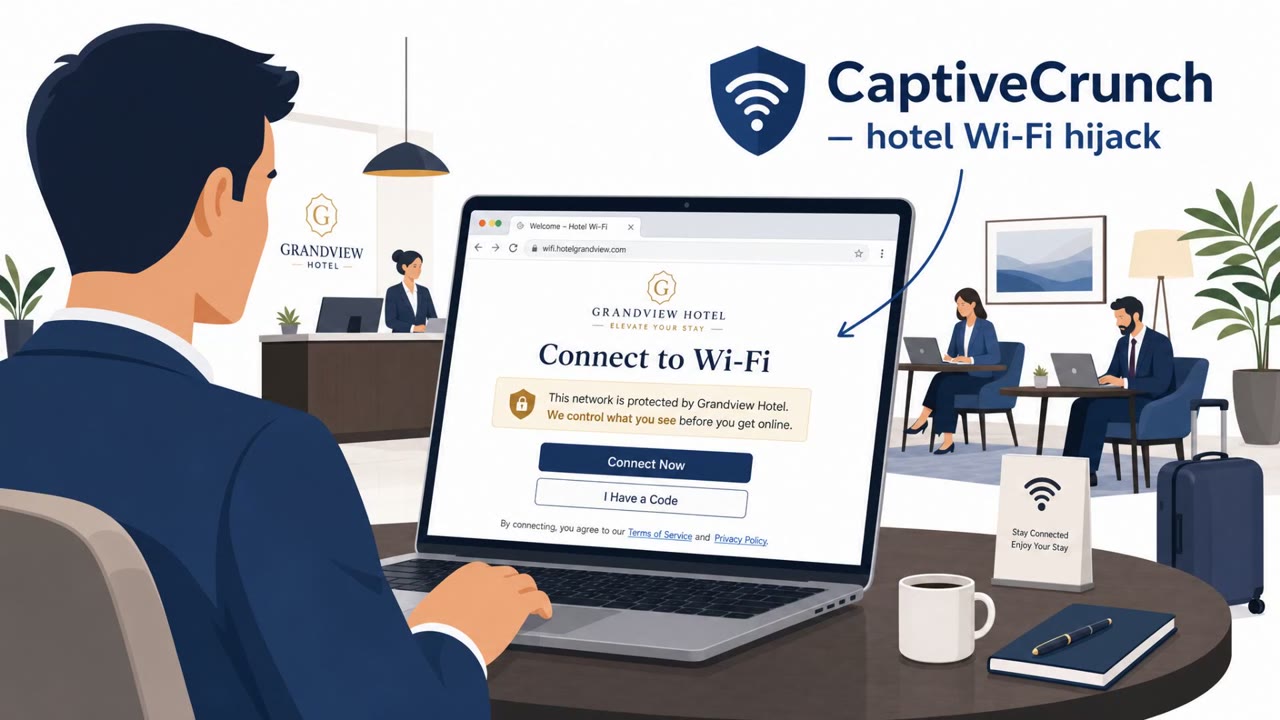
Attackers hijacked hotel/captive-portal Wi‑Fi infrastructure to redirect travelers to fake browser or operating system update pages and trick them into installing spyware. The operation (tracked as CaptiveCrunch) used DNS manipulation and user prompts (including “ClickFix” instructions) to get…

August 1, 2026
Captive Portal Trick Hits Travelers With Fake Updates

Captive Portal Trick Hits Travelers With Fake Updates

Microsoft reports a real-world campaign where attackers tamper with Wi‑Fi captive portal traffic at hotels and similar venues to redirect travelers to attacker-controlled pages. Victims are pushed into fake Microsoft sign-ins (device code/OAuth phishing) or tricked into installing “browser/OS…

July 31, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo