Threat Watcher

Page 13 of 51
EvilTokens MFA Phish Hijacked 12,000 Inboxes

EvilTokens MFA Phish Hijacked 12,000 Inboxes

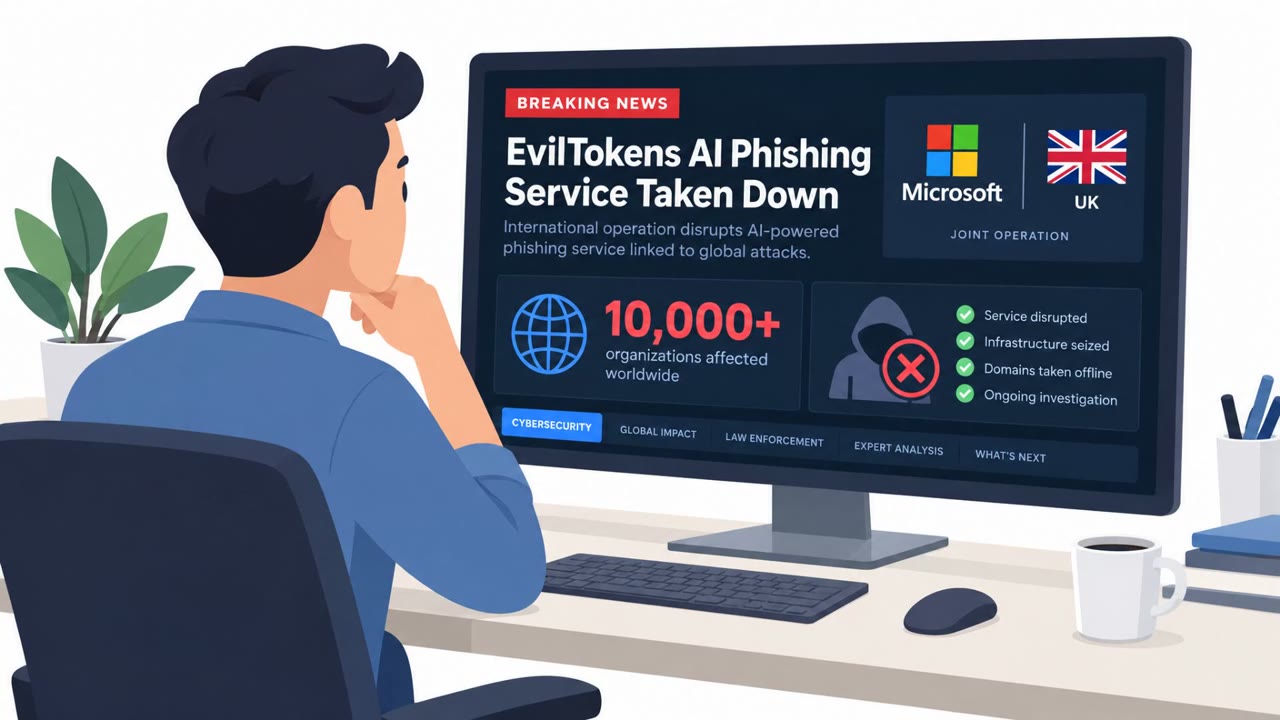
Microsoft and partners disrupted “EvilTokens,” a phishing service that helped criminals break into more than 12,000 mailboxes across 10,000+ organizations. Victims were tricked into entering an authentication code on a real Microsoft sign-in page, letting attackers capture access tokens and get…

September 23, 2026
EvilTokens Device-Code Phish Hit 12,000 Inboxes

EvilTokens Device-Code Phish Hit 12,000 Inboxes

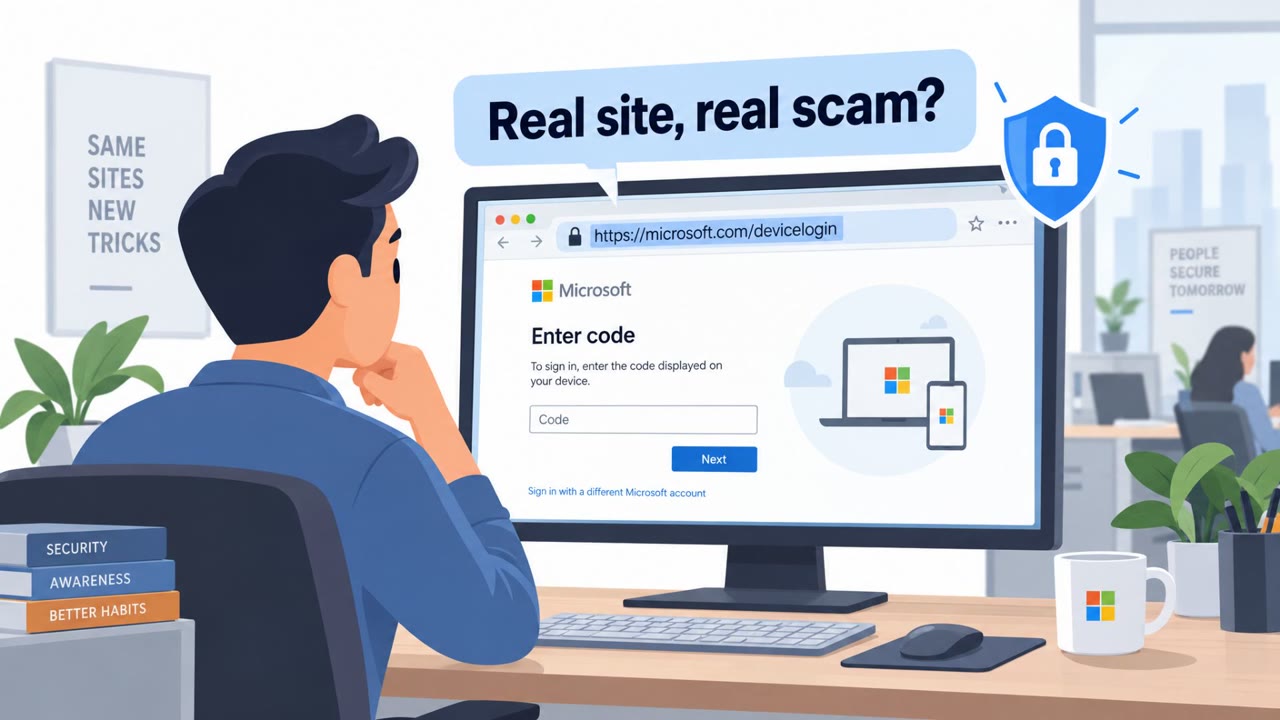
EvilTokens was a phishing-as-a-service operation that used “device code phishing” to trick employees into authorizing an attacker session on Microsoft’s real login infrastructure, often bypassing MFA without stealing passwords. After access, attackers used AI to find payment-related conversations…

September 23, 2026
Fake NGO Sites Lure Victims Into Chrome 0-Day Chain

Fake NGO Sites Lure Victims Into Chrome 0-Day Chain

China-linked actor UTA0565 sent phishing emails that pushed recipients to click spoofed links to fake media/NGO websites. Visiting the sites triggered a Chrome-to-Windows zero-day exploit chain that escaped the browser sandbox and installed CLEANGULP malware for remote control.

September 23, 2026
Fake LastPass GitHub Drops Rapuncel Stealer

Fake LastPass GitHub Drops Rapuncel Stealer

Attackers impersonated LastPass on GitHub and tricked people searching for the “LastPass Authenticator download” into installing a fake installer. The infection chain used a Microsoft-signed driver to disable many security tools, then deployed an infostealer that stole passwords, crypto wallets,…

September 23, 2026
EvilTokens Used Device-Code Phish + AI for BEC

EvilTokens Used Device-Code Phish + AI for BEC

Microsoft disrupted EvilTokens, a phishing-as-a-service operation linked to thousands of compromised Microsoft 365 inboxes. The group used “device code” phishing to steal valid session tokens (not passwords) and then used an AI chatbot to scan mailboxes and help craft business email compromise…

September 22, 2026
Fake Twilio Bug-Bounty Tool Hides Credential Stealer

Fake Twilio Bug-Bounty Tool Hides Credential Stealer

Researchers found a malicious npm package that pretended to be an “authorized” Twilio bug-bounty security probe to trick developers into running it. When executed in a Twilio developer environment, it collected system details and (in some versions) attempted to steal Twilio credentials like Account…

September 22, 2026
China-Linked Phish Uses Fake Sites to Exploit Chrome

China-Linked Phish Uses Fake Sites to Exploit Chrome

Researchers say a China-aligned group (UTA0565) sent phishing emails to government targets and used multiple fake websites to lure victims into visiting pages that triggered a Chrome-and-Windows zero-day exploit chain. The messages used political advocacy themes and spoofed well-known organizations…

September 22, 2026
Device-Code Phishing Service Hit After 12K Breaches

Device-Code Phishing Service Hit After 12K Breaches

Microsoft and partners disrupted “EvilTokens,” a phishing-as-a-service platform Microsoft links to over 12,000 compromised inboxes across more than 10,000 organizations. The service used deceptive emails to trick people into pasting a “device code” into Microsoft’s real sign-in page…

September 22, 2026
EvilTokens Used AI to Supercharge Phishing Scams

EvilTokens Used AI to Supercharge Phishing Scams

Microsoft and UK police took down “EvilTokens,” an AI-powered phishing service sold on Telegram that helped criminals compromise email accounts and then rapidly find the best ways to commit fraud. The service could analyze a victim’s inbox to identify trusted relationships and financial workflows,…

September 22, 2026
EvilTokens Uses Device Codes to Bypass MFA

EvilTokens Uses Device Codes to Bypass MFA

Microsoft reports that the EvilTokens phishing-as-a-service platform helped criminals compromise thousands of organizations by tricking users into completing a legitimate Microsoft “device code” login. The lure drives victims to enter a short code at microsoft.com/devicelogin, which unknowingly…

September 22, 2026
EvilTokens Takedown Exposes AI-Driven BEC Fraud

EvilTokens Takedown Exposes AI-Driven BEC Fraud

Microsoft and partners disrupted “EvilTokens,” a phishing-as-a-service operation linked to more than 12,000 compromised Microsoft email inboxes across 10,000+ organizations. The service used AI to pick targets, impersonate trusted contacts, and steal session tokens so criminals could stay in…

September 22, 2026
Fake Payment Plan Email Drops Global Ransomware

Fake Payment Plan Email Drops Global Ransomware

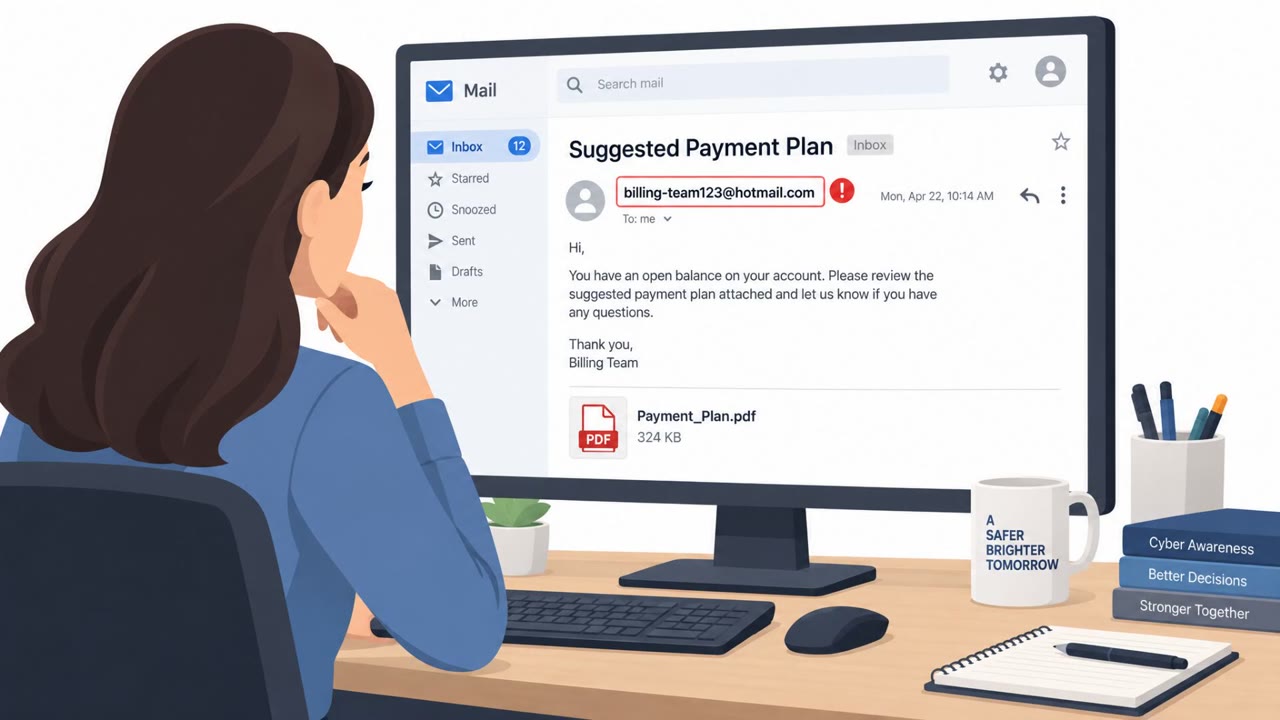
Cofense investigated a real ransomware delivery chain that starts with an email posing as a “Suggested Payment Plan” and a PDF attachment. The PDF contains a “Download” button that redirects victims to a malicious site to save an ISO file, ultimately leading to an encryptor download and system-wide…

September 22, 2026
Brevo Hack Injects Fake Cloudflare “Verify” Prompts

Brevo Hack Injects Fake Cloudflare “Verify” Prompts

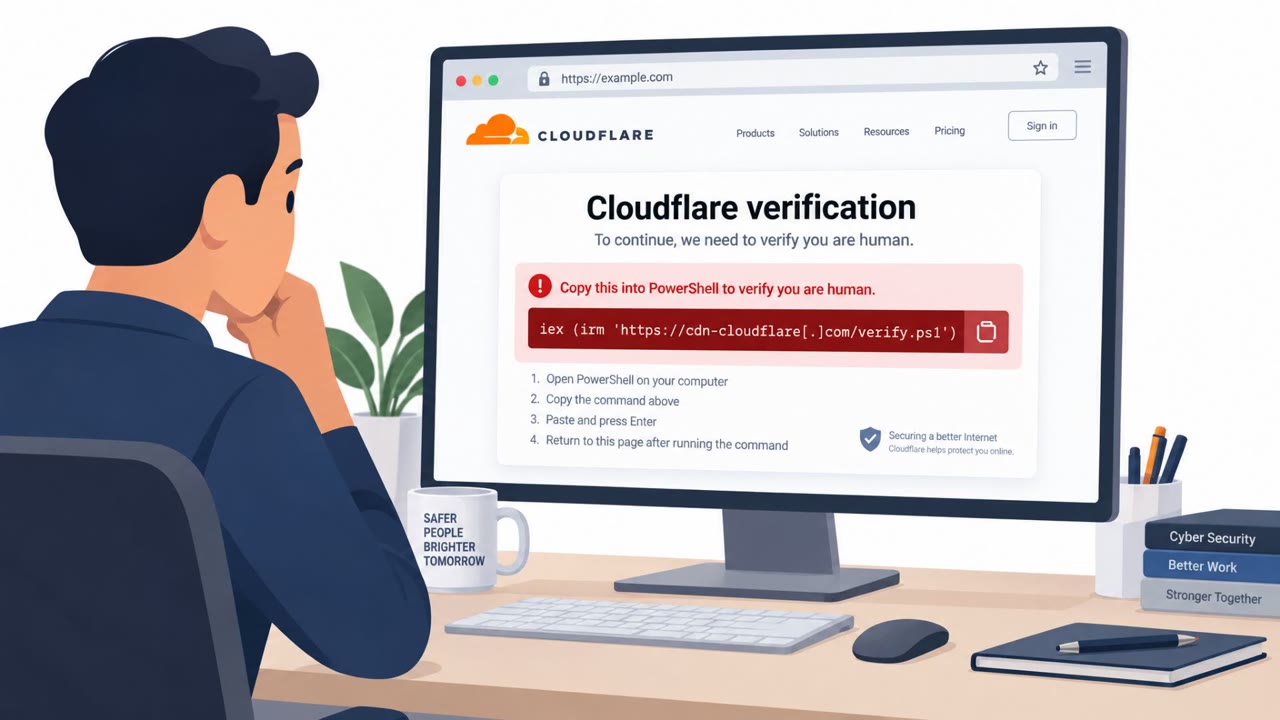
Attackers compromised Brevo’s Cloudflare setup using a long-lived API key found in source code, then altered website content at the CDN edge. Visitors were shown fake Cloudflare verification prompts to run Windows commands, and logged-in WordPress admins were targeted with a hidden backdoor plugin…

September 22, 2026
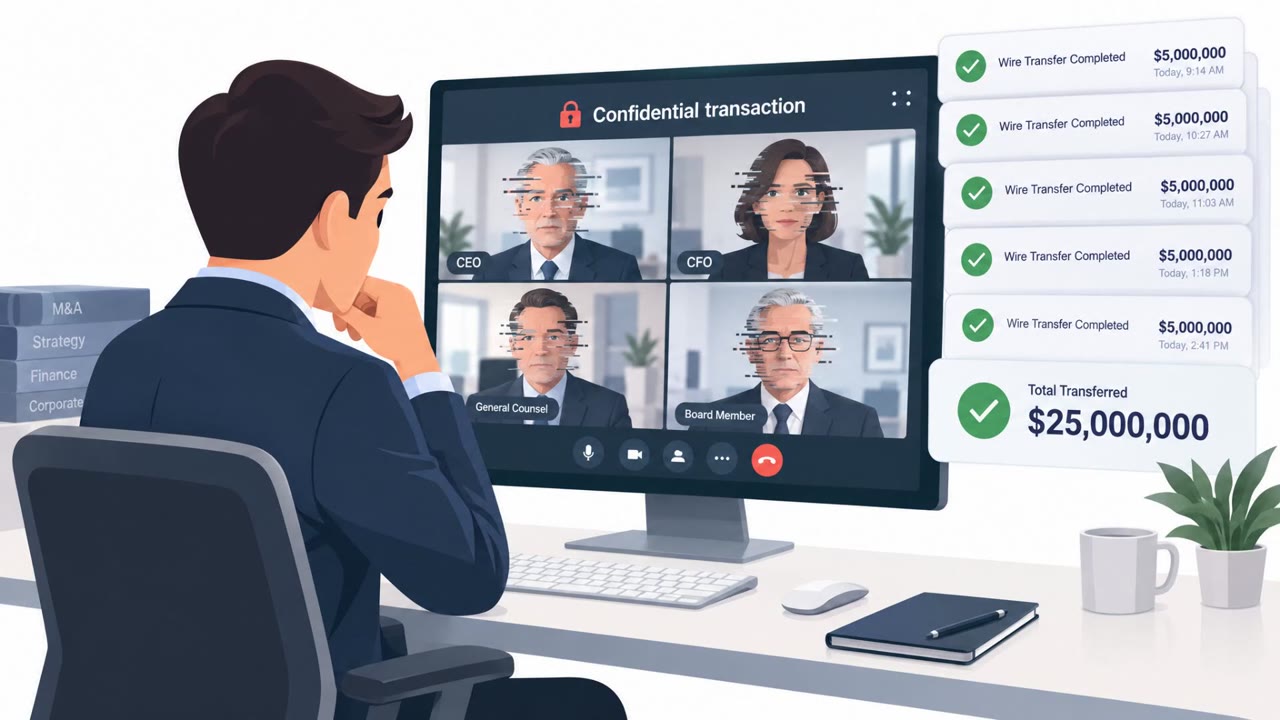
Deepfake CFO Video Call Triggers $25M Transfer

Deepfake CFO Video Call Triggers $25M Transfer

The article highlights that deepfakes are being used in real social-engineering incidents, including audio and video calls that impersonate trusted leaders. It cites a well-known 2024 Hong Kong case where scammers used a fake video meeting to pose as a company’s CFO and colleagues, leading an…

September 22, 2026
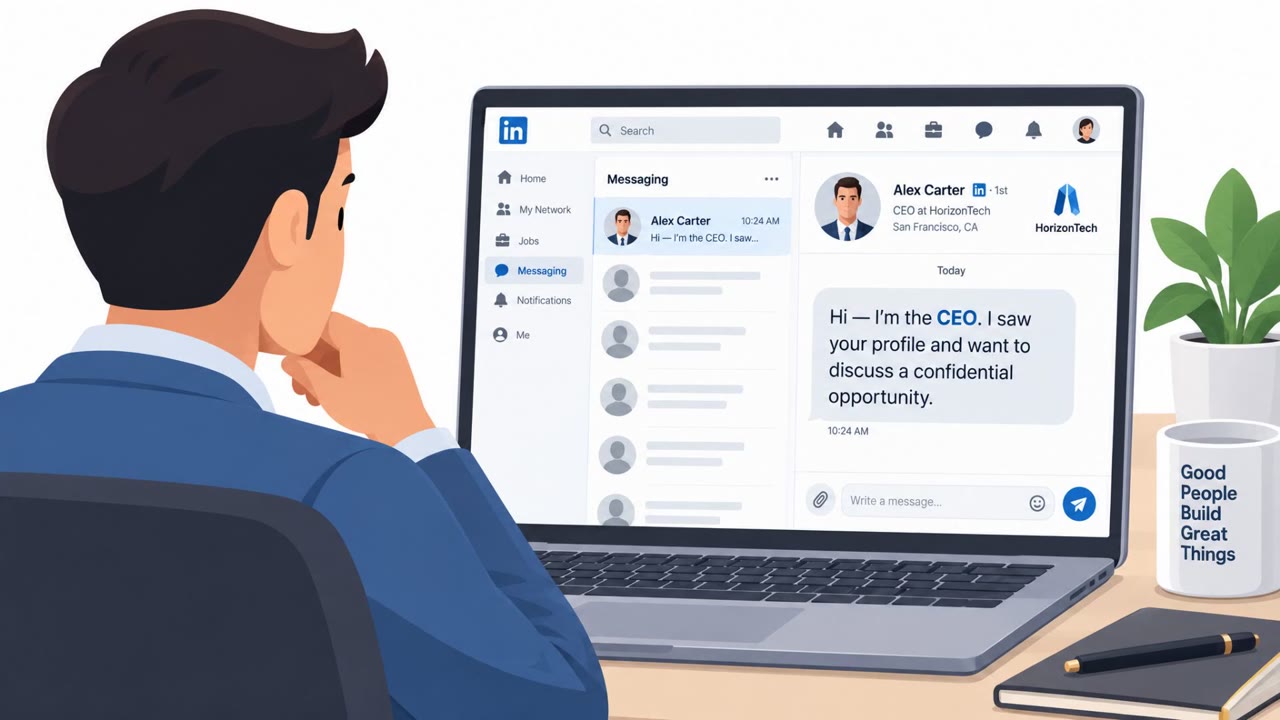
Fake CEOs on LinkedIn Fuel IP & Data Theft

Fake CEOs on LinkedIn Fuel IP & Data Theft

A CSC report describes real-world scams where criminals impersonate executives and brands online to steal personal or payment information. Examples include fake CEOs contacting people on LinkedIn with bogus job offers, and lookalike “FIFA” domains used for fake ticket sales, travel offers, and…

September 22, 2026
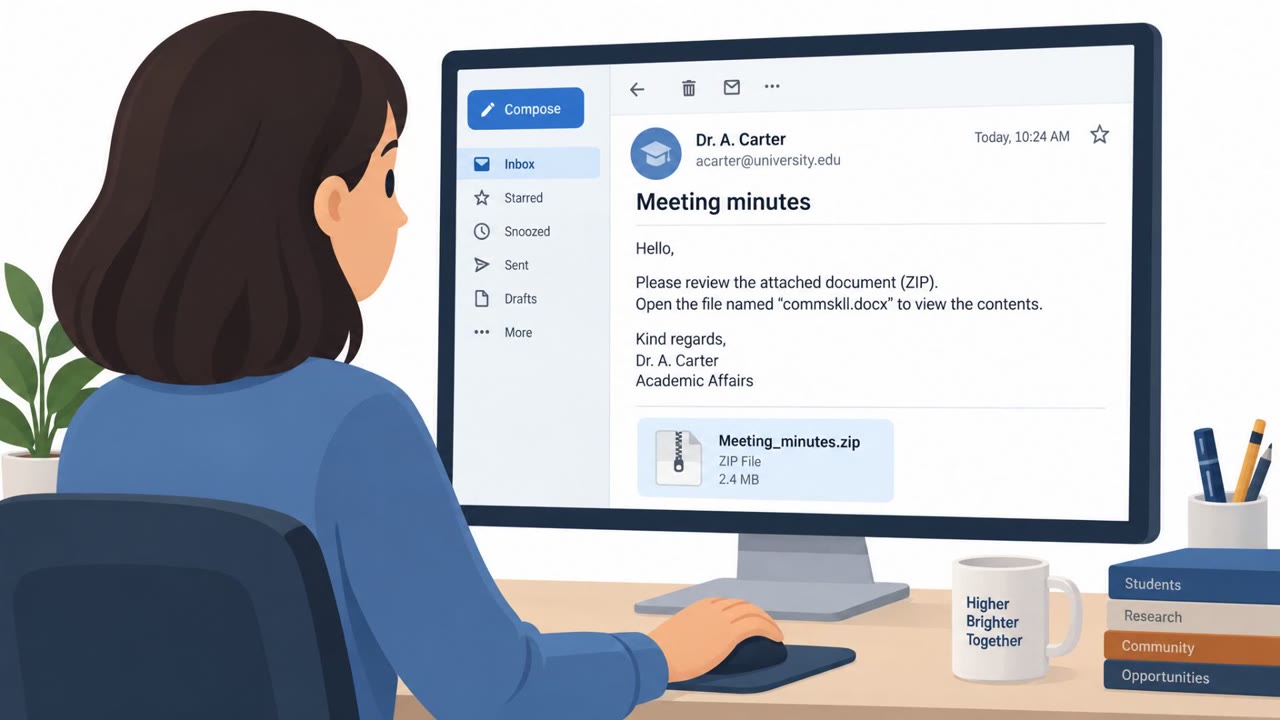
SideCopy Phishes Indian Universities With Fake Docs

SideCopy Phishes Indian Universities With Fake Docs

Pakistan-linked APT group SideCopy expanded from targeting Indian government entities to targeting Indian academic institutions using spear-phishing. The emails deliver a weaponized ZIP containing a fake “document” shortcut that launches mshta.exe to pull down and run malware, ultimately installing…

September 22, 2026
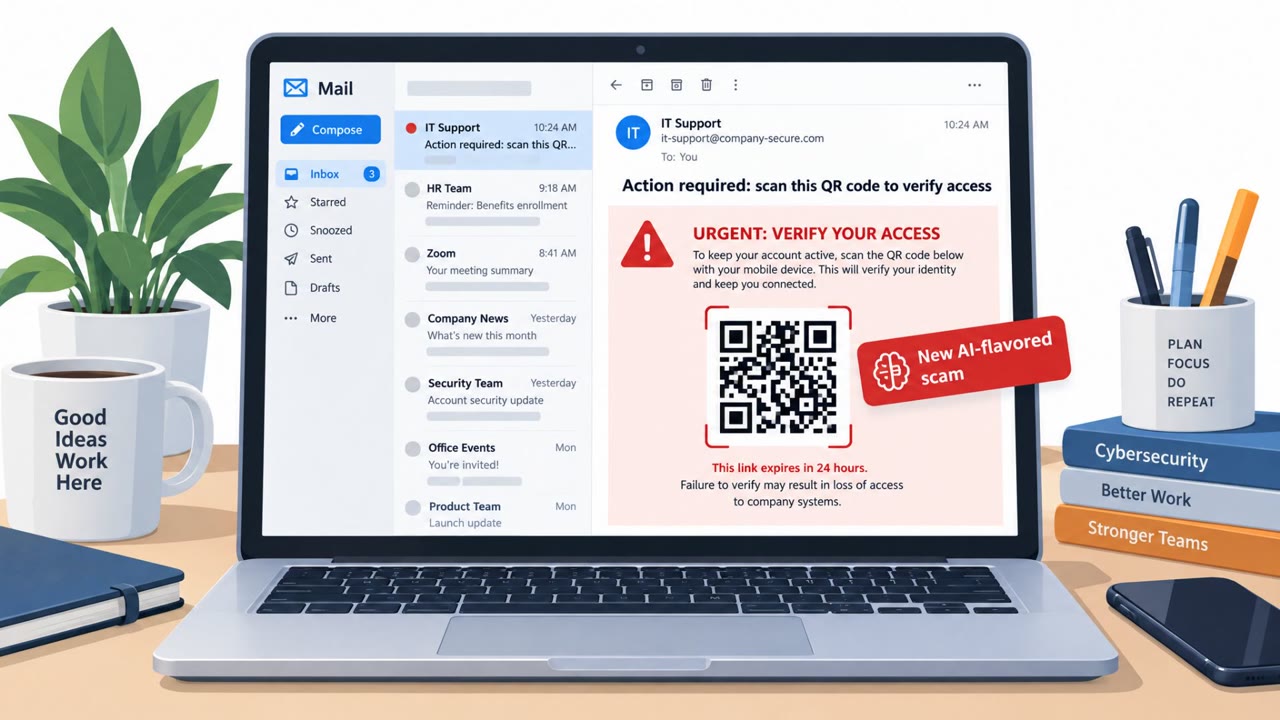
AI-Boosted Phishing and “ClickFix” Scams Hit SMBs

AI-Boosted Phishing and “ClickFix” Scams Hit SMBs

The article warns that small and mid-size businesses are facing a squeeze: new risks from AI agents connected to company systems, and faster, more effective versions of familiar scams like phishing. It highlights real-world trends such as QR-code phishing and “ClickFix,” where fake error pages…

September 22, 2026
Deepfake Video Call Fooled Staff into $25M Transfers

Deepfake Video Call Fooled Staff into $25M Transfers

The article describes how criminals are using AI-generated video (“deepfakes”) to impersonate executives and trusted colleagues on live video calls. A real 2024 case at engineering firm Arup shows how a finance employee was convinced by a deepfake CFO and colleagues to send about $25 million across…

September 22, 2026
DPRK Poses as Recruiters to Malware IT Pros

DPRK Poses as Recruiters to Malware IT Pros

Australian and allied agencies warned that North Korean-linked actors are impersonating recruiters and fake AI/crypto/NFT companies to lure IT professionals into a hiring process that installs malware. The goal is to steal sensitive information and drain cryptocurrency wallets, with reporting…

September 22, 2026
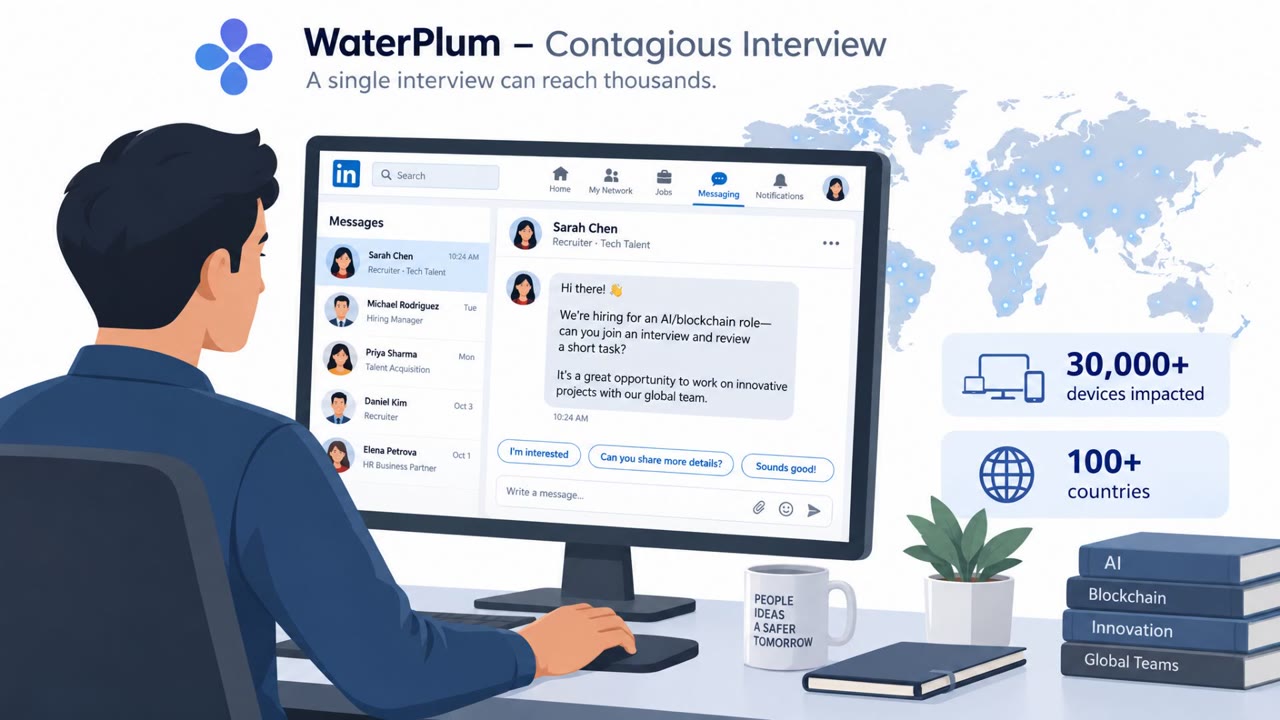
Fake AI Recruiters Hit 30K Devices Worldwide

Fake AI Recruiters Hit 30K Devices Worldwide

A weekly threat bulletin highlights a North Korea–linked campaign where attackers posed as AI or blockchain employers to trick IT professionals into getting infected and losing cryptocurrency. It also notes a phishing kit that abuses Microsoft’s legitimate device login flow to gain long-lasting…

September 22, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo