Recent Professional Services Cyber Attacks

Page 3 of 6
Fake Recruiters Steal Enterprise Logins on Mobile

Fake Recruiters Steal Enterprise Logins on Mobile

A real “fake recruiter” phishing campaign (tracked as RecruitTrap) is targeting employees’ corporate credentials, especially on mobile devices. The scam uses lookalike recruitment domains and full-screen fake login pages that hide browser cues, and it rejects personal email addresses to focus on…

August 25, 2026
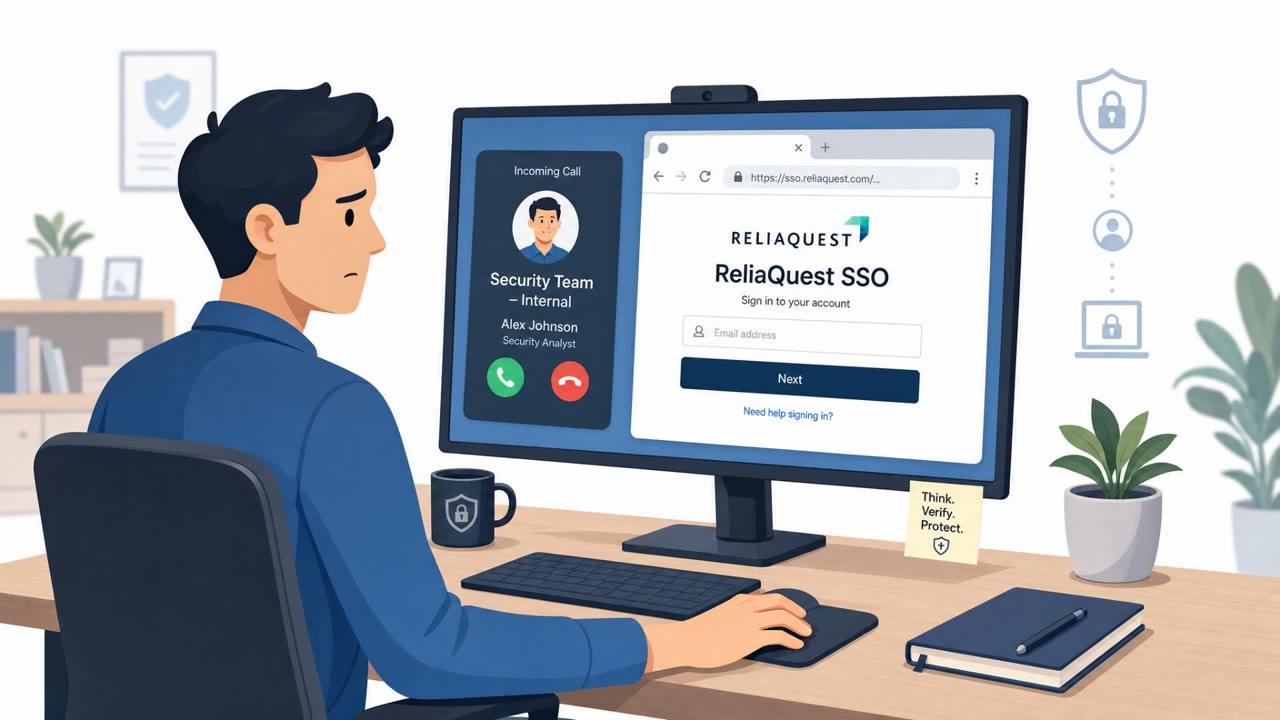
ReliaQuest Employee Tricked Into Okta SSO Login

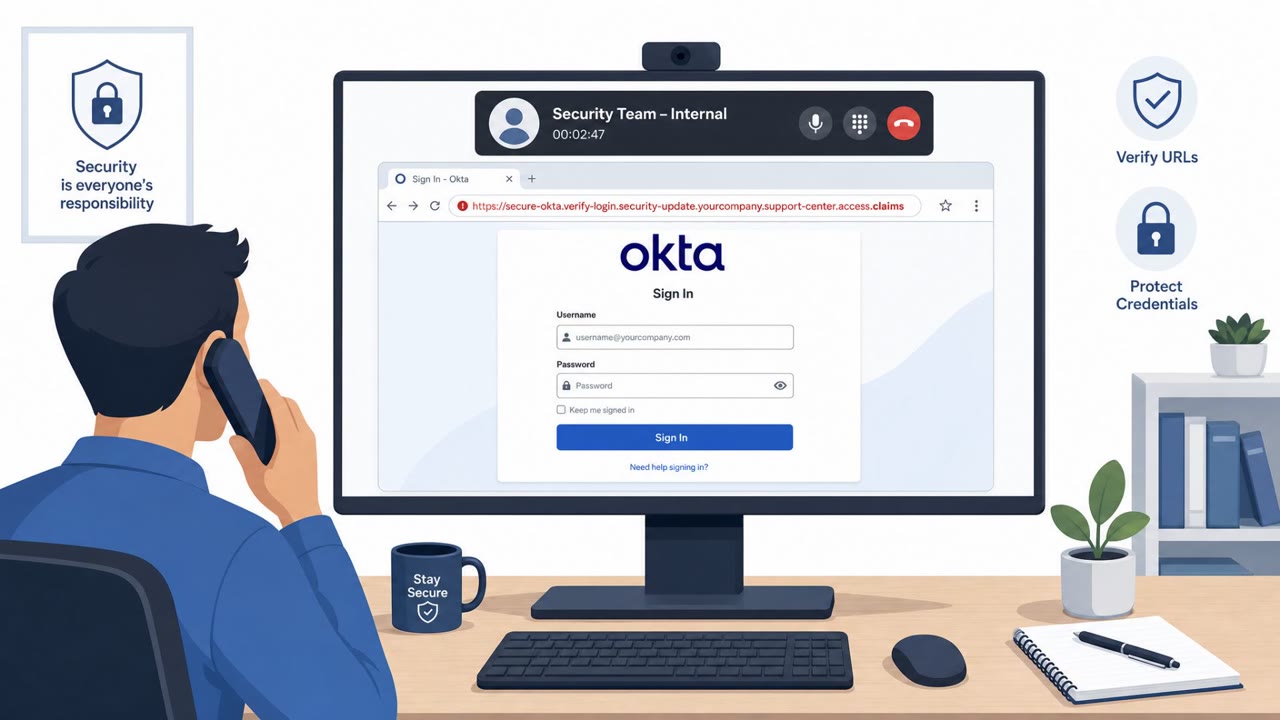
ReliaQuest Employee Tricked Into Okta SSO Login

ReliaQuest confirmed an employee was socially engineered into entering their password on a fake SSO page and approving an MFA push, giving attackers a brief “view only” session in the company’s identity dashboard. The attackers allegedly impersonated a named member of the security team over the…

August 25, 2026
ShinyHunters Impersonation Call Tricked ReliaQuest MFA

ShinyHunters Impersonation Call Tricked ReliaQuest MFA

ReliaQuest disclosed a real social engineering incident where attackers registered a lookalike domain, hosted a fake ReliaQuest SSO page, and called employees while impersonating a named security employee. One employee entered credentials and approved an MFA push, briefly giving the attacker…

August 25, 2026
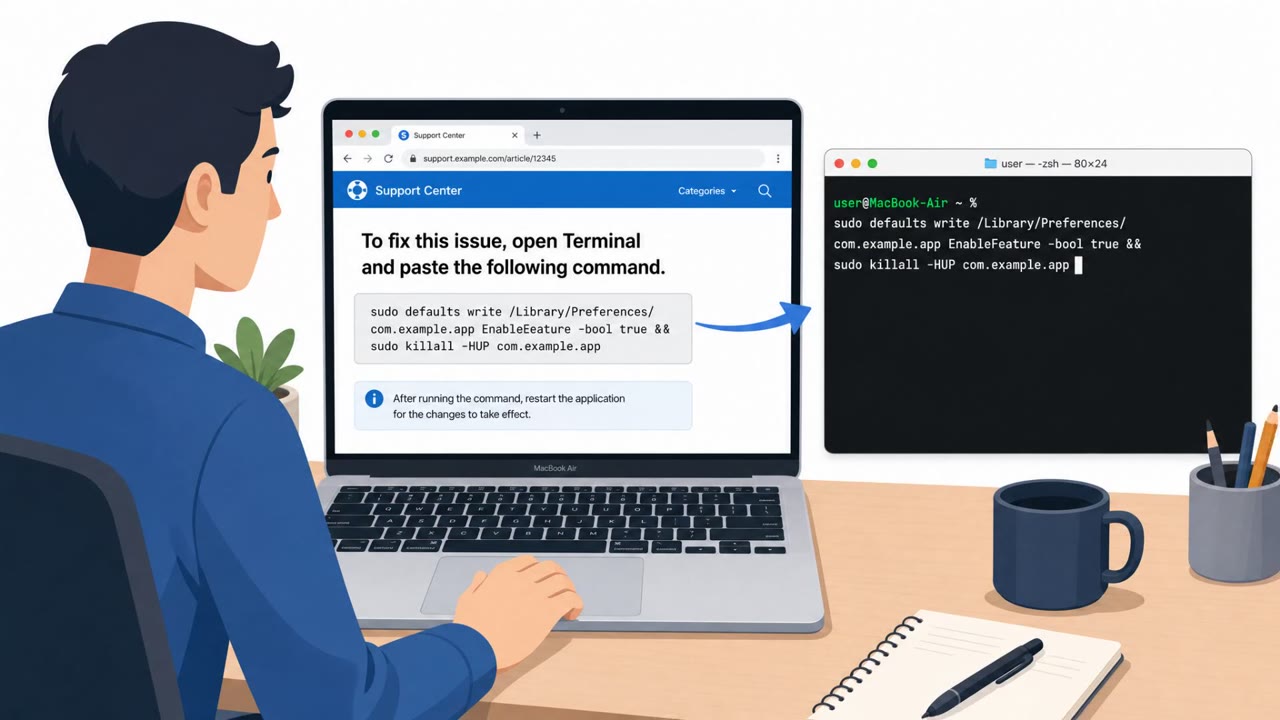
Fake “OpenAI Codex” Ads Push Mac ClickFix Malware

Fake “OpenAI Codex” Ads Push Mac ClickFix Malware

Attackers are buying sponsored Google search ads that send Mac developers to fake OpenAI Codex download pages. The pages instruct victims to paste a Terminal command that looks like a normal install step, but actually downloads and runs a multi-stage malware payload.

August 25, 2026
ShinyHunters Hit ReliaQuest With SSO Phish + Calls

ShinyHunters Hit ReliaQuest With SSO Phish + Calls

ReliaQuest said it was targeted in a ShinyHunters-linked social engineering attack that used a fake domain hosting a ReliaQuest single sign-on (SSO) phishing page. Attackers then called employees while impersonating named security staff to push victims to the fake login page, resulting in one…

August 24, 2026
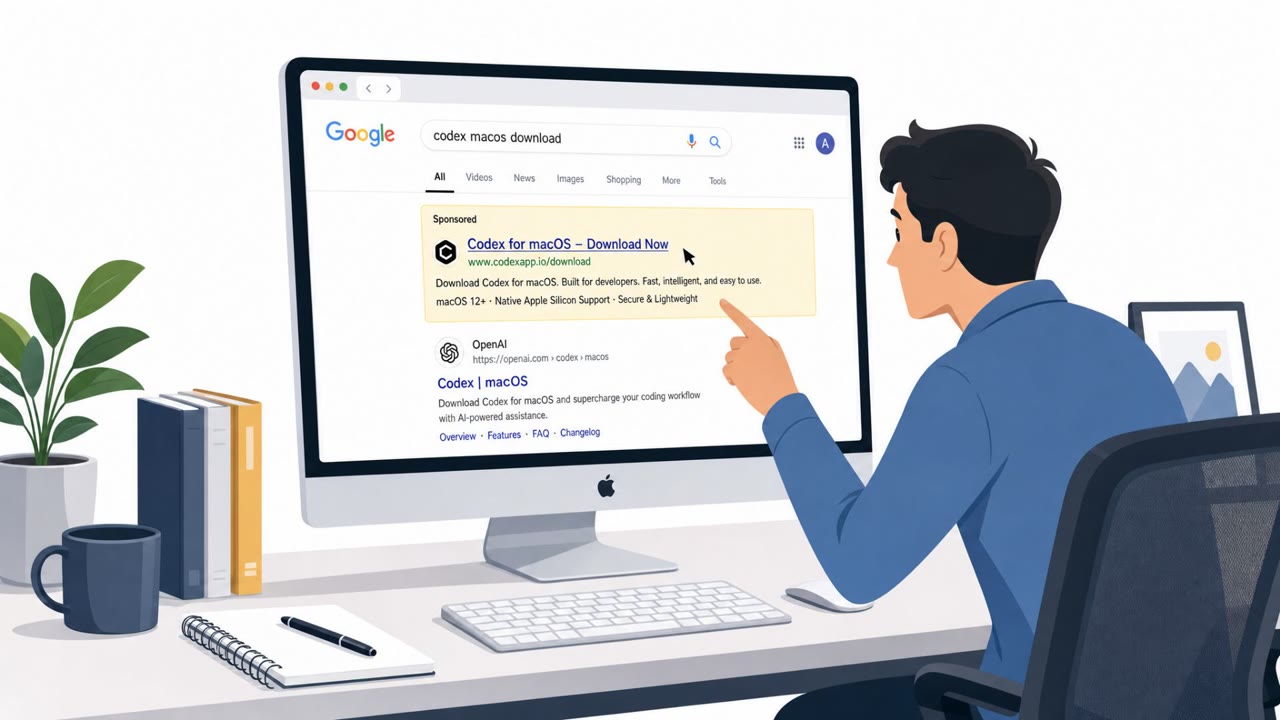
Fake Codex Download Lures Macs Into Terminal Malware

Fake Codex Download Lures Macs Into Terminal Malware

Researchers described a real macOS malware campaign that tricks people searching for “Codex macos download” into clicking a sponsored Google result and landing on a fake OpenAI Codex download site. Victims are then coached to open Terminal and paste a command that fetches and runs malware (a…

August 24, 2026
Apollo Breach Tied to IT Helpdesk Vishing

Apollo Breach Tied to IT Helpdesk Vishing

Apollo Global Management disclosed a breach after attackers used social engineering to access some of its cloud platforms over several days in July. The company says personal data may have been exposed, including names, contact details, and Social Security numbers. Reporting links the incident to…

August 24, 2026
DEF CON Phish Uses Fake Coindesk VP + Google Doc

DEF CON Phish Uses Fake Coindesk VP + Google Doc

A real phishing campaign is targeting DEF CON speakers and attendees through X/Twitter messages pretending to be a Coindesk executive. Victims are sent to a Google document that attempts a “click-fix” trick to get them to paste malicious commands into a terminal or download malware. The goal is to…

August 21, 2026
Deepfake CFO Video Call Triggers $25M Fraud

Deepfake CFO Video Call Triggers $25M Fraud

The article describes real-world deepfake and identity-fraud incidents where attackers used believable human impersonation to manipulate employees. In one case, a staff member at Arup joined a video call with what appeared to be the CFO and was tricked into sending about $25M across multiple wire…

August 21, 2026
DEF CON Attendees Hit With Fake CoinDesk DMs

DEF CON Attendees Hit With Fake CoinDesk DMs

After Black Hat/DEF CON, cybercriminals allegedly targeted conference attendees by impersonating a CoinDesk executive over X direct messages. Victims were pushed into a realistic workflow using Google Docs and a fake Dropbox DocSend installer to trick them into running malware on macOS or Windows.

August 21, 2026
Wall Street Hit by Help Desk Impersonation Calls

Wall Street Hit by Help Desk Impersonation Calls

A real campaign of voice-phishing (vishing) calls targeted major hedge funds and private equity firms by impersonating internal IT/help desk staff. Victims were pressured into completing “routine” security steps and were sent to fake login pages that captured usernames, passwords, and MFA codes in…

August 20, 2026
Def Con DMs Lure Targets Into Fake Google Docs

Def Con DMs Lure Targets Into Fake Google Docs

A researcher was targeted after Black Hat/Def Con by an attacker posing as a CoinDesk executive and using X direct messages to build trust. The scam used familiar platforms (Google Docs and Dropbox DocSend) to push “ClickFix”-style steps or a fake installer intended to get the victim to run malware.

August 20, 2026
MacSync Stealer Uses ClickFix Terminal Paste Trap

MacSync Stealer Uses ClickFix Terminal Paste Trap

Microsoft reports real-world macOS infections where victims were tricked into pasting commands into Terminal (a “ClickFix”-style social-engineering method). The malware then downloads a payload, steals credentials and other sensitive data (like Keychain and browser sessions), and uploads it in…

August 19, 2026
Deepfake CFO Scam Turns Phishing Into Video Wire Fraud

Deepfake CFO Scam Turns Phishing Into Video Wire Fraud

The article describes how modern phishing can start with an email impersonation and then move into live deepfake video calls to pressure employees into sending money. It cites a widely reported case at engineering firm Arup where an employee, convinced by a deepfake video call featuring synthetic…

August 19, 2026
Wrong-Number Texts That Turn Into Scams

Wrong-Number Texts That Turn Into Scams

The article describes how “wrong-number” SMS messages are used as a first-step social engineering test to identify people who will engage with strangers. If the target replies, scammers may either build a long relationship that leads to fake investment fraud (“pig butchering”) or recycle the…

August 19, 2026
CoSnitch: One-Link Copilot Data Exfil Chain

CoSnitch: One-Link Copilot Data Exfil Chain

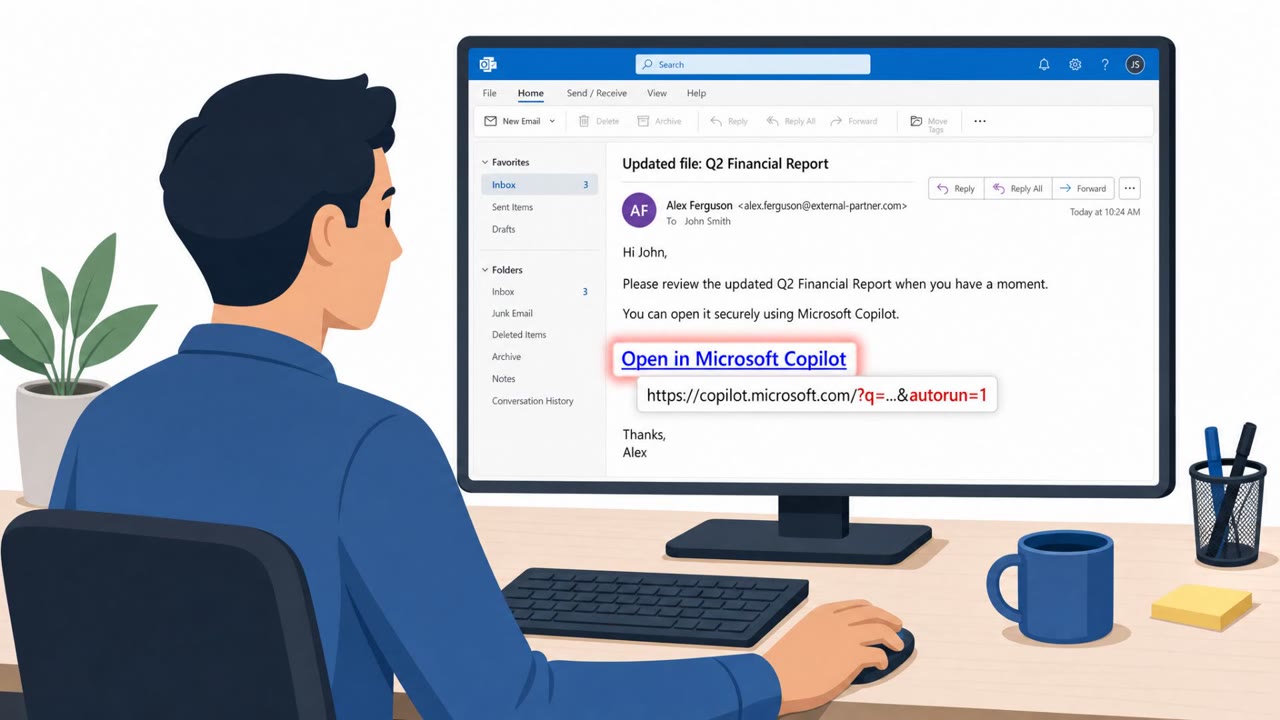
Researchers disclosed a critical Microsoft Copilot (personal) vulnerability chain that could let an attacker steal enterprise data by getting a user to open a legitimate-looking link or summarize a crafted webpage. The attack abuses Copilot features (auto-running prompts, connected-app access, and…

August 19, 2026
One-Click Copilot Link Triggers Data Exfil

One-Click Copilot Link Triggers Data Exfil

Researchers showed how an attacker could trick Microsoft Copilot into running a malicious prompt automatically just by getting a user to click a specially crafted link. The prompt can then make Copilot search connected accounts (like email and cloud storage) and send information to an external…

August 18, 2026
Azure Employee Directories Dumped via Stolen Access

Azure Employee Directories Dumped via Stolen Access

A threat actor called “TheHatman” claims they stole and posted large internal employee directories from multiple Fortune 500 companies’ Microsoft Azure tenants. Hudson Rock says the leaked samples look like real Azure directory exports, but the exact way the attacker got in is still unclear. One…

August 18, 2026
Fake GitHub Page Tricks Mac Users Into Malware

Fake GitHub Page Tricks Mac Users Into Malware

Researchers found a real macOS malware campaign that uses a fake GitHub download page to convince users to paste a command into Terminal and enter their Mac password. The malware then steals credentials, cookies, and files, and can even turn the victim’s Chromium browser into a remotely controlled…

August 17, 2026
DPRK “Remote Worker” Scam Slips Into Real Jobs

DPRK “Remote Worker” Scam Slips Into Real Jobs

The article describes North Korean operatives posing as legitimate remote IT candidates to get hired, obtain real company credentials, and gain trusted internal access. It cites an FBI investigation into a DPRK remote IT worker at a U.S. federal agency and a research “hire-and-observe” operation…

August 17, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo